
AuthManager_Mac on Mac: is it a virus, or just old Citrix?
AuthManager_Mac is, in most reports, a helper program of Citrix that macOS has refused to run since August 2021, not a virus. This page shows how to tell that case from real adware and what to do in each.
Facts checked October 6, 2026. Removal steps checked against Apple's current documentation and the security vendors' reports. We have not run the malware on a Mac.
Automatic
Get a free scan and check if your Mac is infected.
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds before you decide anything.
Do it yourself · free Remove AuthManager_Mac yourself 2 steps, about 6 minutes, no software needed.
Start the stepsAuthManager_Mac: summary
| Type | Usually an old Citrix helper that macOS rejects (not a virus); adware only if the file is not the Citrix one |
|---|---|
| Risk | Citrix file: low, a repeating alert at login. If it is adware: ads, redirects and changed browser settings |
| Symptoms | A dialog "AuthManager_Mac will damage your computer" at login, or a changed search engine, ads and unknown profiles |
| How to get rid of it | Citrix file: update or uninstall Citrix, restart, remove leftover com.citrix startup files. Adware: remove app, profile, extension and startup items |
| Our check (6 October 2026) | One Mac with no Citrix (macOS 26.4.1): no such file or startup entry. The affected case could not be tested |
| Alerts reported since | 28 April 2020 (Citrix forum); widespread from 23 August 2021 |
| Check the PC | The genuine file needs no removal. Fortect's free scan checks the Mac for malware hiding under system file names. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 7 more facts
| Genuine path | /usr/local/libexec/AuthManager_Mac.app, startup file com.citrix.AuthManager_Mac.plist |
|---|---|
| Distribution | Installed with Citrix software on a Mac; for the adware reading, fake updates, bundled installers and pirated software |
| Damage | None from the Citrix file beyond the repeating alert; adware can change browser settings and show ads |
| Detection names | No Microsoft detection name is known for the Citrix file: it is not detected as malware. Microsoft files Mac adware of the Adload type as Adware:MacOS/Adload.A |
| First seen by us | 4 March 2020, in our own first article |
| File name | AuthManager_Mac |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against our own look at a Mac without Citrix, Malwarebytes, Apple, Citrix and the Adload write-ups of Apple, SentinelOne and Microsoft.
What the AuthManager_Mac file is
What AuthManager_Mac is
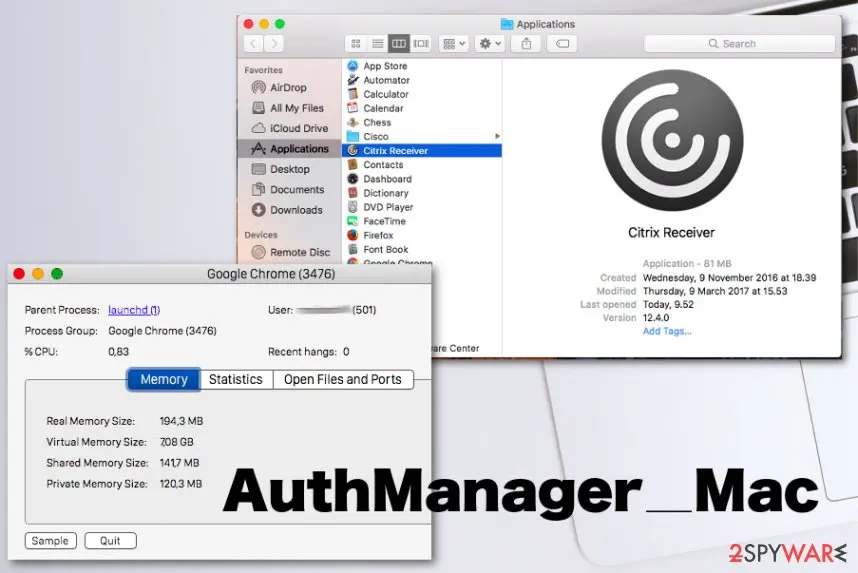
AuthManager_Mac is, in the reports we found, a helper program of Citrix, the remote-desktop software, not a virus. Our 2020 page already tied it to Citrix Receiver; what changed in 2021 is why macOS complains about it.
- 1
Citrix was installed once
Older Citrix Receiver builds for Mac put helper programs in
/usr/local/libexec:AuthManager_Mac.app,ReceiverHelper.appandServiceRecords.app. Each came with a startup file in/Library/LaunchAgents, for examplecom.citrix.AuthManager_Mac.plist. - 2
A startup file runs it at login
macOS reads those files at every login, whether or not you open Citrix. When the app is dragged to the Bin, the files can stay: one user's EtreCheck report shows
Executable not foundfor ServiceRecords beside a ReceiverHelper entry, so the startup file points at a program that is no longer there. - 3
Apple stopped trusting the signature
On 23 August 2021 Apple updated XProtect and its other Mac security systems to reject code signed with a certificate issued by Symantec. Citrix had used one. Malwarebytes' Thomas Reed wrote that the files themselves had not been changed, and named AuthManager_Mac among the affected Citrix programs.
- 4
Gatekeeper shows the alert
Gatekeeper, the check macOS runs before software starts, shows "will damage your computer". Apple says the message appears when macOS detects malicious content or the software's authorisation was revoked, so the wording alone cannot tell the two apart.
- Genuine file
/usr/local/libexec/AuthManager_Mac.app, a Citrix program- Startup entry
/Library/LaunchAgents/com.citrix.AuthManager_Mac.plist, the name our 2020 page gave- Travels with
ReceiverHelperandServiceRecords: same alert, same cause- First alerts we found
- 28 April 2020 on a Citrix forum; widespread from 23 August 2021
- Our 2020 page
- Published 4 March 2020, before the 2021 alert wave; it already called this a Citrix leftover
What we could and could not check
There is no website to test here, because AuthManager_Mac is a file, not a domain. We looked at one Mac with no Citrix on it. That cannot show what your file is, but it shows what a clean Mac looks like.
macOS 26.4.1 (Apple silicon) · 6 October 2026 · one Mac
- The folder
/usr/local/libexecdoes not exist here, so noAuthManager_Mac.appis in it. - Startup files
/Library/LaunchAgents,/Library/LaunchDaemonsand~/Library/LaunchAgentsheld no file withcitrixorauthmanagerin the name. - Apps and SpotlightNo Citrix app in
/Applications. A Spotlight search for the name found only our own old page pictures and research file, plus an unrelated payment-library source file withAuthManagerin its name. - Apple's definitionsXProtect version 5363, long past the 23 August 2021 update.
- Not testedA Mac that still has the Citrix files, the
spctlverdict on a real copy, a Mac with adware, other macOS versions. Nothing was run or installed.
Sources only for the affected case We could not run the affected case. What follows about the Citrix files comes from Malwarebytes, Apple, Citrix and users' own logs. It clears no file on your Mac, and it is one clean Mac, one visit.
Is AuthManager_Mac safe or a virus?
Our 2020 page said the file makes a Mac slow and could be tied to adware. The Citrix link holds up; the speed and spyware claims have no source we could find.
| Old claim | What we found | Verdict |
|---|---|---|
| It is part of Citrix Receiver | Malwarebytes names AuthManager_Mac as an affected Citrix program in /usr/local/libexec | Holds |
| It slows the Mac down | No source measures this. A helper that Gatekeeper rejects is not allowed to run, so the repeating alert is the documented effect | Not supported |
| It can mean a potentially unwanted program | Only when the file is not the Citrix one: a copy in Downloads, a random-named folder, or a changed browser | Possible, check the path |
| It tracks browsing, even with keyloggers | No source ties this name to tracking or keyloggers; that is the general risk of adware, not of this file | Not supported for this file |
| It is no virus | Malwarebytes: "this isn't malicious at all" | Holds for the Citrix file |
- Low
Old Citrix files
Not malware. The cost is a repeating alert at login and a few files in a folder where Mac software does not normally live.
- Medium
Something else with the same look
A changed search engine, ads on pages that had none, or a profile you did not install mean other software is present. Remove it whatever it is called.
- High
Clicking through the warning
Apple's page says to look for an updated version or another app. Open Anyway on a file you cannot place means running unknown code.
How to check the AuthManager_Mac file
Look before you delete. If the Mac belongs to your employer, stop after the second step and ask IT.
- 1
Find where the file sits
When the dialog has a Show in Finder button, press it. A file called
AuthManager_Mac.app,ReceiverHelper.apporServiceRecords.appinside/usr/local/libexecis the Citrix case. One inDownloads, in a folder of random letters, or tucked inside an app you never opened is not, and it stays suspect until you know where it came from. - 2
Work out if Citrix is yours
Does your job or school give you a Citrix desktop? If so, get the current version from the company portal or from Citrix itself, never from a pop-up or a page that found the problem for you.
- 3
Ask macOS what it thinks
In Terminal, run
codesign --verify --verbose /usr/local/libexec/AuthManager_Mac.app, thenspctl -a /usr/local/libexec/AuthManager_Mac.app. For the sister file ReceiverHelper, Malwarebytes gotvalid on diskandsatisfies its Designated Requirementfrom the first andrejectedfrom the second, which means intact but no longer trusted. Without the file we could not repeat this. - 4
Read the startup folder
Type
ls /Library/LaunchAgents | grep -i citrix. Entries beginningcom.citrix.mean Citrix was installed here once. A file with a random name in~/Library/LaunchAgentsfits the adware pattern instead. - 5
Compare your browser with what you chose
A search engine or start page you did not set, banners on sites that were clean before, or an entry under System Settings > General > Device Management that you never installed all point to the adware chapter.
Where AuthManager_Mac comes from
Two routes matter: an old install never cleaned up, and the installers adware uses. Our 2020 page said no Mac is immune; that part stands.
| Route | What it looks like | What helps |
|---|---|---|
| Work software left behind | A Citrix or similar remote-access client set up for a job, then dragged to the Bin. Its helper programs and startup files stay and run at every login. | Run the vendor's uninstaller, restart, then search LaunchAgents for the vendor's name. |
| Look-alike download pages | A page imitating a known software maker offers an app or an update. Adobe ended Flash support on 31 December 2020 and blocked Flash content from 12 January 2021, so a Flash update is always a trick. | Update through System Settings > General > Software Update or the app's own menu. |
| Cracked programs | Pirated apps from torrent sites, often repacked with extra components. | Pay for the program or use a free, legitimate one. |
| Bundled installers | A free utility brings an extension or search page along behind boxes already ticked. | Pick the custom or advanced install and untick the extras. |
| Scare ads | Banners claiming your Mac is infected or out of date. | Close the tab; a genuine warning does not come from a web page. |
What to do with AuthManager_Mac
How to check AuthManager_Mac
The genuine file is part of Windows and needs no removal.
These steps tell it apart from an impostor.
Step 1: Check the location and signature of AuthManager_Mac
Open Task Manager (Ctrl + Shift + Esc), right-click
AuthManager_Macon Processes and choose Open file location. The genuine file is in/usr/local/libexec/AuthManager_Mac.app; the same name anywhere else, especially in %AppData% or %Temp%, is an impostor to remove.Right-click the file > Properties > Digital Signatures to see who signed it. A genuine file needs nothing done, and ending it can make Windows 11 or Windows 10 unstable.
Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 2: Scan the PC, then run the offline scan
A scan finds the parts of AuthManager_Mac that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
If it is the old Citrix files
The first three steps follow Citrix's uninstall page and the fourth is Malwarebytes' last resort. None was run on an affected Mac by us.
- 1
Choose whether Citrix stays
Keep it on a work Mac and ask IT for the current Citrix Workspace app. On a personal Mac that no longer reaches a Citrix desktop, take it off.
- 2
Uninstall with Citrix's own method
Quit the app with Command-Q, drag Citrix Workspace (or the old Citrix Receiver) from Applications to the Bin and type your password. Citrix says this removes the app and its system files. The installer
.dmgalso holds Uninstall Citrix Workspace App, and Citrix documents one Terminal command:sudo /Library/Application\ Support/Citrix\ Receiver/Uninstall\ Citrix\ Workspace.app/Contents/MacOS/Uninstall\ Citrix\ Workspace --nogui. - 3
Restart and test
No alert after the restart means you are finished, and you can install the current Citrix if you still need it. If the alert is back, open
/Library/LaunchAgentsand look forcom.citrix.*.plist, for examplecom.citrix.AuthManager_Mac.plist; Citrix does not say its page covers files left by the old Receiver. - 4
Only then remove the leftovers
Malwarebytes says deleting AuthManager_Mac, ReceiverHelper and ServiceRecords from
/usr/local/libexecmay fix it, may break something because it is not a full uninstall, and is done at your own risk. Our 2020 page named the threecom.citrixstartup files for deletion too. A Citrix administrator suggestslaunchctl remove com.citrix.ReceiverHelperfirst; we have not tried it, or its AuthManager_Mac equivalent. Leave every name startingcom.apple.alone.
If it is adware: removal on a Mac
These steps are for a hijacker or adware, not for Citrix. They come from our 2020 guide, corrected for current menu names and for file locations a university IT page and SentinelOne document for Adload-type adware.
- 1
Stop what is running
Open Activity Monitor (in Applications > Utilities), pick the process you do not recognise, press the stop button at the top left and choose Force Quit. Note its name first: you will look for it on disk.
- 2
Bin the program
In the Applications folder, sort by Date Added. Anything you never installed, or that arrived just before the trouble began, goes to the Bin; then empty the Bin.
- 3
Clear login items and profiles
Open System Settings > General > Login Items & Extensions and remove items you do not know; switch off unknown entries under Allow in the Background. On macOS 12 and older the list is in System Preferences > Users & Groups > Login Items. Then look at General > Device Management: a profile you did not install can be selected and removed with the minus button.
- 4
Search the usual hiding places
In Finder choose Go > Go to Folder and type
~/Library/Application Support. The University of Illinois describes adware there as a folder of random digits and letters holdinghelperandpcyx.ver, and another startingorg.plus random characters withapp_assistantinside. Remove them, and the matching random-named.plistin~/Library/LaunchAgents. - 5
Repeat for the system-wide folders
Do the same in
/Library/Application Support,/Library/LaunchAgentsand/Library/LaunchDaemons, deleting only what belongs to the program you removed. SentinelOne also saw a scheduled job, so typecrontab -lin Terminal and look for a line that starts a file from Application Support. - 6
Restart and look twice
SentinelOne says several persistence methods can mean one pass is not enough. Restart, glance at Activity Monitor and the folders again, and repeat once.
| Browser | What to do |
|---|---|
| Chrome | Open the three-dot menu > Extensions > Manage extensions and Remove unknown ones. In Settings > Privacy and security > Delete browsing data tick history, cookies and cached files. If the settings keep reverting use Settings > Reset settings > Restore settings to their original defaults; bookmarks are kept. |
| Firefox | Go to Add-ons and themes > Extensions and remove what you did not add. If the start page keeps coming back choose Help > More troubleshooting information > Refresh Firefox. |
| Safari | See the Safari tab of the removal chapter; current Safari has no Reset button. |
After the check: keep Windows clean
No device is out of reach of malware, but a few habits stop both leftovers and adware. Our 2020 page said there is nothing you can do about it; that was wrong.
Do
- When a job or course ends, run the vendor's own uninstaller for its remote-access software and restart afterwards.
- Get apps from the App Store or the developer's own site; at each installer step pick the custom option to see what else comes along.
- Install every macOS update, since Apple ships XProtect definitions that way.
- Keep a Time Machine copy on a drive that is unplugged when not in use.
- A VPN from its maker's site hides your address; it neither removes adware nor repairs a signature alert.
Don't
- Do not run cracked programs or tools pushed by banners and pages imitating real software vendors.
- Do not believe a pop-up that says your Mac needs Flash or a browser update.
- Do not press Open Anyway on a file whose origin you cannot name.
- Do not install a configuration profile offered by a web page unless your employer or school requested it.
Questions about AuthManager_Mac
Is AuthManager_Mac a virus?
No, not in the reports we found. Malwarebytes' Mac expert Thomas Reed wrote in August 2021 that AuthManager_Mac, ReceiverHelper and ServiceRecords are components of Citrix, and that macOS began flagging them after Apple stopped trusting the certificate that signed them. The files themselves had not changed.
A copy outside Citrix's usual folder is a different matter, so check the path, whether you ever used Citrix, and whether your browser settings changed before you decide. If you are unsure, ask the person who set up your Mac for work, or search the Citrix and Apple forums with the exact wording of your alert.
What is AuthManager_Mac and where is it?
It is a helper program of the Citrix Receiver and Workspace app for Mac. Malwarebytes places the affected Citrix apps in /usr/local/libexec/, and our 2020 page named a startup file com.citrix.AuthManager_Mac.plist in the LaunchAgent folders.
ReceiverHelper and ServiceRecords sit beside it and trigger the same alert. Malwarebytes noted that this folder is not where Mac software normally lives. If your copy is in Downloads or a folder of random characters, it is not the Citrix file.
Do not follow instructions from sites that label the name a virus and sell a cleaner: Malwarebytes warned that such results for these names are automatically generated pages promoting junk software.
Why does my Mac say AuthManager_Mac will damage your computer?
Apple says macOS shows this when it detects malicious content or when the software's authorisation has been revoked. The reported cause here is the second: on 23 August 2021 Apple began rejecting code signed with a Symantec-issued certificate, which Citrix had used.
Newer Macs may word the alert differently, for example that the file contains malware, and we could not confirm the cause is still the same on every version, so check the path before trusting either reading.
The alert tells you that macOS no longer trusts the file, not that the file did anything, so nothing in it suggests your data was taken.
How do I remove AuthManager_Mac from my Mac?
First decide whether you still need Citrix. If you do, update to the current Citrix Workspace app. If not, quit it, drag it from Applications to the Bin, enter your password, restart and see whether the alert is gone.
Citrix's page does not say its uninstaller clears leftovers from the old Receiver, so check /Library/LaunchAgents for com.citrix files. If instead your browser was hijacked, use the adware steps on this page. A Terminal command is not needed for the first three steps; they use the Finder and Citrix's own uninstaller.
Can I delete AuthManager_Mac, ReceiverHelper and ServiceRecords?
If you do not use Citrix, yes, and nothing else on the Mac should depend on them. Malwarebytes cautions that deleting only these files is not a complete uninstall and may cause other problems, so treat it as a last resort.
On a Mac your employer manages, leave them and ask IT, because a management profile can put them back. Never delete files whose names begin with com.apple., whatever an alert says. If an alert names a file that is not in /usr/local/libexec, stop and check where it is before you remove anything.
Does AuthManager_Mac slow down my Mac?
We found no source that says so. Our 2020 page claimed it, but a helper that Gatekeeper rejects is not allowed to run, and the documented effect is the repeating alert. If your Mac is slow, open Activity Monitor, sort by % CPU and by Memory, and see which process is busy; that is more reliable than blaming a leftover file.
A slow Mac with a changed search engine or unknown profiles points to adware instead. Whichever cause you find, the fix for a signature alert is to remove or update the owner software, not to hide the dialog.
Will an antivirus scan find AuthManager_Mac?
Not in the Citrix case, because it is not malware: Malwarebytes said of these files, "that's not what this is".
In the adware case a scan can help, but Adload-type adware is built to avoid static detection: SentinelOne showed Apple's own rule missing new builds, and a University of Illinois page says Mac antivirus did not reliably detect the variant it saw.
A clean scan therefore does not clear a Mac with a changed search engine or unknown profiles. It also helps to check the scan's detection name against the vendor's own page rather than a third-party cleaner site.
Does AuthManager_Mac track me or log keystrokes?
We found no source that says so about this name. Our 2020 page described tracking with cookies and, in the worst case, keystroke loggers; those are risks of adware in general, not documented behaviour of this Citrix file.
If you see ads, redirects or profiles you did not add, treat that as a separate problem, remove the software behind it, and change passwords from a device you trust if you entered them while it was active. Since our page gave no sign of such behaviour, we leave the claim out of the summary table on purpose.
Will AuthManager_Mac come back after I delete it?
It can. If it is the Citrix helper, its startup file keeps trying to start it, and a managed Mac may have it reinstalled by a profile or by an old installer in Downloads.
If it is adware, SentinelOne found several persistence methods in Adload-type malware, a launch agent, two launch daemons and a scheduled job, so removing one can leave another that rewrites the files.
Restart, recheck the startup folders and repeat the steps once before calling it clean. If the alert comes back after a restart, something is still starting the file at login.
Will Fortect remove AuthManager_Mac?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For AuthManager_Mac, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Malwarebytes Labs: Macs turn on apps signed by Symantec, treat them as malware (31 August 2021) (read October 6, 2026)
- Apple Support: Safely open apps on your Mac (read October 6, 2026)
- Apple Platform Security: Protecting against malware in macOS (read October 6, 2026)
- Citrix Docs: Install, uninstall, and upgrade (Citrix Workspace app for Mac) (read October 6, 2026)
- Citrix Community: Software will damage your computer??? (28 April 2020) (read October 6, 2026)
- Apple Community (German): ServiceRecords.app beschädigt deinen Computer (26 August 2021) (read October 6, 2026)
- SentinelOne Labs: How AdLoad macOS malware continues to adapt and evade (read October 6, 2026)
- Microsoft Security Intelligence: Adware:MacOS/Adload.A (read October 6, 2026)
- University of Illinois Technology Services: Removing Adload macOS spam malware (read October 6, 2026)
- Adobe: Flash Player end of life (read October 6, 2026)
- Reddit r/Citrix: removing Citrix Workspace helper and service records (read October 6, 2026)
- Mac-Forums: MacBook Pro keeps crashing (EtreCheck listing of com.citrix.ReceiverHelper.plist) (read October 6, 2026)