
Critical System Failure" virus: what it is and how to remove it
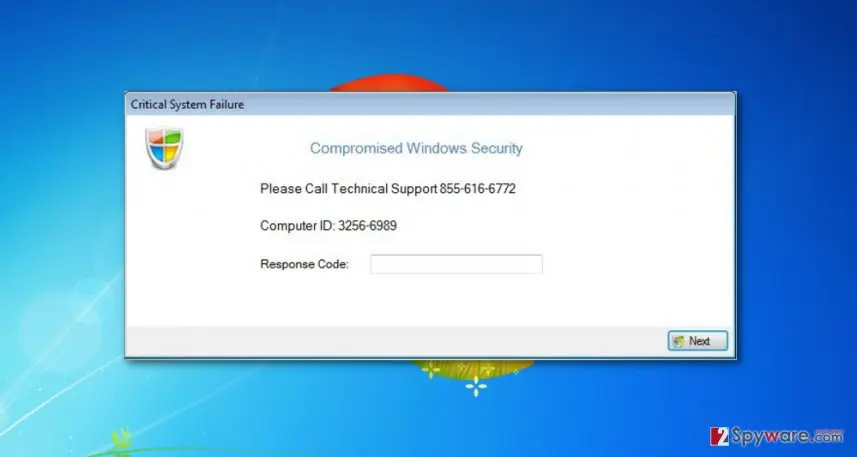
If you just got an alert message on your computer screen, stating that your Windows Security has been compromised, and if the pop-up title says "Critical System Failure," then your computer has been infected by Critical System Failure virus. This virus belongs to Tech Support Scam family, and it is meant to display deceptive and scary warnings on the PC screen.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Programs like Critical System Failure" virus usually arrive in groups; a free scan lists the companions that are easy to miss.
Do it yourself · free Remove Critical System Failure" virus yourself 5 steps, about 15 minutes, no software needed.
Start the steps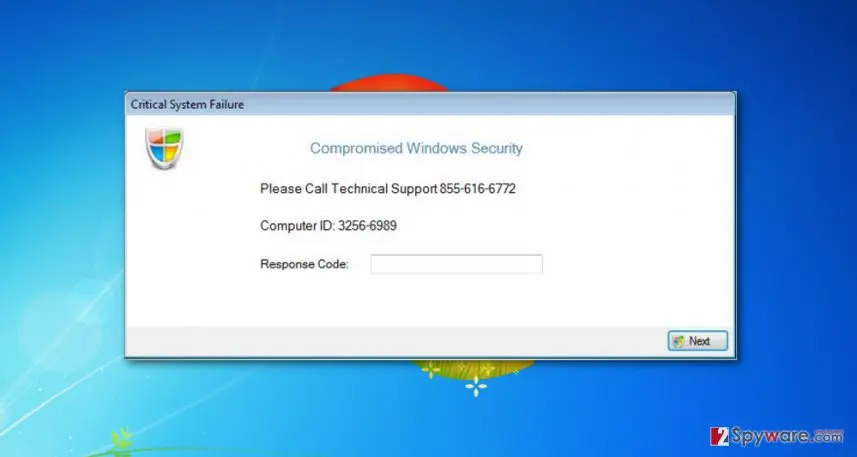
Critical System Failure" virus: summary
| Detection names | No Microsoft detection name is known |
|---|---|
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Name | Critical System Failure" virus |
| Type | Loader |
| Symptoms | An unknown program in Installed apps |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 3 more facts
| Evidence | One write-up by a security site; details still limited |
|---|---|
| First seen | 21 September 2016 |
| Facts checked | 7 October 2026 |
What Critical System Failure" virus does on an infected PC
From our report of Sep 2016 · not reviewed since
"Critical System Failure" virus - what should you do about it?
If you just got an alert message on your computer screen, stating that your Windows Security has been compromised, and if the pop-up title says "Critical System Failure," then your computer has been infected by Critical System Failure virus.
This virus belongs to Tech Support Scam family, and it is meant to display deceptive and scary warnings on the PC screen. There are many similar viruses created already, such as Fake Windows Activation screen, Productkeyupdate, or "Call certified Microsoft technicians" virus. Typically, scammers seek to achieve at least one of these goals:
Computer users are advised to ignore such phony alerts and take measures to remove "Critical System Failure" malware from the compromised computer. Luckily, there is a way to block these pop-ups and eliminate the virus from the system without even using a malware removal tool - just enter 642358497351 into the "Response code" box and click Next. That should close the pop-up and remove malware from the computer.
If this does not work, it means that you are infected with an updated version of this malware, and it means that using a malware removal tool is the best option to get rid of it. We strongly recommend using or software. You can find comprehensive instructions on how to start "Critical System Failure" removal procedure below this post.
- Talk the victim into buying useless and possibly insecure software;
- Gain remote access to the computer;
- Convince the victim to reveal personal data, such as bank card details.
How Critical System Failure" virus got on your PC
From our report of Sep 2016 · not reviewed since
Tech support scammers get surprisingly creative when it comes to distribution of such malicious programs.
They seek to integrate their programs into computer systems silently and without causing suspicion to actually make users believe that the computer has been compromised somehow and needs to be fixed immediately. Sadly, unskillful computer users can easily fall for such deceptive messages and call tech support scammers.
What is even worse, they might believe what these scammers say and do as they command. We would like to say that all computer users should consider annoying pop-up messages or web pages suspicious if they urge the victim to get in touch with tech support team ASAP.
To avoid installing such deceptive Trojans, users should pay more attention to programs they install and how they install them. We advise users to opt for Custom/Advanced settings when installing new programs rather than leaving Default/Standard mode on. Advanced or Custom settings provide the possibility to see all attached downloads and detach them by removing check marks next to them.
What is more, users should stay away from offers to install fake Java updates. These can be encountered while visiting untrustworthy third-party pages, gambling or adult-oriented sites. Such bogus software updates frequently contain hidden files that appear to be malicious. Do not be tricked into installing them unknowingly!
How to remove Critical System Failure" virus
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to Critical System Failure" virus or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 2: Remove it from startup
Whatever Critical System Failure" virus installed usually starts with Windows.
Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
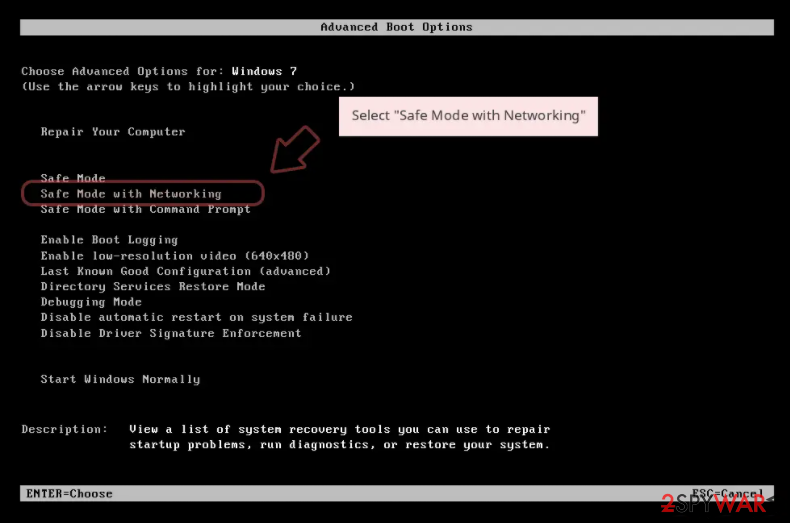
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
Windows 10 / Windows 8
- Right-click on Start button and select Settings.
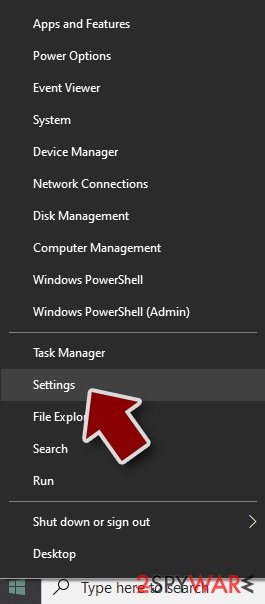
- Scroll down to pick Update & Security.
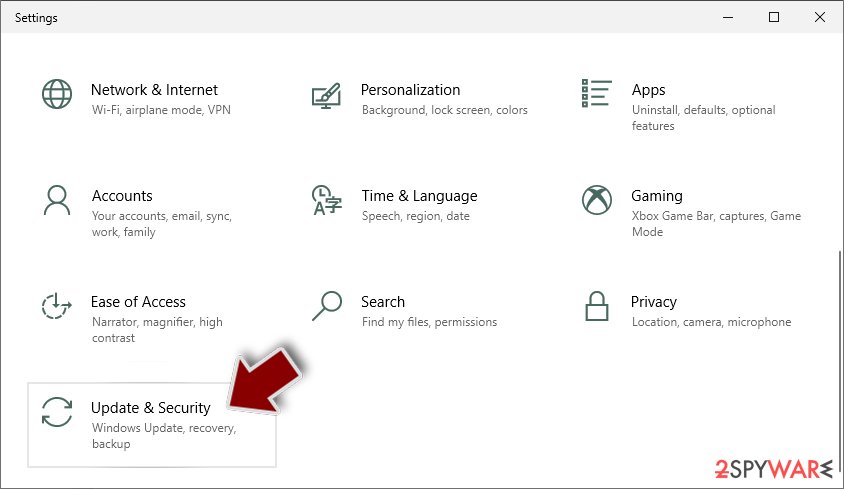
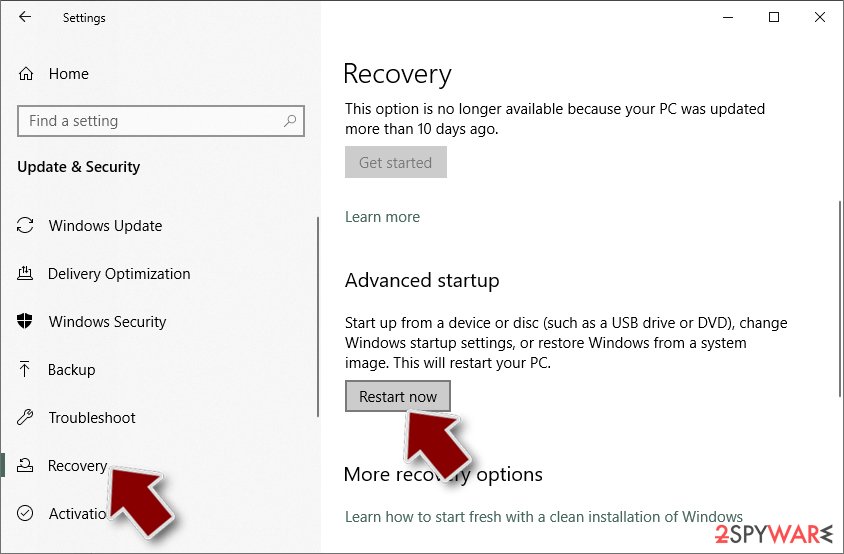
- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.
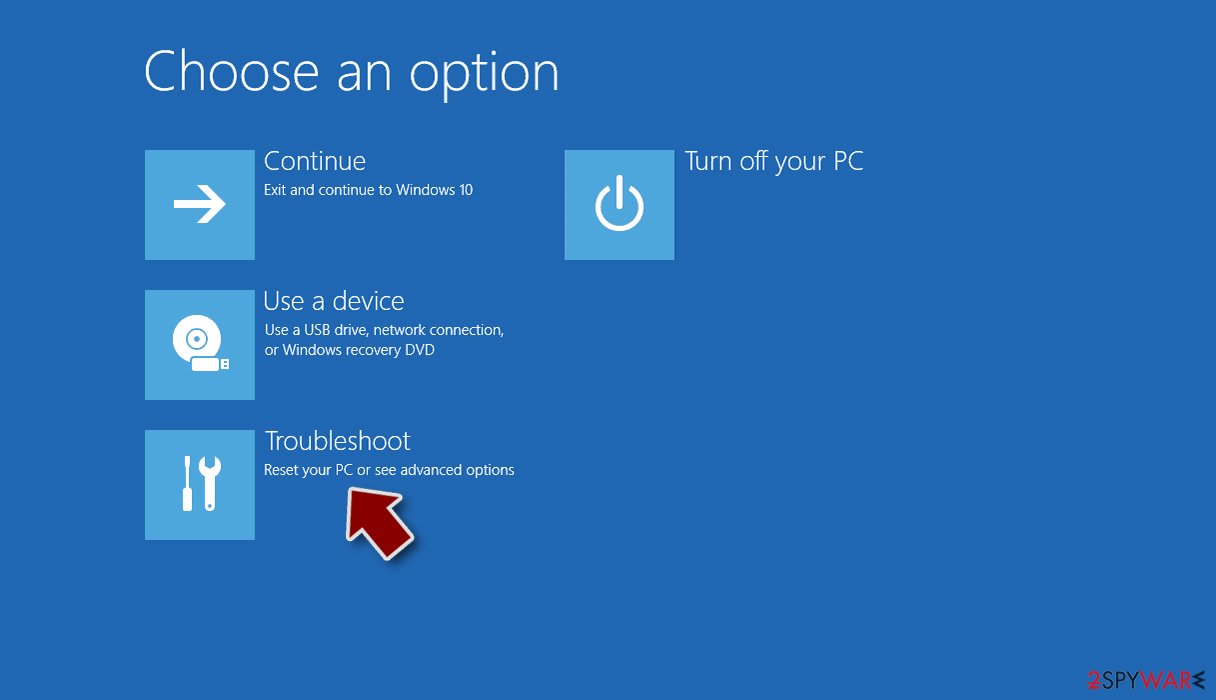
- Select Troubleshoot.
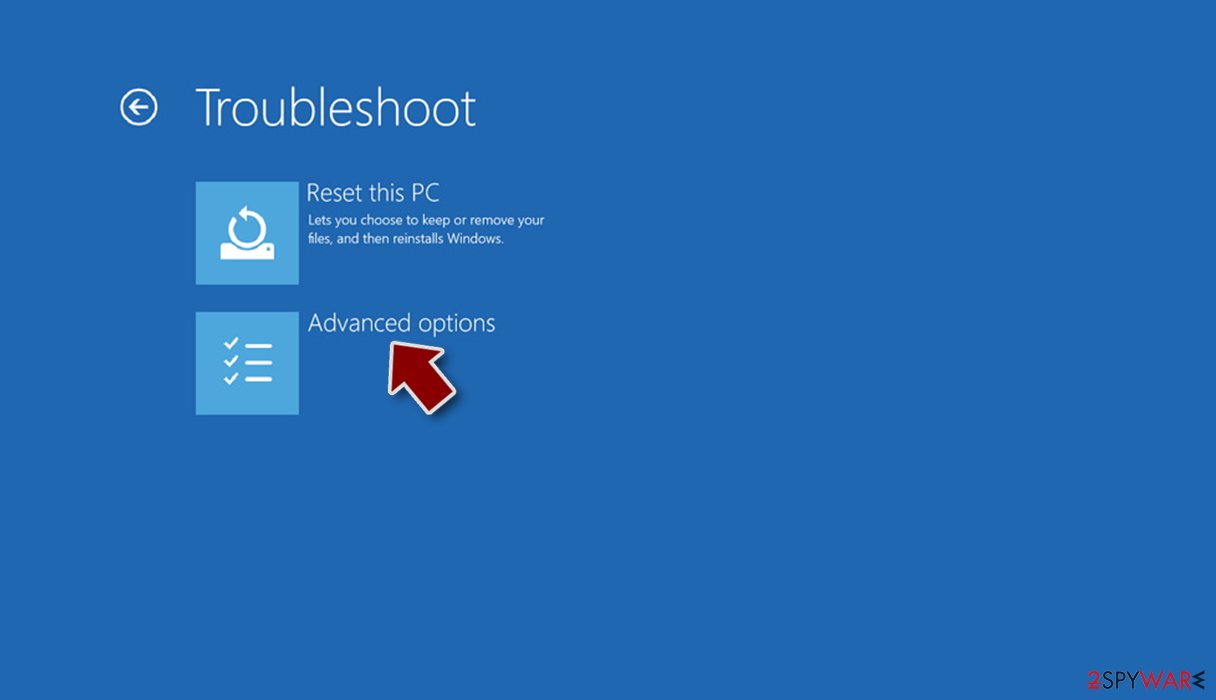
- Go to Advanced options.
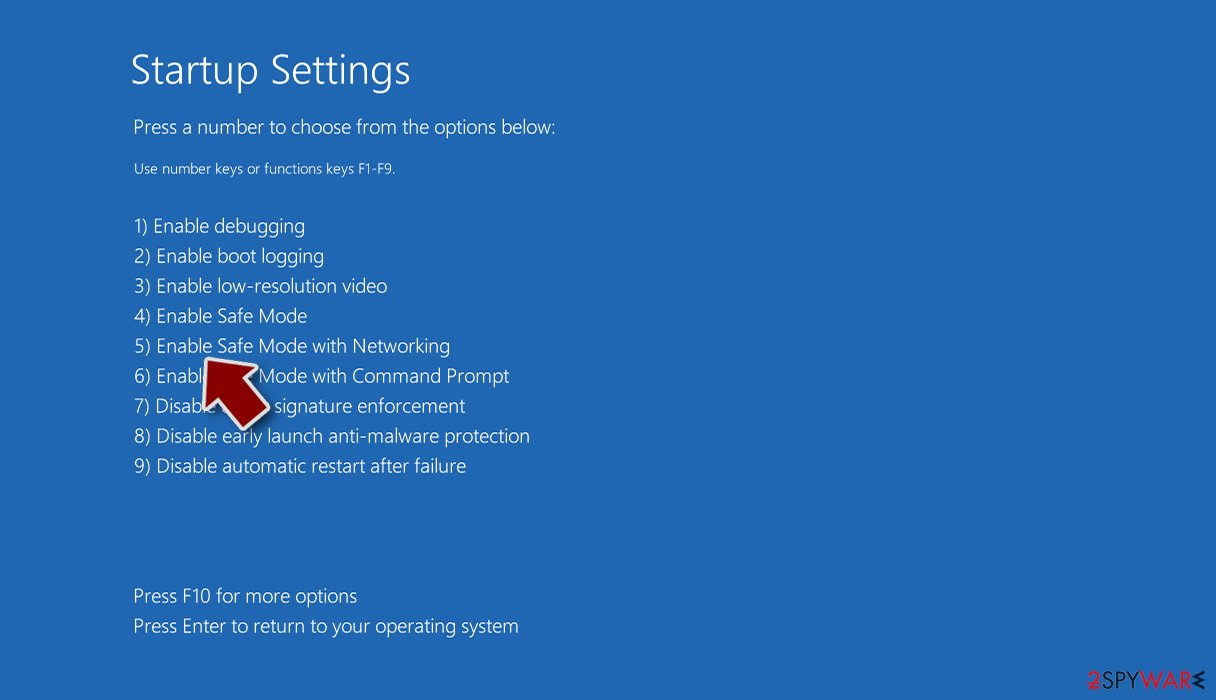
- Select Startup Settings.
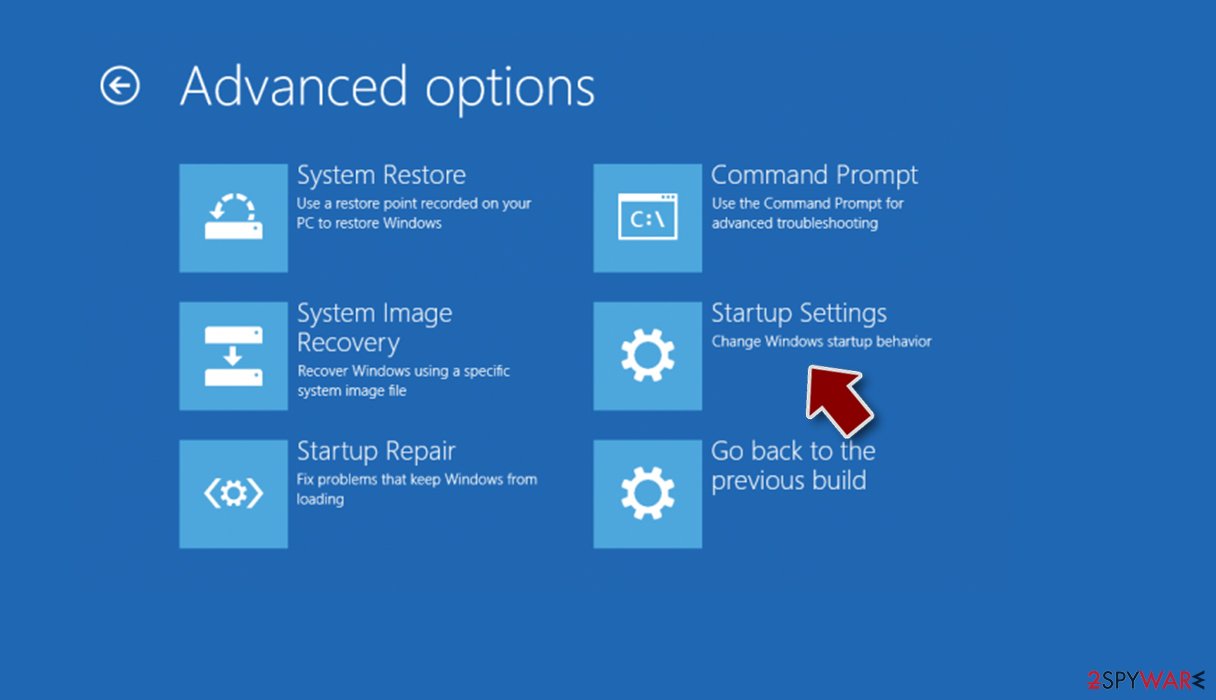
- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.
Step 2. Shut down suspicious processes
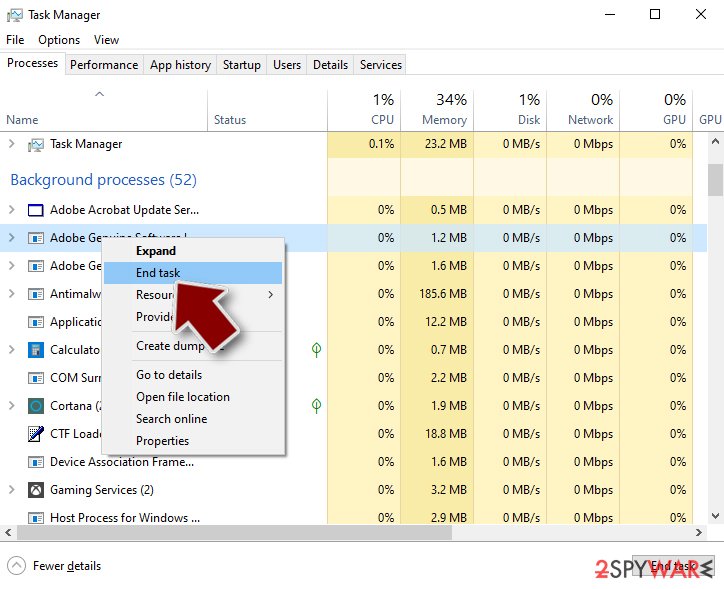
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
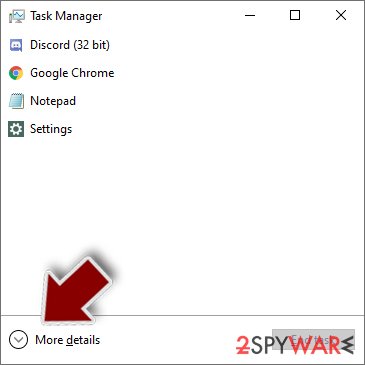
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.
- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.
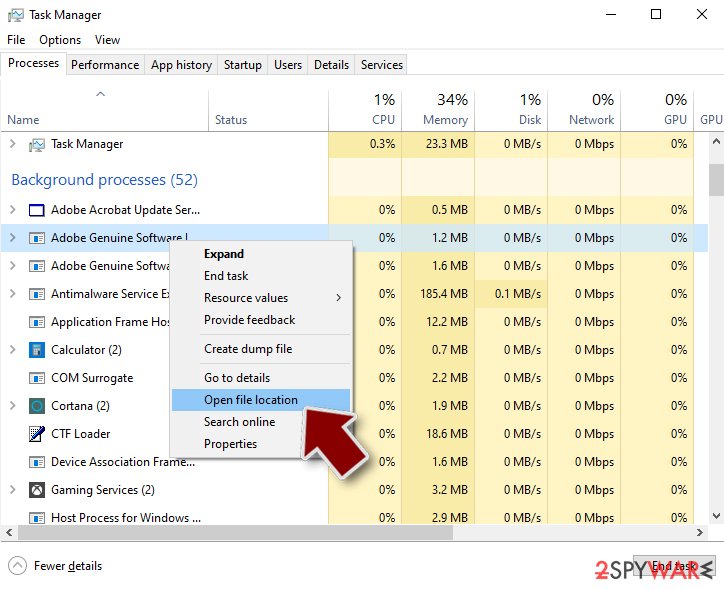
- Go back to the process, right-click and pick End Task.
- Delete the contents of the malicious folder.
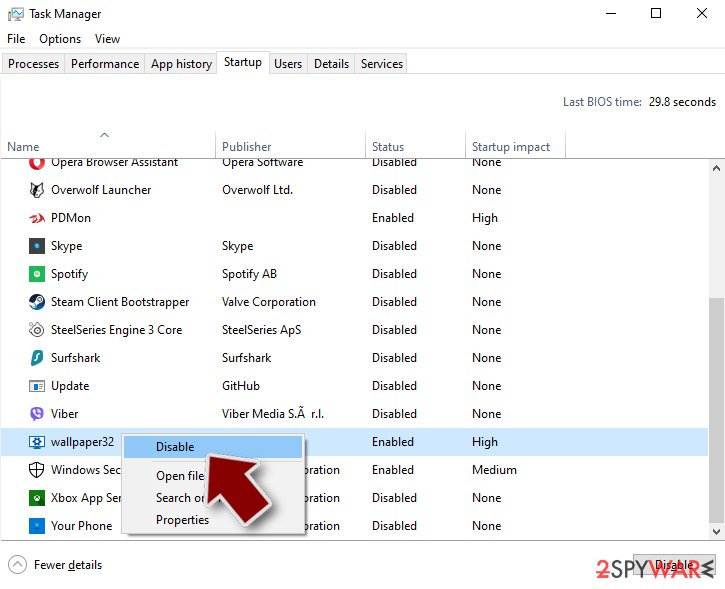
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.
Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
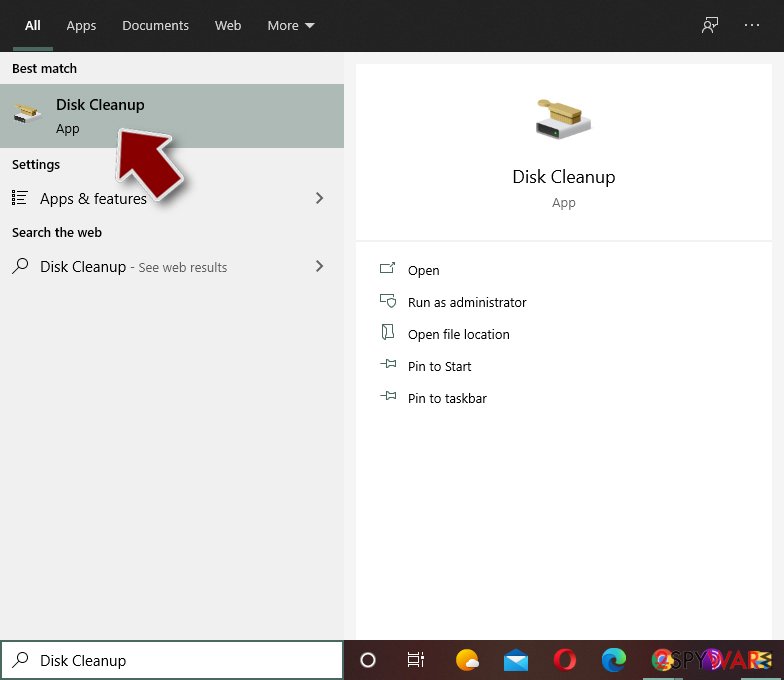
- Type in Disk Cleanup in Windows search and press Enter.
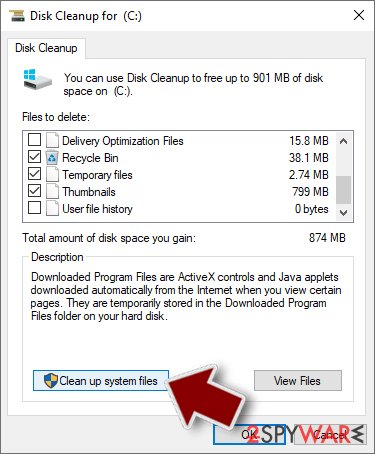
- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.
- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Sep 2016 · not reviewed since
How to remove Critical System Failure malware?
You must remove Critical System Failure virus if you do not want to see these lying messages anymore and, of course, if you wish to protect your system.
We strongly advise you to check the entire system for its components and delete all suspicious files at once. Now, this can be a hard task to do, unless you are a professional at programming and can identify malicious files.
Otherwise, we do not recommend you to play around with random files and delete the ones that you consider untrustworthy. You might end up deleting essential and necessary files instead of dangerous ones. Therefore, you should go for automatic Critical System Failure removal option and remove it by using one of the following programs:
[GI=method-1]Enter this code in the "Response Code" field - 642358497351 . This should close the pop-up and uninstall the malware.
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed critical System Failure" virus in the list of installed apps, a sign of a program that could read browser data, the clean-up is only half of the work. The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
Questions about Critical System Failure" virus
Is Critical System Failure" virus a virus?
Most programs that appear the way Critical System Failure" virus did are not viruses in the strict sense. They are potentially unwanted programs:
- real software that arrives bundled with other downloads and then shows offers
- changes browser settings
- starts with Windows
Some are harmless, some are annoying and a few carry adware. What makes it worth removing is that you did not choose it.
Uninstall it from Installed apps and check the startup list and the browsers for anything added the same day. If it refuses to uninstall or returns after a restart, treat it as more serious and run a Microsoft Defender offline scan.
How do I stop programs like Critical System Failure" virus from being installed again?
Most unwanted programs arrive through installers, so the fix is in how you install software. Download programs from their official sites or the Microsoft Store, not from download portals or ads above search results. During setup, choose Custom or Advanced installation and untick every extra offer, including browsers, toolbars and optimizers.
Decline update prompts that appear inside other programs unless you know them. In Windows Security, turn on reputation-based protection and potentially unwanted app blocking. These steps would most likely have stopped Critical System Failure" virus before it reached the app list.
Which malware family is Critical System Failure" virus?
That is not known yet. Critical System Failure" virus has been reported by people who saw critical System Failure" virus in the list of installed apps, but no sample has been analysed publicly, so security companies have not assigned it to a family.
The name you see may be a file or program name chosen by the authors, not a family name. This does not stop you from removing it: the startup points, the offline scan and the account steps are the same for most families of this type.
If Microsoft Defender or another scanner gives the file a detection name, write it down; that name is the best clue to the family and is useful when you report the incident.
Can Critical System Failure" virus spread to other devices on my network?
Most trojans aimed at home users stay on the PC they infected, but an attacker with remote access can look at the network, open shared folders and try passwords on other devices. Loaders sometimes deliver worms or ransomware that do spread.
Disconnect the PC while cleaning, run a full scan on other Windows PCs, change the router's admin password and the Wi-Fi password if they were saved on the infected PC, and update the router's firmware. If other PCs show the same detection, treat them as infected too.
Should I reset my PC because of Critical System Failure" virus?
Only if the signs point to deeper access. Reset when you see critical System Failure" virus in the list of installed apps again after removal, when Windows Security cannot start or update, when remote access tools you did not install keep appearing, or when you simply cannot trust the PC any more.
Otherwise, the plan in this guide plus an offline scan is enough. If you do reset, choose Remove everything and Cloud download for a fresh copy of Windows, restore only documents and photos, and reinstall programs from their official sites. Change important passwords from the clean system afterwards.
What are the signs of a trojan infection?
Most trojans try to leave no visible signs, so look for side effects. Common ones:
- Windows Security turned off or unable to update
- new entries in Startup apps or Task Scheduler
- programs in Installed apps you did not install
- browser settings that changed by themselves
- unusual network activity while the PC is idle
- password-reset or login-alert e-mails you did not trigger
None of these proves an infection on its own. Together with an antivirus alert naming Critical System Failure" virus, they are a strong reason to follow the full plan.
Can a normal remote support program be a backdoor?
Yes. Tools such as AnyDesk, TeamViewer and ScreenConnect are legitimate, but whoever controls the account behind them controls the PC. Scammers install them during fake support calls, and some trojan campaigns install them silently because antivirus programs do not flag a genuine, signed product.
If you find one you did not set up, uninstall it, check Startup apps for related entries and change passwords from another device. If money or accounts were involved, call your bank and report the incident.
Why didn't my antivirus stop Critical System Failure" virus?
New trojan builds are packed and changed often so that signatures do not match, and some are signed with stolen or bought certificates. Many arrive inside password-protected archives, which scanners cannot open until you extract them.
Some downloads also tell the user to turn off the antivirus "because it gives false alarms", a common line in cracked software instructions. Keep real-time protection on, never disable it for an installer, and run the offline scan whenever you suspect something slipped through.
Is a trojan infection worth reporting to the police?
If there was harm, yes. Unauthorised payments, accounts used for fraud, blackmail or a remote session during a scam call all belong in a report, and banks often ask for its reference number before they refund anything.
If antivirus caught Critical System Failure" virus before it ran and nothing was misused, there is nothing to report. Keep the evidence anyway:
- protection history
- the original download
- the dates
Businesses may also have to notify a data protection authority if personal data could have been accessed.
Will Fortect remove Critical System Failure" virus?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Critical System Failure" virus, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- FTC: How to recognize, remove and avoid malware (read October 7, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 7, 2026)
- Microsoft Learn: How Microsoft names malware (read October 7, 2026)