
DanaBot: what it is and how to remove it
DanaBot - malware that spreads using spam email campaigns and malicious file attachments. Creators put malware scripts into the MS Office documents and send thousands of questionable emails to users.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
An automatic scan checks installed programs, startup items and browser extensions for anything that came with DanaBot.
Do it yourself · free Remove DanaBot yourself 5 steps, about 15 minutes, no software needed.
Start the steps
DanaBot: summary
| Distribution | Email attachments with malicious macros and scripts, websites with direct malware download functions provide the stealthy infiltration opportunities for the malware creators |
|---|---|
| Name | DanaBot |
| Type | Trojan |
| Targets | Australia and Europe are the most known targets where various info-stealing malware campaigns affected large businesses and companies |
| Tactics | Stealthy infiltration allows the malware to infect machines. Social engineering,[3] phishing emails and other methods allow the trojan to achieve these goals |
| Danger | The virus is capable of stealing sensitive information and making fraudulent transactions when online banking platform credentials get stolen |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Damage | Not recorded in the old report |
| Symptoms | An unknown program in Installed apps |
| Evidence | 5 write-ups by security sites; details still limited |
| First seen | 18 May 2020 |
| Facts checked | 7 October 2026 |
What DanaBot does on an infected PC
From our report of May 2020 · not reviewed since
DanaBot trojan gathers sensitive information from the infiltrated system and includes ransomware-type virus features
DanaBot - malware that spreads using spam email campaigns and malicious file attachments.
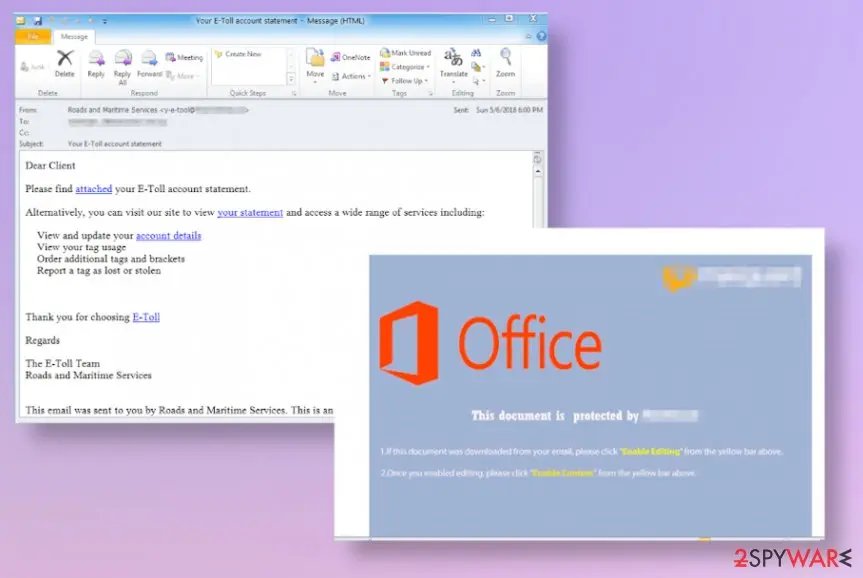
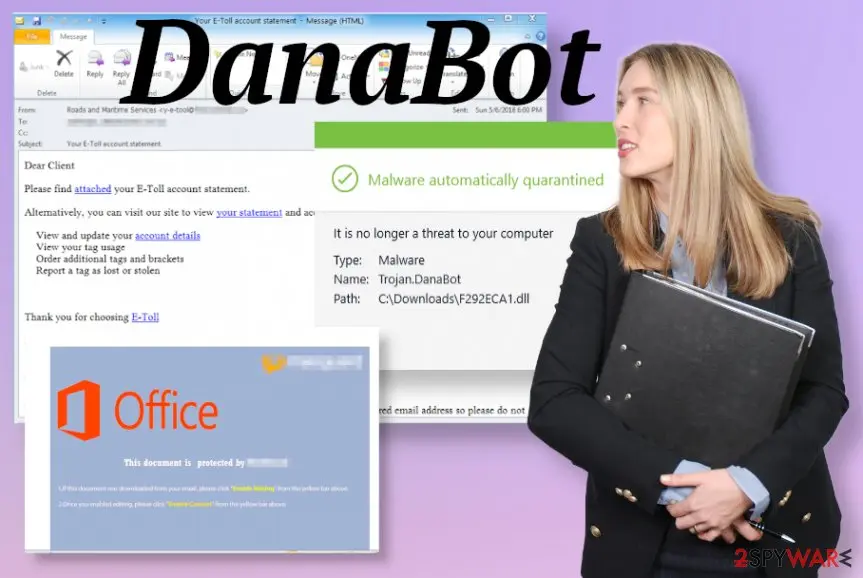
Creators put malware scripts into the MS Office documents and send thousands of questionable emails to users. When any gullible user receives the notification and goes through downloading and opening the file triggers the launch of the trojan virus. There is not much that the user needs to do because malicious scripts get enabled by pressing one button on the document when it is opened on the computer directly.
DanaBot Trojan started as a typical banking trojan and traveled through users' devices gathering sensitive data, planting other threats, and damaging machines. Later on, in 2019 the threat was upgraded and became a powerful threat that targets companies all over the world.
First targets were Australia, and some countries in Europe and malware evolved to modular malware that can download and launch DLL files, inject scripts on banking sites and steal information from various sites and the infected computer.
It is known that the DanaBot virus can manipulate browser sessions and redirect visits to financial services and steal credentials when users submit them to log in. Malware is capable of taking screenshots of the desktop, transfer all the stolen data to the C&C server that hackers control, and use such details to make fraudulent transactions, and steal money from banking accounts directly.
DanaBot trojan started with attacks targeting Australian banks, and other hackers managed to get the malware as a part of the affiliate system. When malicious actors use, rent or purchase the trojan they share profits with developers, and a team that created trojan in the first place can make a profit no matter what.
DanaBot trojan is compared to Zeus virus because it has many functions as a banking trojan and downloader components, including web injects that the Zeus is known for.
It gets upgrades and is used for different purposes since the malware can be used as a tool of exfiltrating data. It is often using browsers and OS fingerprinting to deliver the fake website copies in the place of legitimate banking domains or e-commerce services.
It even masks C2 communications and requests updates by relying on the Tor module. DanaBot virus can target larger businesses and reduce the number of attacks while focusing on quality and choose to profile the victims' worth before running the malware. This is how attackers ensure to make more profit.
DanaBot malware upgrades revealed that threat included some capabilities besides those info-stealing functions:
It also involved in ransomware-type campaigns when DanaBot encrypted files. Non-ransomware appended files using .non and .bkc extensions before dropping the HowToBackFiles.txt file containing the message for victims. At the time, this functionality was associated with Blitzkrieg ransomware activities.
When this not ransomware function affected files, DanaBot virus added files in system folders could trigger various processes. Malware can disable disk restoration, services, programs, monitoring software, and Windows Defender or other AV tools.
Trojan can delete shadow copies and clear EventLog or different folders and directories. Ransomware can be designed to revive itself after the killing by adding the scheduled task using the modified Schtasks tool. At the time researchers explained:
DanaBot ransomware has a tool that can be launched as a decryptor that you can find here.
DanaBot is the banking trojan that actively gets updates and techniques targeted towards avoiding the detection and maintaining continuous operations. Attackers aim for financial gain, so financial rewards can be ensured when all the functions run uninterrupted. New tactics and operations can emerge, and since targets mainly are financial institutions and e-commerce, streaming services there are many places where the threat can spread and act further.
DanaBot malware is linked with other threats, and the relations were confirmed in the past, so same injection patterns and progression can show that this trojan will continue to be one of the most dangerous banking trojans in the future. Organizations should be aware of potential targeting and keep these malware campaigns in mind.
To avoid DanaBot removal, organizations can implement fraud detections within their web platforms. Detecting banking trojans and blocking fraudulent transactions can combat phishing attacks ant these fraud tactics that result in losses of money and sensitive data.
As for users that needed to remove DanaBot and fight malware on the machine, changing email addresses, logins and usernames on other platforms could be a great step once the system is cleared. Intrusion detection systems, anti-malware tools, and other antivirus programs are the best for the initial virus termination.
However, there are still issues with virus damage that is leftover after the DanaBot trojan attack. Affected system functions, damaged files or folders, and entries in places like Windows registries can create issues after the malware is terminated.
Such alterations often happen to trigger detection avoidance and persistence of the threat, especially when it comes to ransomware-type viruses. Get a proper tool like for PC repair purposes and system optimization to find and fix issues with damage and changed settings.
- stealing browser client credentials;
- collecting logins to crypto wallet services;
- running a proxy on the infected machine;
- web injects;
- requesting updates via the Tor browser.
From our report of May 2020 · not reviewed since
DanaBot trojan termination tips and precautionary measures listed
Since the DanaBot virus can run in the background unnoticed and unexpected it is more dangerous than any other threat.
There are many functions in addition to banking trojan and password-stealing features, so full system cleaning is the only solution when dealing with this threat. Do not forget that even though these malware campaigns more targeted towards businesses, everyday users can also receive malicious emails with the trojan payload.
To avoid DanaBot removal in the future, you should have security or optimization tools like on the machine and run them more often, so all the issues, alterations, and damage can get fixed in time. This way there are no flaws in the system that attackers could exploit and spread their products.
When the process of DanaBot removal is inevitable, rely on proper tools, official providers, and sources that distribute , , or any other reliable anti-malware tool. These programs can check various parts where the attackers planted their malicious scripts. In addition to the software, you can reboot the machine in Safe Mode with Networking, so the functions that get disabled can freely run, and your AV tool is not blocked.
[GI=method-1]When a threat is affecting the performance and disabling some functions, rebooting the PC in Safe Mode with Networking can help with DanaBot removal
[GI=method-2]System Restore is the function that can give the opportunity of recovering machine in a previous state when the trojan was not active
From our report of May 2020 · not reviewed since
More from our earlier report on DanaBot
- DanaBot removal requires proper tools because not all files and programs associated with the trojan can be found or seen, so anti-malware tools can detect and clear all the malware traces automatically
- Some settings and features of the infected machine can get affected by the threat.
- Especially when system files and folders get affected and corrupted, so run for the best virus damage fixing results
- The ransomware enumerates logical drives, visits all the directories except Windows, and encrypts all the files using AES128.
- The password is a string representation of the system volume serial number.
- Every file is encrypted in a separate thread.
How DanaBot got on your PC
From our report of May 2020 · not reviewed since
Email campaigns circulate on the internet with subject lines claiming about invoices, e-tools, order information, and other details that help trick people into opening notifications and download malicious files without batting an eye. Microsoft Word attachments include macro viruses that get enabled by few clicks on the screen and triggers PowerShell or different functions to load malware payload directly on the system.
Then malware triggers all the processes, manipulates browser sessions, pulls other modules and inject sites, steals information without any symptoms created. The infection can be avoided, but not easily noticed if you do not pay attention to the email, sender, and topics of these emails.
When you notice any suspicious emails that you were not expecting to receive and notifications include file attachments or links you need to pay attention to other details because any red flag can indicate malicious behavior and purposes of the email, files included on it.
Delete any suspicious messages and do not open files that you are not sure about. Financial-themed emails are not coming randomly from services and platforms, so do not fall for such tricks.
How to remove DanaBot
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Programs like DanaBot add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 2: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after DanaBot, its publisher or created on the day the problem started. Delete those folders, and check C:\Program Files and C:\Program Files (x86) too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
A scan finds the parts of DanaBot that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
DanaBot can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed danaBot in the list of installed apps, a sign of a program that could read browser data, the clean-up is only half of the work.
The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
Protect your privacy - employ a VPN
There are several ways how to make your online time more private - you can access an incognito tab.
However, there is no secret that even in this mode, you are tracked for advertising purposes. There is a way to add an extra layer of protection and create a completely anonymous web browsing practice with the help of VPN. This software reroutes traffic through different servers, thus leaving your IP address and geolocation in disguise.
Besides, it is based on a strict no-log policy, meaning that no data will be recorded, leaked, and available for both first and third parties. The combination of a secure web browser and VPN will let you browse the Internet without a feeling of being spied or targeted by criminals.
No backups? No problem. Use a data recovery tool
If you wonder how data loss can occur, you should not look any further for answers - human errors, malware attacks, hardware failures, power cuts, natural disasters, or even simple negligence.
In some cases, lost files are extremely important, and many straight out panic when such an unfortunate course of events happen. Due to this, you should always ensure that you prepare proper data backups on a regular basis.
If you were caught by surprise and did not have any backups to restore your files from, not everything is lost. is one of the leading file recovery solutions you can find on the market - it is likely to restore even lost emails or data located on an external device.
Questions about DanaBot
What is DanaBot and why is it on my PC?
DanaBot is a program that was installed on the PC, most likely together with something else you downloaded. Free software sites and many installers add extra programs on setup pages with pre-ticked boxes, so the extra install looks like your choice even though nobody read the page.
Check the install date in Settings, Apps, Installed apps: the program you installed that day is the probable carrier. If you do not need DanaBot, uninstall it. If it belongs to your hardware or to a program you use, search its exact name and publisher first, because drivers and their tools can have unfamiliar names.
How do I stop programs like DanaBot from being installed again?
Most unwanted programs arrive through installers, so the fix is in how you install software. Download programs from their official sites or the Microsoft Store, not from download portals or ads above search results. During setup, choose Custom or Advanced installation and untick every extra offer, including browsers, toolbars and optimizers.
Decline update prompts that appear inside other programs unless you know them. In Windows Security, turn on reputation-based protection and potentially unwanted app blocking. These steps would most likely have stopped DanaBot before it reached the app list.
My antivirus was on. How did a trojan get past it?
Antivirus programs see a file only when it is written or run, and criminals test each new build against popular scanners before release. Detection catches up within hours or days, which is often after the first victims ran it.
Archives with passwords, installers that fetch the malware later, and scripts run through PowerShell make the job harder. That is why behaviour such as downloading cracks or pasting commands matters more than any setting. Keep Windows and Defender updated, and turn on Reputation-based protection in App & browser control.
Do I need to reinstall Windows to get rid of DanaBot?
Usually not. A thorough clean-up is enough when the offline scan finds nothing afterwards and you do not see danaBot in the list of installed apps again. A reset is the safer choice if an attacker had remote control, if security tools were switched off, or if detections come back after every clean-up.
Windows 11 can reset itself without a USB stick under Settings > System > Recovery > Reset this PC. Copy documents and photos out first and scan the copies. A reset does not change passwords or undo stolen data, so the account steps still apply.
Why can't I find DanaBot in antivirus databases?
Because it is new or because it is listed under a different name. Antivirus companies name threats after the family they belong to, and a program that appears as DanaBot on your PC may carry a generic or unrelated label in their databases.
Many new samples are first detected only by behaviour, without a family name. What you saw, danaBot in the list of installed apps, is enough to act on:
- end the program
- remove its startup entry
- run a Microsoft Defender offline scan
- secure your accounts
A detection name from a scan is worth noting for later.
How do I know if my PC has DanaBot?
Often you do not, which is the point of a trojan. Possible signs are an antivirus alert naming DanaBot or a generic trojan detection, unknown programs or scheduled tasks, processes with random names in Task Manager, browser extensions you did not add, security settings turned off, slower performance, or account alerts about logins from unknown places.
The reliable check is a full scan followed by Microsoft Defender's offline scan. If you recently ran a crack, a fake installer or a command a website told you to paste, scan even without symptoms.
I found AnyDesk or ScreenConnect that I did not install. Is that DanaBot?
Not necessarily DanaBot, but it is a warning sign. These are legitimate remote support tools, and criminals use them as ready-made backdoors, especially after tech support scams or fake invoice calls.
If you did not install it and no one you trust set it up, uninstall it, change passwords from a clean device and check your bank account. If someone connected to your PC through it, follow the steps for remote access trojans and consider a Windows reset. Installed apps sorted by date shows when it appeared.
How dangerous is DanaBot?
Treat it as serious until proven otherwise. The visible sign is danaBot in the list of installed apps, and programs that behave this way often have more abilities than they show:
- copying passwords
- downloading other malware
- giving remote access
Its family is not known yet, so nobody can say which of these it uses. The good news is that the response is the same in every case and takes about an hour:
- cut the network
- remove the startup entry
- run an offline scan
- change passwords from a clean device
If someone had remote control, a full reset is safer.
Should I report DanaBot?
Report it if you lost money, if accounts were taken over, if you are a business, or if the trojan came through a scam call. A police or national cybercrime report gives you a reference number for your bank and insurer and helps link cases.
You do not need to report a trojan that antivirus blocked before it ran. Before reporting, write down the dates, the detection name, file names and any messages or transactions linked to the attack; screenshots of antivirus alerts are useful evidence. The country list is in the report section above.
Will Fortect remove DanaBot?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For DanaBot, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Wikipedia: macro virus (read October 7, 2026)
- ZDNet: DanaBot banking Trojan jumps from Australia to Germany in quest for new targets (read October 7, 2026)
- CSOonline: Social engineering explained: How criminals exploit human behavior (read October 7, 2026)
- VirusTotal: Malware detection rate (read October 7, 2026)
- FTC: How to recognize, remove and avoid malware (read October 7, 2026)