
Kronos malware: what it is and how to remove it
Kronos malware – banking trojan that had a few updates since 2014 when it first got released. This malware is the type of virus that pretends to be a simple email attachment, so it can infect the computer further and spread other malware.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If Kronos malware keeps coming back after uninstalling, a scan can find what reinstalls it.
Do it yourself · free Remove Kronos malware yourself 3 steps, about 9 minutes, no software needed.
Start the steps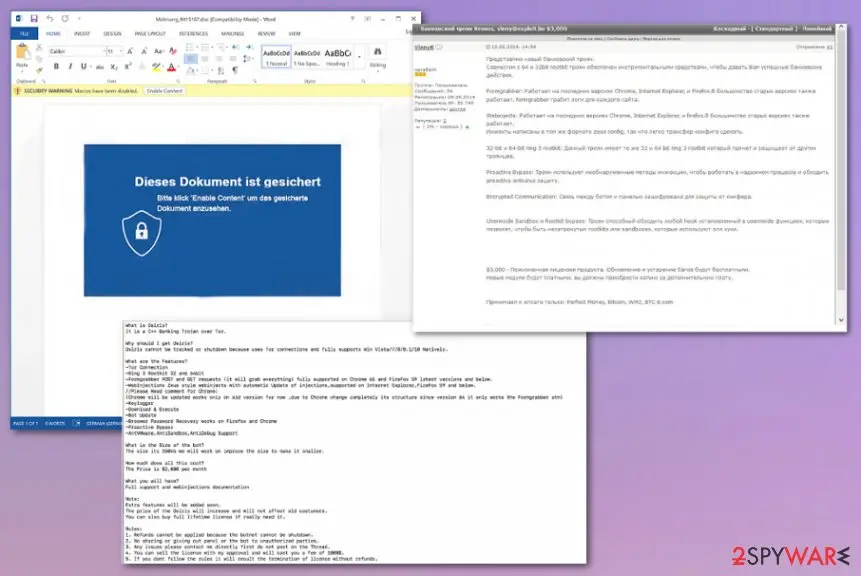
Kronos malware: summary
| Distribution | Emails with infected attachments, injected with macro viruses and malicious online pages deliver this malware. Pirated software, cracks and game cheats also can help distribute the threat. As well as other infections |
|---|---|
| Name | Kronos malware |
| Type | Banking trojan/ info-stealer[1] |
| Tactics | A trojan is set to infiltrate the system without any particular symptoms and steal credentials, banking site logins and passwords or redirect the person from an email to malicious URL of a banking site that is injected with malicious code, so all the details filled out get collected |
| Danger | The trojan is aiming to steal credentials of banking accounts, so transfers, purchases could be made in the name of the person. This is how many people get into debts and lose their funds, savings. More personal credentials can be used in targeted scam campaigns later on |
| Known since | 2014 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Damage | Not recorded in the old report |
| Symptoms | An unknown program in Installed apps |
| Evidence | 5 write-ups by security sites; details still limited |
| First seen | 28 January 2020 |
| Facts checked | 6 October 2026 |
What Kronos malware does
From our report of Jan 2020 · not reviewed since
Differences and similarities of Kronos malware campaigns
In Germany, the recent malware campaign was spread using spam emails with claims that notifications are sent from financial firms.
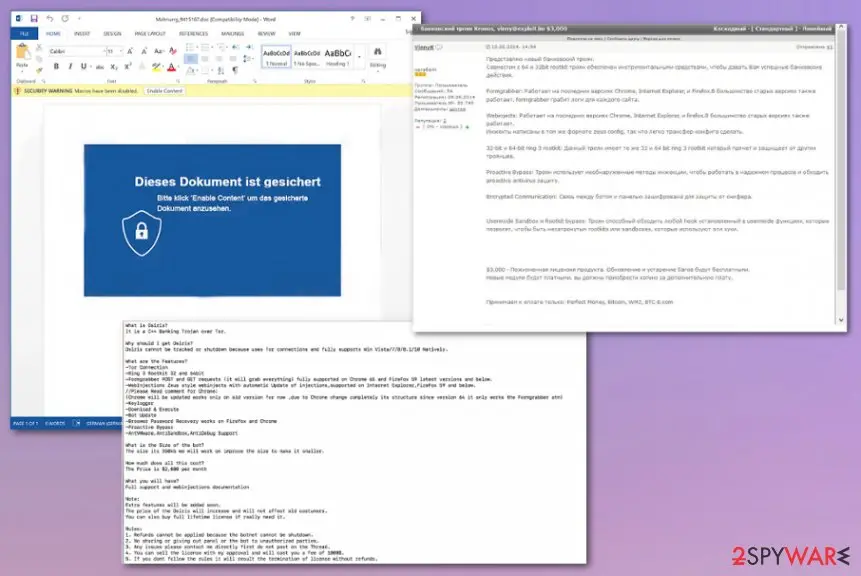
Subject lines of such emails stated about terms and conditions, updates of the privacy policy. Kronos malware used URLs connected to command and control servers and documents containing macros that get triggered when the Word document gets opened and additional content enabled by the user.
One of the emails used in Germany-targeting Kronos virus campaigns:
Attacks in Japan were discovered on July 15-16. The malvertising-based campaign involved chain emails with URLs redirecting to sites with malicious JavaScript injections. The RIG exploit kit was also included and smoke-loader downloader malware led to Kronos banking trojan drop.
The same attackers targeted Poland on the same days of July 2017. In this campaign., criminals used attachments resembling invoice attachments with malicious code to exploit the Microsoft Equation Editor vulnerability also known as CVE-2017-11882 that got patched the same year.
The fourth campaign of the trojan was observed using the English language and music streaming website, in particular, to lure victims. All of the versions observed uses the same Windows API hashing technique and hashes, same C&C protocol and encryption and the code that is identified as Kronos by the developers themselves.
A few newer versions also adopt key-logger functionalities and more similarities to the Zeus Panda banking trojan and the original Zeus web-injecting feature.
These facts and associations with other malicious programs make it more dangerous and persistent. Nevertheless, if you noticed any suspicious activities with your computer try to scan the machine using the AV tool and remove Kronos malware as soon as possible. Contact your provider when unauthorized transfers appear on your account activities.
Kronos malware removal may seem impossible since there is no particular program that trojan installs on the machine, but anti-malware tools based on detecting malicious behavior can find and terminate files and programs related to this trojan, its own payload dropped on the computer. You need to trust a reliable program and fully scan the machine, so it can eliminate the malware. Rely on .
From our report of Jan 2020 · not reviewed since
Make sure to terminate Kronos malware virus and clean the machine to avoid money and data loss
When you notice any suspicious activity on the machine and think that your device may be affected by the virus, you should scan the system immediately and use a reliable anti-malware program for that, so you can remove Kronos malware or any other virus if needed. When the software indicates all the detections follow suggested steps and clean the machine.
It may be difficult to perform Kronos malware removal when the trojan alters particular functions, disables programs or changes settings, so reboot the machine in a Safe Mode and then run or o get rid fo the virus. Then you should fix those unwanted changes and virus damage with a program like , for example.
[GI=method-1]Try rebooting the system in Safe Mode with Networking before scanning the PC with your AV tool, so you can remove Kronos malware
[GI=method-2]System Restore feature can help with the Kronos malware elimination
From our report of Jan 2020 · not reviewed since
Kronos malware is the trojan designed to steal sensitive information from victims and transfer funds from the bank accounts
Kronos malware – banking trojan that had a few updates since 2014 when it first got released.
This malware is the type of virus that pretends to be a simple email attachment, so it can infect the computer further and spread other malware. It can infect the machine and give the particular attacker remote access to financial details, emails or passwords and logins. Trojan also has this web injecting functionality that helps directly record credentials from fake financial pages.
It first was spotted in 2014 when in the Russian underground forum where the virus got offered for $7,000. Developers claimed various detection evading modules and other features to make more sales. This was a tool that got used to stealing sensitive details like banking data directly from users machines with the help of keyloggers
This high-risk trojan is sent via spam emails that come to thousands of people every day. Once the email attachments get opened and user downloads or enable the content, Kronos ends up installed on the machine without causing many symptoms at this point.
Most of the trojan infections got detected in Poland, Germany, and Japan, but campaigns are not that specifically targetted, so anyone anywhere can end up with this threat on their machine. Many researchers thought it was no longer active after the first campaign in 2014, but it came back a few times after that.
Kronos malware is based on a man-in-the-browser technique that helps trojan to record needed information. The method allows to exploit vulnerabilities to modify the content on the web browser, so any sensitive information like credentials and logins can get collected once entered.
Trojan targets finance related sites because criminals aim to get as much revenue as possible using hacked accounts and performing financial tasks, purchases, transfers. This is how people lose their money, savings or even get into debt when criminals use their accounts to profit.
Kronos malware was spotted in a few different instances and after the first campaigns, it was thought that trojan is no longer active and working. However, it came back with a new command-and-control feature that works wit Tor anonymizing network.
These were the campaigns mainly targeting Germany, Poland, and Japan. During analysis on these newer campaigns researchers also identified that Kronos malware may have been renewed and rebranded with the name Osiris. A trojan is being sold on underground forums and other market places with this name.
Kronos malware, first discovered in 2014 reportedly has four distinct campaigns distributing malicious files that lead to direct trojan installation. A trojan is capable of stealing information from banking websites. It also includes Ring3 rootkit that helps to defend from other trojans. In 2016, when trojan was no longer found active, researches believed that malware was no longer working.
Kronos virus came back in 2017 when the FBI accused a whitehat hacker who stopped WannaCry for building the trojan. Hutchins was named a hero when he discovered a kill switch for the WannCry ransomware and stopped the infamous virus. FBI claimed that Kronos banking trojan has been around since June 2014 and began as a banking trojan based on the Zeus virus code.
From our report of Jan 2020 · not reviewed since
More from our earlier report on Kronos malware
- To remove Kronos malware, you need a good anti-malware tool that could detect the threat and clean the machine from all the traces
- Subject: Aktualisierung unsere AGBs Sehr geehrter Herr Max Mustermann, Die Fidor Bank optimiert ihr Angebot permanent weiter, um Sie noch besser bei Ihren Finanzgeschäften zu unterstützen.
- Daher werden wir ab dem 07.07.2018 folgende Neuerungen/Anpassungen einführen: -Ausbaut des Zahlungsverkehrs in Bezug auf Überweisungen sowie Sonderbedingungen hinsichtlich der Einführung des Produktes "Geld Notruf" -Anpassung unserer AGB nach §22-31 DSGVO, zur Rechtsgrundlagen der Verarbeitung personenbezogener Daten Der anschließend kurze Datenabgleich ist erforderlich um Sie als primären Kontoinhaber zu legitimieren.
- Sollten wir unregelmäßigkeiten bei Ihrem Datenabgleich feststellen, ist die Bestätigung unserer angepassten AGBs nurnoch auf dem Postweg möglich, und notwendig um die Handlungsfähigkeit Ihres Kontos zur erhalten.
- Legitimation beginnen Wichtiger Hinweis: Die geänderten AGB gelten als von Ihnen angenommen, wenn Sie den Datenabgleich erfolgreich durchgeführt haben, und Sie der Änderung nicht innerhalb von sechs Wochen schriftlich widersprechen.
- Sofern Sie Fidor zu den geänderten Bedingungen nicht weiter nutzen möchten, senden Sie Ihren Wiederruf bitte an: Fidor Bank AG, Kundenservice Widerruf, Sandstr.
- 33, D-80335 München Sie haben noch Fragen?
- Unser Kundenservice steht Ihnen jederzeit zur Verfügung.
- Mit freundlichen Grüßen Ihr Fidor Bank Team
How Kronos malware got on your PC
From our report of Jan 2020 · not reviewed since
Trojans, worms, ransomware, and other viruses that end up installed directly on the machine cannot be easily noticed and spotted during the infection because criminals use deceptive methods and misleading techniques to hide their purposes of dropping the threat.
In most cases, such information-stealing trojans and banking malware get delivered via spam email campaigns where subject lines state about important information and the sender resembles a company or a service that people know.
Such emails contain messages and URLs or Microsft document attachments containing encouragements to enable the content or allow the macros. Once the malicious files get permission to download the code, the machine gets infected and affected by the trojan directly, so all the processes can get triggered.
Often malicious actors can inject web code on legitimate-looking financial sites, so all the information entered there end up collected by criminals. These hyperlinks also are offered on those emails, so stay away from any suspicious emails and notifications you are not expected to receive.
How to remove Kronos malware
A stealer usually takes what it wants within minutes and may already be gone.
The scan comes first, then the accounts.
Step 1: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 2: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
Protect your privacy - employ a VPN
There are several ways how to make your online time more private - you can access an incognito tab.
However, there is no secret that even in this mode, you are tracked for advertising purposes. There is a way to add an extra layer of protection and create a completely anonymous web browsing practice with the help of VPN. This software reroutes traffic through different servers, thus leaving your IP address and geolocation in disguise.
Besides, it is based on a strict no-log policy, meaning that no data will be recorded, leaked, and available for both first and third parties. The combination of a secure web browser and VPN will let you browse the Internet without a feeling of being spied or targeted by criminals.
No backups? No problem. Use a data recovery tool
If you wonder how data loss can occur, you should not look any further for answers - human errors, malware attacks, hardware failures, power cuts, natural disasters, or even simple negligence.
In some cases, lost files are extremely important, and many straight out panic when such an unfortunate course of events happen. Due to this, you should always ensure that you prepare proper data backups on a regular basis.
If you were caught by surprise and did not have any backups to restore your files from, not everything is lost. is one of the leading file recovery solutions you can find on the market - it is likely to restore even lost emails or data located on an external device.
Questions about Kronos malware
Can I safely uninstall Kronos malware?
If you did not install Kronos malware yourself and it is not part of your hardware or a program you rely on, yes. Uninstalling an unwanted program does not harm Windows. Before you do, search the exact name and publisher to be sure it is not a driver tool, a printer utility or a game launcher with an odd name.
Then remove it from Settings, Apps, Installed apps. Ignore any offers or warnings in its uninstaller about losing protection or performance. Afterwards check Startup apps and your browsers for leftovers, and restart once to confirm that it does not reinstall itself.
How do I stop programs like Kronos malware from being installed again?
Most unwanted programs arrive through installers, so the fix is in how you install software. Download programs from their official sites or the Microsoft Store, not from download portals or ads above search results. During setup, choose Custom or Advanced installation and untick every extra offer, including browsers, toolbars and optimizers.
Decline update prompts that appear inside other programs unless you know them. In Windows Security, turn on reputation-based protection and potentially unwanted app blocking. These steps would most likely have stopped Kronos malware before it reached the app list.
Is Kronos malware still on my computer?
Possibly, possibly not. Some stealers stay and keep collecting; others delete themselves after one run. The sign you saw, kronos malware in the list of installed apps, only shows that data was used, not where the program is now.
A Microsoft Defender offline scan answers the first question; checking Startup apps, Task Scheduler and the Downloads folder for files from the days before helps too. Either way, the account steps are needed, because stolen passwords and cookies keep working after the program is gone, sometimes for weeks.
Can I get back what Kronos malware took?
Accounts, usually yes; money, sometimes. Most services restore an account through their recovery process if you act quickly and still control the e-mail address. Card payments can often be disputed with the bank.
Crypto sent after kronos malware in the list of installed apps is much harder, because transactions cannot be reversed; report it to the exchange the funds went to and to the police, with the wallet addresses and times.
Do not answer offers from "recovery services" that contact you; they are a common second scam aimed at people who just lost funds.
What happens to the stolen data?
Stolen data is packed into "logs", one per infected PC. The criminal who ran the stealer uses them directly or sells them in online markets, where others search them for bank, crypto, e-mail, gaming and business accounts.
This can happen days or months after the infection. That is why changing passwords and ending sessions matters even if nothing has happened yet. Breach notification services such as Have I Been Pwned can tell you when your e-mail address appears in known leaks.
Should I stop using this PC?
Only for sensitive things, and only until it is clean. Do not log in to banking, e-mail or crypto on it until the offline scan finds nothing. You can keep using it to follow the removal steps.
If the scans keep finding new items, or protection keeps switching off, back up your documents and reset Windows. After that the PC is as safe as a new one, but the accounts still need the steps in this guide, because a reset cannot undo data that was already sent.
Is Kronos malware a known stealer?
Not as a named family yet. The sign, kronos malware in the list of installed apps, is typical of information stealers, keyloggers or clippers, but no analysis links Kronos malware to a specific one. That is common:
- victims notice the effects
- such as lost accounts or swapped addresses
- before anyone sees the file
You do not need the family name to act. Change passwords from a clean device, sign out of all sessions, move crypto to a new wallet and run a Microsoft Defender offline scan on the PC. If a scan gives a detection name, note it for the report.
How can someone log in without my two-step code?
By using a session instead of a login. When you sign in, the site gives the browser a cookie that says you already passed both steps. Spyware like Kronos malware copies that cookie, and the attacker loads it into their own browser, so the site sees a logged-in user and asks for nothing.
The fix is to end all sessions in the account's security settings, which makes the copied cookie worthless, and then change the password. Some services also show active sessions with locations, which helps spot misuse.
Should I reset my PC because of Kronos malware?
Only if the signs point to deeper access. Reset when you see kronos malware in the list of installed apps again after removal, when Windows Security cannot start or update, when remote access tools you did not install keep appearing, or when you simply cannot trust the PC any more.
Otherwise, the plan in this guide plus an offline scan is enough. If you do reset, choose Remove everything and Cloud download for a fresh copy of Windows, restore only documents and photos, and reinstall programs from their official sites. Change important passwords from the clean system afterwards.
Will Fortect remove Kronos malware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Kronos malware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Wikipedia: Trojan horse malware (read October 6, 2026)
- Threatpost: WannaCry Kill Switch Hero Faces New Charges, But Code Evals Say Little (read October 6, 2026)
- Trendmicro: 17-Year Old MS Office Flaw (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)