
PEGASUS SPYWARE ACTIVATED scam: how to spot it and what to do
"PEGASUS SPYWARE ACTIVATED" is nothing but a scam which targets explicitly Mac OS users. If you keep getting these persistent pop ups, it is highly likely that you are affected by a PUP (potentially unwanted program).
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Do it yourself · free Remove PEGASUS SPYWARE ACTIVATED scam yourself 4 steps, about 12 minutes, no software needed.
Start the steps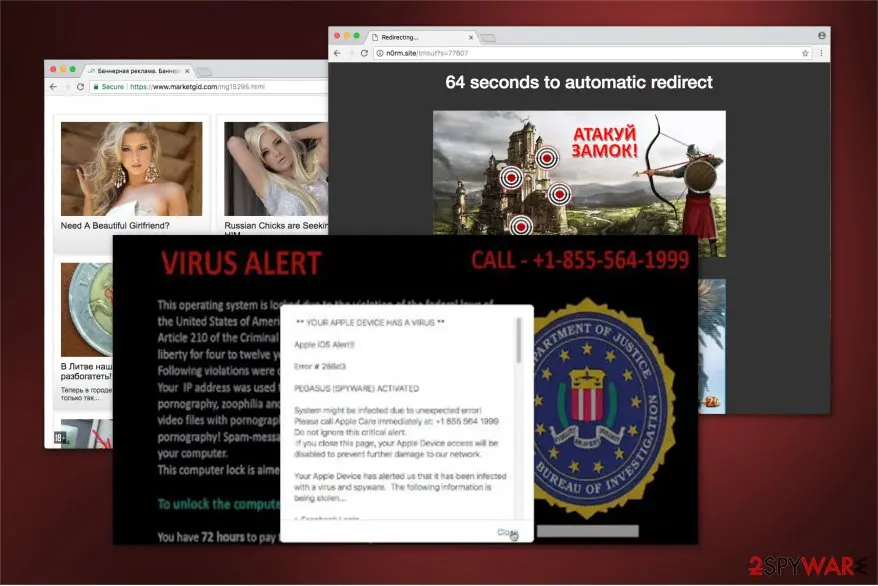
PEGASUS SPYWARE ACTIVATED scam: summary
| Name | PEGASUS SPYWARE ACTIVATED scam |
|---|---|
| Type | Phishing message |
| Symptoms | A phishing e-mail asking you to sign in |
| Evidence | 4 write-ups by security sites; details still limited |
| Arrives as | |
| Pretends to be | |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 4 more facts
| Claim | Your account needs urgent attention |
|---|---|
| Asks for | Your password |
| First seen | 8 January 2018 |
| Facts checked | 7 October 2026 |
What the PEGASUS SPYWARE ACTIVATED scam message looks like
** YOUR APPLE DEVICE HAS A VIRUS **
Apple iOS Alert!!
Error # 268d3
PEGASUS (SPYWARE) ACTIVATED
The system might be infected due to unexpected error!
Please call Apple Care immediately at: +1-8333-370-777
Do not ignore this critical alert.
If you close this page, your Apple Device access will be disabled to prevent further damage to our network.
Your Apple Device has alerted us that it has been infected with a virus and spyware. The following information is being stolen…
> Facebook Login
> Credit Card Details
> Email Account Login
> Photos stored on this Device
You must contact us immediately so that our engineers can walk you through the removal process over the phone. Please call us within the next 5 minutes to prevent your Apple Device from being disabled.
Is PEGASUS SPYWARE ACTIVATED scam dangerous? What the senders want
From our report of Jan 2018 · not reviewed since
"PEGASUS SPYWARE ACTIVATED" scam baffles Mac OS X users
"PEGASUS SPYWARE ACTIVATED" is nothing but a scam which targets explicitly Mac OS users.
If you keep getting these persistent pop ups, it is highly likely that you are affected by a PUP (potentially unwanted program).
After seeing "PEGASUS SPYWARE ACTIVATED" pop-up for the first time, users might think that they are at the high risk of exposing their personal data and, if no action is taken, all the information will be stolen.
"PEGASUS SPYWARE ACTIVATED" scam advises calling a specific number (which can vary since there are multiple versions of the malware like Error # 268d3 virus) to contact technical support, which will then charge a certain amount of money either for a lengthy phone call itself, or various unneeded services offered by scammers.
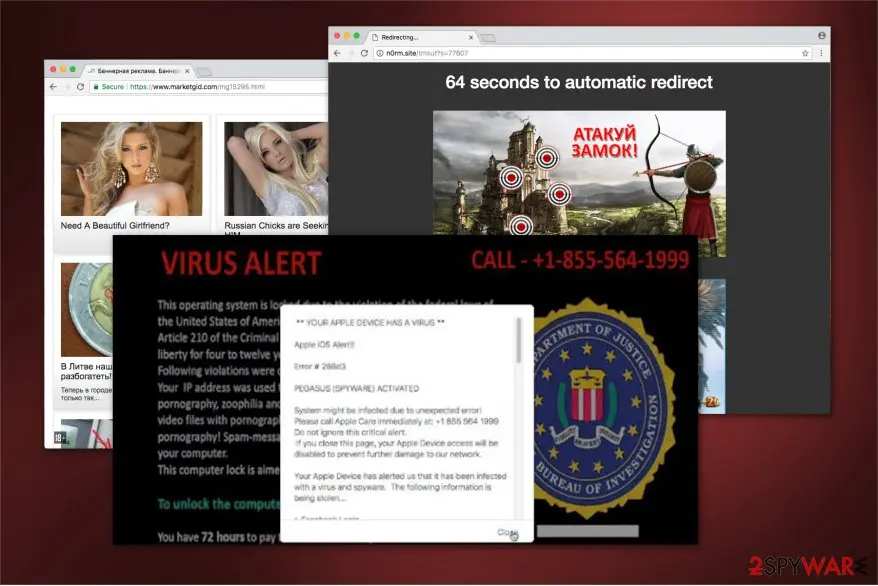
The following message is displayed in the popup:
Adware like "PEGASUS SPYWARE ACTIVATED" virus are technically more complicated than regular PUPs as they are designed to surpass firewall which is used to prevent such fake pop-ups from occurring. The complicated code helps scammers to deceive and scare regular users while trying to make some money.
Please be aware that "PEGASUS SPYWARE ACTIVATED" popup has nothing to do with Apple and people who pick up the phone call are not Apple employees. Additionally, fake technicians can ask for a remote access to your Mac. After connecting to your system, they pretend to find problems and malware that does not exist, and then ask for specific payments in exchange for assisting users with these "issues."
Quite often, scammers will attempt to install malware or change system settings and steal actual login information, such as your social media accounts, credit card accounts, etc. To protect yourself, make sure you remove "PEGASUS SPYWARE ACTIVATED" scam from your computer. The easiest way to do that is to run a full system scan with .
"PEGASUS SPYWARE ACTIVATED" virus has many similarities with various similar scam schemes, which all claim that user's system is damaged or infected with malware and that the only way of fixing the issue is by calling certain phone lines or by paying "a fine."
Please, do NOT fall for them because PUPs like these are designed to scam the unaware persons and steal their money. You are highly recommended to take care of "PEGASUS SPYWARE ACTIVATED" removal by eliminating all adware hiding on your PC system.
From our report of Jan 2018 · not reviewed since
Tech support scams can get into your Mac with the help of bundling, links in spam e-mails, intrusive ads and extracted suspicious files
To protect yourself from scams like this one, keep in mind that Bundling is used to get PUPs into your system.
Usually, users tend to skip many steps and use Quick/Recommended settings when installing new software downloaded from the internet. It is highly advised to read all the installation instructions properly and opt out of any additions to the installation while in Advanced mode.
In addition, PUPs can be obtained while clicking on links in spam e-mails or clicking on intrusive ads, so make sure you are careful with them. It is also not recommended downloading and extracting files of an unknown origin. All these actions can lead to various infections of your machine, so it is essential to be wary at all times.
What to do after the PEGASUS SPYWARE ACTIVATED scam e-mail
If you only received the message and clicked nothing, step 3 is all you need.
If you clicked the link or typed anything on the page it opened, do every step, starting with the password.
Step 1: Change the password you typed on the fake page
If you entered a password after clicking the link in the PEGASUS SPYWARE ACTIVATED scam message, treat that account as known to the sender.
Open the provider's real site by typing its address yourself, not through any link in the e-mail, and change the password there. Choose a new one you have never used before, and change it on every other account that shared the old one.
Then use the option to sign out of all other sessions or devices, if the provider has one. This works the same in any browser on Windows 11 and Windows 10.
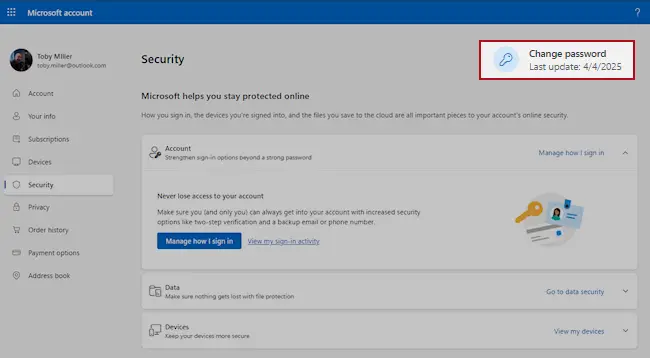
Microsoft account, Security page (account.microsoft.com/security): Change password. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Turn on two-step verification
Two-step verification asks for a code from your phone or an authenticator app whenever someone signs in from a new device. A stolen password alone is then not enough to open the mailbox.
Turn it on in the security settings of the e-mail account first, then for the bank, shop and social accounts that send their reset links to that address.
While you are there, check the recovery e-mail and phone number and the forwarding rules, which attackers sometimes change to keep access. The settings pages look the same on Windows 11 and Windows 10.
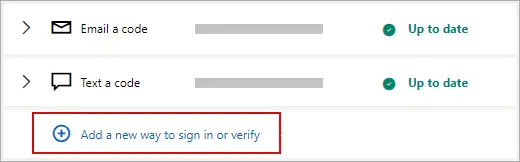
Microsoft account: Manage how I sign in, where two-step verification and the sign-in methods are. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Report the e-mail and delete it
Report the message instead of only deleting it. In Outlook choose Report > Report phishing, in Gmail the three-dot menu > Report phishing; the provider then blocks the same message for other people.
Do not reply and do not click anything else in it. On a work account, forward it to your IT team as an attachment first. Web mail and the mail apps on Windows 11 and Windows 10 offer the same options.
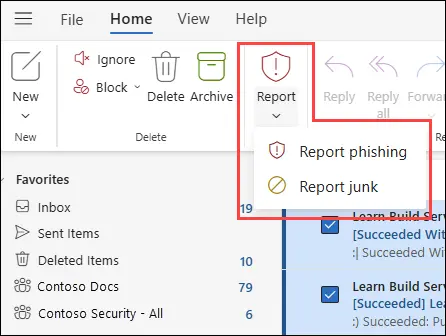
New Outlook for Windows and Outlook on the web: Report > Report phishing. Full procedure with screenshots: Report a phishing e-mail
Step 4: Scan the PC if you opened a file from the message
A page that only asked for a password installs nothing, so most readers can skip this step.
If the PEGASUS SPYWARE ACTIVATED scam e-mail or the page it opened made you download or open a file, delete it and run a full scan, then a Microsoft Defender Offline scan.
In Windows 11 and Windows 10 open Windows Security > Virus & threat protection > Scan options, select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts and the scan takes about 15 minutes, so save your work first.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
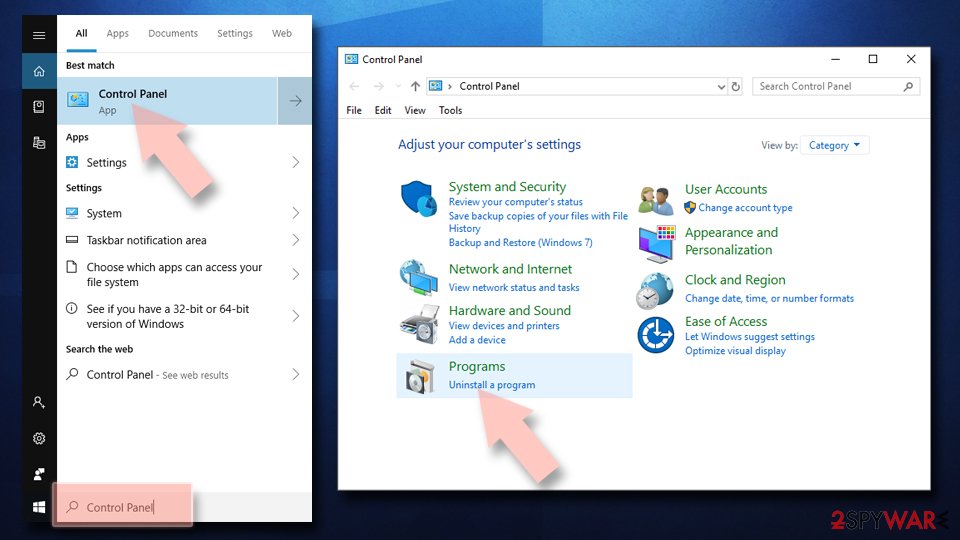
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
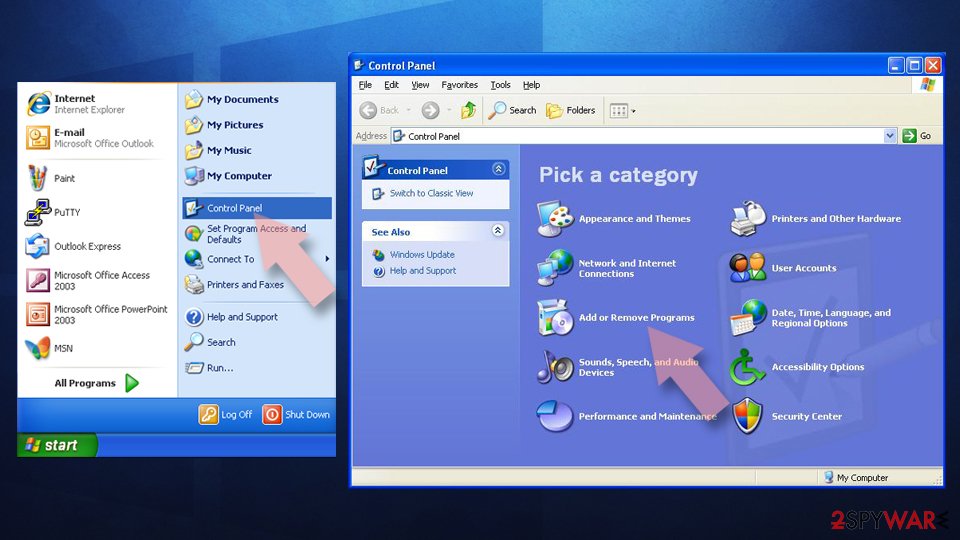
Remove the unwanted program:
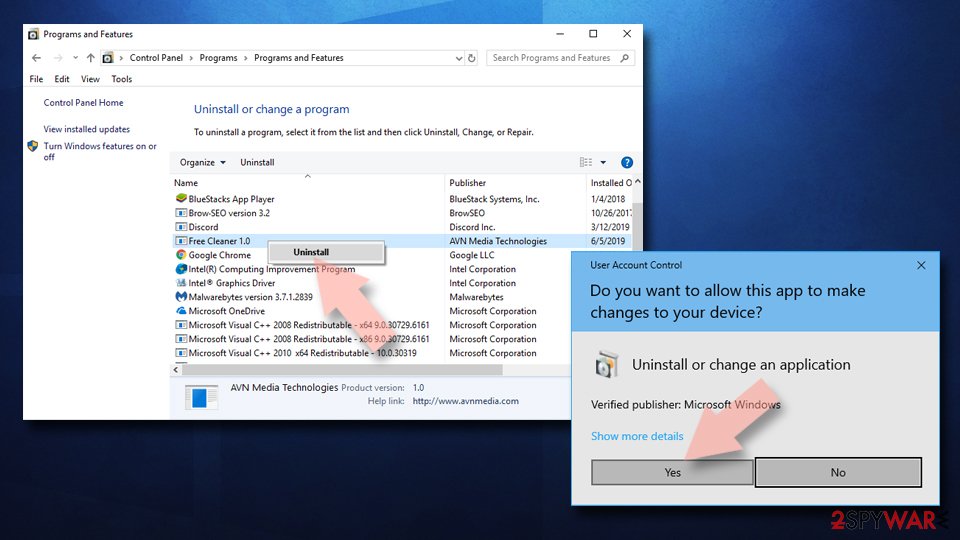
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
Uninstall all suspicious entries and reset Chrome to get rid of the annoying pop-up.
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.

Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.

Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.

Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.

Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.

Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.

Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.

Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.

Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.

Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.

Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.

Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.

- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.

Delete from Safari
Fix Safari by deleting unknown extensions which might be linked to the adware. Afterward, do not forget to reset the browser.
Remove dangerous extensions:
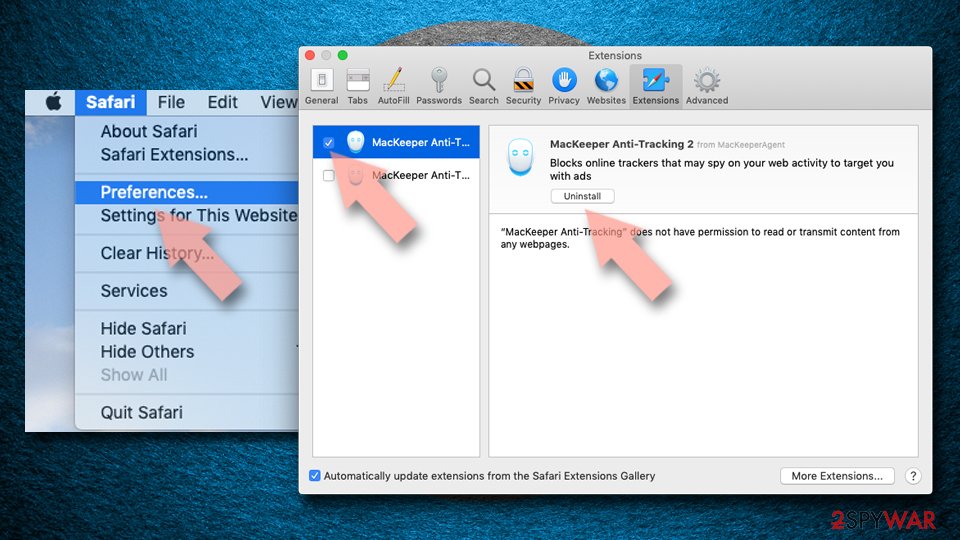
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
Clear history and website data:
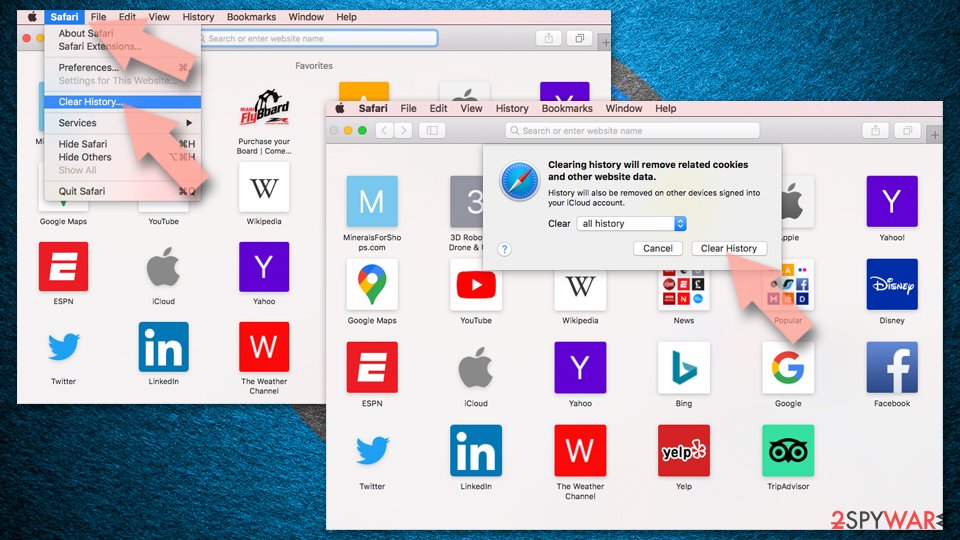
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
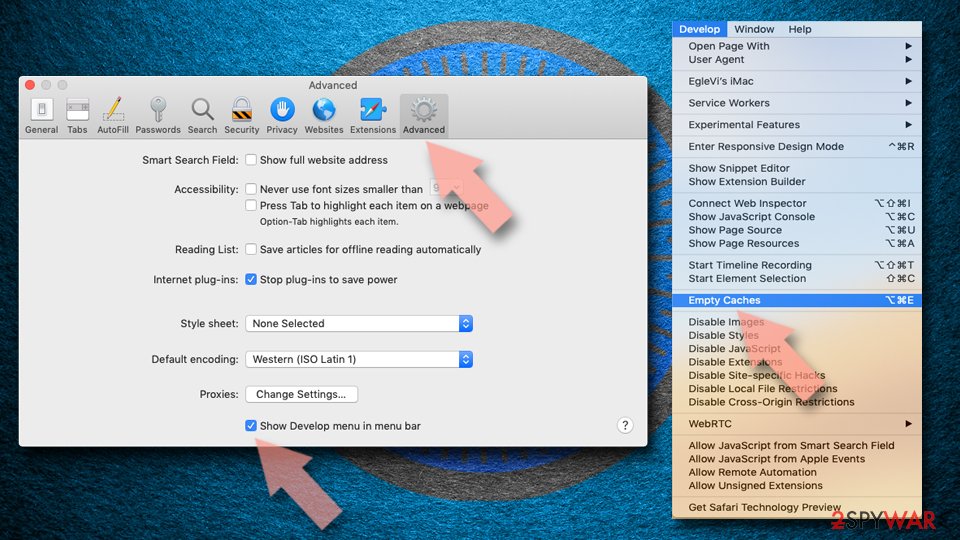
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
If you have encountered a scam message, immediately remove the adware from Mac:
Remove the unwanted application:
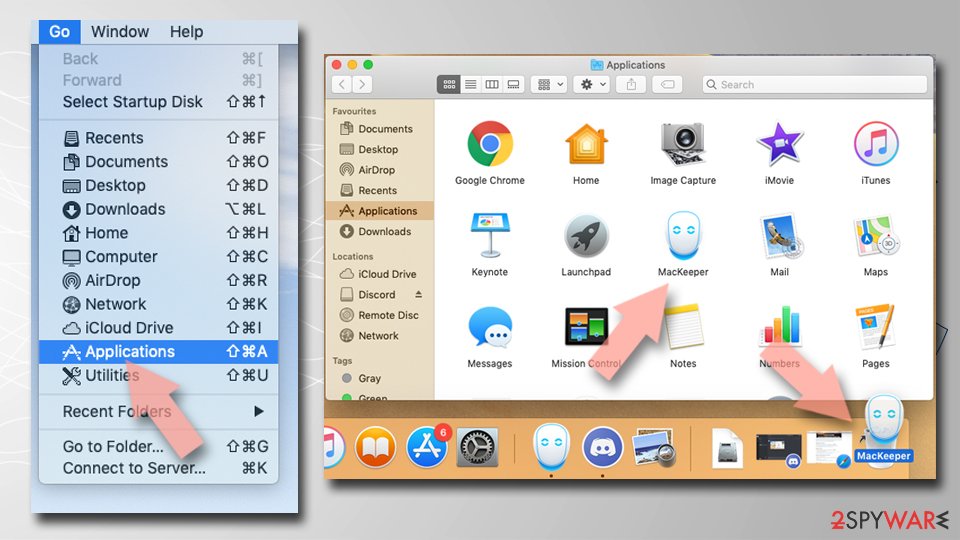
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
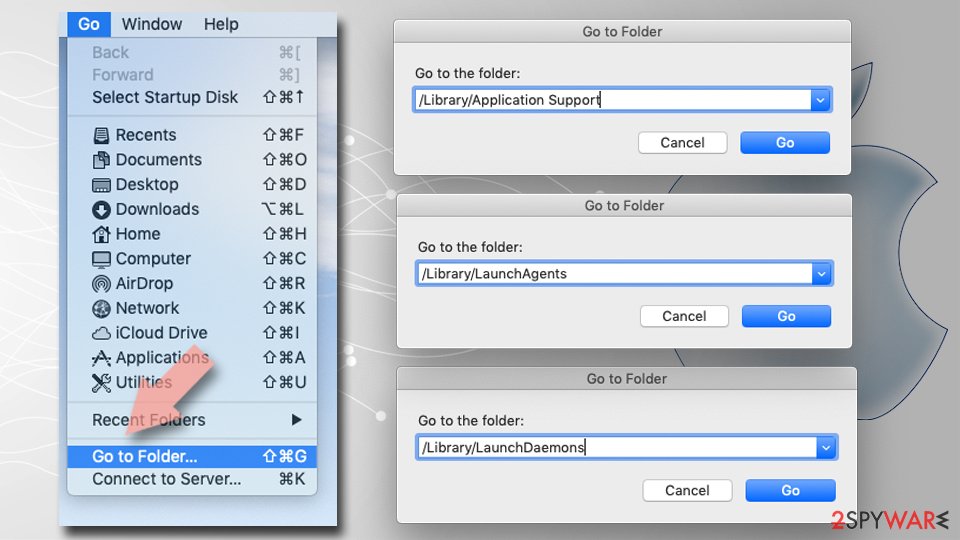
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Reset Internet Explorer
Remove dangerous add-ons:
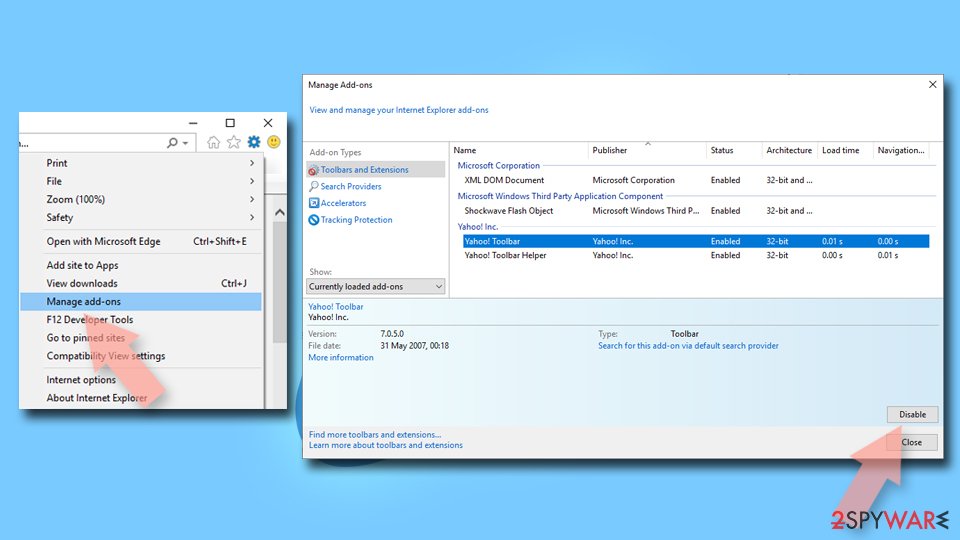
- Open Internet Explorer, click on the Gear icon (IE menu) on the top-right corner of the browser
- Pick Manage Add-ons.
- You will see a Manage Add-ons window. Here, look for suspicious plugins. Click on these entries and select Disable.
Change your homepage if it was altered:
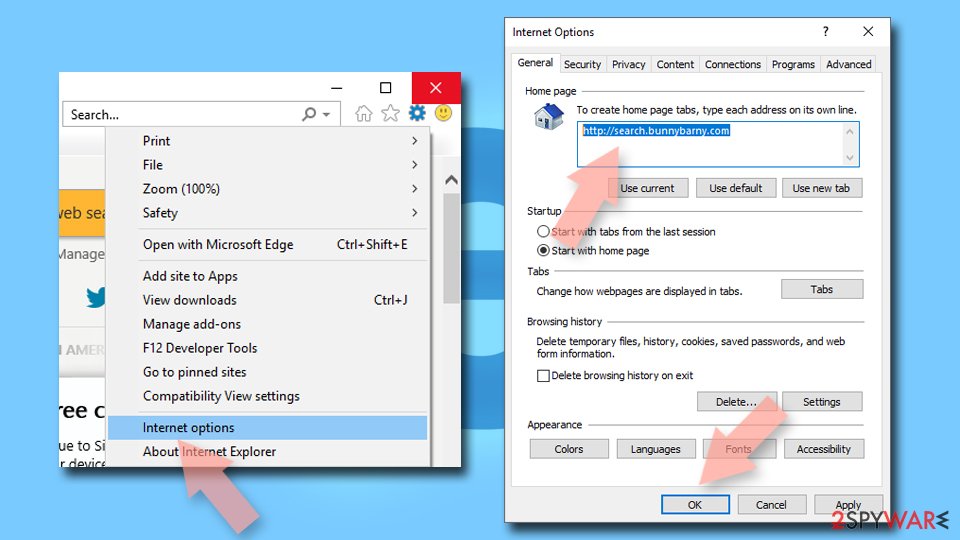
- Open IE and click on the Gear icon.
- Select Internet Options.
- In the General tab, delete the Home page address and replace it by your preferred one (for example, Google.com).
- Click Apply and then select OK.
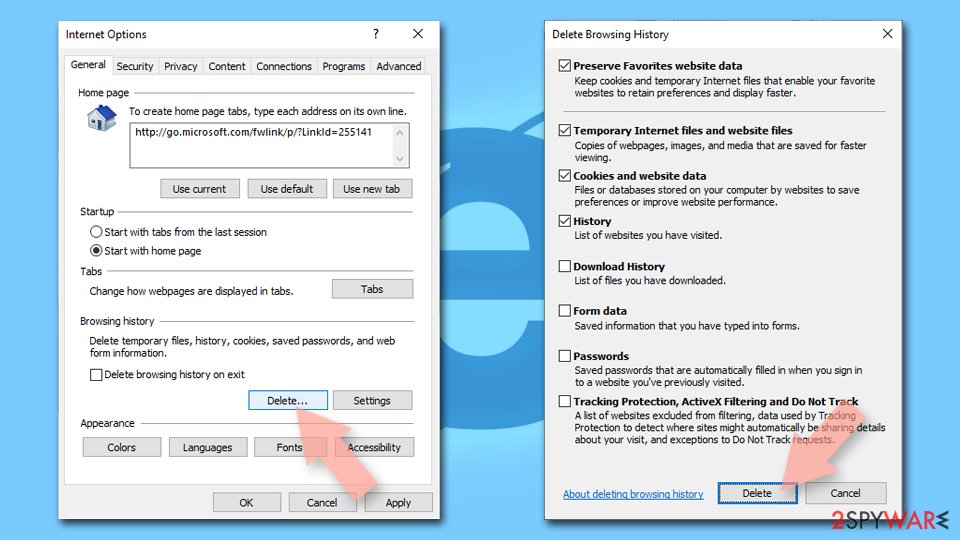
Delete temporary files:
- Press on the Gear icon and select Internet Options.
- Under Browsing history, click Delete...
- Select relevant fields and press Delete.
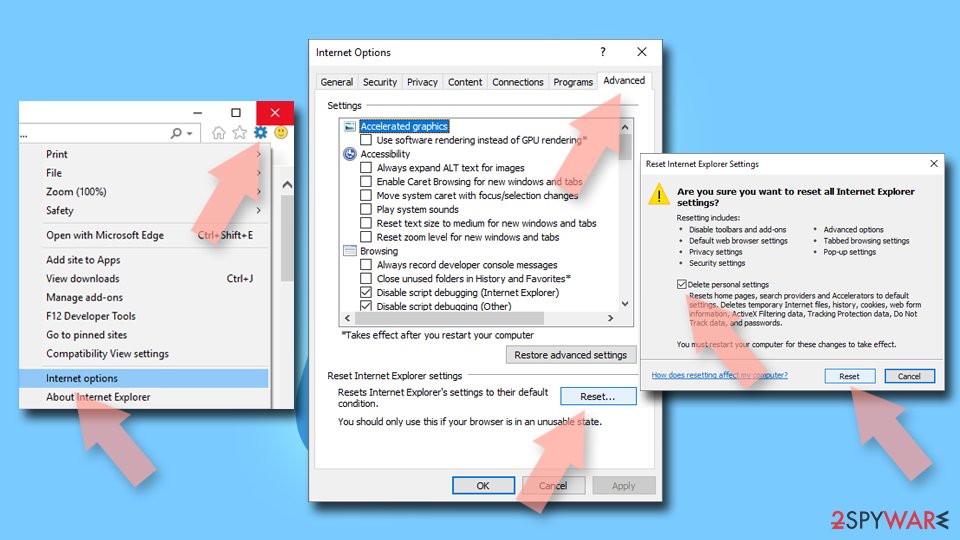
Reset Internet Explorer:
- Click on Gear icon > Internet options and select Advanced tab.
- Select Reset.
- In the new window, check Delete personal settings and select Reset.
Protect your privacy - employ a VPN
There are several ways how to make your online time more private - you can access an incognito tab.
However, there is no secret that even in this mode, you are tracked for advertising purposes. There is a way to add an extra layer of protection and create a completely anonymous web browsing practice with the help of VPN. This software reroutes traffic through different servers, thus leaving your IP address and geolocation in disguise.
Besides, it is based on a strict no-log policy, meaning that no data will be recorded, leaked, and available for both first and third parties. The combination of a secure web browser and VPN will let you browse the Internet without a feeling of being spied or targeted by criminals.
No backups? No problem. Use a data recovery tool
If you wonder how data loss can occur, you should not look any further for answers - human errors, malware attacks, hardware failures, power cuts, natural disasters, or even simple negligence.
In some cases, lost files are extremely important, and many straight out panic when such an unfortunate course of events happen. Due to this, you should always ensure that you prepare proper data backups on a regular basis.
If you were caught by surprise and did not have any backups to restore your files from, not everything is lost. is one of the leading file recovery solutions you can find on the market - it is likely to restore even lost emails or data located on an external device.
From our report of Jan 2018 · not reviewed since
Uninstalling "PEGASUS SPYWARE ACTIVATED" pop up from the system
Acccording to LosVirus.es experts, in case you have already engaged with scammers, allowed them to access your Mac remotely and paid some money, please do the following:
A detailed guide is provided below:
- Do a full scan of your system using security application to remove "PEGASUS SPYWARE ACTIVATED" fake alert (even if Apple is not security utilities friendly, you can still install particular anti-malware tools on MacOS). You need to delete any suspicious software found on your system;
- Call your bank and revert all the payments that have been made;
- Change all your passwords;
- Update your Mac with the recent updates as soon as they are available;
- Reset browser settings to complete PEGASUS SPYWARE ACTIVATED removal from your computer.
Questions about PEGASUS SPYWARE ACTIVATED scam
Can reading " YOUR APPLE DEVICE HAS A VIRUS " infect my computer?
Reading it cannot. An e-mail is text and pictures, and current versions of Outlook, Gmail and other web mail services do not run code from a message just because you opened it. What can cause harm is an action:
- signing in on the page the link opens
- opening an attachment
- enabling macros in a document
The message " YOUR APPLE DEVICE HAS A VIRUS " was built to lead you to one of those steps. If you stopped at reading, delete it and use the report button so the provider can block the same wave for others. Nothing needs to be removed from Windows.
How fast do I need to react after signing in on the " YOUR APPLE DEVICE HAS A VIRUS " page?
As fast as you can. Stolen passwords are often tried within minutes, and the first thing an attacker usually changes is the recovery e-mail or phone, which locks you out. Change the password from a clean device first, then sign out everywhere and review the recovery settings.
If you are already locked out, use the provider's account recovery form straight away and mention that the page behind " YOUR APPLE DEVICE HAS A VIRUS " took your password. Warn your contacts, since a taken-over mailbox is often used to send the same phishing to them.
Is PEGASUS SPYWARE ACTIVATED scam really from Facebook?
No. It is sent by scammers who copy the name and look of Facebook. The sender address and the links do not belong to it, and the message asks for your password, which a real company does not request through an unexpected message.
If you want to be sure about your account, open the website or app of Facebook the way you normally do, not through the message, and look for notices there. Then delete the message and report it as phishing. If you already followed its instructions, use the steps in this guide for your case.
Is it true that your account needs urgent attention?
No. The claim that your account needs urgent attention is the hook of PEGASUS SPYWARE ACTIVATED scam, invented to give you a reason to act quickly. Scammers pick a story that could plausibly apply to many people, so it may feel relevant to you, but nothing in the message is based on your real accounts or devices.
If the claim concerns a service you use, check it there directly, by opening the website or app yourself. You will find no such problem. Then delete the message and report it as phishing.
What happens if I do what PEGASUS SPYWARE ACTIVATED scam asks?
The scammers get your password, and they use it quickly. Passwords are tried on the real service within minutes, cards are charged or added to phone wallets, remote access is used to open your bank, and crypto is moved on at once.
Documents surface later as accounts in your name. If you already did what the message asked, do not wait to see what happens; follow the steps in this guide for your case today. Speed matters more than anything else here.
Will Facebook refund me if I fell for PEGASUS SPYWARE ACTIVATED scam?
Facebook did not send the message and is not responsible for it, so a refund usually comes from your bank or card issuer, not from the brand. Call the bank first if you paid.
It still helps to tell the real company: they can secure your account, add notes for their fraud team and take down pages that use their name. Contact them through their official website or app only, never through the message or a search ad. Keep the message as evidence.
Does PEGASUS SPYWARE ACTIVATED scam mean my PC is hacked?
Not necessarily. The sign reported, an e-mail with the subject " YOUR APPLE DEVICE HAS A VIRUS ", is usually caused by a password that leaked or was phished, not by malware on the PC.
Passwords leak in breaches of other websites and are tried on many services. Still, rule out the PC:
- run a full scan in Windows Security
- check Installed apps for anything you do not recognise
- look at the browser's extensions
If all is clean, the problem lies with the account, and changing the password with two-step verification turned on is the fix.
How quickly do scammers use a phished password?
Often within minutes. Phishing kits send each password to the operators as soon as it is typed, and many test it automatically on the real service. Some kits also pass the two-step code through in real time.
That is why the first hour matters: change the password, end all sessions and check that the recovery details are still yours. If nothing has changed by then, you were probably fast enough, but keep watching for login alerts and password-reset e-mails for a few weeks.
Should I reply or unsubscribe?
No. A reply confirms that your address is active and read, which leads to more scams. The unsubscribe link in a scam message is part of the scam and may lead to a phishing page. Mark the message as spam or phishing and delete it.
Block the sender if your mail app allows it, though scammers change addresses often. If the scam came by text message, do not reply STOP either. If it came through social media, use the platform's report function and block the account.
Will Fortect remove PEGASUS SPYWARE ACTIVATED scam?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For PEGASUS SPYWARE ACTIVATED scam, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- GetCyberSafe: Fraudulent Technical Support (read October 7, 2026)
- LosVirus: LosVirus (read October 7, 2026)
- FTC: How to recognize and avoid phishing scams (read October 7, 2026)
- CISA: Recognize and report phishing (read October 7, 2026)
- Microsoft Support: Protect yourself from phishing (read October 7, 2026)