RedLine: what it is and how to remove it
RedLine malware was first observed in 2020. It is an information stealer mainly targeting Windows users.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
An automatic scan can look at AddInProcess.exe and the other programs installed around the same time.
Do it yourself · free Remove RedLine yourself 6 steps, about 18 minutes, no software needed.
Start the steps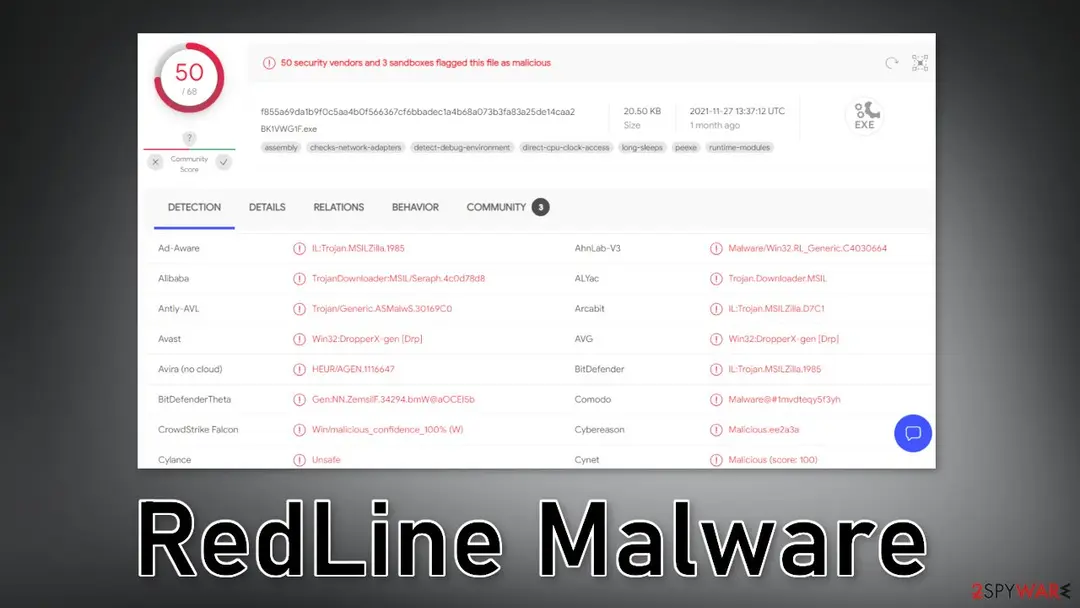
RedLine: summary
| Distribution | Email attachments, torrent websites, deceptive advertisements, social engineering |
|---|---|
| NAME | RedLine |
| TYPE | Trojan virus; malware |
| SYMPTOMS | No particular symptoms are noticeable to the victims as the malware acts in the background |
| DANGERS | Users' passwords, banking information, and other sensitive data can be stolen, which could lead to monetary losses, identity theft, and the victims' computers being added to a botnet |
| Detection names | No Microsoft detection name is known |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Damage | Not recorded in the old report |
|---|---|
| Name | RedLine |
| Type | Loader |
| Symptoms | An unknown process in Task Manager |
| Evidence | 6 write-ups by security sites; details still limited |
| File names | AddInProcess.exe |
| First seen | 30 December 2021 |
| Facts checked | 6 October 2026 |
What RedLine does on an infected PC
From our report of Dec 2021 · not reviewed since
More from our earlier report on RedLine
- Professional security tools should eliminate the threat completely with all the related files
- Use a maintenance tool like to fix any remaining damage and optimize your machine
What RedLine can steal or download
From our report of Dec 2021 · not reviewed since
RedLine malware was first observed in 2020.
It is an information stealer mainly targeting Windows users. It steals victims' passwords, autofill data, cryptocurrency wallets, browser information, FTP connections, and OS information such as system hardware, time zone, IP address, geolocation, OS version, and default language.
Cybercriminals can use this information to access various accounts, like social media, email, and banking. They can deceive people into transferring money and making fraudulent purchases. The malicious program can also infect victims' machines with other malware like ransomware, cryptocurrency miners, trojans, etc.
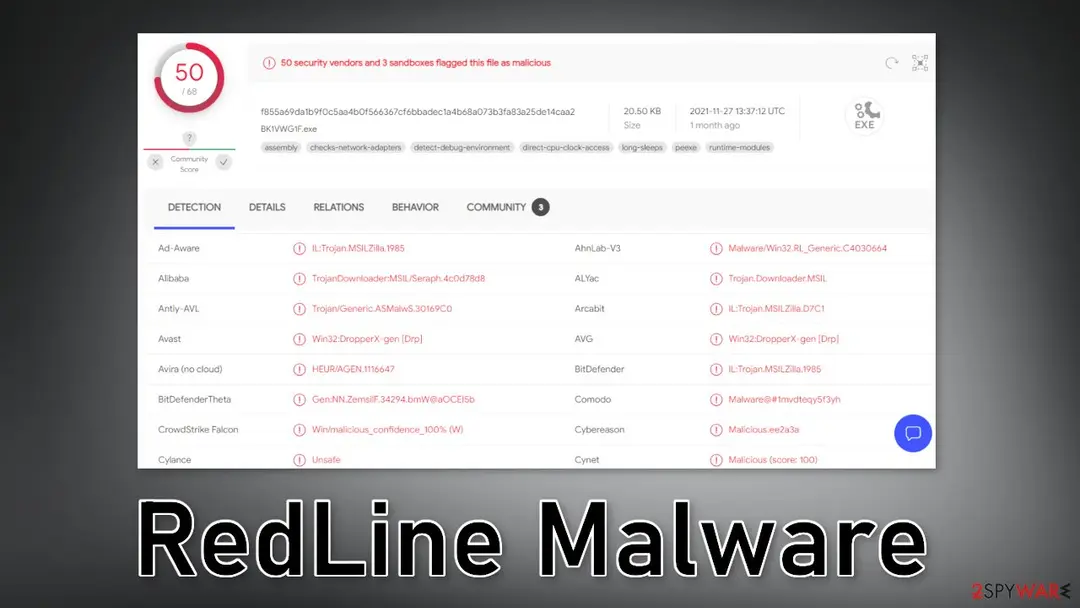
It shows up in users' systems as AddInProcess.exe which was flagged by 50 security vendors and 3 sandboxes as malicious. It also acts as a Trojan because it does not show any particular symptoms and performs tasks in the background. Most people may not even know that they have been infected by this malware.
Usually, people will notice that something is wrong if they suffer from financial losses or identity theft. If malware causes the installations of other malicious programs that can also be the point where users notice the infection. Otherwise, a lot of time can pass before users find out about the threat.
How RedLine got on your PC
From our report of Dec 2021 · not reviewed since
Currently, the RedLine malware is advertised on various cybercriminal forums as a MaaS (Malware-as-a-Service) model.
The malicious program can be purchased through the Redline telegram official channel. The threat actors offer a monthly, weekly, and lifetime subscription for the prices of 100$, 150$, and 800$ respectively. They accept payment in Bitcoin, Ethereum, XMR, LTC, and USDT.
Those who buy the subscription use various methods to spread RedLine malware. Healthcare was one of several industry sectors affected by this threat in the last few months. Crooks take advantage of the global pandemic by using it in their social engineering scams. A spam email was found to distribute RedLine Stealer by disguising it as the Folding@home application:
The email comes from Shannon Wilson who claims to be working for Mobility Research Inc. It is a company providing rehabilitation solutions for physically disabled patients. The email urges recipients to help the company find a cure for the coronavirus by enrolling in the Folding.@Thome program.
Mobility Research does in fact have a project known as Folding@home, which lets participants donate computing power for disease research and computational drug design by downloading a particular app. As you can see the social engineering tactics the cybercriminals use are very clever. Even if victims did go online and tried to confirm the information in the email, they would not suspect a thing.
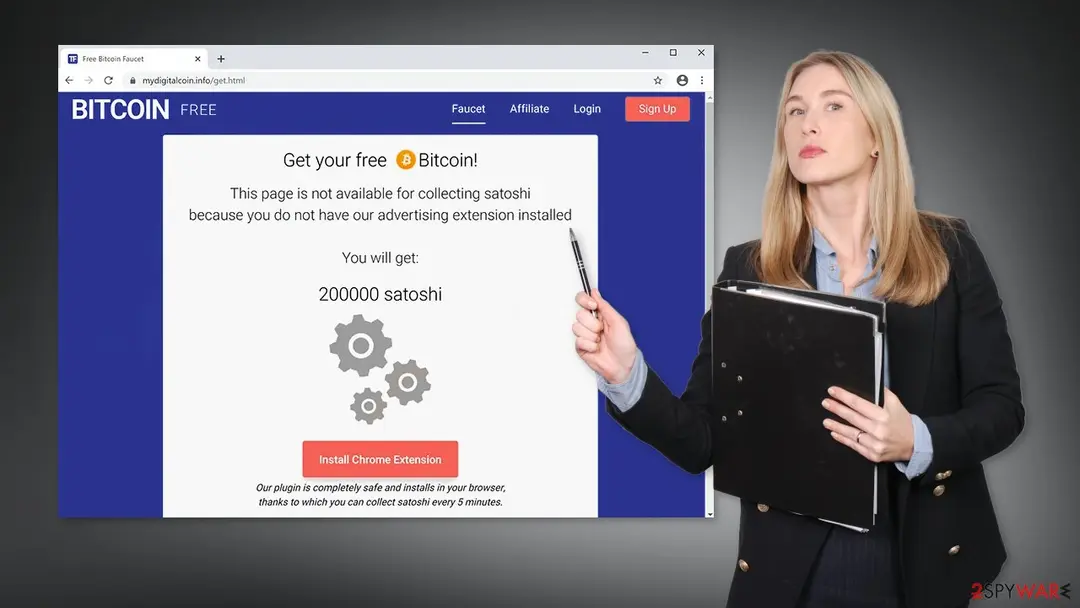
Researchers also found a scam website mydigitalcoin.info that was used to promote the malicious program:
Here users are tempted with an attractive offer:
Supposedly, all that users have to do is just install a simple Chrome extension and they will receive free Bitcoin for doing nothing. With the craze of cryptocurrencies rising, threat actors use it to their advantage. There is no doubt that if you would click the Install button on this website you would open the doors for the virus to enter your system.
That is why you should be very careful while surfing the web, especially with email. If you do not know the person who sent the email, do not open any attachments or click on any links.
Sometimes crooks do very good research and disguise the email as it was sent from one of your contacts. So if the email came from someone on your friend list but you were not expecting it, it would be beneficial to double-check with them through a different platform.
How to check the PC for RedLine
- File:
AddInProcess.exe
How to remove RedLine
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Check where AddInProcess.exe runs from and stop it
In Task Manager (Ctrl + Shift + Esc) find
AddInProcess.exeon Processes, right-click it and choose Open file location before ending anything.Windows' own files live in
C:\Windows\System32; the same name in%AppData%, %Temp% or C:\Users\Public is an impostor. If the folder is wrong, right-click the process again, choose End task and delete the file.If it starts again within seconds, a task or another process restarts it, so run the scan step in Safe Mode. Task Manager works the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 2: Delete scheduled tasks that bring it back
Programs like RedLine add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 3: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after RedLine, its publisher or created on the day the problem started. Delete those folders, and check C:\Program Files and C:\Program Files (x86) too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 5: Scan the PC, then run the offline scan
A scan finds the parts of RedLine that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
RedLine can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Remove from Google Chrome
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.

Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.

Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.

Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.

Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.

Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.

Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.

Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.

Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.

Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.

Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.

Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.

- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.

From our report of Dec 2021 · not reviewed since
The removal process
It can be very difficult to detect and remove RedLine on time because it usually operates without showing any visible indications of its presence.
It may take weeks, or even months for the victim to notice the effects of the virus activity. If you want to prevent such threats from entering your machine in the future, you should use professional security tools.
A PC without an antivirus is like a house without a door. Anti-malware tools can remove the intruders before they can do any changes to your system. and are great tools that you can use for the full elimination of RedLine. We do not recommend performing the removal manually as you can leave some traces behind which could result in the renewal of the infection.
Some Trojan-based programs can block your security software and prevent you from accessing the settings for malware removal. If malware is not letting you use antivirus in normal mode, access Safe Mode and perform a full system scan from there:
Windows 7 / Vista / XP
Windows 10 / Windows 8
Once you reach Safe Mode, launch , , or another reputable antivirus, update it with the latest definitions and perform a full system scan to eradicate malware and all its malicious components.
- Click Start > Shutdown > Restart > OK.
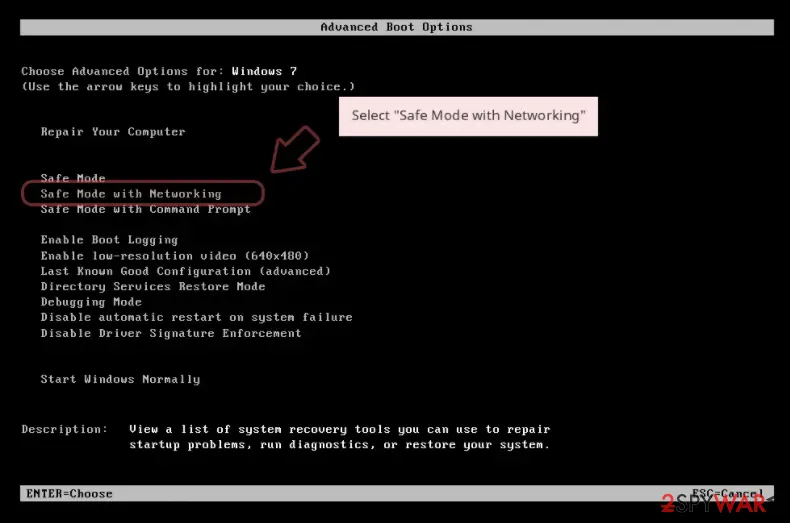
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
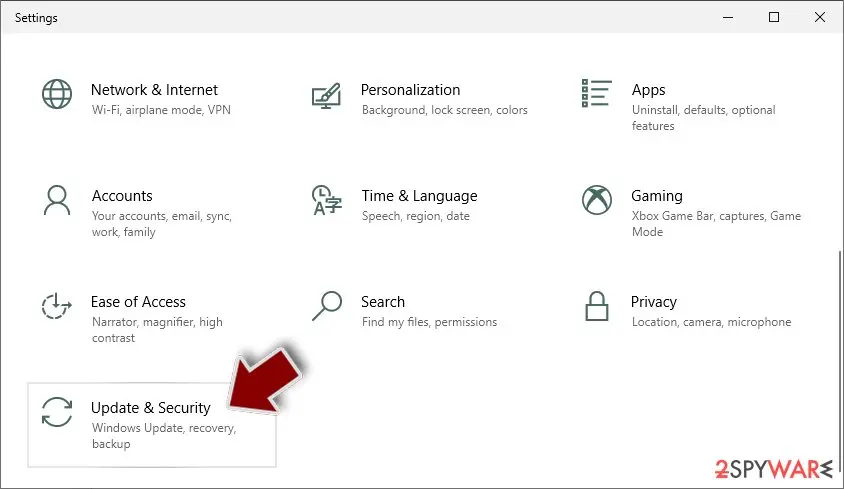
- Right-click on Start button and select Settings.
- On the left side of the window, pick Recovery.
- Click Restart now.
- Select Troubleshoot.
- Go to Advanced options.
- Select Startup Settings.
- Click Restart.
- Press 5 or click 5) Enable Safe Mode with Networking.
From our report of Dec 2021 · not reviewed since
Repair the damaged operating system
Performance, stability, and usability issues, to the point where a full Windows reinstall is required, are nothing unusual after a malware infection.
These types of intruders can alter the Windows registry database, damage vital bootup, and other sections, delete or corrupt DLL files, etc. Once a system file is damaged, antivirus software cannot fix it.
Manual troubleshooting of such damage is also very complicated and can take a long time. This is why was developed. It can fix a lot of the damage caused by an infection like this.
Blue Screen errors, freezes, registry errors, damaged DLLs, etc., can make your computer completely unusable. By using this useful maintenance tool, you could prevent yourself from having to reinstall Windows completely.
If you experience setting changes in your browsers, like the homepage, new tab address, redirects, or push notifications, you can look for instructions on how to deal with those issues below this article. There is a big chance that the malware automatically installed other threats that could cause unwanted symptoms in your browsers. Guides are available for Google Chrome, Mozilla Firefox, MS Edge, and Internet Explorer.
- Download the application by clicking on the link above
- Click on the ReimageRepair.exe
- If User Account Control (UAC) shows up, select Yes
- Press Install and wait till the program finishes the installation process
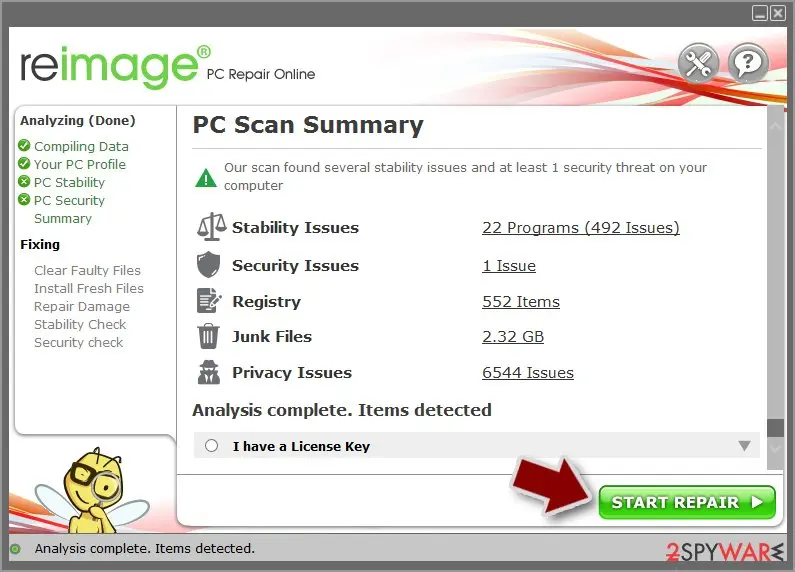
- The analysis of your machine will begin immediately
- Once complete, check the results - they will be listed in the Summary
- You can now click on each of the issues and fix them manually
After removal: passwords, accounts and prevention
Secure your accounts after the clean-up
Assume that whatever was saved in the browsers on this PC while the PC showed an unfamiliar process called AddInProcess.exe in Task Manager has been copied:
- passwords
- cookies
- autofill data
Work from a clean device, or from this PC once the offline scan finds nothing.
Start with your main e-mail account, because it can reset everything else, then banking and payment, then social and gaming accounts. Change each password, sign out of all sessions and turn on two-step verification: Turn on two-step verification / secure a hacked account.
The full order, including crypto wallets and card replacement, is in securing your accounts after malware.
Protect your privacy - employ a VPN
There are several ways how to make your online time more private - you can access an incognito tab.
However, there is no secret that even in this mode, you are tracked for advertising purposes. There is a way to add an extra layer of protection and create a completely anonymous web browsing practice with the help of VPN. This software reroutes traffic through different servers, thus leaving your IP address and geolocation in disguise.
Besides, it is based on a strict no-log policy, meaning that no data will be recorded, leaked, and available for both first and third parties. The combination of a secure web browser and VPN will let you browse the Internet without a feeling of being spied or targeted by criminals.
No backups? No problem. Use a data recovery tool
If you wonder how data loss can occur, you should not look any further for answers - human errors, malware attacks, hardware failures, power cuts, natural disasters, or even simple negligence.
In some cases, lost files are extremely important, and many straight out panic when such an unfortunate course of events happen. Due to this, you should always ensure that you prepare proper data backups on a regular basis.
If you were caught by surprise and did not have any backups to restore your files from, not everything is lost. is one of the leading file recovery solutions you can find on the market - it is likely to restore even lost emails or data located on an external device.
Questions about RedLine
Is AddInProcess.exe a virus?
The name AddInProcess.exe is not enough to say. Malware often uses technical-sounding names, and harmless updaters often use odd ones. Check three things:
- the folder the file runs from
- the Digital Signatures tab in its properties
- the program that starts it (Startup apps, Task Scheduler or services)
A signed file from a company whose product you use is almost certainly fine. An unsigned file in a user folder that no installed program explains should be removed, and the PC scanned with Microsoft Defender in offline mode.
Can I end AddInProcess.exe in Task Manager?
Ending an unknown process is safe in the sense that Windows will warn you before you close anything critical, and a restart brings back whatever Windows needs. Ending AddInProcess.exe will not remove it, though: if a task or startup entry launches it, it returns at the next sign-in.
Use ending the process as a test. If something important stops working, it belonged to a program you use. If nothing changes and it comes back by itself, find and disable its starter, delete the file and scan the PC.
I found AnyDesk or ScreenConnect that I did not install. Is that RedLine?
Not necessarily RedLine, but it is a warning sign. These are legitimate remote support tools, and criminals use them as ready-made backdoors, especially after tech support scams or fake invoice calls.
If you did not install it and no one you trust set it up, uninstall it, change passwords from a clean device and check your bank account. If someone connected to your PC through it, follow the steps for remote access trojans and consider a Windows reset. Installed apps sorted by date shows when it appeared.
How do I know if my PC has RedLine?
Often you do not, which is the point of a trojan. Possible signs are an antivirus alert naming RedLine or a generic trojan detection, unknown programs or scheduled tasks, processes with random names in Task Manager, browser extensions you did not add, security settings turned off, slower performance, or account alerts about logins from unknown places.
The reliable check is a full scan followed by Microsoft Defender's offline scan. If you recently ran a crack, a fake installer or a command a website told you to paste, scan even without symptoms.
Do I need to reinstall Windows to get rid of RedLine?
Usually not. A thorough clean-up is enough when the offline scan finds nothing afterwards and you do not see an unfamiliar process called AddInProcess.exe in Task Manager again. A reset is the safer choice if an attacker had remote control, if security tools were switched off, or if detections come back after every clean-up.
Windows 11 can reset itself without a USB stick under Settings > System > Recovery > Reset this PC. Copy documents and photos out first and scan the copies. A reset does not change passwords or undo stolen data, so the account steps still apply.
Should I check my other computers too?
Yes, it takes little time and removes doubt. RedLine itself usually stays on one PC, but the download that carried it may have been copied to other computers, shared drives may hold the same installer, and an attacker who had access could have tried saved passwords on other devices.
Run a full scan on every Windows PC in the home or office, check shared folders for the original download, and change Wi-Fi and router passwords if they were stored on the infected machine.
Can I keep using the PC while RedLine is on it?
Not for anything that matters. As long as the program behind an unfamiliar process called AddInProcess.exe in Task Manager runs, it can see what you type and what the browser stores, and it may download more malware. Disconnect the PC from the internet while you remove it, and do your banking, e-mail and password changes from another device.
Once the offline scan finds nothing and the sign does not return after a few restarts, normal use is fine. If the scan keeps finding new items, or you cannot remove the startup entry, a reset of Windows is the safer choice.
Should I report RedLine?
Report it if you lost money, if accounts were taken over, if you are a business, or if the trojan came through a scam call. A police or national cybercrime report gives you a reference number for your bank and insurer and helps link cases.
You do not need to report a trojan that antivirus blocked before it ran. Before reporting, write down the dates, the detection name, file names and any messages or transactions linked to the attack; screenshots of antivirus alerts are useful evidence. The country list is in the report section above.
Why can't I find RedLine in antivirus databases?
Because it is new or because it is listed under a different name. Antivirus companies name threats after the family they belong to, and a program that appears as RedLine on your PC may carry a generic or unrelated label in their databases.
Many new samples are first detected only by behaviour, without a family name. What you saw, an unfamiliar process called AddInProcess.exe in Task Manager, is enough to act on:
- end the program
- remove its startup entry
- run a Microsoft Defender offline scan
- secure your accounts
A detection name from a scan is worth noting for later.
Will Fortect remove RedLine?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For RedLine, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Educba: What is FTP? (read October 6, 2026)
- Makeuseof: What Is Malware-as-a-Service? (read October 6, 2026)
- Confluence: What is Bitbucket? (read October 6, 2026)
- Microsoft: What is a DLL (read October 6, 2026)
- Wikipedia: Blue screen of death (read October 6, 2026)