
ThinkPoint: what it is and how to remove it
ThinkPoint virus is a rogue anti-spyware program that usually comes into Windows after users get tricked by the fake Microsoft Security Essentials Alert. It is promoted through e-mail phishing and P2P (peer-to-peer) networks and often comes along with Trojans and exploit kits.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
An automatic scan can look at hotfix.exe and the other programs installed around the same time.
Do it yourself · free Remove ThinkPoint yourself 5 steps, about 15 minutes, no software needed.
Start the steps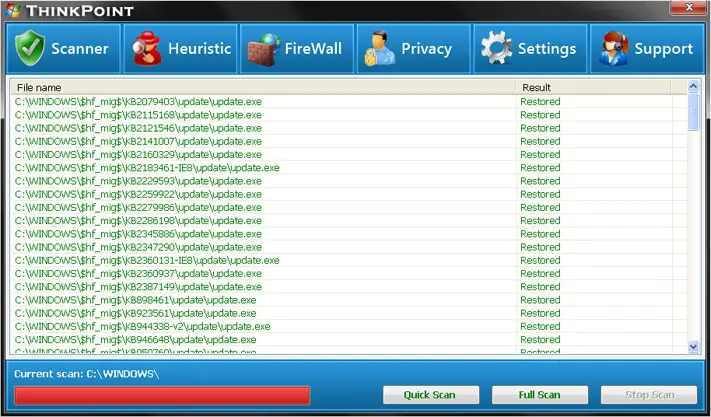
ThinkPoint: summary
| Detection names | No Microsoft detection name is known |
|---|---|
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Name | ThinkPoint |
| Type | Rogue antivirus |
| Symptoms | An unknown process in Task Manager |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 4 more facts
| Files and processes | hotfix.exe |
|---|---|
| Evidence | One write-up by a security site; details still limited |
| First seen | 9 March 2021 |
| Facts checked | 7 October 2026 |
Is ThinkPoint a real security program?
- File:
hotfix.exe
From our report of Mar 2021 · not reviewed since
ThinkPoint is a fake anti-malware you should never trust
ThinkPoint virus is a rogue anti-spyware program that usually comes into Windows after users get tricked by the fake Microsoft Security Essentials Alert.
It is promoted through e-mail phishing and P2P (peer-to-peer) networks and often comes along with Trojans and exploit kits.
Once installed, the rogue program will prompt you to restart your computer because of the supposedly found malware on your computer.
As evident, the main goal of this malicious software is to monetize users by using scam and fraud techniques. Thus, once victims are convinced that their PCs are infected with malware, they might panic and end up buying rogue anti-virus software.
What users might believe that they are paying for is a virus removal program, but in reality, they would not only be scammed out of their money but also install a virus on their systems. Not to mention that crooks behind ThinkPoint might steal credit card information and use it for malicious purposes, resulting in financial losses to victims.
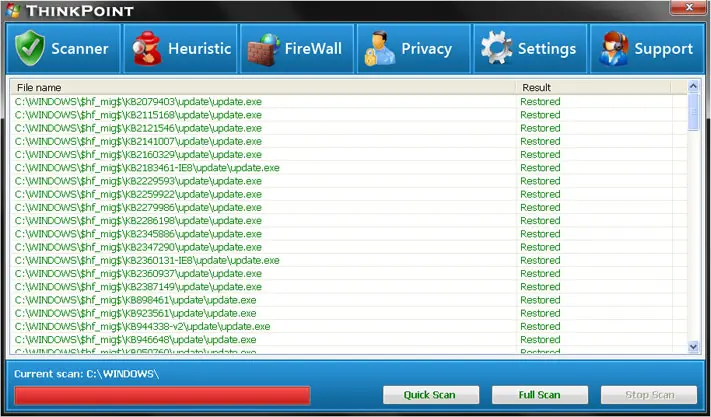
During the operation of the ThinkPoint virus, you are likely to see various pop-up messages - here are a few examples:
Even if you try scanning your computer online, it remove any infections from your computer because they are simply non-existent. If you do not purchase the full version of the program, it may start dropping threatening messages that the computer is supposedly bombarded with viruses trying to get in.
However, you should not be deceived because it is merely a scareware program, using social engineering techniques to trick people into bringing easy profit for this virus creators. You should take action as soon as you notice this program or its threatening notifications on your device.
ThinkPoint removal instructions provided at the end of this article. However, it is always advisable scanning your computer with a reliable antivirus tool, such as to delete the rogue program automatically.
While running, ThinkPoint will block legit programs on your computer. It will block task manager, registry editor and other tools too claiming that these tools were block due the security reasons and might be infected with malicious code. The main process of the virus is usually called hotfix.exe or thinkpoint.exe.
You will have to end this process first and then either remove ThinkPoint-related files manually or use an automatic removal tool. One possible way is to reboot your computer in safe mode with networking and download an automatic removal tool and run a quick system scan or manually delete ThinkPoint files listed below.
It seems like the malicious app allows you to run only Internet Explorer, but in some cases it might allow you to run other web browsers as well.
From our report of Mar 2021 · not reviewed since
More from our earlier report on ThinkPoint
- Microsoft Security Essentials detected potential threats that might compromise your privacy or damage your computer.
- Your access to these items may be suspended until you take action.
How to remove ThinkPoint
Nothing it reports is real.
These steps remove it and undo a payment if you made one.
Step 1: Do not pay, and undo a payment if you made one
ThinkPoint reports problems to sell a licence: the "threats" or "errors" it lists are invented or harmless leftovers. If you already paid, ask your card issuer to dispute the charge and cancel the subscription both in the seller's account and through your bank.
If you called a phone number it showed and let someone connect, treat the PC as remotely accessed and remove the remote tool. Uninstalling it from Windows 11 or Windows 10 does not cancel a subscription by itself.
Full procedure with screenshots: What to do after paying a scammer
Step 2: Uninstall programs you did not mean to install
Open Settings > Apps > Installed apps in Windows 11, or Settings > Apps > Apps & features in Windows 10, and sort the list by install date. Look at what appeared around the day the problem started and uninstall every program you do not recognise or did not choose.
Free converters, PDF and video tools, "system optimizers" and unknown browsers are the usual carriers of ThinkPoint. If a name is unclear, search for it before you remove it, so you do not uninstall a driver or a Windows component.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 3: Remove it from startup
Whatever ThinkPoint installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 5: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Remove from Google Chrome
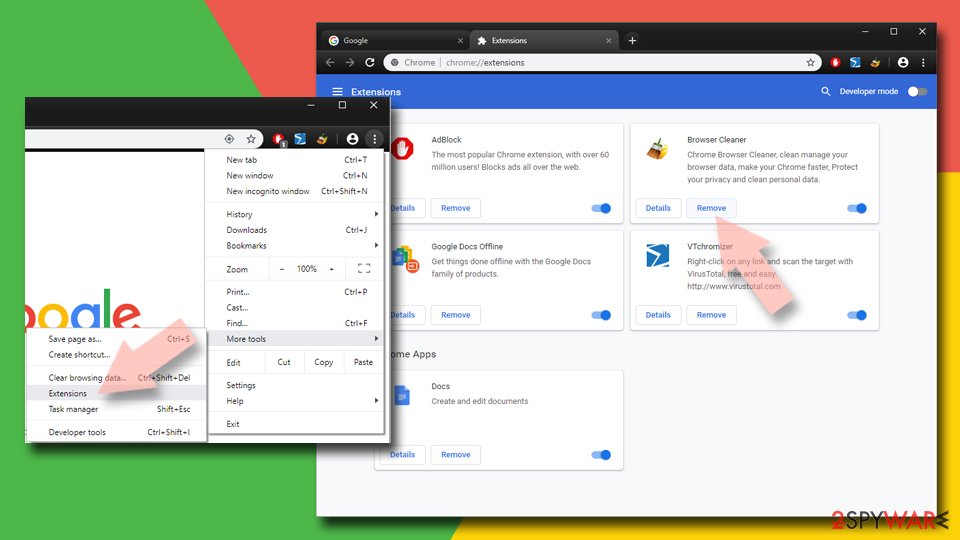
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
Clear cache and web data from Chrome:
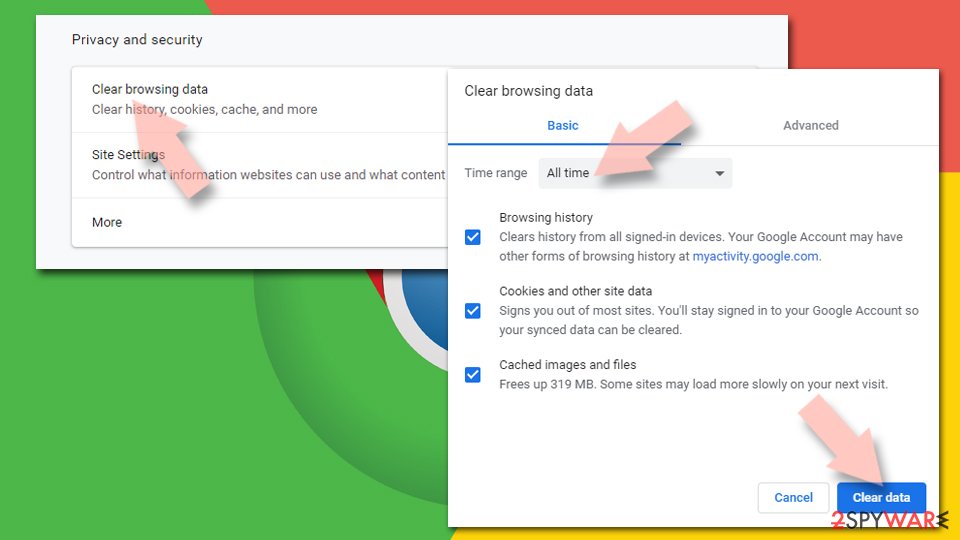
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.
Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.
Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.
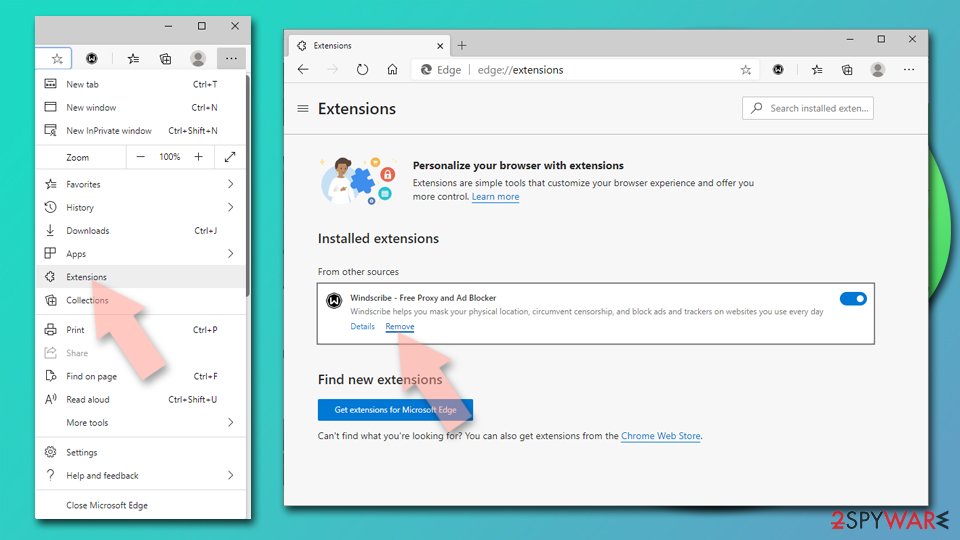
Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
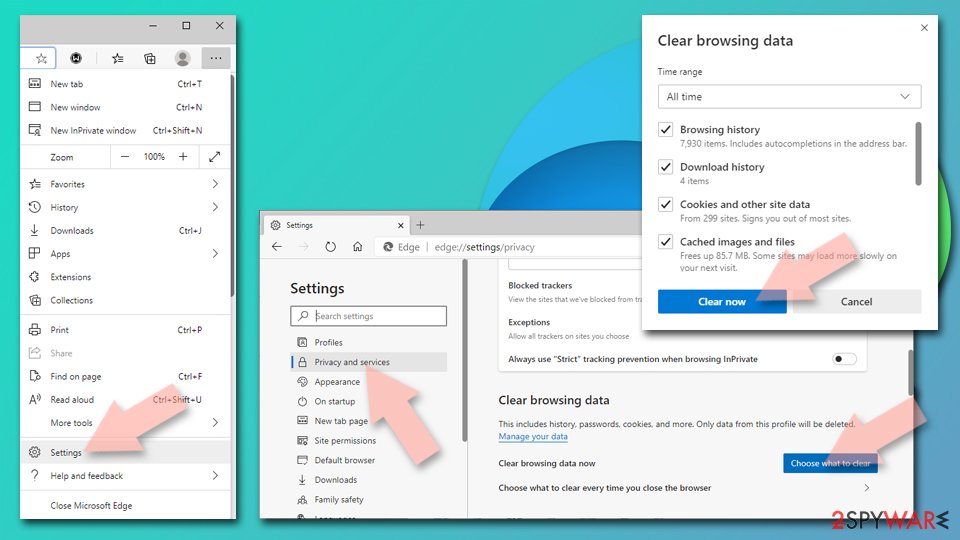
Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
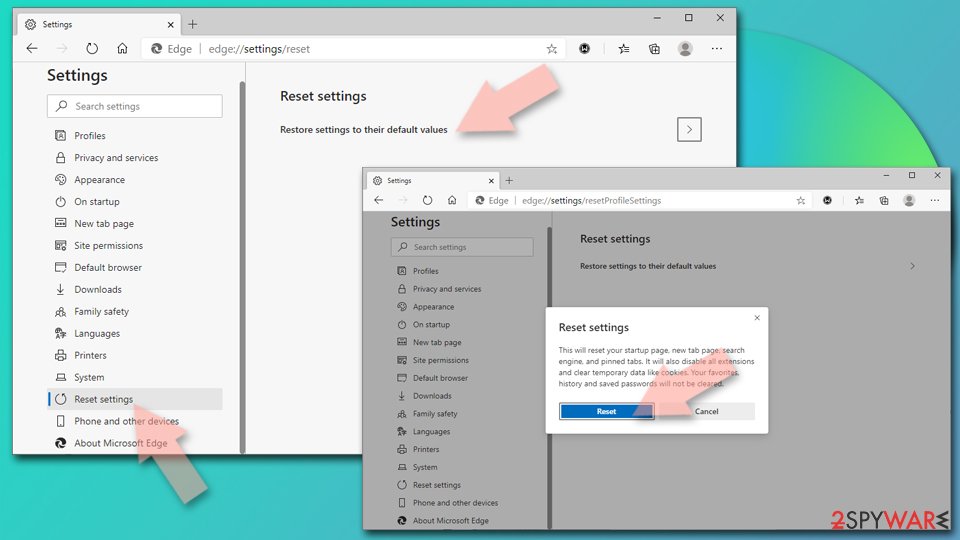
Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.
Remove from Mozilla Firefox (FF)
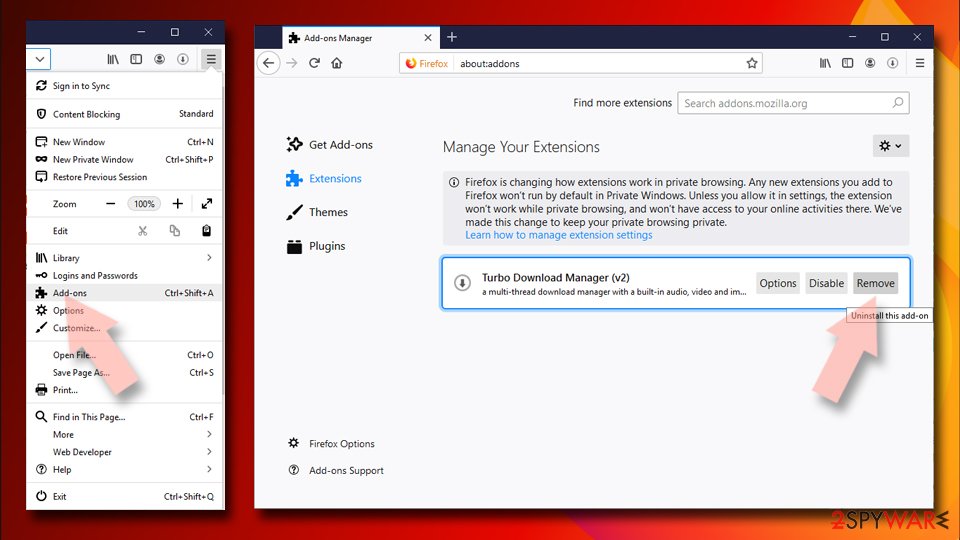
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
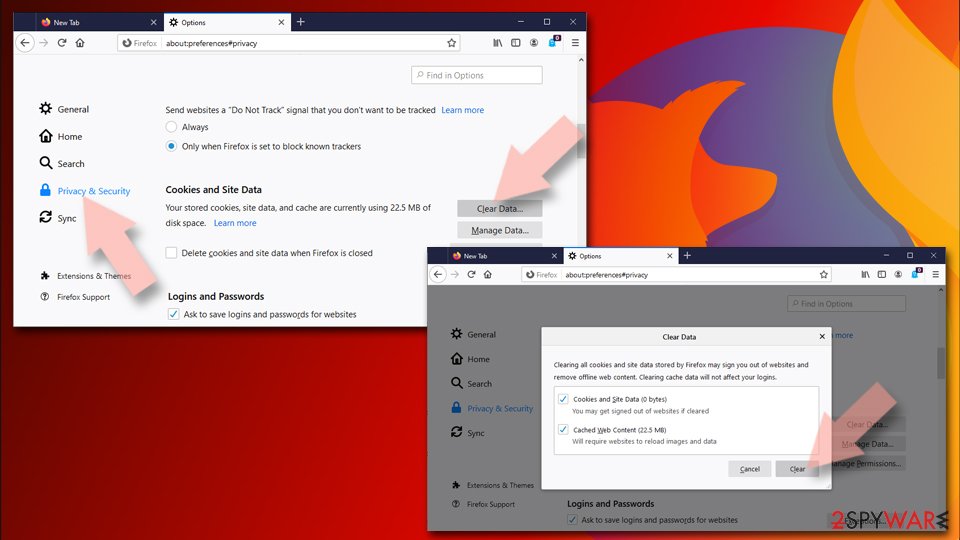
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
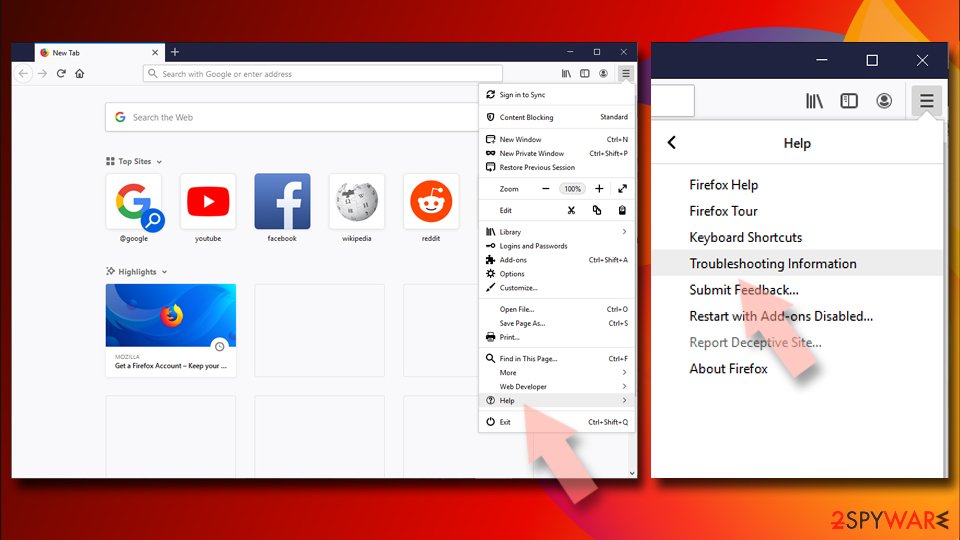
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
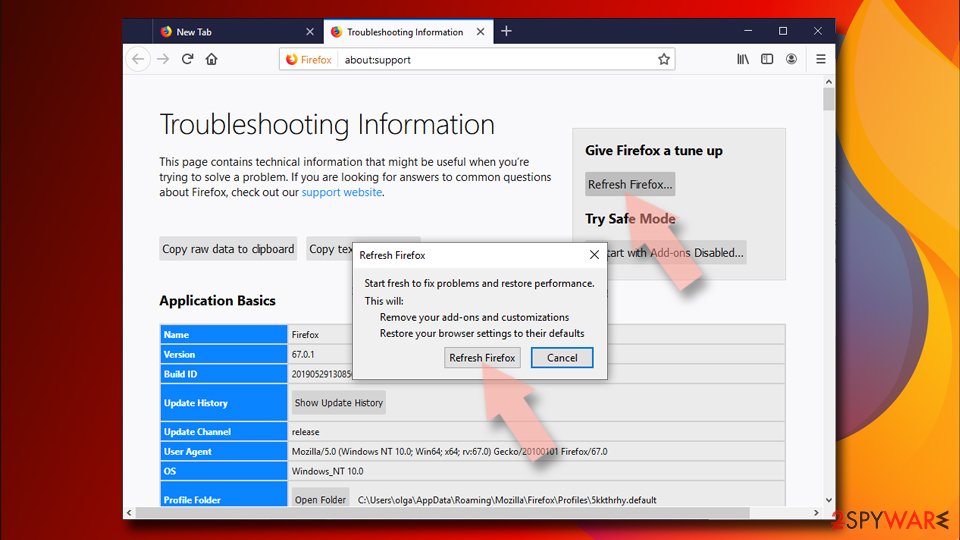
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
Remove dangerous extensions:
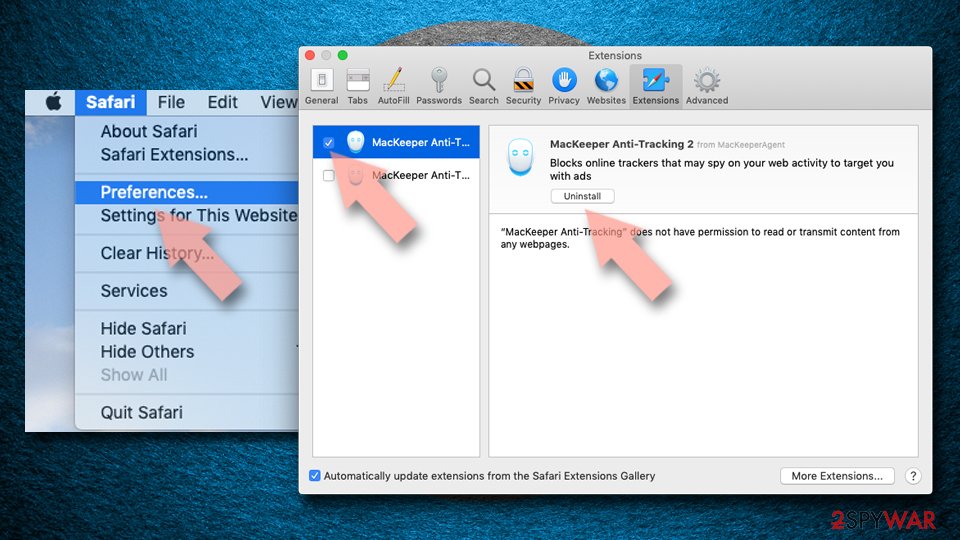
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
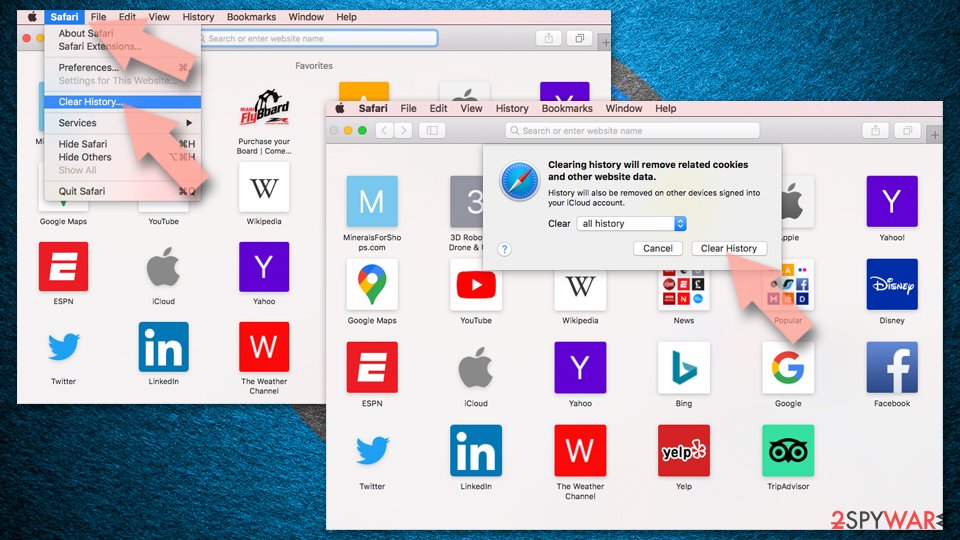
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
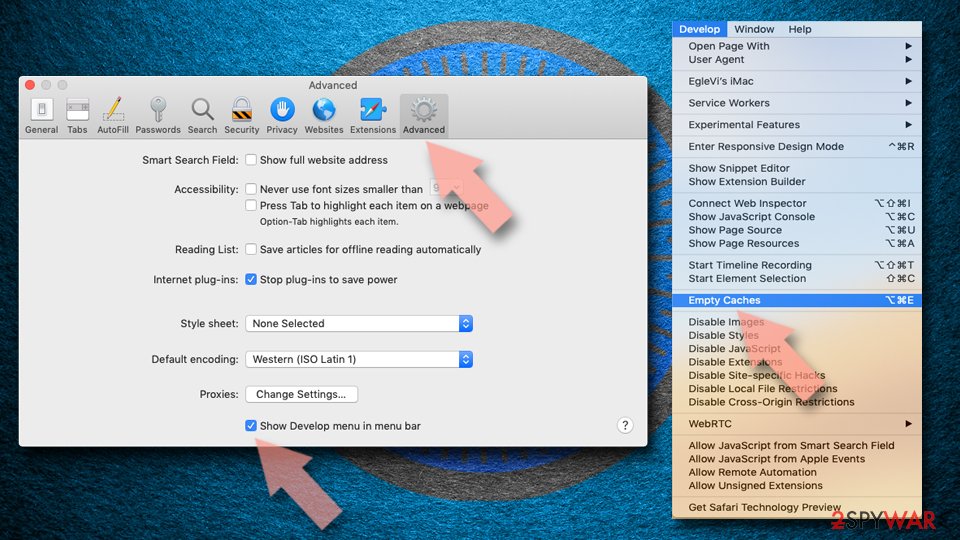
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
From our report of Mar 2021 · not reviewed since
ThinkPoint removal guide
As you can see, ThinkPoint is nothing more but a scam.
It reports fake infections and prompts to pay for a full version of the program to remove them. The problems that the reported infection do not even exist. Also, this rogue program significantly diminishes the computer's performance, so you may also start encountering different system errors too.
If you have already bought this rogue program, then you should contact your credit card company and dispute the charges. Finally, please use an automatic removal tool given below to remove ThinkPoint from your computer or delete its files manually.
Before you remove this infection, you have to recover the Internet connection if you have problems with that and end all processes associated with ThinkPoint malware. Otherwise, you will not be able to run any anti-spyware/virus software.
From our report of Mar 2021 · not reviewed since
Disable proxy server for LAN in Internet Explorer or use another browser, for example, Firefox or Opera.
How to disable a Proxy server for LAN in Internet Explorer:
NOTE: Do not reboot your computer after using Process Explorer and terminating ThinkPoint processes. Also, don't forget to clean your web browsers as explained below.
- Open Internet Explorer. Click on the Tools menu and then select Internet Options.
- In the Internet Options window, click on the Connections tab. Then click on the LAN settings button.
- Now, you will see the Local Area Network (LAN) settings window. Uncheck the checkbox labeled Use a proxy server for your LAN under the Proxy Server section and press OK.
- Now download renamed Process Explorer (explorer.com) and terminate ThinkPoint processes. Should be hotfix.exe and thinkpoint.exe.
Questions about ThinkPoint
Is hotfix.exe safe?
It depends on where the file is and who signed it, not on the name. Open Task Manager, go to the Details tab, right-click hotfix.exe and choose Open file location. A file inside Program Files or System32 with a valid digital signature from a known company is usually part of a legitimate program.
A file in AppData, Temp or ProgramData with no signature, especially one that restarts itself after you end it, is suspicious. If you cannot tie the process to anything you installed, uninstall recent unfamiliar programs and run a Microsoft Defender Offline scan.
Can I end hotfix.exe in Task Manager?
Ending an unknown process is safe in the sense that Windows will warn you before you close anything critical, and a restart brings back whatever Windows needs. Ending hotfix.exe will not remove it, though: if a task or startup entry launches it, it returns at the next sign-in.
Use ending the process as a test. If something important stops working, it belonged to a program you use. If nothing changes and it comes back by itself, find and disable its starter, delete the file and scan the PC.
What if I paid ThinkPoint?
Contact your bank or card issuer the same day, explain that the payment went to a fake security program and ask for a chargeback. Keep screenshots of an unfamiliar process called hotfix.exe in Task Manager, the payment receipt and any e-mails.
If you gave card details in the program, ask the bank to block and replace the card. Then uninstall the program and run a full scan in Windows Security. If you also called a number and let someone connect to your PC, uninstall the remote-access tool they used and change your passwords from another device.
Do I need to buy antivirus after removing ThinkPoint?
No. Windows 11 and Windows 10 include Microsoft Defender in Windows Security, which provides real-time protection, scheduled scans, the offline scan and protection against unwanted apps at no cost. Keep it switched on and updated, and turn on Reputation-based protection under App & browser control.
If you prefer a third-party product, buy it from the vendor's own site after reading independent test results, never from a pop-up or a phone call. The lesson of ThinkPoint is that security offers which arrive unasked are the ones to avoid.
Is ThinkPoint a real Windows warning?
No. Real Windows Security notifications appear in the notification area and in the Windows Security app, use Microsoft's design and never ask you to call a phone number or pay to fix anything. What people report is an unfamiliar process called hotfix.exe in Task Manager, drawn by a program that copies the look of a system message.
Open Windows Security from the Start menu to see the real status of your PC. If it shows no threats while the window keeps appearing, the window itself is the problem, and the plan in this guide removes the program that shows it.
I let a technician connect to my PC because of ThinkPoint. Is it safe now?
Not until you check. While connected, the caller could install other programs, create a user account or look at saved passwords. Disconnect from the internet, uninstall the remote access program and anything else installed during the call, and run a full scan and the Microsoft Defender offline scan.
From another device, change your e-mail and banking passwords and turn on two-step verification. If the caller opened your online banking, call the bank today. A reset of Windows is the safest option if you cannot tell what was done.
Should I reset my PC because of ThinkPoint?
Only if the signs point to deeper access. Reset when you see an unfamiliar process called hotfix.exe in Task Manager again after removal, when Windows Security cannot start or update, when remote access tools you did not install keep appearing, or when you simply cannot trust the PC any more.
Otherwise, the plan in this guide plus an offline scan is enough. If you do reset, choose Remove everything and Cloud download for a fresh copy of Windows, restore only documents and photos, and reinstall programs from their official sites. Change important passwords from the clean system afterwards.
What is ThinkPoint?
ThinkPoint virus is a rogue anti-spyware program that usually comes into Windows after users get tricked by the fake Microsoft Security Essentials Alert. It is promoted through e-mail phishing and P2P (peer-to-peer) networks and often comes along with Trojans and exploit kits.
The summary table at the top of this guide lists the type, the detection names, the symptoms and the damage of ThinkPoint. Reading it first helps you decide whether your computer shows the same signs. The removal plan below it works in order, from the safest step to the more thorough ones.
Will Fortect remove ThinkPoint?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For ThinkPoint, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- FTC: How to recognize, remove and avoid malware (read October 7, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 7, 2026)
- Microsoft Learn: How Microsoft names malware (read October 7, 2026)