
TR/Crypt.XPACK.Gen: what the Avira alert means and how to handle it
TR/Crypt.XPACK.Gen is the name Avira products give to a file that matches a generic trojan rule; it is not a program you can uninstall and it is often a false positive. Check the file's path and origin first, then follow the scan and removal steps.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If an Avira alert for TR/Crypt.XPACK.Gen on a file keeps coming back after uninstalling, a scan can find what reinstalls it.
Do it yourself · free Remove TR/Crypt.XPACK.Gen yourself 5 steps, about 15 minutes, no software needed.
Start the steps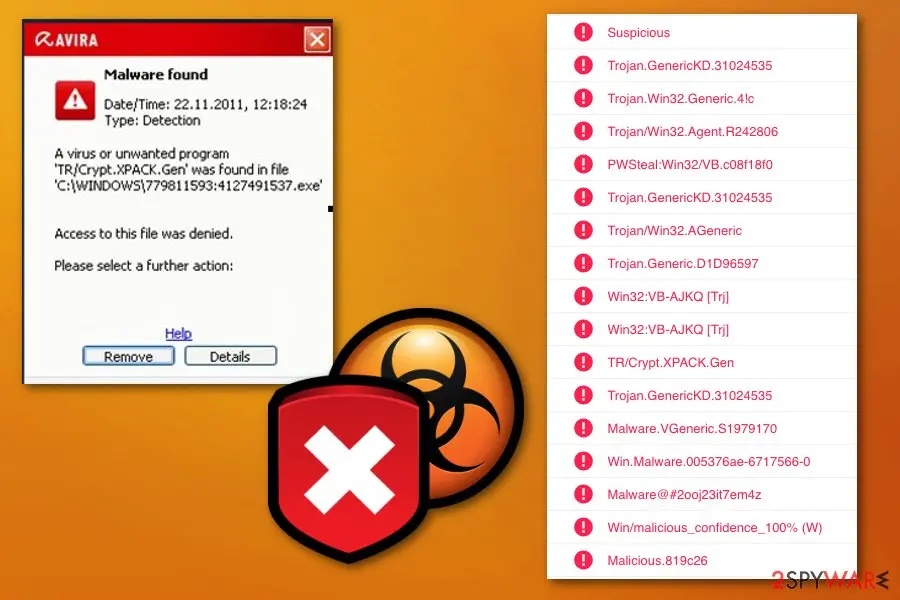
TR/Crypt.XPACK.Gen: summary
| Type | An Avira detection name for generic trojans; not a program name |
|---|---|
| Risk | Unknown for the name: no payload is documented for it. Cases range from false positives on games and developer tools to the trojan PCrisk describes. Treat as medium until the path and origin are checked |
| Symptoms | An Avira alert naming a file, often with the file quarantined or removed; a program that broke after the removal in one 2013 case; no other sign in most cases |
| How to get rid of it | Check the path and origin, send a false positive to Avira, or use Safe Mode, a full scan, Windows Security, Microsoft Defender Offline and Windows updates |
| Our check (6 October 2026) | No PC test: we read Avira's support page, three 2013 forum threads, AV-Comparatives' 2024 test, PCrisk and Microsoft help pages; no sample was run |
| Running since / first seen | No vendor date; forum reports from March 2013, our first guide from 7 May 2019, and the name was still produced in AV-Comparatives' September 2024 test |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Detection | Avira: TR/Crypt.XPACK.Gen. On PCrisk's sample: Avast Win32:VB-AJKQ [Trj], BitDefender Trojan.GenericKD.31024535, ESET a variant of Win32/Packed.EnigmaProtector.J suspicious, Kaspersky HEUR:Trojan.Win32.Generic. No Microsoft detection name is known for this label |
|---|---|
| Shown by | Avira products; Avira Free Security 1.1 in the 2024 test |
| Not to be confused with | Other vendors' labels for the same file and Microsoft's Trojan:Win32/ names, which are other detections |
| Name | TR/Crypt.XPACK.Gen |
| Evidence | 0 write-ups by security sites; details still limited |
| First seen | 7 May 2019 |
| Distribution | Typically fake installers, cracked programs, e-mail attachments, fake "verify you are human" pages and ads for popular apps |
| Damage | Installs other malware, often several programs at once |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against Avira's support article on false positives, PCrisk's page updated on 5 June 2025, AV-Comparatives' September 2024 false alarm test, three forum threads from 2013 and four Microsoft pages. We ran no sample and tested no PC; the removal steps follow those pages and were not tried on a live infection. Not confirmed:
- what Crypt and XPACK stand for
- any payload for the name itself
- how files with this name arrive in most cases
The Avira threat page quoted on a Steam forum and a Reddit thread were not opened by us.
What TR/Crypt.XPACK.Gen is, and what it is not
TR/Crypt.XPACK.Gen is a name that Avira security products show when a file matches one of their generic rules. It is not the name of one program, so there is nothing to find in the Apps list, and the name alone does not say what the file does or whether the alert is right.
- 1
Avira's own wording
A 2013 Steam forum post quotes Avira's threat description for the name: a generic detection routine designed to detect common family characteristics shared in several variants, developed to detect unknown variants and enhanced continuously. A rule written for the traits of a family will sometimes match files that only look like it.
- 2
Trojan
PCrisk files the name as a Trojan and says such programs are typically designed to steal personal details or to spread other malicious programs such as ransomware. It describes it as a generic name for threats that Avira classes as unknown trojans.
- 3
Crypt, XPACK and Gen
We found no Avira page we could read that explains what Crypt and XPACK stand for, so we do not guess. Gen is the part that marks the name as generic, one label for many files.
- 4
What our 2019 guide got wrong
It said the file can be part of Microsoft or of the Windows operating system itself, and that the name can be linked with worms. The reports we read name a game's DLL, a developer's tool and a vendor's installer files, not a Windows file, and we found no source that ties the name to worms. We kept the idea that a clean file can carry the label and rewrote the rest as what the reports show.
- Shown by
- Avira products; AV-Comparatives' September 2024 false alarm test lists the name for Avira Free Security 1.1
- Usual form
- TR/Crypt.XPACK.Gen with no suffix; the alert names a file and a path
- Platform
- Windows: every report we read names a Windows file (.exe, .dll)
- Is it a file?
- Yes: unlike a website alert, it names a path, such as the one in the old Avira window in our picture
- Not the same as
- The names other vendors give the same file (table in the next chapter) or Microsoft's own Trojan:Win32/ names, which come from other detection rules
The label tells you how one vendor classed a file, not what the file does. The chapters that follow help you decide, from the path and where the file came from, whether the alert was right.
What TR/Crypt.XPACK.Gen does on an infected PC
TR/Crypt.XPACK.Gen and what other vendors call the same sample
Every antivirus names a file by its own rules. PCrisk's page, updated on 5 June 2025, lists the names that four other engines give one sample with the SHA-256 hash da60bad3bd8de8a4e163c0358d2729f72d8ced37ff3c754e9bd102fcdb33db39.
| Engine | Name for that sample | What it tells you |
|---|---|---|
| Avira | TR/Crypt.XPACK.Gen | A generic rule for unknown trojans; this is the name on this page |
| Avast | Win32:VB-AJKQ [Trj] | A trojan label: the Trj tag in brackets marks it as a trojan |
| BitDefender | Trojan.GenericKD.31024535 | A generic trojan label that ends in a number; the old picture shows it three times |
| ESET-NOD32 | a variant of Win32/Packed.EnigmaProtector.J suspicious | Names the packer wrapped around the file rather than what it does; we found no page that explains how ESET uses the word suspicious |
| Kaspersky | HEUR:Trojan.Win32.Generic | Another generic label, so even this vendor does not name a specific family |
Two things follow. When a sample reaches researchers, each vendor names it by its own scheme, which is why a file can carry a specific name in one product and a generic one in another. And the name TR/Crypt.XPACK.Gen is Avira's only: if your other security tool shows a different label for the same file, that is not a second opinion that it is clean.
What we checked on 6 October 2026, and what we could not
There is no website to test here and we did not run a sample. We read Avira's support page, three forum threads from 2013, AV-Comparatives' 2024 test, PCrisk's page and Microsoft's help pages, and we ran nothing on a PC.
Our reading of the sources, 6 October 2026
- The detection still existsAV-Comparatives' False Alarm Test of September 2024 lists TR/Crypt.XPACK.Gen for a clean package called Comsytec, found by Avira Free Security 1.1. We read the page through an automated reader.
- Avira's own descriptionQuoted in a Steam post of 26 March 2013 as a generic detection routine for unknown variants. We did not open the Avira page that the post links to, so we cite the post.
- What the file isNot known from the name. Reports range from a game's DLL to a development tool, and PCrisk's table lists the sample's other names as trojan labels.
- Real infection or false positiveNot settled by the name. National Instruments said in August 2013 that its file was a false positive and AV-Comparatives lists the name for a clean package, yet PCrisk says the trojan behind it spreads by spam e-mail, ads and software cracks.
- What Crypt and XPACK meanNot found in any Avira page we could read.
- A clean second scanDoes not clear it. A file can be removed before it runs, and a clean rescan says only that nothing else matched at that moment.
Check where the file came from before you decide One alert can be a false alarm, a blocked download or the trace of an infection. Write down the path, find out where the file came from, then follow the check and removal chapters. We tested nothing on a live PC, so a clean scan is one data point only.
How readers met the name, from 2011 to 2025
Our guide dates from 7 May 2019. The pictures are from it, and the other entries are forum and test pages we read for this rewrite.
22 November 2011
The date on the alert in our picture
The Avira window in our 2019 guide shows 22.11.2011, 12:18:24 and a file in the C:\WINDOWS folder with a long numeric name. We do not know who captured it or what the file was.
From our 2019 guide: an Avira window of an older design, dated 22.11.2011 on its face, next to a list of detection names. We did not take this screenshot and do not know where the file in it came from, so it shows what the alert looked like, not that the file was malicious. 25 March 2013
A game's DLL flagged on a Steam forum
A player wrote that Avira flagged nvtt.dll in the Binaries folder of BioShock Infinite right after the game was unpacked and quarantined it. Others reported the same alert, one thought it a false positive, and one wrote that a product update of Avira changed two files and the alarm went away.
18 June 2013
A program broken after Avira removed the file
A user of Enterprise Developer Personal Edition for Visual Studio wrote that the program worked until Avira detected TR/Crypt.XPACK.Gen and eliminated it. Afterwards the program showed errors, among them Error 1068, and said it could not communicate with the licensing daemon.
9 August 2013
A National Instruments installer
A user installing LabWindows/CVI 2013 asked whether Avira's alert on iw.exe in the cvi2013 bin folder was real. National Instruments wrote that it was confident of a false positive, probably tied to the new compiler in that release, and that the antivirus companies would fix it in their next update.
7 May 2019
Our first guide
We described the name as a generic result that can be a false positive and that sometimes covers trojans, and we showed the Avira window.
The other picture of our 2019 guide: the same Avira window and list with the title and a stock photo of a woman shrugging. The woman is decoration, not a victim or an analyst. September 2024
Still produced on clean files
AV-Comparatives lists TR/Crypt.XPACK.Gen among the 15 false alarms of Avira Free Security 1.1 in its September 2024 test, for a package it calls Comsytec.
5 June 2025
PCrisk's update
PCrisk updated its page and says that if Avira detected the name, it may be a false positive, while a genuine detection should be removed immediately. It names spam e-mail, malicious ads, social engineering and software cracks as the ways the trojan spreads.
False alarm or real: what the reports show
A generic name can be right, early or wrong. These are the situations the reports describe and what to do in each.
| What you see | What is going on, from the reports | What to do |
|---|---|---|
| One alert on a game or program you installed from its maker | nvtt.dll in BioShock Infinite in 2013 and iw.exe from National Instruments in 2013 were flagged and called false positives, and a game developer asked on Reddit about his own game flagged by a player's antivirus | Update Avira, scan again and send the file to Avira for analysis |
| The program stops working after Avira removed a file | A user in 2013 lost a development tool's licensing service after the removal | Restore the file only after you know it is clean, or repair the program with its own installer |
| A file you did not expect, from an e-mail, a crack or a free download | PCrisk says the trojan behind the name arrives by spam e-mail, ads and cracks | Do not run it again; treat the PC as possibly infected and use the removal steps |
| The alert repeats within minutes or returns after reboots | Something keeps putting the file back or starting it, which a false alarm on a single file would not do | Go to the removal chapter and look at what starts with Windows |
| Other scanners name the file too | On PCrisk's sample, four other engines name the file, each with its own label | Take the alert seriously and look up the file's hash |
What TR/Crypt.XPACK.Gen can steal or download
What a trojan of this kind can cost you
No source we read documents what one specific file named TR/Crypt.XPACK.Gen does. The risks below are those of trojans in general, taken from our 2019 guide and PCrisk, and they are possibilities, not findings about every alert.
- High
Remote access for someone else
Our old guide said a malicious trojan can give a malicious person remote access to the device and open backdoors for remote hackers. Any trojan that gets to run can do so, but we found no report that links these to this name.
- High
Stolen passwords, banking data and identity
The old guide said it can be set to steal passwords and banking information, collect financial information such as banking logins and lead to identity theft. PCrisk lists stolen banking information and passwords, identity theft and a place in a botnet as the damage. If you ran the file, treat passwords and bank sessions used on that PC as at risk until it is cleaned.
- Medium
Other malware brought in
The old guide said a trojan can spread other programs on the system, such as ransomware and banking information-stealing malware, and PCrisk says the same. We found no ransomware case for this name.
- Medium
Background processes
The old guide said such a program can run processes in the background of the device. That is why the removal steps look at what starts with Windows and add an offline scan.
- Low
Breaking a program that was fine
The reverse risk is real too: in 2013 a user lost a working development tool after the antivirus removed the file it flagged. Do not delete or restore a file without checking where it came from.
What you may notice, and what the reports show
PCrisk says trojans are designed to infiltrate stealthily and remain silent, so no particular symptoms are clearly visible. Here is what the reports we read actually show.
| Sign | What we found |
|---|---|
| The alert itself | Reported in every case: an Avira message naming a file and offering Remove or Details, as in our picture, often followed by quarantine |
| A program that stops working | Reported in 2013: the Enterprise Developer tool showed Error 1068 and a licensing daemon error after the removal; the player of BioShock Infinite reported that the game ran once real-time protection was off |
| The alert coming back | Not reported in the pages we read for this name; if it repeats, something puts the file back |
| Slowdowns, pop-ups, redirects | Not reported with this name in any page we read; they are a reason to scan, not proof of this detection |
| No sign at all | This is the case for a real trojan according to PCrisk, and also for a false alarm, so the silence settles nothing |
How to check the PC for TR/Crypt.XPACK.Gen
How a file with this name gets onto a PC
No vendor page we read says how every file named TR/Crypt.XPACK.Gen arrives. These are the routes our 2019 guide gave, the ones PCrisk lists and the ones the reports show.
- 1
Infected e-mail and links
Our guide said cybercriminals spread trojans and worms by spam campaigns and phishing, and that one or two clicks on the e-mail or on a link in it start the installation. PCrisk says the trojan Avira detects as this name spreads mostly through spam e-mail with malicious attachments.
- 2
The attachment itself
The old guide said a payload dropper launches malicious macros and a script loads in the background, and that the victim sees nothing. PCrisk lists Office documents, ZIP and RAR archives, .exe and JavaScript files and PDF documents as the common attachments. The opening of the file is still the step that starts it, which is why users cannot recall installing the trojan themselves.
- 3
Cracks and untrusted downloads
PCrisk adds malicious online advertisements, social engineering and software cracks, and names peer-to-peer networks, free file hosting sites and third-party downloaders as dubious sources. Auto-run on removable media is on its list too.
- 4
Nothing malicious at all
The most common case in the reports is a game, tool or installer that the user got from its maker and a scan that flagged it. Then the file is not an intruder, and the answer is a false positive report. Our old guide agreed that there is no specific information on how the name arrives, because the same name can sit on a secure and non-malicious file.
Check your PC before you delete anything
Write down exactly what the alert says before you click Remove, Details or an exclusion: the detection name, the file path and the time. A forum helper or the vendor will ask for them.
- 1
Copy the alert
Take a screenshot. Note the full name, the path and whether Avira says it blocked, quarantined or removed the file. The path taught the 2013 readers more than the name did.
- 2
Ask where the file came from
A file in Downloads, Temp or AppData that you did not knowingly save is more worrying than one inside a game or tool you installed on purpose. A path inside a program folder from a known maker points to a false positive.
- 3
Look up the file's hash
In PowerShell run
Get-FileHash "C:\path\to\file". The cmdlet computes a SHA256 value by default and the value depends only on the file's content, not on its name. Search that value on VirusTotal, as PCrisk suggests, instead of uploading a file that holds private data. - 4
Look for a second antivirus
Open Settings > Apps > Installed apps and look for another security product with live protection. Two of them can report each other's files, so keep one.
- 5
Look at what starts with Windows
Press Ctrl + Shift + Esc, open Startup apps and note names you do not know. If the alert repeats, something is starting the file again.
- 6
Ask whether you ran something new
A document, installer, crack or download from just before the first alert is the likeliest route. If you ran it, treat the PC as possibly infected and use the account steps further down.
How to remove TR/Crypt.XPACK.Gen
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Programs like TR/Crypt.XPACK.Gen add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 2: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after TR/Crypt.XPACK.Gen, its publisher or created on the day the problem started. Delete those folders, and check C:\Program Files and C:\Program Files (x86) too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
A scan finds the parts of TR/Crypt.XPACK.Gen that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
TR/Crypt.XPACK.Gen can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Remove it from Windows 11 and Windows 10
Removing a real infection should be done without delay, as our 2019 guide said, but only after you have checked that the file is not a program you installed on purpose. Do the steps in order and stop when a full scan is clean and the alert has not returned. We did not run them on a live infection; they follow Microsoft's pages and Avira's advice.
- 1
Do not delete files by hand yet
Leave the file in Quarantine. Our old guide said not to rush to delete files that may be secure, and the 2013 Enterprise Developer case shows why: removing the flagged file broke a program that had worked.
- 2
Start in Safe Mode with Networking
Open the Windows Recovery Environment, then choose Troubleshoot > Advanced options > Startup Settings > Restart and press 5 for Safe Mode with Networking. Microsoft says it adds the network drivers and services you need to reach the internet. Our old guide said this lets you scan the machine without the virus interrupting.
- 3
Update Avira and scan again
Avira's support page says to check the file again with the latest VDF update. A 2013 reader found that a product update of Avira changed two files and the alert disappeared. If the scan finds the file again, keep it in Quarantine.
- 4
Run a full scan with Windows Security
Open Windows Security > Virus & threat protection > Scan options, choose Full scan and Scan now. Our old guide said to scan with a few different anti-malware tools and to pay attention to the results; a second engine from its maker's own site is a good second opinion.
- 5
Run Microsoft Defender Offline
In the same Scan options choose Microsoft Defender Offline scan and Scan now. Microsoft says you will be signed out, Windows shuts down in under a minute and the scan runs outside the usual Windows environment for about 15 minutes before it restarts. Review the result under Protection history.
- 6
Decide on the file
If every tool names the same file and it came from an e-mail or a crack, remove it and use the account steps below. If only Avira names it and it sits inside a program you installed from its maker, go to the false alarm chapter instead.
- 7
Update Windows
Open Settings > Windows Update and install everything offered, then restart.
Be careful with software that promises to clean a PC. Fake security programs exist, and a real removal never needs a phone number from a pop-up or a payment page before the scan.
Could it be a false alarm?
Quite possibly. Avira's own support article says false positives are harmless files incorrectly identified as malicious, and that programs which behave like malware or use identical file compression and protection techniques are susceptible to them. Only the vendor can confirm that a file is clean.
| Points to a real infection | Points to a false positive |
|---|---|
| The path is in Downloads, Temp or AppData and you do not know the file | The path is inside a game or program you installed from its maker |
| The file came in an e-mail or from a crack or a keygen | The file is a developer's tool, a game's DLL or an installer you took on purpose |
| The alert repeats within minutes or after each reboot | The alert came once and Avira quarantined the file |
| Other scanners name the file too | Only Avira names it and a product update stops it |
| Files were renamed or the PC behaves strangely | The PC works normally and only the alert is odd |
- 1
Do not rush to delete
Our old guide said the detected file can be safe, that rushing into removal may cause other problems, and that the file might even be something a program needs. The 2013 Enterprise Developer thread shows it: after Avira removed the file the program failed with licensing errors and the workaround was to turn its services on again in Computer Management.
- 2
Why a safe file gets flagged
PCrisk says misleading entries in malware databases lead to false positive detections, and that criminals disguise malicious files with the names of legitimate files and processes, such as operating system files. Its page names msfeedssync.exe, gwx.exe and csrss.exe as examples. The old guide said safe files and programs, DLL or executable files, can be misused by malicious actors based on a common type or name. The reports we read are DLL and executable files; we found none where an antivirus program was flagged.
- 3
Ask more than one engine
If more than one engine names the same file as dangerous, removal is justified, our old guide said, but only without rushing. Agreement is a stronger signal than one alert, yet check the path and origin as well.
- 4
Send the file to Avira
Avira says to check the file again with the latest VDF update, and if it is still detected as malicious, to submit the suspicious file on its analysis page. National Instruments did this in 2013 and the antivirus companies fixed the detection in an update.
- 5
Exclude only when you are certain
Avira's article says that if you are certain the detected file is clean, you can set it as an exception at your own risk. We would add the vendor's confirmation first; an exception hides every later alert for that file.
- 6
A program broken afterwards
Our old guide said to fix other issues caused by corrupted files or missing parts of an application, and to try troubleshooting instead of malware removal. A system optimizer does not undo a false positive. Reinstall or repair the program from its maker's installer, with the file restored from Quarantine only if the vendor has said it is clean.
After removal: passwords, accounts and prevention
Secure your accounts after the clean-up
Assume that whatever was saved in the browsers on this PC while the PC showed an Avira alert for TR/Crypt.XPACK.Gen on a file in the list of installed apps has been copied:
- passwords
- cookies
- autofill data
Work from a clean device, or from this PC once the offline scan finds nothing.
Start with your main e-mail account, because it can reset everything else, then banking and payment, then social and gaming accounts. Change each password, sign out of all sessions and turn on two-step verification: Turn on two-step verification / secure a hacked account.
The full order, including crypto wallets and card replacement, is in securing your accounts after malware.
If it was real: what to do about your accounts
The scans above deal with the PC. These steps deal with what a trojan could have seen, and they matter most if you ran the file before the alert.
- 1
Change passwords from another device
Email first, then banking, then everything else. Turn on two-step sign-in. Do this before you use banking on the infected PC.
- 2
Sign out everywhere
Use the sign out of all sessions option in your Google, Microsoft and social accounts so stolen cookies stop working.
- 3
Check your money
Look at card statements and any wallets for payments you did not make.
- 4
Look for ransomware signs
Check whether documents were renamed or a note file appeared. If so, do not pay and do not reinstall yet; identify the family first.
- 5
Scan again in a week
A clean scan today does not clear everything. Run another full scan and a Defender Offline scan a week later, and keep the alert screenshot.
Keep trojans off your PC
Make sure to choose reliable software from an official source, our 2019 guide said, to avoid more malware and PUPs that come with insecure installers and deceptive freeware sites. PCrisk gives the same advice: official sites and direct links only.
Do
- Download programs and updates from their makers' sites or the Microsoft Store, and choose Custom or Advanced when an installer offers it.
- Open attachments only when you expected them and the sender's address matches. Be careful with ZIP, RAR, EXE, DOC and PDF files from suspicious e-mails, the types criminals misuse most.
- Clean the spam folder often and delete questionable e-mails instead of opening them.
- Keep one security product with live protection on. Microsoft Defender and the Windows Firewall are built into Windows 11 and 10.
- Install Windows Update monthly and update browsers, Office and PDF readers when patches come out.
- Keep a backup of documents on a disk you unplug (File History or OneDrive), so a wrong removal or an infection costs less.
Don't
- Do not run cracks, keygens or cracked software.
- Do not use third-party updaters; update from the program itself.
- Do not run two antivirus programs with live protection at once.
- Do not restore a quarantined file or add an exclusion until a vendor says it is clean.
- Do not call a number shown in an alert.
- Do not buy a VPN to remove a trojan: it hides your connection and does not clean a file on your PC.
TR/Crypt.XPACK.Gen is a Windows detection from Avira. A message with this name on a phone or a Mac is more likely a scam page than a real scan.
Questions about TR/Crypt.XPACK.Gen
What is TR/Crypt.XPACK.Gen?
TR/Crypt.XPACK.Gen is a detection name that Avira security products show when a file matches a generic rule for unknown trojans. It is not a program you can uninstall. A 2013 Steam post quotes Avira's description of it as a generic detection routine designed to detect common family characteristics shared in several variants.
That wording explains why the label tells you little about the file. We found no Avira page that explains the letters Crypt and XPACK. The reports we read range from a game's DLL to a development tool, so check the path and origin before you decide.
Is TR/Crypt.XPACK.Gen a virus or a false positive?
It can be either, and the name alone cannot tell you which. In August 2013 National Instruments said its iw.exe was a false positive and that antivirus companies would fix it, and AV-Comparatives lists the name for a clean package in its September 2024 false alarm test.
PCrisk, on the other hand, says the trojan behind the name spreads through spam e-mail, malicious ads and software cracks, and that a genuine detection should be removed immediately. Check the path first: a file inside a program from its maker points to a false positive; a file from an e-mail or a crack points to a real one.
How do I remove TR/Crypt.XPACK.Gen from Windows 11 or 10?
First check the file's path and origin, because deleting a clean file can break a program. If it looks real, start in Safe Mode with Networking, update Avira and scan again, then run a full scan in Windows Security and a Microsoft Defender Offline scan, and install all Windows updates.
If you ran the file, change your passwords from another device. We did not test these steps on a live infection; they follow Microsoft's help pages, Avira's support article and our 2019 guide. Do not delete the file by hand before the checks are done.
Is it safe to delete or restore the file Avira flagged?
Not until you know what the file is. Leave it in Quarantine while you check where it came from. In 2013 a user of Enterprise Developer Personal Edition lost the program's licensing service after Avira removed a flagged file, so deleting can do harm.
Restoring can too, if the file is malicious. Avira's article says that if you are certain the file is clean you can set an exception at your own risk. We suggest waiting for the vendor's answer first, and sending the file to Avira's analysis page if you think it is safe.
How do I report a false positive to Avira?
Avira's support article gives two steps: check the file again with the latest VDF update, and if the file is still detected as malicious, submit it on Avira's analysis page. Keep the file name, the path and a screenshot of the alert with your report.
National Instruments contacted the antivirus companies about iw.exe in August 2013 and wrote that they implemented a fix for their next update. Meanwhile keep the file in Quarantine rather than adding an exception, and update the product at intervals.
Why does my antivirus keep detecting TR/Crypt.XPACK.Gen again?
Something keeps putting the file back or starting it. It may be a program that restores its own files, such as a game's repair or update tool, or a real infection that copies itself from a startup entry.
Open Startup apps in Task Manager, look at the path in the alert and see whether the file belongs to a program you installed. If it does not, run the removal steps, including the offline scan. If it does, send the file to Avira as a false positive and check whether the vendor has a fixed version.
Does TR/Crypt.XPACK.Gen steal passwords or install other malware?
The name alone does not say. Our 2019 guide said a malicious trojan can steal passwords and banking information, open backdoors, run processes in the background and bring in other malware such as ransomware, and PCrisk lists stolen banking data, identity theft and botnet use as the damage.
No report we read ties those effects to one named file. If you ran the file before the alert, assume the worst:
- change passwords from another device
- sign out of your accounts
- check your money
- scan again a week later
Can other antivirus programs show TR/Crypt.XPACK.Gen?
Not under this name. It is an Avira label, and other engines name the same sample by their own rules. On PCrisk's sample, Avast shows Win32:VB-AJKQ [Trj], BitDefender Trojan.GenericKD.31024535, ESET a variant of Win32/Packed.EnigmaProtector.J suspicious and Kaspersky HEUR:Trojan.Win32.Generic.
If only one product flags a file and others stay silent, a false positive becomes more likely, but it is not proved. If several engines flag it, take the alert seriously and check the file's path, its origin and its hash before you delete anything or restore it from Quarantine.
Can a game or a Windows file be flagged as TR/Crypt.XPACK.Gen?
A game's file can: in March 2013 players reported Avira flagging nvtt.dll in BioShock Infinite, and a game developer asked on Reddit why his game was detected. A Windows file is less likely, and our 2019 guide's claim that the name can sit on a Microsoft file is not backed by a report we read.
PCrisk warns that criminals disguise malicious files with the names of operating system files such as csrss.exe. So check the path and the file's hash instead of trusting the name.
Will Fortect remove TR/Crypt.XPACK.Gen?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For TR/Crypt.XPACK.Gen, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Avira Support: What is a false positive Avira Antivirus detection? (read October 6, 2026)
- PCrisk: TR/Crypt.XPACK.Gen Virus (updated 5 June 2025) (read October 6, 2026)
- AV-Comparatives: False Alarm Test September 2024 (Avira Free Security 1.1, 15 false alarms) (read October 6, 2026)
- Steam Community, BioShock Infinite: Malware TR/Crypt.XPACK.Gen found (25 and 26 March 2013; quotes Avira's description) (read October 6, 2026)
- Rocket Software Community: TR/Crypt.XPACK.Gen (18 June 2013) (read October 6, 2026)
- NI Community: CVI2013 install, Avira detects TR/Crypt.XPACK.Gen (9 August 2013) (read October 6, 2026)
- Reddit r/antivirus: Should I be worried? Avira detects my game as TR/Crypt.XPACK.Gen (title and search excerpt only; the page could not be opened) (read October 6, 2026)
- Microsoft Support: Windows startup settings (Safe Mode) (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline scan in Windows (read October 6, 2026)
- Microsoft Support: Virus and threat protection in the Windows Security app (read October 6, 2026)
- Microsoft Learn: Get-FileHash (read October 6, 2026)