
XHAMSTER ransomware: what it is and how to get your files back
XHAMSTER ransomware is a Phobos-family file encryptor that renames your files with the ending .XHAMSTER and leaves the notes info.hta and info.txt. Do not pay: a free police decryptor for Phobos files has existed since July 2025 and may work on yours.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Before you restore backups, a full scan can confirm the program that added .XHAMSTER is gone.
Do it yourself · free Remove XHAMSTER ransomware yourself 6 steps, about 18 minutes, no software needed.
Start the steps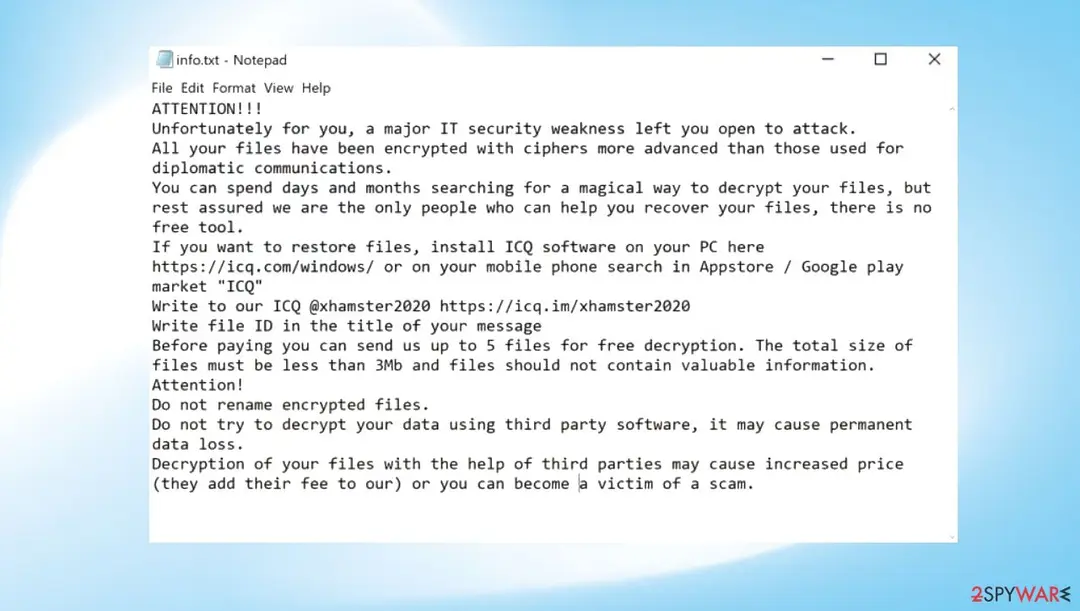
XHAMSTER ransomware: summary
| Type | File-encrypting ransomware (Phobos family) for Windows |
|---|---|
| Risk | High: files are encrypted and the notes demand payment; a free police decryptor for Phobos files may work |
| Symptoms | Files renamed .id[ID].[ICQ@xhamster2020].XHAMSTER, an info.hta pop-up and an info.txt file |
| How to get rid of it | Disconnect, scan with Microsoft Defender Offline, remove what is found, then try the free Phobos decryptor on copies; see the plan |
| Our check | Source check on 6 October 2026 (PCrisk, Japanese police guide, No More Ransom); we did not run the malware |
| First seen | Our first report 23 March 2022; Phobos itself since late 2018 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 12 more facts
| Name | XHAMSTER ransomware (XHAMSTER virus) |
|---|---|
| Encrypted file extension | .XHAMSTER, after the victim ID and the contact handle |
| Ransom note | info.hta (pop-up) and info.txt; the pop-up is quoted below |
| Decryptor | None for XHAMSTER by name; the Phobos / 8base tool by Japanese police may work (not confirmed) |
| Contact | @xhamster2020 on ICQ, which VK closed on 26 June 2024 |
| Detection names | Microsoft: Ransom:Win32/Phobos.PC!MTB; BitDefender: Gen:Variant.Ransom.Phobos.62; ESET: Win32/Filecoder.Phobos.C |
| Distribution | Not documented for this variant; Phobos spreads by exposed remote desktop and phishing mail (ThaiCERT) |
| Damage | Files encrypted and renamed; extra malware may be present |
| Evidence | One write-up by a security site; no sample analysed yet |
| Encrypted files | .XHAMSTER |
| Free decryptor | A free Phobos / 8base decryptor from Japanese police exists, but it is not confirmed for the .XHAMSTER ending (checked 6 October 2026) |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against PCrisk's XHAMSTER guide (updated 13 June 2023), the Japanese National Police Agency's decryptor guide, the No More Ransom tools list and our own 2022 screenshots. We did not run the malware, and the decryptor is not confirmed for the .XHAMSTER ending.
What XHAMSTER ransomware is
XHAMSTER is a Windows file encryptor from the Phobos family: it renames your files to name.ext.id[ID].[ICQ@xhamster2020].XHAMSTER, drops the notes info.hta and info.txt, and asks you to pay in Bitcoin through an ICQ account. Since July 2025 a free police decryptor for Phobos files exists, and it is the first thing to try.
The name comes from the attackers' contact handle, @xhamster2020. Nothing we read links this malware to the adult website of the same name, and the site is not needed to understand or remove it.
- Family
- Phobos ransomware, a ransomware-as-a-service operation (Fortra)
- Extension
.XHAMSTER, added after the victim ID and the contact handle- Example
1.jpgbecomes1.jpg.id[C279F237-2797].[ICQ@xhamster2020].XHAMSTER(PCrisk)- Notes
info.hta(a pop-up window) andinfo.txt(a text file)- Contact
@xhamster2020on ICQ; no e-mail address in the notes- Payment
- Bitcoin; the notes print no wallet, and the price "depends on how fast you write"
- Free test
- Up to 5 files, under 3 MB in total, no databases or backups
- Decryptor
- No XHAMSTER-specific tool; the Phobos / 8base decryptor from Japanese police may work (see the decryption chapter)
How the XHAMSTER story went
Late 2018
Phobos appears
Fortra says Phobos emerged in late 2018 as ransomware-as-a-service, with affiliates who run the attacks and pay the administrators.
23 March 2022
Our first report
We described XHAMSTER as a Phobos variant that locks files with a complex extension and asks for cryptocurrency through ICQ. The 2022 guide said decryption was not possible.
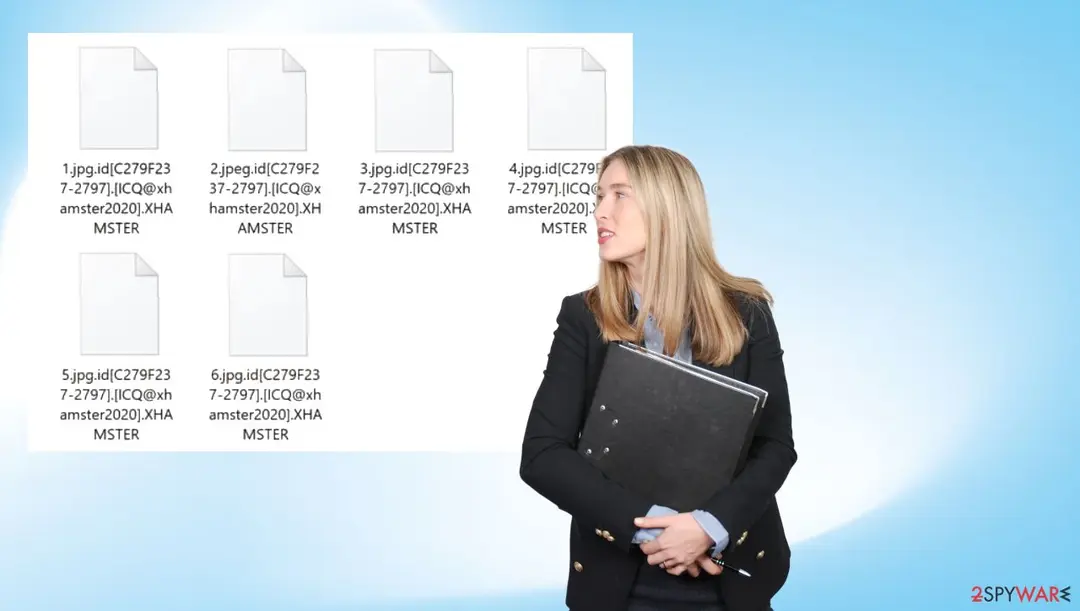
Six files renamed with the .id[...].[ICQ@xhamster2020].XHAMSTER ending, from our 2022 report (the person in the picture is report artwork). 26 June 2024
ICQ closes
VK shut down the ICQ messenger, which is the only contact the notes name.
February 2025
Charges and server seizures
The US Department of Justice unsealed charges against two alleged Phobos affiliates, and law enforcement took down servers tied to Phobos and its 8Base offshoot (Fortra, Europol).
July 2025
Free decryptor released
Japan's National Police Agency published a free Phobos / 8base decryptor, shared through Europol and the FBI and listed on No More Ransom.
6 October 2026
Our recheck
We rewrote the guide: the old claim that decryption is impossible is no longer safe to repeat.
What we checked and what we did not
XHAMSTER is not a website we can test, and we did not run the malware, so this is a source check; the old guide's claims were read against current sources.
XHAMSTER ransomware · source check · 6 October 2026
- Name, extension and notesPCrisk's guide (updated 13 June 2023) and our own 2022 screenshots agree on
.XHAMSTER,info.hta,info.txtand the ICQ handle. - Decryptor for .XHAMSTERThe police guide lists
.phobos,.8base,.elbie,.faustand.LIZARDand says other extensions with the same file-name pattern may work..XHAMSTERis not named, so it is not confirmed. - How it got inNo source documents how XHAMSTER reached any victim; only general Phobos routes are known.
- Shadow copies, registry, startupNot documented for this variant; not confirmed.
Serious, with a real chance of recovery Files are encrypted and there is no XHAMSTER-specific key, but the file names fit what the free police tool decrypts. Try it on copies before anything else, and do not pay.
What antivirus programs call it
Detection names change from week to week, so use them only to confirm that a scan found the right family.
| Who | Name | Where it comes from |
|---|---|---|
| Microsoft | Ransom:Win32/Phobos.PC!MTB | PCrisk, June 2023 |
| BitDefender | Gen:Variant.Ransom.Phobos.62 | PCrisk, June 2023 |
| ESET | A variant of Win32/Filecoder.Phobos.C | PCrisk, June 2023 |
| Avast | Win32:Trojan-gen | PCrisk, June 2023 |
| Kaspersky | HEUR:Trojan.Win32.Generic | PCrisk, June 2023 |
How XHAMSTER ransomware behaves
What it does to your files
Everything in this chapter is from PCrisk's description of XHAMSTER and from the Japanese police guide for Phobos files; we did not run the malware ourselves.
- 1
It encrypts your files
PCrisk reports that XHAMSTER encrypts files and renames each one by appending the victim's ID, the ICQ handle and the
.XHAMSTERextension. Without the matching key the files do not open. - 2
The name carries three pieces of information
After the original name and extension comes
.id[and an eight-character code, a dash and four digits, then].[ICQ@xhamster2020].XHAMSTER. The code is your victim ID, which the attackers ask you to put in the title of your message. - 3
A pop-up and a text file appear
PCrisk lists two ransom messages:
info.hta, a window that opens on the screen, andinfo.txt, a text file. The old 2022 guide described the same two files. - 4
The note tells you not to touch anything
Both notes say do not rename the encrypted files and do not use third-party software, because it may cause permanent data loss, and that third parties raise the price or may scam you. These are pressure lines; they are not a technical fact.
What you will see
- .XHAMSTER
- info.hta
- info.txt
- @xhamster2020
- id[XXXXXXXX-NNNN]
- ICQ
What the notes demand
The notes ask you to contact the attackers on a messenger service, not to pay straight away, and they name no price at all.
| Item | What the note says | What it means |
|---|---|---|
| Contact | Install ICQ and write to @xhamster2020, with your file ID in the title | ICQ was shut down by its owner VK on 26 June 2024, so the channel the notes name may not be reachable at all. |
| Price | "Depends on how fast you write to us"; payment in Bitcoin | No sum is printed, which lets the attackers set the price per victim. |
| Free test | Up to 5 files, under 3 MB in total, no databases, backups or large Excel files | The usual way ransomware gangs persuade victims that the decryptor exists. |
| Claim | "We are the only people who can recover your files and there is no free tool" | Not true for Phobos files since July 2025, when police released a free tool. |
How it reaches PCs
No source documents how XHAMSTER specifically got onto any computer.
What is known is how Phobos spreads in general, and that is where the old guide's list belongs.
- High
Remote desktop scanned and guessed
ThaiCERT's summary of Phobos names RDP port scans among the usual ways in. An exposed remote desktop with a weak password lets an attacker run any file.
- Medium
Phishing mail
The same summary lists phishing e-mails. The old guide named Office, PDF and JavaScript attachments and links; PCrisk adds archives and executables.
- Medium
Pirated software and games
The old guide said a cracked program can launch an EXE file after the install; PCrisk names unofficial activation tools and fake updaters for ransomware in general.
- Medium
Torrent sites and free file hosts
PCrisk lists peer-to-peer networks, unofficial sites and free file-hosting pages as channels for malicious files.
Similar names and lookalikes
Phobos has many names, and the wrong instructions can waste days.
The ending on your files decides which page you need.
| Name | How it relates | What to do |
|---|---|---|
.phobos, .8base, .elbie, .faust, .LIZARD | Other endings of the same file pattern that the police decryptor supports | Same steps as here: remove first, then try the tool on copies |
| 8Base | A group that built its own variant on Phobos infrastructure and also stole data before encrypting (Europol) | If you had a business network, treat it as data theft too |
STOP/Djvu (.djvu, .wwka and similar) | A different family with different keys | The Phobos tool does not work on it |
Was anything stolen?
Nothing we read says XHAMSTER copied files out, but treat your passwords as exposed if the attacker had access to the PC: Phobos affiliates get in through remote access.
- Medium
Remote access before the encryption
If the way in was a hacked remote desktop, someone was logged in to your PC before the files were locked, and saved passwords in browsers were within reach.
- Low
No leak site for XHAMSTER
Neither the notes nor PCrisk mention a leak site or a threat to publish data. The related 8Base group did use double extortion (Europol), so the risk is higher for a company network.
The XHAMSTER ransomware note
All your files have been encrypted!
All your files have been encrypted due to a security problem with your PC.
If you want to restore them, install ICQ software on your PC here hxxps://icq.com/windows/ or on mobile phone from Appstore/Google Play Market search for "ICQ". Write to our ICQ @xhamster2020 hxxps://icq.im/xhamster2020. Write this ID in the title of your message.
You have to pay for decryption in Bitcoins. The price depends on how fast you write to us.
Free decryption as guarantee. Before paying you can send us up to 5 files for free decryption. The total size of files must be less than 3Mb (non archived), and files should not contain valuable information (databases, backups, large excel sheets, etc.).
Attention!
Do not rename encrypted files.
Do not try to decrypt your data using third party software, it may cause permanent data loss.
Decryption of your files with the help of third parties may cause increased price (they add their fee to our) or you can become a victim of a scam.
Be assured we are the only people who can recover your files and there is no free tool.
Can XHAMSTER ransomware files be decrypted?
Can .XHAMSTER files be decrypted now?
Possibly, and for free: since July 2025 Japan's National Police Agency distributes a Phobos / 8base decryptor through No More Ransom, and the file-name pattern of XHAMSTER matches the one it supports. It is not confirmed for this extension, so test it on copies.
Our 2022 guide, like PCrisk, said no decryption was possible. That was true then. It is out of date now, and we corrected it here.
| What to check | What the police guide says | Does XHAMSTER fit? |
|---|---|---|
| File name pattern | {original name}.id[{8 random characters}-{4 digits}].[{mail address}].{extension} | Yes: .id[C279F237-2797].[ICQ@xhamster2020].XHAMSTER has the same shape, with the ICQ handle where a mail address would be. |
| Extensions | .phobos, .8base, .elbie, .faust, .LIZARD, and others with the same pattern may work | .XHAMSTER is not listed by name; the tool may still work. |
| Damaged files | Files corrupted by an encryption failure or bug cannot be decrypted; no integrity guarantee | Unknown until you try. |
- 1
Remove the malware first
No More Ransom says to remove the malware before using any decryptor, or it may lock the files again. Follow the removal plan on this page.
- 2
Copy the encrypted files
Copy a few folders of
.XHAMSTERfiles to an external drive. Never work on your only copy. - 3
Download the tool from a trusted place
Open the Phobos / 8base entry on nomoreransom.org and read the how-to guide linked there. Do not download a "Phobos decryptor" from a search result or an e-mail.
- 4
Run it on one folder
The guide has you run
Phdec_gui_v***.exe, agree to the terms, choose the folder or file, choose a different output folder, and press Decrypt. The decrypted files are written to the output folder; the originals are left alone. - 5
Read the result
The tool counts successful, failed and untouched files and writes
output.csvin itslogfolder. Ano_keysresult means the key is broken, andcorruptedmeans the file was damaged or only partly encrypted.
Do
- Test the tool on a small folder of copies and open a few results before running it on everything
- Keep the encrypted originals even after a success; a later tool version may recover more
Don't
- Do not pay the attackers while you are testing
- Do not rename the encrypted files, the tool reads the name for the ID
Should you pay the ransom?
No. The notes name no price, ICQ is closed, and a free decryptor for the family now exists, so there is little to buy and nobody who can be held to a promise.
The 2022 guide said the same in other words: criminals have no mercy and rarely release the files. The new facts make the case stronger.
- High
You may reach nobody
The only contact is an ICQ account, and VK closed ICQ on 26 June 2024.
- High
The free test proves little
Decrypting 5 small files shows the attackers have a key for those files, not that they will hand over the rest.
- Medium
Payment may be illegal
CISA's guidance warns that payments to sanctioned groups can bring legal risk; ask a lawyer if a company is paying.
- Medium
It does not clean the PC
Even a working key does not remove the malware or close the way in.
How to remove XHAMSTER ransomware
Tools you'll need
All of these are free except where noted. Download them on a clean device if the infected PC is offline.
- A USB stick: to keep the ransom note, two or three encrypted files and screenshots off the infected PC.
- Microsoft Defender Offline: built into Windows 11 and Windows 10; scans before Windows starts, so running malware cannot hide.
- Microsoft Safety Scanner: a second, portable scanner with current signatures; each download works for 10 days.
- ID Ransomware: identifies the family from the note and one encrypted file and says whether a decryptor exists.
- No More Ransom: the free decryptors from police and security companies; check it again every few months.
- Fortect (optional): scans Windows for malware and repairs the system files and settings it damaged. The free scan is in the box above.
How to remove XHAMSTER ransomware and get your files back
Work in this order.
Disconnecting comes first, removal comes before any restore, and nothing here asks you to contact the attackers.
Step 1: Disconnect the PC and unplug backup drives
Unplug the network cable or turn off Wi-Fi, and disconnect USB drives, external disks and network shares, so XHAMSTER ransomware cannot reach more files. Pause OneDrive, Google Drive or Dropbox sync, because synced folders upload the encrypted copies over the good ones.
Leave the PC on but offline while you read the next steps, since a restart can let the ransomware run again. This applies to Windows 11 and Windows 10 alike.
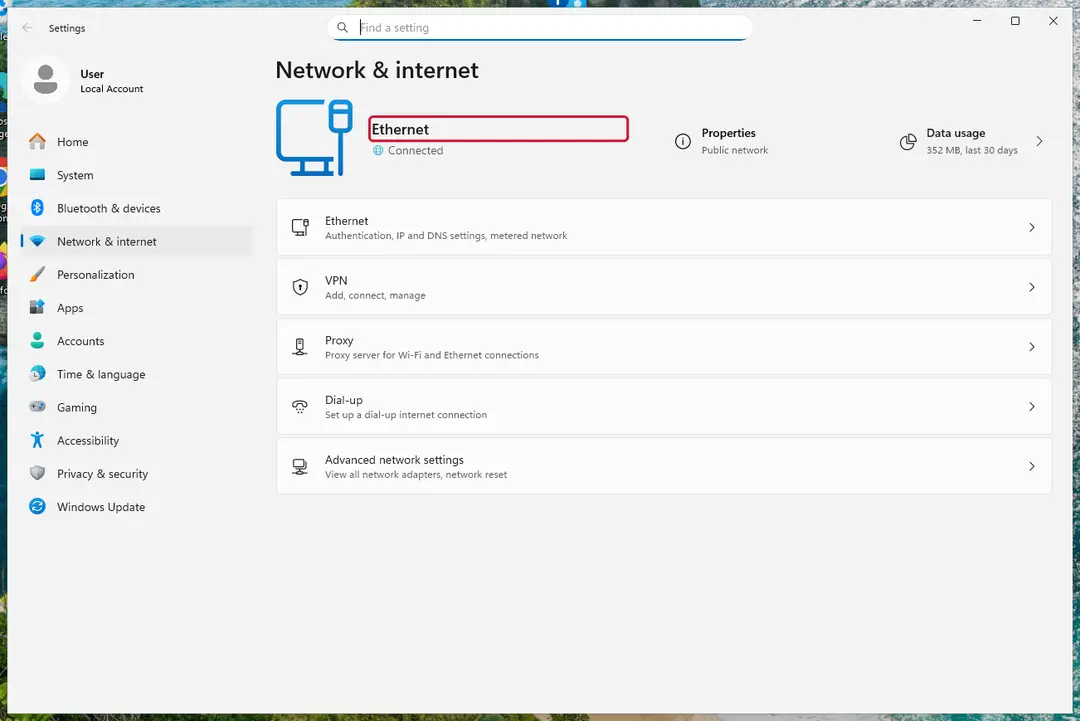
Windows 11: turn off Wi-Fi to take the PC offline. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 2: Save the ransom note and confirm the family
Your files now end in
.XHAMSTERand the instructions are ininfo.hta. Save both to a USB stick, a copy of the note and two small encrypted files, before anything else.On another device, check them with ID Ransomware or Crypto Sheriff: the family name decides which decryptor, if any, can help. Keep the note's ID and contact line for your report.
Windows 11: the ransom note and encrypted files to copy for identification. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 3: Check for a free decryptor
Our last check found that for XHAMSTER ransomware, a free Phobos / 8base decryptor from Japanese police exists, but it is not confirmed for the .XHAMSTER ending (checked 6 October 2026).
Look again yourself in the No More Ransom list and the free decryptor pages of Emsisoft, Avast and Kaspersky, which add new families every year.
A decryptor needs the ransomware gone first, or it encrypts the files again. Keep at least one copy of the encrypted files on an external drive, even if no tool works yet.
Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 4: Remove the ransomware before you restore or decrypt
Removing XHAMSTER ransomware does not bring the files back, but it has to come first. Start with Defender's Full scan, then the offline scan from the same Scan options page, which checks the disk before Windows loads.
If the scan cannot start, use Safe Mode with Networking. Delete the ransom notes only after you have saved a copy, because removal tools sometimes leave them behind on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Look for shadow copies of the files
Windows keeps shadow copies for restore points and backups, and some ransomware fails to delete them.
vssadmin list shadowsin an administrator Command Prompt tells you at once whether any exist.If they do, right-click the folder that held your files, open Properties > Previous Versions, select a version from before the attack, and click Open to check it before you Restore or copy the files out. Windows 11 and Windows 10 both have the tab.
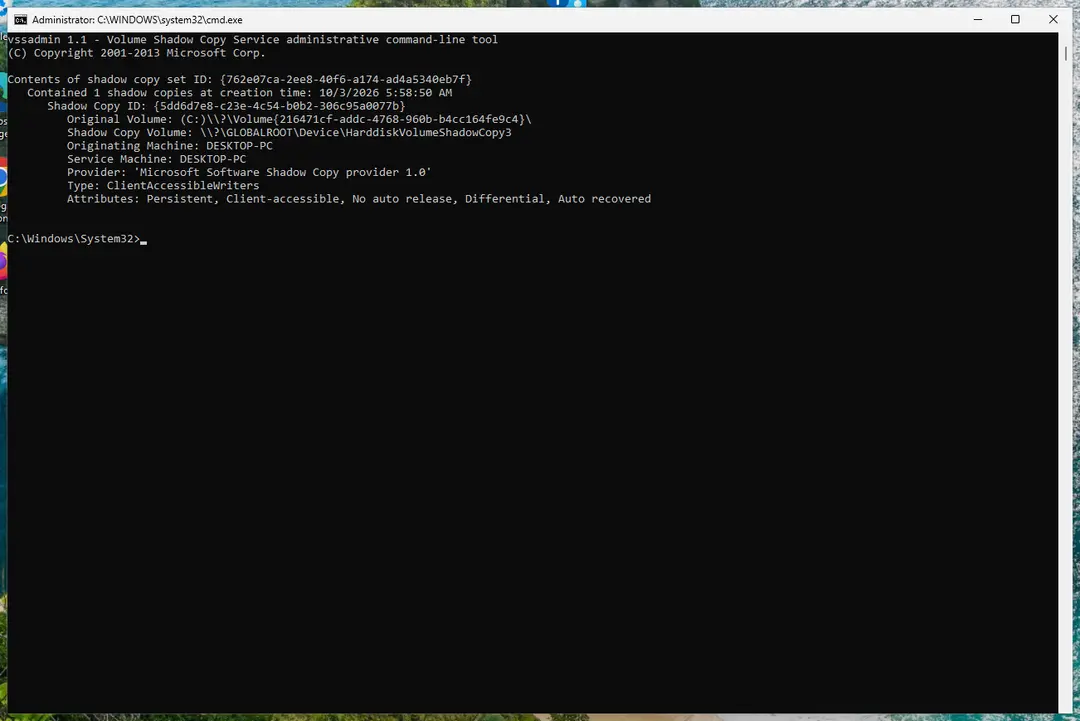
Windows 11: vssadmin list shadows shows whether shadow copies exist. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 6: Restore the files from a backup or recover deleted originals
A backup made before the attack is the surest way back. Connect it only once the PC is clean, then restore from File History, Windows Backup, OneDrive's Restore your OneDrive or your own external copies.
Without a backup, try file recovery: the originals that XHAMSTER ransomware deleted may still be on the disk until something overwrites them. Install nothing new on the drive you want to recover from on the Windows 11 or Windows 10 PC.
Full procedure with screenshots: Recover deleted files (Recycle Bin, backups, OneDrive) On uGetFix
Report it and recover your files
Report it
Report the attack even if you do not expect the files back: insurers and banks ask for the report number, and police use the contacts in the note to link cases.
- United States
- FBI IC3 · FTC ReportFraud
- United Kingdom
- Report Fraud (formerly Action Fraud) · NCSC
- Australia
- ReportCyber (ASD)
- EU countries
- Europol: national reporting sites
Give the victim ID, the note and the date the files were encrypted. A business that holds personal data may also have to notify its data protection authority, in the EU within 72 hours.
If the decryptor does not work: other ways to get files back
Check these in order, and do not save anything new to the disk until you have tried them.
- 1
Your own backups
A copy on an external drive, a NAS or cloud storage (OneDrive, iCloud, Dropbox) is the most reliable source. Connect it only after the PC is clean.
- 2
Cloud version history
OneDrive, Dropbox and Google Drive keep earlier versions of files. Roll individual files or the whole account back to a date before the attack.
- 3
Previous Versions
Right-click the folder, choose Properties > Previous Versions (on Windows 11: Show more options first). If nothing is listed, System Restore protection was off or the copies were deleted.
- 4
Shadow copies
Run
vssadmin list shadowsin an administrator Command Prompt. If copies are listed, a free viewer such as ShadowExplorer can browse them. Whether XHAMSTER deletes them is not confirmed. - 5
Wait for a better tool
Keep the encrypted copies. The police tool arrived three years after the first reports, and the tools list on No More Ransom is updated whenever a new key is found.
How to prevent XHAMSTER ransomware and the next attack
Phobos gets in by a few ordinary routes, and each has a simple habit against it.
For backups, follow the 3-2-1 rule that CISA's ransomware guidance recommends:
- three copies
- on two kinds of storage
- with one copy away from the PC
Do
- Close remote desktop (TCP port 3389) to the internet, or put it behind a VPN with a long password and two-step sign-in
- Keep Windows, your browser and Microsoft Defender updated, and run a full scan after you open anything unusual
- Delete unexpected e-mails and attachments, especially Office, PDF, JavaScript and ZIP files
- Turn on file extensions in File Explorer (View > Show > File name extensions)
- Unplug a backup USB drive after each backup, because a connected drive can be encrypted too
- Open a file from your backup now and then to see that it works
Don't
- Do not install cracks, keygens or pirated games
- Do not download programs from torrent sites or free file hosts
- Do not run an update that came from a pop-up instead of the program itself
- Do not leave the only backup plugged in all the time
Questions about XHAMSTER ransomware
Is there a decryptor for XHAMSTER ransomware?
Possibly yes, but it is not confirmed for this extension. Since July 2025 Japan's National Police Agency distributes a free Phobos / 8base decryptor through No More Ransom, and XHAMSTER files follow the same file-name pattern, id[code].[contact].extension.
The police guide names .phobos, .8base, .elbie, .faust and .LIZARD and says other endings with that pattern may work. Remove the malware first, copy your files, and test the tool on one folder. Older pages, including our 2022 guide, said no decryption was possible, which is now out of date.
How do I open .XHAMSTER files?
You cannot open them directly, because the contents are encrypted. Each file is renamed to something like 1.jpg.id[C279F237-2797].[ICQ@xhamster2020].XHAMSTER, and renaming it back does not help. The only ways to see the contents again are a backup, a shadow copy, or decryption.
Try the free Phobos decryptor from No More Ransom on copies of the files after you have removed the malware. Keep the encrypted originals untouched until you have checked that the decrypted copies open.
Should I pay the XHAMSTER ransom?
No. The notes print no price and tell you to write to an ICQ account, but VK closed ICQ on 26 June 2024, so you may reach nobody. The free test of five files only shows that the attackers hold a key for those files.
A free police decryptor for Phobos files now exists, and paying does not remove the malware or close the way in. Keep the notes and the ID, report the attack, and follow the plan on this page.
What is the ICQ @xhamster2020 contact?
It is the attackers' only contact in the notes, an account on the ICQ messenger, written as @xhamster2020 with the link icq.im/xhamster2020. You are told to put your file ID in the title of the message.
ICQ was shut down by VK on 26 June 2024, so the account may no longer be reachable. The handle is also in every file name, which is how the ransomware got its name. Do not contact it; the handle is useful only for identifying the variant.
Is XHAMSTER ransomware connected to the xHamster website?
Nothing we read connects them. The name comes from the attackers' contact handle, @xhamster2020, which they used as the file extension and message handle. PCrisk, which we used as a source, treats it as a Phobos variant and says nothing about the website.
You do not have to have visited an adult site to be hit; ransomware of this kind reaches PCs through exposed remote desktop, phishing mail and pirated software.
How did XHAMSTER get on my computer?
We do not know, and no source documents the delivery of this variant. For Phobos in general, ThaiCERT lists phishing e-mails, RDP port scans and loaders such as SmokeLoader. PCrisk names malicious attachments, torrent sites, fake updaters and cracked software.
Think of what you opened or installed just before the first renamed file, and whether remote desktop is open to the internet. Keep the file for the scan, and change the password of anything that was stored on the PC.
Does XHAMSTER ransomware steal data?
Nothing we read says so. The notes and PCrisk mention no leak site and no threat to publish files. The related 8Base group did steal data before encrypting, according to Europol, so a company network deserves more caution than a home PC.
If an attacker used remote desktop to get in, they could have reached saved passwords. As a precaution, change your main passwords from a clean device, starting with e-mail and banking.
What is the difference between XHAMSTER and other Phobos variants?
Mostly the ending and the contact handle. Phobos is a ransomware-as-a-service operation, so different affiliates use the same malware with their own extension, such as .phobos, .8base, .elbie, .faust or .LIZARD, and their own contact.
The file-name pattern id[code].[contact].extension stays the same, and that is what the police decryptor reads. The ransom note can look different between affiliates, so judge the family by the file names, not by the wording of the pop-up.
Can a data recovery company or paid service help?
A recovery service may help with deleted files, but for encrypted ones the free police decryptor is the first thing to try, and it costs nothing.
Be careful with anyone who offers a paid XHAMSTER decryptor or promises to negotiate with the attackers; PCrisk warns that they are often scams or middlemen. A restore from your own backup, Previous Versions or a cloud version history is faster and safer. Try those before you spend money.
Will Fortect remove XHAMSTER ransomware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For XHAMSTER ransomware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- PCrisk: XHAMSTER ransomware (read October 6, 2026)
- Japan National Police Agency: PhDec decryptor guide (PDF) (read October 6, 2026)
- No More Ransom: decryption tools (Phobos / 8base) (read October 6, 2026)
- Fortra: Free decryptor for victims of Phobos ransomware released (read October 6, 2026)
- The Record: Japanese police release decryptor for Phobos ransomware (read October 6, 2026)
- ThaiCERT: Free decryption tool for Phobos and 8Base (read October 6, 2026)
- Windows Central: VK ends support for ICQ on 26 June 2024 (read October 6, 2026)
- CISA: StopRansomware (read October 6, 2026)