
17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware: what it is and how to remove it
17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F is a Trojan that specializes in stealing funds from users' cryptocurrency wallets. The principle of the virus is relatively simple: it hijacks the clipboard data (which is why these types of infections are known as "clipper hijackers") and replaces it with the cybercriminals' cryptocurrency wallet data.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If ReimageRepair.exe returns after removal, a full scan can find the entry that brings it back.
Do it yourself · free Remove 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware yourself 6 steps, about 18 minutes, no software needed.
Start the steps
17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware: summary
| Distribution | Torrents, software cracks, illegal websites |
|---|---|
| Name | 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware |
| Type | Trojan, clipper hijacker |
| Function | To steal funds from users' Bitcoin cryptocurrency wallets |
| Symptoms | Due to malware's functionality, it is hardly possible to notice its malicious operations |
| Detection names | No Microsoft detection name is known |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 5 more facts
| Damage | Not recorded in the old report |
|---|---|
| Evidence | 4 write-ups by security sites; details still limited |
| File name | ReimageRepair.exe |
| First seen | 7 April 2022 |
| Facts checked | 7 October 2026 |
What 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware does
From our report of Apr 2022 · not reviewed since
Trojans and clapboard hijackers explained
Trojans are usually identified by their distribution principles rather than functionality.
Whenever users install a file they believe to be safe (a cracked program, fake Flash Player update, a malicious spam email attachment disguised as a valid MS Office document, etc.) but it ends up infecting their systems with malware, it is classified as a Trojan.
For this precise reason, Trojans can operate drastically differently, depending on the payload delivered in such a manner. Ransomware, for example, is often detected as a Trojan, as it is usually distributed via spam email attachments or software cracks. In this case, the function of the 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F virus is to steal funds from cryptocurrency wallets.
89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ is yet another clipboard hijacker we've recently discussed. This function of malware has been becoming more widespread recently, as Bitcoin and other cryptocurrency usage is constantly rising.
The malware can also come with additional functions, for example, keylogging, or might also allow the attackers to install additional payloads. Also, when downloading software from third-party websites, it might also contain potentially unwanted programs such as adware.
From our report of Apr 2022 · not reviewed since
More from our earlier report on 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware
- Employ powerful security software to remove all the components from the system at once
- After malware removal, make sure you clean your browsers and repair damage done to the system files.
- You can do this quickly with the PC repair and maintenance tool
How 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware got on your PC
From our report of Apr 2022 · not reviewed since
17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F is a dangerous clipper-hijacking malware that spreads via torrent sites
17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F is a Trojan that specializes in stealing funds from users' cryptocurrency wallets.
The principle of the virus is relatively simple: it hijacks the clipboard data (which is why these types of infections are known as "clipper hijackers") and replaces it with the cybercriminals' cryptocurrency wallet data.
Consequently, instead of transferring funds to their own wallets, victims end up making a transaction to cybercriminals' Bitcoin wallets. An alternative crypto wallet address can also sometimes be used - 3PxkHEMPaNMPMyiiHpHEj6ZgWzShh54N65.
17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware otherwise would not show any signs or symptoms, hence it might not be noticed for a while. As a result, the affected users might lose thousands of dollars in Bitcoin if such sums are being transferred.
From our report of Apr 2022 · not reviewed since
Distribution and avoidance
In order to be successful, malware authors employ several distribution methods - this guarantees that more people can be exposed to the infection.
As a result, they can expect more funds to flow into their personal crypto-wallets.
Most commonly, users install 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ malware when downloading illegal software installers or cracks from unsolicited websites. These sites are often poorly protected, and any registered user with a simple account can upload and share files. This serves as a perfect ground for malware authors.
It is not difficult to see why software cracks and illegal pirated apps work so well. Those who have security software installed on their machines often assume that the detection of a malicious file, such as RAR, EXE, or RUN, is a false positive, which follows by disabling the warning and putting the file as an exception.
Therefore, you should not visit such websites, let alone download files from them. Purchase software that won't infect your system or instead rely on freeware programs, although you should always be careful about potentially unwanted applications that are pretty common on third-party websites.
How to check the PC for 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware
- File:
ReimageRepair.exe
How to remove 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware
How to remove 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware and protect your crypto
Check every pasted wallet address until the PC is clean, because clippers act at the moment you paste.
Step 1: Move your crypto and check every pasted address
A clipper swaps a copied wallet address for the attacker's at the moment you paste it, so compare the first and last six characters of every pasted address with the original.
Move funds from software wallets used on this PC to a new wallet created on a clean device, with a new recovery phrase, because the old phrase may have been read.
Crypto transfers cannot be reversed, but report a theft to the exchange and to the police at once. Until the scans are clean, do not use the Windows 11 or Windows 10 PC for crypto.
Full procedure with screenshots: What to do after paying a scammer
Step 2: Check where ReimageRepair.exe runs from and stop it
ReimageRepair.exeis the part you can see, and its location tells you whether it belongs there. Right-click it on the Processes page of Task Manager and choose Open file location, then right-click the file > Properties > Digital Signatures to see who signed it.An unsigned file, or one in a user folder such as
%AppData%, is the one to remove: end the task, then delete the file.Note the folder name, because the same folder usually holds its other files. This is the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 3: Remove it from startup
Whatever 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 5: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Protect your privacy - employ a VPN
There are several ways how to make your online time more private - you can access an incognito tab.
However, there is no secret that even in this mode, you are tracked for advertising purposes. There is a way to add an extra layer of protection and create a completely anonymous web browsing practice with the help of VPN. This software reroutes traffic through different servers, thus leaving your IP address and geolocation in disguise.
Besides, it is based on a strict no-log policy, meaning that no data will be recorded, leaked, and available for both first and third parties. The combination of a secure web browser and VPN will let you browse the Internet without a feeling of being spied or targeted by criminals.
No backups? No problem. Use a data recovery tool
If you wonder how data loss can occur, you should not look any further for answers - human errors, malware attacks, hardware failures, power cuts, natural disasters, or even simple negligence.
In some cases, lost files are extremely important, and many straight out panic when such an unfortunate course of events happen. Due to this, you should always ensure that you prepare proper data backups on a regular basis.
If you were caught by surprise and did not have any backups to restore your files from, not everything is lost. is one of the leading file recovery solutions you can find on the market - it is likely to restore even lost emails or data located on an external device.
From our report of Apr 2022 · not reviewed since
Removal steps explained
Scan with anti-malware
Malware removal should be performed as soon as possible. Once installed, Trojan can root itself deep into the system after dropping numerous files, which might be difficult to find without advanced IT knowledge.
Therefore, we strongly recommend you remove 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware with the help of powerful anti-malware software, such as or . By using it, you will ensure that all the malicious components are deleted at once, and none of the malware's processes are running in the background. Security software is also your first line of defense when it comes to initial malware attacks.
Remove unwanted programs and extensions
If you have downloaded a potentially unwanted program such as adware along with the virus, you should remove it as well. The most malicious apps can be eliminated by anti-malware software, although browser extensions/hijackers are not usually detected. Thus, you should check the extensions section on your browser and remove everything suspicious.
You should also remove the installed programs as follows:
Repair damaged system files and clean your browsers
It can clean your browsers and other leftover files for you instantaneously. In case malware has caused damage to your system files, it can repair them, consequently stopping crashes, errors, and other post-infection issues.
Web browser cleaning is also a mandatory process, especially after malware/adware removal. If you would rather clean browsers manually, please follow these steps:
- Enter Control Panel into the Windows search box and hit Enter or click on the search result.
- Under Programs, select Uninstall a program.
- From the list, find the entry of the suspicious program.
- Right-click on the application and select Uninstall.
- If User Account Control shows up, click Yes.
- Wait till uninstallation process is complete and click OK.
- Download
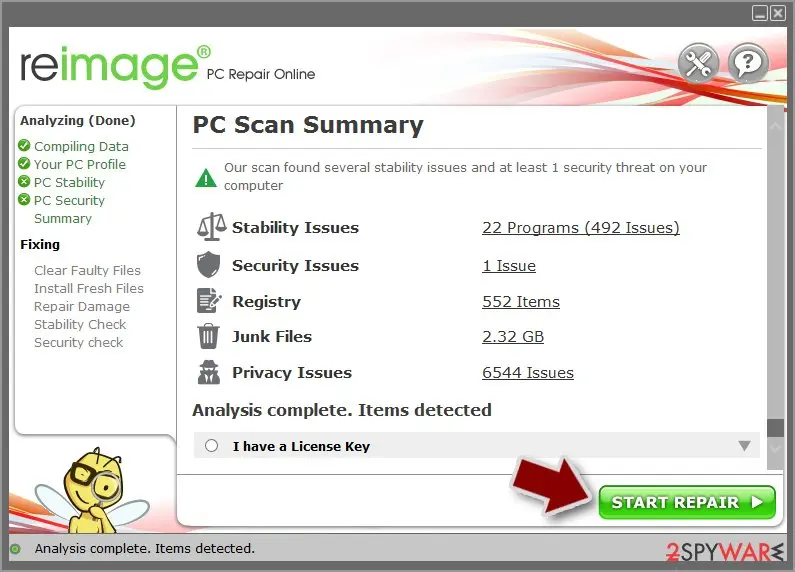
- Click on the ReimageRepair.exe
- If User Account Control (UAC) shows up, select Yes
- Press Install and wait till the program finishes the installation process
- The analysis of your machine will begin immediately
- Once complete, check the results - they will be listed in the Summary
- You can now click on each of the issues and fix them manually
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies, and other site data, as well as Cached images and files.
- Click Clear data.
- Click Menu and pick Options.
- Go to Privacy & Security section.
- Click on Clear Data...
- Select Cookies and Site Data, as well as Cached Web Content and press Clear.
- Click on Menu and go to Settings.
- Select Privacy and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
- Click Safari > Clear History...
- From the drop-down menu under Clear, pick all history.
- Confirm with Clear History.
Questions about 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware
What is ReimageRepair.exe and why is it running?
Every process is started by something:
- a program you installed
- a Windows service
- a scheduled task
- a startup entry
To learn why ReimageRepair.exe runs, find its file with Open file location in Task Manager, then look for an entry pointing to that file in Settings > Apps > Startup and in Task Scheduler.
Sort Installed apps by date to see what arrived when the process first appeared. Once you know the owner, you can decide whether to keep it, switch it off at startup or uninstall it completely.
Can I delete the ReimageRepair.exe file?
Only after you know what it belongs to. If ReimageRepair.exe is part of a program, uninstall that program through Settings instead, so its services and tasks go too. If it belongs to nothing and is unsigned, end the process, disable whatever starts it and then delete its folder.
Do not delete files from the Windows folder or files signed by Microsoft: those are part of the system, and removing them can stop Windows from starting. When in doubt, run a Microsoft Defender scan first and let it decide.
Is ReimageRepair.exe a virus?
If your antivirus links ReimageRepair.exe to 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware, yes. The name is used by this spyware, sometimes chosen to look like a system or driver file. Look at the location: a copy in Downloads, a temporary folder or %AppData% with no publisher under Properties > Details is not a genuine Windows file.
Do not run it again to check. Remove it with the offline scan from the plan above, and follow the account steps whether or not the file is still there, because the data may already have been sent.
Should I reset my PC because of 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware?
Only if the signs point to deeper access. Reset when you see an unfamiliar process called ReimageRepair.exe in Task Manager again after removal, when Windows Security cannot start or update, when remote access tools you did not install keep appearing, or when you simply cannot trust the PC any more.
Otherwise, the plan in this guide plus an offline scan is enough. If you do reset, choose Remove everything and Cloud download for a fresh copy of Windows, restore only documents and photos, and reinstall programs from their official sites. Change important passwords from the clean system afterwards.
Why is there no analysis of 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware?
Because nobody has shared a sample yet. Reports start with what victims see, here an unfamiliar process called ReimageRepair.exe in Task Manager; analysis follows only when the file that caused it reaches researchers.
Many stealers also delete themselves after sending the data, which leaves little to analyse on the PC. This guide therefore sticks to what is safe for every case:
- secure the accounts
- clean the PC
- remove the likely source
If you find the file you ran before this started, do not open it again; keep it for a scan.
Should I stop using this PC?
Only for sensitive things, and only until it is clean. Do not log in to banking, e-mail or crypto on it until the offline scan finds nothing. You can keep using it to follow the removal steps.
If the scans keep finding new items, or protection keeps switching off, back up your documents and reset Windows. After that the PC is as safe as a new one, but the accounts still need the steps in this guide, because a reset cannot undo data that was already sent.
Can I get crypto back that a clipper redirected?
Usually not. Blockchain transfers are final, and the receiving address belongs to the attacker. There are two things worth doing.
If the coins went to an address at a known exchange, contact that exchange's support with the transaction ID quickly; they can sometimes freeze funds. And report the theft to the police with the transaction details.
Be careful with anyone who offers to recover crypto for a fee: "recovery services" are a common follow-up scam aimed at people who have just lost money.
Should I report a stealer infection?
Report it if money was taken, accounts were used for fraud, or your identity was misused. The report gives you a reference number for your bank and helps police link cases. Also tell the services involved:
- banks
- PayPal
- crypto exchanges and e-mail providers have their own fraud teams that can freeze transfers
- restore accounts
An infection with no misuse yet does not need a police report, but acting on your accounts does. Keep the antivirus log that shows 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware; it helps explain the case.
Will changing my password stop 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware?
Only part of it. A new password blocks logins with the old one, but stolen session cookies can keep an attacker signed in until you choose to sign out of all sessions.
If the program behind an unfamiliar process called ReimageRepair.exe in Task Manager is still on the PC, it can also steal the new password as you type it. So the order is: clean device for the changes, sign out everywhere, two-step verification on, then clean or reset the affected PC before using it for anything important again.
Will Fortect remove 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For 17uoEtuihi6Lsg4hdedT7PUhF4FNgBPD2F malware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Fortinet: Trojan Horse Virus (read October 7, 2026)
- Wikipedia: Freeware (read October 7, 2026)
- FTC: How to recognize, remove and avoid malware (read October 7, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 7, 2026)
- Microsoft Learn: How Microsoft names malware (read October 7, 2026)