Adf.ly virus: is it safe? Ads, redirects and how to remove them
Adf.ly is a link shortener that shows an ad before the page you wanted; it is a website, not a virus. In our October 2026 test adf.ly ended on linkvertise.com and asked for nothing, so the risks left are ads on short links and any permission or file you accepted.
Facts checked October 4, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Not sure what sends your browser to adf.ly? An automatic scan looks at the usual sources for you.
Do it yourself · free Remove Adf.ly yourself 1 step, about 5 minutes, no software needed.
Adf.ly: summary
| Type | Link shortener that shows third-party ads (a website); not malware |
|---|---|
| Risk | Medium: the page we tested was quiet, but short links lead to ads and files we did not test |
| Symptoms | Ad pages before a link, pop-ups, redirects, or notifications from uclaut.net or another site you allowed |
| How to get rid of it | Take back notification permissions and remove unknown extensions in the browser (steps below); scan only if you ran a file |
| Our check (4 October 2026) | adf.ly ended on linkvertise.com; no notification request, no pop-ups; Google Ad Manager; a consent dialog naming 1004 partners |
| First reported by us | 29 May 2019 (reader questions since March 2017) |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 11 more facts
| Installed on the PC | Nothing: visiting the site installs no program; only an installer or extension you accept adds anything |
|---|---|
| Microsoft detection | None: Microsoft Defender has no detection name for a website, because nothing is installed by visiting it |
| Evidence | Our test of the site, our 2019 report and its pictures |
| Name | Adf.ly |
| Domains | adf.ly |
| Ads shown as | Redirects through ad pages |
| Browsers | Chrome, Edge and Firefox |
| First seen | 29 May 2019 |
| Distribution | Typically ad scripts on free streaming, file-hosting and adult sites, typo domains and hacked websites |
| Damage | Redirects to scam pages, fake updates and tech support scams |
| Facts checked | 4 October 2026 |
Facts checked on 4 October 2026 against our own test of adf.ly in desktop Chromium from Europe. The .ly registry offers no public RDAP record. We did not open a shortened link or download a file.
What Adf.ly is and how it works
Adf.ly is a link shortener, not a program. Someone pastes a long web address into it, gets a short adf.ly/... address back, and every visitor who opens the short address sees an ad page first. The owner of the link is paid for those views.
- 1
Someone shortens a link
A user pastes the address of a file, video or page into Adf.ly and receives a short address to share on a forum, a video description or a download page.
- 2
You click the short address
Instead of the real page you get an Adf.ly page with an advertisement and a Skip Ad button, as in the 2019 pictures below.
- 3
The ad pays the person who shared it
After you press Skip Ad you are sent on to the real destination. The ad is what earns the money, which is why the pages are built to hold your attention.
- Address today
- adf.ly answered with status 200 and the address bar ended on
linkvertise.com, another link-monetisation service (our test, 4 October 2026) - Business
- Link shortening paid by advertising; our 2019 report described it as a way for users to earn money from shortened links
- Installed on your computer
- Nothing. Adf.ly is a website; a program is involved only if one was installed from an ad or an installer
- Registration
- Not readable: the registry for the
.lydomain has no public RDAP service, so we have no registration date
Because the page you see is chosen by an ad network, the same short link can show different ads to different people. The shortener is the doorway; what you meet behind it depends on the advertiser.
Is Adf.ly dangerous?
Our test on 4 October 2026
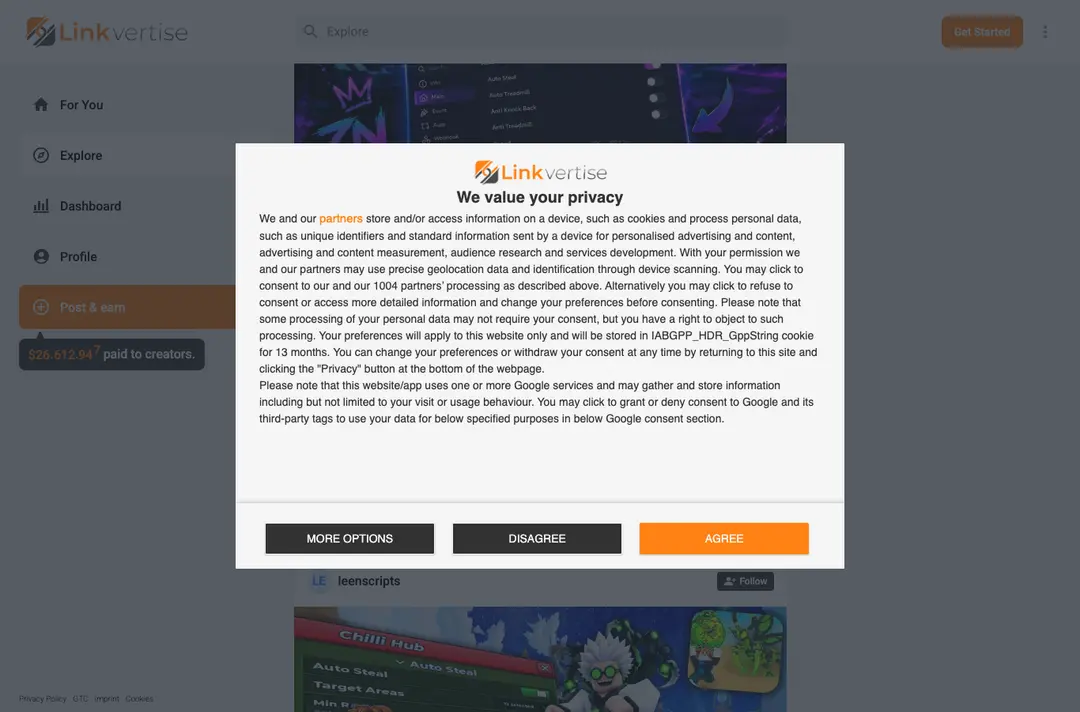
We opened adf.ly the way a visitor does: a clean desktop Chromium browser in Lithuania, no extension, no account. We did not open a shortened link, so we did not see the ad page that people clicking an Adf.ly address meet.
adf.ly · desktop Chromium · Europe · 4 October 2026
- Where we ended upThe request to
adf.lywas answered with status 200, but the address bar ended onlinkvertise.com, a different domain. The title was "The Search Engine for exclusive Content!". - Notification requestNone on this one visit.
- Pop-upsNo pop-up or new window opened.
- Service workerNone registered in the browser.
- Ad networkGoogle Ad Manager was the only ad network we found. We saw no pop-under or push-notification network.
- Consent dialogA privacy box says personal data is used for personalised advertising and shared with 1004 partners. It offers More options, Disagree and Agree.
- Other services loadedThe page contacts hCaptcha, Stripe, Chargebee, Google Analytics and Cloudflare, which fits a site that sells subscriptions and shows ads.
- Not testedA real shortened
adf.ly/...link, other countries, and the old Adf.ly ad pages; ad networks change what they show by country, device and time. We also did not retestuclaut.netorgloyah.net, named in our 2019 report.
Low on the page, unknown on the links The page we reached asked for nothing and opened nothing, but it was not Adf.ly itself, and the short links where the ads live were not tested. Judge each short link by what it asks you to allow.
What changed since our 2019 report
March 2017
Readers ask whether Adf.ly ads are infectious
The earliest question we kept came on 20 March 2017: someone using a forum comment as a reason to doubt the shortener. Two more in June 2018 reported intrusive ads and a computer that seemed infected after clicking a link.
May 2019
Our report: a shortener that adware borrows
We described Adf.ly as a legitimate ad platform whose short links and ad pages were being used by adware and bundled installers. The picture shows the home page with the invitation to get paid for sharing links, and an Adf.ly ad page in a small window on top.
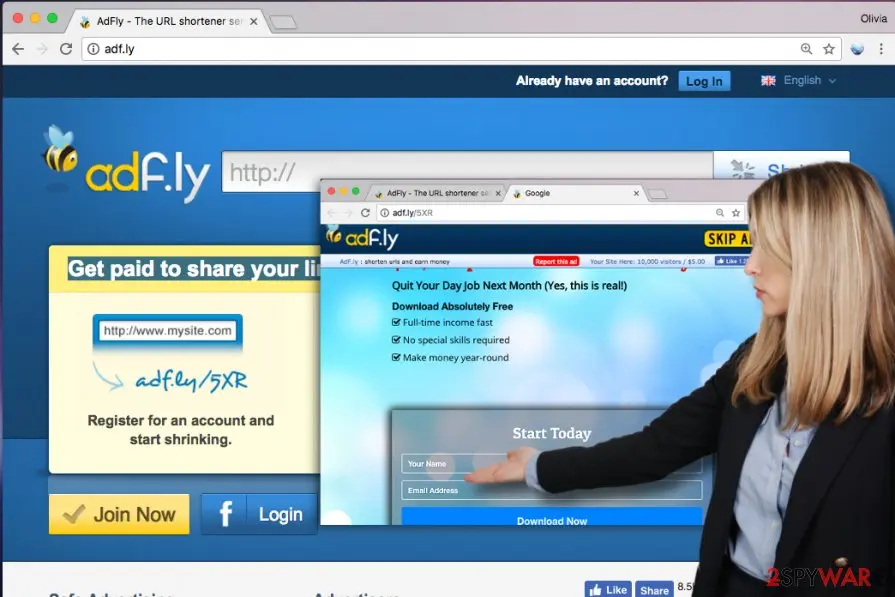
Adf.ly in 2019, from our old report: the home page offering money for sharing links, with a short-link ad page open above it. The woman is a stock-photo illustration. 2019
An ad page with a fake prize box
A second picture from the same report shows the Adf.ly interstitial with a Skip Ad button, and a Windows-style window below it saying "Congratulations! Get your USA Green Card" with name and country boxes. That is the kind of ad people meant by an "Adf.ly virus": an advertiser's page, not code on your computer.
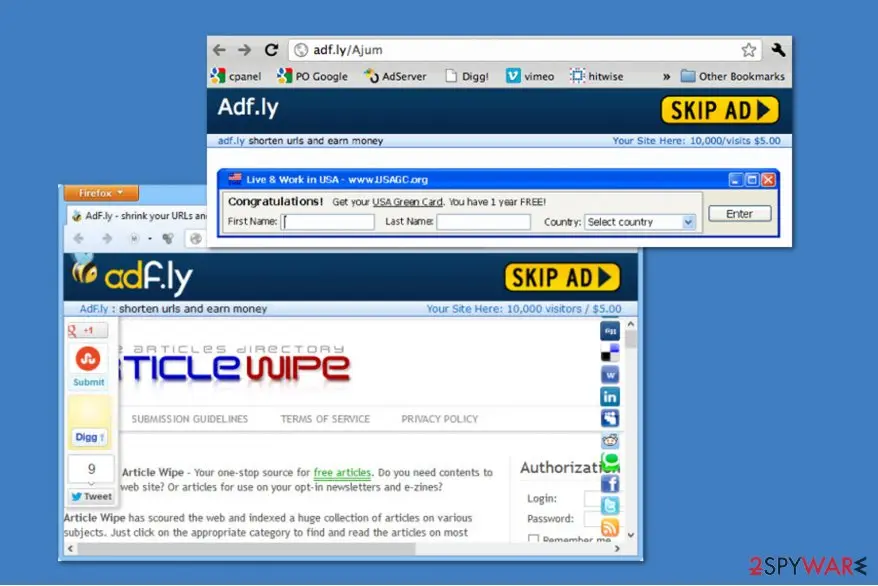
Adf.ly ads in 2019, from our old report: a Skip Ad bar above a fake "Congratulations" green-card window. November 2019
Last update to the old guide
The old guide was last edited on 26 November 2019 and sent readers to antivirus software.
October 2026
Our new check: the address leads to Linkvertise
Opening
adf.lyended onlinkvertise.com, with no notification request and no pop-up, and with a consent dialog naming 1004 partners.
Before you click a short link
A short link hides its destination. Check these three things before you trust what it opens.
- 1
Read the page address after it loads
The page you finally reach should match what the person who sent the link promised. A different site, or an address full of random letters, means close the tab.
- 2
Close a pop-up without clicking inside it
If a window opens saying you have won something or your computer is at risk, close the tab or window with the X or Alt + F4; do not press its buttons.
- 3
Refuse permission requests
A short-link page has no reason to send you notifications. Choose Block; if you already pressed Allow, use the browser steps further down.
Do
- Ask the sender for the real address when the file or page matters.
- Open short links in a browser profile with notifications blocked.
- Disagree on the consent dialog if you do not want 1004 partners to receive your data.
Don't
- Press Allow because a page says you must to continue.
- Open an
.exeor.msithat a short link handed you. - Believe a window that says you won a prize.
The real risks, from most to least serious
"Adf.ly virus" is not accurate for the site: opening it installs nothing. These are the ways a short link, or software that borrows its name, can still go wrong.
- High
Running a file or installer behind a short link
Short links are used to hide where a download really leads. A file that arrives as
.exe,.msior a browser-extension offer can carry adware or worse; the shortener cannot tell you which. - Medium
Clicking Allow on a notification request
Our 2019 report linked Adf.ly to notifications from
uclaut.net. One click on Allow lets a site push ads onto your desktop until you take the permission back. In Chrome and Edge they can arrive with the window closed. - Medium
Ads that send you on to other sites
The ad page can lead to prize draws, survey offers or fake support pages. We saw none on 4 October 2026, but we did not open a short link.
- Medium
Your data on the consent dialog
Agree on the dialog we met means personalised advertising and sharing with 1004 partners, as the page says. Disagree or More options lets you refuse.
- Low
Installers that bundle adware
Free programs from unreliable sites sometimes add extra software in the same installer. That is where a browser that keeps redirecting usually comes from, rather than from the shortener.
What adware installed from such ads typically collects
- IP address
- Internet provider
- Websites visited
- Links and ads clicked
- Browser and device details
- Installed apps and extensions
The point is to target ads at you. If you installed something from an ad, remove it with the steps below.
How to remove Adf.ly
How to stop the Adf.ly redirects
Work in this order and test a few links after each step, so you know which one was the cause.
Which browser shows the ads?
Take back notification permissions
Open Settings > Privacy and security > Site settings > Notifications. Under Allowed to send notifications remove every site you do not recognise with the three-dot menu > Remove, or choose Block; an old
uclaut.netentry, if present, goes too. Set Don't allow sites to send notifications to stop new requests.Remove extensions you do not recognise
Paste
chrome://extensionsinto the address bar and click Remove on anything you did not install yourself.Full procedure with screenshots: Remove a browser extension
Clear the site data
Press Ctrl + Shift + Delete, choose All time, tick Cookies and other site data and Cached images and files, and click Delete data.
Reset Chrome
Open Settings > Reset settings > Restore settings to their original defaults and confirm with Reset settings. This resets the start page, search engine and pinned tabs and turns off extensions; bookmarks and saved passwords stay. To stop notifications after you close Chrome, also turn off Settings > System > Continue running background apps when Google Chrome is closed.
Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Take back notification permissions
Open Settings > Cookies and site permissions > Notifications. Under Allow remove every site you do not recognise with the three-dot menu > Remove, or choose Block.
Remove extensions you do not recognise
Paste
edge://extensionsinto the address bar and click Remove under anything you did not install yourself.Full procedure with screenshots: Remove a browser extension
Clear the site data
Open Settings > Privacy, search, and services > Delete browsing data > Choose what to clear, set All time, tick Cookies and other site data and Cached images and files, and click Clear now.
Reset Edge
Open Settings > Reset settings > Restore settings to their default values and confirm with Reset. Extensions are turned off and the start page goes back to default; favourites, history and saved passwords stay. To stop notifications after you close Edge, turn off Settings > System and performance > Continue running background extensions and apps when Microsoft Edge is closed.
Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Take back notification permissions
Open Settings > Privacy & Security, scroll to Permissions, click Settings... next to Notifications, select every site you do not recognise and click Remove Website. Tick Block new requests asking to allow notifications and Save Changes.
Remove add-ons you do not recognise
Paste
about:addonsinto the address bar, open Extensions, and choose Remove from the three-dot menu of anything you did not install yourself.Full procedure with screenshots: Remove a browser extension
Clear cookies and site data
Open Settings > Privacy & Security > Cookies and Site Data > Clear Data, tick both boxes and click Clear.
Refresh Firefox
Open the menu > Help > More troubleshooting information and click Refresh Firefox. Add-ons and custom settings are removed and the home page goes back to default; bookmarks, history and passwords stay.
Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Take back the notification permission
Safari 18 and later on macOS: open Safari > Settings > Websites > Notifications, select any site you do not recognise and set it to Deny, or click Remove. Untick Allow websites to ask for permission to send notifications at the bottom so no site can ask again.
Remove extensions you do not recognise
In Safari > Settings > Extensions, select anything you did not install yourself and click Uninstall.
Clear the site data
In Safari > Settings > Privacy > Manage Website Data, remove the site's data, or use History > Clear History > all history. To empty the cache as well, turn on Show features for web developers in Settings > Advanced and choose Develop > Empty Caches.
Check the Mac for apps from the ads
Ads also target Mac users with fake players and "cleaners". In Finder > Applications, move anything unknown to the Bin. In System Settings > General > Login Items & Extensions, remove unknown items. Then use Go > Go to Folder to check
/Library/LaunchAgents,~/Library/LaunchAgents,/Library/LaunchDaemonsand/Library/Application Supportfor folders and files with the same unknown names, and empty the Bin.
Then, whichever browser you use
Step 1: Scan the PC if you downloaded anything from the ads
If you only saw the notifications and clicked nothing, you can stop before this step. If a notification led you to download or run something, delete that file, then scan Windows.
In Windows Security > Virus & threat protection > Scan options, run a Full scan, then choose Microsoft Defender Antivirus (offline scan) and Scan now. The offline scan restarts the PC and takes about 15 minutes on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
After removal: keep the ads from coming back
If you allowed notifications or ran a file
The browser steps for your browser, in the tabs above, cover notification permissions and extensions. If you also ran a file that came from a short link, do these three things.
- 1
Remove the extension
Look in the extensions page of your browser for anything you did not choose, especially an ad blocker, video helper or search add-on that appeared the day you used the link.
- 2
Uninstall what came with it
In Windows 11 go to Settings > Apps > Installed apps (Apps & features in Windows 10), sort by date and remove whatever appeared the day you ran the file (Uninstall a program or app in Windows On uGetFix).
- 3
Scan, then scan offline
Start a Microsoft Defender Full scan; when it ends, run Microsoft Defender Antivirus (offline scan) too, because some trojans hide while Windows is running.
Typed a password or card number on a page an ad opened? Change that password today and tell your bank about the card.
How to keep it from happening again
Do
- Stop sites from even asking: in Chrome, Settings > Privacy and security > Site settings > Notifications > Don't allow sites to send notifications.
- If an installer offers Custom or Advanced setup, take it and untick every extra program; refuse Quick or Recommended.
- Get programs from the maker's own site or the Microsoft Store, not from a link someone shortened.
- Install extensions only from your browser's own store, and open the store page yourself.
- Leave SmartScreen (Windows Security > App & browser control) on, or use Chrome's Enhanced protection; both warn about pages and files already known to be bad.
- Keep Microsoft Defender or your security program updated.
- Back up your documents with File History or OneDrive, so a bad download or a failing disk cannot take them.
- A VPN on public Wi-Fi hides your IP address from sites and ad networks; it blocks neither ads nor malware.
Don't
- Press Allow because a page says you need it to continue.
- Install a browser extension that an ad page tells you to add.
- Click ads on download or torrent sites; the ad networks serving them also sell space to scammers.
- Pay for "cleaner" software offered by a pop-up.
Questions about Adf.ly
Is Adf.ly a virus?
No. Adf.ly is a link-shortening website, and opening it does not install anything. The word virus comes from ads and redirects that people met after clicking short links, and from adware that borrowed the name. In our check on 4 October 2026 the address adf.ly ended on linkvertise.com, asked for no notifications and opened no pop-ups.
We did not open a shortened link, so we cannot vouch for what such links show. If you never installed a program, never ran a file from a link and never clicked Allow on a permission request, there is nothing to remove.
Is Adf.ly safe?
The page we reached on 4 October 2026 asked for nothing and opened nothing, but it was Linkvertise, not Adf.ly, and we did not test a shortened link. A short link hides its destination, and the ad page in front of it is chosen by an ad network, so the experience varies by country and time.
Our 2019 pictures show a Skip Ad page with a fake green-card prize box. Treat short links like any link from a stranger: check the address you land on, refuse notification requests and never run a file that arrives as .exe or .msi.
What is Adf.ly?
Adf.ly is a service that turns a long web address into a short one and shows the visitor an advertisement before the real page. The person who made the short link is paid for views of the ad. That is why the pages carry a Skip Ad button and why advertisers pay for the space.
Our 2019 report described it as a service that lets users earn money by shortening links. In October 2026 the address adf.ly took our test browser to linkvertise.com, another link-monetisation service, and we have no registration record to say who runs it.
Why does Adf.ly redirect me to other websites?
A short link redirects by design: it sends you to an ad page and then to the target address. Unwanted redirects to prize pages or fake alerts have two usual causes. One is the ad shown on the page, which comes from an ad network and changes with the visitor.
The other is adware on your computer, usually from a bundled installer, that redirects pages whatever you visit. If it happens on every site, check your extensions and installed apps with the steps above; if only on short links, the cause is the link.
How do I stop notifications from Adf.ly or uclaut.net?
Notifications only appear if you pressed Allow on a request, and you can take the permission back. In Chrome open Settings, Privacy and security, Site settings, Notifications, then remove or block the sites you do not recognise.
Edge keeps the list under Cookies and site permissions, and Firefox under Privacy and Security, Permissions, Notifications, Settings. In Safari use Settings, Websites, Notifications. Our 2019 report linked uclaut.net to Adf.ly notifications; we did not retest it in 2026, so remove any unknown site you find.
I clicked an Adf.ly link and my computer seems infected. What should I do?
Clicking a short link and closing the page does not by itself infect a computer. Trouble starts when you allow a permission, install an extension or run a file. Close the page, check your browser's notification list and extensions page for entries you did not choose, and remove them.
In Windows open Settings, Apps, Installed apps and sort by date. If you ran a downloaded program, start a Microsoft Defender Full scan, then run the offline scan. If you typed a password on a page an ad opened, change it today.
Do I need antivirus to remove Adf.ly ads?
No special tool is needed to stop ads from a website: you close the tab or leave it. Software matters only if an installer or add-on came from an ad.
Then Windows already includes Microsoft Defender, which can run a Full scan and an offline scan, and your browser's extensions page and Windows Installed apps list let you remove what you did not choose.
Our 2019 guide recommended a paid anti-malware program for every case; for a quiet page like the one we tested, that is not needed. Keep your security program updated either way.
Is it safe to click Skip Ad?
The Skip Ad button on a short-link page moves you on to the destination, and clicking it is how the page is meant to work. Danger lies in the other buttons and windows on the page, and in the destination itself.
In our 2019 pictures a fake congratulations box sat beside the button. Press only Skip Ad, close any window that claims you won something, refuse a permission request, and check the address you arrive at. If the destination offers a file that is not what the sender promised, leave.
How can I avoid adware from bundled installers?
Adware arrives in the same installer as a free program, usually from a site that is not the maker's own. Get programs from the maker's own site or the Microsoft Store. When an installer offers Custom or Advanced setup, take it and untick every extra program; refuse Quick or Recommended.
Read each screen before pressing Next. Keep Microsoft Defender and SmartScreen on, and never run a file that a short link or an ad handed you. If a browser starts redirecting after an install, remove the program in Installed apps and the extension in the browser.
Will Fortect remove Adf.ly?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Adf.ly, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Adf.ly: address test (our test, ended on linkvertise.com) (read October 4, 2026)
- Linkvertise: home page reached from adf.ly (read October 4, 2026)
- IANA: RDAP bootstrap registry for DNS (no entry for .ly) (read October 4, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 4, 2026)
- FTC: How to recognize, remove and avoid malware (read October 4, 2026)