
Borat RAT: what it is and how to remove it
Borat RAT is a malicious application that can cause erratic behavior on the machine. The letters "RAT" in the name, stand for Remote Access Trojan, which makes it a serious threat.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If ReimageRepair.exe returns after removal, a full scan can find the entry that brings it back.
Do it yourself · free Remove Borat RAT yourself 6 steps, about 18 minutes, no software needed.
Start the steps
Borat RAT: summary
| Distribution | P2P networks; software "cracks"; malicious links; social engineering |
|---|---|
| NAME | Borat RAT |
| TYPE | Remote Access Trojan; Malware |
| SYMPTOMS | Erratic device behavior, encrypted files, various malfunctions |
| DANGERS | This RAT has a keylogger feature so users' personal data may be stolen and cause monetary losses or even identity theft |
| Detection names | No Microsoft detection name is known |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Damage | Not recorded in the old report |
|---|---|
| Name | Borat RAT |
| Type | Remote access trojan |
| Symptoms | An unknown process in Task Manager |
| Evidence | 6 write-ups by security sites; details still limited |
| File names | ReimageRepair.exe |
| First seen | 5 April 2022 |
| Facts checked | 6 October 2026 |
What Borat RAT does on an infected PC
From our report of Apr 2022 · not reviewed since
Borat RAT overview
The Remote Access Trojan has a keystroke logger module that allows it to record keys that are being pressed.
Keystroke loggers are usually used to steal personal data, like credit card details, passwords, social security numbers, ID card information, and more.
Another powerful feature that this malicious program has is the ability to deliver other malware, like ransomware automatically, without any user knowledge. Ransomware can encrypt peoples' personal files and ask for payment in return for a decryption key.
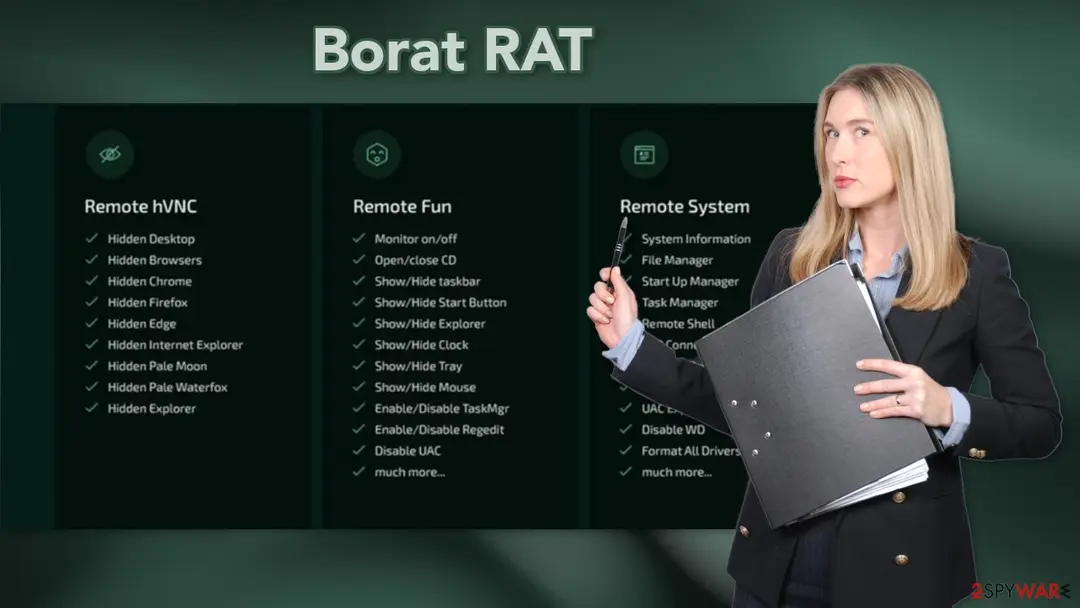
Borat can also record audio through the connected microphone, and record videos using a webcam, which is a serious privacy issue. Crooks can gain complete control of the computer, including the mouse, keyboard, and screen. They can use scare tactics to make their victims paranoid.
Users report hearing strange audio at different times, the desktop and taskbar disappearing, the webcam light flashing, the monitor turning off, the mouse button being swapped, and many more. The virus can also cause damage by stealing Discord tokens and cookies, browser bookmarks, and saved login credentials.
From our report of Apr 2022 · not reviewed since
Avoid malware installations
To avoid malware infections, you should use only official web stores and developer sites for software installation.
Crooks use untrustworthy sources for downloading software. Avoid peer-to-peer file-sharing networks, shady websites, third-party downloaders, and "free file" pages. By using the official sources, you will know for sure that the files you are downloading are safe and not infected.
You should also keep your operating system and software up-to-date. System and program updates can include important security patches. By keeping software updated, it is harder for cybercriminals to exploit holes in the security. This practice should be coupled together with having reliable antivirus software installed on your computer and running system scans with it regularly.
From our report of Apr 2022 · not reviewed since
More from our earlier report on Borat RAT
- Use professional security tools for complete malware removal
- Fix damaged files with a maintenance tool like
What Borat RAT can steal or download
From our report of Apr 2022 · not reviewed since
Borat RAT is a malicious application that can cause erratic behavior on the machine.
The letters "RAT" in the name, stand for Remote Access Trojan, which makes it a serious threat. The Trojan, named after comedian Sacha Baron Cohen's character can mistake many people into thinking that this is a joke.
However, the malware was found not to settle for standard remote access functions. Instead, it includes spyware and ransomware capabilities which means it can deliver ransomware, log keystrokes, perform DDoS attacks, steal login credentials from browsers, etc.
How Borat RAT got on your PC
From our report of Apr 2022 · not reviewed since
There are multiple channels that fraudsters use to spread malware.
The most popular methods include email, "cracked" software, and fake updates. Unreliable sources for downloading files and programs are exploited for cybercriminals' gain. Their primary goal is to trick unsuspecting users into launching malicious files by themselves.
Threat actors use email to include their malicious links or attachments. Usually, they try to disguise the emails and make them look like legitimate important letters from trustworthy entities - banks, and government institutions. Attackers can use many files to deliver malicious programs, like PDFs, executables, JavaScript files, ZIP, and RAR.
How to check the PC for Borat RAT
- File:
ReimageRepair.exe
How to remove Borat RAT
How to remove Borat RAT and lock the attacker out
Someone may have had remote control of the PC.
Cut the connection first, then remove the trojan and secure your accounts.
Step 1: Remove remote access tools and lock the attacker out
Unplug the network cable or turn off Wi-Fi first, so any remote session drops.
In Settings > Apps > Installed apps (Windows 11) or Apps & features (Windows 10), uninstall remote access programs you did not set up yourself, such as AnyDesk, ScreenConnect, TeamViewer or an unknown "support" tool.
Check Settings > Accounts > Other users (Family & other users in Windows 10) for accounts you did not create. Turn off Remote Desktop under Settings > System unless you use it.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 2: Check where ReimageRepair.exe runs from and stop it
ReimageRepair.exeis the part you can see, and its location tells you whether it belongs there. Right-click it on the Processes page of Task Manager and choose Open file location, then right-click the file > Properties > Digital Signatures to see who signed it.An unsigned file, or one in a user folder such as
%AppData%, is the one to remove: end the task, then delete the file.Note the folder name, because the same folder usually holds its other files. This is the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 3: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to Borat RAT or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 4: Remove it from startup
Whatever Borat RAT installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 5: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
From our report of Apr 2022 · not reviewed since
Removal of Borat RAT
Removal of remote access trojans can be a complicated task.
The minute such an infection enters a machine, it does heavy modifications to system files and settings to establish persistence and becomes extremely hard to detect. Usually, it is best to allow antivirus or anti-malware programs to do this automatically.
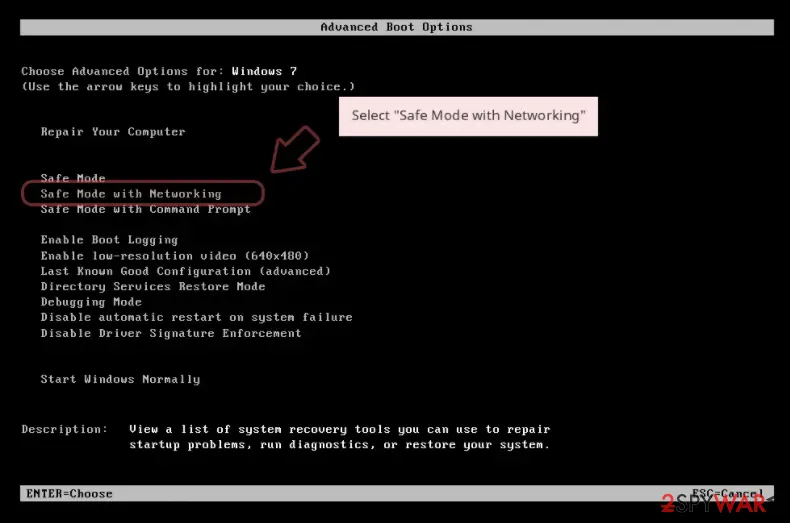
However, in some cases, the malware might disable your anti-malware tools and camouflage its processes as legitimate Windows tasks. If malware is not letting you use antivirus in normal mode, access Safe Mode and perform a full system scan from there.
Windows 7 / Vista / XP
Windows 10 / Windows 8
Once you reach Safe Mode, you can launch a reputable antivirus program. You should update the security program of your choice with the latest definitions, and perform a full system scan to eradicate malware and all its malicious components.
A scan should reveal all malicious files hiding in your device, isolate them, and give the option of removal to you. Trustworthy anti-malware software is a must-have for every individual who spends at least a few minutes on the internet each day. Cybercriminals are getting more creative with how they distribute their dangerous creations. Anti-malware tools are the main instruments of defense.
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
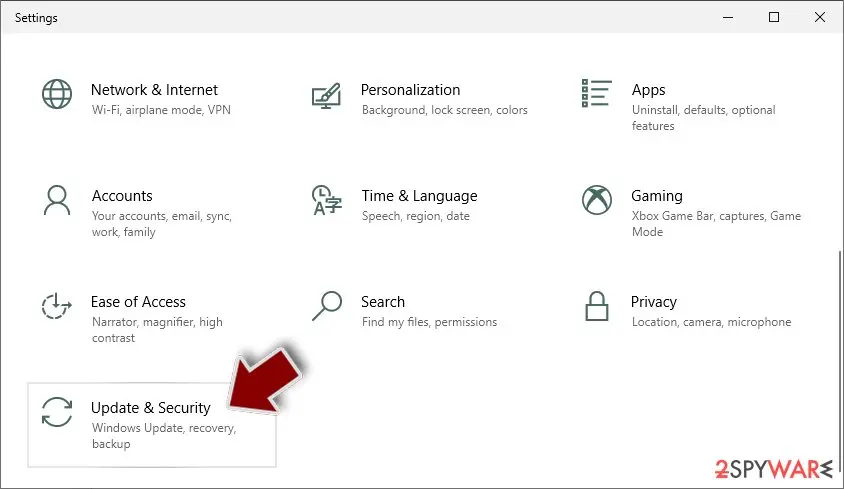
- Right-click on Start button and select Settings.
- On the left side of the window, pick Recovery.
- Click Restart now.
- Select Troubleshoot.
- Go to Advanced options.
- Select Startup Settings.
- Click Restart.
- Press 5 or click 5) Enable Safe Mode with Networking.
From our report of Apr 2022 · not reviewed since
Fix the damaged operating system
Once a computer is infected with malware, its system is changed to operate differently.
For example, an infection can alter the Windows registry database, damage vital bootup, and other sections, delete or corrupt DLL files, etc. Once a system file is damaged by malware, antivirus software is not capable of doing anything about it, leaving it just the way it is. Consequently, users might experience performance, stability, and usability issues, to the point where a full Windows reinstallation is required.
Therefore, we highly recommend using a one-of-a-kind, patented technology of repair. Not only can it fix virus damage after the infection, but it is also capable of removing malware that has already broken into the system thanks to several engines used by the program.
Besides, the application is also capable of fixing various Windows-related issues that are not caused by malware infections, for example, Blue Screen errors, freezes, registry errors, damaged DLLs, etc.
By employing , you would not have to worry about future computer issues, as most of them could be fixed quickly by performing a full system scan at any time. Most importantly, you could avoid the tedious process of Windows reinstallation in case things go very wrong due to one reason or another.
- Download the application by clicking on the link above
- Click on the ReimageRepair.exe
- If User Account Control (UAC) shows up, select Yes
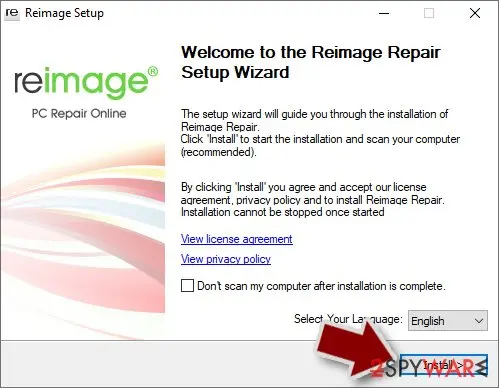
- Press Install and wait till the program finishes the installation process
- The analysis of your machine will begin immediately
- Once complete, check the results - they will be listed in the Summary
- You can now click on each of the issues and fix them manually
After removal: passwords, accounts and prevention
Secure your accounts after the clean-up
Assume that whatever was saved in the browsers on this PC while the PC showed an unfamiliar process called ReimageRepair.exe in Task Manager has been copied:
- passwords
- cookies
- autofill data
Work from a clean device, or from this PC once the offline scan finds nothing.
Start with your main e-mail account, because it can reset everything else, then banking and payment, then social and gaming accounts. Change each password, sign out of all sessions and turn on two-step verification: Turn on two-step verification / secure a hacked account.
The full order, including crypto wallets and card replacement, is in securing your accounts after malware.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
Questions about Borat RAT
Is ReimageRepair.exe a virus?
The name ReimageRepair.exe is not enough to say. Malware often uses technical-sounding names, and harmless updaters often use odd ones. Check three things:
- the folder the file runs from
- the Digital Signatures tab in its properties
- the program that starts it (Startup apps, Task Scheduler or services)
A signed file from a company whose product you use is almost certainly fine. An unsigned file in a user folder that no installed program explains should be removed, and the PC scanned with Microsoft Defender in offline mode.
ReimageRepair.exe keeps coming back. What should I do?
A process that returns after you end it has a restart mechanism, and that is a reason to treat ReimageRepair.exe as unwanted. Check Settings > Apps > Startup, Task Scheduler and the Services list for entries pointing to its folder, and disable them.
Look in Installed apps for anything added the same day and uninstall it. Then delete the folder and run a Microsoft Defender Offline scan, which works before Windows starts and can remove files that are locked or hidden while the system is running.
Can I just delete ReimageRepair.exe?
Deleting ReimageRepair.exe by hand rarely removes Borat RAT. While the trojan runs, Windows may refuse to delete the file, and if you succeed, a scheduled task, a service or a second copy may bring it back at the next restart.
The file can also be only one part of the infection: loaders and remote access tools often install other programs. Use the Microsoft Defender offline scan, which removes the file together with its startup entries before Windows loads, and then check startup items and scheduled tasks as described in the plan.
Should I reset my PC because of Borat RAT?
Only if the signs point to deeper access. Reset when you see an unfamiliar process called ReimageRepair.exe in Task Manager again after removal, when Windows Security cannot start or update, when remote access tools you did not install keep appearing, or when you simply cannot trust the PC any more.
Otherwise, the plan in this guide plus an offline scan is enough. If you do reset, choose Remove everything and Cloud download for a fresh copy of Windows, restore only documents and photos, and reinstall programs from their official sites. Change important passwords from the clean system afterwards.
Why didn't my antivirus stop Borat RAT?
New trojan builds are packed and changed often so that signatures do not match, and some are signed with stolen or bought certificates. Many arrive inside password-protected archives, which scanners cannot open until you extract them.
Some downloads also tell the user to turn off the antivirus "because it gives false alarms", a common line in cracked software instructions. Keep real-time protection on, never disable it for an installer, and run the offline scan whenever you suspect something slipped through.
Can Borat RAT spread to other devices on my network?
Most trojans aimed at home users stay on the PC they infected, but an attacker with remote access can look at the network, open shared folders and try passwords on other devices. Loaders sometimes deliver worms or ransomware that do spread.
Disconnect the PC while cleaning, run a full scan on other Windows PCs, change the router's admin password and the Wi-Fi password if they were saved on the infected PC, and update the router's firmware. If other PCs show the same detection, treat them as infected too.
Why can't I find Borat RAT in antivirus databases?
Because it is new or because it is listed under a different name. Antivirus companies name threats after the family they belong to, and a program that appears as Borat RAT on your PC may carry a generic or unrelated label in their databases.
Many new samples are first detected only by behaviour, without a family name. What you saw, an unfamiliar process called ReimageRepair.exe in Task Manager, is enough to act on:
- end the program
- remove its startup entry
- run a Microsoft Defender offline scan
- secure your accounts
A detection name from a scan is worth noting for later.
What are the signs of a trojan infection?
Most trojans try to leave no visible signs, so look for side effects. Common ones:
- Windows Security turned off or unable to update
- new entries in Startup apps or Task Scheduler
- programs in Installed apps you did not install
- browser settings that changed by themselves
- unusual network activity while the PC is idle
- password-reset or login-alert e-mails you did not trigger
None of these proves an infection on its own. Together with an antivirus alert naming Borat RAT, they are a strong reason to follow the full plan.
Can I keep using the PC while Borat RAT is on it?
Not for anything that matters. As long as the program behind an unfamiliar process called ReimageRepair.exe in Task Manager runs, it can see what you type and what the browser stores, and it may download more malware. Disconnect the PC from the internet while you remove it, and do your banking, e-mail and password changes from another device.
Once the offline scan finds nothing and the sign does not return after a few restarts, normal use is fine. If the scan keeps finding new items, or you cannot remove the startup entry, a reset of Windows is the safer choice.
Will Fortect remove Borat RAT?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Borat RAT, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Wikipedia, the free encyclopedia: Denial-of-service attack (read October 6, 2026)
- Howtogeek: Everything You Need To Know About the Blue Screen of Death (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)
- Microsoft Learn: How Microsoft names malware (read October 6, 2026)