
CoreSync.exe Trojan: what it is and how to remove it
CoreSync.exe - malware that is designed to conceal cryptocurrency mining operations with executable files found in temporary folders. It manages to get on the machine unnoticed and trigger processes without any permissions needed.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If CoreSync.exe comes back after a restart, a full scan can find the task or service that relaunches it.
Do it yourself · free Remove CoreSync.exe Trojan yourself 6 steps, about 18 minutes, no software needed.
Start the steps
CoreSync.exe Trojan: summary
| Distribution | The file can be distributed via torrent services and malicious sites or spam email campaigns when files can be automatically launched on the system and trigger background processes |
|---|---|
| Name | CoreSync.exe Trojan |
| Type | Cryptocurrency miner |
| Issues | The file name is related to Adobe software, but more often gets misused as a process to hide malware behavior in the background. When the process uses high CPU or other resources it should be considered potentially malicious or dangerous |
| Danger | The trojan relies on computer resources to mine cryptocurrency and makes a profit. It can run unnoticed for a long while and cause damage or even infiltrate other intruders silently |
| Placement | If the file is safe it should be found in C:\Program Files (x86)\Adobe\Adobe Creative Cloud\CoreSync. If not, you can be sure that file is disguising the trojan or is related to other shady programs |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Damage | Not recorded in the old report |
| Symptoms | An unknown process using the processor or graphics card |
| Evidence | 4 write-ups by security sites; details still limited |
| Files | CoreSync.exe and C:\Program |
| Location | C:\Program |
| First seen | 15 May 2020 |
| Facts checked | 6 October 2026 |
What CoreSync.exe Trojan does
From our report of May 2020 · not reviewed since
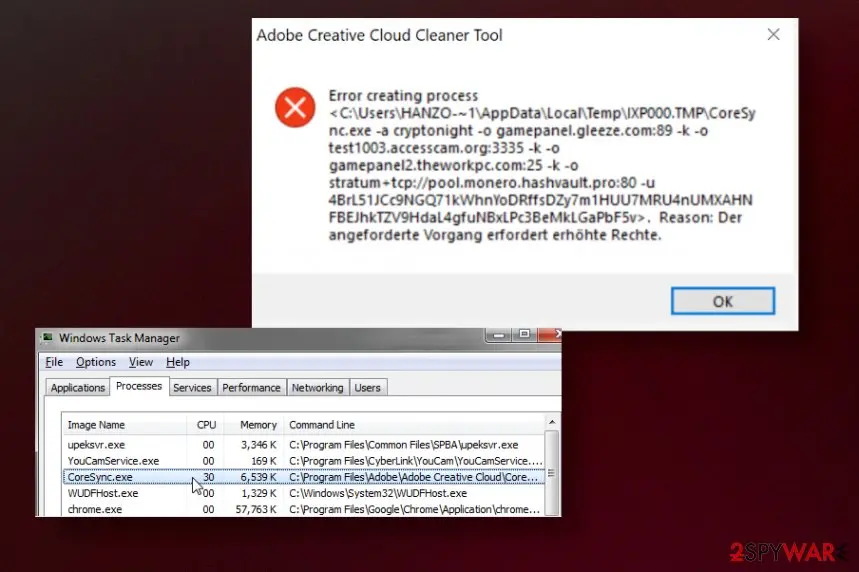
CoreSync.exe is the trojan that uses processes and files that run in the background triggering cryptojacking functionalities
CoreSync.exe - malware that is designed to conceal cryptocurrency mining operations with executable files found in temporary folders.
It manages to get on the machine unnoticed and trigger processes without any permissions needed. The trojan launches mining operations that use the resources of the infected computer and makes a profit without interfering with users at all.
However, the threat eventually is noticed by the owner of the computer because background processes cause issues with the performance and speed of a machine and trojan uses exhaustive power consumption, near 200% of CPU and causes attention to those powered.exe or CoreSync.exe files that continuously runs in the background out of nowhere.
The rise in the usage of these resources like RAM or GPU triggers issues like overheating. Unfortunately, these issues become noticeable after a while, so malware can run for a long time until the person can guess that there is something wrong.
CoreSync.exe virus is not using your money, accounts, or cryptocurrency funds to get money. However, trojans spread using stealthy methods and can be included in the pack with other malware, act as a backdoor besides mining the cryptocurrency. When malware is present on the system it can lead to more serious infections without you even noticing, so the sooner you clean all the threats, the better.
CoreSync.exe, in general, is the name of a legitimate file belonging to Adobe software. However, users complain about shady processes and CPU or RAM issues. Developers have stated that such symptoms like the high usage of resources and system problems cannot be caused by this software component and that the name is misused by malicious actors to hide the purpose and dangerous behavior.
CoreSync.exe can be associated with a cryptojacking malware, but this is the name of the genuine software component. Adobe Acrobat uses this executable as a core synchronizer. When the file is legitimate it should be found in the Program Files folder under the Adobe directory.
The first tell-all about malicious purposes should be the placement. If the executable is found somewhere else besides C:\Program Files (x86)\Adobe\Adobe Creative Cloud\CoreSync, you need to consider the file malicious and associated with the trojan.
The safe CoreSync.exe runs the process of synchronization and handles such issues, so you may see it in the background, but not all the time. This file is not an essential file of the Windows system, so you can remove it if it causes any issues or is related to questionable programs or trojan, in many cases.
It is a common technique used by malware creators to misuse file names that are popular and ask their malicious activities. This is why crypto mining trojans rise in popularity of malware.
In comparison to ransomware or other financial gains-based threats, cryptocurrency miners are more dangerous and should be considered seriously. Even though there is no blackmailing or direct interaction with the victim, CoreSync.exe makes huge amounts of money. Monero cryptocurrency is the preferred one for this trojan miner. Creators can make fortune and leave the system unnoticed if the process is silent and quick enough.
That is unfortunate for the user because CoreSync.exe miner trojan can leave some damage or additional malware in the system once it leaves. It is especially dangerous when you cannot detect or find any particular program that causes all the problems and interferes with the performance and speed.
This is why many experts offer to have anti-malware tools up and running more often. You can remove CoreSync.exe sooner and avoid serious damage if your AV tool is launched while the threat is active and not hidden deep in the system. If you experience issues with the speed and performance of the machine trojan may already be running for a while.
CoreSync.exe trojan is focusing on mining the Monero cryptocurrency by running on the processor resources, so constant freezes and crashes are inevitable. Trojan can also exploit some Microsoft processes and evade AV detection because the file is rarely detected as malicious. Especially, when the files dropped by brute-forcing the login credentials of targeted servers.
You still need to employ a professional anti-malware tool for proper CoreSync.exe removal because only such programs can find all related files and applications and fully clear them off of your device. You should also take into consideration that malware can inject malicious files in some folders:
These changes are not the only ones that CoreSync.exe miner trojan can trigger, so any control that malware has over the system functions or programs can cause issues and errors. You need to repair these changes and recover from virus damage by fixing affected files and programs using something like .
- %AppData%
- %Local%
- %LocalLow%
- %Roaming%
- %Temp%
From our report of May 2020 · not reviewed since
More from our earlier report on CoreSync.exe Trojan
- CoreSync.exe removal is needed when the malware is still running and to ensure that other threats are not left behind.
- The best way to clean the machine is by using anti-malware tools
- There is a high risk of system damage and virus-made changes in the system, so rely on and clear these issues, repair programs, and computer functions safely
How CoreSync.exe Trojan spreads and got on your PC
From our report of May 2020 · not reviewed since
Trojans, worms, and other threats that focus on background processes can silently infect the machine and cause all the needs processes to launch without causing any symptoms for the victim to notice. Thrid-party installers and malicious sites can inject malicious payload automatically, so you do not know what happened. When you click on malicious pop-up or banner on the shady page the payload drop is automatic.
It also may happen when JavaScript file downloads actual malware on the computer instead of a pirated program or a game cheat, licensed version of the software. Such files like executables and malicious scripts can be injected and affect the machine from the first launch.
Some of the malicious files can also get on the computer via spam email campaigns when malicious scripts get triggered after downloading and opening the MS document on the machine. Such emails often get disguised as notifications from companies or services, online shopping sites, delivery services, and similar popular companies, so people do not think twice and open the document immediately.
Check your PC for CoreSync.exe Trojan
- Path:
C:\Program - File:
CoreSync.exe
How to remove CoreSync.exe Trojan
Miners hide when Task Manager opens and add Defender exclusions.
The steps deal with both, then remove the files.
Step 1: Check where CoreSync.exe runs from and stop it
In Task Manager (Ctrl + Shift + Esc) find
CoreSync.exeon Processes, right-click it and choose Open file location before ending anything.Windows' own files live in
C:\Windows\System32; the same name in%AppData%, %Temp% or C:\Users\Public is an impostor. If the folder is wrong, right-click the process again, choose End task and delete the file.If it starts again within seconds, a task or another process restarts it, so run the scan step in Safe Mode. Task Manager works the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 2: Delete scheduled tasks that bring it back
Programs like CoreSync.exe Trojan add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 3: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Turn Microsoft Defender back on and remove its exclusions
Open Windows Security > Virus & threat protection > Manage settings and switch Real-time protection and Tamper Protection on.
Further down, under Exclusions, click Add or remove exclusions and remove every folder, file or process you did not add, because malware excludes its own folder so the scan skips it.
If the switches are greyed out with "This setting is managed by your administrator", a policy was written to the registry, which the scan in the next steps usually clears. The pages are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Turn off Microsoft Defender protection for a moment On uGetFix
Step 5: Delete the files and folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them. Start with
C:\Program: paste it into the File Explorer address bar and delete the folder once nothing from it is running.Then press Windows + R, open
%LocalAppData%,%AppData%and %ProgramData% one by one, and look for folders with the same name or created on the same day.If Windows says a file is in use, end it in Task Manager or delete it after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 6: Scan the PC, then run the offline scan
A scan finds the parts of CoreSync.exe Trojan that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
From our report of May 2020 · not reviewed since
Clear any traces of malware from the machine by running proper CoreSync.exe trojan removal tools
CoreSync.exe virus can run programs and disable existing applications to affect system performance, speed, and AV detection tools.
There are some features like Safe Mode that allow bypassing some changes, so enter this mode by following the guide below before you run the anti-malware program.
To remove CoreSync.exe properly, get a professional anti-malware tool or security software like or and run the full system scan using those. When all the places of the computer get checked for suspicious or malicious files and programs, you can easily get all the indications and delete threats quickly.
Besides this step of the CoreSync.exe removal, you also need to take care of all the startup and Windows registry alterations that trojans trigger. Some essential files and folders get affected behind your back, so run to fix the malware damage on the device.
[GI=method-1]CoreSync.exe trojan can be persistent and powerful, so rely on AV tools and reboot the machine before the scan to ensure better results
Questions about CoreSync.exe Trojan
Can CoreSync.exe damage my computer?
A miner does not usually destroy files, but running the processor or graphics card at full load for weeks raises temperatures, wears out fans and shortens laptop batteries. It also makes the PC slower and raises the electricity bill.
The bigger risk is what came with it: miners are often installed by loaders or bundled with cracks that also drop password stealers. That is why removing CoreSync.exe should be followed by a full offline scan, and, if the PC shows other signs, by changing the passwords saved in your browsers.
How do I make sure CoreSync.exe is really gone?
Restart the PC, leave it idle for half an hour without opening Task Manager, then check whether the fan is quiet and the processor load is low. Open Task Manager afterwards and look for CoreSync.exe or a new name with the same behaviour.
Check Task Scheduler and the Startup list again for entries pointing to the old folder. Finally, open Windows Security and confirm that real-time protection is on and that no exclusions were added. A clean offline scan together with a quiet idle PC is a good sign the miner is gone.
Is CoreSync.exe part of CoreSync.exe Trojan?
Yes, CoreSync.exe is one of the files we found in infections with CoreSync.exe Trojan. Malware often uses names that look like Windows or common programs, so the name alone is not proof; the location matters too.
Right-click the process in Task Manager and choose Open file location. A file with this name in a user folder or a random-named folder is very likely malicious. Do not just delete it by hand; run the offline scan so related tasks and entries go too.
Is it enough to quarantine CoreSync.exe Trojan?
Quarantine stops the file from running, which is the main point. It is not the whole clean-up, though. Malware rarely consists of one file: there may be a scheduled task, a startup entry, a second copy or a payload that was installed later.
Run a full scan and the offline scan, check Task Scheduler and Startup apps for unfamiliar entries, and follow the plan in this guide. Never restore an item from quarantine unless you are certain it was a false alarm.
Windows Security keeps finding CoreSync.exe Trojan again. Why?
Something is reinstalling it. Common causes are a scheduled task that downloads it again, a second program from the same source, an infected USB drive that is plugged in regularly, or another infected PC on the same network. Remove the detection, then check Task Scheduler, Installed apps sorted by date and every connected drive.
Run the offline scan with all USB drives unplugged. If the detection still comes back, resetting Windows is often faster than continuing the search. Copy only documents and photos before a reset.
Do I need to reinstall Windows to get rid of CoreSync.exe Trojan?
Usually not. A thorough clean-up is enough when the offline scan finds nothing afterwards and you do not see CoreSync.exe using the processor or graphics card at full load again. A reset is the safer choice if an attacker had remote control, if security tools were switched off, or if detections come back after every clean-up.
Windows 11 can reset itself without a USB stick under Settings > System > Recovery > Reset this PC. Copy documents and photos out first and scan the copies. A reset does not change passwords or undo stolen data, so the account steps still apply.
Could CoreSync.exe Trojan have come from a website?
Visiting a website alone rarely installs malware on an up-to-date Windows PC. What websites do is persuade people to download and run something:
- a fake update
- a crack
- a codec
- a command pasted into the Run box
For CoreSync.exe Trojan, the exact route is not known yet, but CoreSync.exe using the processor or graphics card at full load means a program or script was started on the PC at some point.
Check your Downloads folder and browser history for the days before the sign appeared, and remove any program installed then. Keeping Windows, the browser and Microsoft Defender updated closes the few routes that need no click at all.
Did CoreSync.exe Trojan steal my passwords?
There is no evidence either way yet, because CoreSync.exe Trojan has not been analysed in public. The reported sign, CoreSync.exe using the processor or graphics card at full load, does not show theft by itself. However, malware of this kind is often installed together with a password stealer, which works in seconds and leaves nothing to see.
The cautious approach costs little: once the PC is clean, change the passwords saved in your browsers from another device, starting with e-mail, then banking and payment accounts. Sign out of all sessions and turn on two-step verification. If a bank card was saved in the browser, ask the bank about a replacement.
Can a cryptominer damage my hardware?
Not directly in most cases; modern processors and graphics cards slow down before they overheat. But weeks of constant full load wear fans and batteries faster, raise temperatures inside laptops and add to the power bill. Dust-clogged laptops suffer most.
Once the miner is removed, the load drops and normal wear resumes. If fans stay loud afterwards, clean the vents, and check in Task Manager that nothing else is still using the processor or graphics card. A laptop cooling pad can help while you clean up.
Will Fortect remove CoreSync.exe Trojan?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For CoreSync.exe Trojan, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Adobe: Coresync.exe PLEASE KILL IT!!! (read October 6, 2026)
- Coindesk: Hackers Plant Crypto Miners by Exploiting Flaw in Popular Server Framework Salt (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)
- Microsoft Learn: How Microsoft names malware (read October 6, 2026)