
Ffshrine: what it is and how to remove it
Ffshrine virus is a malicious Trojan horse infection that might have been injected into Ffshrine ("Final Fantasy Shrine Forum") domain. The detection was flagged as High Risk and initially considered as a false positive detection, though later it has been revealed that the URL of the domains FFshrine.net and Ffshrine.org has been hacked and misused for Ffshrine Trojan distribution.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Programs like Ffshrine usually arrive in groups; a free scan lists the companions that are easy to miss.
Do it yourself · free Remove Ffshrine yourself 5 steps, about 15 minutes, no software needed.
Start the steps
Ffshrine: summary
| Name | Ffshrine |
|---|---|
| Type | Trojan horse |
| Distribution means | Hacked websites, fake AV alerts, backdoor access, exploit kits, rootkits, Trojan downloaders, Trojan droppers |
| Precautions | Keep a powerful antivirus installed. Never click on online pop-ups warning about virus infection and urging to download a scanner for free. |
| Symptoms | System crashes, high CPU usage, malicious processes running in the background, questionable programs installed on the system, terminated AV tools. |
| Detection names | No Microsoft detection name is known |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 4 more facts
| Damage | Not recorded in the old report |
|---|---|
| Evidence | 4 write-ups by security sites; details still limited |
| First seen | 10 April 2020 |
| Facts checked | 6 October 2026 |
What Ffshrine does on an infected PC
From our report of Apr 2020 · not reviewed since
More from our earlier report on Ffshrine
- Initially, registered forum users started reporting about unusual Norton AV alerts Web Attack: Formjacking Website 2 showing up when browsing the forum.
- According to cybersecurity researches, criminals misuse many famous names of AV tools, including Norton, McAfee, Windows Defender, and others.
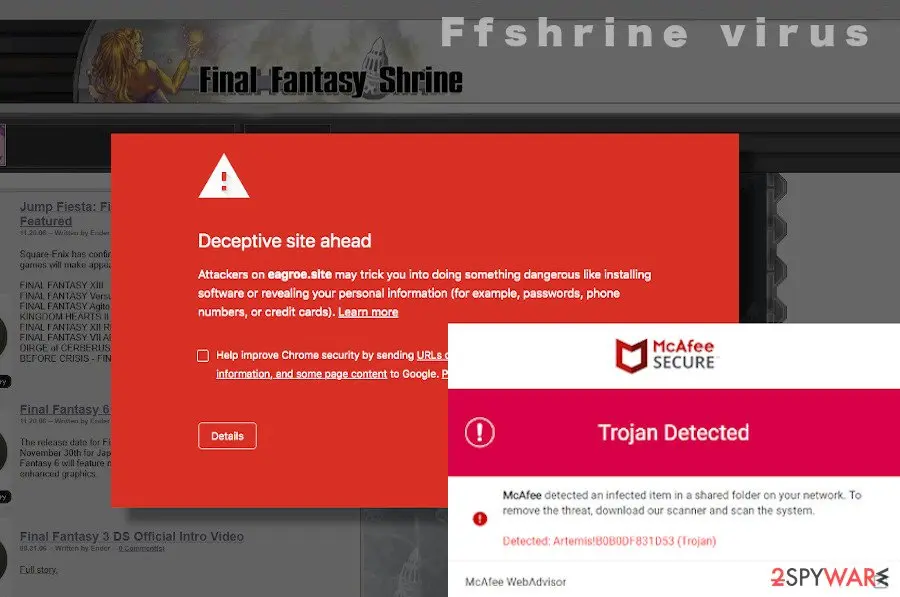
- One of the malicious pop-up imitating McAfee design warns about Trojan detection Artemis!B0B0DF831D53 found in a shared folder of the network.
- It's essential to draw attention to the fact that such notifications show up for people who are not using McAfee.
- Viruses like Ffshrine trojan can be terminated with a reputable antivirus program, for example or .
- Yet another misleading pop-up Web Attack: Formjacking Website 2 detection by Norton raises more questions about its authenticity.
- As Norton explains, Formjacking is a type of website hack when criminals inject malicious JavaScript codes, which may result in a disclosure of information, such as credit card details, logins, and similar.
- Several Norton users reported such alerts of security forums and assured red that the Formjacking Website 2 detection pop-up indicates the IP address from which the attack has been initiated.
- Therefore, the warning delivered by Norton can hardly be treated as a false negative.
- However, it can only be genuine if the PC runs the Norton security suite.
What Ffshrine can steal or download
From our report of Apr 2020 · not reviewed since
Ffshrine virus is a malicious Trojan horse infection that might have been injected into Ffshrine ("Final Fantasy Shrine Forum") domain.
The detection was flagged as High Risk and initially considered as a false positive detection, though later it has been revealed that the URL of the domains FFshrine.net and Ffshrine.org has been hacked and misused for Ffshrine Trojan distribution.
Ffshrine virus on the infected domains typically manifests in the form of fake AV security software alerts that urge people to download software to eliminate the infection. Thus, clicking on a download link may lead to the infiltration of a dangerous Trojan, Spyware, key logger, or activate ransomware payload.
Otherwise, clicking on possibly fake AV download pop-up may result in a Ffshrine virus infiltration.
Forum.ffshrine, which has had a considerable number of registered users before the closedown, has been represented as a forum where people can discuss the Final Fantasy series of Japanese Role-Playing Games. However, only the minority of the users were aware of such a game at all.
The primary service of this questionable, though very popular, forum was to share original soundtrack albums from media like animes, games, and movies in archived .zip, .rar, .tar, and other forms. Such activity has been approved by most of the registered users who seek free services, but at the same time disapproved by opponents of illegal free file-sharing services.
Keep in mind that domains that initiate free file-sharing activities are a great target for hackers and other cybercriminals who may seek to cause the website's crash or distribute malicious components via downloadable database.
If the Ffshrine Trojan virus is launched on the system, it may perform a multitude of malicious activities on the network. Trojans are used by hackers to gain access to people's data, analyze keystrokes, or gain backdoor access to the system. Such and similar cyber infections can:
Ffshrine virus and similar may be difficult to detect, and as they tend not to disclose their presence directly. A Trojan may reside silently and keep modifying the system's registry entries and weakening its core. The presence of the virus may manifest as software crashes, BSODs , questionable processes running on the background, high CPU usage, and similar.
While the slow system and its malfunctioning may be irritating, the most significant risk Trojans like Ffshrine virus pose is a ransomware or spyware download. These infections may encrypt documents and demand a ransom in exchange for decryption software. At the same time, spyware may capture keystrokes and take screenshots to steal banking information, ID card numbers, and other most sensitive details.
For those who have any suspicions that the Ffshrine virus may have entered the system, we highly recommend rebooting the system into Safe Mode with Networking and initiating a full system scan. Unfortunately, there's no way to remove FFshrine or other Trojans of its type manually. The longer the dangerous program keeps active on the system, the higher is the risk of damage.
- Remove pieces of information stored on the system;
- Block access to particular data and files;
- Modify the system's registry entries and compromise other crucial components;
- Copy data and transmit it to remote servers;
- Diminish PCs performance and disrupt network connections;
- Block AV tools and self-replicate after inappropriate removal;
- Open backdoor access to ransomware and other viruses.
How Ffshrine got on your PC
From our report of Apr 2020 · not reviewed since
A Trojan related to the Ffshrine domain is a dangerous infection, which may cause the system's crashes and initiate data leakage.
According to experts, it is distributed via fake pop-ups imitating trustful AV security tools. Perfectly emulating the design and other features, these pop-ups might have tricked thousands of users and lure them into cybercriminals' hands.
The forum that has been found spreading the virus is currently down. As soon as a malicious JavaScrip was optioned, the widespread discussion and music streaming domains were closed entirely and are not reachable up-till-now. Nevertheless, this fact does not guarantee that the Ffshrine or its clones are not circulating on the Internet via other popular hacked domains.
In addition to infected domains, such and similar cyber infections can get inside PCs via backdoor access, exploit kits, rootkits, Trojan downloaders, Trojan droppers, and similar highly suspicious means. Therefore, it's essential to ensure the full system's protection.
First of all, rely on a comprehensive AV security tool, which has a powerful virus detection engine and make sure to download required updates regularly. Moreover, do not access suspicious websites and ignore misleading pop-ups, banners, hyperlinks, and other content that can initiate redirects to unknown domains.
Last, but not least recommendation is to pay close attention to freeware and be careful with torrent websites since they tend to have security vulnerabilities making them easily accessible to criminals. The system's security with a pack of reliable programs and your awareness about dangers online should be sufficient to maintain your safety.
How to remove Ffshrine
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Programs like Ffshrine add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 2: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after Ffshrine, its publisher or created on the day the problem started. Delete those folders, and check C:\Program Files and C:\Program Files (x86) too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
A scan finds the parts of Ffshrine that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Ffshrine can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Apr 2020 · not reviewed since
Guide for FFshrine virus removal
If you consider your PC infected with a Trojan, there's only one way to get rid of it, i.e., a full system scan with a professional AV tool.
If you have already tried, but Ffshrine removal failed without even getting started, the virus may be running the command to block the antivirus program. To make it run, please restart the system into Safe Mode with Networking, as explained below.
However, Ffshrine removal should also be followed by a careful system's repair. As we have pointed out earlier, Trojan infections contaminate a multitude of entries on the Registries, corrupt running processes, delete libraries, and cause similar damage.
[GI=method-1]If your security software is blocked, before starting Ffshrine removal restart the system into Safe Mode with Networking. The guide below will help you to do that.
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed ffshrine in the list of installed apps, a sign of a program that could read browser data, the clean-up is only half of the work.
The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
Questions about Ffshrine
Is Ffshrine a virus?
Most programs that appear the way Ffshrine did are not viruses in the strict sense. They are potentially unwanted programs:
- real software that arrives bundled with other downloads and then shows offers
- changes browser settings
- starts with Windows
Some are harmless, some are annoying and a few carry adware. What makes it worth removing is that you did not choose it.
Uninstall it from Installed apps and check the startup list and the browsers for anything added the same day. If it refuses to uninstall or returns after a restart, treat it as more serious and run a Microsoft Defender offline scan.
Ffshrine came back after I uninstalled it. Why?
Something else is reinstalling it. Common causes are a second program from the same publisher, a scheduled task that downloads it again, or a browser extension that keeps prompting for it. Sort Installed apps by install date and uninstall each entry from the same day that you did not choose.
Then open Task Scheduler and look in the Task Scheduler Library for tasks with updater-style names that you do not recognise. Check Startup apps in Task Manager too. If Ffshrine still returns, start Windows in Safe Mode, uninstall it there and run a Microsoft Defender offline scan, which looks for loaders that ordinary scans can miss.
Which malware family is Ffshrine?
That is not known yet. Ffshrine has been reported by people who saw ffshrine in the list of installed apps, but no sample has been analysed publicly, so security companies have not assigned it to a family. The name you see may be a file or program name chosen by the authors, not a family name.
This does not stop you from removing it: the startup points, the offline scan and the account steps are the same for most families of this type. If Microsoft Defender or another scanner gives the file a detection name, write it down; that name is the best clue to the family and is useful when you report the incident.
Do I need to reinstall Windows to get rid of Ffshrine?
Usually not. A thorough clean-up is enough when the offline scan finds nothing afterwards and you do not see ffshrine in the list of installed apps again. A reset is the safer choice if an attacker had remote control, if security tools were switched off, or if detections come back after every clean-up.
Windows 11 can reset itself without a USB stick under Settings > System > Recovery > Reset this PC. Copy documents and photos out first and scan the copies. A reset does not change passwords or undo stolen data, so the account steps still apply.
My antivirus was on. How did a trojan get past it?
Antivirus programs see a file only when it is written or run, and criminals test each new build against popular scanners before release. Detection catches up within hours or days, which is often after the first victims ran it.
Archives with passwords, installers that fetch the malware later, and scripts run through PowerShell make the job harder. That is why behaviour such as downloading cracks or pasting commands matters more than any setting. Keep Windows and Defender updated, and turn on Reputation-based protection in App & browser control.
Should I check my other computers too?
Yes, it takes little time and removes doubt. Ffshrine itself usually stays on one PC, but the download that carried it may have been copied to other computers, shared drives may hold the same installer, and an attacker who had access could have tried saved passwords on other devices.
Run a full scan on every Windows PC in the home or office, check shared folders for the original download, and change Wi-Fi and router passwords if they were stored on the infected machine.
Should I report Ffshrine?
Report it if you lost money, if accounts were taken over, if you are a business, or if the trojan came through a scam call. A police or national cybercrime report gives you a reference number for your bank and insurer and helps link cases.
You do not need to report a trojan that antivirus blocked before it ran. Before reporting, write down the dates, the detection name, file names and any messages or transactions linked to the attack; screenshots of antivirus alerts are useful evidence. The country list is in the report section above.
How do I know if my PC has Ffshrine?
Often you do not, which is the point of a trojan. Possible signs are an antivirus alert naming Ffshrine or a generic trojan detection, unknown programs or scheduled tasks, processes with random names in Task Manager, browser extensions you did not add, security settings turned off, slower performance, or account alerts about logins from unknown places.
The reliable check is a full scan followed by Microsoft Defender's offline scan. If you recently ran a crack, a fake installer or a command a website told you to paste, scan even without symptoms.
Can I keep using the PC while Ffshrine is on it?
Not for anything that matters. As long as the program behind ffshrine in the list of installed apps runs, it can see what you type and what the browser stores, and it may download more malware. Disconnect the PC from the internet while you remove it, and do your banking, e-mail and password changes from another device.
Once the offline scan finds nothing and the sign does not return after a few restarts, normal use is fine. If the scan keeps finding new items, or you cannot remove the startup entry, a reset of Windows is the safer choice.
Will Fortect remove Ffshrine?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Ffshrine, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Kaspersky: What is a Trojan Virus? (read October 6, 2026)
- Norton: What is Formjacking and How Does it Work? (read October 6, 2026)
- Ugetfix: How to fix Windows 10 BSOD Error 0x00000139 (KERNEL_SECURITY_CHECK_ FAILURE)? (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)