
FileRepMalware: what it is and how to remove it
FileRepMalware is a generic trojan detection primarily associated with hacked KMSPico software, capable of stealing credentials and downloading additional malware. The threat spreads through cracked software and bundled installations.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If FileRepMalware keeps coming back after uninstalling, a scan can find what reinstalls it.
Do it yourself · free Remove FileRepMalware yourself 5 steps, about 15 minutes, no software needed.
Start the steps
FileRepMalware: summary
| Alternative name | Win32:Evo-gen [Susp] |
|---|---|
| Related to | KMSPico |
| Category | Adware/ trojan horse |
| Prevention tips | Avoid possible infections of adware or malware by taking control of your downloads (Custom configuration), preventing visits to third-party pages, and installing reputable antimalware on your machine |
| Main dangers | Can be used to infect the system with malware; can steal personal information |
| Detection names | No Microsoft detection name is known |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Distribution | Not recorded in the old report |
|---|---|
| Damage | Not recorded in the old report |
| Name | FileRepMalware |
| Type | Loader |
| Symptoms | An unknown program in Installed apps |
| Evidence | 8 write-ups by security sites; details still limited |
| First seen | 2 January 2021 |
| Facts checked | 5 October 2026 |
What FileRepMalware does on an infected PC
From our report of Jan 2021 · not reviewed since
FileRepMalware is a potential threat reported on users' computers by antivirus programs and tools
FileRepMalware is the cyber threat that can have various functionalities from PUP to trojan.
This detection name also is known as Win32:Evo-gen . In most cases, antivirus terminates the threat and reports about the already eliminated intruder. It is associated with suspicious KMSPico installations and similar apps that are supposed to activate programs without the developer's knowledge. But there is a big possibility that this malware gets on the system as a virus itself and proliferates Windows system.
Since various commercial content comes to your screen due to this infection, it is believed that FileRepMalware virus is a PUP but other detection names associated with the virus show trojan functionalities and possible danger to your system. You shouldn't ignore those alerts and employ AV to clean the device.
The FileRepMalware virus has been considered as a Trojan Horse. It's one of the generic detections, which means that antivirus fails to recognize the exact behavior of the file, but due to suspicious traits, classify it as potentially malicious, and immunize immediately. Besides, the popularity of the file seems to be important as well.
The technical references of the FileRepMalware, which is Win32:Evo-gen , can be translated as follows - Win32 means that the reported file is a part of Windows system, while the Evo-gen imply a generic classification of trojan-type files.
If your antivirus returned an alert urging to remove FileRepMalware PUP from the system, all certified security specialists would agree that should do so without delay. This potentially unwanted program (PUP) or file has been discovered spreading with a fake KMSPico app.
The latter is capable of downloading an adware program to the system. Therefore, the malware may be responsible for opening the back door and executing other malware (adware, browser hijacker) to the system.
To prevent suspicious activities that malware is capable of doing, you should initiate FileRepMalware removal asap. If your antivirus has already warned you about this threat, terminate it without any doubt. Additionally, fix the damage caused by this malware with the help of or another reliable security tool. Those who did not deal with malware before should know these facts:
Unfortunately, more updated and severe malware can delete files on your system or even add new suspicious data on the device to make sure the main virus is persistent and difficult to remove. When FileRepMalware virus is on the system, repetitive errors appear on the screen, and various programs even get shut down out of nowhere.
You need to focus on removing FileRepMalware because slow computer performance is only the start of frustration and possible damage to your device that this threat can cause. If you store your personal information on the computer, malware can access that and even use in further scams when you receive spam email messages or suspicious calls on the phone.
Also, repair tools like can improve the performance by cleaning possible virus damage and fixing issues.
- Advertising malware can cause real havoc on the system. Adware programs generate an excessive amount of third-party advertisements in such intrusive forms as pop-ups, banners or interstitials.
- Ads injected by malware can cause redirects to suspicious or even dangerous websites.
- Malware programs can hijack web browser. In other words, they can take over the start page, search provider, URL address of the new tab, and furthermore displayed compromised search results.
- The FileRepMalware virus may also use tracking cookies or other small files for tracking people's browsing activities. Usually, tracking cookies gather some pieces or sensitive information, including IP address, email address, geo-location, name, and similar.
From our report of Jan 2021 · not reviewed since
More from our earlier report on FileRepMalware
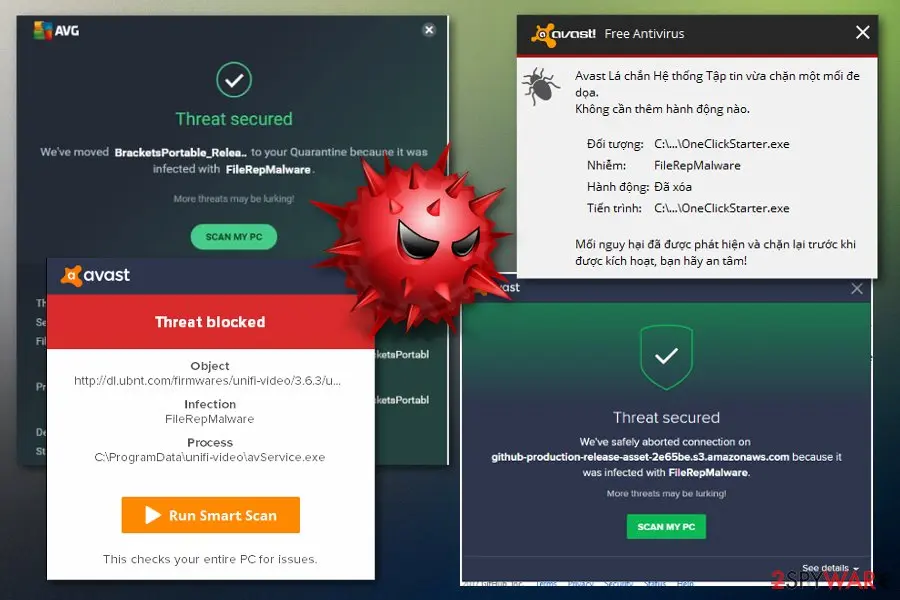
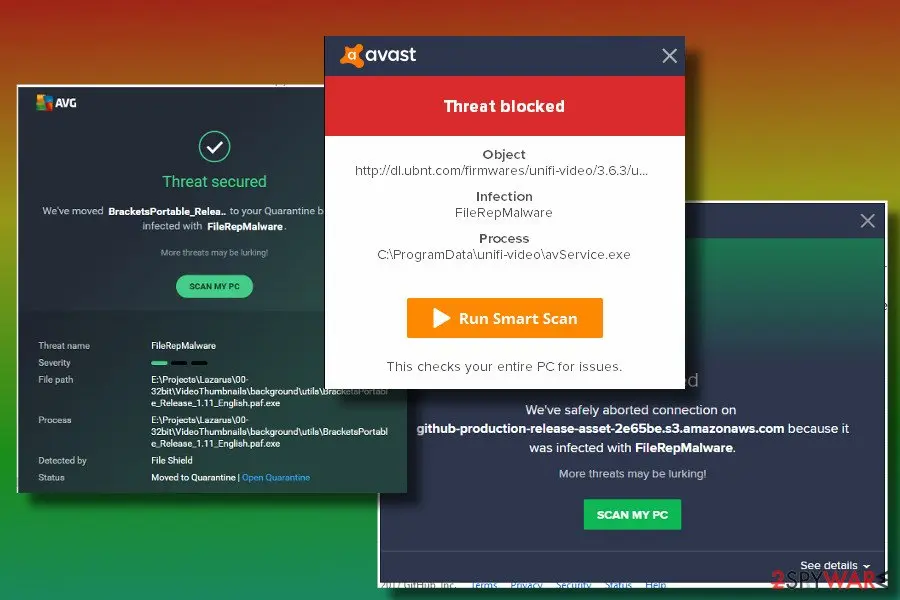
- Most commonly Avast and Avg AV engines reporting about the potential danger of the file or website.
- Detele FileRepMalware automatically using anti-malware program, repair system with
What FileRepMalware can steal or download
From our report of Jan 2021 · not reviewed since
However, if the worst had happened and a Trojan horse entered your Windows computer system by the name of FileRepMalware, you need to be prepared to face unwanted and even damaging consequences. Trojan infections never bring anything positive and sometimes are very hard to detect by the human eye.
If you have ever been infected with a trojan via FileRepMalware, you will supposedly receive increased CPU and GPU work. Also, the malware might relate to software and computer slowdowns, start injecting harmful executables in different locations and run malicious processes in the Windows Task Manager directory.
Be aware if FileRepMalware appears to be a malicious program and not just an ad-supported application. Trojan horses might relate to the collection of personal data and crucial system details. If you discover this dangerous threat, do not hesitate and grab reputable anti-malware software to permanently delete the virus from the machine.
How FileRepMalware got on your PC
From our report of Jan 2021 · not reviewed since
Typically malware spreads as a part of legitimate free apps.
Indeed, illegal or dangerous programs can also transmit potentially malicious files, but needless to say that such programs should never be installed. Few people reported that they were not allowed to install specific software updates due to the AV detection of these malicious files.
To proceed with the installation, they disabled the antivirus temporarily. Please don't do that! Although AV engines can be wrong, the warning about a potentially malicious file should not be ignored as you can end up with malware on your PC. Besides, having an expert-tested antimalware program is always crucial for any type of computer system.
Also, it's essential to check whether an "Advanced" or "Custom" installation option is available. To monetize free services, freeware developers often attach PUPs to the main installer and discloses them under "Quick" or "Basic" installation methods. Therefore, to prevent unwanted programs on the system, be extremely careful when choosing and installing free apps.
To add, we want to say that various potentially malicious and potentially unwanted applications are distributed by using third-party gaming, gambling, and porn sources. Be aware of what type of content you entire throughout the web as questionable-looking websites only increase the risk of the appearance of a malicious program.
How to remove FileRepMalware
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to FileRepMalware or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 2: Remove it from startup
Whatever FileRepMalware installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
If you want to try to remove FileRepMalware manually, remove all potentially unwanted programs from Control Panel. Also, check all Windows and Windows System folder and HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Run folder in Windows Registry:
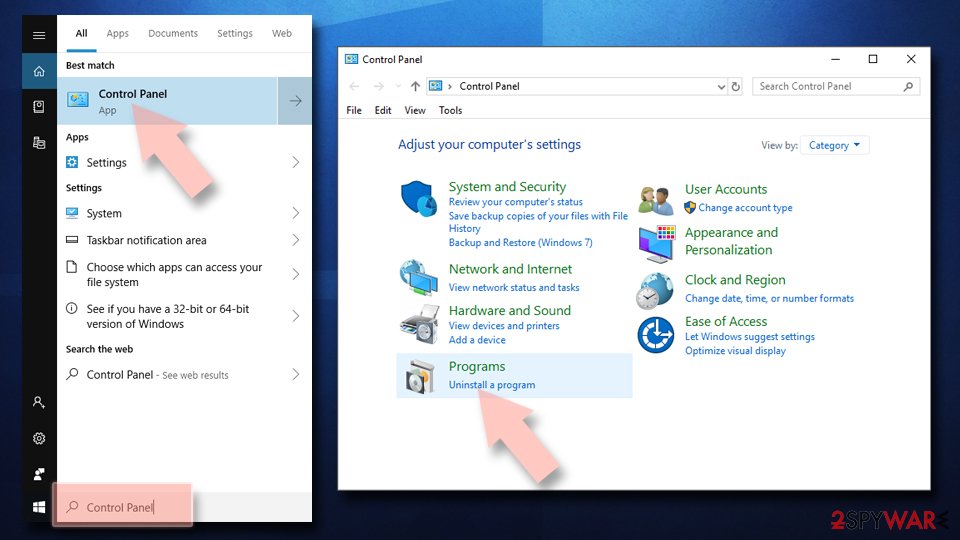
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
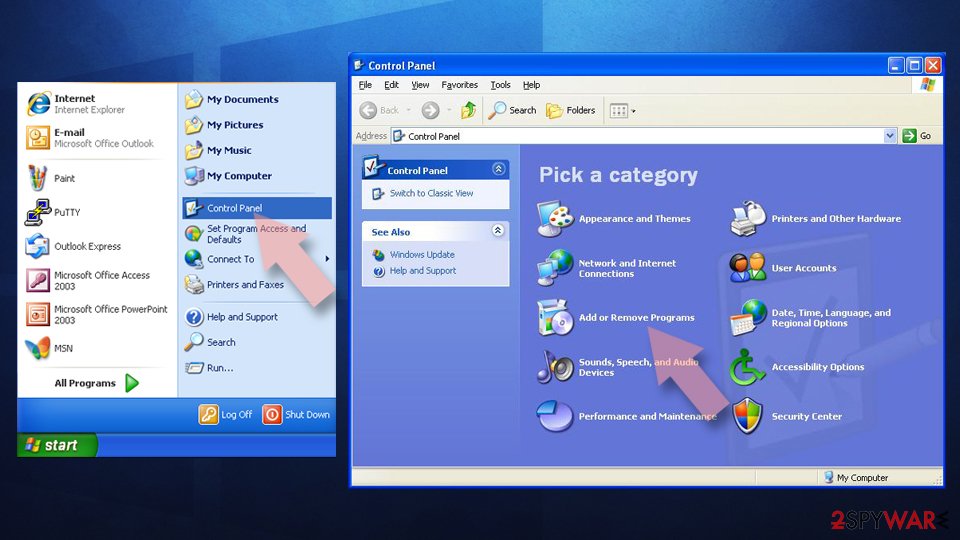
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
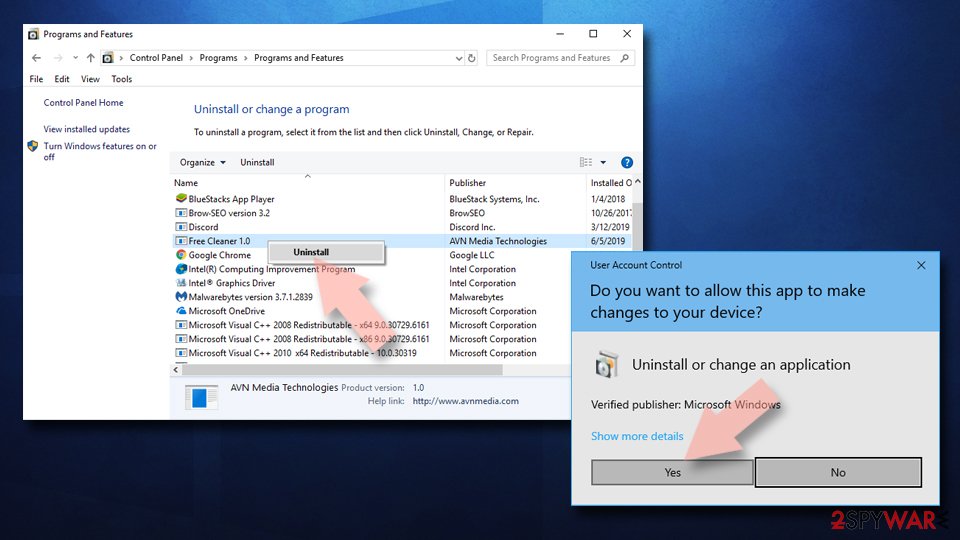
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
You may need additional checking for threats related to FileRepMalware virus on your Google Chrome browser:
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.

Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.

Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.

Remove from Microsoft Edge
Cleaning Microsoft Edge is possible if you complete all of the below-given instructing steps correctly:
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.

Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.

Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.

Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.

Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.

Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.

Remove from Mozilla Firefox (FF)
Discovered something suspicious in Mozilla Firefox? Do not worry, you can remove all unwanted objects from your web browser by performing these below-given steps:
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.

Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.

Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.

- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.

Delete from Safari
Findin unexpected extensions or plug-ins in your Safari web browser does not signal about anything good. The removal of adware-based objects can be successful by following this guide:
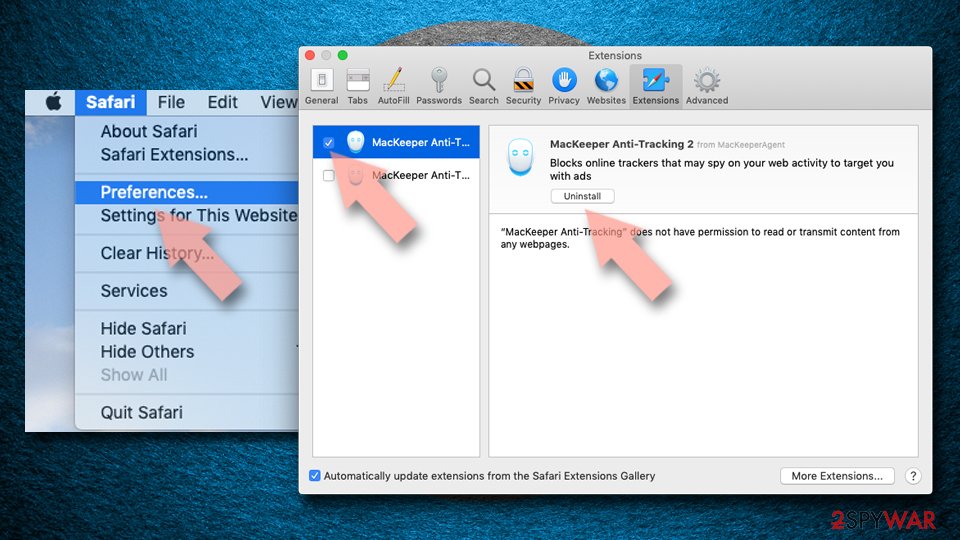
Remove dangerous extensions:
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
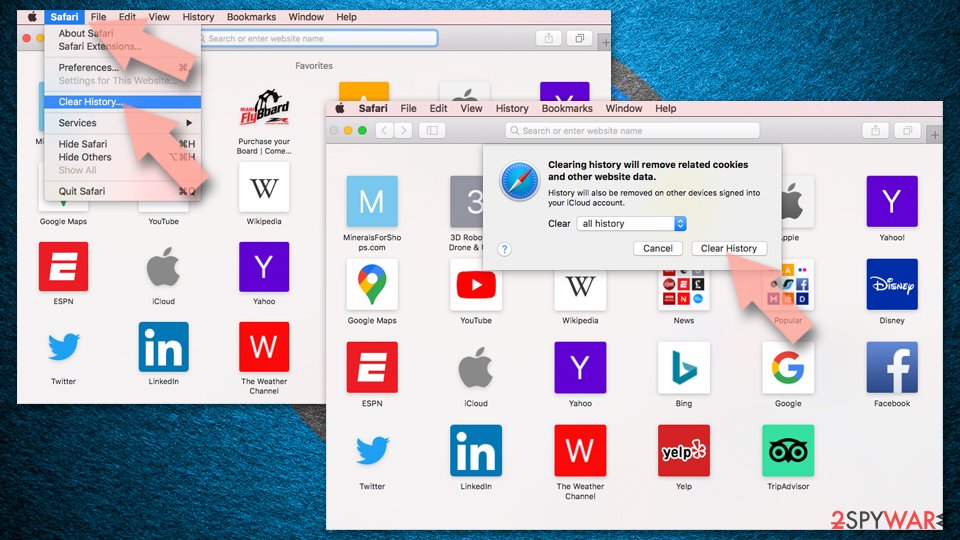
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
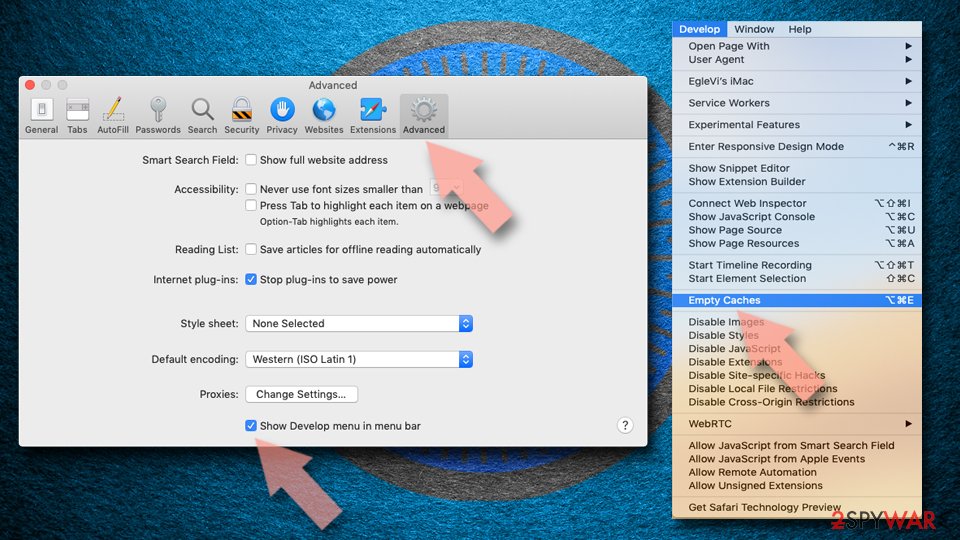
Reset Safari:
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Reset Internet Explorer
If you noticed an excessive amount of advertisements when browsing, remove PUPs and potentially malicious files and then reset your web browser.
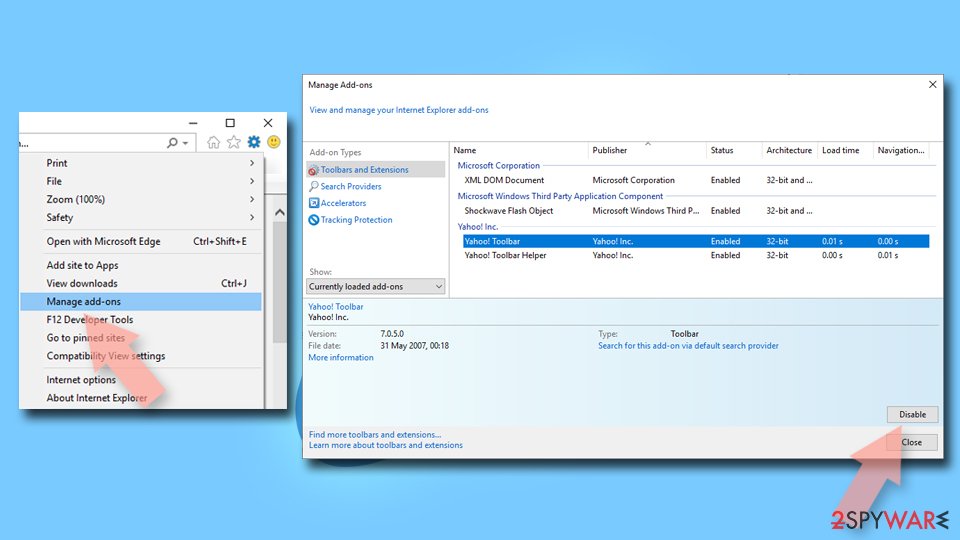
Remove dangerous add-ons:
- Open Internet Explorer, click on the Gear icon (IE menu) on the top-right corner of the browser
- Pick Manage Add-ons.
- You will see a Manage Add-ons window. Here, look for suspicious plugins. Click on these entries and select Disable.
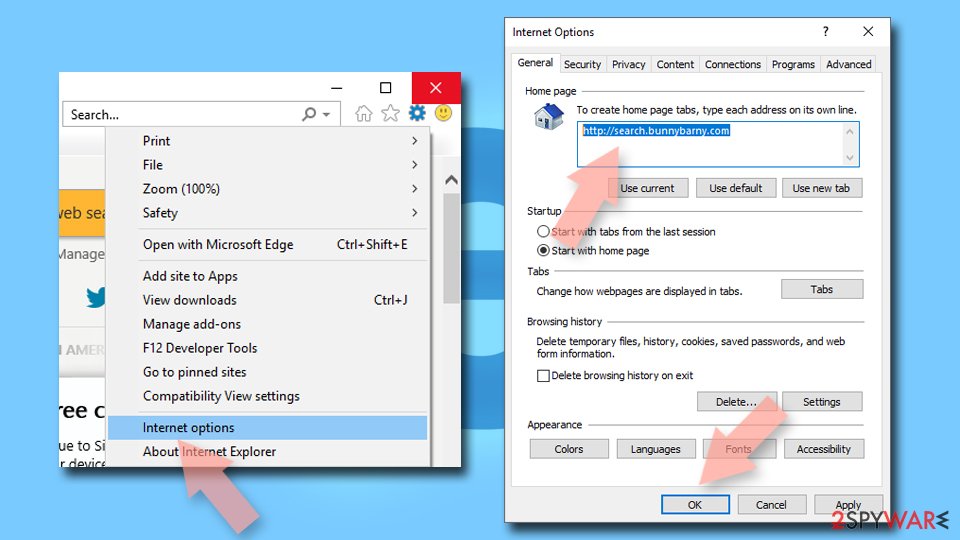
Change your homepage if it was altered:
- Open IE and click on the Gear icon.
- Select Internet Options.
- In the General tab, delete the Home page address and replace it by your preferred one (for example, Google.com).
- Click Apply and then select OK.
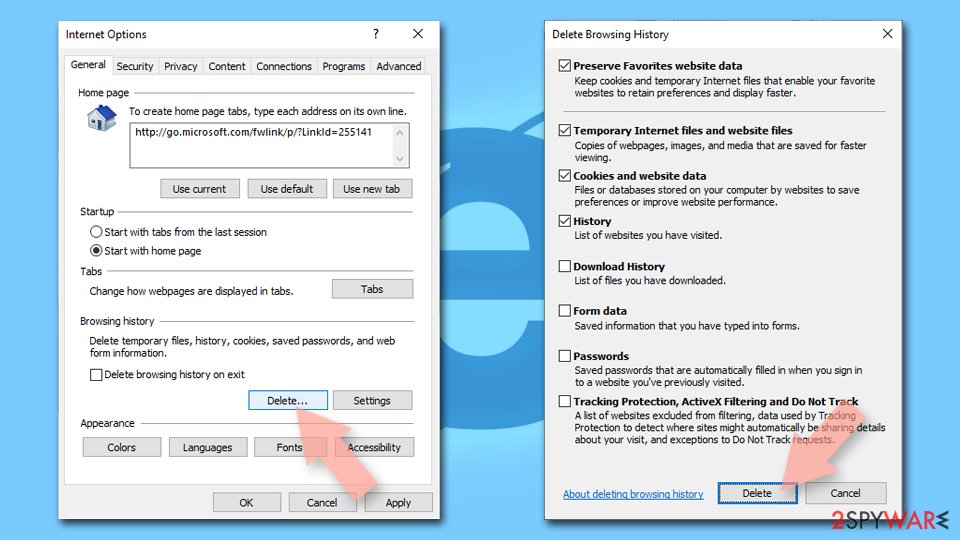
Delete temporary files:
- Press on the Gear icon and select Internet Options.
- Under Browsing history, click Delete...
- Select relevant fields and press Delete.
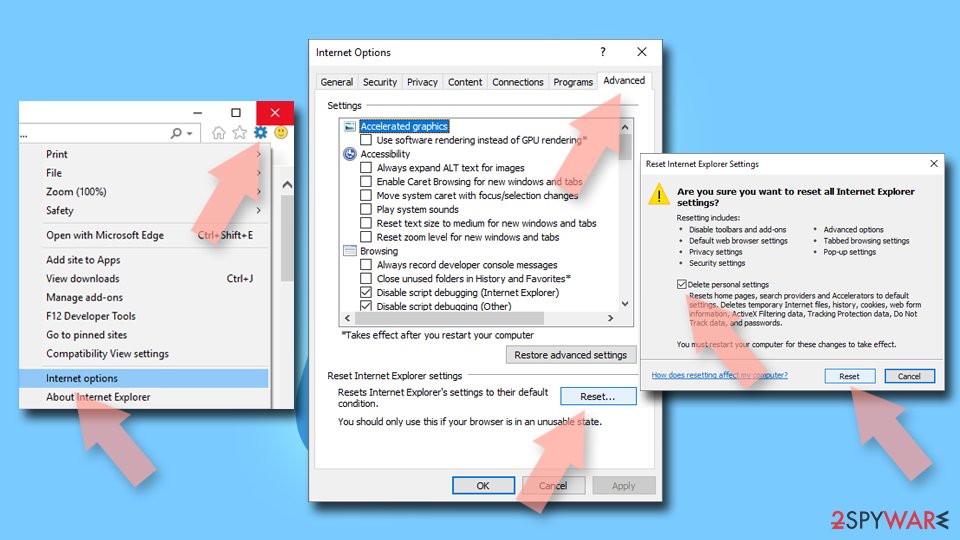
Reset Internet Explorer:
- Click on Gear icon > Internet options and select Advanced tab.
- Select Reset.
- In the new window, check Delete personal settings and select Reset.
From our report of Jan 2021 · not reviewed since
Eliminate FileRepMalware virus and fix possible damage
If your antivirus successfully immunized the file, you don't have to bother anymore.
If, however, you were informed about a threat by your antivirus or noticed the file on one of the Windows or Windows system folders, get rid of it asap. As long as the behavior of this file hasn't been clarified, we would highly recommend you to perform FileRepMalware removal asap.
It's challenging to remove FileRepMalware manually. This file may come into the system, meddle into Windows system folders and then multiply. Additionally, you should use a professional utility to recover your Registry to its primary state. Note that the virus tends to alter it according to its needs.
Also, you should also check for KMSPico and other potentially unwanted programs on the system that was installed on the system at the same time as FileRepMalware virus. Note that a big variety of software can hide suspicious content into web browser applications, so you should check Chrome, Firefox, Edge, Explorer, and other browsers too.
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed fileRepMalware in the list of installed apps, a sign of a program that could read browser data, the clean-up is only half of the work.
The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
Questions about FileRepMalware
What is FileRepMalware?
FileRepMalware is a detection name reported by antivirus programs for a cyber threat that can range from potentially unwanted programs to trojans. Also known as Win32:Evo-gen, this detection primarily comes from Avast and AVG antivirus engines.
Most commonly, antivirus software terminates the threat and reports it as already eliminated. FileRepMalware is associated with suspicious KMSPico installations—software allegedly activating Windows and Microsoft Office without developer permission.
However, the malware can also arrive as a standalone virus itself and proliferate throughout Windows system directories. The generic detection name indicates antivirus engines recognize suspicious traits but cannot identify the exact malware type. Ignoring such alerts carries significant risk.
How does FileRepMalware infect computers?
FileRepMalware typically spreads bundled within KMSPico or similar software activation tools downloaded from third-party sources. Users seeking free Windows activation download hacked KMSPico installations unknowingly containing the malware.
The threat also spreads through malicious free applications, potentially unwanted program bundles, and unsafe websites hosting cracked or repacked software. Browser downloads combined with third-party sources carry high infection risk.
The malware may enter via compromised websites exploiting browser vulnerabilities or through email attachments from spam campaigns. Trojan downloaders often deliver FileRepMalware as a secondary payload. Once installed, it can open backdoors for additional malware installation or hide in Windows system folders multiplying the infection.
What capabilities does FileRepMalware have?
FileRepMalware functions as a trojan horse with capabilities ranging from data theft to system manipulation. It can steal personal information including login credentials and financial data used for identity theft or fraud.
The malware tracks browsing activities using cookies or keylogging to gather sensitive information. It can hijack web browsers changing homepage, search provider, and tab settings. The infection causes system slowdowns, repetitive errors, and crashes due to malicious processes running silently.
FileRepMalware can download and install additional malware on the system opening further vulnerabilities. In severe cases, it deletes files or modifies firmware making removal extremely difficult. The combination of these capabilities makes it a significant security threat.
Should I ignore antivirus warnings about FileRepMalware?
No, do not ignore FileRepMalware alerts from your antivirus software. While antivirus engines sometimes generate false positives, warnings about potentially malicious files should never be dismissed. If antivirus successfully quarantined or eliminated the threat, no further action is necessary beyond continued monitoring.
If the file appears in Windows or system folders and antivirus reports detection, you should remove it immediately without delay. Although antivirus engines can occasionally be wrong, the warning indicates the file displays suspicious traits requiring investigation.
Disabling antivirus to permit installation of questionable files dramatically increases infection risk. Professional antivirus testing of files is always preferable to user guessing about file legitimacy.
How do I remove FileRepMalware?
Run reputable anti-malware software performing a full system scan to detect and eliminate FileRepMalware and associated threats. The malware often hides in Windows system folders and multiplies across the system, requiring comprehensive scanning.
Use system repair tools to restore Windows registry and system files altered by the infection. Check your system for KMSPico and other potentially unwanted programs installed alongside FileRepMalware, removing all detected threats. Scan all web browsers—Chrome, Firefox, Edge, Explorer—for malicious extensions and settings changes.
Clear browser cache and cookies completely. After removal, restart your computer and run another scan confirming complete elimination. Monitor your system closely for residual malware activity or re-infection.
Can FileRepMalware re-infect my system?
Yes, FileRepMalware can re-infect if the original distribution method remains active. If you downloaded infected KMSPico installation files, rerunning the installer reintroduces the malware. If adware remains on your system, it may download FileRepMalware again.
Browser compromises like malicious extensions can trigger re-infection through malicious sites. To prevent recurrence, completely remove all initially installed applications used to deliver the malware.
Eliminate any bundled adware or PUAs that arrived with FileRepMalware. Use browser extensions only from official sources and regularly audit installed extensions.
Avoid re-downloading from sources that previously contained malware. Keep antivirus updated and run regular scans. Download software exclusively from official developers.
Should I use Windows or a third-party activation tool?
Use Windows licensing legitimately rather than activation tools like KMSPico. Microsoft offers affordable ways to purchase Windows licenses on its official website. Educational institutions provide free copies to students.
If cost is prohibitive, alternative operating systems like Linux are free and legitimate. Using activation tools designed to bypass licensing is risky for multiple reasons.
Software cracks and hacked installers frequently contain malware delivering trojans and other threats. Users downloading from untrusted sources expose themselves to infection.
Legitimate Windows installations receive important security updates immediately, while hacked systems may miss critical patches. Professional antivirus testing detected KMSPico as potentially dangerous software. Legitimate Windows licensing avoids these risks entirely.
How can I protect my computer from FileRepMalware?
Download software only from official developer websites and verified retailers. Never use cracks, keygens, or KMSPico for software activation. Be extremely careful selecting installation options, choosing Custom or Advanced options to deselect optional programs.
Avoid downloading from torrent websites or unsafe sources. Keep antivirus software installed, updated, and actively scanning. Run regular full system scans even without obvious symptoms.
Never disable antivirus warnings to permit questionable installations. Keep Windows and all software updated with security patches. Use strong, unique passwords for important accounts.
Know the risks of untrusted software sources and share this knowledge with others. If unsure about file legitimacy, research it before installation rather than risking infection.
Will Fortect remove FileRepMalware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For FileRepMalware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Malwarebytes Labs: PUP. (read October 5, 2026)
- Avast security forum: Topic: FileRepMalware - Bloody (read October 5, 2026)
- LosVirus: Noticias Sobre Seguridad Y Virus (read October 5, 2026)
- Nvidia: What's the Difference Between a CPU and a GPU? (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)