
Win32:Evo-gen: what it is and how to remove it
Win32:Evo-gen is a heuristic detection name used by Avast when it finds suspicious behavior suggesting a trojan or potentially unwanted program. The detection frequently triggers false positives.
Facts checked October 12, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If Win32:Evo-gen keeps coming back after uninstalling, a scan can find what reinstalls it.
Do it yourself · free Remove Win32:Evo-gen yourself 5 steps, about 15 minutes, no software needed.
Start the steps
Win32:Evo-gen: summary
| Distribution | Pirated software, torrent sites, malicious files. Fake software and such installations can deliver malicious files and programs to the system |
|---|---|
| Name | Win32:Evo-gen |
| Type | Heuristic detection name/ trojan |
| Meaning | This detection indicates potentially malicious behavior of processes or programs, files. It can report the trojan infiltration or a potentially unwanted program |
| Possible symptoms | Commercial content, system slowdowns, other malware infiltrations, crashes, or freezes. Malware infections cause suspicious processes in the background and appearance of files or programs installed without your permission |
| Main danger | Malware can use your computer for fraud or malicious processes like cryptocurrency mining. Hackers may access information stored on the device, remotely manage the system, or inject the computer with serious malware like cryptovirus |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 7 more facts
| Diagnosis/ elimination | You should scan the machine with a professional anti-malware tool to know if you need to remove the threat or analyzed further instead to avoid system corruption issues |
|---|---|
| Detection names | No Microsoft detection name is known |
| Damage | Not recorded in the old report |
| Symptoms | An unknown program in Installed apps |
| Evidence | 5 write-ups by security sites; details still limited |
| First seen | 8 January 2020 |
| Facts checked | 5 October 2026 |
What Win32:Evo-gen does on an infected PC
What readers reported about Win32:Evo-gen
My laptop affected with VirTool: Win32/DefenderTamperingRestore. My laptop affected with VirTool: Win32/DefenderTamperingRestore. Help me
What is this C:UsersdadDesktopsqlite-dll-win32-x.zip folder?. C:UsersdadDesktopsqlite-dll-win32-x.zip Why is this folder sitting on my deaktop when I did nothing connected to it?
removal of Clock.Win32.ransomware virus. Is deleting it with anti-virus sufficient?
From the comments under our earlier guide; names and contact details removed.
From our report of Jan 2020 · not reviewed since
Win32:Evo-gen – is the threat indicator that can be triggered on Windows devices
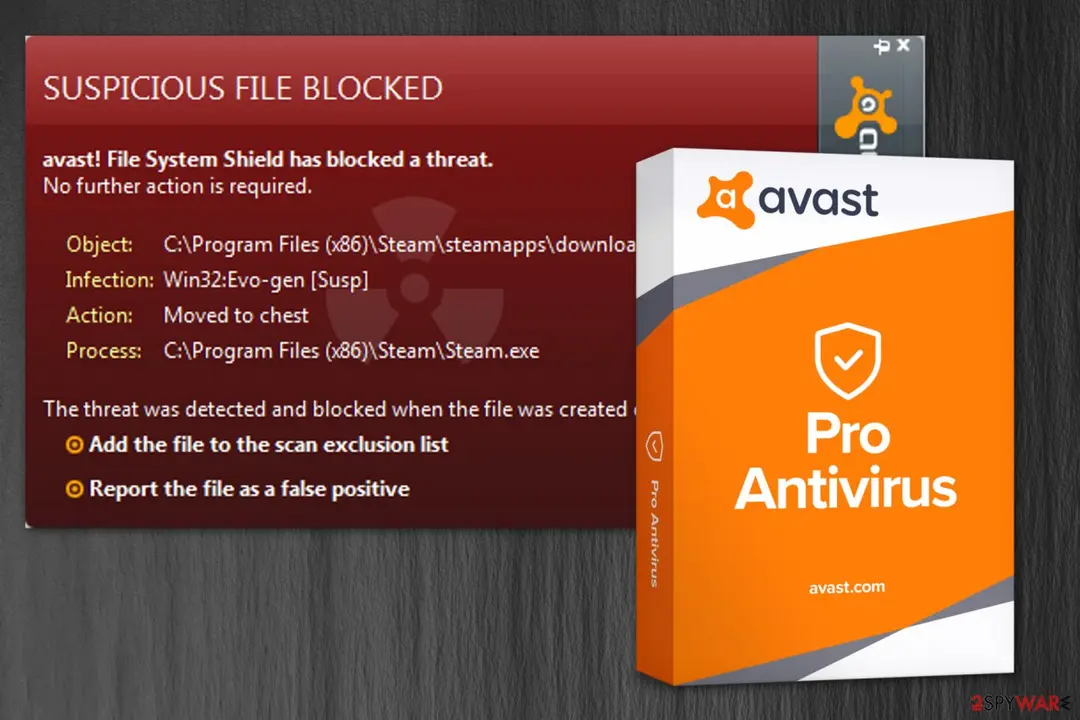
Win32:Evo-gen is a heuristic detection name used by anti-malware tools on Windows OS devices - it shows up when a trojan horse is found on the system, or a file/ application appears to have trojan-like features or such behavior.
The threat can be either a potentially unwanted program or a Trojan horse, so the term does not describe the virus accurately and can report any program or process that is running on the machine.
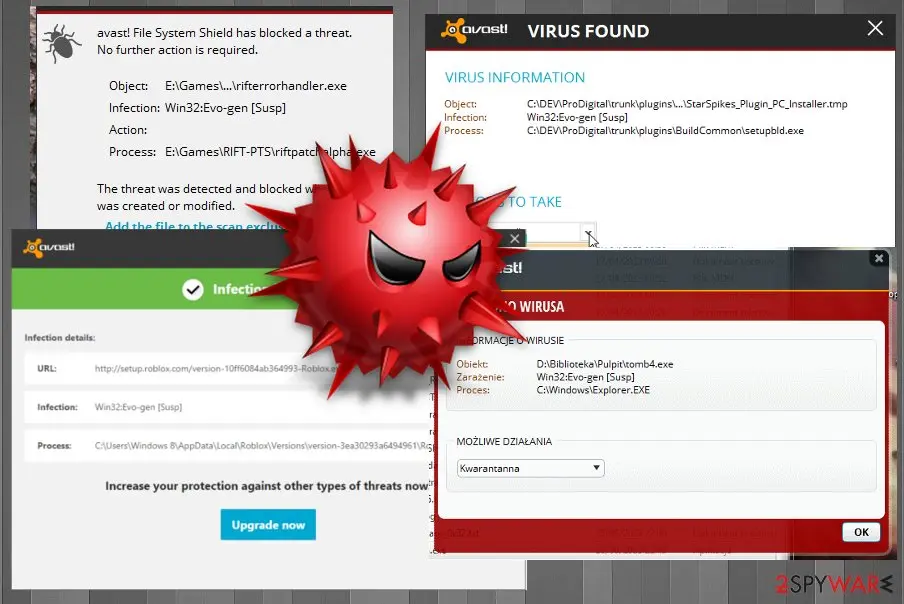
Besides, the heuristic code can also be used in false positives, so you should double-check the file before removing it from the system. This is the reason why symptoms, distribution methods in damage level can vary. Either way, you need a full system scan using anti-malware tools to diagnose the issue further.
Win32:Evo-gen might appear as an infection detection, but later on after the proper system scan it is not blocked because of the in-depth analysis that shows the real purpose of the file or a program in question. Always check it further with a reputable anti-malware tool if you have any suspicions about the file or program before you delete it completely.
Since this is the generic detection that can mean many scenarios and different malware infections, such malware can install itself by copying its executable to the system folder. Once those files get added malware becomes more persistent. Also, such infections alter registry keys, one that can be associated with the malicious activity that may appear on your device: HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Run. It is supposed to run the executable at each system reboot.
The initial Win32:Evo-gen payload can be designed to:
All these actions can appear on the screen alongside general slowness and system crashes, but you need to assess these symptoms and further scan the device before jumping to conclusions. The virus removal can be more damaging to your device if you try to delete associated files or even registry keys.
Anti-malware tools are the way to go because those tools can show the purposes of the file and perform termination if needed. If you know the program or file that is suspicious, try to upload it on VirusTotal or a similar malware scanning service. Try or as alternate tools.
Win32:Evo-gen is the detection alert that Steam users and online gamers encounter more often than other internet browsers. Such services, in general, get to be indicated as malicious or harmful while they are not.
It seems suspicious, but when you block the file installation or delete the suggested program, some functions may not work anymore. You need to either inspect the file or application more or simply restrain from using the given or service.
If the security alert actually identifies a Trojan Horse on your computer, it might initiate typical activities, such as dropping a keylogger to track the victim's online activity and log the keystrokes. This way, criminals can take over credentials like account logins, passwords, and other valuable information, leading the victim to money loss or even identity theft.
Moreover, Win32:Evo-gen might indicate an infection that can lead to the installation of other high-risk computer threats, such as ransomware or malware. Programs with Trojan-like viruses can exploit backdoors which help to find system vulnerabilities to infect your PC. Likewise, you might lose your date due to the infiltration of file-encrypting viruses as well.
Thus, we strongly recommend you to immediately check your system with different antivirus software and remove the infection. Note that regular computer users are not experienced enough to tell whether their systems are at risk.
Additionally, BedyNet.ru team recommends you using professional anti-malware software after Win32:Evo-gen removal as well. This way, you will be fully protected from all potentially dangerous computer hazards in the future, and any executables or different files related to the intruder can get deleted completely.
- download and spread other malware;
- use resources of your device;
- record keystrokes and steal that data;
- send information from your machine to a remote hacker;
- give remote access to a malicious actor;
- show commercial content to generate ad revenue.
From our report of Jan 2020 · not reviewed since
More from our earlier report on Win32:Evo-gen
- This broad classification is used by the Avast Behavior Monitor feature that finds exhibits of suspicious behavior and categorizes those detections as potentially malicious indications.
- Alternatively known as Win32:Evo-gen , Win32:Evo-gen is an infection code used by Avast antivirus software.
- Avast is the software that uses this detection name for a general indication of malcious behavior
- Recover any functions that get altered with the help of
- Besides, you can always opt for the help of a certified IT technician, security expert, or simply use Avast Antivirus or Avast Internet Security as Win32:Evo-gen removal tool.
How Win32:Evo-gen got on your PC
From our report of Jan 2020 · not reviewed since
Usually, a malware detection alert appears when the user downloads a suspicious file or software from shady websites.
Since the security software is not sure whether the application is actually malicious, you can simply avoid this infection alert by downloading software only from official pages. Many users reported that they encountered such alert after YouTube Downloader installation or during a video game cracking. These activities are involving pirated software sites, torrent services, promotional content.
Also, change Quick/Recommended parameters of the installer to Advanced/Custom if they were pre-selected. Always choose Custom installations because the previous setup is designed to skip many essential steps of the installation procedure, which increases the risk of infiltrating potentially unwanted programs (PUPs).
Afterward, attentively seek any checkmarks which have been ticked before and de-select them. Those marks allow installing additional software on your computer that might be malicious and put your computer's security at risk. Likewise, you should be careful when installing third-party software on your PC.
Keep your anti-malware tools updated because outdated programs or tools that use old virus databases can show false positive detections and indicate games or files that are harmless and safe as malicious or dangerous. Before terminating any file or program that seems suspicious, run a system scan to be sure about the purpose of the one in question.
How to remove Win32:Evo-gen
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to Win32:Evo-gen or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 2: Remove it from startup
Whatever Win32:Evo-gen installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Jan 2020 · not reviewed since
Learn how to get rid of Win32:Evo-gen from the system
To help you remove the intrusive virus from the system, we highly recommend employing professional malware removal software.
You can use , , or to uninstall this malware from your computer or double-check the warning and make sure that it is a false positive.
Also, we kindly ask you NOT to try performing Win32:Evo-gen removal by yourself. Typically, high-risk computer infections use deceptive tricks to hide their presence. One of them is disguising as a legitimate system process. If you terminate vital processes or uninstall important files of your PC, it might cause permanent damage.
If you can't launch any security software because malware is blocking you, you should try rebooting your computer to Safe Mode with Networking or using System Restore:
After removal: passwords, accounts and prevention
Secure your accounts after the clean-up
Assume that whatever was saved in the browsers on this PC while the PC showed win32:Evo-gen in the list of installed apps has been copied:
- passwords
- cookies
- autofill data
Work from a clean device, or from this PC once the offline scan finds nothing.
Start with your main e-mail account, because it can reset everything else, then banking and payment, then social and gaming accounts. Change each password, sign out of all sessions and turn on two-step verification: Turn on two-step verification / secure a hacked account.
The full order, including crypto wallets and card replacement, is in securing your accounts after malware.
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
Questions about Win32:Evo-gen
What does Win32:Evo-gen mean?
Win32:Evo-gen is a heuristic detection name used by Avast antivirus software when it discovers behavior patterns suggesting a trojan horse or malicious activity. Heuristic detection analyzes how programs behave rather than matching signatures in a virus database.
This broad classification can flag legitimate programs that exhibit suspicious behavior, making false positives common. The threat can be either a genuinely dangerous trojan or a perfectly safe program that simply behaves in a way the security software considers suspicious.
Is Win32:Evo-gen definitely a virus?
No. Win32:Evo-gen may or may not indicate a real threat. Since it is a heuristic detection, it frequently generates false positives where legitimate files are flagged as malicious. The detection does not describe the virus accurately and can report any program exhibiting suspicious behavior patterns.
Before removing the flagged file, investigate further using alternative anti-malware tools or upload it to VirusTotal to check how other security vendors treat it. Many users have encountered this alert on legitimate software.
How can I tell if this detection is accurate?
Double-check the detection using different anti-malware tools or upload the flagged file to VirusTotal to see how multiple security vendors classify it. If only Avast detects it as malicious while other AVs consider it clean, it is likely a false positive.
Legitimate programs, especially games and software downloads, frequently trigger this alert incorrectly. If many antivirus engines flag the file as malicious, the detection is more credible. Also consider whether you downloaded the file from a reputable source like an official website or established software store.
What should I do if my security software shows this detection?
Do not immediately delete the file. First, determine what program it belongs to. If it is an unrecognized file from an unknown source, deletion is safer.
However, if the file belongs to software you intentionally installed, further investigation is warranted. Perform a full system scan with your anti-malware tool to check for other threats.
Upload the specific file to VirusTotal to see how it is rated by multiple security vendors. If confident it is a false positive, add it to your security software's exclusion list.
Can Win32:Evo-gen be a trojan?
Yes. Win32:Evo-gen can indicate a real trojan infection, particularly if the detection occurs on recently downloaded suspicious files. Trojans detected under this name might install other malware, record keystrokes to steal credentials, send information to remote hackers, give remote access to malicious actors, or show commercial content for ad revenue.
If the detected file comes from a torrent site or suspicious source, it is more likely to be a genuine threat. Symptoms like system slowdown or unexpected processes suggest real infection.
What risks does an actual Win32:Evo-gen trojan pose?
If the detection is legitimate, the trojan could download and spread other malware onto your system. It might use your computer's resources for cryptocurrency mining or botnet activities. The trojan could steal personal information, banking credentials, and passwords for identity theft.
It might enable keyloggers that record everything you type, including credit card numbers and account logins. The trojan could provide remote access to cybercriminals, allowing them to control your PC. Data loss and monetary theft are serious risks from confirmed trojan infections.
How do I remove an actual Win32:Evo-gen trojan?
Use professional anti-malware software like Avast, AVG, or Malwarebytes to scan and remove the infection. Update the software's virus database before scanning to ensure it detects current threats. Run a full system scan in Safe Mode with Networking to prevent the trojan from interfering with the removal process.
Do not attempt manual removal unless you are highly experienced, as deleting wrong files can cause system damage. After removal, change all passwords for important accounts, monitor online banking, and use system recovery tools to repair any damage.
Why do legitimate programs trigger Win32:Evo-gen detection?
Legitimate programs trigger heuristic detection when they exhibit behaviors the security software associates with malware, such as modifying system files, injecting code, or attempting unusual network connections. Game cracks, keygens, and software modification tools frequently trigger these alerts.
YouTube downloaders and similar utility programs commonly cause detections. Legitimate software from less-known developers also triggers more false positives than software from major companies. The detection is overly sensitive by design to catch threats early, resulting in frequent false alarms.
Will Fortect remove Win32:Evo-gen?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Win32:Evo-gen, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Reddit: What is Win32:Evo-Gen[Susp] from steam? (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)
- Microsoft Learn: How Microsoft names malware (read October 5, 2026)
- Gridinsoft: Avast Detection Names Explained: Win32, Trj, PUP, and gen (read October 12, 2026)