
Graizoah.com ads: what it is and how to remove it
Graizoah.com is the PUP related to advertisers and services that focus on commercial content publishing because sponsored material ensures that unwanted surveys, adult sites, online web games, and various software providers get views. Adware-type programs are designed to show shady pop-ups and other questionable material that triggers redirects to various pages and windows with advertisements.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If redirects to graizoah.com keep coming back, a free scan can check extensions, programs and browser settings in one pass.
Do it yourself · free Remove Graizoah.com ads yourself 3 steps, about 9 minutes, no software needed.
Start the steps
Graizoah.com ads: summary
| Distribution | This PUP can get installed without your permission because freeware installations and deceptive sites that show promotional material instead of valuable content. If you click on anything possibly malicious or harmful, you can easily get unwanted programs installed on the system without notice. Choosing the right source for your programs can help since Advanced or Custom options provide the opportunity to de-select unwanted applications |
|---|---|
| Damage | These PUPs can affect the performance and speed of the internet, an infected device with the behavior, but additional relation with advertisers and third-party companies exposes users' data to malicious people and can trigger privacy or identity issues[2] |
| Name | Graizoah.com |
| Type | Adware/ redirect virus |
| Detection names | No Microsoft detection name is known |
| Symptoms | Redirects to an unknown domain |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Evidence | 4 write-ups by security sites; details still limited |
|---|---|
| Domains | graizoah.com |
| Ads shown as | Redirects through ad pages |
| Browsers | Chrome, Edge and Firefox |
| First seen | 19 June 2020 |
| Facts checked | 6 October 2026 |
Is Graizoah.com ads dangerous?
From our report of Jun 2020 · not reviewed since
Graizoah.com is the browser-based threat that creates redirects and possibly indicates the adware infection
Graizoah.com is the PUP related to advertisers and services that focus on commercial content publishing because sponsored material ensures that unwanted surveys, adult sites, online web games, and various software providers get views. Adware-type programs are designed to show shady pop-ups and other questionable material that triggers redirects to various pages and windows with advertisements.
Pay-per-click revenue is the main source of the payment that PUPs receive and the way that developers can spread their threats further. These advertising services can gather revenue from views, visits, clicks on ads, and redirects, but also may record information about your habits while browsing online or search queries, settings of the web browser.
Unfortunately, these symptoms that Graizoah.com virus shows on the screen that include pop-ups and redirects are only the part of the full behavior and activities that potentially unwanted program can trigger on the infected machine.
When this site causes those unwanted redirects and the browser starts acting differently than before, you need to react and clean threats off of the system. PUP resides in the background and without automatic anti-malware tools, you cannot fully delete it since you should find all the related files and programs to do so.
Graizoah.com - the program that is causing pop-ups and redirects to ensure the traffic on needed sites. There is nothing valuable or useful about this site, so you should exit the page as soon as you notice anything unwanted or get redirected to many similar domains.
The more often this behavior keeps you from accessing what you wanted, the more intrusive this PUP can get and the more exposed you are to possibly malicious material.
Graizoah.com enters the system without permission and starts running in the machine, so the infected device gets significantly slower due to all the pop-ups, redirects to shady sites, and promotional software pages. This is the harmless program itself, but domains that appear on the screen due to a PUP can be malicious or associated with hackers, cybercriminals.
You should ignore any messages that Graizoah.com displays on the screen, especially pop-ups that suggest allowing notifications or agree to additional content, installs of the software or browser-based applications, threats that can gather information about your habits and activities on the internet.
Graizoah.com redirects lead to various different types of websites, so you may end up on a hacked site or the domain that affects more than your internet speed and triggers third-party ad tracking functions. Most of the techniques used can include cookies, tags, geo-locators, pixels. Also, these sites can be scams and trie to trick people into allowing additional content, setting changes, and result in serious virus infections.
Graizoah.com removal is extremely important for this reason because experts always not that PUPs re not harmful themselves, but he material that is delivered can trigger unwanted changes and slow down your computer, perform unwanted activities. If your personal or sensitive data gets recorded or even misused by malicious actors, you will end up with a more permanently damaged machine.
You need to remove Graizoah.com as soon as you notice any redirects or pop-ups that come out of nowhere. The sooner you react to the pop-up and appearance of the browser-based threat, the sooner your device gets cleaned and safe again.
This is the PUP that gives no value for your machine. You most likely are not the one responsible for this download and installation, so take care of the PC and fully terminate all threats yourself.
Graizoah.com also triggers alterations in the system folders and settings that affect reboots, changes in startup preferences. These affected files can slow down the machine internet speed and disable some programs or functions of the operating system.
From our report of Jun 2020 · not reviewed since
Installers related to third-party advertising services include additional downloads
The most known method that potentially unwanted programs use is software bundling because this technique is basically working on the pre-packing method.
Unwanted applications get added as extra parts of the installation setup, so the user allows those installs without noticing.
Skipping through steps, choosing Quick or Recommended options instead of the Advanced or Custom installations, relying on shady sites leads to PUP infections. PUPs get involuntarily added on the computer, so you cannot know when the infection happened.
Go for official developers, sites that provide real, trustworthy software, and download programs for you instead of promotional ads and peer-to-peer platforms. This is how you control what happens on the machine.
From our report of Jun 2020 · not reviewed since
More from our earlier report on Graizoah.com
- Graizoah.com removal process is quick and easy when you eliminate PUPs using anti-malware tools, proper programs designed to keep the machine safe and secure
- The system gets significantly slower when all the programs in the background trigger issues with the content delivery and display of the malicious material.
Check your browser and PC
- Address:
graizoah.com
How to remove Graizoah.com ads
How to stop the Graizoah.com redirects
Work in this order and test a few links after each step, so you know which one was the cause.
Step 1: Check the browser's extensions
Redirects to
graizoah.comon sites that normally behave mean something in the browser is sending you there. In Chrome openchrome://extensions, in Edge edge://extensions, in Firefox the menu > Extensions and themes.Remove every extension you do not remember adding, especially new tab, search, coupon, PDF or video downloader add-ons. The extension pages look the same on Windows 11 and Windows 10.
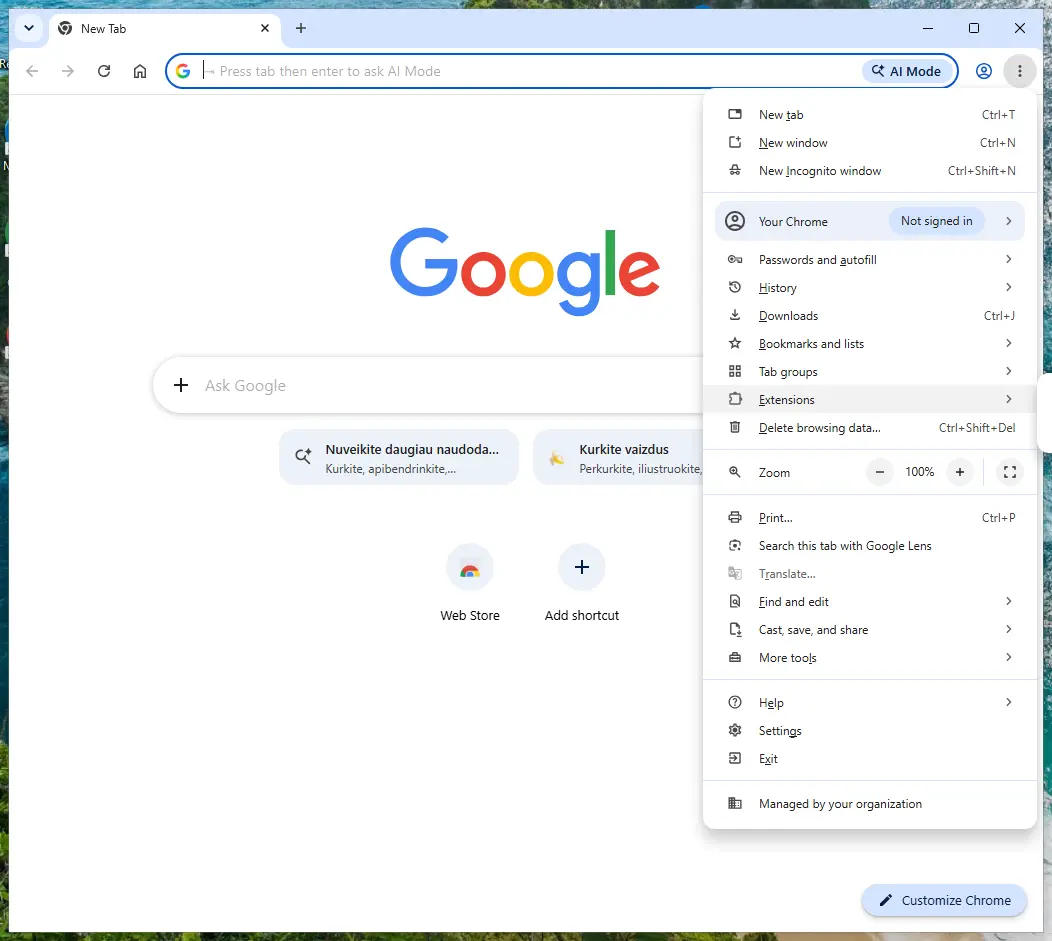
Chrome on Windows 11: More > Extensions > Manage extensions. Full procedure with screenshots: Remove a browser extension
Step 2: Reset the browser if the redirects continue
If
graizoah.comstill opens after the extensions are gone, put the browser's settings back to their defaults. In Chrome open Settings > Reset settings > Restore settings to their original defaults; in Edge Settings > Reset settings; in Firefox Help > More troubleshooting information > Refresh Firefox.Tip: Bookmarks and saved passwords stay, while site permissions, the start page and the search engine are reset.
Redirects that survive a reset in every browser point to a program installed in Windows 11 or Windows 10, so uninstall anything you do not recognise in Settings > Apps > Installed apps.
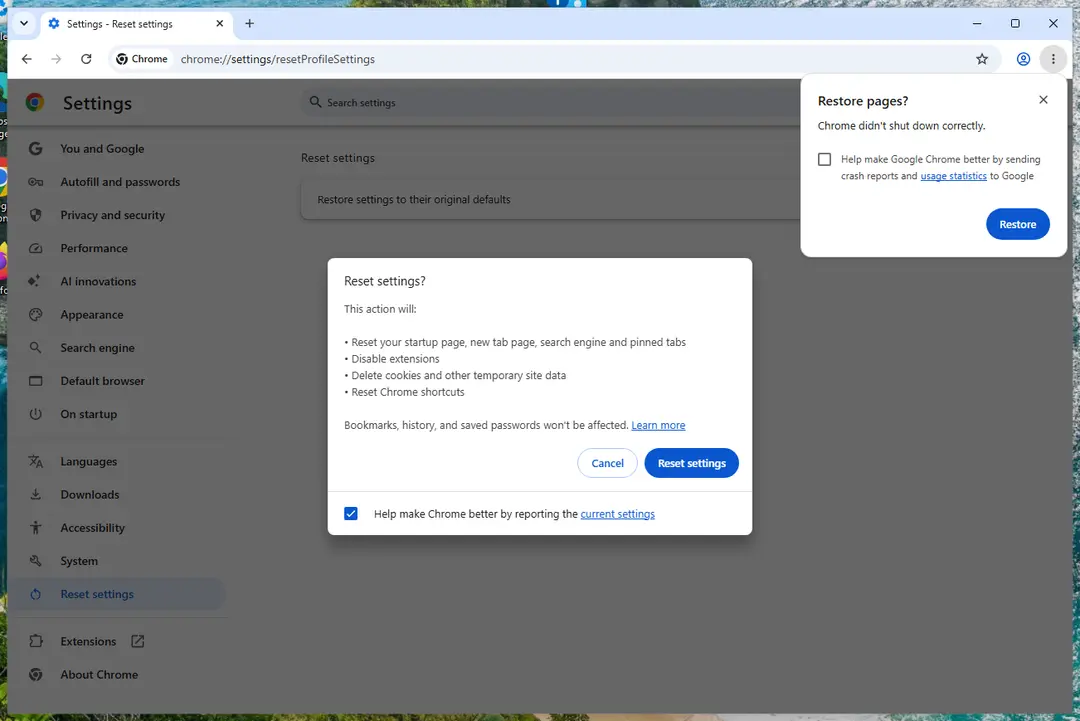
Chrome on Windows 11: Settings > Reset settings. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 3: Scan the PC if you downloaded anything from the ads
If you only saw the notifications and clicked nothing, you can stop before this step. If a notification led you to download or run something, delete that file, then scan Windows.
In Windows Security > Virus & threat protection > Scan options, run a Full scan, then choose Microsoft Defender Antivirus (offline scan) and Scan now. The offline scan restarts the PC and takes about 15 minutes on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
The system needs to get cleaned properly, so you should remove Graizoah.com by following the guide
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
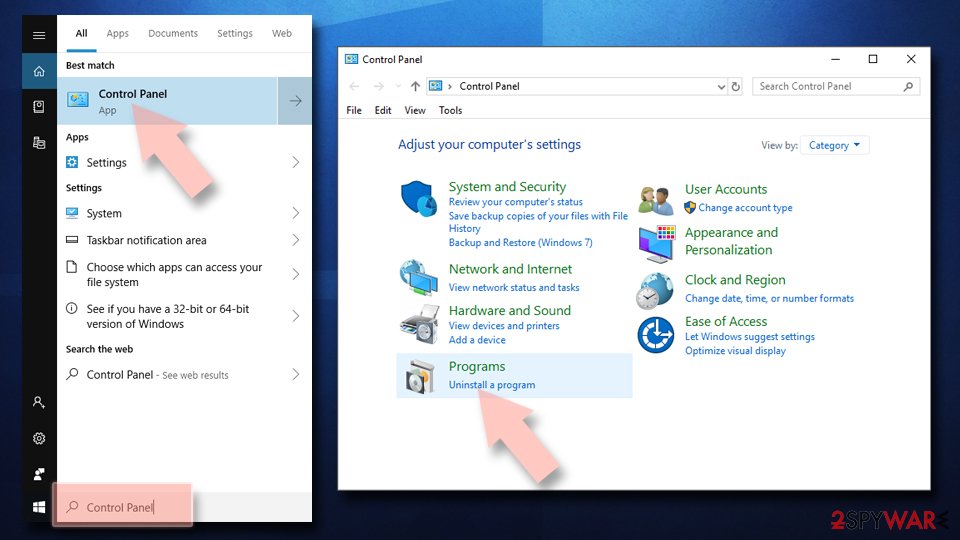
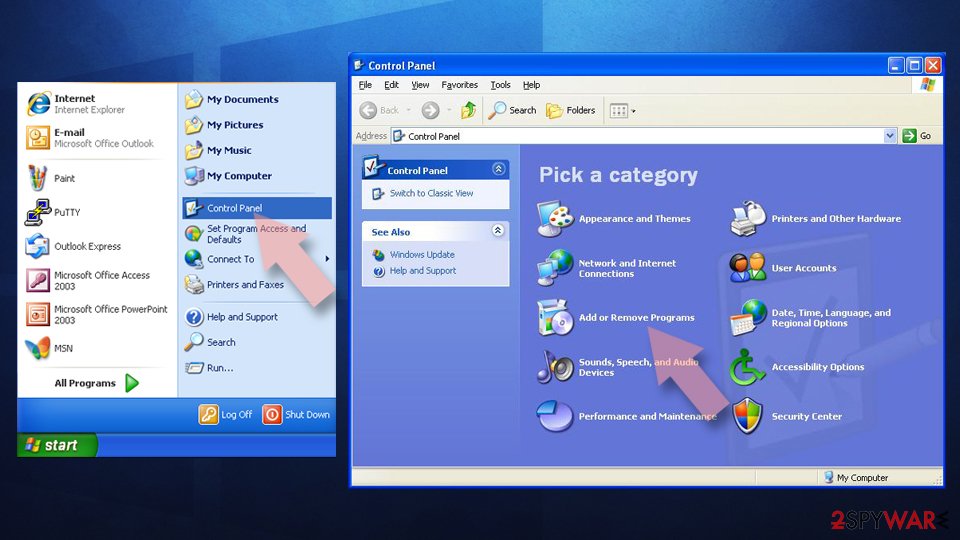
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
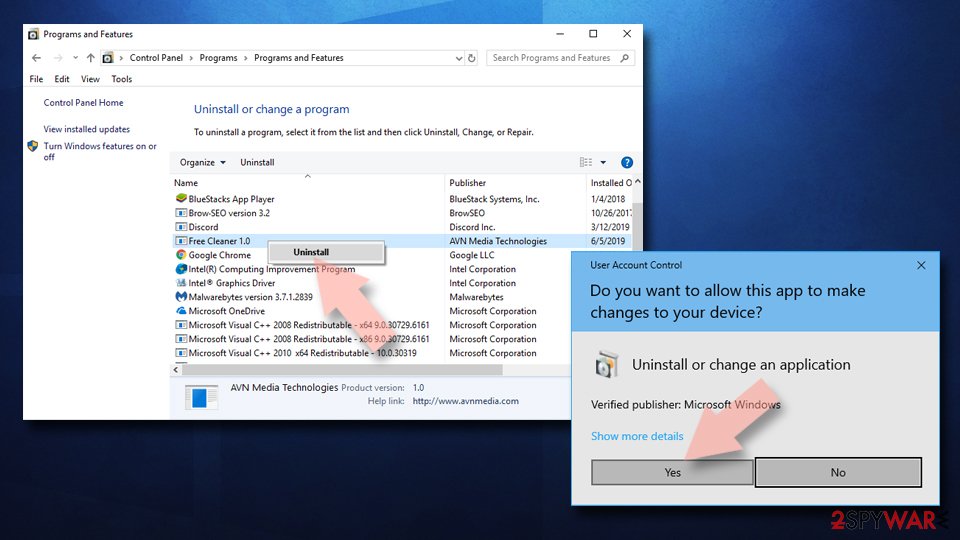
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
Remove Graizoah.com virus from your machine and clear the browser manually
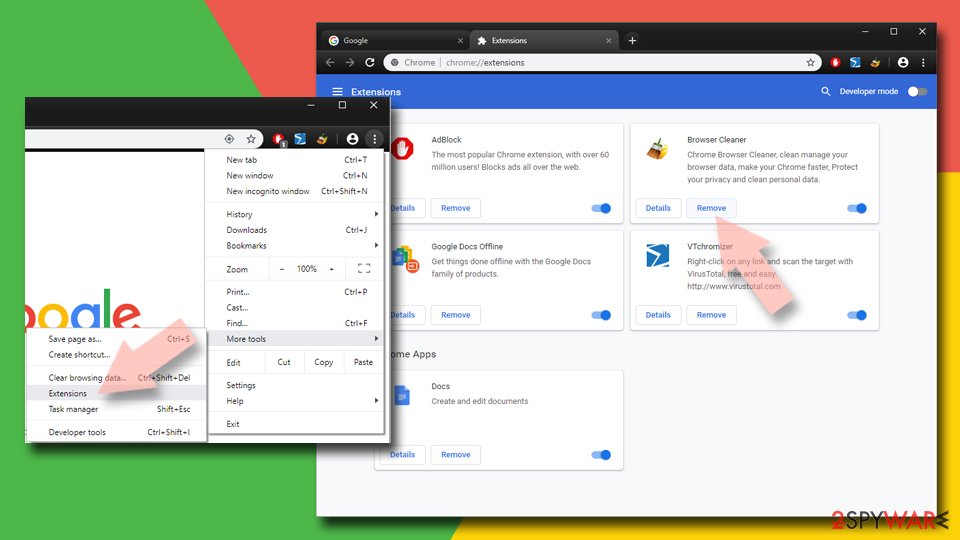
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
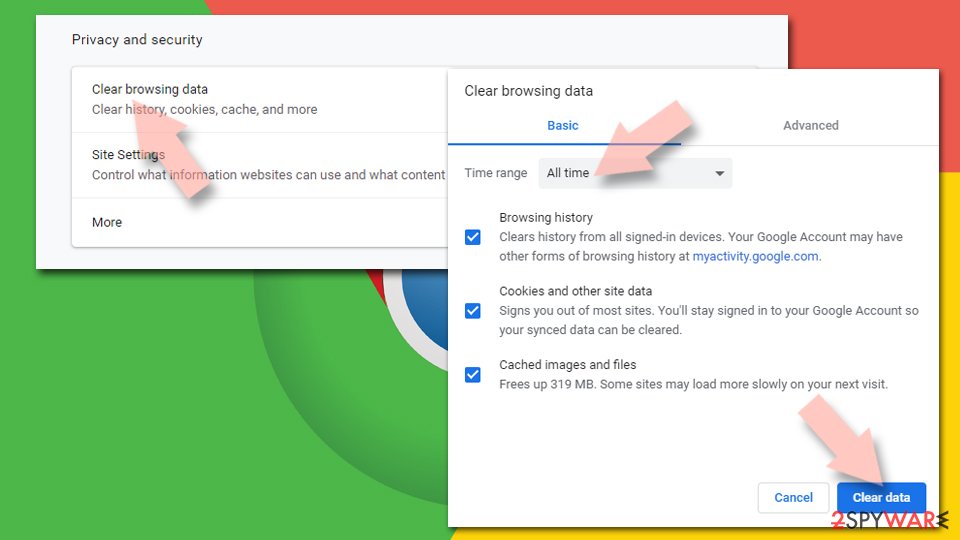
Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
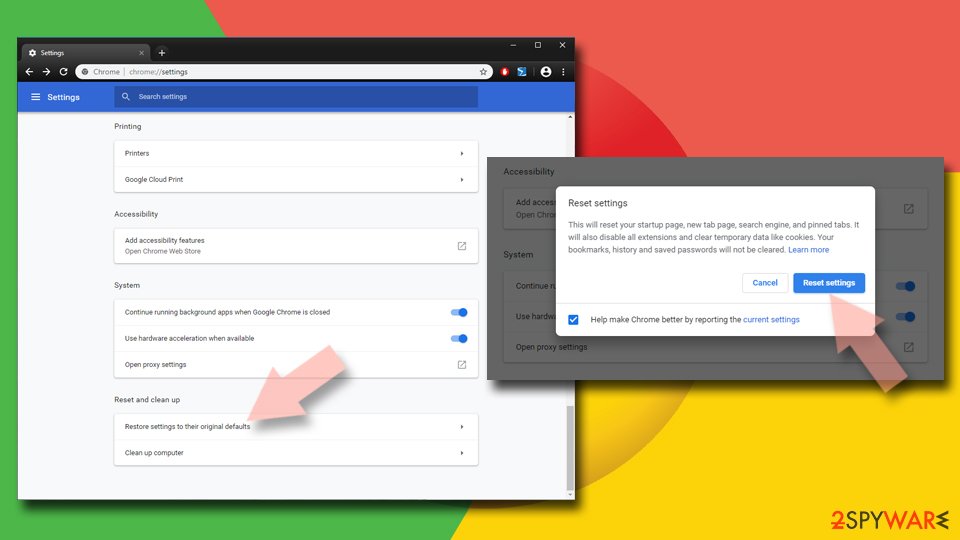
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Microsoft Edge
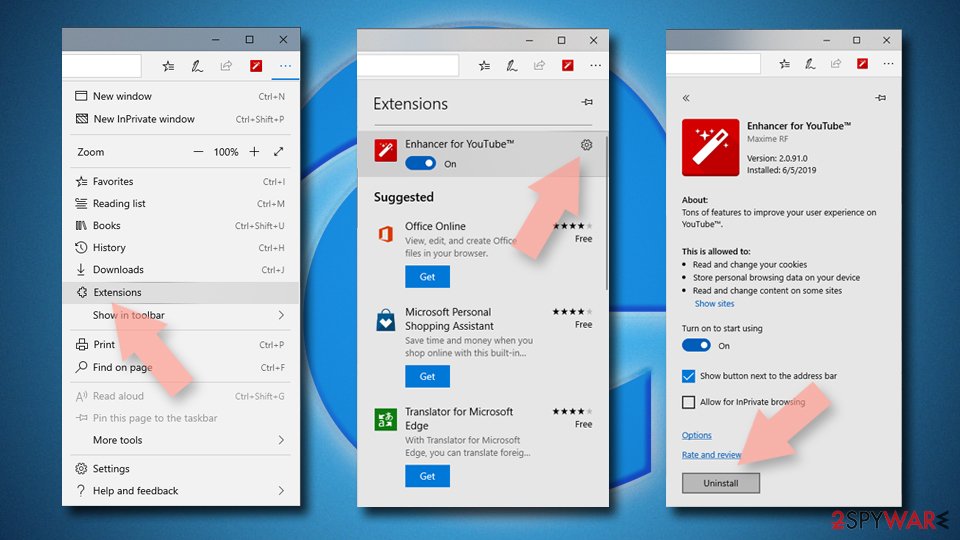
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.
Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.
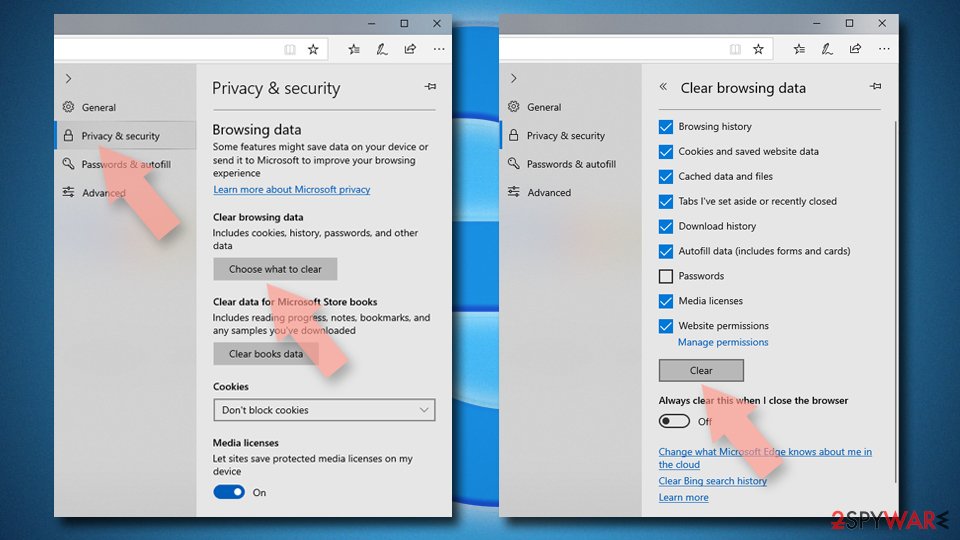
Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
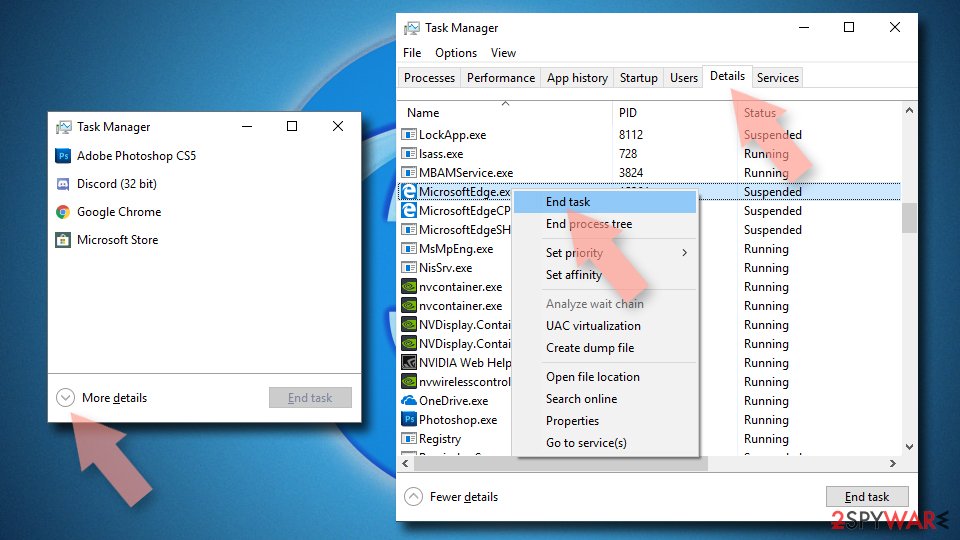
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.
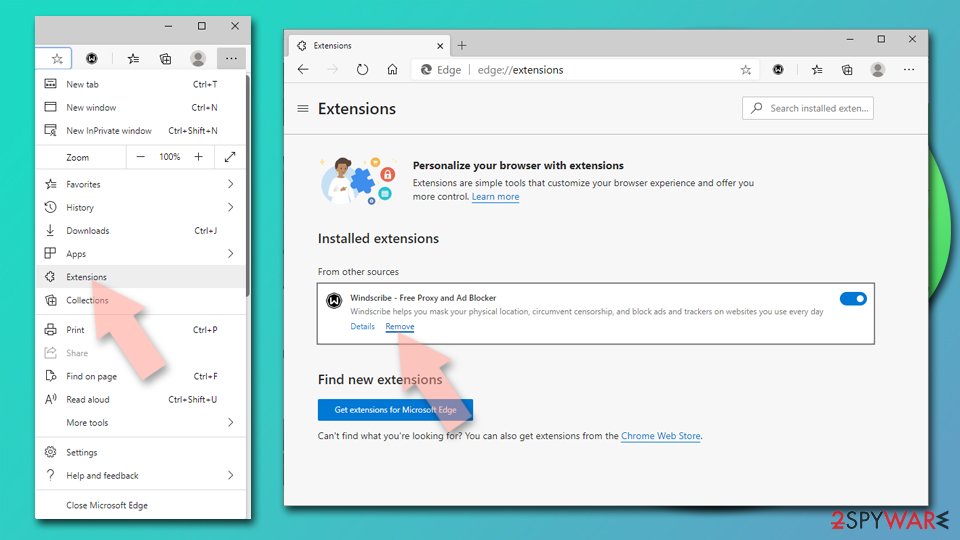
Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
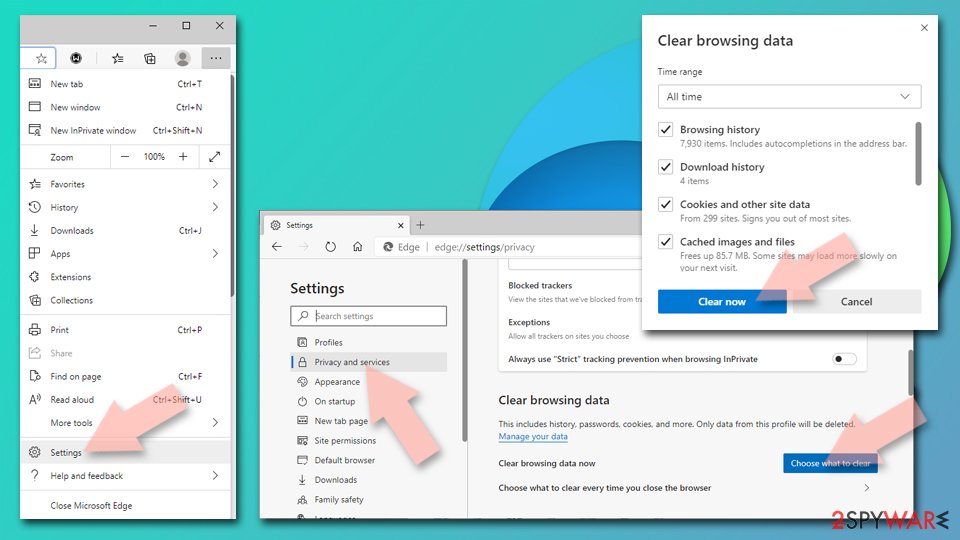
Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
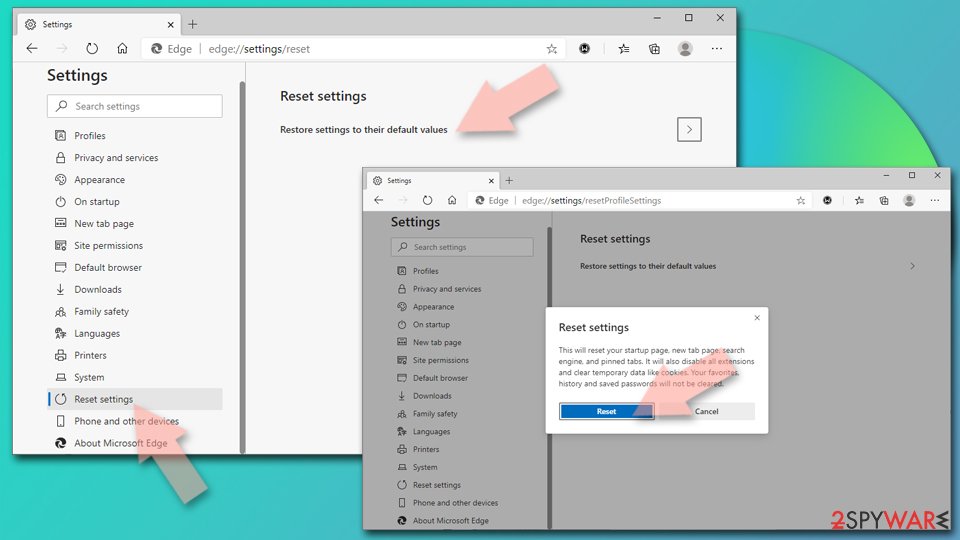
Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.
Remove from Mozilla Firefox (FF)
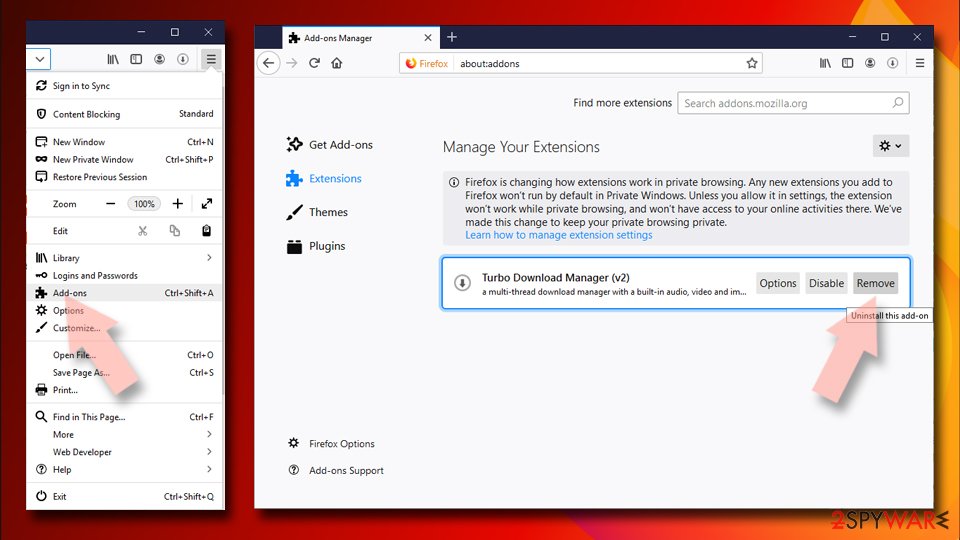
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
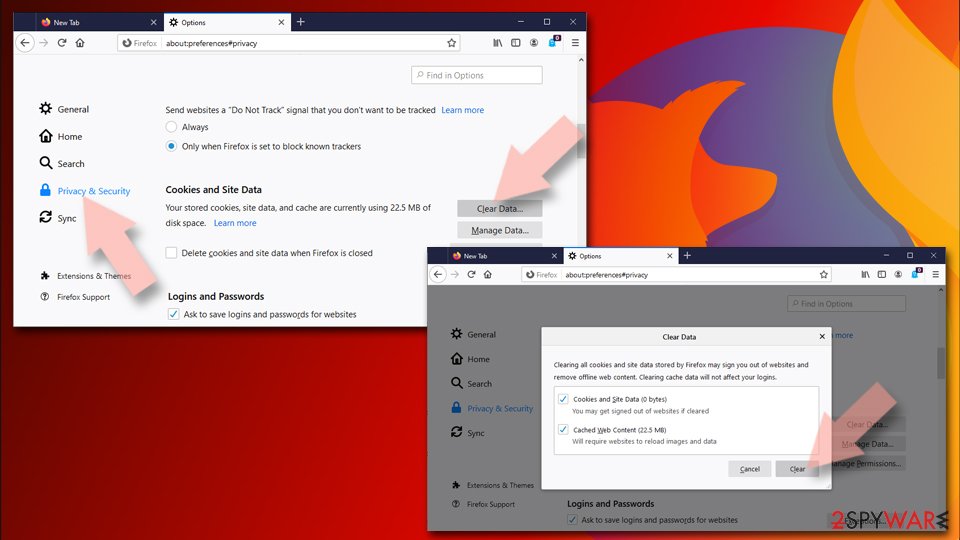
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
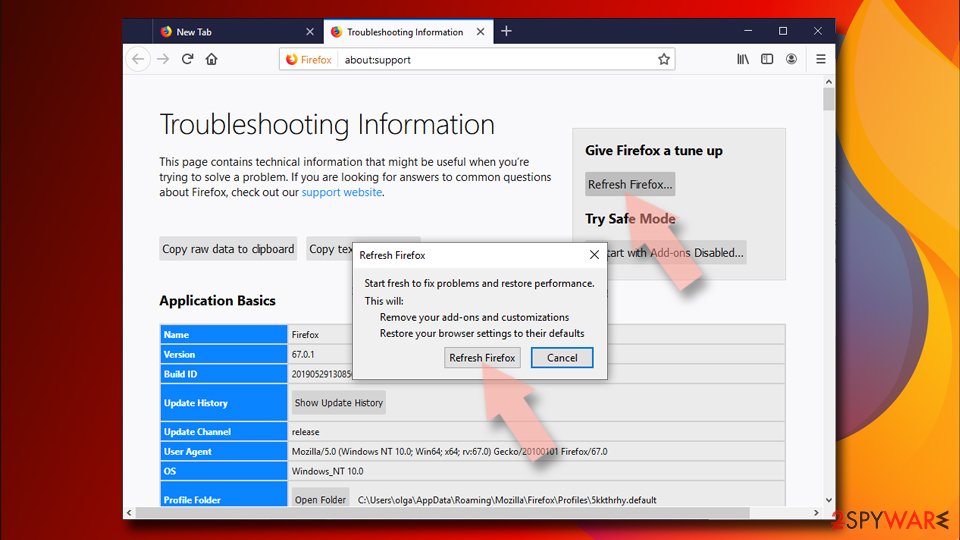
- Go to Help and then choose Troubleshooting Information.
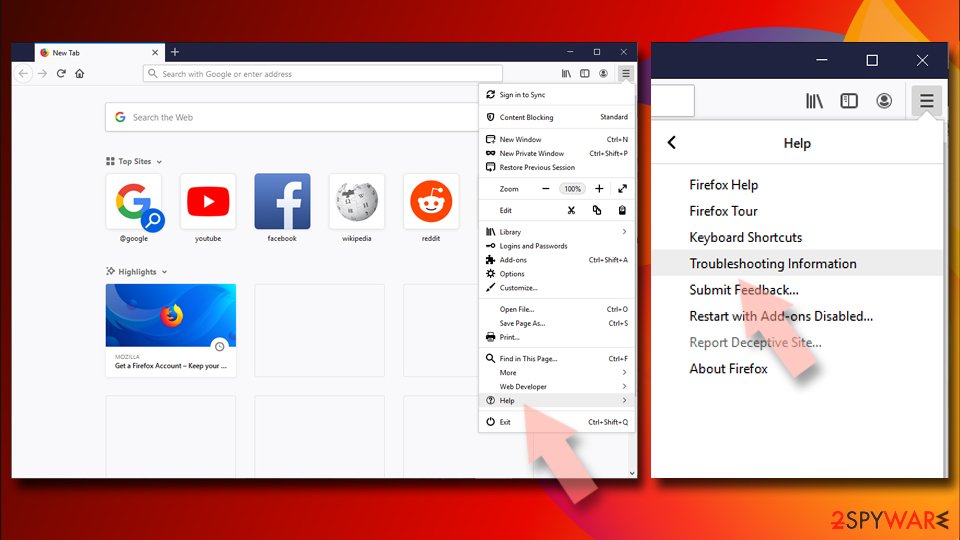
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
Make the browser running smooth again by eliminating any Graizoah.com related applications or browser extensions
Remove dangerous extensions:
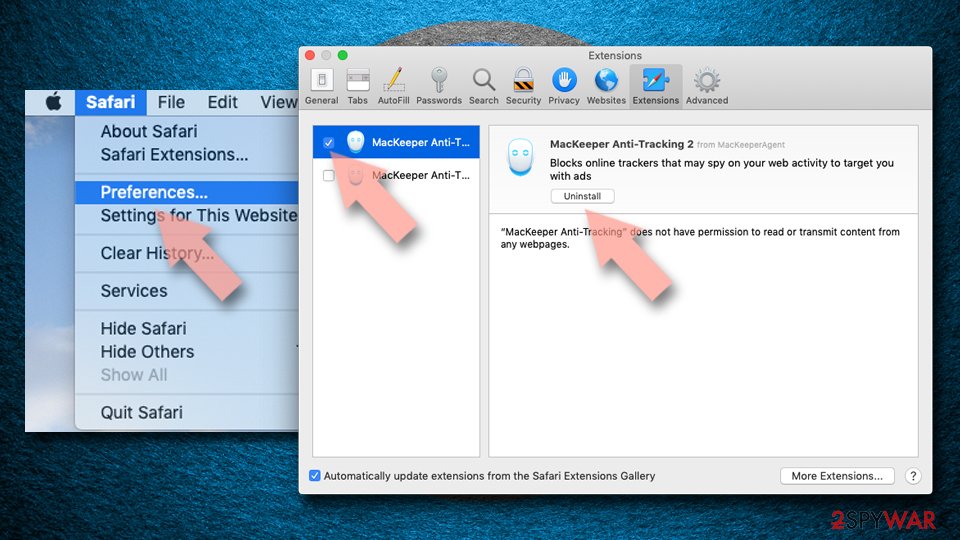
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
Clear history and website data:
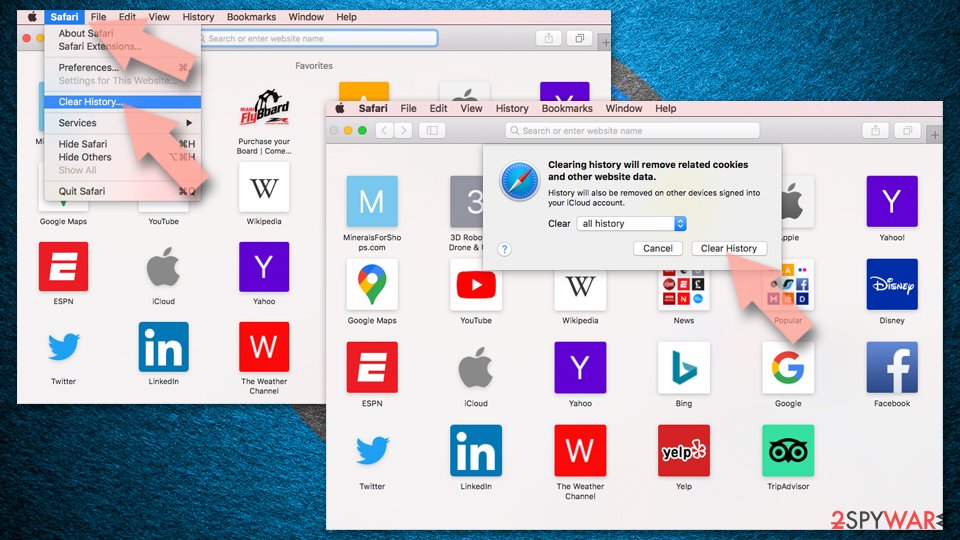
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
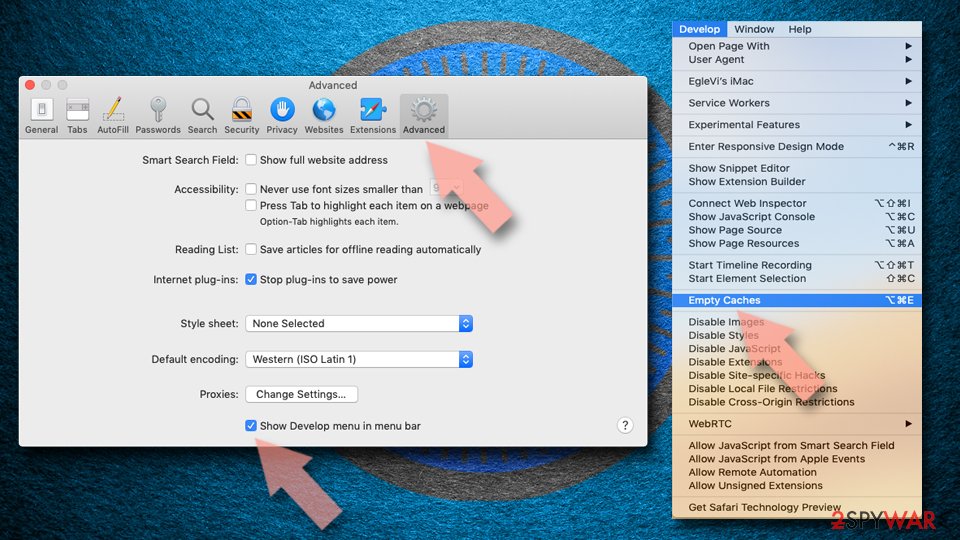
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
Remove Graizoah.com from macOS yourself
Remove the unwanted application:
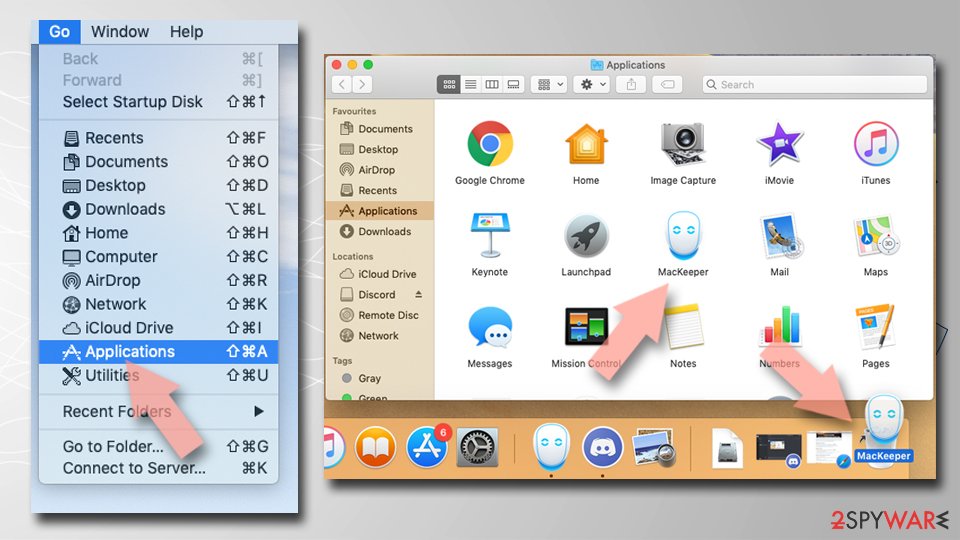
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
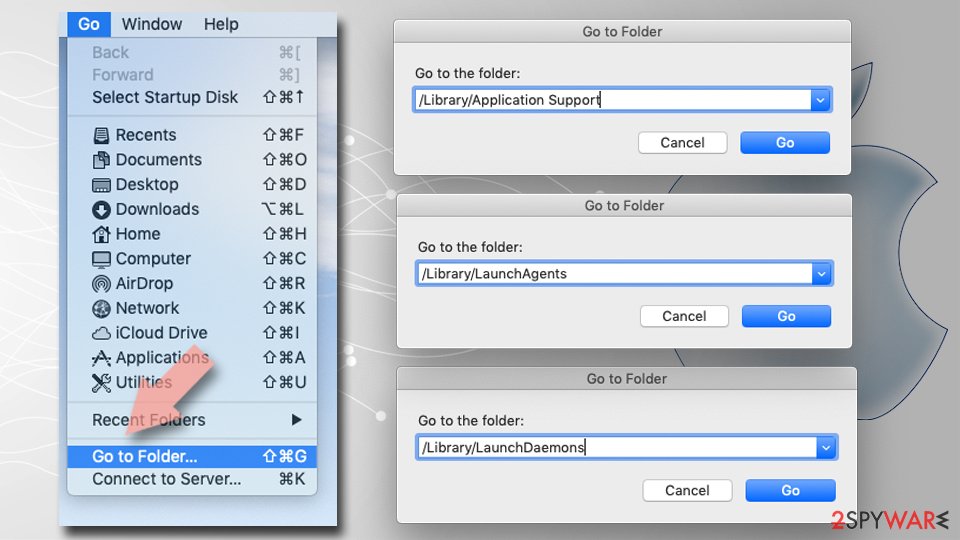
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Reset Internet Explorer
Remove dangerous add-ons:
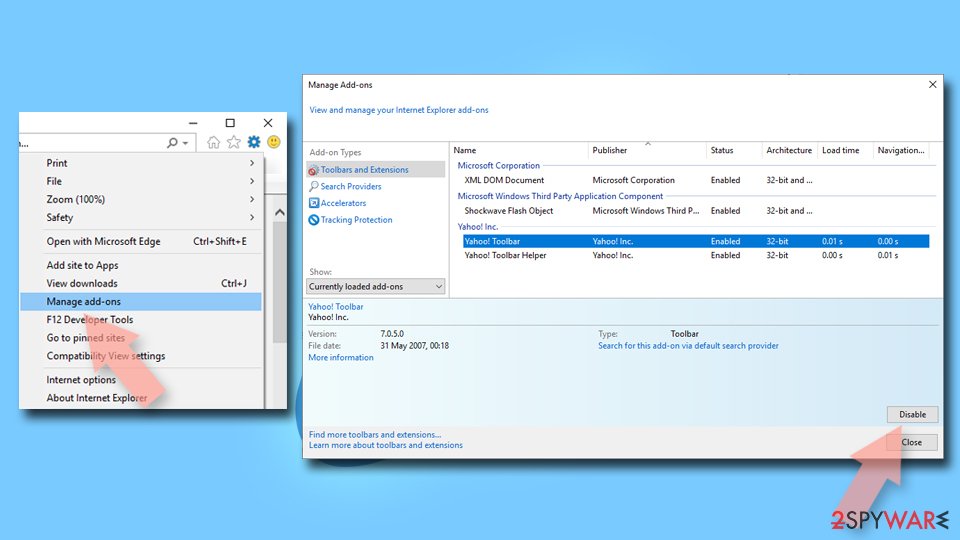
- Open Internet Explorer, click on the Gear icon (IE menu) on the top-right corner of the browser
- Pick Manage Add-ons.
- You will see a Manage Add-ons window. Here, look for suspicious plugins. Click on these entries and select Disable.
Change your homepage if it was altered:
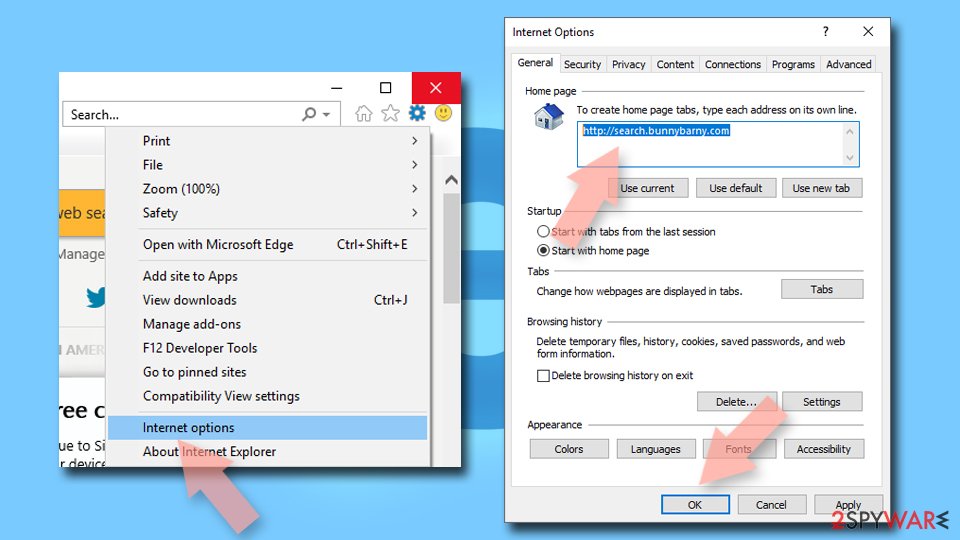
- Open IE and click on the Gear icon.
- Select Internet Options.
- In the General tab, delete the Home page address and replace it by your preferred one (for example, Google.com).
- Click Apply and then select OK.
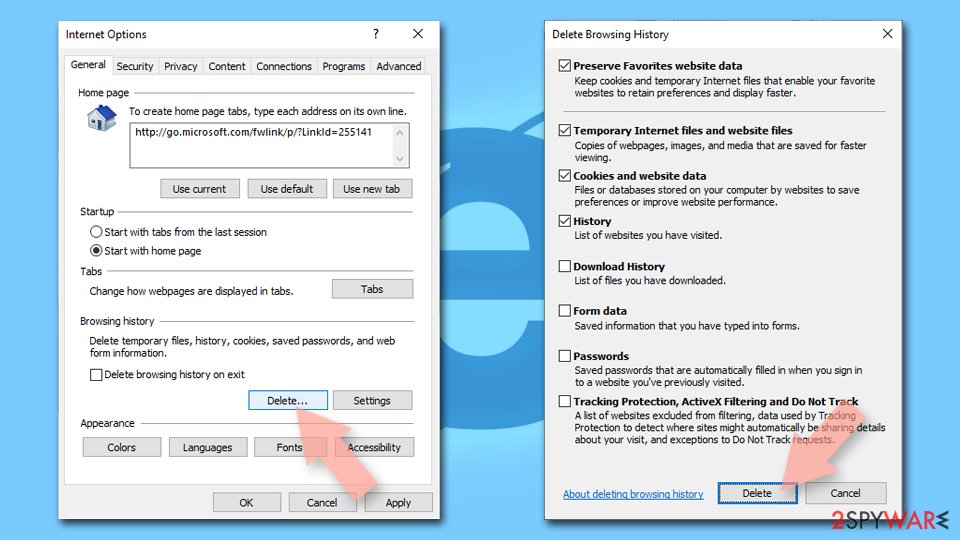
Delete temporary files:
- Press on the Gear icon and select Internet Options.
- Under Browsing history, click Delete...
- Select relevant fields and press Delete.
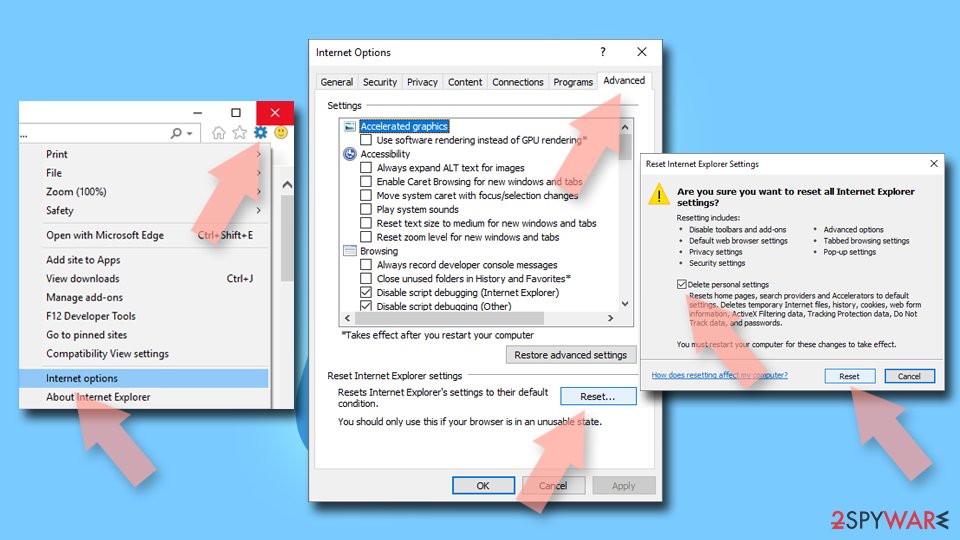
Reset Internet Explorer:
- Click on Gear icon > Internet options and select Advanced tab.
- Select Reset.
- In the new window, check Delete personal settings and select Reset.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
From our report of Jun 2020 · not reviewed since
Proper guide for the Graizoah.com virus elimination
Make the system clear and PUP-free again by running the proper anti-malware tool on the system.
This is how you can remove Graizoah.com, find and delete any related threats, programs that rigger changes in the browser settings, and system preferences. You need some help from such automatic tools even though you are not a tech-savvy person.
Since the PUP managed to get on your machine, check various parts of the machine, so the virus is found and terminated. Remember that such intruders aim to modify settings on the web browser to cause all the redirects more frequently.
Google Chrome, Internet Explorer, Mozilla Firefox, Safari, and other browsers get altered, so you may need to go through those preferences manually. Perform the proper Graizoah.com removal with professional anti-malware tools.
Questions about Graizoah.com ads
Why does my browser keep going to graizoah.com?
Something is sending it there. On one site only, that site's ads are the cause and leaving the site ends it.
On many different sites, the usual causes are an extension you installed with something else, a site you once allowed to send notifications, or an ad-supported program in Windows that changes how the browser behaves. graizoah.com itself is only a stop on the way: it records the visit and forwards you to whatever advertiser pays most.
Check the extensions page, then the list of sites allowed to send notifications, then Installed apps sorted by date. Removing the cause stops the redirects; blocking the domain alone usually does not, because the network moves to a new one.
Did graizoah.com install a virus on my PC?
Very unlikely, unless you downloaded and opened something from the pages it led to. Redirect domains such as graizoah.com sell your visit to advertisers; they do not need to install anything to make money.
What can be installed is the thing that causes the redirects in the first place, such as an extension or an ad-supported program that came with free software. That is why the checks in this guide look at extensions, notification permissions and Installed apps.
A full scan with Microsoft Defender afterwards gives you a clear answer about the rest of the PC. If the scan is clean and the redirects stop after removing the cause, you are done.
Why does Graizoah.com show me ads?
Because that is its whole purpose. Graizoah.com is an ad redirect domain, and its operators are paid for every ad it displays and every click it gets. In this case the ads take the form of redirects through ad pages.
They are chosen by ad networks that accept almost any advertiser, which is why so many look like warnings or prizes. The ads are not a sign that your PC is broken or infected with something worse; they are a sign that something on it, or in the browser, has permission to advertise. Removing that permission or program stops them.
Is graizoah.com safe to visit?
No. The site graizoah.com exists to push visitors towards ads, and the pages it leads to include fake virus warnings, fake updates, prize scams and notification prompts. Visiting it once does not infect an up-to-date PC, but anything you click or download there is a gamble.
Do not enter personal details, do not allow notifications and do not call phone numbers it shows. If it opens by itself, close the tab and check the browser's extensions and notification permissions. Blocking the single domain helps little, because the operators register new names regularly.
Do I have to clean every browser?
Yes, if you use more than one. We saw Graizoah.com in Chrome, Edge and Firefox, and each browser keeps its own extensions, notification permissions and settings. Chrome and Edge share the same extension format, so one installer can add the same adware to both, while Firefox has its own add-ons.
Check every browser on the PC, including ones you rarely open. If you sync a browser with an account, clean it while signed in, so that the removal reaches your other computers rather than the adware returning from them.
How do I know the ads come from Graizoah.com?
Look for redirects to graizoah.com. That is the trace Graizoah.com leaves, and it shows up as redirects through ad pages. Ads that appear on every site, including ones that never carried ads before, point to something on your PC or in the browser rather than to the sites themselves.
A quick test is a private window, where extensions are off by default: if the ads disappear there, an extension is responsible. If they appear even with the browser closed, the source is a notification permission or a program in Windows.
I clicked on one of the ads. Am I infected?
Probably not. Clicking an ad usually only opens a page, and a page cannot install programs on an up-to-date Windows PC without your help.
You are at risk only if you then downloaded and ran a file, allowed notifications, entered card or login details, or called a phone number shown on the page. Delete any download and run a full and offline scan.
Change passwords you typed, from a clean device. Call your bank if you gave card details. If you called a number or allowed remote access, see the next question.
Does adware steal passwords?
Ordinary adware is built to show ads, not to steal logins, and most of it never touches saved passwords. The line is blurry, though. Extensions that can read every page could capture what you type, and adware ads sometimes lead to phishing pages that ask for passwords directly.
If you entered credentials on a page reached through an ad, change that password from a clean device and turn on two-step verification. Otherwise, removing ad redirect domain and clearing cookies is usually enough.
An ad showed a phone number and I called it. What now?
The number belongs to scammers, not to Microsoft or an antivirus company. If you only talked, hang up and do not call back. If you let them connect to the PC, disconnect it from the internet, uninstall the remote access program they used, such as AnyDesk, TeamViewer, ScreenConnect or UltraViewer, and run a full and offline scan.
If you paid or gave bank details, call your bank at once on the number printed on your card. Change any passwords you typed while they were connected, and report the call.
Will Fortect remove Graizoah.com?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Graizoah.com, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Wikipedia: Pay-per-click (read October 6, 2026)
- Krebsonsecurity: FEMA IT Specialist Charged in ID Theft, Tax Refund Fraud Conspiracy (read October 6, 2026)
- Virusai: Virusai (read October 6, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)