
Guildma: what it is and how to remove it
Guildma is a sophisticated data-stealing malware that was recently discovered and analyzed by most prominent security research teams. The virus targets more than 130 Latin American banking systems and 75 local web services, with its primary goal being to steal banking, email, entertainment service, and other credentials.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Unsure whether wmic.exe is safe? A free scan checks the file and what starts it.
Do it yourself · free Remove Guildma yourself 5 steps, about 15 minutes, no software needed.
Start the steps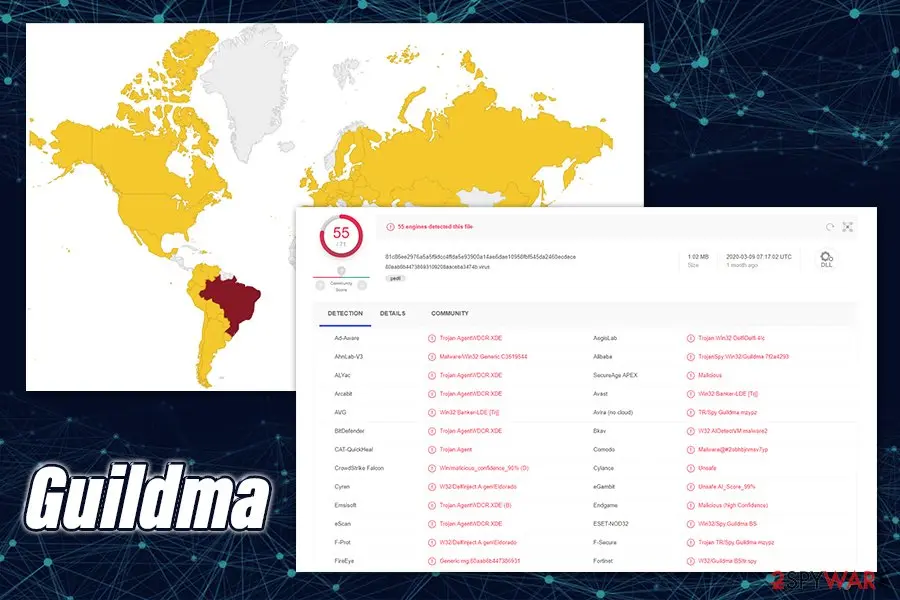
Guildma: summary
| Damage | Loss of sensitive information (disclosure to cybercriminals), financial losses, identity theft, infection of other malware |
|---|---|
| Name | Guildma |
| Also known as | Astaroth |
| Type | Banking Trojan |
| Platform | Windows |
| Programming languages | Threat actors use a combination of different programming languages which the malware is written in: Delphi, JS, VBS, and others |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 11 more facts
| Affected area | Malware is almost elusively focusing on Latin America – Brazil in particular |
|---|---|
| Infection means | Guildma malware is spread exclusively using spam email attachments and incorporating Facebook and YouTube profiles. Emails are sent as invoices, tax reports, and similar messages – these include a .zip file which, once opened, initiates the infection process |
| Functions | Records keystrokes, takes screenshots, proliferates other malware, emulates keyboard and mouse inputs, steals credentials of e-commerce, email, and other services |
| Detection names | No Microsoft detection name is known |
| Distribution | Not recorded in the old report |
| Symptoms | An unknown process in Task Manager and a Windows Security "Threats found" notification |
| Evidence | 4 write-ups by security sites; no sample analysed yet |
| File names | wmic.exe |
| First seen | 17 April 2020 |
| Microsoft Defender name | Trojan:Win32/Guildma.V!MTB |
| Facts checked | 6 October 2026 |
What Guildma does on an infected PC
From our report of Apr 2020 · not reviewed since
Guildma is modular malware capable of stripping victims of the most sensitive information
Throughout its existence, Guildma was released in several different versions and has been tweaked and improved over time.
While threat actors employed a variety of different programming languages, data-stealing methods, as well as infection techniques, most of the code patterns such as encryption algorithms, file names, and other components remained unchanged.
Before starting the infection routine, Guildma Trojan first checks whether it accessed a sandbox environment (or a virtual machine which is often used by security researchers to analyze malware samples and their operation principles), and only proceeds if it detects a regular "user" machine. It will also not infect machines that are not located in the country of interest, i.e., mostly Brazil - Guildma checks keyboard language for that.
According to researchers, Guildma also checks for running applications, which is then followed by immediate data-stealing practice:
The main module ("Module G") is very diverse and is responsible for such operations as C&C server communication establishment (which also incorporates YouTube and Facebook profiles to retrieve the C&C servers), loading of other modules, running application tracking, and much more.
Besides the regular banker malware capabilities, Guildma is equipped with an array of modules (at least 10), each capable of performing different tasks. These tasks are not only comprised of data-stealing but also include the following functionality:
Guildma uses a variety of tricks to make users expose their credentials. Once the malware is active on the system, it forcefully logs users out of accounts on Google Chrome, Mozilla Firefox, Internet Explorer or MS Edge, making them re-enter credential data repeatedly.
This information is later sent to the C&C server via an established network connection. Guildma will also record everything typed by the keyboard and take screenshots to steal relevant information.
Guildma also has a from grabber function, which allows the virus to capture email lists from MS Outlook, Thunderbird, and other email desktop clients. This module also includes the capability of stealing data from relevant websites.
As evident, the presence of Guildma Trojan can seriously compromise the infected machine and result in financial losses, or even identity theft. Therefore, users should ensure that they would not get tricked by realistically crafted phishing emails, although protection of anti-malware software is the most critical component that would defend victims from malware intrusions.
- Screenshot capture
- Keystroke capture
- System reboot
- Keyboard and mouse emulation
- Keyboard shortcut blocking (such as Alt + F4 or Ctrl + W)
- File fetching
- Implementation of secondary payloads (backdoor function)
From our report of Apr 2020 · not reviewed since
More from our earlier report on Guildma
- Throughout the execution, it frequently performs checks for opened windows, mostly looking for banking applications or PuTTY.
- These detections trigger injections, screenshots, key hooking and "flag" file creation.
- All these actions are orchestrated by a vast array of interacting timers with a rather complicated hierarchy.
What Guildma can steal or download
From our report of Apr 2020 · not reviewed since
Guildma is a sophisticated data-stealing malware that was recently discovered and analyzed by most prominent security research teams.
The virus targets more than 130 Latin American banking systems and 75 local web services, with its primary goal being to steal banking, email, entertainment service, and other credentials. Threat actors behind Guildma launched multiple large campaigns that were infecting as many as 50 thousand people a day via contaminated spam email attachments.
Its first emergence traces date back to 2015, although its peak was (so far) in summer/autumn of 2019. Currently, the Guildma virus is still spiking in popularity, and is currently the most prominent banking malware in Latin America, infecting ten times more victims than the second most common banking malware in the area.
Malware infection might not be so apparent, as, just like many other Trojans, it barely emits any symptoms and performs its operations in the background, which might prevent Guildma removal for weeks or even months. In the meantime, users might be running their computers as normal, providing the most sensitive information directly to cybercriminals.
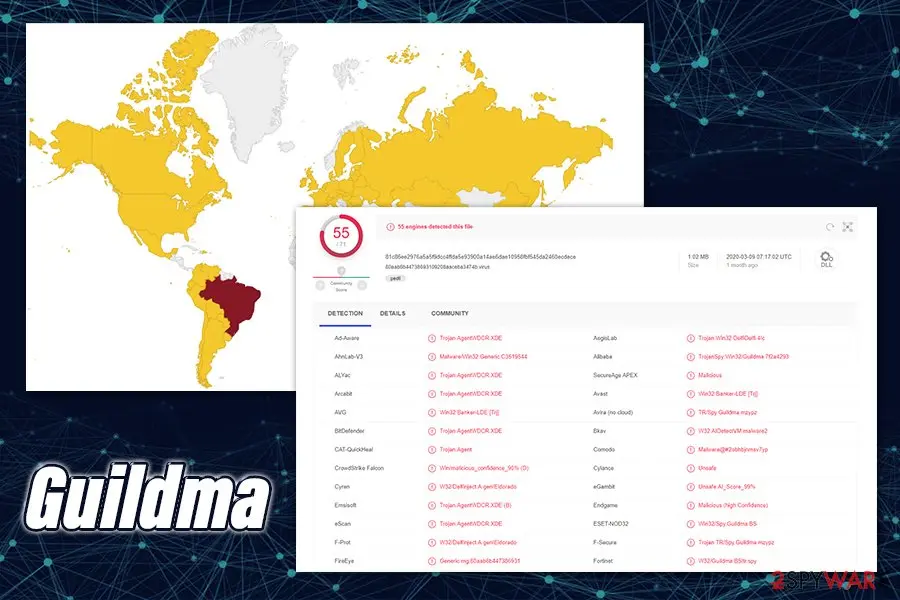
Nevertheless, most of the legitimate anti-malware solutions would be able to stop all variants of Guildma, as its main executable is recognized as follows:
To remove Guildma, you will have to download and install one of the reputable AV providers, such as , and perform a full system scan. Since malware is modular and might interfere with anti-malware operation, you might need to access Safe Mode with Networking and perform the scan from there. Once Guildma is terminated, you can also take care of Windows system files and fix the damage done with tools like .
- Trojan.AgentWDCR.XDE (B)
- TR/Spy.Guildma.mzypz
- Trojan.Win32.DelfiDelfi.4!c
- Trojan.TR/Spy.Guildma.mzypz
- Trojan:Win32/Guildma.V!MTB
- Mal/Generic-L
- W32/Guildma.BS!tr.spy, etc.
How Guildma got on your PC
From our report of Apr 2020 · not reviewed since
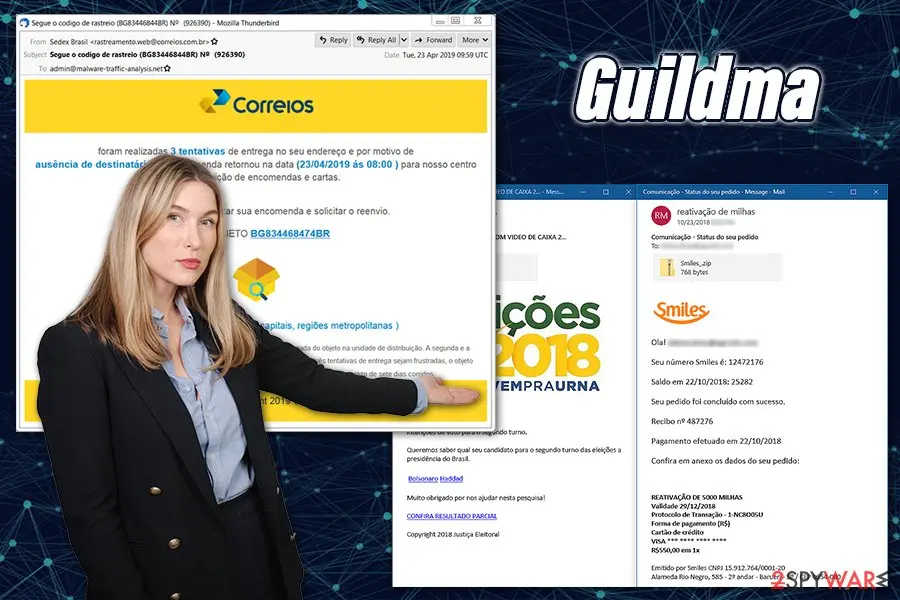
While Guildma malware is spread via spam email attachments, its method of doing so is innovative and sophisticated.
To spread malicious emails, threat actors behind the malware are using mostly hacked or fake websites, where a malicious PHP code is installed. With this, the attackers can use the gathered email addresses to launch mass spam campaigns, infecting thousands of users daily.
The phishing emails come in the native (Portuguese) language and represent tax refunds, invoices, invitations, and similar events. Each of such emails is injected with a .zip file, usually named as follows:
- cheque.htm.zip
- curriculum_.htm.zip
- dados unidas rent a car.htm.zip
- nota_fiscal.484.582.85.zip
- etc. Such emails look professional
- many users could get tricked and open the clipped attachment
Inside the archive, there is an obfuscated shell link (LNK) file, which calls the wmic.exe via Command Prompt to download the XSL file. The latter contains the malicious payload that begins the infection routine on the targeted machine.
To prevent infiltration of Guildma malware, users should not open attachments carelessly, as some phishing emails can look very believable. Thus, only open attachments you know are safe and are coming from a secure source. Uploading such attachments to Virus Total or similar analysis services can also help you determine whether it is malicious.
How to check the PC for Guildma
What antivirus programs call Guildma
Microsoft Defender reports Guildma as Trojan:Win32/Guildma.V!MTB.
In a Defender name, the part before the colon is the category, the part after it is the platform, and the part after the slash is the family Microsoft assigned. A suffix after ! is an internal Microsoft marker, not a different threat.
Generic labels such as Agent, GenericKD or Malware.AI only say that a file looks malicious, not what it does; our guide to antivirus detection names shows how to read them.
- File:
wmic.exe
How to remove Guildma
How to remove Guildma and protect your bank account
Call the bank first, because money can move faster than you can clean the PC.
Step 1: Call your bank
Money moves fast, so call the bank before anything else on this list is finished.
Use the number on the back of your card or in the bank's app, report possible fraud, and ask for the card to be blocked and new online banking credentials to be issued.
Ask whether payments made in the last days can be stopped or disputed. Do not sign in to the bank from the Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: What to do after paying a scammer
Step 2: Check where wmic.exe runs from and stop it
In Task Manager (Ctrl + Shift + Esc) find
wmic.exeon Processes, right-click it and choose Open file location before ending anything.Windows' own files live in
C:\Windows\System32; the same name in%AppData%, %Temp% or C:\Users\Public is an impostor. If the folder is wrong, right-click the process again, choose End task and delete the file.If it starts again within seconds, a task or another process restarts it, so run the scan step in Safe Mode. Task Manager works the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 3: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Scan the PC, then run the offline scan
A scan finds the parts of Guildma that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Guildma can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Apr 2020 · not reviewed since
Eliminate Guildma from the system immediately
As previously mentioned, Guildma virus can cause significant damage to the computer owner, as it can steal such sensitive data like banking, email, and other login credentials.
As a result, users might see their credit card accounts being drained without permission, or goods being purchased under their names. Online banking accounts should always be monitored for unsolicited transactions. In case you noticed that your bank account was was emptied, there is a high chance you should immediately remove Guildma from your computer.
To remove Guildma malware from the system, download and install a powerful anti-malware program, bring it up to date, and perform a full system scan. This will ensure that all the malicious components, along with other possible malware, is eliminated at once. If you are struggling when trying to perform a scan, you should access Safe Mode with Networking and employ anti-malware software from there.
Additionally, if you have been a victim of Guildma attack, you should reset all your passwords after malware termination. Also, contact your bank and explained what happened, as you should close any compromised bank accounts.
[GI=method-1]If you are unable to remove Guildma in a regular mode, access Safe Mode with Networking:
After removal: passwords, accounts and prevention
Secure your accounts after the clean-up
Assume that whatever was saved in the browsers on this PC while the PC showed an unfamiliar process called wmic.exe in Task Manager has been copied:
- passwords
- cookies
- autofill data
Work from a clean device, or from this PC once the offline scan finds nothing.
Start with your main e-mail account, because it can reset everything else, then banking and payment, then social and gaming accounts. Change each password, sign out of all sessions and turn on two-step verification: Turn on two-step verification / secure a hacked account.
The full order, including crypto wallets and card replacement, is in securing your accounts after malware.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
Questions about Guildma
Is wmic.exe a virus?
The name wmic.exe is not enough to say. Malware often uses technical-sounding names, and harmless updaters often use odd ones. Check three things:
- the folder the file runs from
- the Digital Signatures tab in its properties
- the program that starts it (Startup apps, Task Scheduler or services)
A signed file from a company whose product you use is almost certainly fine. An unsigned file in a user folder that no installed program explains should be removed, and the PC scanned with Microsoft Defender in offline mode.
Is Trojan:Win32/Guildma.V!MTB a false positive?
Sometimes. Names ending in !ml or describing behaviour are generated by machine learning and occasionally flag cracked tools, game mods or small unsigned utilities. A false positive is likely only when the file is a program you installed from its official developer, it is signed by that developer and other scanners do not flag it.
Files from cracks, cheats, fake updates or unknown downloads are rarely false positives, whatever the detection name. If you are sure the file is genuine, you can report it to Microsoft as a false positive; never add an exclusion for Trojan:Win32/Guildma.V!MTB just to make the alert stop.
wmic.exe keeps coming back. What should I do?
A process that returns after you end it has a restart mechanism, and that is a reason to treat wmic.exe as unwanted. Check Settings > Apps > Startup, Task Scheduler and the Services list for entries pointing to its folder, and disable them.
Look in Installed apps for anything added the same day and uninstall it. Then delete the folder and run a Microsoft Defender Offline scan, which works before Windows starts and can remove files that are locked or hidden while the system is running.
Why does Trojan:Win32/Guildma.V!MTB keep coming back?
Because removing the file does not remove what creates it. The usual causes are a scheduled task, a startup entry, a service or a browser extension that downloads or rebuilds the file, or a second program that installed it in the first place.
Look in Task Scheduler and Startup apps for unknown entries, check Installed apps sorted by date, and run a Microsoft Defender Offline scan, which can remove items that are locked while Windows runs. Also check that no exclusions were added in Windows Security. If Trojan:Win32/Guildma.V!MTB still returns, back up documents and reset Windows.
Is Microsoft Defender enough to remove Guildma?
For most home PCs it is a solid first step. Defender detects this threat as Trojan:Win32/Guildma.V!MTB, and a full scan followed by an offline scan covers the places where Guildma usually hides. The offline scan runs before Windows starts, so malware that hides while Windows is running cannot interfere: Run a Microsoft Defender Offline scan.
Defender does not undo everything, though. It does not restore browser settings, decrypt files or change passwords that may have been copied, which is why this guide has separate steps for those. If Defender finds the same item again after removal, something else keeps reinstalling it.
Can I keep using the PC while Guildma is on it?
Not for anything that matters. As long as the program behind an unfamiliar process called wmic.exe in Task Manager runs, it can see what you type and what the browser stores, and it may download more malware. Disconnect the PC from the internet while you remove it, and do your banking, e-mail and password changes from another device.
Once the offline scan finds nothing and the sign does not return after a few restarts, normal use is fine. If the scan keeps finding new items, or you cannot remove the startup entry, a reset of Windows is the safer choice.
Which malware family is Guildma?
That is not known yet. Guildma has been reported by people who saw an unfamiliar process called wmic.exe in Task Manager, but no sample has been analysed publicly, so security companies have not assigned it to a family. The name you see may be a file or program name chosen by the authors, not a family name.
This does not stop you from removing it: the startup points, the offline scan and the account steps are the same for most families of this type. If Microsoft Defender or another scanner gives the file a detection name, write it down; that name is the best clue to the family and is useful when you report the incident.
Should I report Guildma?
Report it if you lost money, if accounts were taken over, if you are a business, or if the trojan came through a scam call. A police or national cybercrime report gives you a reference number for your bank and insurer and helps link cases.
You do not need to report a trojan that antivirus blocked before it ran. Before reporting, write down the dates, the detection name, file names and any messages or transactions linked to the attack; screenshots of antivirus alerts are useful evidence. The country list is in the report section above.
My antivirus was on. How did a trojan get past it?
Antivirus programs see a file only when it is written or run, and criminals test each new build against popular scanners before release. Detection catches up within hours or days, which is often after the first victims ran it.
Archives with passwords, installers that fetch the malware later, and scripts run through PowerShell make the job harder. That is why behaviour such as downloading cracks or pasting commands matters more than any setting. Keep Windows and Defender updated, and turn on Reputation-based protection in App & browser control.
Will Fortect remove Guildma?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Guildma, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- We Live Security: Guildma: The Devil drives electric (read October 6, 2026)
- Virus Total: 81c86ee2976a5a5f9dcc4ffda5e93900a14ae6dae10958fbf545da2460ecdece (read October 6, 2026)
- Decoded: Deep Dive into Guildma Malware (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)