
MacClean: what it is and how to remove it
MacClean is the macOS utility that gets indicated as potentially malicious by various AV tools. Detection names differ from tool to tool due to various databases, but this is the intruder that falls into a category of potentially unwanted programs or Mac malware since it targets Apple devices.
Facts checked October 6, 2026. Removal steps checked against Apple's current documentation and the security vendors' reports. We have not run the malware on a Mac. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your Mac is infected.
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds before you decide anything.
If you want to confirm nothing else came with PUA:Win32/Presenoker, a full scan checks the usual places in one pass.
Do it yourself · free Remove MacClean yourself 7 steps, about 21 minutes, no software needed.
Start the steps
MacClean: summary
| Distribution | Freeware bundling, visiting deceptive websites, other potentially unwanted programs can also load rogue tools on the machine automatically |
|---|---|
| Name | MacClean |
| Type | Rogue tool/ potentially unwanted program |
| Developer | iMobie |
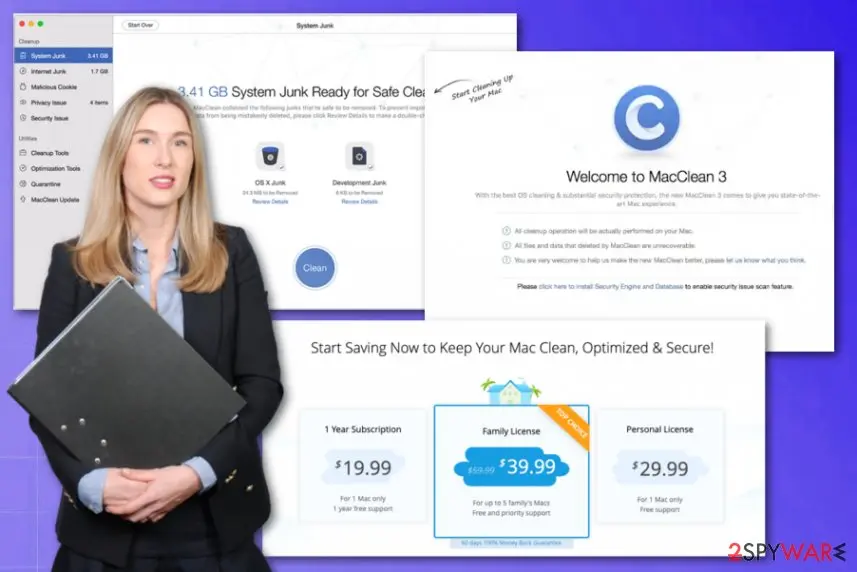
| Symptoms | Pre-determined scan results show up on the screen stating that you need to purchase the full version of the tool to fix the issues. Various claims show up on promotional ads and commercial content that fills up the screen exposing the user to possibly harmful material |
| Price of the tool | The license goes from $19.99 to $39.99 per year |
| Removal | Scan the Mac with security software to find the malware and anything installed with it. Fortect for Mac scans for malware and unwanted programs. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 7 more facts
| Danger | Ad-tracking[1] is one of the more common features that can lead to issues with your privacy or expose to malware-filled pages and result in more serious infection |
|---|---|
| Detection names | No Microsoft detection name is known |
| Damage | Not recorded in the old report |
| Evidence | 5 write-ups by security sites; details still limited |
| First seen | 25 November 2019 |
| Microsoft Defender name | PUA:Win32/Presenoker |
| Facts checked | 6 October 2026 |
Is MacClean a real security program?
What antivirus programs call MacClean
Microsoft Defender reports MacClean as PUA:Win32/Presenoker.
In a Defender name, the part before the colon is the category, the part after it is the platform, and the part after the slash is the family Microsoft assigned. A suffix after ! is an internal Microsoft marker, not a different threat.
Generic labels such as Agent, GenericKD or Malware.AI only say that a file looks malicious, not what it does; our guide to antivirus detection names shows how to read them.
From our report of Nov 2019 · not reviewed since
MacClean is the clean-up tool that should help to optimize the computer, but installer potentially contains viruses
MacClean is the macOS utility that gets indicated as potentially malicious by various AV tools.
Detection names differ from tool to tool due to various databases, but this is the intruder that falls into a category of potentially unwanted programs or Mac malware since it targets Apple devices. Also, some detection names include the name of developers and providers -iMobie.
The China-based company offers various tools and software for consumers and claims that the name is inspired by words optimistic, brave, independent, and efficient, which should represent the main characters of the team. All the convincing claims and statements can make people trusting and lead to app installation on purpose.
Too bad for the people that install MacClean and need to encounter suspicious content, messages from AV tools, or security features when the system utility provides nothing positive to the system. This is one of many tools offering to optimize Mac devices. However, Apple computer doesn't need optimization software or cleaning, maintenance utilities.
However, in most cases, the MacClean tool comes like any other potentially unwanted program - without permission.
Common techniques used to spread threats like MacClean virus include deceptive sites, promotional content, advertisements, and websites where this program is described as a tool that cleans, optimizes, and safeguards your machine from potential risks, malware infections.
Many functionalities listed on ads and the official developers' page claims that deep malware scans and junk file cleaning should make the device safe, clean, and fast. Unfortunately, the program is reported as unreliable and possibly containing malware and questioned by many users online.
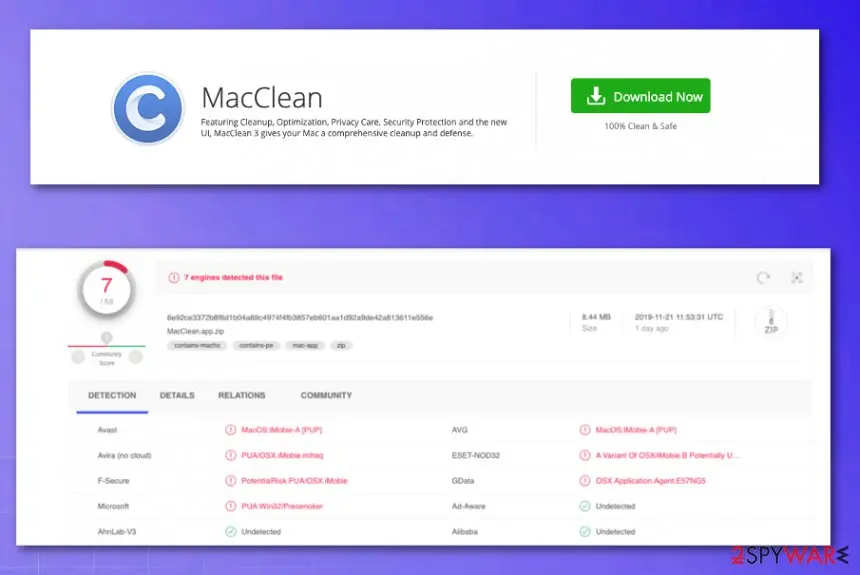
MacClean is considered dangerous due to AV tool detections that can show up when you scan the machine. The following names are indicated once you check the application file, but other names may appear depending on the particular program you use:
Mac Clean is the program made and distributed by iMobie company that is a China-based team creating Apple software. The official page for this tool or many other applications seem legitimate and provides information that attracts people to buying and downloading the program themselves.
However, MacClean virus is the mane used by people because PUP comes without the users' knowledge or permission using misleading and shady techniques. In most cases, developers and creators of such programs focus on advertising revenue generation and promoting the software enough, so money can be made.
Once you see the shady ad for the rogue system optimization utility, you need to remove MacClean from the machine and exit every pop-up ad or a window with commercial material. Sales are the main priority for the PUP developers, so there is nothing valuable from the rogue application, especially when macOS is a system that is not requiring any tools like this.
MacClean removal is important because there is nothing that the tool can be used for. Mac devices are completely self-optimizing, and utilities like this have no place on the machine. However, anti-malware tools are needed, even though some people think macOS is the virus-free system. Such programs are the best for fighting PUPs like this shady application.
You may additionally need to check the web browsers yourself to terminate additionally loaded extensions, add-ons, plugins, and so on. You can find instructions for that below. Also, run on the machine to fix the damage that is made on the system behind your back.
- MacOS:IMobie-A ;
- PUA:Win32/Presenoker;
- A Variant Of OSX/iMobie.B Potentially Unwanted;
- OSX.Application.Agent.E57NG5.
From our report of Nov 2019 · not reviewed since
MacClean termination involves proper AV tools and full system cleaning to end background processes
Keeping any program like MacClean virus can lead to monetary loss when you buy this app or make purchases of other shady applications, and constant commercial content delivery, exposure to potentially harmful material. There are many symptoms these cyber intruders have that you cannot notice yourself, so the cleaning process gets affected.
When you decide to remove MacClean from your machine, you should remember that it installs itself and can load other programs during the same process or later on. The company that makes this PUP also promotes other software that can get installed on your computer without any permission required.
The best way to tackle the MacClean removal is to get the anti-malware program and check the system for malicious programs automatically. Such software can indicate dangerous programs, suspicious applications, and delete them once and for all. Additionally, you should run system programs to repair needed parts of the directories or functions, to avoid infection repetition.
From our report of Nov 2019 · not reviewed since
More from our earlier report on MacClean
- For MacClean removal, you should get an anti-malware tool compatible with macOS that can clean the machine fully from PUPs
- Unfortunately, this cyber infection can also affect system folders, directories, and startup preferences, so you should get a tool like to repair at least some of the more crucial files without damaging them further
How MacClean got on your Mac
From our report of Nov 2019 · not reviewed since
When you surf online you get exposed to various commercial content and promotional ads, so there is a big possibility to get unwanted or even malicious programs installed if you don't think about the content you click on constantly. One-click or page visits can trigger the automatic installation of a rogue tool, potentially unwanted programs like adware, browser hijacker, or even load the malicious script on your system directly.
Promotional content sometimes can download the advertised tool on your computer without additional pop-up with permission requirement, so you should be aware. However, even those installations that deliver you the setup window can lead to freeware infection when you choose not the correct option.
Advanced or Custom installations are the only ones recommended by experts because such options show the full list of pre-packed applications, so you can deselect suspicious programs. Recommended installations allow everything bundled in the package without you even noticing.
How to remove MacClean
Start with the passwords and crypto, from another device: a stealer copies them in seconds.
Then clean the Mac, or erase it.
Step 1: Change passwords from another device first
If you pasted a command into Terminal or opened a downloaded file from MacClean, assume the passwords saved in the browsers and in Keychain on this Mac are known to the attacker.
From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and work accounts, and sign out of all other sessions on each one.
Move any cryptocurrency to a new wallet created on a clean device, because a seed phrase that was stored on this Mac is compromised. Do this before cleaning the Mac: cleaning does not undo the theft.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Quit what is running that you do not recognize
Open Activity Monitor (in Applications > Utilities, or search for it with Command + Space).
In the CPU or Network tab, look for a process you did not install or whose name is random, select it, click the stop button (the octagon with an X) and choose Quit or Force Quit.
Note the name first: you will look for the same name in the next steps. Malware that comes back after a restart is handled in the next two steps.
Step 3: Remove unknown login items and background items
Open System Settings > General > Login Items & Extensions. Under Open at Login and Allow in the Background, switch off or remove anything you do not recognize, especially items whose developer is shown as an unknown name or that appeared on the day you ran the command.
Then open Finder, choose Go > Go to Folder and check
~/Library/LaunchAgents,/Library/LaunchAgentsand /Library/LaunchDaemons for property list (.plist) files you did not add. Drag suspicious ones to the Bin, then restart the Mac.Step 4: Delete apps and downloads you did not intend to install
Open the Applications folder and your Downloads folder. Drag any app you did not install, and any disk image (
.dmg), installer (.pkg) or archive (.zip) that came from MacClean or a site you do not trust, to the Bin, then empty the Bin.Also check
~/Library/Application Supportfor a folder with the same name as the app you removed.Step 5: Check the browsers for extensions and changed settings
In Safari open Settings > Extensions and General (homepage). In Chrome open
chrome://extensions, in Firefoxabout:addons.Remove any extension you did not add, and reset the homepage and search engine if they changed. Browsers hold saved passwords and cookies, which is why the password step comes first.
Step 6: If it was an infostealer, erase and reinstall macOS
Stealers copy data and often leave persistence you cannot be sure you found.
The only complete fix is to back up your personal files only (documents, photos, not apps or settings), then open System Settings > General > Transfer or Reset > Erase All Content and Settings, or use macOS Recovery to erase the disk and reinstall macOS, as Apple describes in its support articles.
Restore only your files afterwards, and install apps again from their official sources.
Step 7: Report it and watch your accounts
Report the site and the command to the authorities in your country, and tell your bank if any card was saved in a browser or in Keychain.
Over the next weeks watch your e-mail, bank and exchange accounts for sign-ins and transfers you did not make. Keep the notes you made, such as the process names and the file dates, in case a bank or the police ask for them.
Full procedure with screenshots: Report a cyber attack or scam to the authorities
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Remove from Google Chrome
Your Chrome browser can get affected significantly by the PUP because it installs other applications without permission
Delete malicious extensions from Google Chrome:
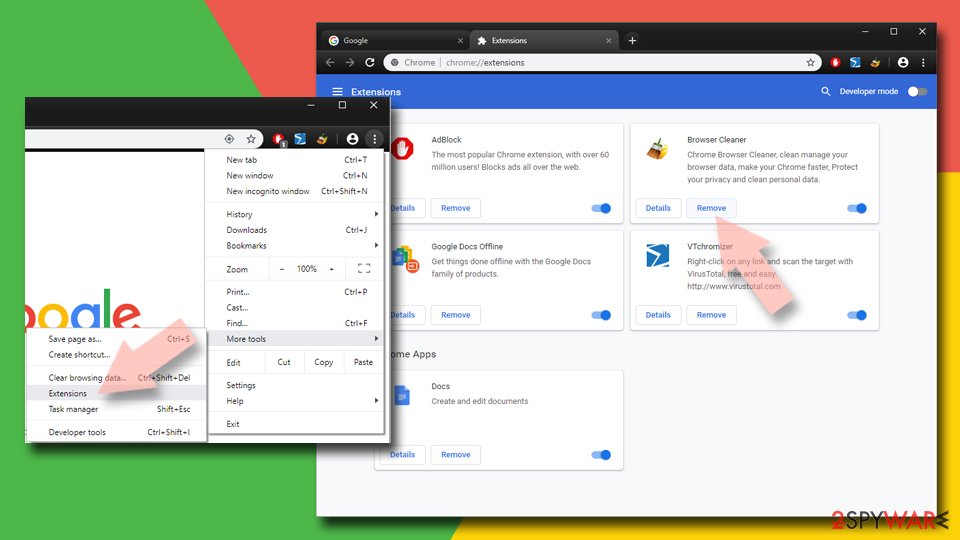
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
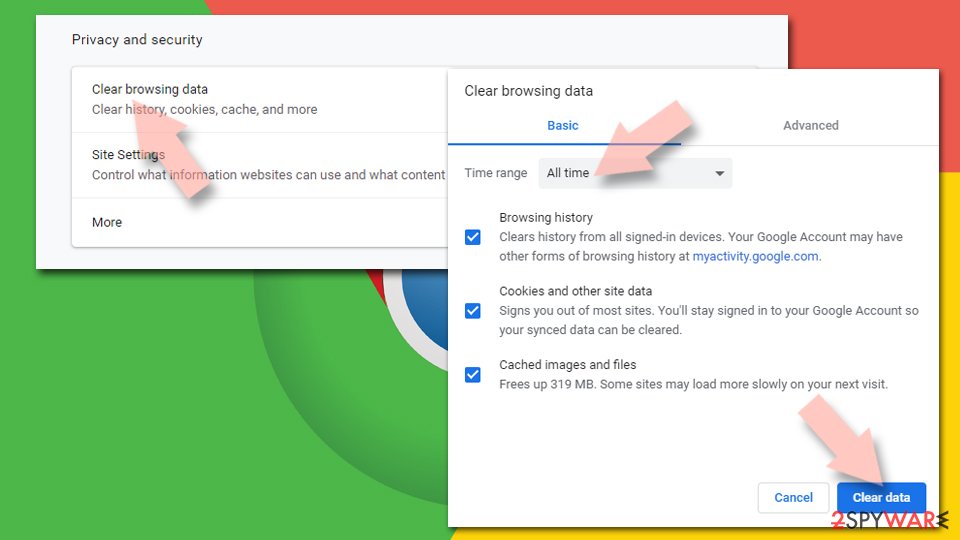
Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
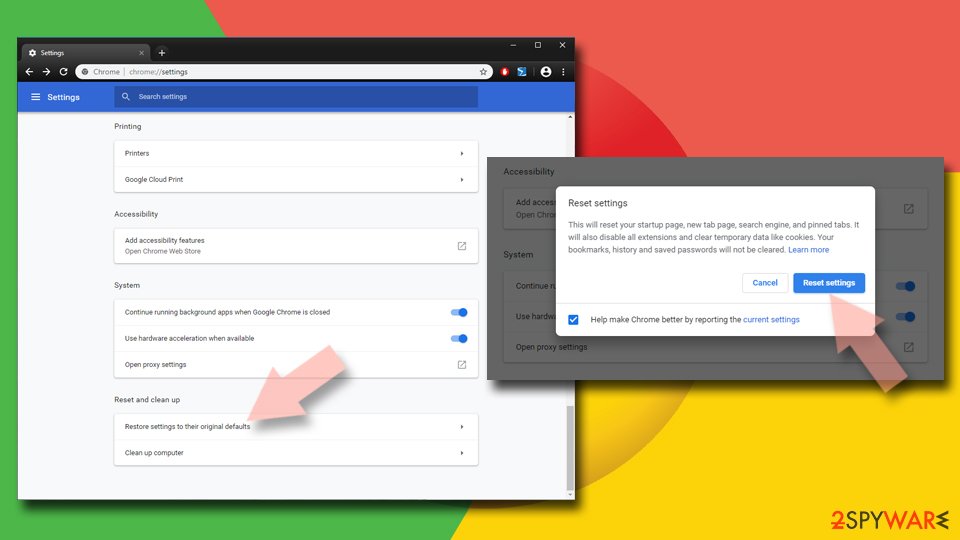
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Mozilla Firefox (FF)
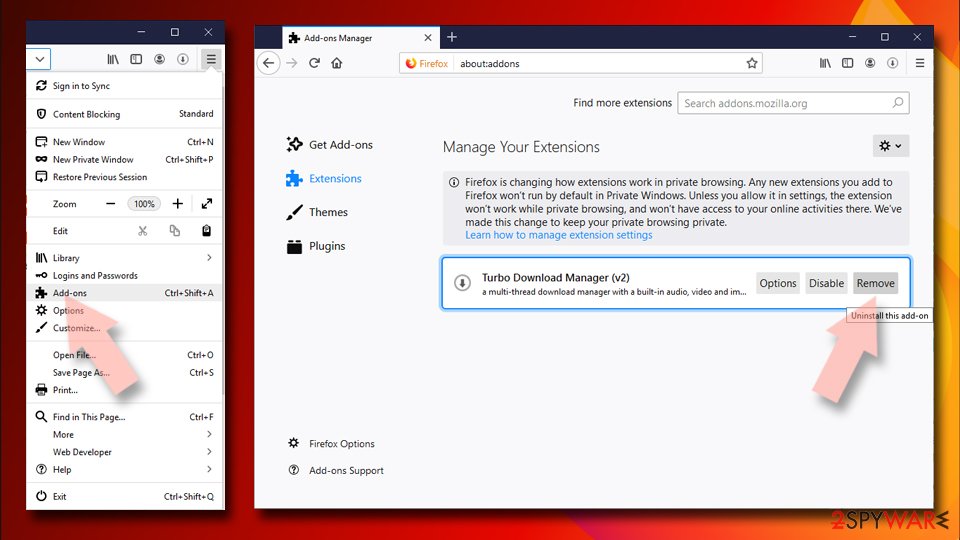
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
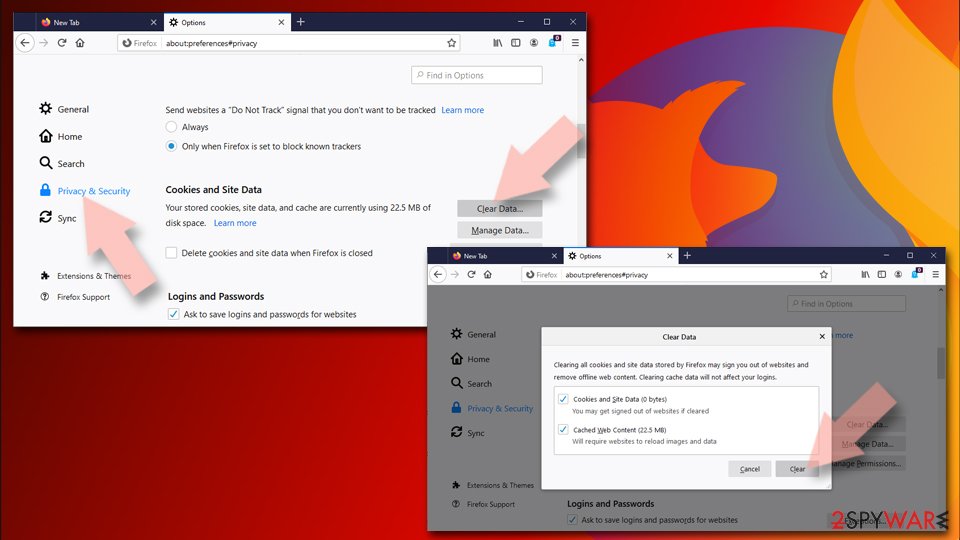
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
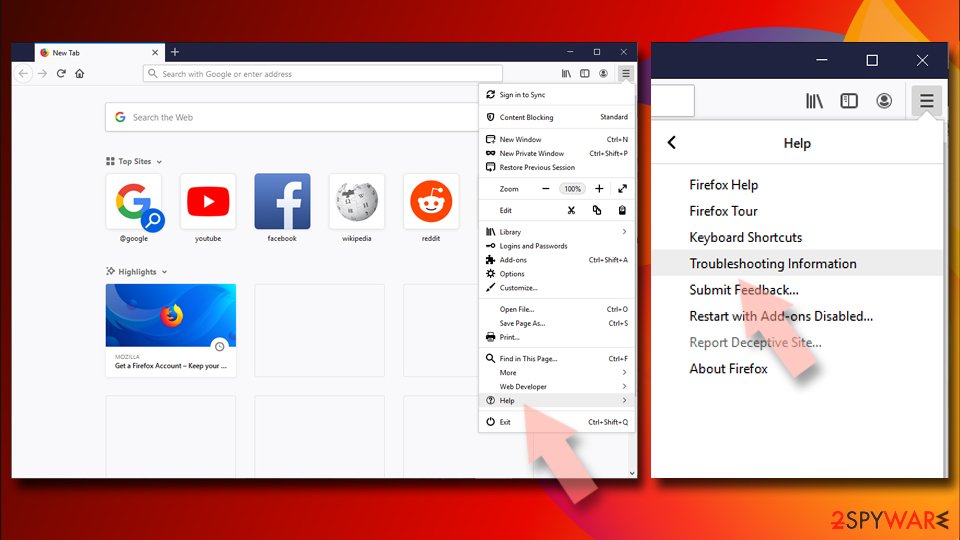
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
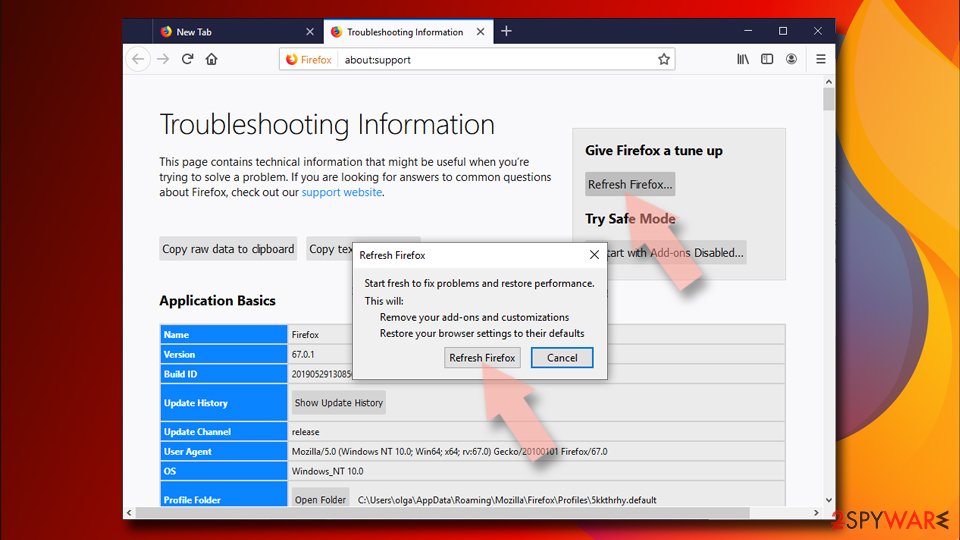
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
Remove dangerous extensions:
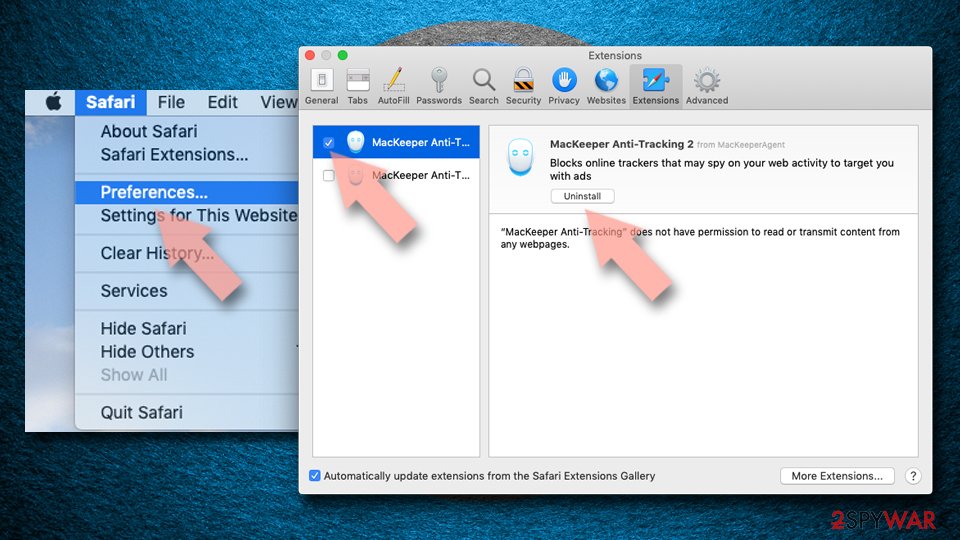
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
Clear history and website data:
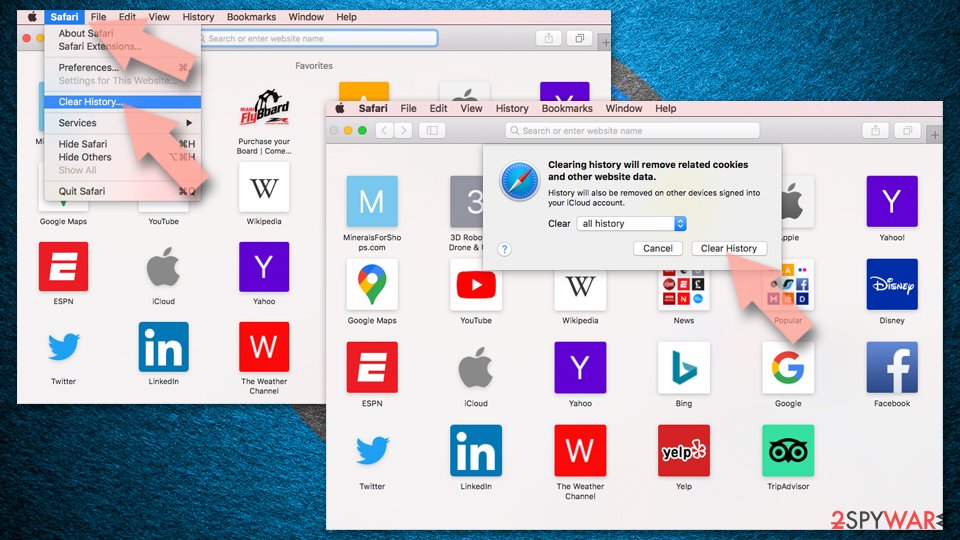
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
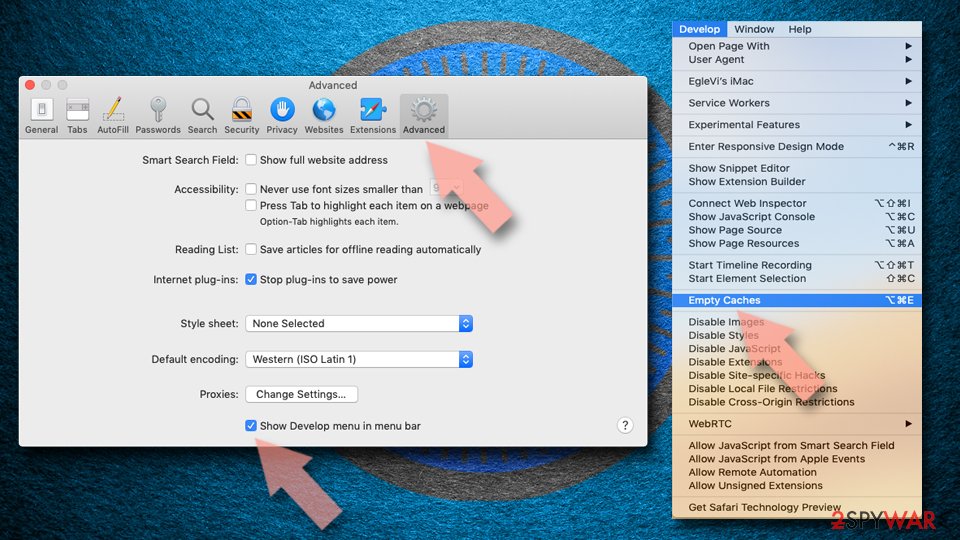
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
MacClean is the rogue tool that you need to uninstall completely to end the unwanted behavior regarding commercial content and promotional ads
Remove the unwanted application:
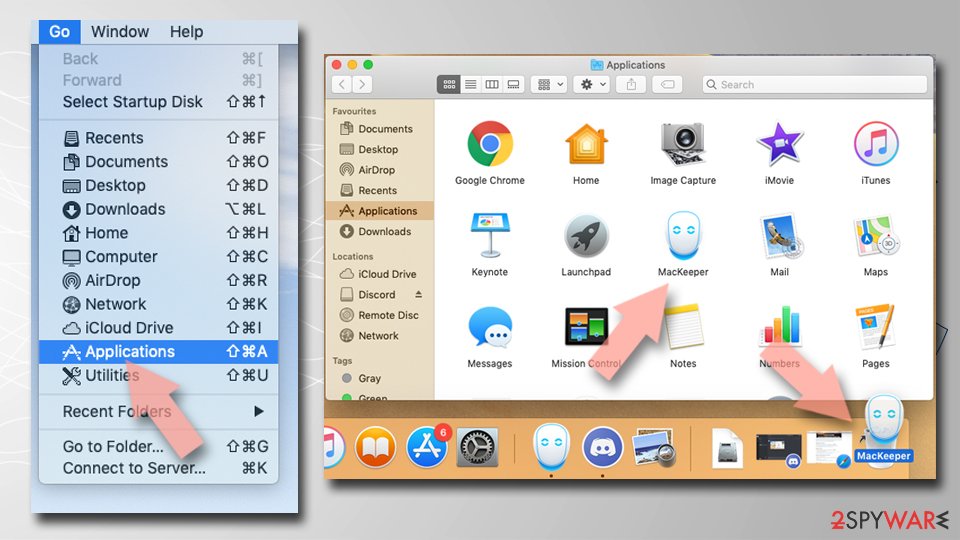
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
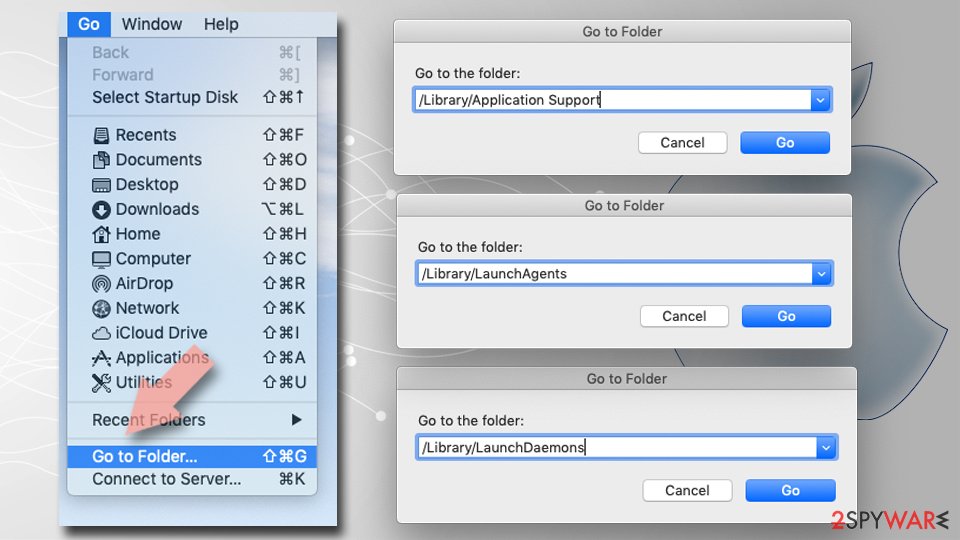
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
Questions about MacClean
What does the name PUA:Win32/Presenoker tell me?
Microsoft builds names in a fixed order:
- category
- then platform
- then family
- sometimes followed by a variant letter
- a suffix
The category is the most useful part for you. Trojan, Backdoor and PWS mean real malware that can download more, give remote access or steal passwords. PUA means unwanted software.
Ransom means ransomware. Suffixes such as !ml or !MTB mean the detection came from machine learning or behaviour analysis. Search for the family part of PUA:Win32/Presenoker together with the word Microsoft to find its entry in Microsoft's security encyclopedia.
Why does PUA:Win32/Presenoker keep coming back?
Because removing the file does not remove what creates it. The usual causes are a scheduled task, a startup entry, a service or a browser extension that downloads or rebuilds the file, or a second program that installed it in the first place.
Look in Task Scheduler and Startup apps for unknown entries, check Installed apps sorted by date, and run a Microsoft Defender Offline scan, which can remove items that are locked while Windows runs. Also check that no exclusions were added in Windows Security. If PUA:Win32/Presenoker still returns, back up documents and reset Windows.
Will Windows Security detect MacClean?
Yes, current Microsoft Defender definitions name it PUA:Win32/Presenoker. Make sure the definitions are up to date first: open Windows Security > Virus & threat protection > Protection updates and click Check for updates. Then run a full scan and the Microsoft Defender offline scan.
If the detection comes back after you remove it, look for the program, task or extension that brings it back, using the plan above. Detection removes files and startup entries, but it does not reverse changes MacClean already made, so follow the other steps in this guide as well.
Do I need to buy antivirus after removing MacClean?
No. Windows 11 and Windows 10 include Microsoft Defender in Windows Security, which provides real-time protection, scheduled scans, the offline scan and protection against unwanted apps at no cost. Keep it switched on and updated, and turn on Reputation-based protection under App & browser control.
If you prefer a third-party product, buy it from the vendor's own site after reading independent test results, never from a pop-up or a phone call. The lesson of MacClean is that security offers which arrive unasked are the ones to avoid.
How do I know MacClean is fake?
Three things give it away. It appears as the Windows Security detection PUA:Win32/Presenoker, a window from a program rather than from Windows Security. It pushes you to act quickly by calling, paying or downloading.
And the threats it reports never show up when you run a scan in the real Windows Security app. Microsoft does not put phone numbers in warnings or charge for removing threats through pop-ups. Close the window, do not call, and follow the steps to find and uninstall the program behind it.
I let a technician connect to my PC because of MacClean. Is it safe now?
Not until you check. While connected, the caller could install other programs, create a user account or look at saved passwords. Disconnect from the internet, uninstall the remote access program and anything else installed during the call, and run a full scan and the Microsoft Defender offline scan.
From another device, change your e-mail and banking passwords and turn on two-step verification. If the caller opened your online banking, call the bank today. A reset of Windows is the safest option if you cannot tell what was done.
Should I reset my PC because of MacClean?
Only if the signs point to deeper access. Reset when you see the Windows Security detection PUA:Win32/Presenoker again after removal, when Windows Security cannot start or update, when remote access tools you did not install keep appearing, or when you simply cannot trust the PC any more.
Otherwise, the plan in this guide plus an offline scan is enough. If you do reset, choose Remove everything and Cloud download for a fresh copy of Windows, restore only documents and photos, and reinstall programs from their official sites. Change important passwords from the clean system afterwards.
What if I paid MacClean?
Contact your bank or card issuer the same day, explain that the payment went to a fake security program and ask for a chargeback. Keep screenshots of the Windows Security detection PUA:Win32/Presenoker, the payment receipt and any e-mails.
If you gave card details in the program, ask the bank to block and replace the card. Then uninstall the program and run a full scan in Windows Security. If you also called a number and let someone connect to your PC, uninstall the remote-access tool they used and change your passwords from another device.
Will Fortect remove MacClean?
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds on your Mac before you decide anything.
For MacClean, follow the plan on this page as well: removing a launch item or an app is done in macOS itself, and a scanner cannot undo what was typed or entered on the infected Mac, such as saved passwords that were copied.
Change your passwords from another device first, and if the page tells you to erase the Mac, a scan is not a substitute. The free scan costs nothing and the full-featured product needs a license.
Sources
- Wikipedia: Ad-tracking (read October 6, 2026)
- Virustotal: MacClean.app.zip detection rate (read October 6, 2026)
- Lesvirurs: Lesvirus (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)