
Pcprimedefense.com e-mail scam: how to spot it and what to do
Pcprimedefense.com tricks users by using bogus messages that are designed to scare them. Some users end up on this website because they have adware infection, but infected links or automatic redirect scripts on other websites are a more probable cause.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Do it yourself · free Remove Pcprimedefense.com e-mail scam yourself 4 steps, about 12 minutes, no software needed.
Start the steps
Pcprimedefense.com e-mail scam: summary
| Distribution | Compromised websites, pop-up ads, potentially unwanted applications |
|---|---|
| Damage | Installation of PUPs or malware, sensitive information disclosure, financial losses |
| Name | Pcprimedefense.com |
| Type | Scam, phishing, redirect, adware |
| Operation | The fake message claims that the system has been infected with malware, which needs to be removed with the promoted software |
| Symptoms | A phishing e-mail asking you to sign in |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 7 more facts
| Evidence | 4 write-ups by security sites; details still limited |
|---|---|
| Arrives as | |
| Pretends to be | A well-known company |
| Claim | Your account needs urgent attention |
| Asks for | Your password |
| First seen | 16 November 2022 |
| Facts checked | 7 October 2026 |
What the Pcprimedefense.com e-mail scam e-mail looks like
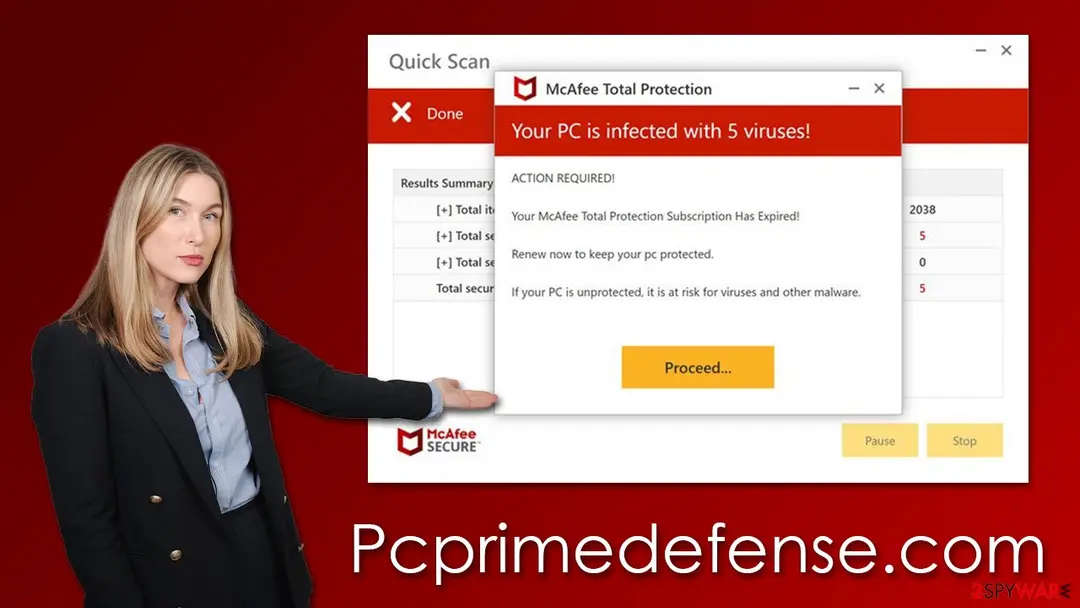
Your PC is infected with 5 viruses!
ACTION REQUIRED
Your McAfeee Subscription Has Expired!
Renew now to keep your PC protected.
If your PC is unprotected, it is at risk for viruses and other malware.
How to tell the Pcprimedefense.com e-mail scam e-mail is fake
From our report of Nov 2022 · not reviewed since
Pcprimedefense.com is a misleading website designed by cybercriminals for profits
Pcprimedefense.com tricks users by using bogus messages that are designed to scare them.
Some users end up on this website because they have adware infection, but infected links or automatic redirect scripts on other websites are a more probable cause. Users who land on the site never anticipate seeing an unexpected system scan, making the scheme successful for those running it.
These results claim that several infections were found and that the subscription to the security software had expired. Users are enticed to click on a link where they can buy a complete license after seeing these fake results.
The scam website Pcprimedefense.com has no direct connections with the security vendor it's referencing; its only purpose is to generate income through clicks on affiliate links. Additionally, since you can never be sure if a redirect to a security software download site is legitimate, you could end up installing malware onto your system instead of a genuine program.
Our advice is to steer clear of any requests to download anything and instead follow our detailed guide. If you suspect your computer might be infected or have installed something, take a look at the information provided below to see what steps come next to ensure your personal safety and computer security.
From our report of Nov 2022 · not reviewed since
More from our earlier report on Pcprimedefense.com
- The scam involves users being shown the supposed findings of a McAfee virus scan.
- Users are alarmed to see a McAfee scan conducted as soon as they arrive on the fraudulent Pcprimedefense.com page.
Is Pcprimedefense.com e-mail scam dangerous? What the senders want
From our report of Nov 2022 · not reviewed since
Tricks used to fool users
Just a few moments later, they are made aware of the scan results that always claim several virus infections.
Here is the full message users can expect to see:
Scammers often target individuals who are not well-versed in internet scams, as they are more likely to fall for them. These individuals might see a message from a "reputable" security vendor and think that their system truly has viruses and that action needs to be taken immediately. Of course, at this point, people are informed that their subscription has expired and needs to be renewed.
As mentioned, none of the legitimate security providers would fearmonger people into purchasing software. It is important to understand that the whole scan process displayed on Pcprimedefense.com is only mimicked - all the logos and names are fabricated to frighten visitors. Only reputable anti-malware installed on the system can tell whether it is infected unless there is already a backdoor installed on the device.
From our report of Nov 2022 · not reviewed since
Check your system for infections
There is no doubt about the fact that all the scan results shown by the bogus website are fake.
However, you should not exclude the probability of the infection completely. Adware is a virus that invades your system and browser, filling it with ads. You may have adware installed if you've been coming across websites like Pcprimedefense.com more frequently and your browser can't seem to get rid of the ads.
However, manual steps can still be effective if you're dealing with a potentially unwanted program. Remember that malicious programs may use some obfuscation techniques to make them difficult to remove.
First off, please remove extensions from the browser that you find suspicious:
MS Edge (Chromium)
Unwanted programs can do more harm than browser extensions, so it is crucial to get rid of them.
While moving apps into Trash is how you delete most normal applications, adware tends to create additional files for persistence. Thus, you should look for .plist and other files that could be related to the virus. If you are not sure, skip this step entirely.
To fully remove an unwanted app, you need to access Application Support, LaunchAgents, and LaunchDaemons folders and delete relevant files:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all the suspicious plugins that might be related to the unwanted program by clicking Remove.
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the window's top-right).
- Select Add-ons.
- In here, select the unwanted plugin and click Remove.
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
- Click Safari > Preferences...
- In the new window, pick Extensions.
- Select the unwanted extension and select Uninstall.
- Open Internet Explorer, click on the Gear icon (IE menu) on the top-right corner of the browser
- Pick Manage Add-ons.
- You will see a Manage Add-ons window. Here, look for suspicious plugins. Click on these entries and select Disable.
- Enter Control Panel into the Windows search box and hit Enter or click on the search result.
- Under Programs, select Uninstall a program.
- From the list, find the entry of the suspicious program.
- Right-click on the application and select Uninstall.
- If User Account Control shows up, click Yes.
- Wait till the uninstallation process is complete and click OK.
- From the menu bar, select Go > Applications.
- In the Applications folder, look for all related entries.
- Click on the app and drag it to Trash (or right-click and pick Move to Trash)
- Select Go > Go to Folder.
- Enter /Library/Application Support and click Go or press Enter.
- In the Application Support folder, look for any dubious entries and then delete them.
- Now enter /Library/LaunchAgents and /Library/LaunchDaemons folders the same way and terminate all the related .plist files.
What to do after the Pcprimedefense.com e-mail
If you only received the message and clicked nothing, step 3 is all you need.
If you clicked the link or typed anything on the page it opened, do every step, starting with the password.
Step 1: Change the password you typed on the fake page
If you entered a password after clicking the link in the Pcprimedefense.com message, treat that account as known to the sender.
Open the provider's real site by typing its address yourself, not through any link in the e-mail, and change the password there. Choose a new one you have never used before, and change it on every other account that shared the old one.
Then use the option to sign out of all other sessions or devices, if the provider has one. This works the same in any browser on Windows 11 and Windows 10.
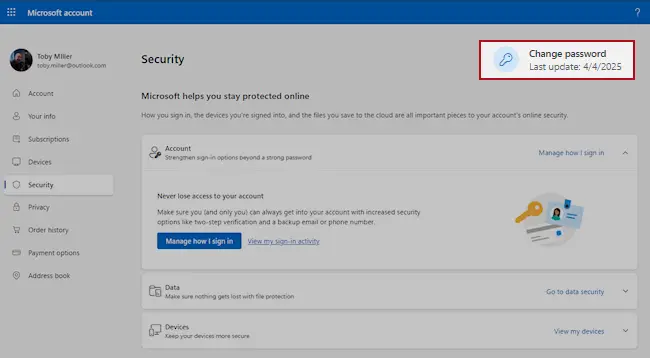
Microsoft account, Security page (account.microsoft.com/security): Change password. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Turn on two-step verification
Two-step verification asks for a code from your phone or an authenticator app whenever someone signs in from a new device. A stolen password alone is then not enough to open the mailbox.
Turn it on in the security settings of the e-mail account first, then for the bank, shop and social accounts that send their reset links to that address.
While you are there, check the recovery e-mail and phone number and the forwarding rules, which attackers sometimes change to keep access. The settings pages look the same on Windows 11 and Windows 10.
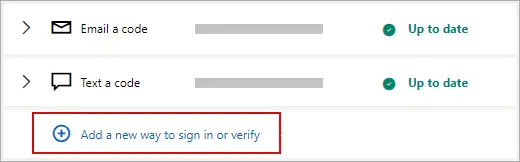
Microsoft account: Manage how I sign in, where two-step verification and the sign-in methods are. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Report the e-mail and delete it
Report the message instead of only deleting it. In Outlook choose Report > Report phishing, in Gmail the three-dot menu > Report phishing; the provider then blocks the same message for other people.
Do not reply and do not click anything else in it. On a work account, forward it to your IT team as an attachment first. Web mail and the mail apps on Windows 11 and Windows 10 offer the same options.
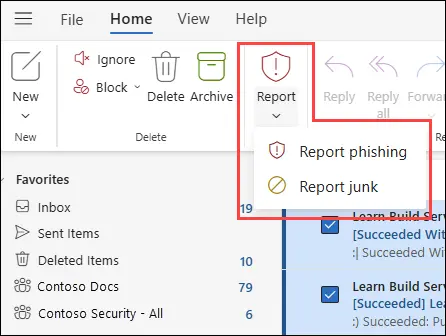
New Outlook for Windows and Outlook on the web: Report > Report phishing. Full procedure with screenshots: Report a phishing e-mail
Step 4: Scan the PC if you opened a file from the message
A page that only asked for a password installs nothing, so most readers can skip this step.
If the Pcprimedefense.com e-mail or the page it opened made you download or open a file, delete it and run a full scan, then a Microsoft Defender Offline scan.
In Windows 11 and Windows 10 open Windows Security > Virus & threat protection > Scan options, select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts and the scan takes about 15 minutes, so save your work first.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
From our report of Nov 2022 · not reviewed since
Get rid of push notifications
In addition to displaying a fake virus infection message, users are offered the option to enable push notifications upon entering the website.
If you accidentally hit the "Allow" button in the notification box, it would result in receiving unsolicited push notifications at random intervals that bring unwanted and harmful links.
While anti-malware scans can easily take care of viruses and can ensure that all leftover components are removed from the device, stopping push notifications is only possible after accessing browser settings.
MS Edge (Chromium):
- Open the Google Chrome browser and go to Menu > Settings.
- Locate the Privacy and security section and pick Site Settings > Notifications.
- Look at the Allow section and look for a suspicious URL.
- Click the three vertical dots next to it and pick Block. This should remove unwanted notifications from Google Chrome.
- Open Mozilla Firefox and go to Menu > Options.
- Click on Privacy & Security section.
- Under Permissions, you should be able to see Notifications. Click the Settings button next to it.
- In the Settings – Notification Permissions window, click on the drop-down menu by the URL in question.
- Select Block and then click on Save Changes. This should remove unwanted notifications from Mozilla Firefox.
- Open Microsoft Edge, and go to Settings.
- Select Site permissions.
- Go to Notifications on the right.
- Under Allow, you will find the unwanted entry.
- Click on More actions and select Block.
- Click on Safari > Preferences...
- Go to the Websites tab and, under General, select Notifications.
- Select the web address in question, click the drop-down menu and select Deny.
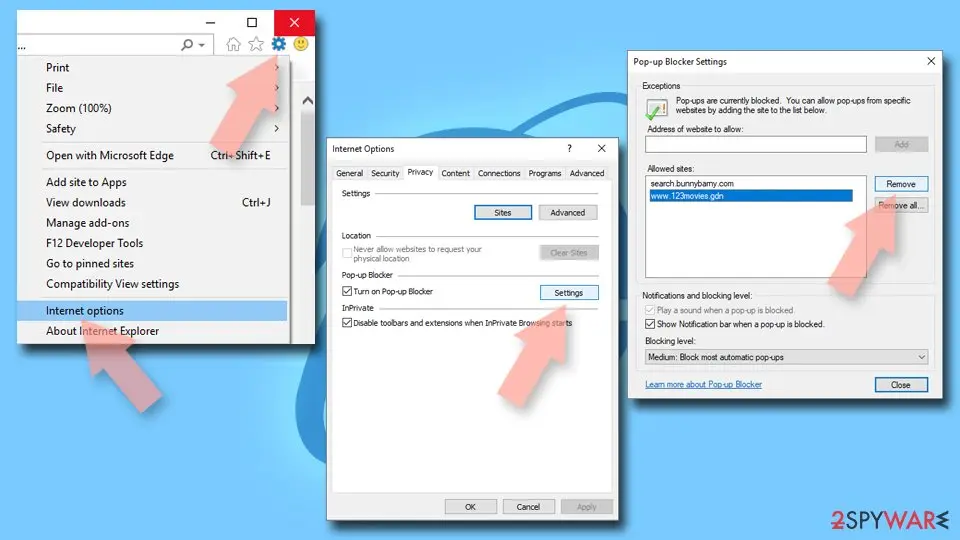
- Open Internet Explorer, and click on the Gear icon at the top-right of the window.
- Select Internet options and go to the Privacy tab.
- In the Pop-up Blocker section, click on Settings.
- Locate web address in question under Allowed sites and pick Remove.
Questions about Pcprimedefense.com e-mail scam
Does getting "Your PC is infected with 5 viruses!" mean my account was compromised?
Not by itself. Phishing waves are sent to long lists of addresses collected from old breaches, websites and guessing, and the sender does not know whether you even have the account the message mentions. Getting "Your PC is infected with 5 viruses!" only means your address is on such a list.
It becomes a problem if you sign in through the link. To be sure, open the real service from a bookmark and check recent activity and security alerts. If you see nothing unusual and you did not type your password into the fake page, your account is fine.
The "Your PC is infected with 5 viruses!" page asked for my code too. Is two-step verification enough?
Not when you typed the code yourself. Some phishing pages pass your password and the one-time code to the real site in real time, which lets the attacker sign in once. Change the password immediately, then sign out of all sessions so the stolen session ends.
Check the account's security page for new devices, app passwords and recovery details, and remove anything you did not add. A passkey or a hardware key is the strongest protection against this trick, because it cannot be typed into a fake page. Keep the e-mail "Your PC is infected with 5 viruses!" for your report, then delete it.
Is Pcprimedefense.com really from a well-known company?
No. It is sent by scammers who copy the name and look of a well-known company. The sender address and the links do not belong to it, and the message asks for your password, which a real company does not request through an unexpected message.
If you want to be sure about your account, open the website or app of a well-known company the way you normally do, not through the message, and look for notices there. Then delete the message and report it as phishing. If you already followed its instructions, use the steps in this guide for your case.
Is it true that your account needs urgent attention?
No. The claim that your account needs urgent attention is the hook of Pcprimedefense.com, invented to give you a reason to act quickly. Scammers pick a story that could plausibly apply to many people, so it may feel relevant to you, but nothing in the message is based on your real accounts or devices.
If the claim concerns a service you use, check it there directly, by opening the website or app yourself. You will find no such problem. Then delete the message and report it as phishing.
What happens if I do what Pcprimedefense.com asks?
The scammers get your password, and they use it quickly. Passwords are tried on the real service within minutes, cards are charged or added to phone wallets, remote access is used to open your bank, and crypto is moved on at once.
Documents surface later as accounts in your name. If you already did what the message asked, do not wait to see what happens; follow the steps in this guide for your case today. Speed matters more than anything else here.
Will a well-known company refund me if I fell for Pcprimedefense.com?
A well-known company did not send the message and is not responsible for it, so a refund usually comes from your bank or card issuer, not from the brand. Call the bank first if you paid.
It still helps to tell the real company: they can secure your account, add notes for their fraud team and take down pages that use their name. Contact them through their official website or app only, never through the message or a search ad. Keep the message as evidence.
Can just reading Pcprimedefense.com harm my PC?
No. Reading the e-mail does nothing to the PC. The risk lies in what the message wants you to do: your password. Every one of those needs an action from you, such as a click, a typed password, a payment or a call.
If you stopped at reading, you are fine. Delete it and report it. If you are unsure whether you clicked something, check your browser history for the time you read the message, and act on what you find there.
Does Pcprimedefense.com mean my PC is hacked?
Not necessarily. The sign reported, an e-mail with the subject "Your PC is infected with 5 viruses!", is usually caused by a password that leaked or was phished, not by malware on the PC.
Passwords leak in breaches of other websites and are tried on many services. Still, rule out the PC:
- run a full scan in Windows Security
- check Installed apps for anything you do not recognise
- look at the browser's extensions
If all is clean, the problem lies with the account, and changing the password with two-step verification turned on is the fix.
How quickly do scammers use a phished password?
Often within minutes. Phishing kits send each password to the operators as soon as it is typed, and many test it automatically on the real service. Some kits also pass the two-step code through in real time.
That is why the first hour matters: change the password, end all sessions and check that the recovery details are still yours. If nothing has changed by then, you were probably fast enough, but keep watching for login alerts and password-reset e-mails for a few weeks.
Will Fortect remove Pcprimedefense.com?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Pcprimedefense.com, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Techopedia: Affiliate Link (read October 7, 2026)
- Imperva: Backdoor Attack (read October 7, 2026)
- FTC: How to recognize and avoid phishing scams (read October 7, 2026)
- CISA: Recognize and report phishing (read October 7, 2026)
- Microsoft Support: Protect yourself from phishing (read October 7, 2026)