
Program:Win32/Contebrew.A!ml ads: what it is and how to remove it
Program:Win32/Contebrew.A?ml is adware that hijacks browsers and displays unwanted advertisements. The 2021 guide noted this threat was persistent and difficult to remove.
Facts checked October 8, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Programs like Program:Win32/Contebrew.A!ml usually arrive in groups; a free scan lists the companions that are easy to miss.
Do it yourself · free Remove Program:Win32/Contebrew.A!ml ads yourself 4 steps, about 12 minutes, no software needed.
Start the steps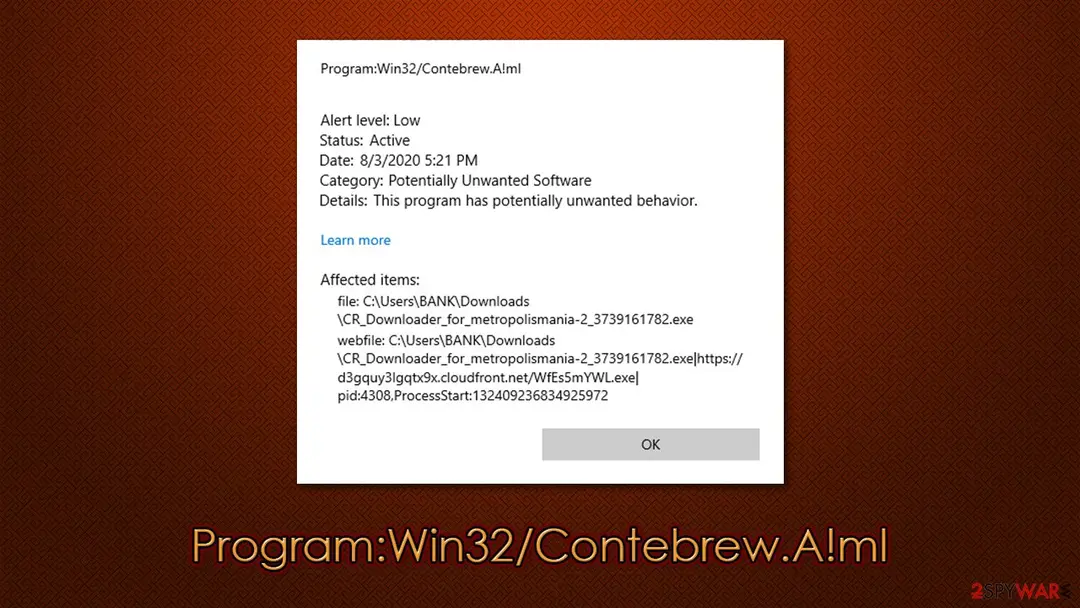
Program:Win32/Contebrew.A!ml ads: summary
| Distribution | Software bundles, deceptive ads, fake Flash Player updates, third-party websites |
|---|---|
| Name | Program:Win32/Contebrew.A!ml |
| Type | Adware, potentially unwanted program |
| Symptoms | Inability to eliminate the potentially unwanted program; unknown browser extension or application installed; intrusive deals, coupons, discounts, offers, and other advertisements; redirects to ad-filled, scam, phishing, and other dangerous websites |
| Dangers | Redirects to malicious websites can result in unwanted site notifications, personal information disclosure to unknown parties, financial losses, installation of other potentially unwanted software or malware |
| Similar | Win32/Bundpil, PUA:Win32/Puwaders.B!ml, VirTool:Win32/DefenderTamperingRestore |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 7 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Damage | Not recorded in the old report |
| Evidence | 4 write-ups by security sites; details still limited |
| Program | Program:Win32/Contebrew.A!ml |
| First seen | 29 December 2020 |
| Microsoft Defender name | Program:Win32/Contebrew.A!ml |
| Facts checked | 5 October 2026 |
Is Program:Win32/Contebrew.A!ml ads dangerous?
What readers reported about Program:Win32/Contebrew.A!ml
Is new Bitdefender 2013 Plus good to protect against FBI virus?. My old desktop was infected with the FBI virus. I threw out the computer and downloaded Bitdefender Antivirus 2013 Plus on my laptop. Do I need to purchase another malware software program to defend against the FBI virus?
How to get rid of IncrediBar in Firefox?. Hello, I have some troubles with Incredibar. It seems there is no an easy way to remove it.. there is no such program in add/remove program list. Can anyone help me to delete Incredibar? I'm using Firefox as a default Browser. thanx in advance Moly
From the comments under our earlier guide; names and contact details removed.
What Conteban.A!ml means and how it differs from Contebrew.A!ml
Conteban.A!ml is a separate Microsoft Defender detection name, usually shown as Trojan:Script/Conteban.A!ml, and it is not the same alert as Program:Win32/Contebrew.A!ml.
Contebrew is filed as a potentially unwanted program on Windows. Conteban is filed as a trojan in a script, which points to a suspicious script file, not to an adware installer. The two names only look alike because both are short labels from the same naming scheme.
Microsoft lists Conteban.A!ml in its Security Intelligence encyclopedia and says Defender detects and removes it, but it publishes no detailed behaviour for this name, according to the Gridinsoft write-up we read.
Pages that promise exact registry keys, payloads or stolen data for Conteban give no evidence for those claims. We found no reliable source for them, so treat any such detail as unproven until Microsoft or a researcher documents it.
If Defender shows Conteban.A!ml, keep the item in quarantine and note the file path it names in Protection history. Delete the download, archive or email attachment it came from if the source was not trusted, update Defender and run a full scan.
If the alert comes back, run Microsoft Defender Offline. Check startup apps, scheduled tasks and browser extensions, and change important passwords from a clean device if you ran a crack or unknown installer.
Do not restore the file only because a forum says every name ending in !ml is a false positive. Our reading is that the suffix marks a detection made by automated analysis, which can be wrong, but the safe test is the source of the file.
If it came from a trusted vendor and you believe Defender is mistaken, submit the file to Microsoft Security Intelligence for review instead of allowing it.
From our report of Dec 2020 · not reviewed since
Program:Win32/Contebrew.A!ml is a detection name for a potentially unwanted program that is trying to break into your device
Program:Win32/Contebrew.A!ml is an adware application that you could have downloaded in a bundle from a suspicious website, or you were tricked into believing that it is useful in the first place.
The threat is typically identified by Windows Defender, although other security apps can use the same name. It belongs to a potentially unwanted program category, which typically represents changes made to Google Chrome, Mozilla Firefox, MS Edge, Safari, or another web browser.
Thus, if the PUP manages to break in, you might see the homepage and new tab address changes, redirects to suspicious websites, and ads showing up during your web browsing sessions, namely popups, banners, deals, coupons, offers, and other intrusive content.
The problem with this potentially unwanted program is that the threat is persistent, and users said they struggled with Program:Win32/Contebrew.A!ml removal. This typically occurs due to a Windows cache bug that can be cleared and the repeated detection terminated for good - check below how.
Adware programs are generally not considered malicious, although some security advocates and researchers claim that some adware might compromise user security and open the system to additional infections. Thus, there is a great need to prevent infiltration of such programs, as they also rarely provide any useful functionality to users in the first place.
Once installed, Program:Win32/Contebrew.A!ml virus focus shifts to delivering intrusive ad campaigns, meaning that those infected would see various ads while browsing the web. Homepage, search provider, and other browser changes can also accompany the unwanted behavior.
Redirects might also occur, landing users on websites that advertise useless software, attempt to extort money with phishing techniques, or include malicious JavaScript that would download and install malware automatically under certain circumstances.
It is also important to note that most potentially unwanted programs such as adware collect a variety of information about users' online activities. With the help of cookies, web beacons, and other tracking technologies, the following data is automatically harvested and later used for marketing purposes:
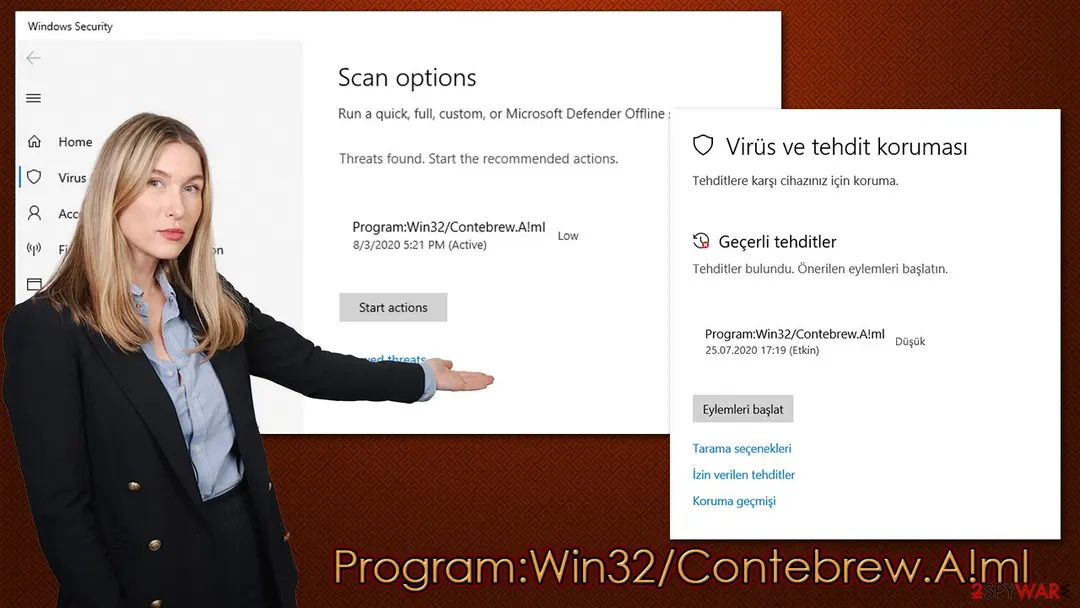
However, if you have your computer equipped with security software such as Windows Defender, it would flag the intrusion as soon as Program:Win32/Contebrew.A!ml would attempt to break in. Unfortunately, users said that the main problem with this detection is that it would not go away and show up regularly, up to a few times a day. They also claimed that they quarantined the threat once it showed up.
There could be a few reasons why this is happening: either there is additional malware installed on the system, Windows Defender can't fully eliminate the PUP or a bug within the Detection history folder.
Thus, you should employ different security software, such as or , and perform a full system scan to remove Program:Win32/Contebrew.A!ml. You could again try to delete the detection history for Windows Defender - you can find more details below.
- IP address
- Internet Service Provider
- Approximate location
- Timestamps
- Links clicked and sites visited
- Search queries
- Technical device data
- Installed apps and extensions, etc.
From our report of Dec 2020 · not reviewed since
Beware of malicious sites when downloading new software
Many people like to download new software - and it's best when it's free.
Unfortunately, third-party software sites serve as a perfect ground for distributing adware and similar unwanted programs, researchers warn. Hence, users who carelessly download apps end up also installing additional components due to a lack of attentiveness. Of course, the distributors of PUPs are also at fault, as they are actively trying to hide promotional offers within the standalone installer.
Thus, you should always be aware that installers could and most commonly do include additional apps within them. You should always pick Advanced/Custom settings instead of recommended ones when prompted and remove all the ticks next to browser extensions, system optimizers, video players, and similar apps.
You should also watch out for fine print text, misleading offers, misplaced buttons, and similar tricks used to mislead users into installing adware or other unwanted software on their machines.
There have been sightings of browser-hijacking and adware apps that come as add-ons for video games. For example, one user claimed that they were struck with an anti-virus popup when they tried downloading a mod (mods are small files that can make significant changes within a game environment) for Minecraft.
While such files are liked by the community, it is crucial to ensure that no unknown websites are used for such a purpose.
From our report of Dec 2020 · not reviewed since
More from our earlier report on Program:Win32/Contebrew.A!ml
- While it is usually easy to uninstall potentially unwanted applications, some threats just don't want to go away - and this is precisely the case.
- In order to get your security software to stop repeatedly detecting this threat, you need to clear the detection history within Windows Defender folder
- Malware or adware infections can diminish the performance of your computer or cause serious stability issues.
Check your browser and PC
If Windows Security shows Program:Win32/Contebrew.A!ml, it has found Program:Win32/Contebrew.A!ml or a file that belongs to it.
Write the name down before you click Remove: it is the most useful search term later, and you will need it if you report the incident.
A family name in the label is more informative than a heuristic one. Our page on why one threat has many antivirus names lists the common formats and what each part means.
How to remove Program:Win32/Contebrew.A!ml ads
How to remove the Program:Win32/Contebrew.A!ml extension
Do the browser steps in every browser and profile on the PC, then check Windows for the program that installed the extension.
Step 1: Remove extensions you did not add
In Chrome open
chrome://extensions, in Edgeedge://extensions, and in Firefox the menu > Extensions and themes.Remove every extension you do not remember adding, especially search, new tab, coupon, PDF, weather or video downloader add-ons. Check every browser and every profile, because each keeps its own list.
If an extension has no Remove button or comes back, a browser policy holds it (see "Managed by your organization" in the procedure below). The pages are the same on Windows 11 and Windows 10.
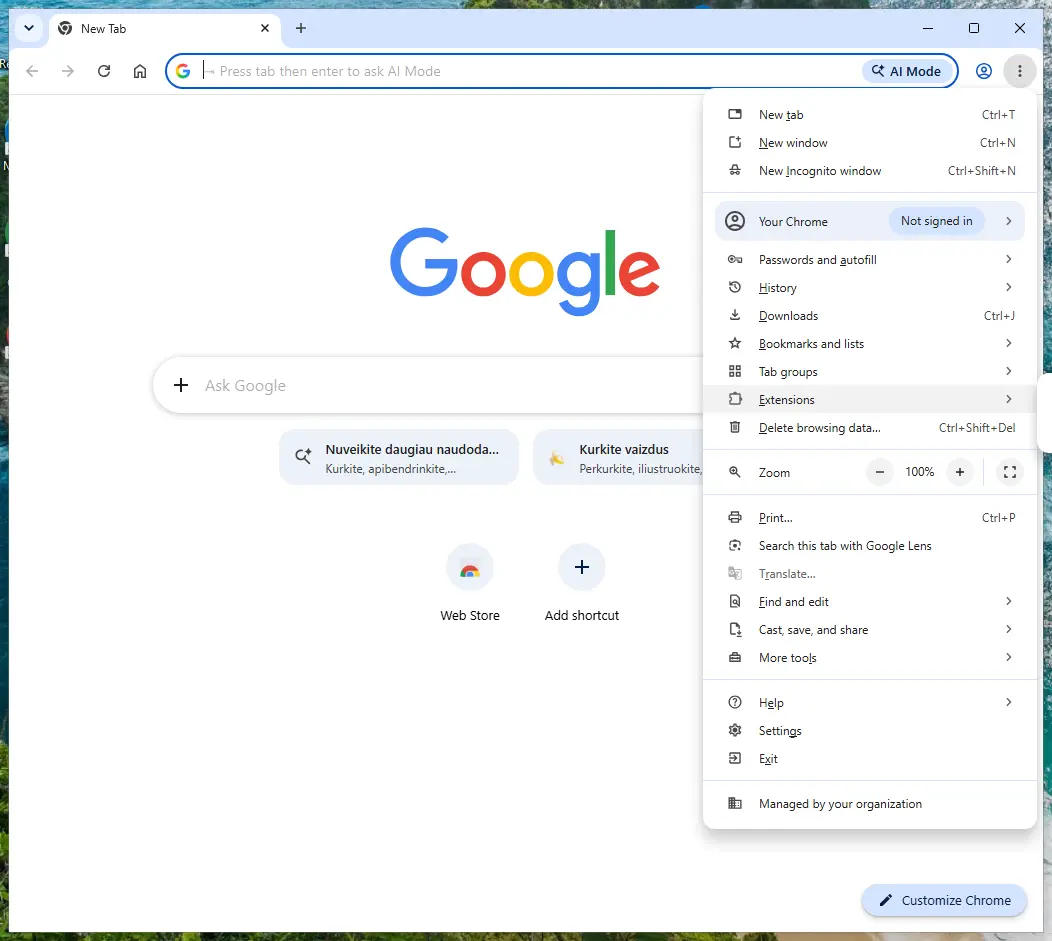
Chrome on Windows 11: More > Extensions > Manage extensions. Full procedure with screenshots: Remove a browser extension
Step 2: Uninstall Program:Win32/Contebrew.A!ml
Program:Win32/Contebrew.A!ml is removed like any other program, from the list of installed apps. In Windows 11 that is Settings > Apps > Installed apps, in Windows 10 Settings > Apps > Apps & features, and in both you can also use Control Panel > Programs and Features.
Select Program:Win32/Contebrew.A!ml, click Uninstall and follow the uninstaller to the end. Then look at the entries just above and below it when the list is sorted by date: bundled programs install at the same minute.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 3: Reset the browser
A reset removes what the steps above could miss:
- changed start pages
- site permissions
- hidden settings
In Chrome open Settings > Reset settings > Restore settings to their original defaults; in Edge Settings > Reset settings; in Firefox Help > More troubleshooting information > Refresh Firefox.
Tip: Bookmarks and saved passwords stay, while extensions are turned off and the search engine and start page return to the defaults.
Reset every browser on the PC, including Edge, which Windows 11 and Windows 10 always have.
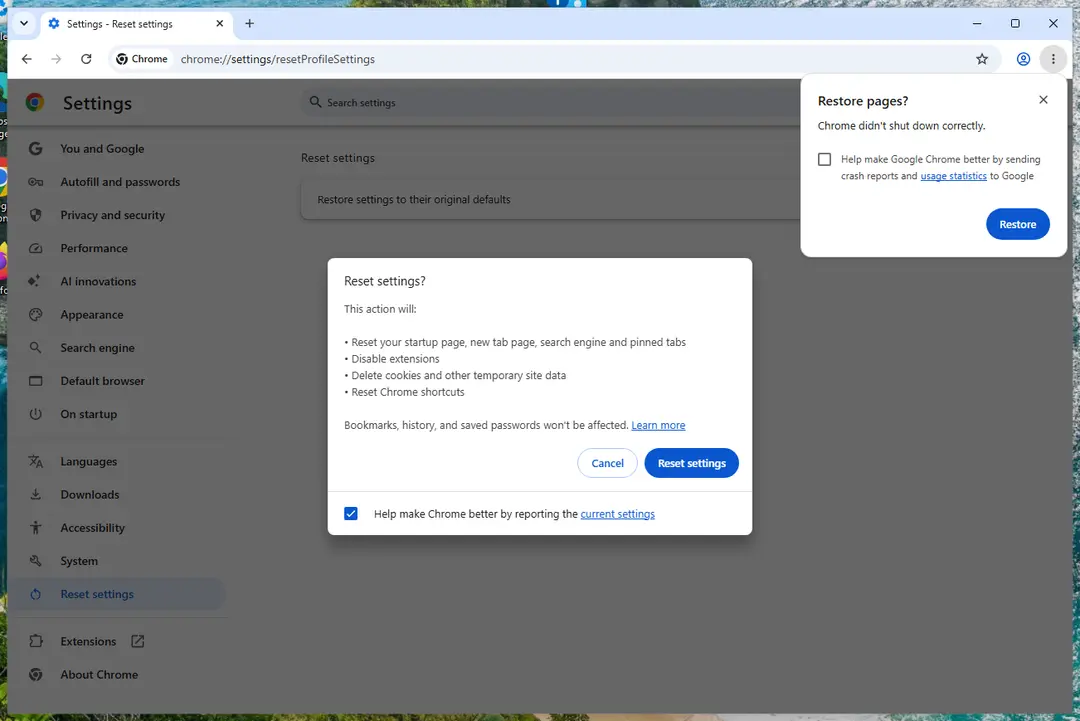
Chrome on Windows 11: Settings > Reset settings. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 4: Scan the PC, then run the offline scan
A scan finds the parts of Program:Win32/Contebrew.A!ml that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
You can uninstall programs from Windows systems by following this guide:
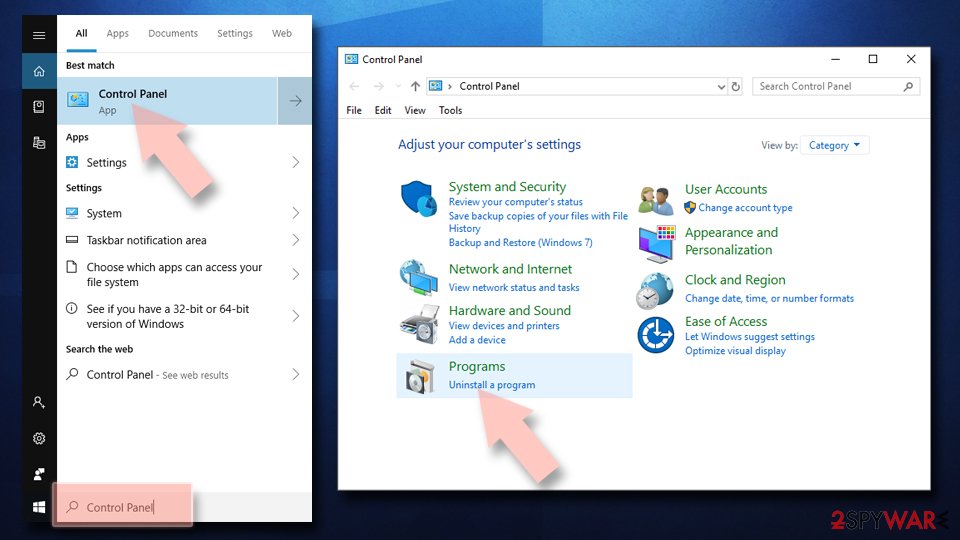
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
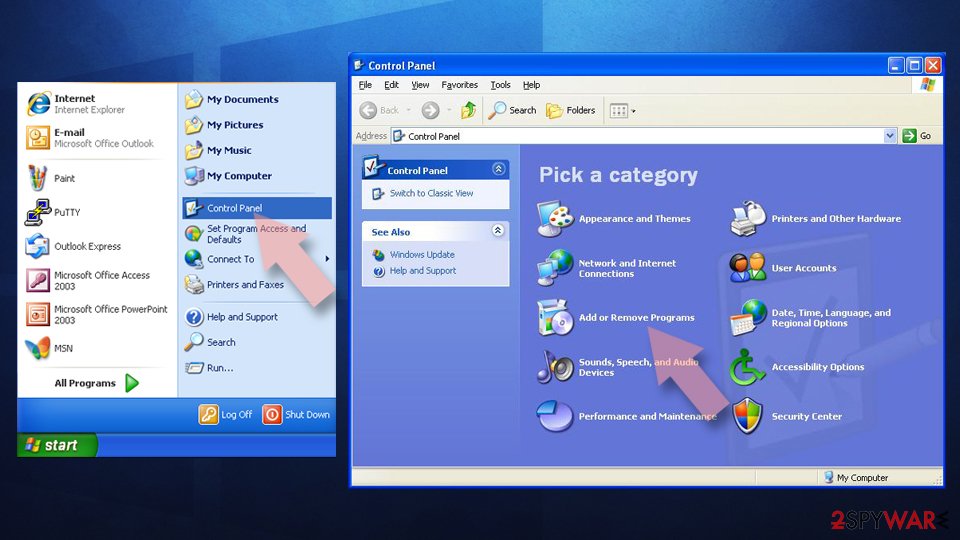
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
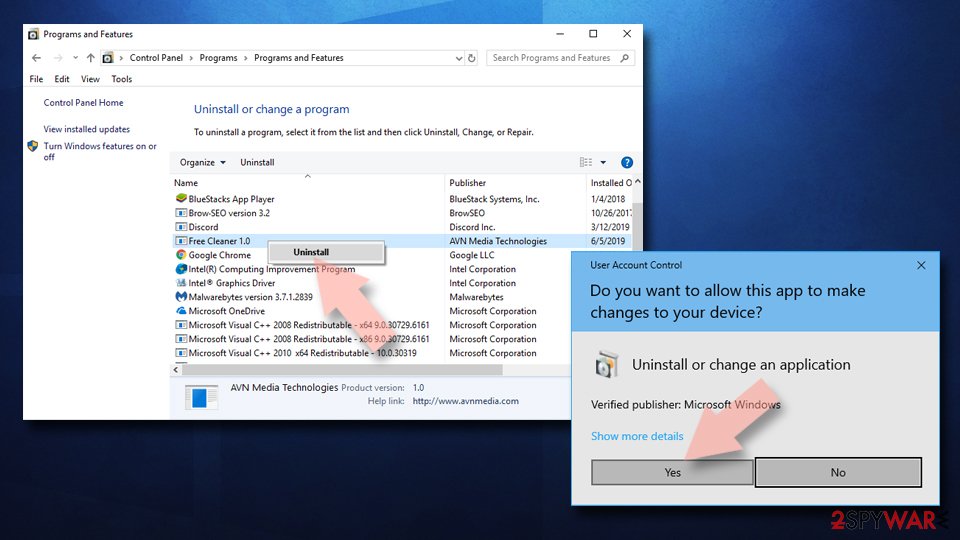
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
To clean Google Chrome, you should access the settings section of the web browser:
Delete malicious extensions from Google Chrome:
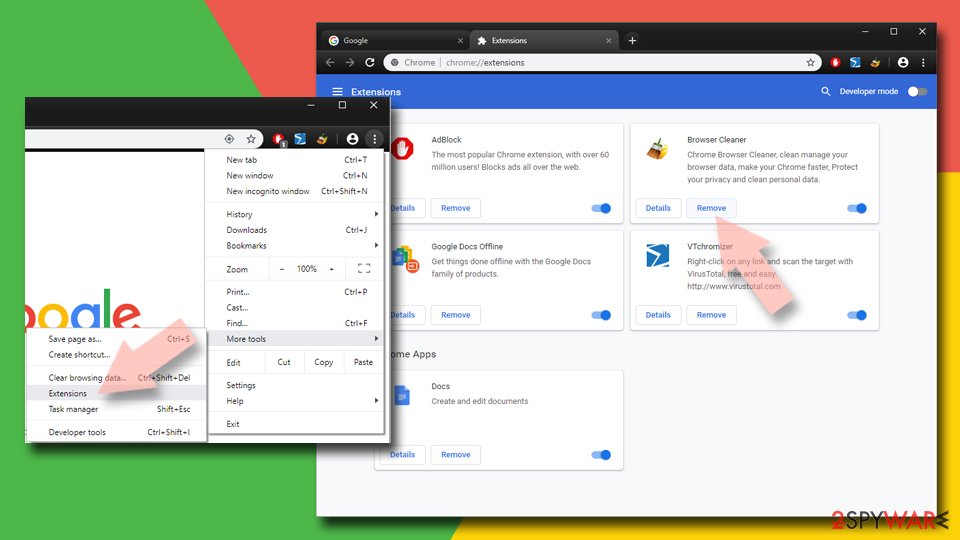
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
Clear cache and web data from Chrome:
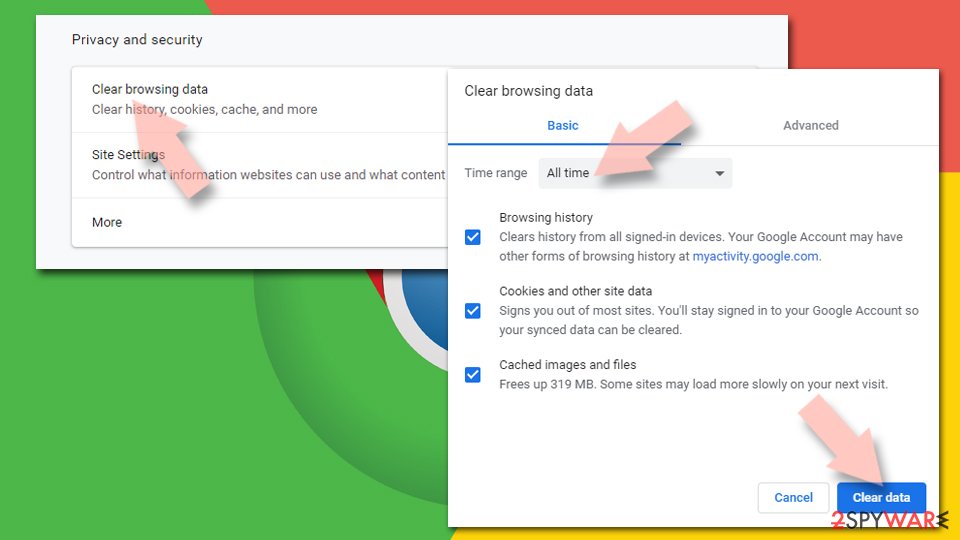
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
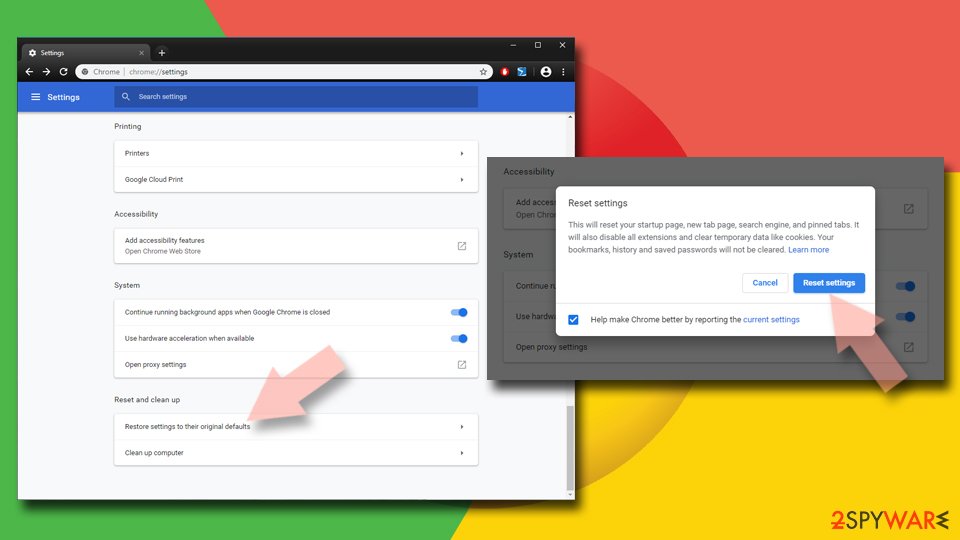
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
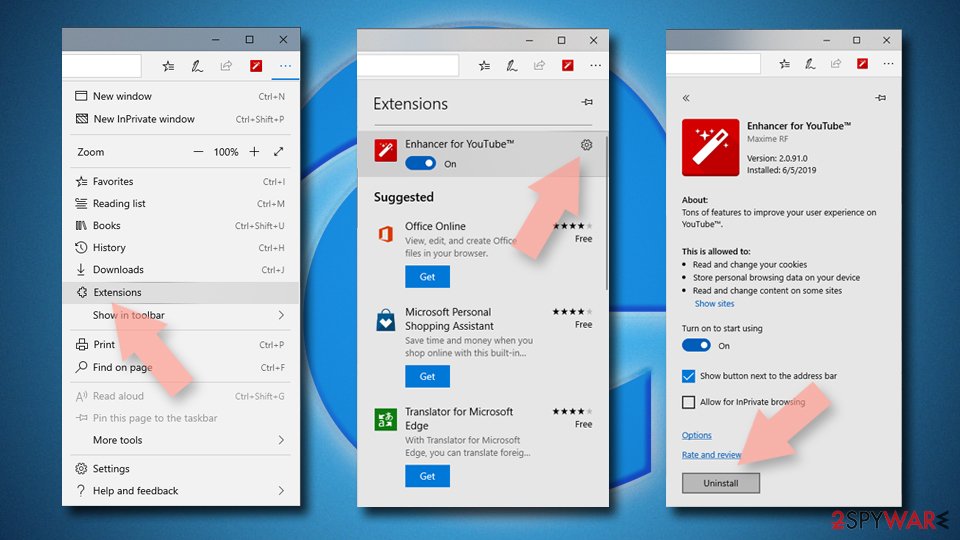
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.
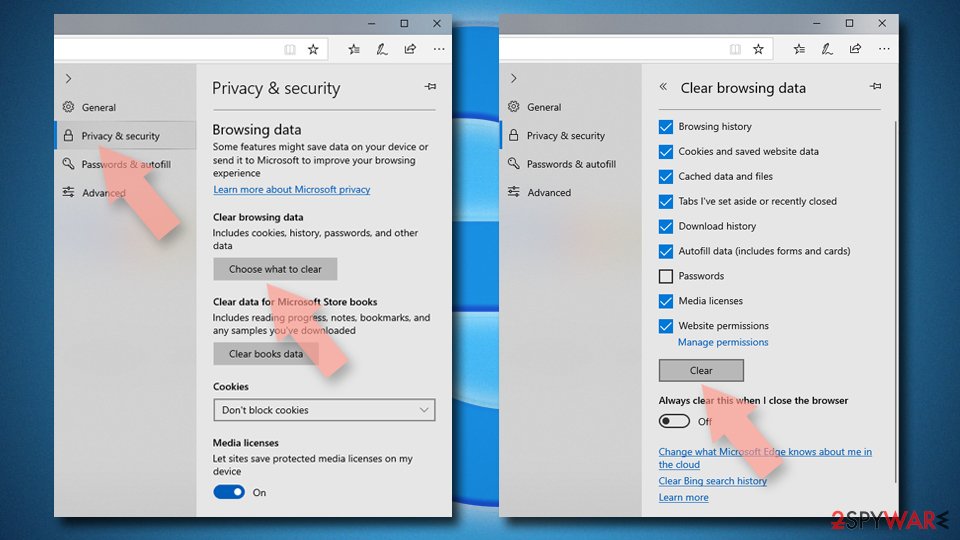
Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.
Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
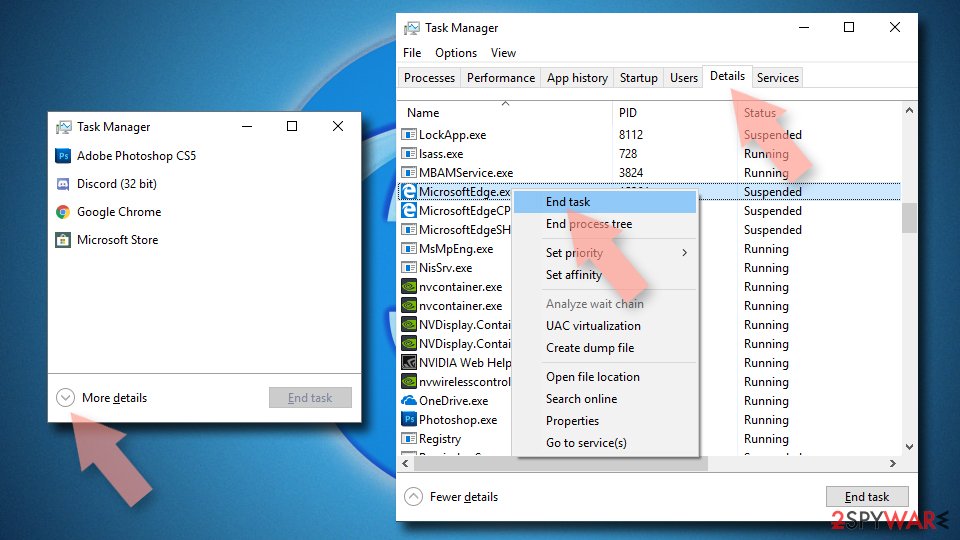
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.
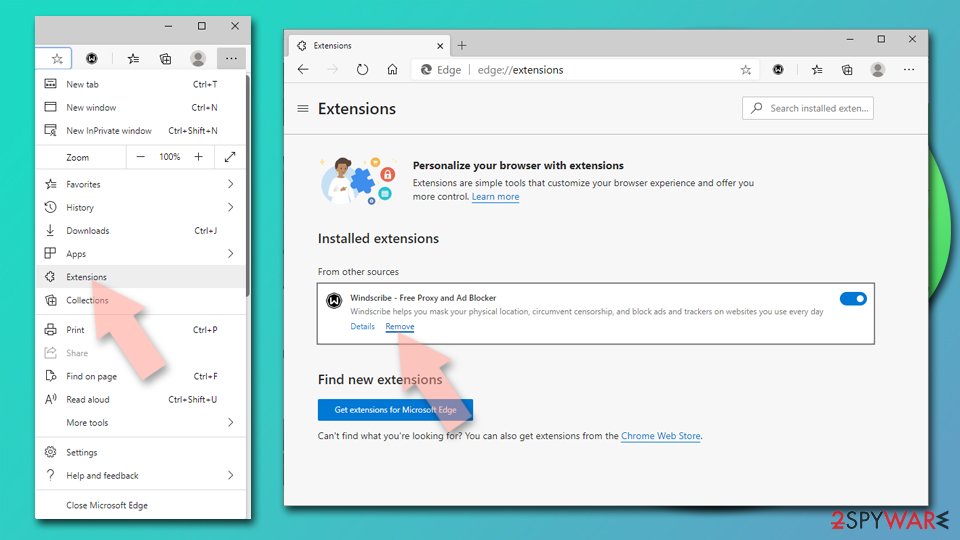
Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
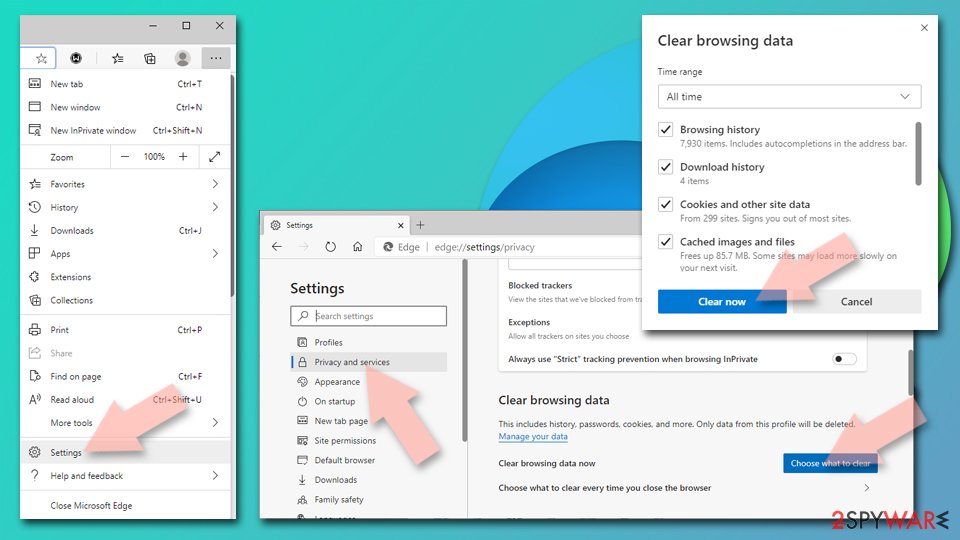
Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
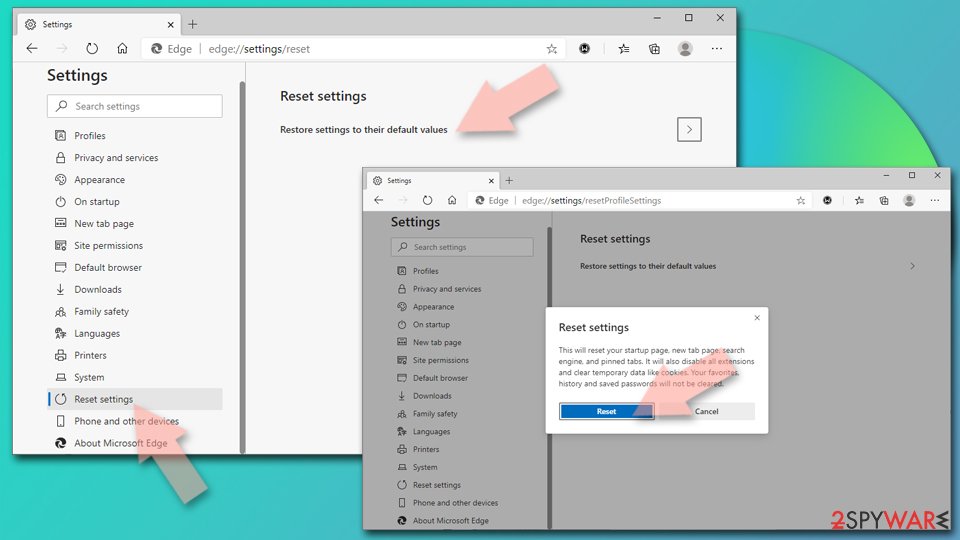
Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.
Remove from Mozilla Firefox (FF)
Look for unwanted browser extensions within Mozilla Firefox browser:
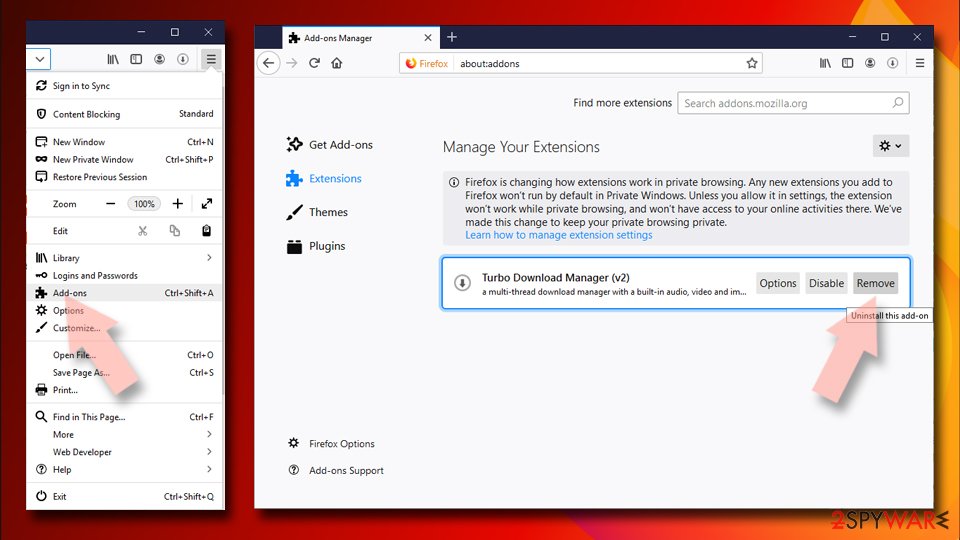
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
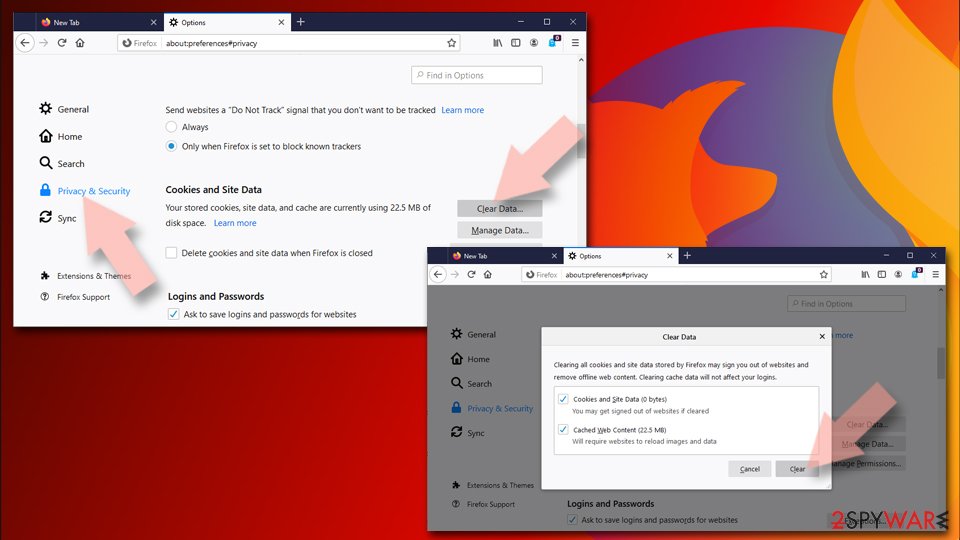
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
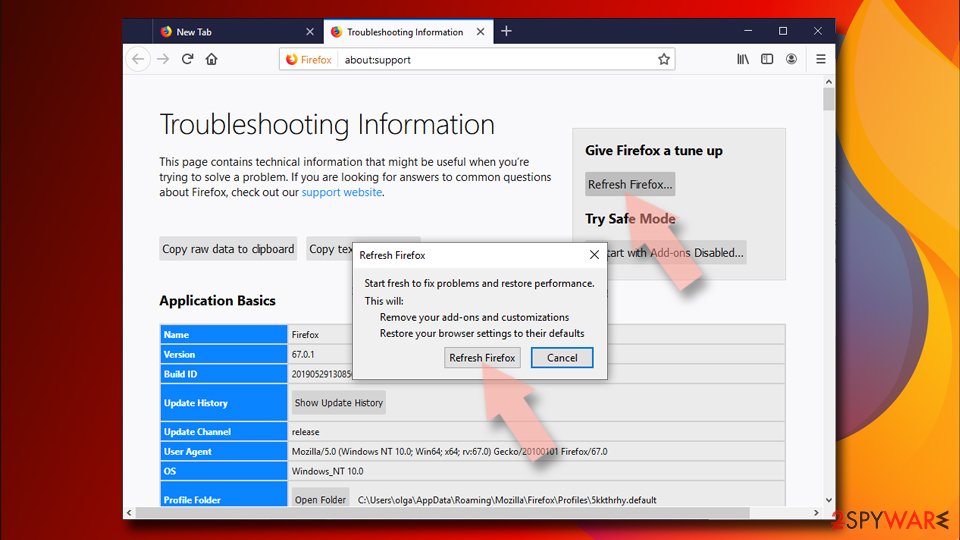
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
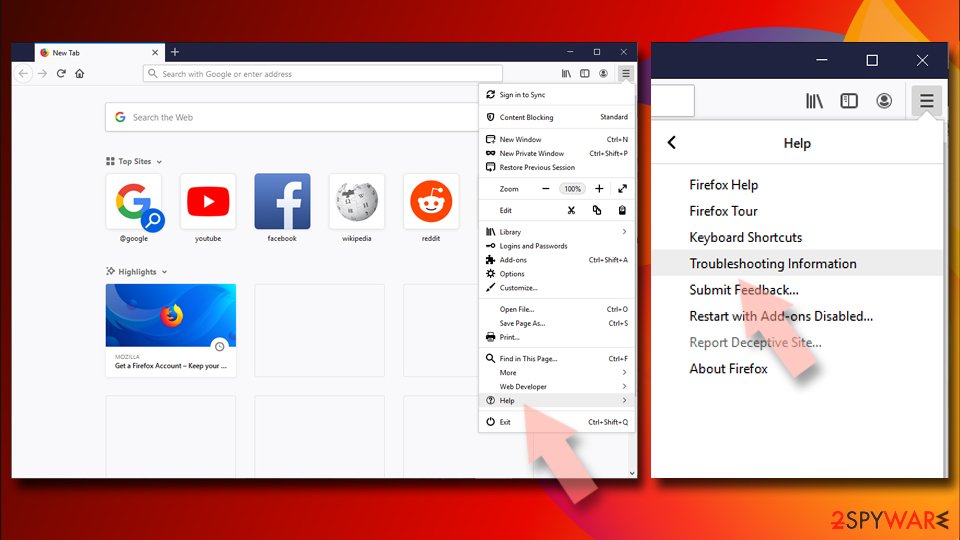
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
Remove dangerous extensions:
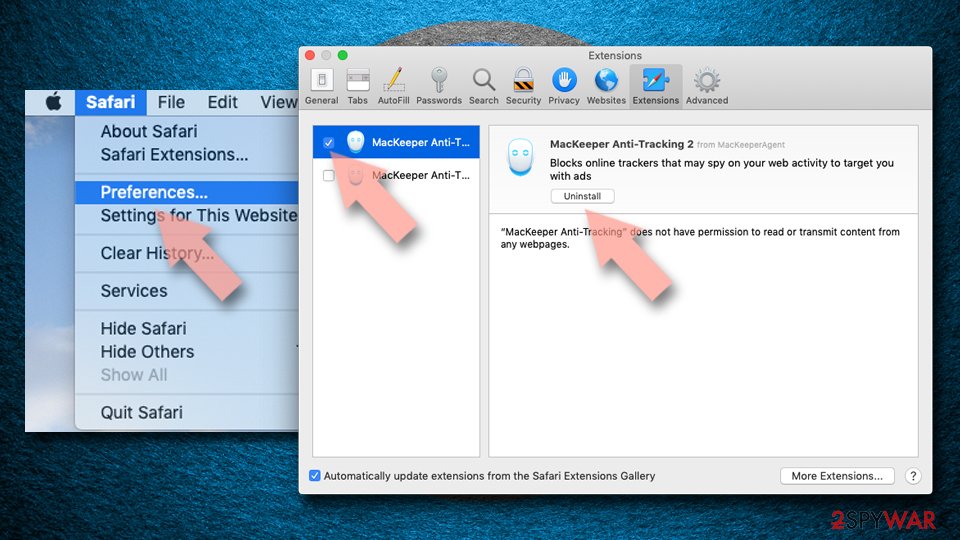
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
Clear history and website data:
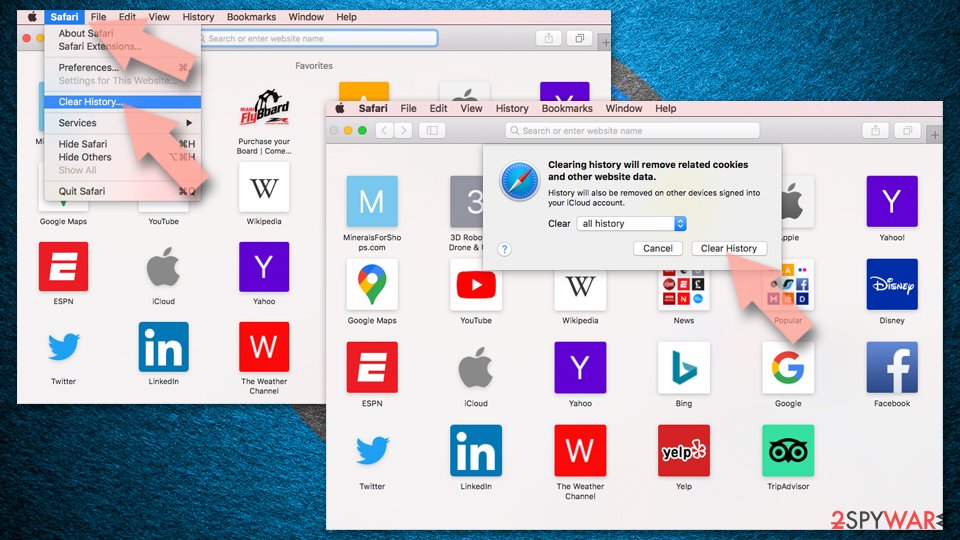
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
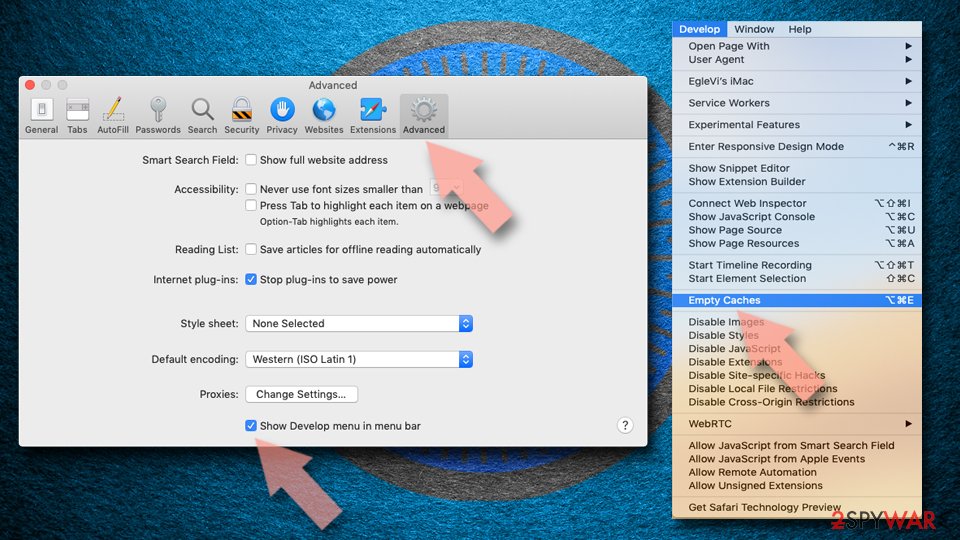
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
macOS users can suffer from the adware as well - here's how to get rid of it:
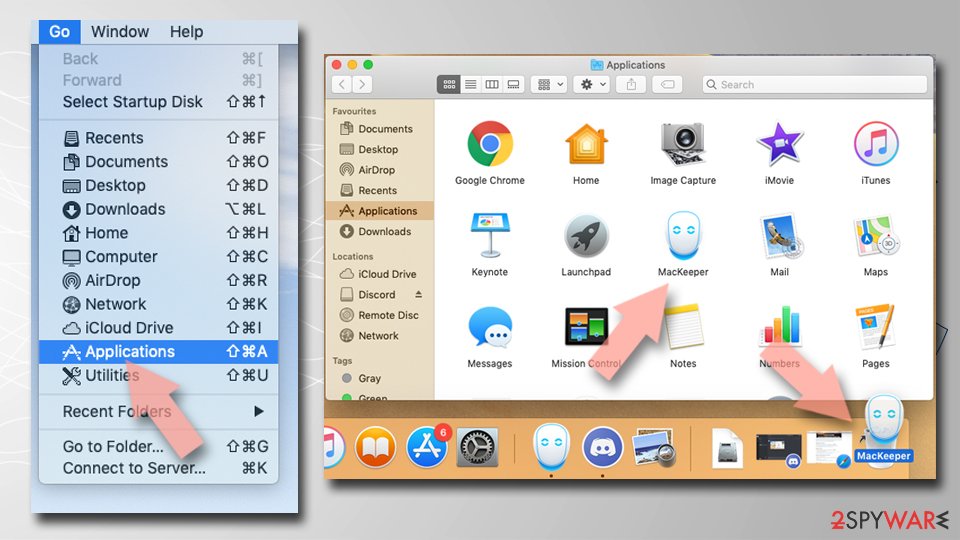
Remove the unwanted application:
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
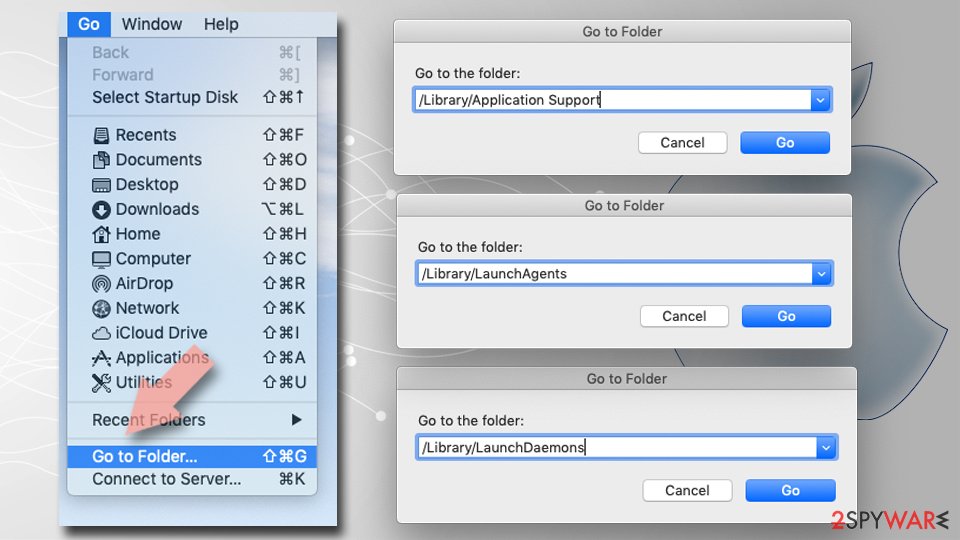
Delete leftover files and folders:
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Choose a proper web browser and improve your safety with a VPN tool
Online spying has got momentum in recent years and people are getting more and more interested in how to protect their privacy online.
One of the basic means to add a layer of security - choose the most private and secure web browser. Although web browsers can't grant full privacy protection and security, some of them are much better at sandboxing, HTTPS upgrading, active content blocking, tracking blocking, phishing protection, and similar privacy-oriented features.
However, if you want true anonymity, we suggest you employ a powerful VPN - it can encrypt all the traffic that comes and goes out of your computer, preventing tracking completely.
Lost your files? Use data recovery software
While some files located on any computer are replaceable or useless, others can be extremely valuable.
Family photos, work documents, school projects - these are types of files that we don't want to lose. Unfortunately, there are many ways how unexpected data loss can occur:
- power cuts
- Blue Screen of Death errors
- hardware failures
- crypto-malware attack
- even accidental deletion
To ensure that all the files remain intact, you should prepare regular data backups. You can choose cloud-based or physical copies you could restore from later in case of a disaster. If your backups were lost as well or you never bothered to prepare any, can be your only hope to retrieve your invaluable files.
From our report of Dec 2020 · not reviewed since
Program:Win32/Contebrew.A!ml removal details
If you are using Windows Defender as your main anti-malware tool, all you have to do is quarantine and remove Program:Win32/Contebrew.A!ml from your system for good.
However, as already mentioned, many users claimed that they could not get rid of the continuous popups despite performing the regular actions that should contain the infection. If that has happened to you, you could check the list of the installed programs on your system, clear your browsers and uninstall unwanted extensions as explained below.
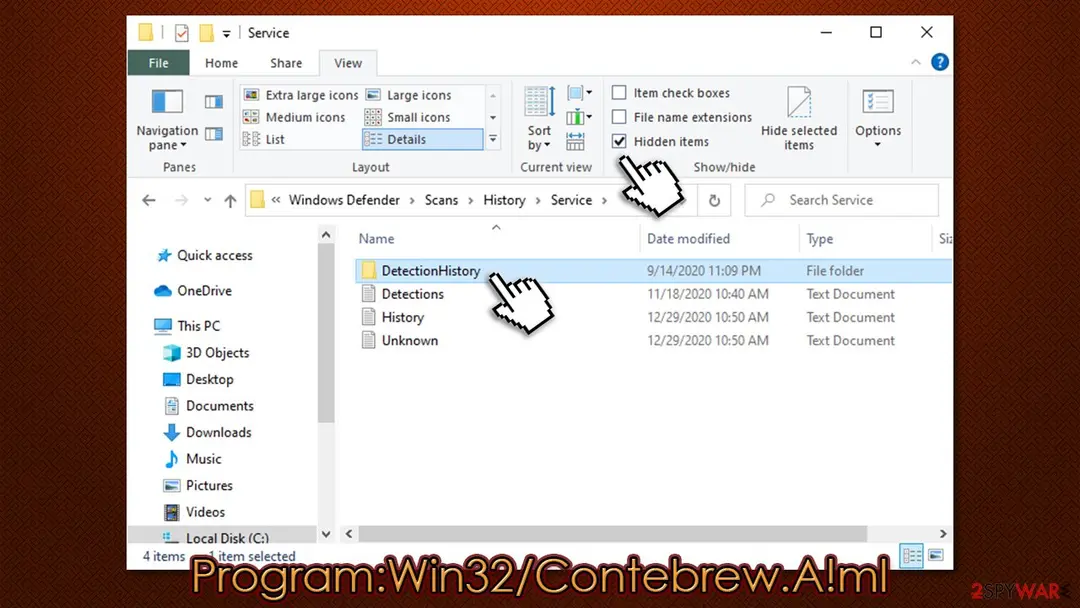
In most cases, a full Program:Win32/Contebrew.A!ml removal can not be achieved due to a bug within the Windows Defender engine. It sometimes detects the same threat repeatedly, even though it claims it has been eliminated for good. In order to bypass this, you should do the following:
- Open File Explorer by pressing Win + E
- Go to View tab at the top and tick the Hidden items option
- Now navigate to C:\ProgramData\Microsoft\Windows Defender\Scans\History\Service folder
- In here, delete the DetectionHistory folder by pressing Shift + Del on your keyboard.
Questions about Program:Win32/Contebrew.A!ml ads
What is Program:Win32/Contebrew.A?ml?
It is a detection name for a potentially unwanted program that changes browser settings without permission. The threat is typically identified by Windows Defender. It belongs to the adware category, which modifies Google Chrome, Mozilla Firefox, MS Edge, Safari, or other browsers.
When installed, users see homepage changes, new tab address modifications, redirects to suspicious websites, and intrusive pop-ups, banners, deals, and coupon advertisements during web browsing sessions.
Is Program:Win32/Contebrew.A?ml a virus?
No. It is classified as potentially unwanted program rather than a true virus. However, it can cause serious issues. While adware programs are generally not considered malicious, security experts note they compromise user security by opening systems to additional infections.
This particular threat is persistent and difficult to remove, often reappearing repeatedly despite users quarantining it in Windows Defender, causing considerable frustration and system performance degradation.
How does Program:Win32/Contebrew.A?ml get on my computer?
You likely downloaded it in a software bundle from a suspicious website or were tricked into believing it was useful software. The infection comes via bundled installers, deceptive advertisements, fake Flash Player updates, and third-party websites offering free tools.
Users often encounter it through software they intentionally downloaded, without realizing additional unwanted components were included in the installation package through deceptive bundling practices.
What damage can Program:Win32/Contebrew.A?ml cause?
It delivers intrusive ad campaigns, hijacks browsers, and collects your online activity data. The threat focuses on changing browser settings and displaying annoying advertisements. With cookies, web beacons, and tracking technologies, it harvests data about links clicked, sites visited, and installed apps.
Most significantly, it can diminish computer performance and cause stability issues. Redirects might lead to phishing websites or sites that automatically download malware through malicious JavaScript.
Why does Windows Defender keep detecting it?
There is a known Windows Defender bug causing repeated detection even after removal. Due to a cache issue within the Detection History folder, Windows Defender repeatedly flags the threat despite claiming successful elimination.
This bug is persistent and users report detecting the virus multiple times daily. Other possibilities include additional malware installed on the system or incomplete elimination of the PUP itself, making thorough remediation necessary to fully resolve the issue.
How do I remove Program:Win32/Contebrew.A?ml?
Use Windows Defender's quarantine feature first, then clear the detection history within the Windows Defender folder to stop repeated alerts. If that fails, employ alternative security software and perform full system scans to find and remove all components.
Clear your browser extensions, homepage, and search settings to their defaults. Check installed programs and uninstall anything suspicious. Then clear Windows cache by navigating to C:\ProgramData\Microsoft\Windows Defender\Scans\History\Service and deleting the DetectionHistory folder.
Should I download antivirus software to remove this?
Microsoft Defender's built-in scans are usually sufficient, but you can use alternative security software if Windows Defender fails. The key is performing a full system scan in Safe Mode with Networking to ensure complete removal.
Do not install multiple antivirus programs simultaneously as they conflict. Focus on running full scans with your chosen tool, then reboot and verify removal. After removing the threat, use offline scans when possible for comprehensive detection that catches hidden components missed by regular scans.
How can I prevent Program:Win32/Contebrew.A?ml in the future?
Always choose Advanced/Custom installation settings instead of Recommended when installing software, and deselect all checkboxes for additional programs. Download only from reputable websites and verify publisher authenticity before installation. Avoid P2P sites, torrent networks, and suspicious download portals.
Watch for misleading offers, fine print, misplaced buttons, and similar tricks used by distributors. Keep your operating system and security software updated. Be cautious with browser extensions and video game mods downloaded from unknown websites, always using verified sources.
Will Fortect remove Program:Win32/Contebrew.A!ml?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Program:Win32/Contebrew.A!ml, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Heimdal Security: (UPDATED 2020) JavaScript Malware – a Growing Trend Explained for Everyday Users (read October 5, 2026)
- Usunwirusa: Usunwirusa (read October 5, 2026)
- Reddit: What is Win32/Contebrew.A!ml? (read October 5, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Gridinsoft: Trojan:Script/Conteban.A!ml: Meaning and Removal Guide (read October 8, 2026)