
VirTool:Win32/DefenderTamperingRestore: what it is and how to remove it
VirTool:Win32/DefenderTamperingRestore is malware designed to disable security software, leaving systems vulnerable to ransomware and trojans. It spreads through email attachments and exploits, creating fake alarm popups to scare users.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
An automatic scan checks installed programs, startup items and browser extensions for anything that came with VirTool:Win32/DefenderTamperingRestore.
Do it yourself · free Remove VirTool:Win32/DefenderTamperingRestore yourself 5 steps, about 15 minutes, no software needed.
Start the steps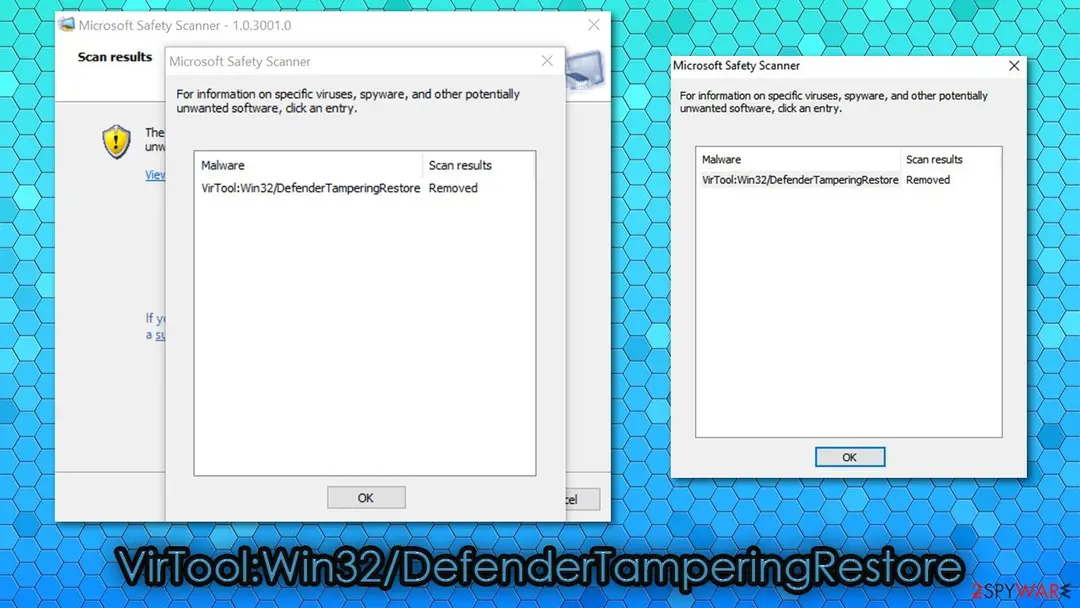
VirTool:Win32/DefenderTamperingRestore: summary
| Distribution | Malware developers typically employ various distribution methods, although the most prevalent one remains spam email links and attachments |
|---|---|
| Damage | Malware can affect the infected users in various ways – it can steal passwords, banking details, take screenshots, install other malware, encrypt files, and much more |
| Name | VirTool:Win32/DefenderTamperingRestore |
| Type | Malware |
| Purpose | To disable Tamper Protection feature of Windows Defender and bypass its security |
| Symptoms | A popup message shows up on the screen; otherwise, malware is programmed to operate without traces (some users may experience crashes, errors, and similar unexpected computer events) |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 5 more facts
| Associated scam | Trojan_Spyware Alert – Error Code #0x268d3 (!x3) |
|---|---|
| Detection names | No Microsoft detection name is known |
| Evidence | 5 write-ups by security sites; details still limited |
| First seen | 30 December 2020 |
| Facts checked | 5 October 2026 |
What VirTool:Win32/DefenderTamperingRestore does on an infected PC
From our report of Dec 2020 · outdated details corrected in October 2026
VirTool:Win32/DefenderTamperingRestore is a type of malware that is programmed to stop your security software from working correctly
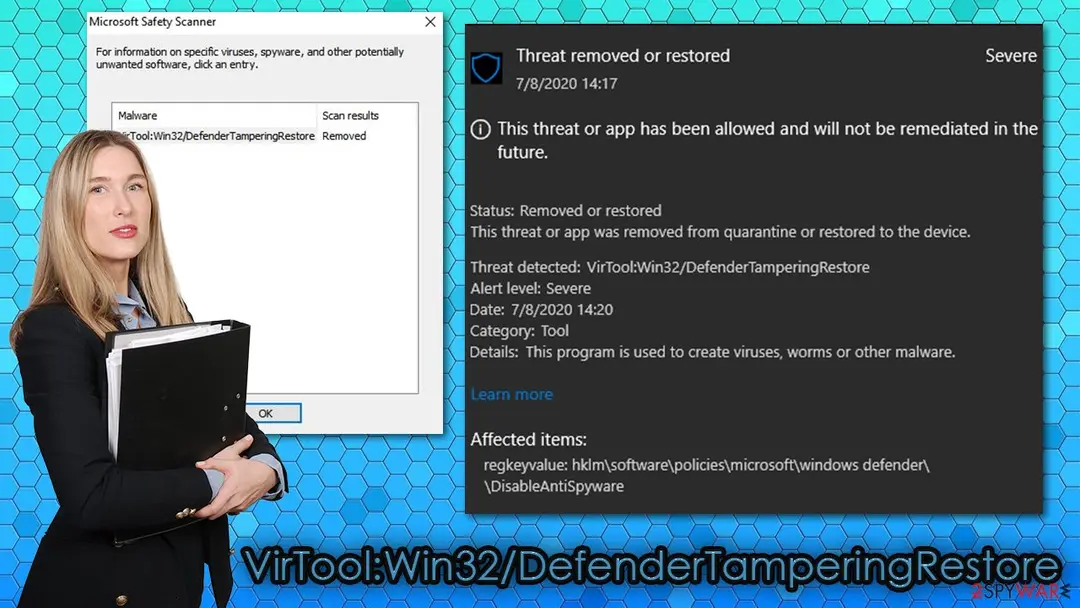
VirTool:Win32/DefenderTamperingRestore is a detection name of a potential threat that is flagged by Windows Defender security software.
The main purpose of the infection is to tamper with the installed anti-malware, weaken computer defenses, and compromise the device. Once the security software has been tampered with, it might not be able to protect users from viruses, trojans, worms, ransomware, and other types of malware.
While the initial goal of this virus is to compromise security software to bypass its defenses, cybercriminals behind it may have various goals. For example, they might place a backdoor on the system in order to compromise it even further, consequently achieving the nefarious goals. Victims of such an attack might suffer from financial losses, additional malware infections, identity theft, and other privacy/security issues.
It has also been widely perceived that the detection might be a false positive when the popup shows up at unexpected times. While it might be the case, it is important to investigate further and check for rootkits, uninstall extensions, reset browser settings, check system files, etc.
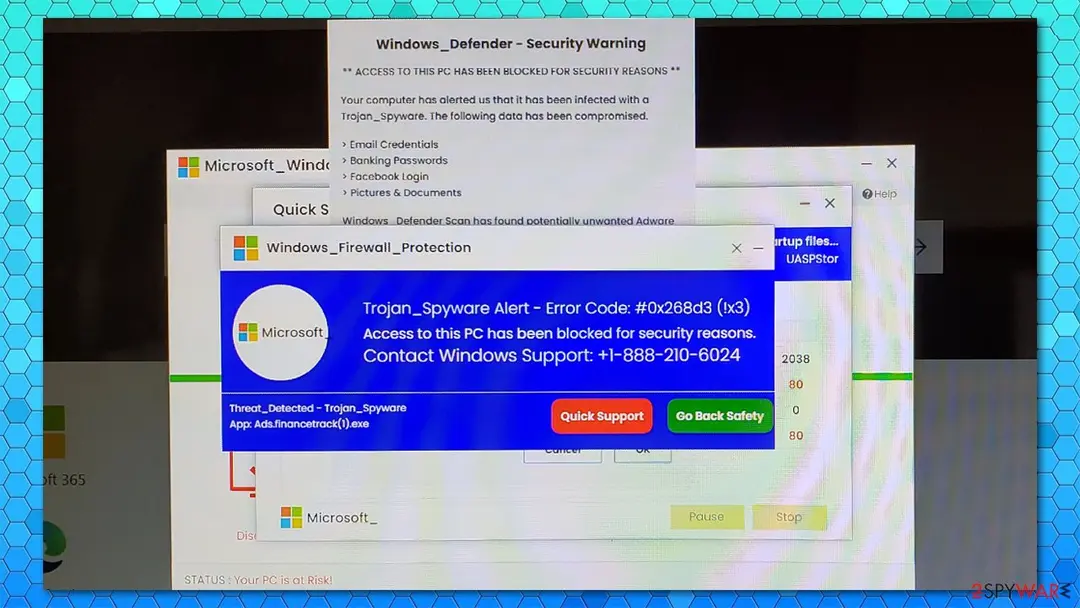
Finally, users who were infected with this malware also reported that their screens had been locked by a scam message which asks users to contact fake Microsoft support.
Several fake warnings popup at the same time and claims that the computer has been locked and that "Trojan_Spyware Alert - Error Code #0x268d3 (!x3)" has been detected on the system. Do not trust these alerts - if you call the provided contact number, you might be scammed into paying money to cybercriminals and infect your PC with more malware.
VirTool:Win32/DefenderTamperingRestore is a rather generic detection that can be encountered at any time. In most genuine cases, however, this occurrence happens when users come in contact with potentially malicious content online. In other words, cybercriminals attempt to spread the infection to as many people as possible, so they often choose multiple attack vectors for higher success chances. Here are a few of them:
Thus, there are several ways how you could come in contact with the VirTool:Win32/DefenderTamperingRestore virus in the first place. Once the contact is made, Windows Defender might or might not detect the intrusion, as the malicious program is designed to disable certain security software defenses (mainly, Tamper Protection feature).
In case the security app does not get compromised completely, it will stop and remove the virus successfully. However, there is also a chance that weakened defenses would prevent a successful elimination. Unfortunately, if case malware manages to break in, it can continue to operate in the background, all while anti-malware is rendered useless.
Users affected by malware can suffer all kinds of damages, as the initial infection can be used only as a pathway for other malware to be infected. For example, ransomware such as Booa, Geno, or Kobos can be deployed in order to lock all personal files on the device and then demand ransom in Bitcoin for their return.
Other invisible infections, such as trojans, may be used to steal all your passwords, bank account details, and other sensitive information, which can be later used for malicious purposes.
It is also important to note that the detection might stem from various settings set by users themselves or programs installed on the PC. For example, in the Windows Registry, the "HKLM\SOFTWARE\Policies\Microsoft\Windows Defender: Restriction" key should never be enabled, as it prevents normal operation of Windows Defender. This setting might also be changed by malware, which, in this case, should be eliminated immediately.
Without a doubt, VirTool:Win32/DefenderTamperingRestore removal should be your top priority. This is why it is important to use additional protection when trying to defend yourself from all types of malware.
- malicious spam email attachments and embedded hyperlinks;
- software vulnerabilities and exploit kits;
- false claims on phishing websites and fake browser or codec updates;
- software cracks and pirated program installers, etc.
From our report of Dec 2020 · outdated details corrected in October 2026
VirTool:Win32/DefenderTamperingRestore infection might start showing "Trojan_Spyware Alert - Error Code #0x268d3 (!x3)" scams
There are plenty of tech support scams all over the internet - malicious actors come up with various bogus claims about users' computer security status and then provide the contact number to call to allegedly resolve the malware infection issues. As it turns out, a VirTool:Win32/DefenderTamperingRestore virus might start showing these types of fake alerts at any time when browsing the web.
While in most cases, suspicious popups are contained within the browser and can be shut down with the tab closure; this time, it is not the case. Users reported that they receive several alerts that try to imitate Windows Defender window, as well as use Windows Firewall name to intimidate users. Here's what one of the alerts claims:
We can assure you that this Trojan_Spyware Alert - Error Code #0x268d3 (!x3) popup has nothing to do with Windows or Microsoft, and all the attributes, such as logos and the identical UI features, are all faked. "Your computer has been blocked" alert is also present in the background, which is commonly used on various websites in a similar manner.
Due to several messages that bombard the screen, many users might be intimidated and believe that these alerts are real.
Warning: You should never call these provided numbers, as you might be scammed or additional malware installed on your system once you contact the crooks and provide them remote access to your machine.
Many users were baffled as they could not use their computers properly due to the screen-locking function. One of the best ways to bypass this is to open the Task Manager and shut down all unneeded programs, including the web browser. If no luck, you should reboot your PC and access Safe Mode, and then perform a full system scan from there.
From our report of Dec 2020 · not reviewed since
Security software conflict issues: VirTool:Win32/DefenderTamperingRestore pop-up might show up as soon as you install a third-party security tool
In such cases, the issues seem to lie within how different security solutions interact with each other.
Windows Defender uses the Tamper Protection feature that can be enabled and disabled via the anti-virus interface or Registry Editor (HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows Defender\Features). Some malware might attempt to tamper with this setting. However, each time a third-party security solution is installed, the Tamper Protection feature is also disabled in order to prevent false positives and allow the normal operation of the software.
Microsoft launched the Tamper Protection feature with the release of Windows 10 version 1903 in early 2019. According to Microsoft, it provides additional protection from outside intervention. Unfortunately, this can also cause major conflicts when third-party security software is used, as the function is disabled each time a new anti-malware is installed.
Therefore, to stop VirTool:Win32/DefenderTamperingRestore popups, if you are using a third-party security tool and disable Tamper Protection, you should follow these steps:
- Type in Windows Security in Windows search and hit Enter
- Pick Virus & threat protection
- Under Virus & threat protection settings, click Manage settings
- Turn the switch to the left to turn Tamper Protection off.
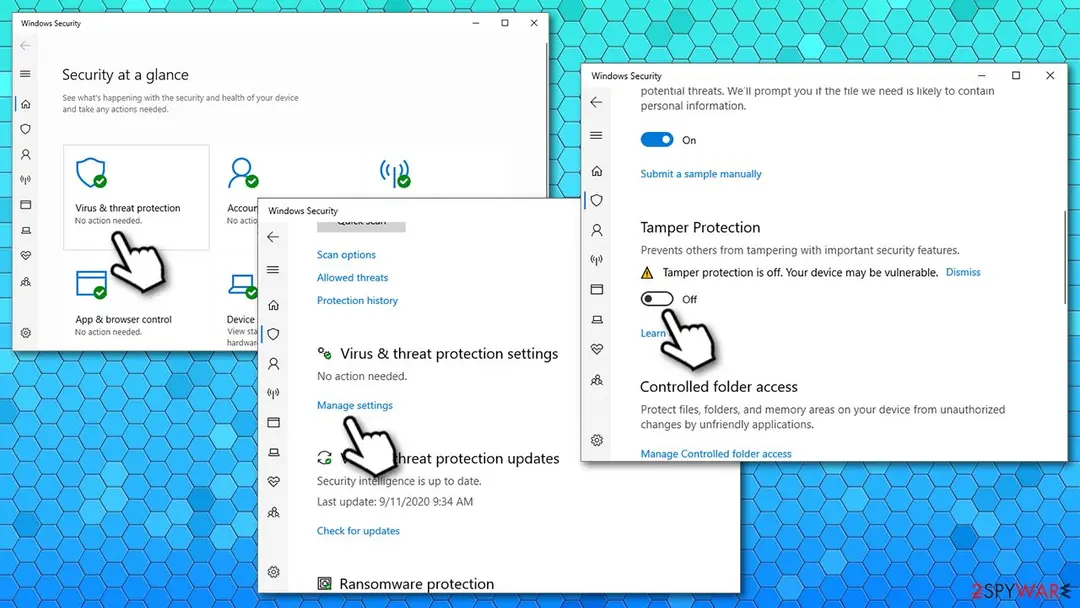
From our report of Dec 2020 · not reviewed since
More from our earlier report on VirTool:Win32/DefenderTamperingRestore
- Windows Defender should be able to detect and eliminate the infection; in some cases, this process might fail due to malware's functionality.
- If malware is tampering with other security solutions, you should access Safe Mode and perform a full system scan from there
- A malware infection can seriously damage Windows operating system files and settings, and security software might fail to fix these compromised items.
- Windows_Firewall_Protection Trojan_Spyware Alert - Error Code #0x268d3 (!x3) Access to this PC has been blocked for security reasons.
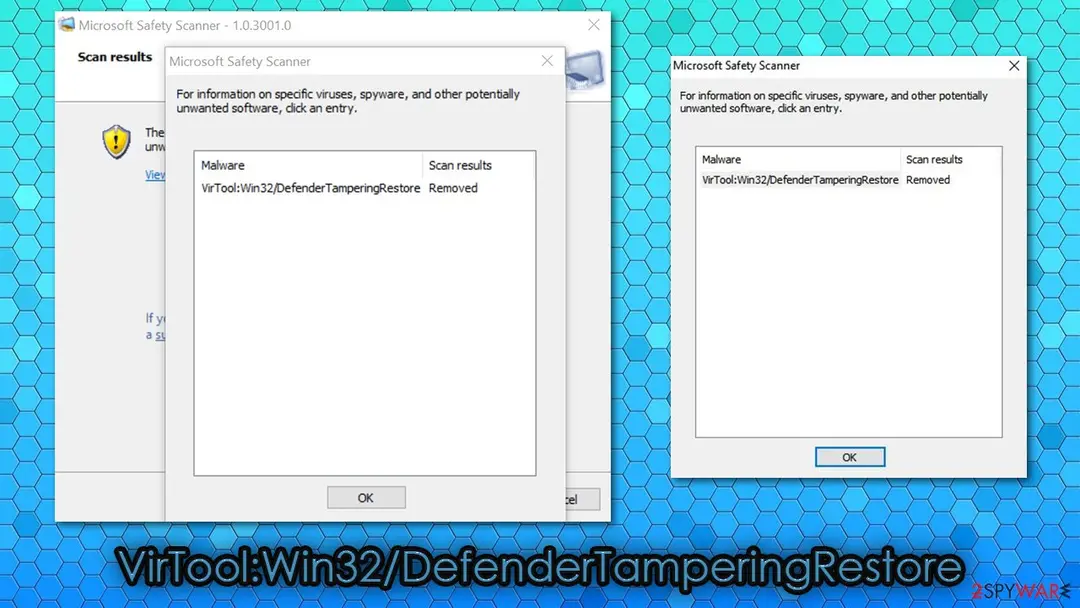
- Some users reported that they keep getting the VirTool:Win32/DefenderTamperingRestore detection on several occasions, i.e., the infection does not go away after removing it with Microsoft Safety Scanner; according to reports, alternative security solutions, such as Norton or Trend Micro, fail to find this threat completely.
How to remove VirTool:Win32/DefenderTamperingRestore
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to VirTool:Win32/DefenderTamperingRestore or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 2: Remove it from startup
Whatever VirTool:Win32/DefenderTamperingRestore installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Dec 2020 · not reviewed since
VirTool:Win32/DefenderTamperingRestore removal instructions
As mentioned above, if your security software managed to catch the infection despite being tampered with, the VirTool:Win32/DefenderTamperingRestore removal process should occur automatically.
If the need arises, you can also access Safe Mode with networking, as explained below, and perform a scan from there.
However, if you are unable to remove this virus automatically and you are using a third-party anti-malware tool along with Microsoft Defender, you should disable the Tamper Protection feature to prevent software conflict from happening in the future.
It was also reported that some malware could cause significant side effects after it is eliminated. For example, the setting "Managed by your organization" might prevent normal functions of anti-virus.
To fix this issue, you might have to edit Group Policy, enable Telemetry Service, and change settings within the Windows registry. If you are not IT-savvy, we highly recommend employing to fix various issues with Windows systems after the infection is deleted.
[GI=method-1]If VirTool:Win32/DefenderTamperingRestore prevents your security software from working normally, perform a scan with alternative software in Safe Mode
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed virTool:Win32/DefenderTamperingRestore in the list of installed apps, a sign of a program that could read browser data, the clean-up is only half of the work.
The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
Protect your privacy - employ a VPN
There are several ways how to make your online time more private - you can access an incognito tab.
However, there is no secret that even in this mode, you are tracked for advertising purposes. There is a way to add an extra layer of protection and create a completely anonymous web browsing practice with the help of VPN. This software reroutes traffic through different servers, thus leaving your IP address and geolocation in disguise.
Besides, it is based on a strict no-log policy, meaning that no data will be recorded, leaked, and available for both first and third parties. The combination of a secure web browser and VPN will let you browse the Internet without a feeling of being spied or targeted by criminals.
No backups? No problem. Use a data recovery tool
If you wonder how data loss can occur, you should not look any further for answers - human errors, malware attacks, hardware failures, power cuts, natural disasters, or even simple negligence.
In some cases, lost files are extremely important, and many straight out panic when such an unfortunate course of events happen. Due to this, you should always ensure that you prepare proper data backups on a regular basis.
If you were caught by surprise and did not have any backups to restore your files from, not everything is lost. is one of the leading file recovery solutions you can find on the market - it is likely to restore even lost emails or data located on an external device.
Questions about VirTool:Win32/DefenderTamperingRestore
What is VirTool:Win32/DefenderTamperingRestore?
VirTool:Win32/DefenderTamperingRestore is a detection name flagged by Windows Defender for malware programmed to disable or weaken security software defenses. The virus's main purpose is tampering with installed antivirus programs, compromising their ability to protect against viruses, trojans, worms, ransomware, and other malware.
Once security software has been tampered with, cybercriminals behind the infection can deploy additional threats like backdoors, ransomware such as Booa or Geno, or trojans stealing passwords and banking details.
The Tamper Protection feature in Windows 10 version 1903 onwards is often the target, designed to provide protection from outside intervention. However, the detection might be a false positive in unexpected cases.
Is VirTool:Win32/DefenderTamperingRestore a false positive?
While VirTool:Win32/DefenderTamperingRestore might occasionally appear as a false positive, it warrants investigation rather than dismissal. Some security software conflicts occur when third-party antivirus tools are installed, temporarily disabling Tamper Protection to prevent conflicts. The detection can stem from various settings in the Windows Registry, particularly if the key HKLM\SOFTWARE\Policies\Microsoft\Windows Defender: Restriction has been enabled.
This setting should never be turned on as it prevents normal Windows Defender operation. Malware can modify this Registry key, requiring immediate elimination. If the detection appears unexpectedly at suspicious times, investigate further by checking for rootkits, uninstalling suspicious extensions, and resetting browser settings.
What damage can VirTool:Win32/DefenderTamperingRestore cause?
This malware can cause severe damage by rendering security software useless, leaving your computer vulnerable to additional infections. Cybercriminals use it as a pathway for deploying ransomware that locks all personal files and demands payment.
Trojans delivered after security software compromise can steal passwords, bank account details, and sensitive information for later misuse. The initial infection enables attackers to place backdoors on systems for further compromise.
Victims suffer financial losses, identity theft, and additional malware infections from opportunistic attackers. Malware can tamper with Windows systems causing errors, crashes, lag, and other stability issues even after termination. The infection should be treated as a critical threat requiring immediate intervention.
How does VirTool:Win32/DefenderTamperingRestore spread?
This malware spreads primarily through malicious spam email links and attachments sent to unsuspecting victims. Software vulnerabilities and exploit kits provide another common distribution method.
False claims on phishing websites and fake Flash Player updates also deliver the infection. Software cracks and pirated program installers frequently contain this threat for users seeking unauthorized access to paid software.
These multiple attack vectors increase success chances for cybercriminals attempting to compromise systems. Users exposed to potentially malicious content online face higher infection risks. Some infections occur through drive-by downloads from compromised websites without any user interaction required.
What are the symptoms of VirTool:Win32/DefenderTamperingRestore infection?
In many cases, the malware operates silently without obvious symptoms, though some users may experience crashes, errors, and unexpected computer events. Windows Defender typically alerts users through notifications when detecting the infection. Some victims report screen-locking scams displaying fake messages claiming their computer has been locked with bogus error codes like "Trojan_Spyware Alert - Error Code #0x268d3 (!x3)".
These fake alerts imitate Windows Defender and Windows Firewall windows to intimidate users. The presence of multiple bombarding alerts claiming your computer is blocked represents common scam behavior. Never call numbers provided in these suspicious pop-ups as they lead to scammers who will charge money and install more malware.
How do I remove VirTool:Win32/DefenderTamperingRestore?
Windows Defender should detect and eliminate the infection automatically in most cases. However, if Windows Defender's detection fails due to the malware tampering with security features, access Safe Mode and perform a full system scan from there. Safe Mode limits malware functionality, allowing antivirus software to operate more effectively.
If the infection persists or your security software becomes compromised, you may need to use alternative security tools like Microsoft Safety Scanner. Some users report using Norton or Trend Micro successfully when Windows Defender struggles. After removal, check that Tamper Protection is re-enabled and Windows Defender operates normally.
Should I disable Tamper Protection if VirTool:Win32/DefenderTamperingRestore appears?
Only disable Tamper Protection if you are using third-party security software that conflicts with it and cannot operate normally alongside Windows Defender. To disable Tamper Protection, open Windows Security, go to Virus & threat protection, click Manage settings under settings, and toggle Tamper Protection off.
Disable it only temporarily while using alternative security software, then re-enable it when returning to Windows Defender alone. Microsoft launched Tamper Protection specifically to prevent malware from tampering with security features, so keeping it enabled is crucial.
Most conflicts between security solutions are resolved by disabling Tamper Protection rather than relying on manual workarounds. If enabling third-party security software causes persistent VirTool detection issues, those tools may be incompatible with your Windows Defender configuration.
Can VirTool:Win32/DefenderTamperingRestore cause permanent damage?
Yes, this malware can cause permanent system damage by deeply compromising Windows operating system files and settings. Security software might fail to fix all compromised items automatically even after removing the malware itself. File corruption and setting alterations may persist after removal, requiring system repair tools to restore functionality.
In severe cases where critical system files become corrupted beyond repair tool capability, Windows reinstallation might become necessary as a last resort. This is why immediate removal is critical before additional damage occurs. After removal, PC repair utilities can usually fix most damage, but prevention through security vigilance remains far preferable to dealing with severe compromises later.
Will Fortect remove VirTool:Win32/DefenderTamperingRestore?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For VirTool:Win32/DefenderTamperingRestore, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- How To-Geek: How To Tell If a Virus Is Actually a False Positive (read October 5, 2026)
- Palo Alto: What is an Exploit Kit? (read October 5, 2026)
- Ghacks: Windows 10 1903: Windows Defender Antivirus gets Tamper Protection feature (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)