
ProstoStealer: what it is and how to remove it
ProstoStealer - malware that is sold online in various Russian hacking sites and forums, so trojan can be used by any malicious actors. Since threat has many functions it can target companies, businesses, or people and operate silently to collect passwords, credentials, and run other commands depending on the operator goals.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Programs like ProstoStealer usually arrive in groups; a free scan lists the companions that are easy to miss.
Do it yourself · free Remove ProstoStealer yourself 3 steps, about 9 minutes, no software needed.
Start the steps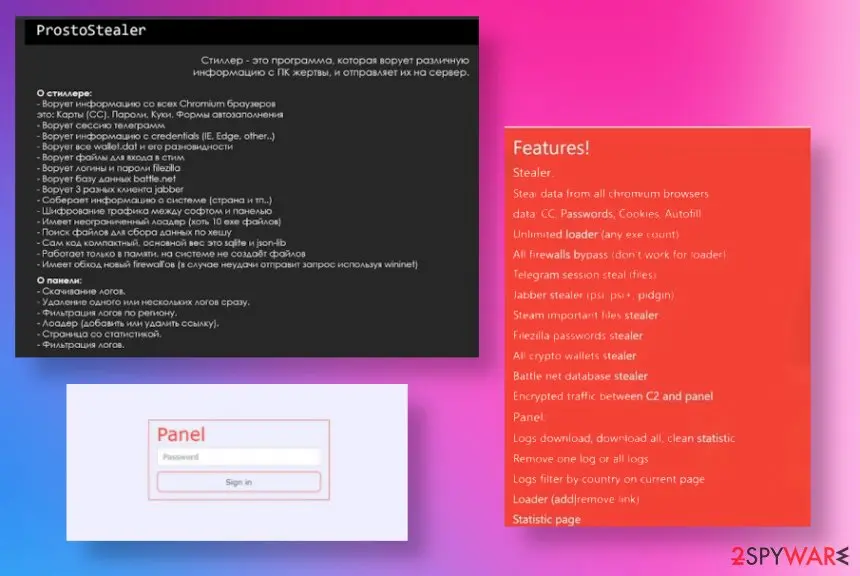
ProstoStealer: summary
| Distribution | Hacked websites, malicious files added to emails, malware scripts from other internet sources or even p2p service packages |
|---|---|
| Name | ProstoStealer |
| Type | Trojan/ Info-stealer malware |
| Purposes | Exploiting the machine to steal valuable information like logins, credentials, passwords, or direct files. All the details get stored on C&C[2] server controlled by hackers and possibly later used for scams or fraudulent transactions, purchases |
| Danger | These threats can be set to work as any criminal wants, so it may act as a backdoor for ransomware or steal valuable information, cryptocurrency wallet funds |
| Detection names | No Microsoft detection name is known |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 5 more facts
| Damage | Not recorded in the old report |
|---|---|
| Symptoms | An unknown program in Installed apps |
| Evidence | 4 write-ups by security sites; details still limited |
| First seen | 20 May 2020 |
| Facts checked | 7 October 2026 |
What ProstoStealer does
From our report of May 2020 · not reviewed since
More from our earlier report on ProstoStealer
- ProstoStealer removal can be difficult when the program runs for a while, but relying on anti-malware tools can be the best solution because this way your device is fully checked and a trojan or other malware can be found and deleted completely
- The system gets affected significantly when the trojan or other more powerful malware infects the machine.
What ProstoStealer collects and where it sends it
From our report of May 2020 · not reviewed since
ProstoStealer is the trojan promoted online as a tool for information stealing and system hacking purposes
ProstoStealer - malware that is sold online in various Russian hacking sites and forums, so trojan can be used by any malicious actors.
Since threat has many functions it can target companies, businesses, or people and operate silently to collect passwords, credentials, and run other commands depending on the operator goals.
There are many features that can be enabled including stealing files, personal conversation data, credentials, and other things like passwords, information from web browsers, and system files. It can even steal the wallet.dat files that allow hackers to collect cryptocurrency wallets and lead to significant financial losses.
ProstoStealer malware can silently infiltrate machine and evade detection, run in the background for a while until any symptoms are noticed. These facts make the malware more dangerous since it operates and is difficult to detect even with AV tools. Fortunately, it is not a widely used threat, so potential hackers are not abusing these functions.
It can create significant damage still and wreck targeted devices. Users encountering any symptoms like application malfunctions, CPU usage, software failure, and significant system crashes should take the infection possibility into consideration and check the system immediately, so trojan can get terminated.
ProstoStealer is the malware that mainly focuses on stealing information and infecting computers using other malware. This program may be the initial infection, but the main intruder gets installed later on. No matter what functions get set as the primary, this trojan can damage the machine significantly.
ProstoStealer can steal information from Chromium-based browsers and cookies, autofill information, passwords, saved credit card and other sensitive details can be sent to a remote server that hackers control. There are tons of applications like Telegram, Jabber, Steam, and other sites, cryptocurrency wallets, platforms, social media that can be accessed for such data exfiltration.
ProstoStealer creators, in this case, launchers can infect machines with ransomware and other malware to control more parts of the system, not only steal credentials. This stealer targets stored passwords, cookies, and look for valuable data that can be sent to Command & Control servers of criminals. Such information can help make fraudulent transactions, blackmail people directly, or perform secondary scams.
ProstoStealer malware victims can suffer financial or data losses, experience damage to their devices. Malware controllers can infect computers or even hack accounts on social media, emails. Stolen credentials and login information can lead to serious privacy issues and identity theft. Trojans like this can create serious problems with privacy and machines.
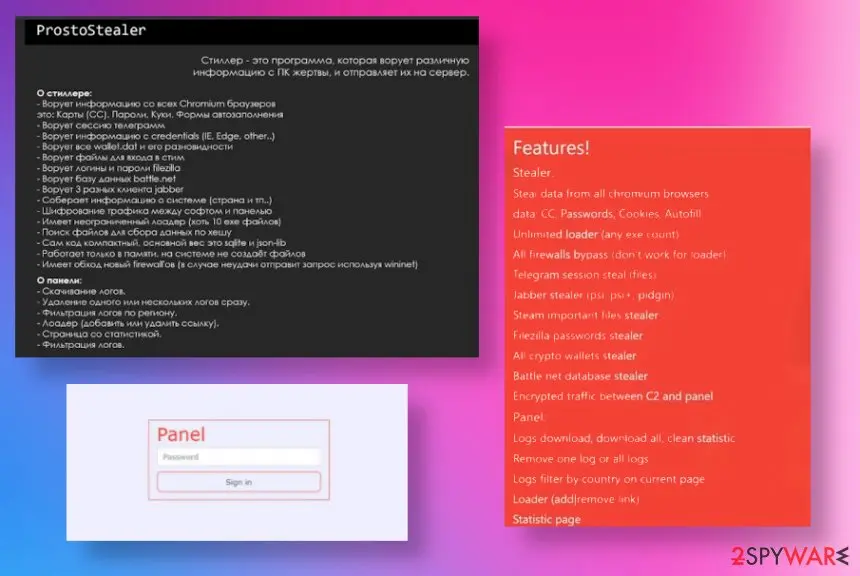
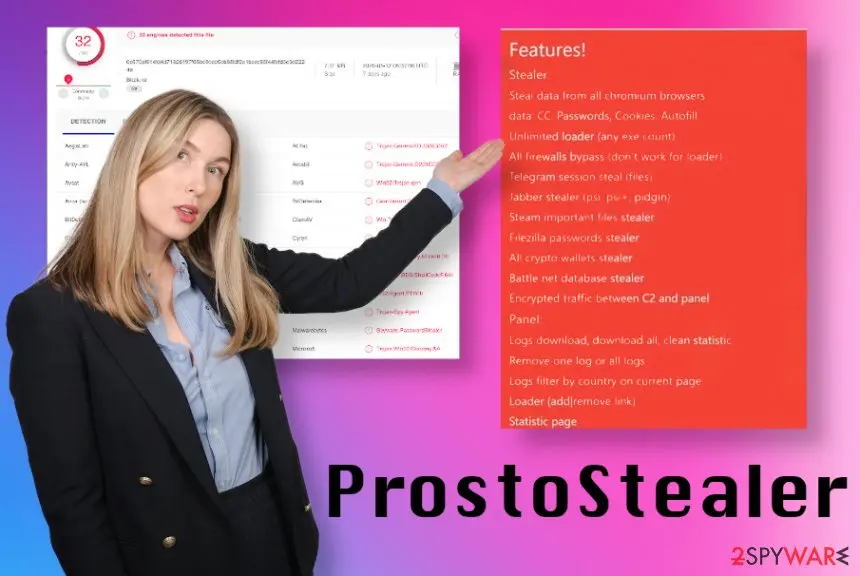
Some of the virus damage can be unrepairable. ProstoStealer is developed as a tool that makes a profit when hackers purchase the trojan from online forums or hacking platforms. Russian hackers are most likely behind this creation because it mainly is promoted on Russian-language sites. To encourage people to purchase the malware developers claim that this virus can:
You need to think about ProstoStealer removal as soon as you notice any issues with the system or experience sudden losses of some files, or even cryptocurrency wallet funds. This malware type is silent and can even evade detection, but the rate of some sample files shows that anti-malware tools can find this intruder and delete it from the system.
To remove ProstoStealer properly, you need to choose the reliable antivirus detection engine-based program and run a check on the machine. It is extremely important to run a full system scan, so all the parts of this or other threats get found and terminated.
Remember that ProstoStealer malware also runs other files and programs on the system. To do that freely and uninterrupted, trojan relies on changing particular settings and affecting files in the system, like registry or startup.
You need to repair that damage if you want to use the machine normally again. File repair programs, PC optimizers like should help you. In such cases, manual interference could create additional issues with startup and other programs, so it is not recommended to alter registry entries yourself.
- steal browser-based data;
- execute any commands;
- bypass firewall;
- steal files from applications like Telegram or Steam;
- gather details from cryptocurrency wallet platforms and applications;
- download and run any malware;
- delete data or programs.
From our report of May 2020 · not reviewed since
ProstoStealer malware termination requires adequate tools for PC protection
Since ProstoStealer virus can be set to perform any functions from the list on promotional pages it can cause damage pretty quickly.
Unfortunately, it is not easy to notice the infection in the first place, especially, when the main processes can be launched in the background alone.
ProstoStealer removal has some additional steps that you should take to achieve the best results. The first one is choosing a proper anti-malware tool that can detect the malware and run the system check fully on the affected computer. Once that is done and you have chosen something like or , you should reboot the system in a Safe Mode with Networking.
When you remove ProstoStealer using these tips, you can run the AV tool and properly check for malware around the operating system without the interruption. Then the only thing left to do is allow the tool to fully clear those intruders and double-check before repairing system file issues with .
[GI=method-1]The Safe Mode with Networking allows the user to run AV tools and remove ProstoStealer without interuption
[GI=method-2]System restore can act as a malware elimination process because this feature can recover machine in a previous state when ProstoStealer malware was not present
How ProstoStealer got on your PC
From our report of May 2020 · not reviewed since
The most common way to attract such malware like trojans is while surfing on insecure or even malicious sites.
Downloading channels, fake software updates, and software cracks can also lead to the infiltration of malware. Websites that resemble official pages or directly copies the interface of some software providers can have malicious scripts running, so interaction, some clicks on the questionable material can trigger a direct drop of the malware payload.
Tha shadiest method that allows malware on the system involves spam email campaigns and notifications stating about financial data, important messages while including malicious files and links. Infectious hyperlinks to malware dropping pages or attachments in the form of MS documents.
These files include malicious macro functionalities, so when the user opens a downloaded file and enables the additional content scripts get literally installed on the system without any permissions needed.
The infection can be avoided if you avoid irrelevant and suspicious emails and delete received notifications with file attachments, links, or questionable subject lines. Stay away from shady software download sites and avoid any other source besides official providers and app developers.
How to remove ProstoStealer
A stealer usually takes what it wants within minutes and may already be gone.
The scan comes first, then the accounts.
Step 1: Scan the PC, then run the offline scan
A scan finds the parts of ProstoStealer that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 2: Change passwords from another device and sign out other sessions
ProstoStealer can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after ProstoStealer, its publisher or created on the day the problem started. Delete those folders, and check C:\Program Files and C:\Program Files (x86) too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
Questions about ProstoStealer
What is ProstoStealer and why is it on my PC?
ProstoStealer is a program that was installed on the PC, most likely together with something else you downloaded. Free software sites and many installers add extra programs on setup pages with pre-ticked boxes, so the extra install looks like your choice even though nobody read the page.
Check the install date in Settings, Apps, Installed apps: the program you installed that day is the probable carrier. If you do not need ProstoStealer, uninstall it. If it belongs to your hardware or to a program you use, search its exact name and publisher first, because drivers and their tools can have unfamiliar names.
How do I stop programs like ProstoStealer from being installed again?
Most unwanted programs arrive through installers, so the fix is in how you install software. Download programs from their official sites or the Microsoft Store, not from download portals or ads above search results. During setup, choose Custom or Advanced installation and untick every extra offer, including browsers, toolbars and optimizers.
Decline update prompts that appear inside other programs unless you know them. In Windows Security, turn on reputation-based protection and potentially unwanted app blocking. These steps would most likely have stopped ProstoStealer before it reached the app list.
Can I change my passwords on the infected PC?
Not while the spyware may still be running. A keylogger or stealer would capture the new passwords too. Use a phone or another computer that was never infected, or wait until the Microsoft Defender offline scan on this PC comes back clean.
Start with your main e-mail account, because it can reset every other password, then banking and payment accounts. When you return to this PC, sign in to the browser again only after the scans are clean and you have ended old sessions.
Nothing has happened yet. Do I still need to change passwords?
Yes. Stolen logs are often sorted and sold before anyone uses them, so the quiet period can last weeks.
The criminals look for the most valuable accounts first, usually crypto, banking and e-mail, and may only reach yours later. Changing passwords and ending sessions now makes the copy worthless whenever it is used.
It takes an evening. Start with e-mail, then money, then everything else saved in the browser, and turn on two-step verification as you go. Watch for login alerts over the following months.
Is ProstoStealer a known stealer?
Not as a named family yet. The sign, prostoStealer in the list of installed apps, is typical of information stealers, keyloggers or clippers, but no analysis links ProstoStealer to a specific one. That is common:
- victims notice the effects
- such as lost accounts or swapped addresses
- before anyone sees the file
You do not need the family name to act. Change passwords from a clean device, sign out of all sessions, move crypto to a new wallet and run a Microsoft Defender offline scan on the PC. If a scan gives a detection name, note it for the report.
Do I need to reinstall Windows to get rid of ProstoStealer?
Usually not. A thorough clean-up is enough when the offline scan finds nothing afterwards and you do not see prostoStealer in the list of installed apps again. A reset is the safer choice if an attacker had remote control, if security tools were switched off, or if detections come back after every clean-up.
Windows 11 can reset itself without a USB stick under Settings > System > Recovery > Reset this PC. Copy documents and photos out first and scan the copies. A reset does not change passwords or undo stolen data, so the account steps still apply.
Is ProstoStealer still on my computer?
Possibly, possibly not. Some stealers stay and keep collecting; others delete themselves after one run. The sign you saw, prostoStealer in the list of installed apps, only shows that data was used, not where the program is now.
A Microsoft Defender offline scan answers the first question; checking Startup apps, Task Scheduler and the Downloads folder for files from the days before helps too. Either way, the account steps are needed, because stolen passwords and cookies keep working after the program is gone, sometimes for weeks.
I have two-step verification. Am I protected?
Partly. Two-step verification stops an attacker who has only your password. But stealers also take session cookies, which represent a login that already passed the second step.
With a cookie, an attacker can open the account until the session expires or you sign out of all devices. So, after an infection, end all sessions as well as changing passwords.
Passkeys and hardware security keys resist phishing better, but a stolen session still needs to be ended. Review trusted devices and remove any you do not recognise.
Should I report ProstoStealer to the police?
Yes, if money was lost or accounts were misused. A police report gives you a reference number that banks, exchanges and insurers often ask for. Include when you first saw prostoStealer in the list of installed apps, the accounts and amounts involved, any wallet addresses or messages, and what you downloaded before it started.
In the US, use the FBI's IC3; in the UK, Report Fraud; in other countries, the national police cybercrime unit. Reporting rarely brings money back quickly, but it helps link cases and is often required for refunds.
Will Fortect remove ProstoStealer?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For ProstoStealer, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Techtarget: command-and-control server (C&C server) (read October 7, 2026)
- VirusTotal: Malware sample detection rate (read October 7, 2026)
- FTC: How to recognize, remove and avoid malware (read October 7, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 7, 2026)
- Microsoft Learn: How Microsoft names malware (read October 7, 2026)