
Royal Raid ads: what it is and how to remove it
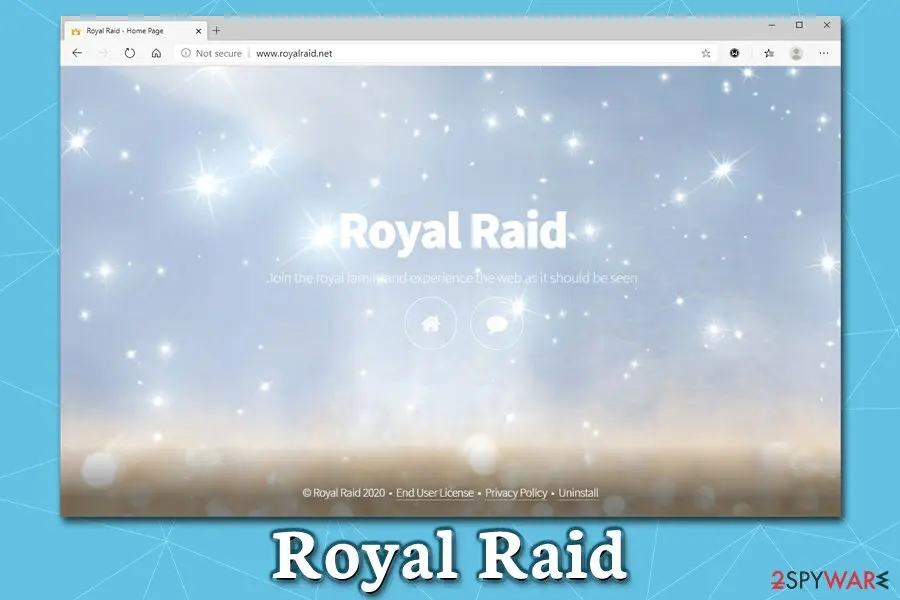
Royal Raid is an adware program that users may have downloaded from its official website - but it is not the most common distribution method of this app. Most users find it on their computers soon after they visit a third-party site to download and install freeware/shareware - this is because most of the potentially unwanted programs are distributed in software bundle packages.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If Royal Raid keeps coming back after uninstalling, a scan can find what reinstalls it.
Do it yourself · free Remove Royal Raid ads yourself 5 steps, about 15 minutes, no software needed.
Start the steps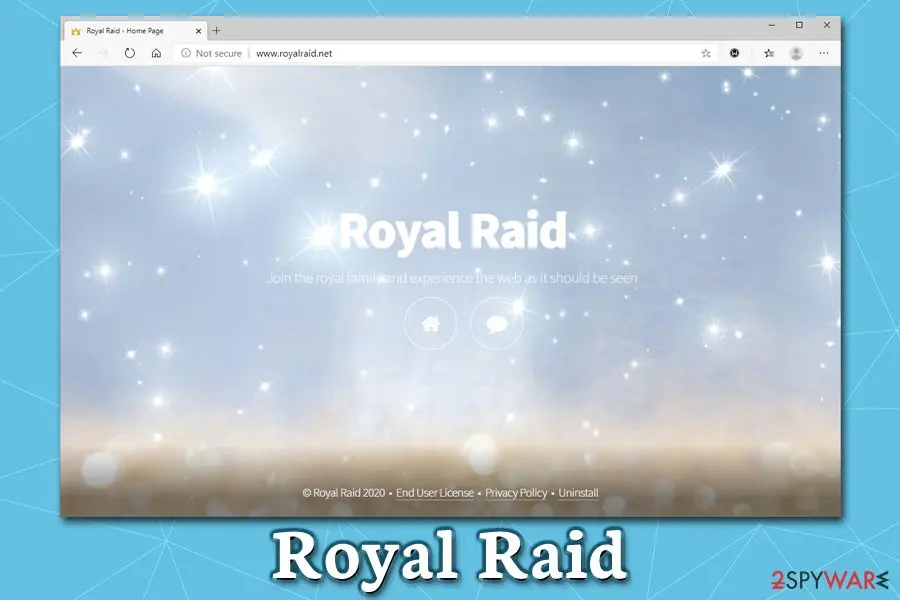
Royal Raid ads: summary
| Damage | Those infected with adware, while not directly endangered, have a risk being lead to insecure websites (phishing, tech support scam, etc.), where they can get tricked into subscribing to useless service, download malicious software, or disclose their sensitive information, such as credit card details |
|---|---|
| Name | Royal Raid |
| Type | Adware, potentially unwanted program |
| Developer | SuperWeb LLC |
| Infiltration | There are several ways users might have installed the PUP on their systems: Bundled software Fake updates Third-party websites or attractive ads |
| Symptoms | Advertisement banners appear on most of the pages that you visit, web browser settings changed without permission, searches are filled with sponsored links, redirects lead to suspicious sites, etc. |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Distribution | Not recorded in the old report |
| Evidence | 5 write-ups by security sites; details still limited |
| Program | Royal Raid |
| First seen | 24 January 2020 |
| Facts checked | 6 October 2026 |
Is Royal Raid ads dangerous?
From our report of Jan 2020 · not reviewed since
Royal Raid is a potentially unwanted program that displays intrusive ads on Chrome, Firefox, and other browsers
Royal Raid is an adware program that users may have downloaded from its official website - but it is not the most common distribution method of this app.
Most users find it on their computers soon after they visit a third-party site to download and install freeware/shareware - this is because most of the potentially unwanted programs are distributed in software bundle packages. Most likely, the Royal Raid virus slipped in because it was offered as an optional component during the installation.
Soon after the infiltration, users will notice Royal Raid ads and redirects, which can come in various forms - coupons, deals, offers, in-text links, flashing windows, etc., and will be shown on every installed browser, such as Google Chrome, Mozilla Firefox, Safari, MS Edge, and other browsers.
The main goal of Royal Raid ads is to expose users to as much commercial content as possible, all while claiming that it is done for their own sake, as the app allegedly "enhances browsing experience."
In reality, what it does is a complete opposite - it clutters browsers by showing ads everywhere and also tracks web browsing data while doing so. Without a doubt, if you value online privacy, you should not wait and remove Royal Raid as soon as possible.
Users who get infected with the Royal Raid virus will not take long to notice its prescience on the machine - visiting a website as eBay or Amazon will instantaneously spawn boxes with promotion ads and links to affiliated websites. Please be aware that these links might not always be safe, so we do not recommend clicking on them.
By exposing users to commercial content online, the developers of this potentially unwanted program earn revenue from each click - even if it is an accidental one. However, potentially unwanted programs are often presented as useful tools that help users to find relevant information online easily, while in reality, the purpose of such apps like Royal Raid is to gain ad revenue.
In most cases, the ads that appear on various websites are random, although in some cases Royal Raid ads might be marked as following:
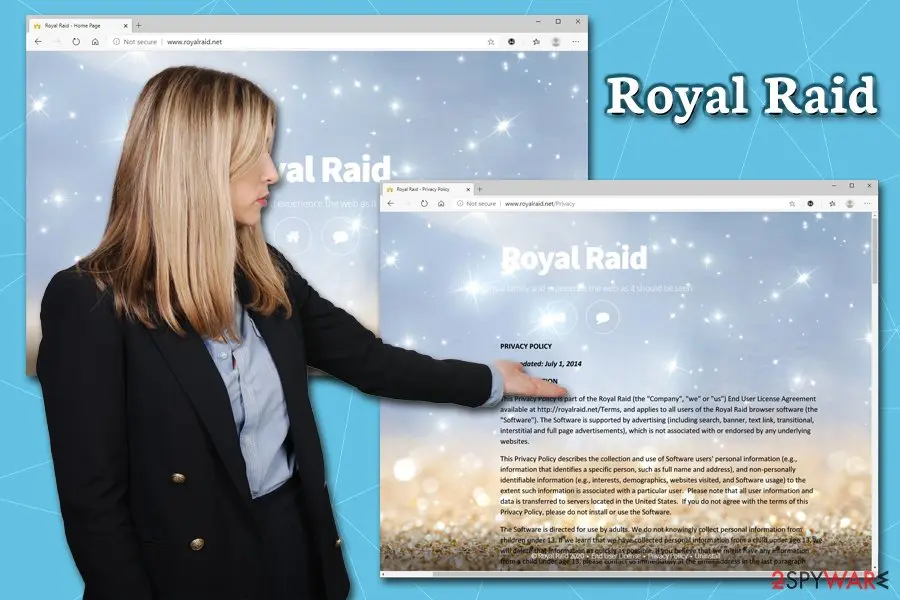
Ads by Royal Raid might seem like a nuisance to most - but the app also brings online tracking practices that might just exceed your regular level of data collection. As stated in the app's Privacy Policy, Flash cookies, JavaScript, pixels, web beacons, DOM data, and other technologies are used to gather a variety of information about app's users:
As evident, Royal Raid is not shy when it comes to the collection of data. What makes matters worse is that it also claims that the information can be used, shared, and sold with third parties and other entities. Thus, if you value your privacy, you should definitely not employ these allegedly helpful search tools that flood you with advertisements and collect information about your every online step.
Optionally, a browser reset can also help you get rid of the changed settings that the PUP established.
- Ads by Royal Raid
- Brought to you by Royal Raid
- Royal Raid ads
- Powered by Royal Raid, etc.
From our report of Jan 2020 · not reviewed since
Potentially unwanted programs usually sneak in along with freeware
Unfortunately, users are pretty careless when it comes to cybersecurity - this includes the careless installation of new applications.
Not only they visit insecure sites that host cracked software, but they also refuse to apply measures that would protect their machines from malicious software. While a browser hijacker and adware are not considered to be major infections, careless online behavior can result in something much more sinister - such as Remote Access Trojan, or ransomware infection.
Therefore, it is very important to take care of the computer and use precautionary measures. As evident, downloading software cracks are a big no-no, as the most prolific malware is spread via these insecure files. It is also imperative to equip your computer with anti-malware software to protect it from threats and patch it as soon as new updates are available.
Finally, you should also take care of good software downloading/installation practices - if possible, pick official sources for your programs.
Microsoft Store, App Store, Google Web Store and similar, are the best places to pick your new applications from, as you will not be surprised with the installation of additional software, unlike on third-party sites like Softonic, FileHippo, Cnet, etc. Installers there are often equipped with promotional programs that are often considered as PUPs.
Thus, if you still decide to go for third-parties, you should make sure that you always pick Advanced/Custom settings during installations, remove all the ticks from pre-ticked boxes, decline all the deals, and watch out for fine print text.
From our report of Jan 2020 · not reviewed since
More from our earlier report on Royal Raid
- Adware and malware can cause significant damage to the operating system.
- When using the software, various types of individual users information is collected, stored, shared with other parties, supplemented, used and sold for business and marketing purposes <...> This user information includes information about your computer system, such as IP address, unique identifier number, hardware, software, configuration, operating system, browser, <...>.
- It also includes information about your internet use, browsing activity, demographics, location, and interests, such as websites visited, pages viewed, search queries entered, <...> and other products or services of interest to you.
How to remove Royal Raid ads
How to remove Royal Raid
Uninstall first, then remove what stays behind, so the ads do not come back after a restart.
Step 1: Uninstall Royal Raid
Royal Raid is removed like any other program, from the list of installed apps. In Windows 11 that is Settings > Apps > Installed apps, in Windows 10 Settings > Apps > Apps & features, and in both you can also use Control Panel > Programs and Features.
Select Royal Raid, click Uninstall and follow the uninstaller to the end. Then look at the entries just above and below it when the list is sorted by date: bundled programs install at the same minute.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 2: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after Royal Raid, its publisher or created on the day the problem started.Delete those folders, and check
C:\Program FilesandC:\Program Files (x86)too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Reset the browser
A reset removes what the steps above could miss:
- changed start pages
- site permissions
- hidden settings
In Chrome open Settings > Reset settings > Restore settings to their original defaults; in Edge Settings > Reset settings; in Firefox Help > More troubleshooting information > Refresh Firefox.
Tip: Bookmarks and saved passwords stay, while extensions are turned off and the search engine and start page return to the defaults.
Reset every browser on the PC, including Edge, which Windows 11 and Windows 10 always have.
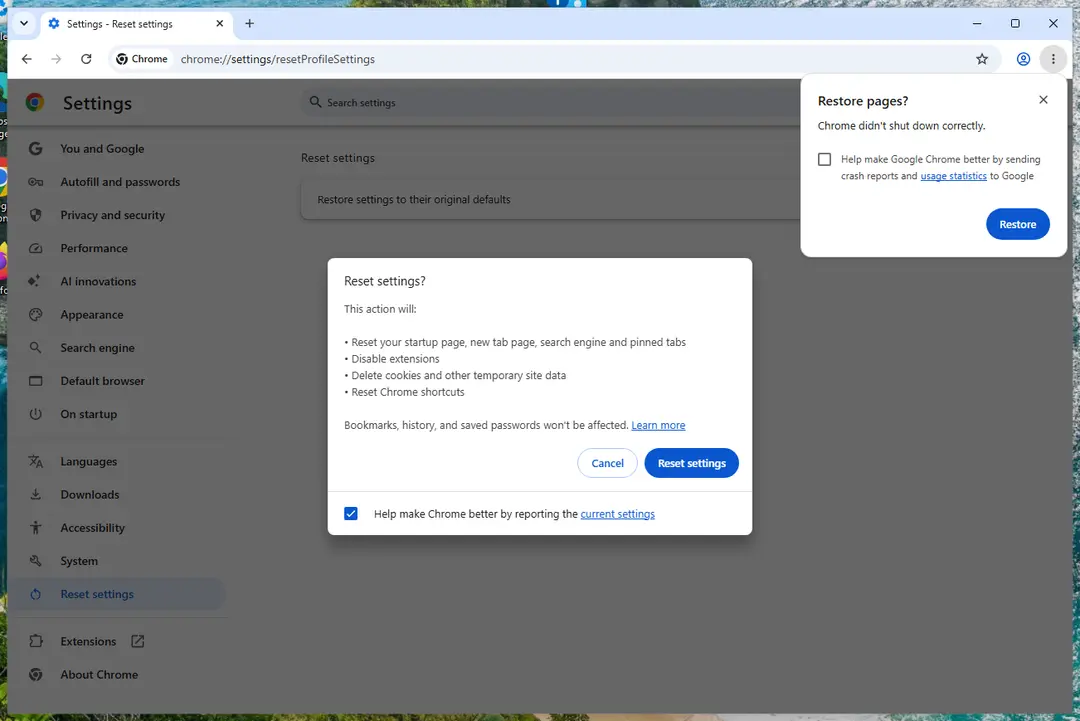
Chrome on Windows 11: Settings > Reset settings. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 5: Scan the PC, then run the offline scan
A scan finds the parts of Royal Raid that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
Get rid of unwanted applications from Windows as per instructions below:
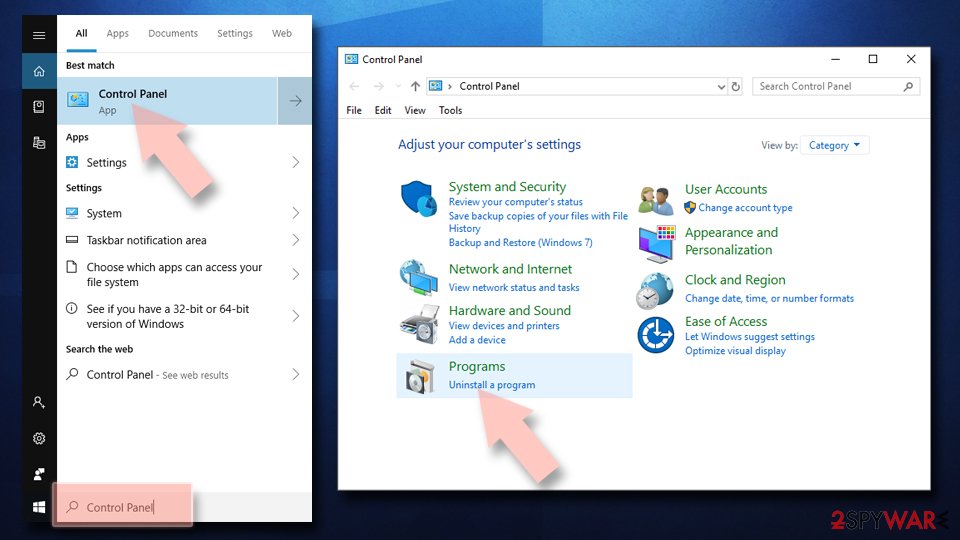
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
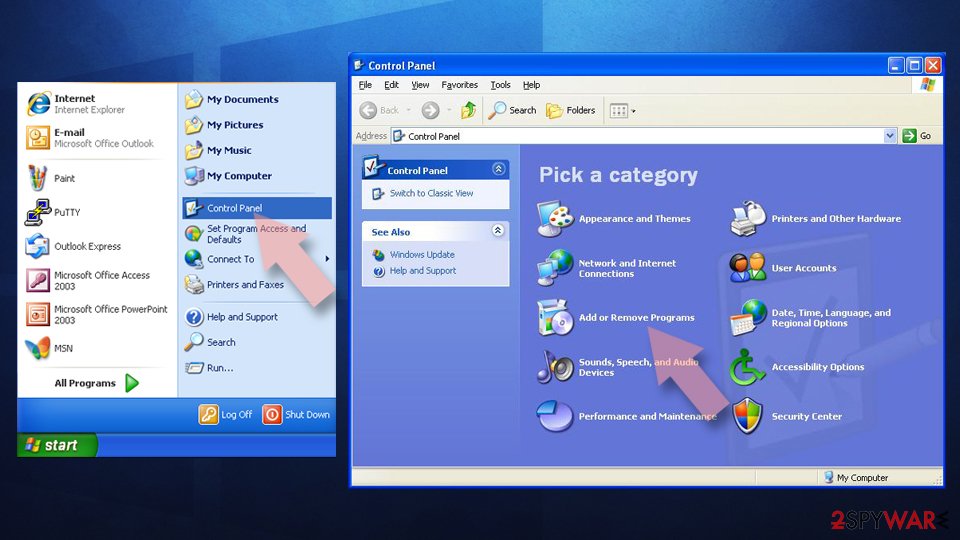
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
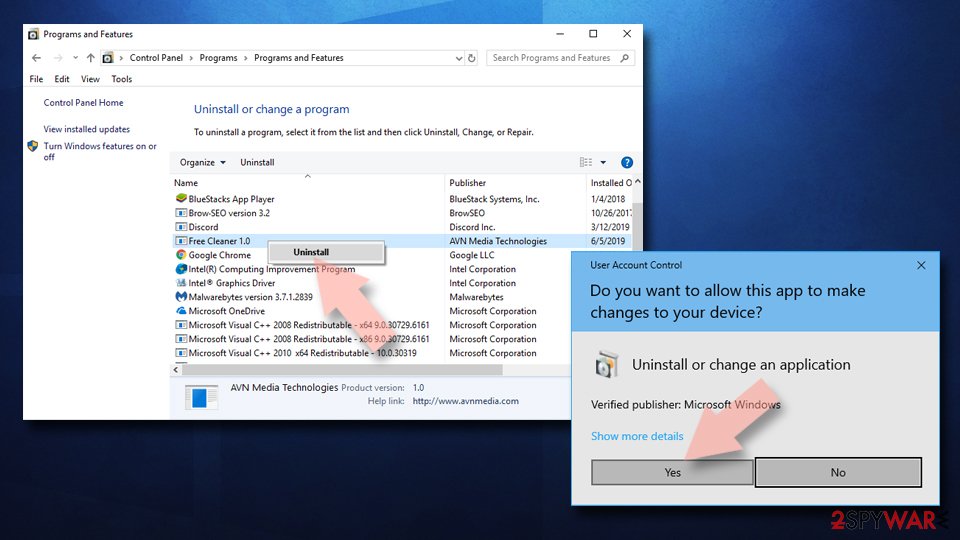
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
Delete malicious extensions from Google Chrome:
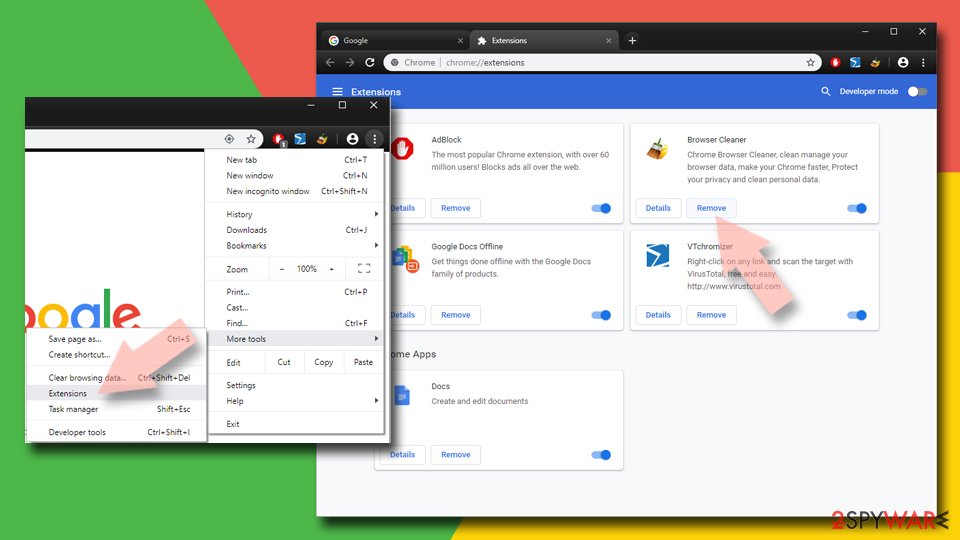
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
Clear cache and web data from Chrome:
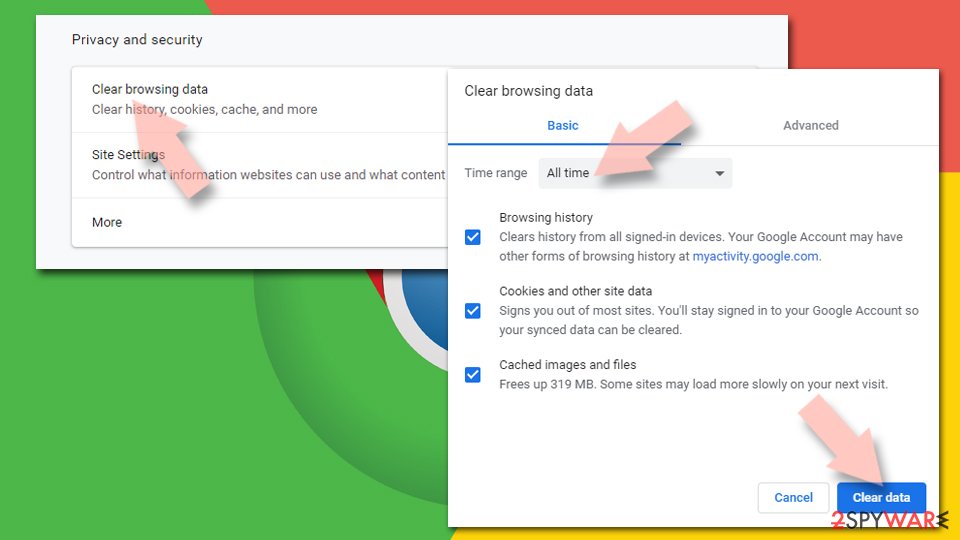
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
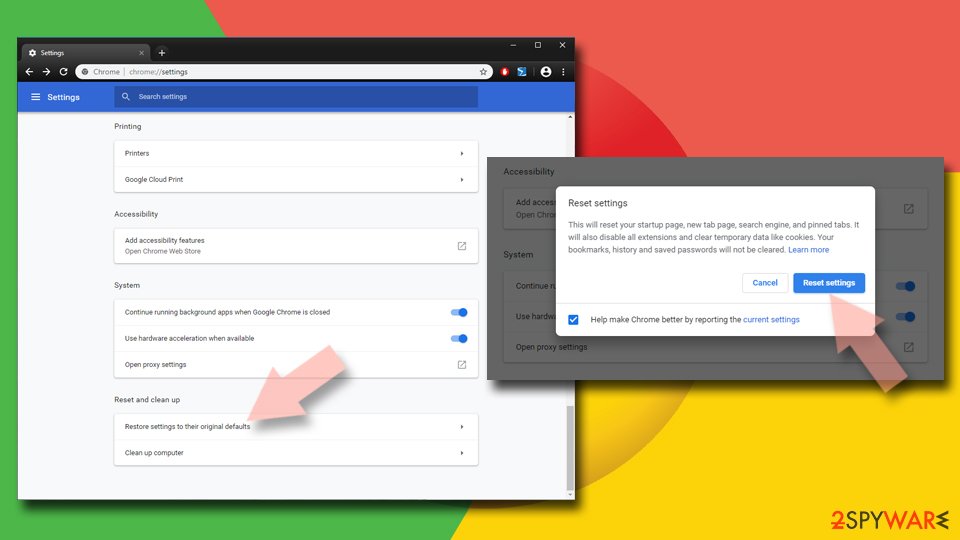
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
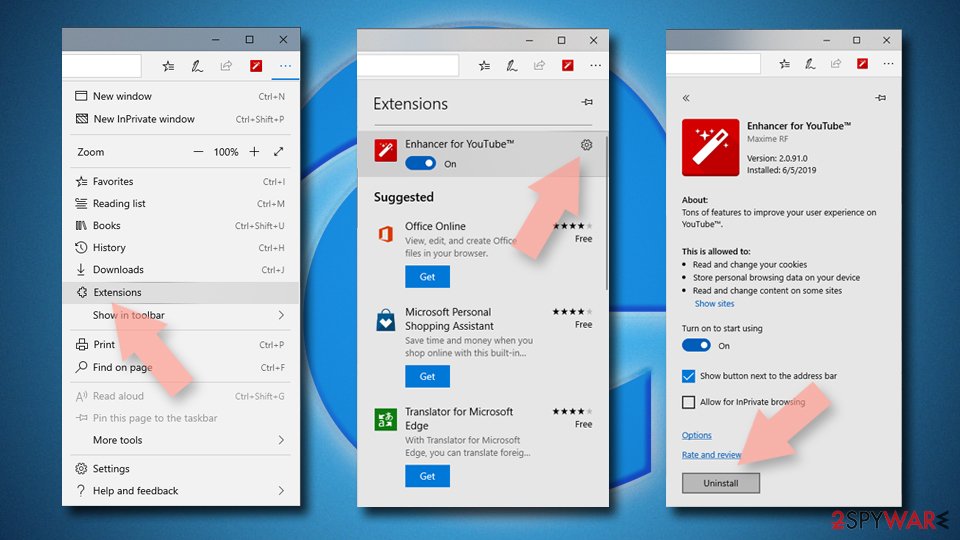
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.
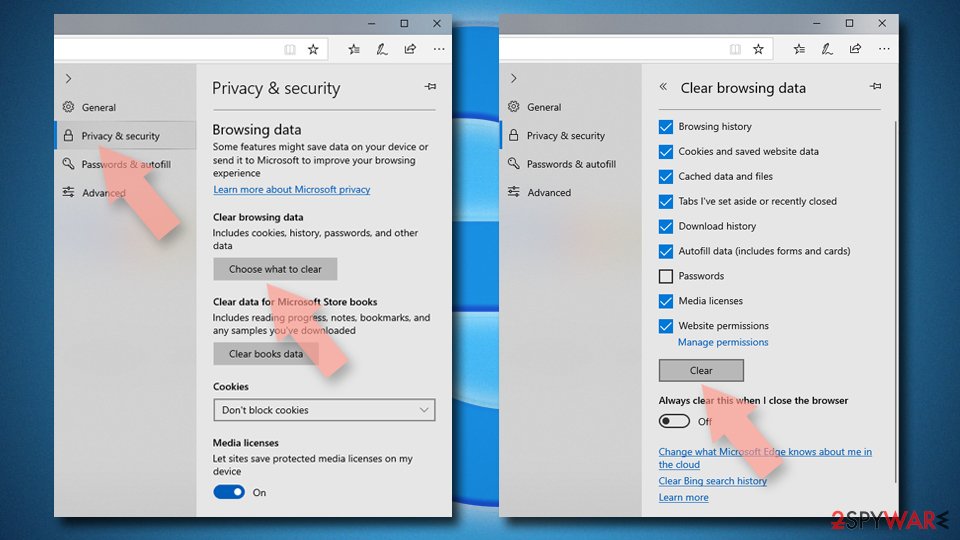
Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.
Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
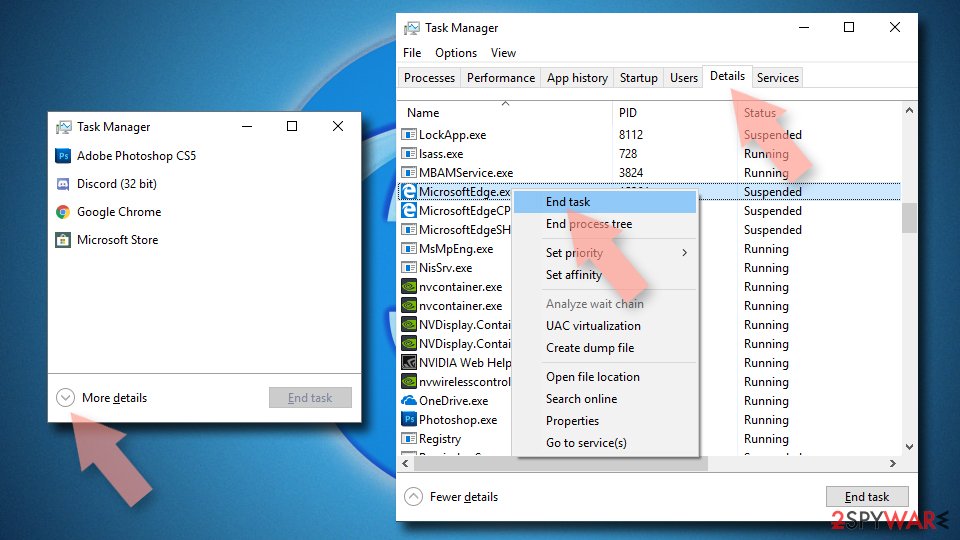
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.
Delete extensions from MS Edge (Chromium):
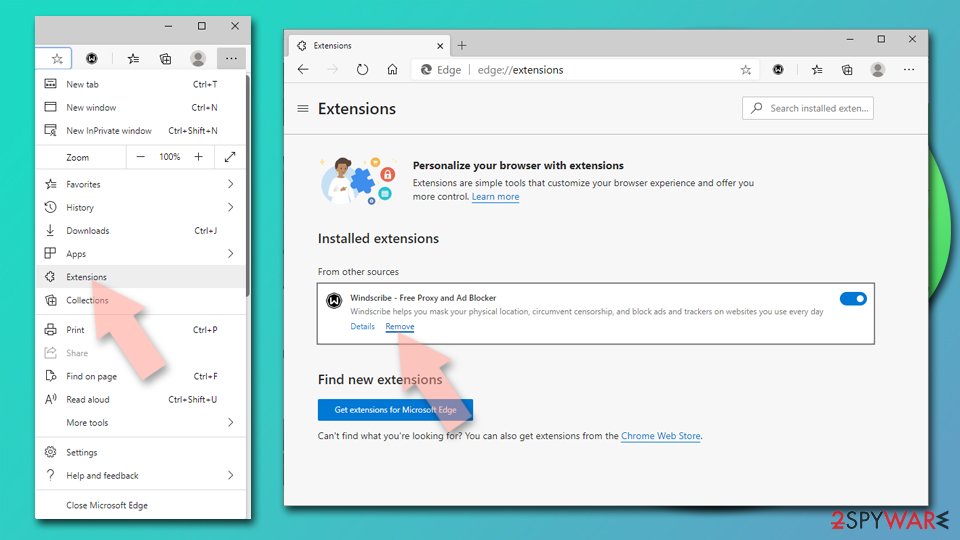
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
Clear cache and site data:
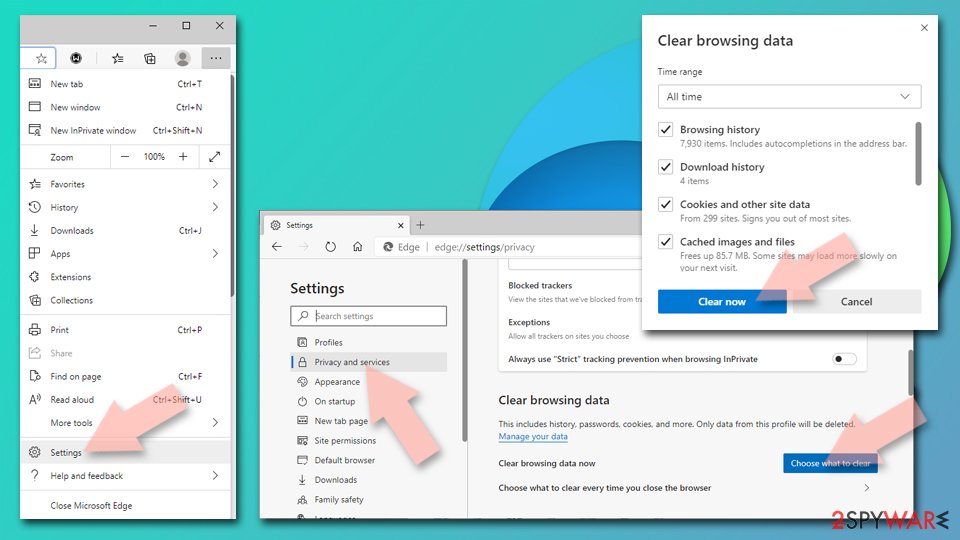
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
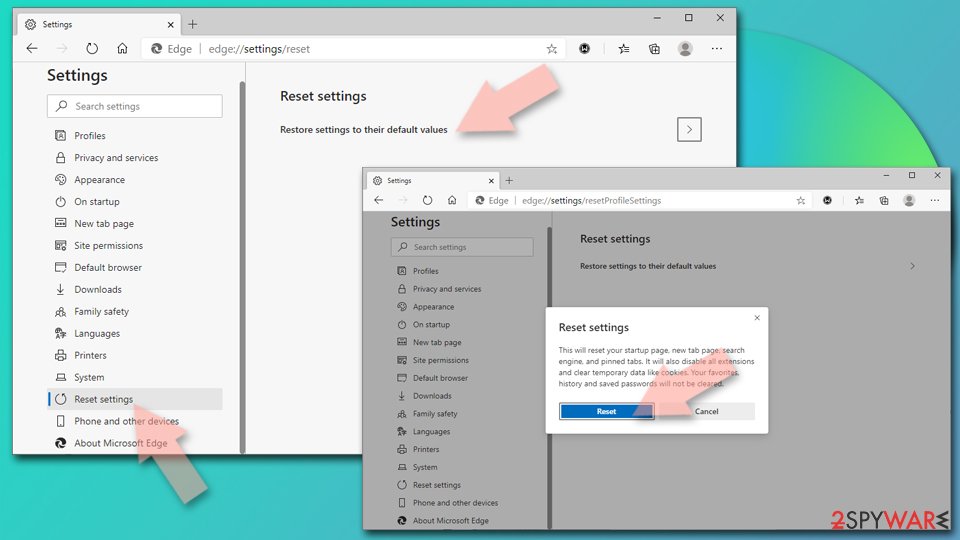
Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.
Remove from Mozilla Firefox (FF)
Reset Mozilla Firefox as soon as you delete PUPs from your system:
Remove dangerous extensions:
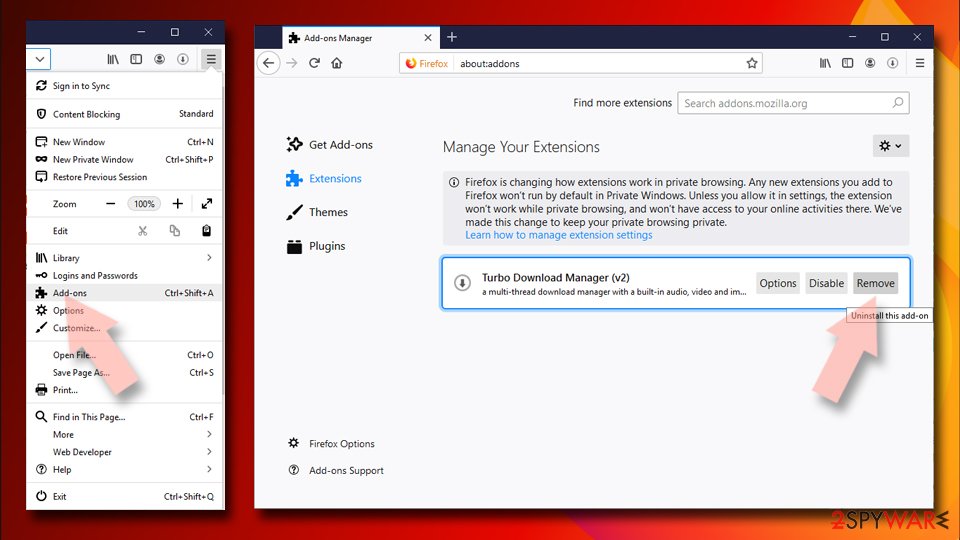
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
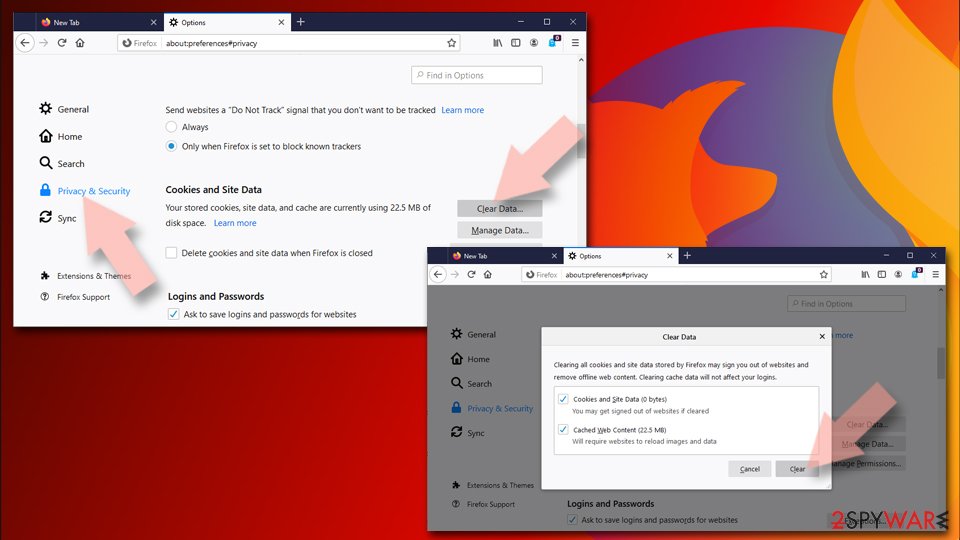
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
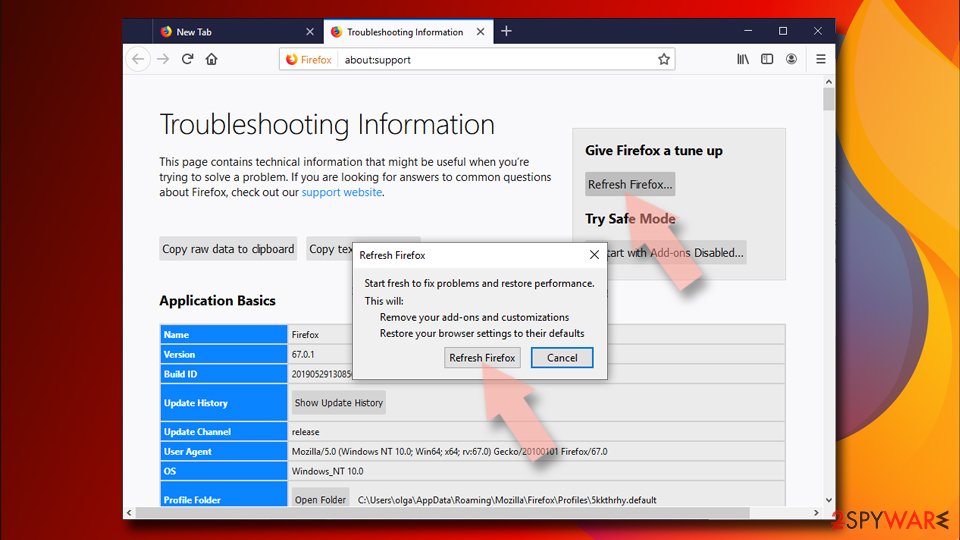
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
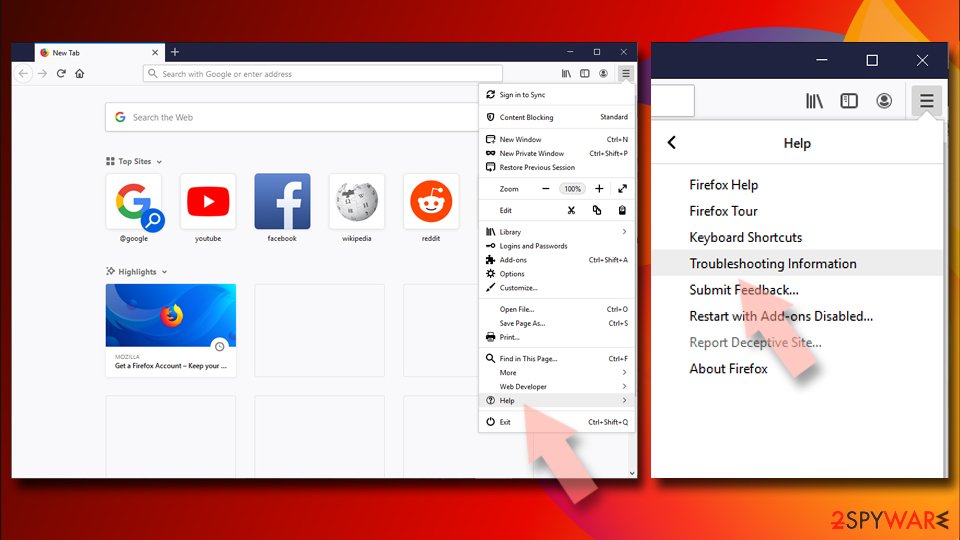
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
Remove dangerous extensions:
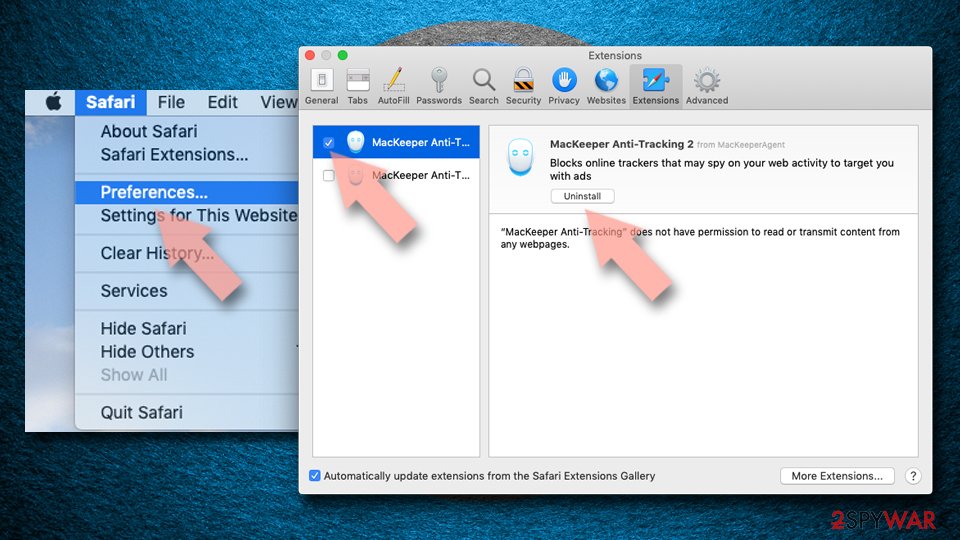
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
Clear history and website data:
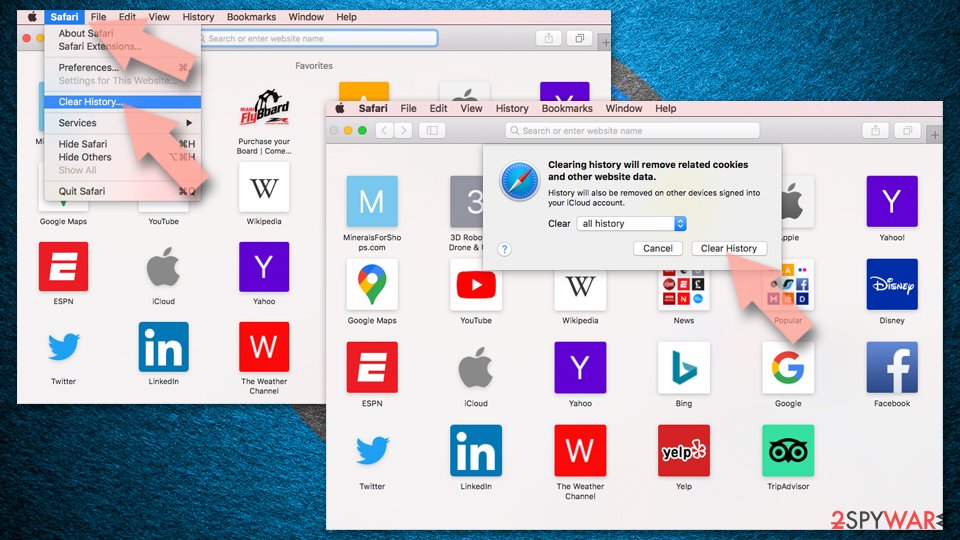
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
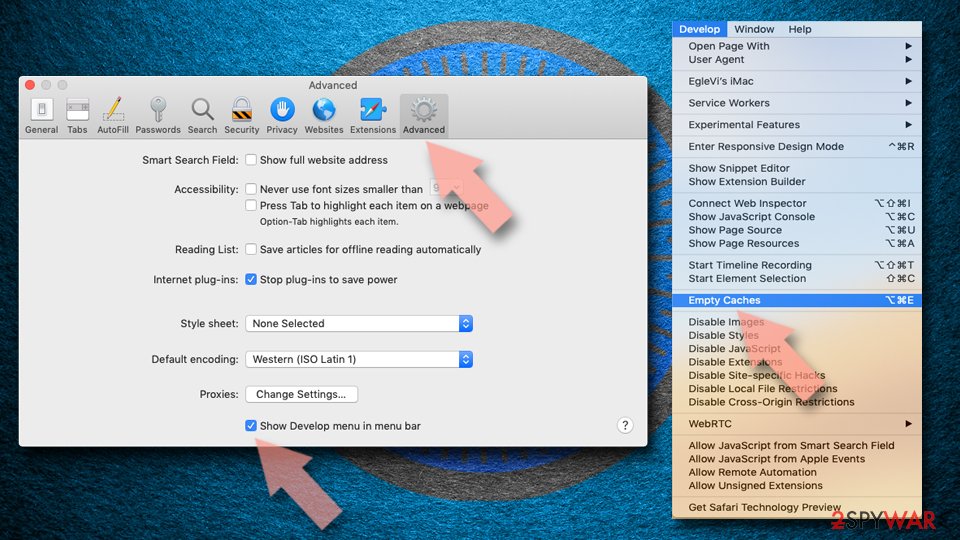
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
macOS users should follow this guide in order to uninstall Royal Raid and other adware
Remove the unwanted application:
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
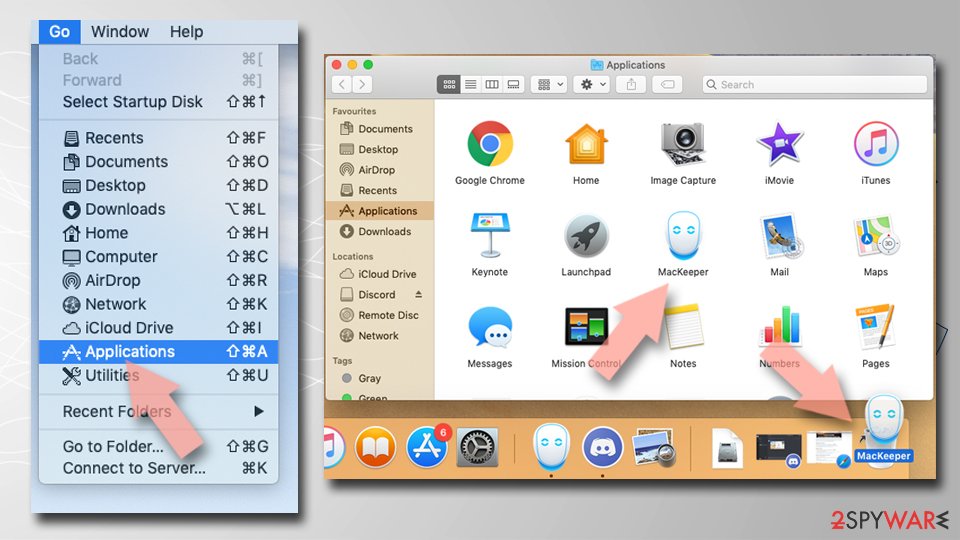
Delete leftover files and folders:
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
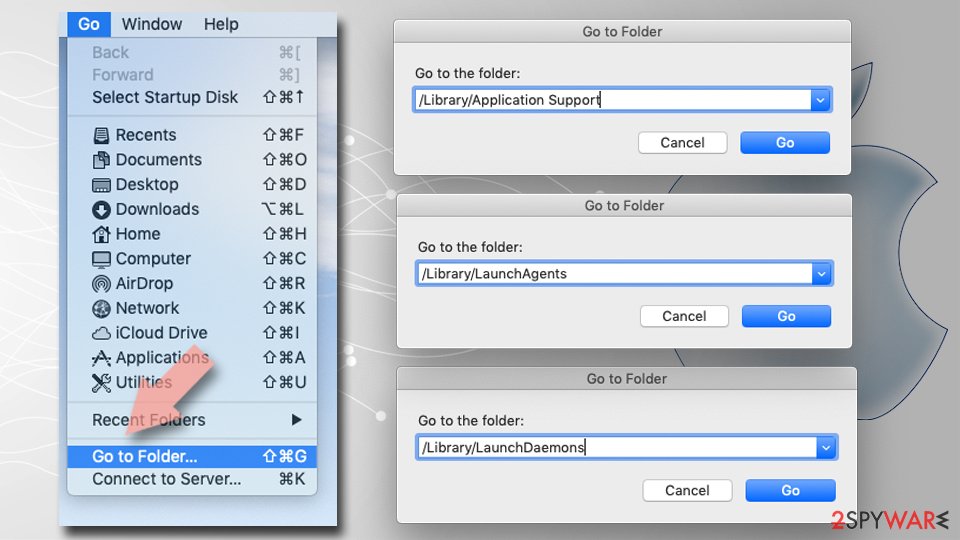
- Finally, empty the Trash to permanently remove the leftovers.
Reset Internet Explorer
Remove dangerous add-ons:
- Open Internet Explorer, click on the Gear icon (IE menu) on the top-right corner of the browser
- Pick Manage Add-ons.
- You will see a Manage Add-ons window. Here, look for suspicious plugins. Click on these entries and select Disable.
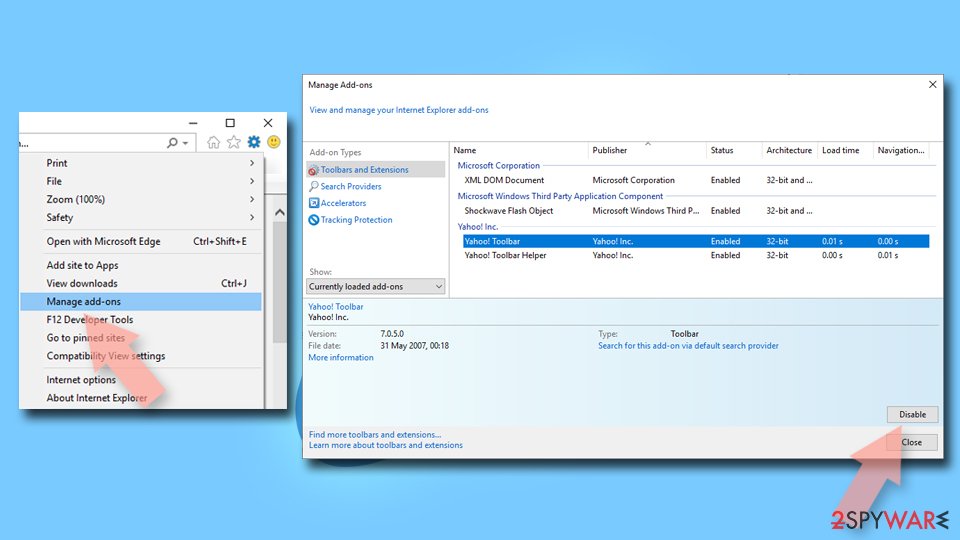
Change your homepage if it was altered:
- Open IE and click on the Gear icon.
- Select Internet Options.
- In the General tab, delete the Home page address and replace it by your preferred one (for example, Google.com).
- Click Apply and then select OK.
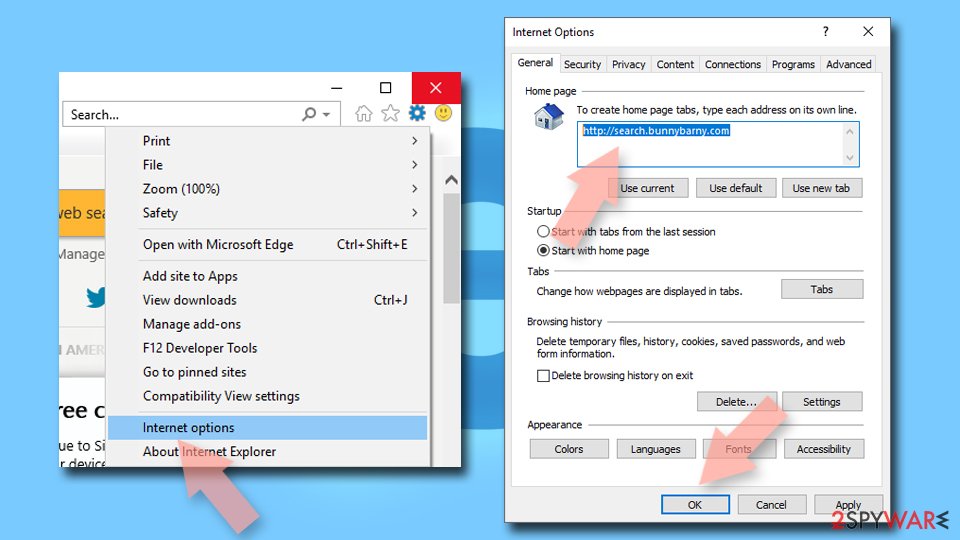
Delete temporary files:
- Press on the Gear icon and select Internet Options.
- Under Browsing history, click Delete...
- Select relevant fields and press Delete.
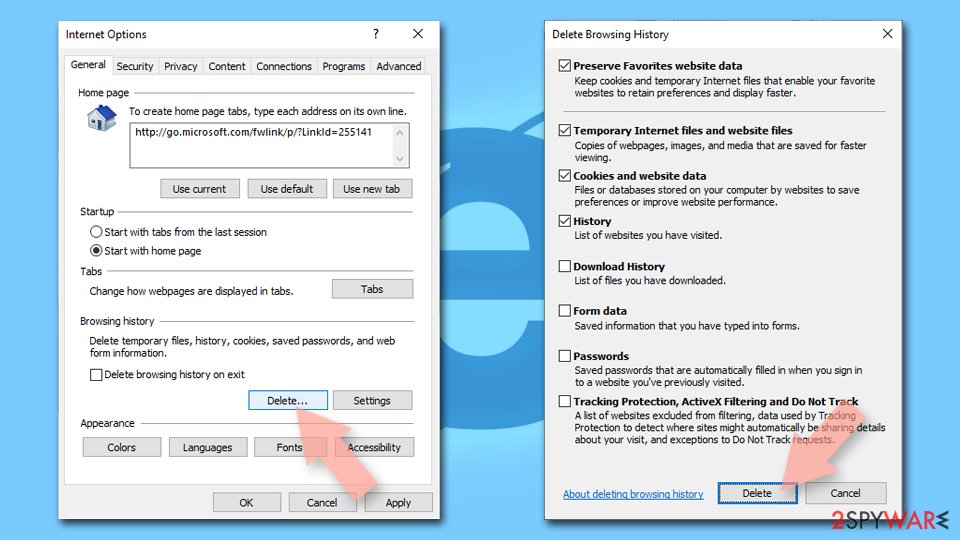
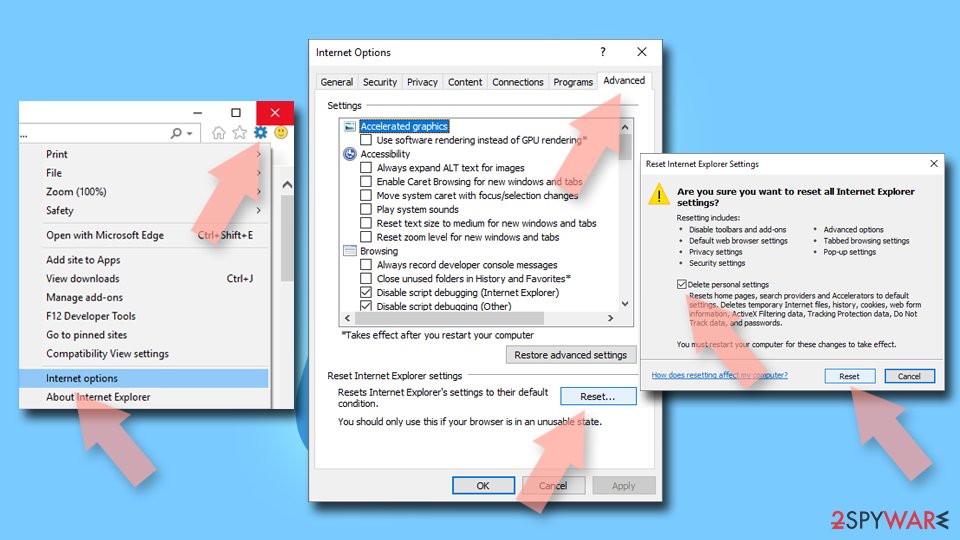
Reset Internet Explorer:
- Click on Gear icon > Internet options and select Advanced tab.
- Select Reset.
- In the new window, check Delete personal settings and select Reset.
Choose a proper web browser and improve your safety with a VPN tool
Online spying has got momentum in recent years and people are getting more and more interested in how to protect their privacy online.
One of the basic means to add a layer of security - choose the most private and secure web browser. Although web browsers can't grant full privacy protection and security, some of them are much better at sandboxing, HTTPS upgrading, active content blocking, tracking blocking, phishing protection, and similar privacy-oriented features.
However, if you want true anonymity, we suggest you employ a powerful VPN - it can encrypt all the traffic that comes and goes out of your computer, preventing tracking completely.
Lost your files? Use data recovery software
While some files located on any computer are replaceable or useless, others can be extremely valuable.
Family photos, work documents, school projects - these are types of files that we don't want to lose. Unfortunately, there are many ways how unexpected data loss can occur:
- power cuts
- Blue Screen of Death errors
- hardware failures
- crypto-malware attack
- even accidental deletion
To ensure that all the files remain intact, you should prepare regular data backups. You can choose cloud-based or physical copies you could restore from later in case of a disaster. If your backups were lost as well or you never bothered to prepare any, can be your only hope to retrieve your invaluable files.
From our report of Jan 2020 · not reviewed since
Get rid of Royal Raid virus
Ads by Royal Raid might not always be noticed right away, as those who do not use ad-blocking extensions are used to commercial content appearing on most sites.
However, there are two different types of advertisements - those embedded within the site that the developer uses to monetize, and those that are injected as a virtual layer into users' web browsers. Thus, many might not differentiate between the two and simply think that Ads by Royal Raid are a part of the site they are visiting.
However, that is not the case, and Royal Raid removal from the computer would drastically reduce the number of advertisements is encountered online. Besides, those infected with adware often have other potentially unwanted programs installed on their systems, so disturbance of web browsing is even greater.
If you suspect that you might have multiple infections on your machine, you should scan it with anti-malware software - it will remove Royal Raid virus along with other PUPs, as well as malware. Alternatively, you can follow our guide below and terminate unwanted programs manually.
Questions about Royal Raid ads
What is Royal Raid and why is it on my PC?
Royal Raid is a program that was installed on the PC, most likely together with something else you downloaded. Free software sites and many installers add extra programs on setup pages with pre-ticked boxes, so the extra install looks like your choice even though nobody read the page.
Check the install date in Settings, Apps, Installed apps: the program you installed that day is the probable carrier. If you do not need Royal Raid, uninstall it. If it belongs to your hardware or to a program you use, search its exact name and publisher first, because drivers and their tools can have unfamiliar names.
Royal Raid will not uninstall. What can I do?
First restart the PC and try again, because the program may have been running and locked its own files. If the uninstaller is missing or fails, start Windows in Safe Mode, where most third-party programs do not start, and remove Royal Raid from Installed apps there.
If it still refuses, delete its startup entry and its scheduled task, restart, and try once more. A program that actively prevents removal is behaving like malware, so finish with a Microsoft Defender offline scan. Avoid third-party uninstallers offered on search ads; several of them are unwanted programs themselves.
Royal Raid has no uninstaller. What now?
Some adware does not register itself properly, or its uninstaller only opens a web page. First try Settings > Apps > Installed apps and the older Control Panel > Programs and Features; one may list it when the other does not.
If neither works, disable its entry in Task Manager > Startup apps, restart, and run a Microsoft Defender full scan and offline scan, which remove known adware files. Then, if anything is left, delete the folder it ran from, which you can find by right-clicking the process in Task Manager and choosing Open file location.
I clicked on one of the ads. Am I infected?
Probably not. Clicking an ad usually only opens a page, and a page cannot install programs on an up-to-date Windows PC without your help.
You are at risk only if you then downloaded and ran a file, allowed notifications, entered card or login details, or called a phone number shown on the page. Delete any download and run a full and offline scan.
Change passwords you typed, from a clean device. Call your bank if you gave card details. If you called a number or allowed remote access, see the next question.
An ad showed a phone number and I called it. What now?
The number belongs to scammers, not to Microsoft or an antivirus company. If you only talked, hang up and do not call back. If you let them connect to the PC, disconnect it from the internet, uninstall the remote access program they used, such as AnyDesk, TeamViewer, ScreenConnect or UltraViewer, and run a full and offline scan.
If you paid or gave bank details, call your bank at once on the number printed on your card. Change any passwords you typed while they were connected, and report the call.
Can adware slow down my PC?
Yes. Adware runs in the background, loads ad scripts, opens extra tabs and contacts its servers, all of which use processor time, memory and bandwidth. Ad-heavy extensions also slow down every page, because they inspect and change it before you see it.
The effect is strongest on older PCs and when several adware programs arrived together. After removal, restart the PC and check Task Manager for anything still using a lot of resources that you do not recognise. Speed usually returns to normal once the ads stop.
Does adware steal passwords?
Ordinary adware is built to show ads, not to steal logins, and most of it never touches saved passwords. The line is blurry, though. Extensions that can read every page could capture what you type, and adware ads sometimes lead to phishing pages that ask for passwords directly.
If you entered credentials on a page reached through an ad, change that password from a clean device and turn on two-step verification. Otherwise, removing ad-supported program and clearing cookies is usually enough.
Why didn't my antivirus catch Royal Raid?
Many security products do not block adware or notification sites by default, because users often agreed to them, even through a misleading prompt. Notification spam installs nothing at all, so there is no file to detect.
In Windows 11 you can make Microsoft Defender block potentially unwanted apps: open Windows Security > App & browser control > Reputation-based protection settings and turn on Potentially unwanted app blocking. If notifications caused the pop-ups, no scanner will report them; the fix is in the browser's site settings.
Will Fortect remove Royal Raid?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Royal Raid, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- SearchSecurity: PUP (potentially unwanted program) (read October 6, 2026)
- Popular Mechanics: What Are Flash Cookies and How Can You Stop Them? (read October 6, 2026)
- Wikipedia: JavaScript (read October 6, 2026)
- Cyware: Cracked software versions are harboring Djvu Ransomware in the form of .TRO files (read October 6, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 6, 2026)