
Unlocker ransomware: what it is and how to remove it
Unlocker ransomware is one of the most recent data-locking malware versions. Ransomware is very damaging because it locks all of the personal files on the victims' computers and makes them impossible to open.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
A free scan checks for the encryptor still on the PC; it does not decrypt .lock files.
Do it yourself · free Remove Unlocker ransomware yourself 6 steps, about 18 minutes, no software needed.
Start the steps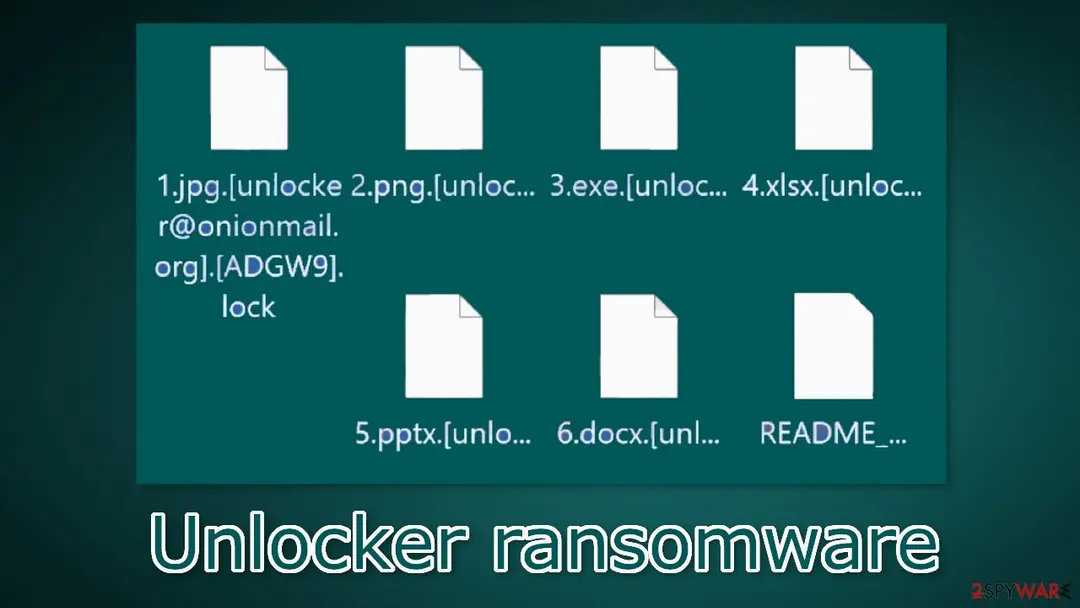
Unlocker ransomware: summary
| Distribution | Email attachments, torrent websites, malicious ads |
|---|---|
| NAME | Unlocker |
| TYPE | Ransomware, cryptovirus, data-locking malware |
| FILE EXTENSION | .[unlocker@onionmail.org].[victim_ID].lock |
| RANSOM NOTE | README_WARNING.TXT |
| FILE RECOVERY | If no backups are available, recovering data is almost impossible. We list alternative methods that could help you in some cases below |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 16 more facts
| MALWARE REMOVAL | Scan your machine with anti-malware software to eliminate the malicious program and all the related files |
|---|---|
| Detection names | No Microsoft detection name is known |
| Contact | unlocker@onionmail.org, unlockersuport@msgsafe.io, nlocker@onionmail.org |
| Encrypted file extension | .lock |
| Decryptor | No free decryptor is known for this variant; check No More Ransom (nomoreransom.org) for updates |
| Damage | Not recorded in the old report |
| Name | Unlocker |
| Type | File-encrypting ransomware |
| Symptoms | Files renamed with a new extension and a ransom note left in folders |
| Evidence | 5 write-ups by security sites; no sample analysed yet |
| Encrypted files | .lock |
| Ransom note | README_WARNING.TXT |
| Attacker contacts | unlocker@onionmail.org |
| Free decryptor | No free decryptor is known (checked 6 October 2026) |
| First seen | 8 April 2022 |
| Facts checked | 6 October 2026 |
- File extension:
.lock - Note file:
README_WARNING.TXT - Contact:
unlocker@onionmail.org
From our report of Apr 2022 · not reviewed since
More from our earlier report on Unlocker
- Malware can cause system errors, crashes, lag, and other stability issues.
The Unlocker ransomware note
Hey!
Can I recover my files? Sure. We guarantee that you can recover all your files easily and safely! But you have to be fast!. How quickly you pay, how quickly all your data will be returned, as before encryption.
To contact write to the mail: unlocker@onionmail.org
Reserved email: unlockersuport@msgsafe.io
Telegram: @unlockersuport
ATTENTION !!!
Do not rename encrypted files.
Do not try to decrypt your data using third party software - this may result in permanent data loss.
We are always ready to cooperate and find the best way to solve your problem.
The sooner you write, the better the conditions will be for you.
Our company values its reputation. We give all guarantees of decryption of your files.
Your personal ID: -
How to remove Unlocker ransomware
Tools you'll need
All of these are free except where noted. Download them on a clean device if the infected PC is offline.
- A USB stick: to keep the ransom note, two or three encrypted files and screenshots off the infected PC.
- Microsoft Defender Offline: built into Windows 11 and Windows 10; scans before Windows starts, so running malware cannot hide.
- Microsoft Safety Scanner: a second, portable scanner with current signatures; each download works for 10 days.
- ID Ransomware: identifies the family from the note and one encrypted file and says whether a decryptor exists.
- No More Ransom: the free decryptors from police and security companies; check it again every few months.
- Fortect (optional): scans Windows for malware and repairs the system files and settings it damaged. The free scan is in the box above.
How to remove Unlocker and get your files back
Work in this order.
Disconnecting comes first, removal comes before any restore, and nothing here asks you to contact the attackers.
Step 1: Disconnect the PC and unplug backup drives
Unlocker encrypts everything it can reach, including drives and shares you connect later. Cut the network first: cable out, or Wi-Fi off from the taskbar.
Then unplug every USB stick and backup disk and pause cloud sync, so the encrypted versions do not replace your online copies. Do not reconnect any of them until the ransomware is removed from the Windows 11 or Windows 10 PC.
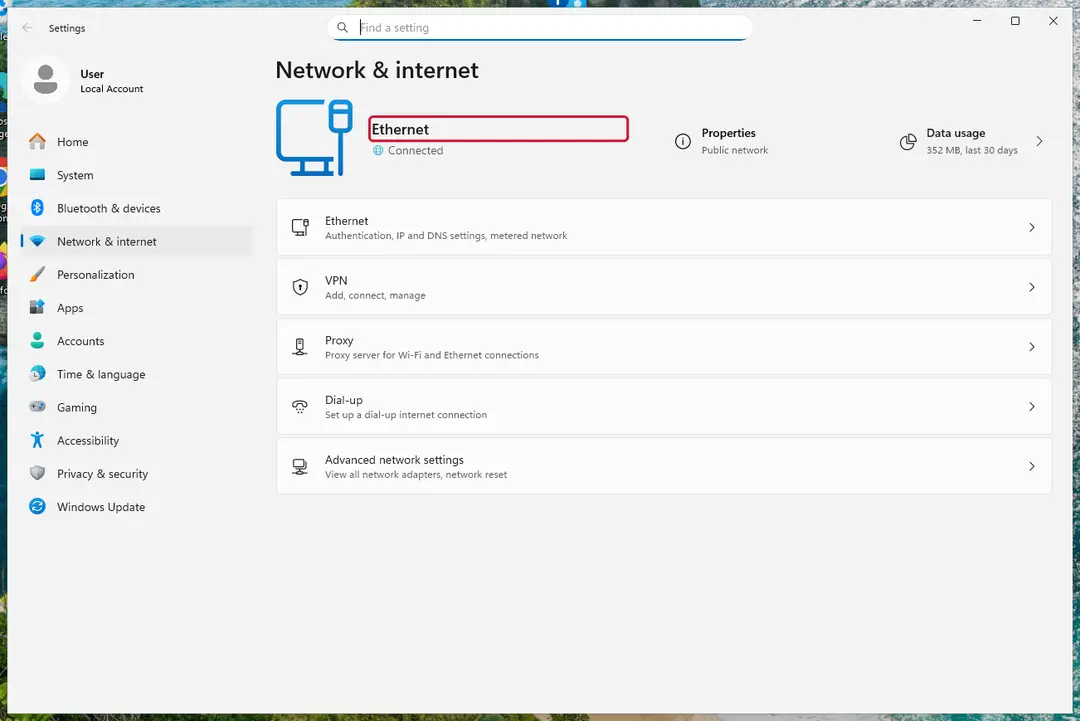
Windows 11: turn off Wi-Fi to take the PC offline. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 2: Save the ransom note and confirm the family
Copy
README_WARNING.TXTand one or two files ending in.lockto a USB stick, and leave the originals where they are.From another device, upload the note and a sample file to ID Ransomware or No More Ransom's Crypto Sheriff, which name the family from the note, the extension and the file structure.
Write down the contact address and your personal ID from the note, because a decryptor or the police may ask for them.
Warning: Never contact the attackers from the infected Windows 11 or Windows 10 PC.
Windows 11: the ransom note and encrypted files to copy for identification. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 3: Check for a free decryptor
For Unlocker, no free decryptor is known (checked 6 October 2026). Search the family name in the No More Ransom decryption tools list and in the free decryptors of Emsisoft, Avast and Kaspersky, because new tools appear years after an attack.
Important: Keep the encrypted files even if nothing works today, and do not pay before every free option is ruled out: payment does not guarantee a working key.
Decryptors run on Windows 11 and Windows 10, but only after the ransomware itself is removed.
Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 4: Remove the ransomware before you restore or decrypt
Restoring or decrypting files while Unlocker still runs lets it encrypt them again. Run a Full scan in Windows Security > Virus & threat protection > Scan options, then the Microsoft Defender Antivirus (offline scan).
If the ransomware blocks Windows Security, start Safe Mode with Networking and scan from there. Some families install a password stealer as well, so let both scans finish on Windows 11 or Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Look for shadow copies of the files
Open Command Prompt as administrator and run
vssadmin list shadows. If it lists copies dated before the attack, right-click a folder with encrypted files in File Explorer, choose Properties > Previous Versions, and open or restore a version from before that date.ShadowExplorer, a free tool, shows the same copies when the tab is empty or hidden. Most current families delete shadow copies, so an empty list is normal, but the check takes two minutes on Windows 11 or Windows 10.
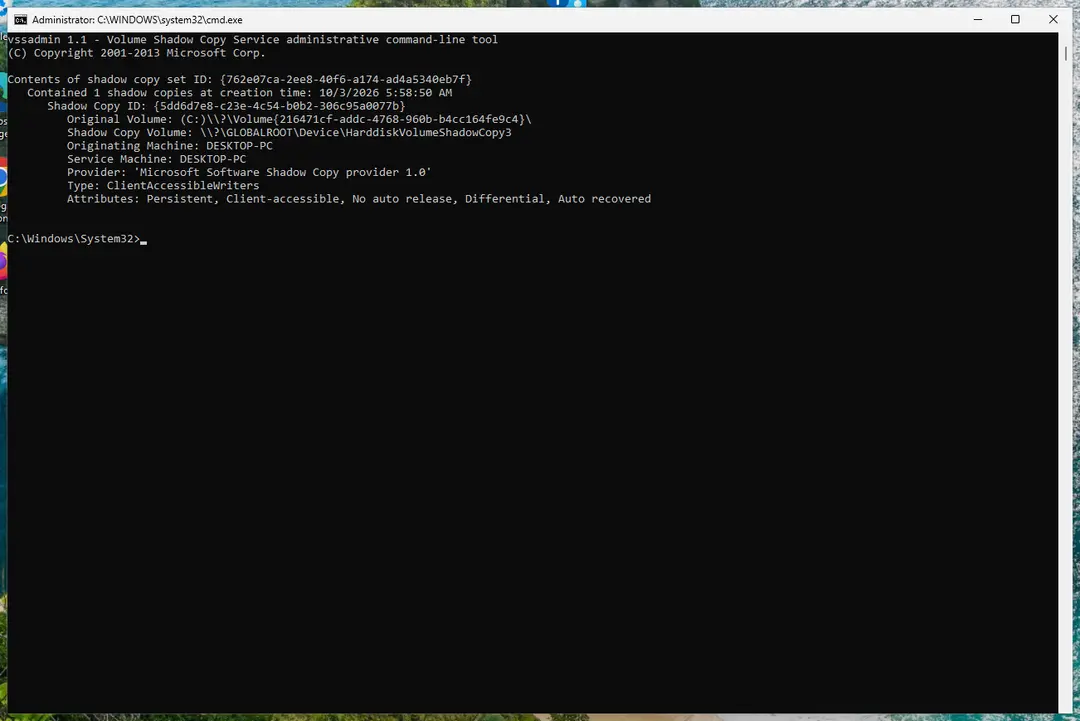
Windows 11: vssadmin list shadows shows whether shadow copies exist. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 6: Restore the files from a backup or recover deleted originals
Restore from an external backup, File History or OneDrive's version history, choosing a date before the attack. Connect the backup drive only after the scans are clean, or the ransomware encrypts it too.
If there is no backup, file recovery software can sometimes find the deleted originals, because some ransomware writes an encrypted copy and deletes the original file.
Stop writing to the drive and try recovery on Windows 11 or Windows 10 before new files overwrite the space.
Full procedure with screenshots: Recover deleted files (Recycle Bin, backups, OneDrive) On uGetFix
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Find a working decryptor for your files
File encryption is a process that is similar to applying a password to a particular file or folder. However, from a technical point of view, encryption is fundamentally different due to its complexity. By using encryption, threat actors use a unique set of alphanumeric characters as a password that can not easily be deciphered if the process is performed correctly.
There are several algorithms that can be used to lock data (whether for good or bad reasons); for example, AES uses the symmetric method of encryption, meaning that the key used to lock and unlock files is the same. Unfortunately, it is only accessible to the attackers who hold it on a remote server - they ask for a payment in exchange for it. This simple principle is what allows ransomware authors to prosper in this illegal business.
While many high-profile ransomware strains such as Djvu or Dharma use immaculate encryption methods, there are plenty of failures that can be observed within the code of some novice malware developers. For example, the keys could be stored locally, which would allow users to regain access to their files without paying. In some cases, ransomware does not even encrypt files due to bugs, although victims might believe the opposite due to the ransom note that shows up right after the infection and data encryption is completed.
Therefore, regardless of which crypto-malware affects your files, you should try to find the relevant decryptor if such exists. Security researchers are in a constant battle against cybercriminals. In some cases, they manage to create a working decryption tool that would allow victims to recover files for free.
Once you have identified which ransomware you are affected by, you should check the following links for a decryptor:
- No More Ransom Project
- Free Ransomware Decryptors by Kaspersky
- Free Ransomware Decryption Tools from Emsisoft
- Avast decryptors
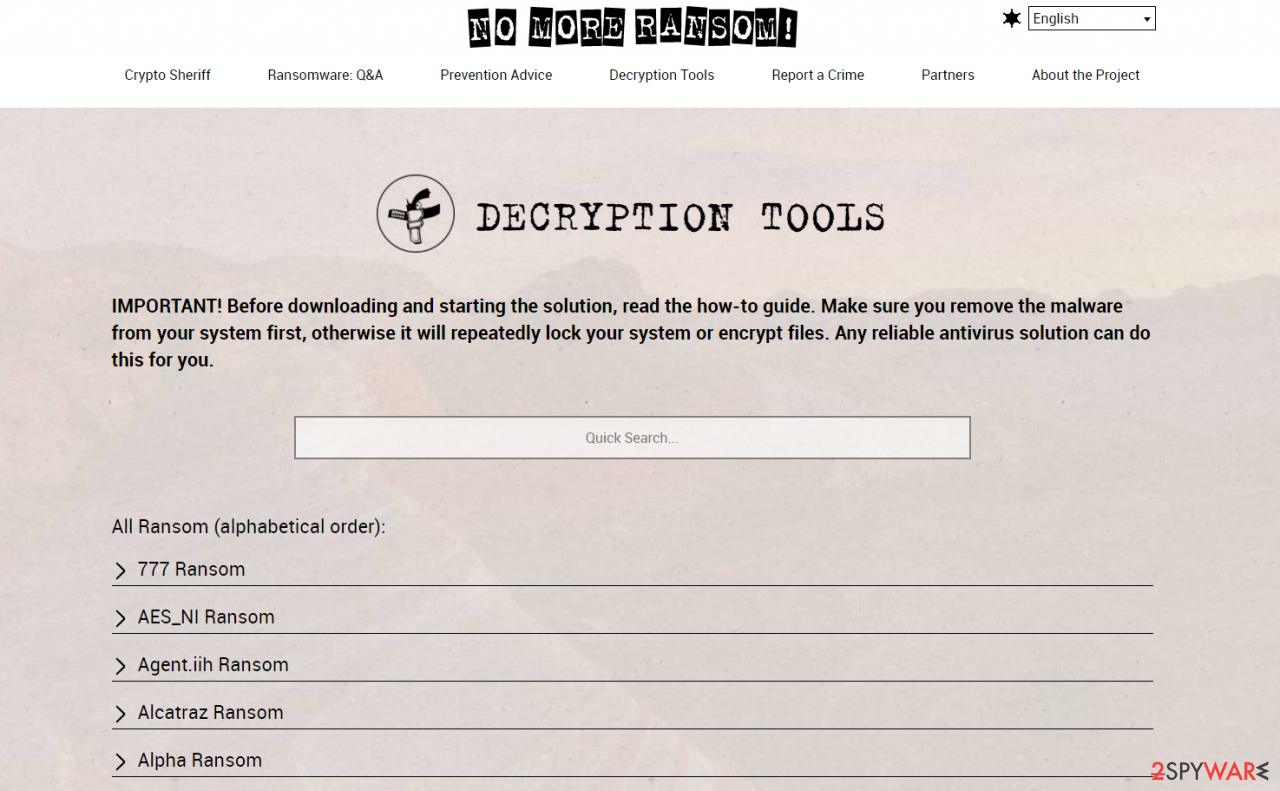
If you can't find a decryptor that works for you, you should try the alternative methods we list below. Additionally, it is worth mentioning that it sometimes takes years for a working decryption tool to be developed, so there are always hopes for the future.
Create data backups to avoid file loss in the future
Report the incident to your local authorities
Ransomware is a lucrative, highly illegal business, and authorities are actively targeting ransomware operators. The level of investigation and follow-up depends on the country, the scale of the incident, and whether the attack is linked to known ransomware groups. To increase the likelihood of identifying the culprits, the agencies need information. In many cases, reports are used primarily for intelligence gathering, trend analysis, and victim support rather than immediate identification of attackers.
Therefore, by reporting the crime, you could help stop the cybercriminal activities and catch the threat actors. Reporting does not guarantee investigation or recovery of data, but it contributes to broader efforts to track ransomware campaigns. Make sure you include all the possible details, including how did you notice the attack, when it happened, etc. Relevant details may also include affected systems, ransom demands, cryptocurrency wallet addresses, and any communication with the attackers. Additionally, providing documents such as ransom notes, encrypted files, or malware executables would be beneficial.
Law enforcement agencies typically deal with online fraud and cybercrime, although it depends on where you live. Here is the list of local authority groups that handle incidents like ransomware attacks, sorted by country:
- USA - Internet Crime Complaint Center IC3
- United Kingdom - ActionFraud
- Canada - Canadian Anti-Fraud Centre
- Australia - ScamWatch
- New Zealand - ConsumerProtection
- Germany - Polizei
- France - Ministère de l'Intérieur
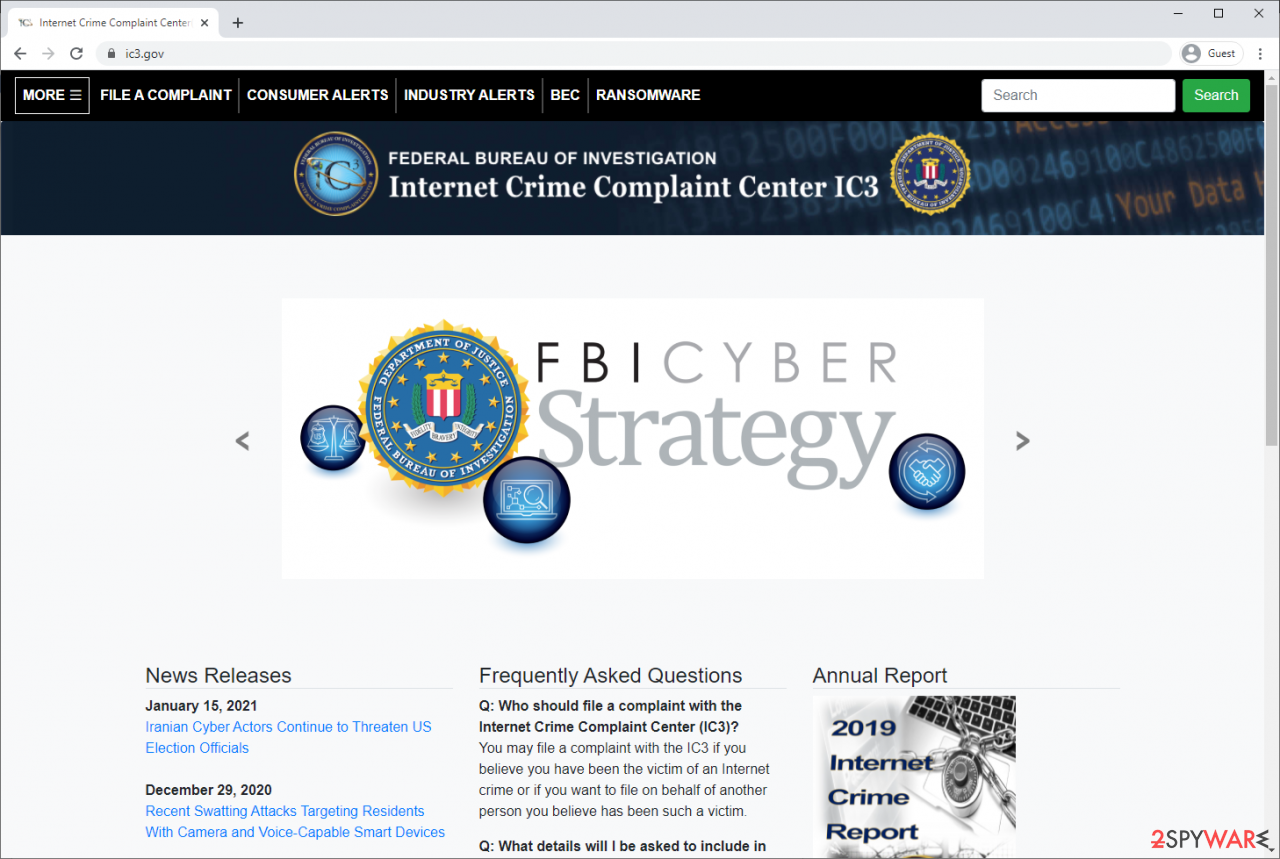
If your country is not listed above, you should contact the local police department or communications center.
Isolate the infected computer
Some ransomware strains aim to infect not only one computer but hijack the entire network. As soon as one of the machines is infected, malware can spread via the network and encrypt files everywhere else, including Network Attached Storage (NAS) devices. NAS devices are commonly compromised via reused administrator credentials and remote access services, and attackers may also delete existing snapshots. If your computer is connected to a network, it is important to isolate it to prevent re-infection after ransomware removal is complete.
In modern environments, ransomware often spreads using stolen credentials, remote management tools, VPN connections, and cloud synchronization services, not only through shared network drives.
The easiest way to disconnect a PC from everything is simply to plug out the ethernet cable. This does not disconnect wireless networks, VPN connections, or cloud services, which must also be disabled separately. However, in the corporate environment, this might be extremely difficult to do (also would take a long time). In many organizations, devices are centrally managed, and network isolation is typically performed by IT or security teams using endpoint security or device management tools. The method below will disconnect from all the networks, including local and the internet, isolating each of the machines involved.
On modern Windows systems, network connections can also be disabled through the Settings app or automatically isolated using endpoint detection and response (EDR) tools.
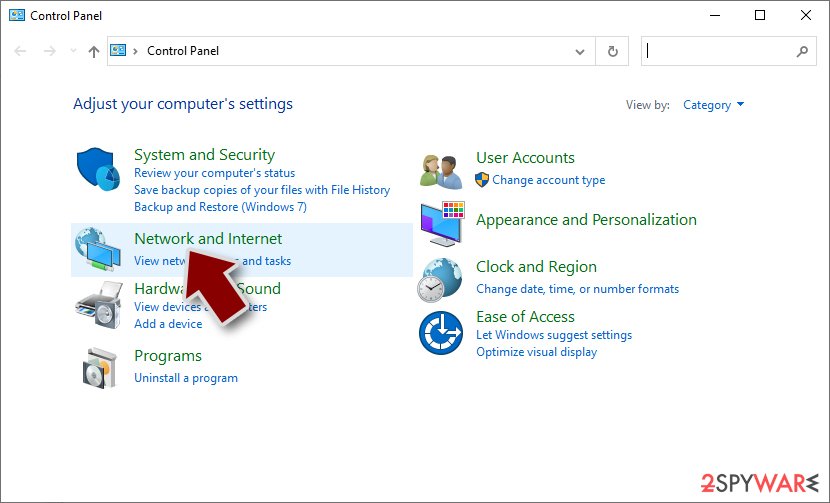
- Type in Control Panel in Windows search and press Enter
- Go to Network and Internet
- Click Network and Sharing Center
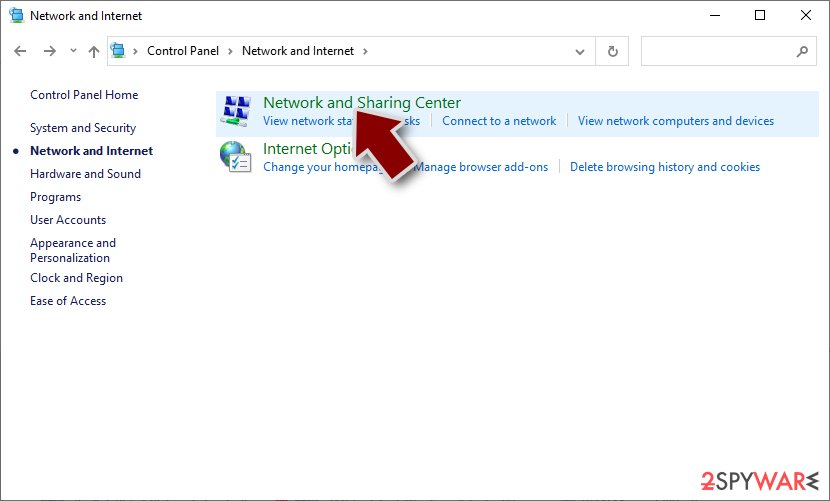
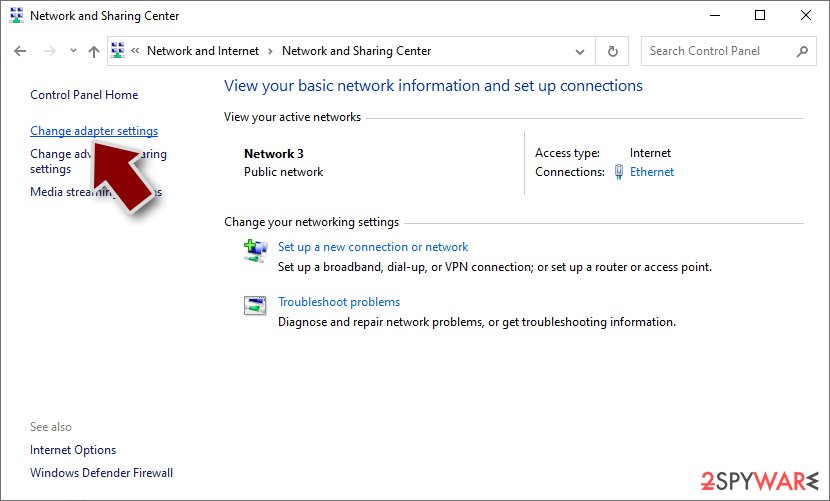
- On the left, pick Change adapter settings
- Right-click on your connection (for example, Ethernet), and select Disable
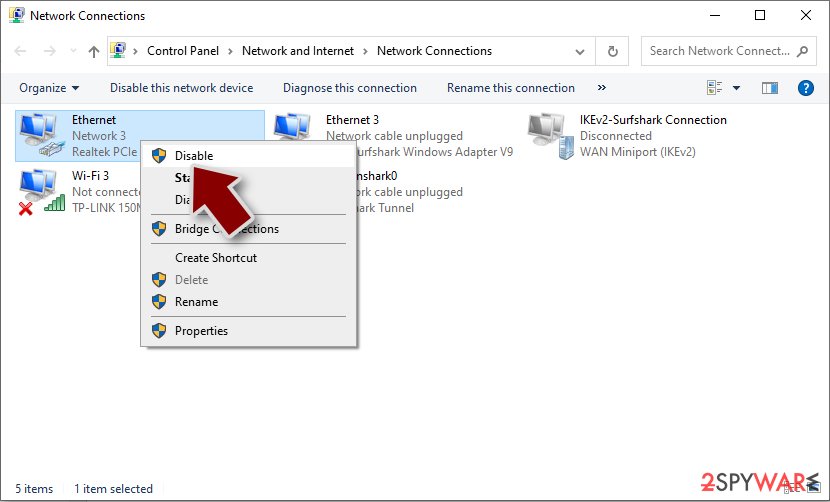
- Confirm with Yes.
If you are using some type of cloud storage you are connected to, you should disconnect from it immediately. It is also advisable to disconnect all the external devices, such as USB flash sticks, external HDDs, etc. Once the malware elimination process is finished, you can connect your computers to the network and internet, as explained above, but by pressing Enable instead. Before reconnecting, credentials should be reset, persistence mechanisms checked, and backups verified to ensure reinfection does not occur.
From our report of Apr 2022 · not reviewed since
Unlocker ransomware blackmails victims into paying a ransom in return for a decryption key
Unlocker ransomware is one of the most recent data-locking malware versions.
Ransomware is very damaging because it locks all of the personal files on the victims' computers and makes them impossible to open. These types of malicious programs have spiked in popularity in recent years because of their nature.
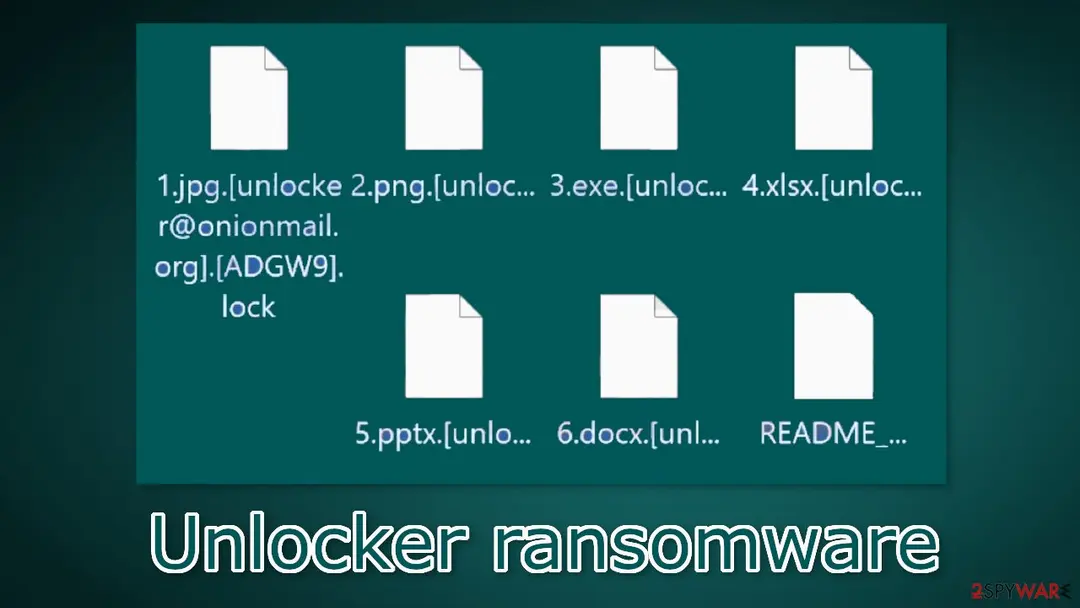
Once the virus enters the system, it begins the encryption process which appends personal files, like photos, videos, and documents with the .lock extension, victim ID, and the cybercriminals' email address.
So if a file was previously named picture.jpg after the encryption process is complete, the name would be changed to picture.jpg.[unlocker@onionmail.org]. .lock. The appearance of the files also gets altered. Users can no longer see the thumbnails, only white pages.
After the encryption is complete, a ransom note README_WARNING.TXT is generated on the victim's device. A ransom note explains what happened to the users' files, and what actions cybercriminals want them to take. Usually, threat actors ask for payment in cryptocurrencies in return for a decryption key.
From our report of Apr 2022 · not reviewed since
The ransom note
Victims are next asked to contact the criminals via email nlocker@onionmail.org.
We do not recommend doing this because ransomware developers cannot be trusted. Threat actors usually choose cryptocurrencies as a form of payment because they cannot be refunded. By paying the money, you risk getting scammed too.
Previous ransomware victims often share their devastating experiences. Many of them never heard back from the cyber criminals after they paid them to get a decryption key or software. By paying the ransom you are also encouraging this criminal activity.
From our report of Apr 2022 · not reviewed since
Distribution methods
- Email attachments - Criminals use clever social engineering tactics to persuade people to download the infected attachments. Sometimes they do extensive research on their targets to make the email seem as legitimate as possible. It is best not to open random email attachments. If it is sent from a person you know, double-check with them through a different platform to see if it was really them who sent it. The file can be delivered in a variety of formats, including a ZIP file, PDF, Word document, Excel spreadsheet, and more.
- Torrent sites - Pirated software is an easy way for ransomware to enter the system. We urge you not to use peer-to-peer file-sharing platforms as they are full of malicious programs. You might think that you are lucky you found software for free that normally costs money but you can never know if that program is safe to install.
- Drive-by downloads - A drive-by download occurs without your knowledge. Unlike many other attack routes, drive-by downloads do not require any action from the user. You do not have to click, open or install anything. Visiting an infected website is all it takes to become a ransomware victim. When users visit the infected website, the malicious content looks for specific vulnerabilities in your device and automatically executes the ransomware in the background.
From our report of Apr 2022 · not reviewed since
Use professional security tools to eliminate malicious files
The thing that you have to do immediately is to disconnect the affected machine from the local network.
Disconnecting the ethernet cable or disabling the Wi-Fi should do the job for home users. If this happened at your workplace, doing that might be complicated, so we have separate instructions for you at the bottom of this post.
If you try to recover your data first, it can result in permanent loss. Malware can also encrypt your files the second time if it is not eliminated first. It will not stop until you remove the malicious files causing it. You should not attempt removing the malicious program yourself unless you have excellent IT skills.
This security software should find all the related files and entries and remove them automatically for you. In some cases, malware can prevent you from using antivirus software, so you need to access Safe Mode and perform a full system scan from there:
Windows 7 / Vista / XP
Windows 10 / Windows 8
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing the F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
- Right-click on the Start button and select Settings.
- On the left side of the window, pick Recovery.
- Click Restart now.
- Select Troubleshoot.
- Go to Advanced options.
- Select Startup Settings.
- Click Restart.
- Press 5 or click 5) Enable Safe Mode with Networking.
From our report of Apr 2022 · not reviewed since
Fix system errors to prevent Windows reinstallation
Performance, stability, and usability issues, to the point where a complete Windows reinstall is required, are expected after malware infection.
These types of viruses can alter the Windows registry database, damage vital bootup, and other functions, delete or corrupt DLL files, etc. Once a system file is damaged by malware, antivirus software will not able to repair it.
This is why was developed. This powerful software can fix a lot of the damage caused by Unlocker ransomware. Blue Screen errors, freezes, registry errors, damaged DLLs, etc., can make your computer completely unusable. By using this maintenance tool, you could avoid Windows reinstallation.
- Download the application by clicking on the link above
- Click on the ReimageRepair.exe
- If User Account Control (UAC) shows up, select Yes
- Press Install and wait till the program finishes the installation process
- The analysis of your machine will begin immediately
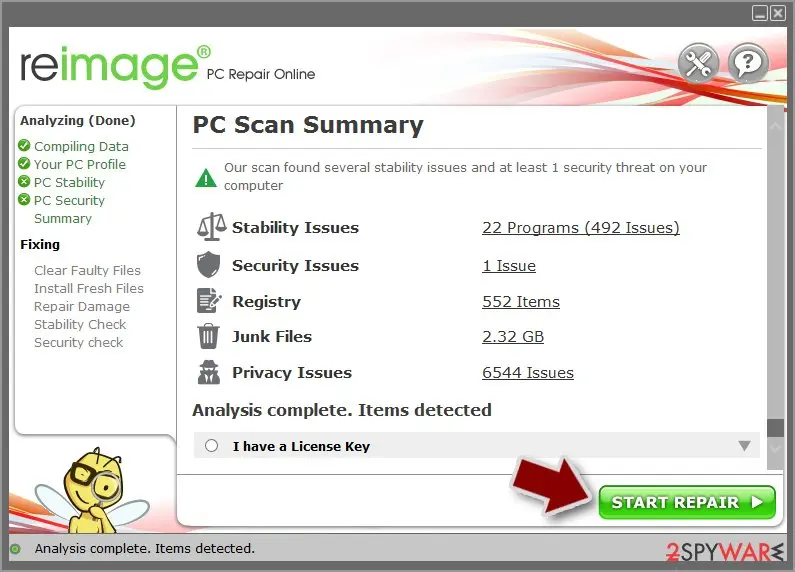
- Once complete, check the results - they will be listed in the Summary
- You can now click on each of the issues and fix them manually
From our report of Apr 2022 · not reviewed since
File recovery options
Many people think that they can fix their files with anti-malware tools, but that is not what they are designed for.
All the security tools can do is detect suspicious processes in your system and eliminate them. The truth is, the files can be restored only with a decryption key or software that only the cybercriminals have.
If you did not back up your data previously, it might be possible that you will never get them back. You can try using data recovery software, but we have to note that third-party programs cannot always decrypt the files.
We suggest at least trying this method. Before proceeding, you have to copy the corrupted files and place them in a USB flash drive or another storage. And remember - only do this if you have already removed the Unlocker ransomware.
Before you begin, several pointers are essential while dealing with this situation:
Install data recovery software
- Since the encrypted data on your computer might permanently be damaged by security or data recovery software, you should first make backups of it - use a USB flash drive or another storage.
- Only attempt to recover your files using this method after you perform a scan with anti-malware software.
- Download .
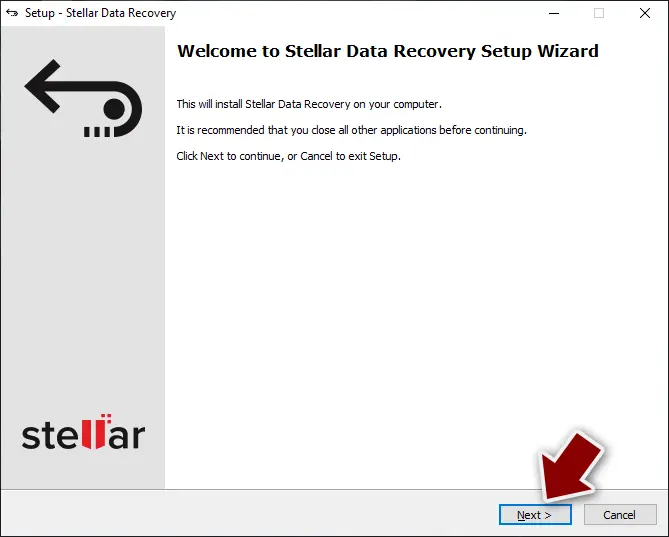
- Double-click the installer to launch it.
- Follow on-screen instructions to install the software.
- As soon as you press Finish, you can use the app.
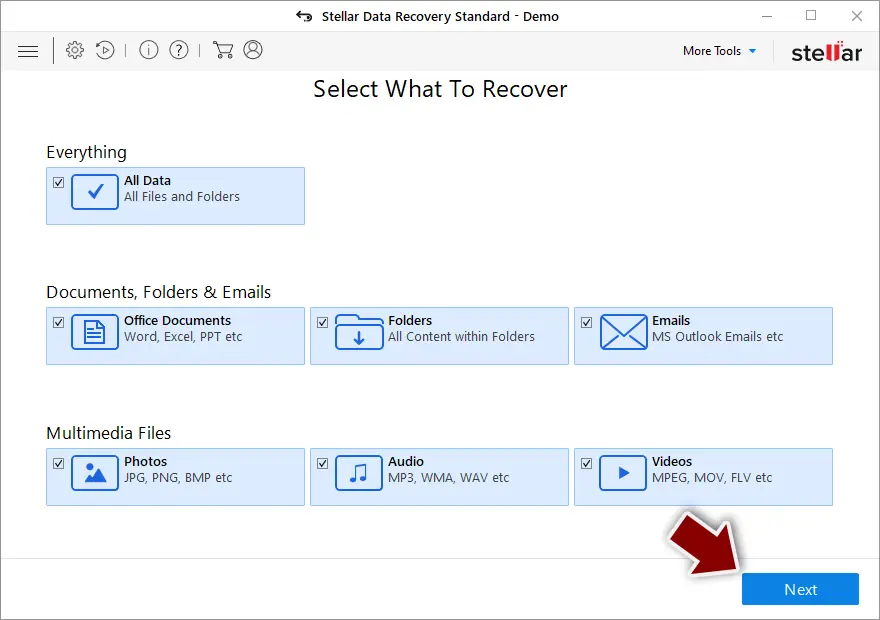
- Select Everything or pick individual folders where you want the files to be recovered from.
- Press Next.
- At the bottom, enable Deep scan and pick which Disks you want to be scanned.
- Press Scan and wait till it is complete.
- You can now pick which folders/files to recover - don't forget you also have the option to search by the file name!
- Press Recover to retrieve your files.
Report it and recover your files
Report it
Report the attack even if you do not expect the files back: insurers and banks ask for the report number, and police use the contacts in the note to link cases.
- United States
- FBI IC3 · FTC ReportFraud
- United Kingdom
- Report Fraud (formerly Action Fraud) · NCSC
- Australia
- ReportCyber (ASD)
- EU countries
- Europol: national reporting sites
Give the victim ID, the note and the date the files were encrypted. A business that holds personal data may also have to notify its data protection authority, in the EU within 72 hours.
Protect the files you restore
Restore only after the scans are clean and the PC no longer shows files that end in .lock and no longer open; otherwise the restored copies can be damaged again.
Then build a backup that survives the next infection:
- one copy in the cloud with version history
- one on an external drive that is disconnected between backups
- the working copy on the PC
Version history matters because a backup that syncs damaged files overwrites the good ones.
How to do this with the tools built into Windows: the 3-2-1 backup rule on Windows.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
Questions about Unlocker ransomware
Is there a decryptor for .lock files?
That depends on the family behind the .lock extension, which this guide cannot confirm yet from the reports alone. Check No More Ransom and ID Ransomware with your ransom note and one encrypted file; they list families with free tools.
If none exists today, keep the encrypted files and a copy of the note on a separate drive, because decryptors are sometimes published months later after flaws are found or servers are seized. Never buy a decryptor from a website that is not the security company that made it.
Should I pay the ransom in README_WARNING.TXT?
Not before you have tried everything else. Identify the family from README_WARNING.TXT and one encrypted file, check No More Ransom for a free decryptor, and look for clean copies in OneDrive, backups and Previous Versions.
Paying funds further attacks, may be illegal if the group is sanctioned, and is no promise of a working key: many victims get partial or broken decryption. If you consider paying for business-critical data, involve the police and a professional incident responder first, and never pay through intermediaries who promise their own decryption.
How do I open .lock files?
You cannot open them by renaming or by choosing another program. The .lock ending shows that Unlocker encrypted the content, and only the matching key can reverse it. Renaming a file back to .docx or .jpg changes nothing except the icon, and it can confuse a future decryptor, so leave the names as they are.
To get the content back, use a backup, an unencrypted copy elsewhere, or a decryptor listed on No More Ransom if one exists for Unlocker. Store the encrypted files on an external disk until then.
Did Unlocker steal my files or passwords?
We do not know yet. Nothing published so far shows data theft by Unlocker, but the only confirmed sign is files that end in .lock and no longer open, which says nothing about what happened before. Many current ransomware attacks copy files or run a password stealer first, so it is wise to act as if they did.
From a clean device, change the passwords that were saved in the browsers on this PC, starting with e-mail and banking, sign out of all sessions and turn on two-step verification. Watch bank statements and account activity for the next few weeks.
Can a data-recovery company decrypt my files for a fee?
Only if a decryptor already exists or the company pays the attackers for you. Some "ransomware recovery" services advertise that they can decrypt families with no known flaw; in practice they negotiate with the attackers and add their own fee. Others use the same free tools listed on No More Ransom.
Before you hire anyone, ask in writing how they will recover the files, whether they will contact the attackers and what happens if they fail. A legitimate service answers clearly. If a free decryptor exists for your family, you can run it yourself.
How did Unlocker get on my computer?
The way Unlocker spreads has not been documented yet, so look at your own recent activity. On home PCs, ransomware most often comes with cracked programs, game cheats, key generators and fake updates, or with an e-mail attachment that was opened. On business networks, attackers usually log in through Remote Desktop with a stolen or guessed password.
Think back to what was downloaded or installed in the days before files that end in .lock and no longer open, and check the Downloads folder and Installed apps sorted by date. Keep anything suspicious for your report, but do not run it again.
Is Unlocker the same as other ransomware with a similar name?
Not necessarily. Ransomware names come from the file extension, the note or a word in the code, so unrelated families often end up with similar names, and one family can appear under several names. The difference matters: a decryptor or advice for one family does not fit another and can damage files.
Compare the ending added to your files and the exact name of the note with the summary table at the top of this guide, then upload the note and one encrypted file to ID Ransomware from a clean device. If the result names another family, follow the guide for that family instead.
What does README_WARNING.TXT tell me about the ransomware?
Quite a lot. The file name README_WARNING.TXT, the wording, the contact addresses and the format of the personal ID are typical for each family. Uploading the note together with one encrypted file to ID Ransomware or No More Ransom's Crypto Sheriff usually names the family within seconds.
That name decides your options: some families have free decryptors, some can be partially recovered, and some cannot be decrypted at all. The note's claims about stolen data should be taken seriously but not at face value.
Should I reinstall Windows after the .lock attack?
Reinstalling removes the ransomware but not the encryption: your files ending in .lock stay encrypted afterwards. So first copy the encrypted files and the ransom note to a separate drive, in case a decryptor appears later. Then decide:
- a clean-up with an offline scan is often enough for home PCs
- while a full reset is safer if remote access was involved
- scans keep finding new items
Restore your backups only after the PC is clean, and change passwords from another device.
Will Fortect remove Unlocker?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Unlocker, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Medium: Ransomware encryption techniques (read October 6, 2026)
- NerdWallet: What Is Cryptocurrency? Here's What You Should Know (read October 6, 2026)
- ZDNet: The 25 most dangerous software vulnerabilities to watch out for (read October 6, 2026)
- CISA: StopRansomware (read October 6, 2026)
- No More Ransom (read October 6, 2026)