
Vagus virus: what it is and how to remove it
Vagus is a type of malware attributed to the RAT category. It is a type of malware that allows attackers to gain remote access and control over a victim's computer, which would allow them to perform all kinds of malicious actions, including stealing sensitive user data via the browser and other installed programs, disabling Windows security software, gaining control over victims' personal accounts, and much more.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If ReimageRepair.exe returns after removal, a full scan can find the entry that brings it back.
Do it yourself · free Remove Vagus virus yourself 3 steps, about 9 minutes, no software needed.
Start the steps
Vagus virus: summary
| Name | Vagus virus |
|---|---|
| Type | Remote Access Tool, Remote Access Trojan, data stealer |
| Infiltration | Can be distributed via software cracks and similar illegal software, malicious websites, fake ads, infected USB drives, etc. |
| Symptos | Can cause slow operation of the system due to the cryptocurrency mining process, system crashes with BSODs, Microsoft Defender malfunctions, etc. |
| Functionality | Collects various sensitive user data Clones browsers, email clients, and other apps to steal personal accounts Uses anti-detection and disables Microsoft Defender Records keystrokes, audio, video, and steals files |
| Detection names | No Microsoft detection name is known |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 7 more facts
| Distribution | Not recorded in the old report |
|---|---|
| Damage | Not recorded in the old report |
| Symptoms | An unknown process in Task Manager |
| Evidence | One write-up by a security site; details still limited |
| File name | ReimageRepair.exe |
| First seen | 18 January 2023 |
| Facts checked | 7 October 2026 |
What Vagus virus does
From our report of Jan 2023 · not reviewed since
What does the Vagus virus do?
Vagus RAT is malware that infiltrates a machine and begins collecting relevant device data.
It employs anti-detection and persistence-ensuring techniques by disabling the Microsoft Defender and Windows Task Manager.
It can also create hidden environments and clone various browsers, email clients, and cryptocurrency wallets in order to gain control over victims' accounts and abuse them for malicious purposes. The gathered login information might be sold to the highest bidder online, or it can also be used to perform phishing attacks against individuals.
Additionally, malware can manage files, infiltrate/execute them, target passwords, record keystrokes, record audio and video, and operate as a cryptocurrency miner. This may seriously slow down the machine and increase the resource consumption to the max in some cases, making Windows operation rather slow or even impossible at times.
The presence of the virus on a device may result in multiple system infections, decreased system performance, data loss, hardware damage, severe privacy issues, financial losses, and identity theft.
If you suspect your computer is infected with Vagus RAT or other malware, it is recommended to use an anti-virus and remove it immediately - we explain how below.
From our report of Jan 2023 · not reviewed since
More from our earlier report on Vagus virus
- Malware might seriously damage some Windows system files, rendering the whole operating system defective.
What Vagus virus collects and where it sends it
From our report of Jan 2023 · not reviewed since
Vagus is a type of malware attributed to the RAT category.
It is a type of malware that allows attackers to gain remote access and control over a victim's computer, which would allow them to perform all kinds of malicious actions, including stealing sensitive user data via the browser and other installed programs, disabling Windows security software, gaining control over victims' personal accounts, and much more.
Since Vagus is a Remote Access Trojan, it can be difficult to know whether you got infected due to its stealthiness, and its removal might also be relatively difficult. That's why we provide all the relative information and instructions on its elimination below, as keeping it installed can seriously compromise one's personal and computer security.
How Vagus virus got on your PC
From our report of Jan 2023 · not reviewed since
Remote Access Trojans are typically spread through phishing emails, malicious websites, software vulnerabilities, and social engineering.
Attackers can use phishing emails to trick victims into downloading and installing the RAT or by embedding a link to a malicious website that downloads the RAT when clicked on. Additionally, they can also be spread by taking advantage of vulnerabilities in software that the victim has installed.
Vagus, on the other hand, is mostly spread via fake links and malicious websites, especially those that distribute repackaged software. Software cracks, torrents, and similar websites are the main culprits of users getting infected. In other cases, the virus was observed attacking users via contaminated USB drives, which is quite an outdated, yet effective method of distribution.
To protect yourself from Trojans such as Vagus, it is important to practice safe browsing habits and to keep your software and operating system up to date. This includes not clicking on links from unknown or suspicious sources and avoiding downloading files from untrusted websites. Additionally, it's also important to have reputable anti-virus software installed on your device, which can detect and remove RATs and other types of malware.
How to check the PC for Vagus virus
- File:
ReimageRepair.exe
How to remove Vagus virus
How to remove Vagus virus and secure your accounts
A stealer usually takes what it wants within minutes and may already be gone.
The scan comes first, then the accounts.
Step 1: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 2: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
From our report of Jan 2023 · not reviewed since
Removal of the virus
Remote Access Trojans are dangerous threats, and they shouldn't be treated lightly.
The longer one of such threats runs on your system, the worse it might become, as all the data you put into your browser or other apps can be stolen at any time. Even your hardware might sometimes malfunction due to RATs.
The easiest way to remove the Vagus virus is by employing powerful security software such as or , as Windows Defender is disabled upon installation of the malicious software. Security software is specially designed to locate all malicious files and remove them at once. Follow these steps:
By employing , you would not have to worry about future computer issues, as most of them could be fixed quickly by performing a full system scan at any time. Most importantly, you could avoid the tedious process of Windows reinstallation in case things go very wrong due to one reason or another.
If malware is interfering with its removal, you can instead access Safe Mode as explained below and perform all the necessary scans from there:
Windows 7 / Vista / XP
Windows 10 / Windows 8
- Download
- Click on the ReimageRepair.exe
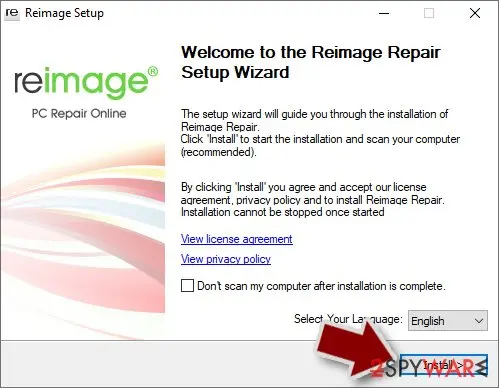
- If User Account Control (UAC) shows up, select Yes
- Press Install and wait till the program finishes the installation process
- The analysis of your machine will begin immediately
- Once complete, check the results - they will be listed in the Summary
- You can now click on each of the issues and fix them manually
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
- Right-click on Start button and select Settings.
- On the left side of the window, pick Recovery.
- Click Restart now.
- Select Troubleshoot.
- Go to Advanced options.
- Select Startup Settings.
- Click Restart.
- Press 5 or click 5) Enable Safe Mode with Networking.
Questions about Vagus virus
Is ReimageRepair.exe safe?
It depends on where the file is and who signed it, not on the name. Open Task Manager, go to the Details tab, right-click ReimageRepair.exe and choose Open file location. A file inside Program Files or System32 with a valid digital signature from a known company is usually part of a legitimate program.
A file in AppData, Temp or ProgramData with no signature, especially one that restarts itself after you end it, is suspicious. If you cannot tie the process to anything you installed, uninstall recent unfamiliar programs and run a Microsoft Defender Offline scan.
ReimageRepair.exe keeps coming back. What should I do?
A process that returns after you end it has a restart mechanism, and that is a reason to treat ReimageRepair.exe as unwanted. Check Settings > Apps > Startup, Task Scheduler and the Services list for entries pointing to its folder, and disable them.
Look in Installed apps for anything added the same day and uninstall it. Then delete the folder and run a Microsoft Defender Offline scan, which works before Windows starts and can remove files that are locked or hidden while the system is running.
Is ReimageRepair.exe a virus?
If your antivirus links ReimageRepair.exe to Vagus virus, yes. The name is used by this spyware, sometimes chosen to look like a system or driver file. Look at the location: a copy in Downloads, a temporary folder or %AppData% with no publisher under Properties > Details is not a genuine Windows file.
Do not run it again to check. Remove it with the offline scan from the plan above, and follow the account steps whether or not the file is still there, because the data may already have been sent.
Should I report a stealer infection?
Report it if money was taken, accounts were used for fraud, or your identity was misused. The report gives you a reference number for your bank and helps police link cases. Also tell the services involved:
- banks
- PayPal
- crypto exchanges and e-mail providers have their own fraud teams that can freeze transfers
- restore accounts
An infection with no misuse yet does not need a police report, but acting on your accounts does. Keep the antivirus log that shows Vagus virus; it helps explain the case.
How can someone log in without my two-step code?
By using a session instead of a login. When you sign in, the site gives the browser a cookie that says you already passed both steps. Spyware like Vagus virus copies that cookie, and the attacker loads it into their own browser, so the site sees a logged-in user and asks for nothing.
The fix is to end all sessions in the account's security settings, which makes the copied cookie worthless, and then change the password. Some services also show active sessions with locations, which helps spot misuse.
What happens to the stolen data?
Stolen data is packed into "logs", one per infected PC. The criminal who ran the stealer uses them directly or sells them in online markets, where others search them for bank, crypto, e-mail, gaming and business accounts.
This can happen days or months after the infection. That is why changing passwords and ending sessions matters even if nothing has happened yet. Breach notification services such as Have I Been Pwned can tell you when your e-mail address appears in known leaks.
Will changing my password stop Vagus virus?
Only part of it. A new password blocks logins with the old one, but stolen session cookies can keep an attacker signed in until you choose to sign out of all sessions.
If the program behind an unfamiliar process called ReimageRepair.exe in Task Manager is still on the PC, it can also steal the new password as you type it. So the order is: clean device for the changes, sign out everywhere, two-step verification on, then clean or reset the affected PC before using it for anything important again.
Should I reset my PC because of Vagus virus?
Only if the signs point to deeper access. Reset when you see an unfamiliar process called ReimageRepair.exe in Task Manager again after removal, when Windows Security cannot start or update, when remote access tools you did not install keep appearing, or when you simply cannot trust the PC any more.
Otherwise, the plan in this guide plus an offline scan is enough. If you do reset, choose Remove everything and Cloud download for a fresh copy of Windows, restore only documents and photos, and reinstall programs from their official sites. Change important passwords from the clean system afterwards.
Can I get back what Vagus virus took?
Accounts, usually yes; money, sometimes. Most services restore an account through their recovery process if you act quickly and still control the e-mail address. Card payments can often be disputed with the bank.
Crypto sent after an unfamiliar process called ReimageRepair.exe in Task Manager is much harder, because transactions cannot be reversed; report it to the exchange the funds went to and to the police, with the wallet addresses and times.
Do not answer offers from "recovery services" that contact you; they are a common second scam aimed at people who just lost funds.
Will Fortect remove Vagus virus?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Vagus virus, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- FTC: How to recognize, remove and avoid malware (read October 7, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 7, 2026)
- Microsoft Learn: How Microsoft names malware (read October 7, 2026)