
Your Windows PC has been infected e-mail scam: how to spot it and what to do
"Your Windows PC has been infected" scam is a deceptive message that users might encounter during their web browsing sessions.
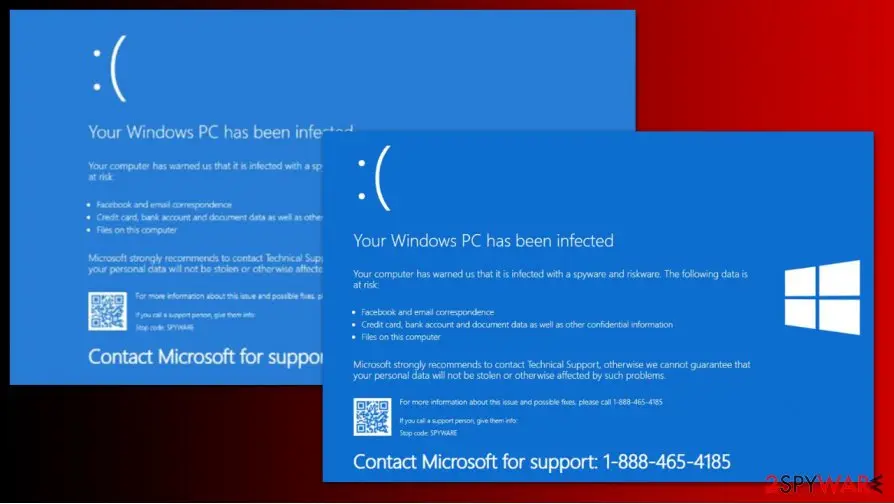
The alert, which tries to imitate the Windows Blue Screen of Death (BSOD) crash window, informs users that their machine has been infected with malware and riskware and that personal information, such as credit card, banking, Facebook login, and personal files located on the computer is in the process of being compromised.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Do it yourself · free Remove Your Windows PC has been infected e-mail scam yourself 4 steps, about 12 minutes, no software needed.
Start the steps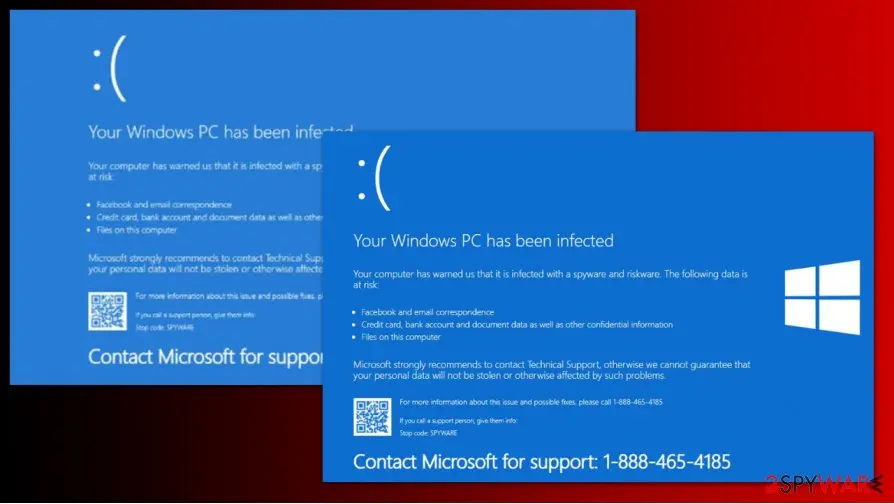
Your Windows PC has been infected e-mail scam: summary
| Distribution | Malicious websites, adware |
|---|---|
| Damage | Financial losses, malware infections, personal file compromise, privacy issues, identity theft |
| Name | Your Windows PC has been infected |
| Type | Fake alert, phishing, tech support scam |
| Related | System Blocked for Security Reasons, Your Device Has Been Blocked |
| Claim | The message claims that the computer has been infected and personal information is at risk |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Aim | To make users call the fake Microsoft Support techniciants and make them pay money for the alleged services |
|---|---|
| Symptoms | A phishing e-mail asking you to sign in and a support phone number shown on screen |
| Evidence | 5 write-ups by security sites; details still limited |
| Arrives as | |
| Pretends to be | Microsoft |
| Asks for | Your password |
| Phone number | 888-984-7569 |
| First seen | 30 September 2020 |
| Facts checked | 6 October 2026 |
How to tell the Your Windows PC has been infected e-mail scam e-mail is fake
- Phone number:
888-984-7569
From our report of Sep 2020 · not reviewed since
More from our earlier report on Your Windows PC has been infected
- You are not in danger, as long as you do not engage with the fraudulent message in any way.
- Simply close down the tab to leave the page.
- If you are unable to, call up the Task Manager and shut down the process of your web browser.
- If you called fraudsters and paid money, contact your bank and try to revert the payment.
- If your security software flagged something, you should also reset the installed web browsers and perform system fix with tools like
Is Your Windows PC has been infected e-mail scam dangerous? What the senders want
From our report of Sep 2020 · not reviewed since
"Your Windows PC has been infected" is a scam that tries to trick Windows users into calling a fake tech support
"Your Windows PC has been infected" scam is a deceptive message that users might encounter during their web browsing sessions.
The alert, which tries to imitate the Windows Blue Screen of Death (BSOD) crash window, informs users that their machine has been infected with malware and riskware and that personal information, such as credit card, banking, Facebook login, and personal files located on the computer is in the process of being compromised.
Allegedly, users need to contact Microsoft support by calling 1-888-984-7569, 1-888-465-4185 (or another) number in order to resolve this issue.
However, "Your Windows PC has been infected" is a regular technical support scam that attempts to mislead users about their computer safety status and scare them by threatening with sensitive data compromise. If contacted, cybercriminals would attempt to offer users useless but expensive software, ask for a remote connection to install data-stealing malware and charge for allegedly provided support services.
Warning: Therefore, never call the provided number, and quick the malicious page without thinking twice.
One of the first signs of "Your Windows PC has been infected" BSOD deception is that it is actually not a Blue Screen of Death. These stop errors occur when Windows has to shut down to prevent damage to software or hardware on the computer (in case you encounter legitimate errors frequently, you can use to fix them automatically).
However, the "Your Windows PC has been infected" scam notification shows up within the web browser instead. The truth is, no diagnostics about your machine can be performed by a website - even by Microsoft itself. Thus, if you see a suspicious URL trying to convince you about virus infections and asking you to call alleged support - don't, as you will get scammed and lose money.
Besides, while the legitimate error messages can be imitated precisely, it is important to note that Microsoft, Google, or any other reputable tech company would never provide tech support contact information within such an alert. If you are worried, you should instead visit the official website and retrieve the phone number from there.
While you might encounter the "Your Windows PC has been infected" scam alert seemingly out of nowhere, one of the most common reasons for suspicious redirects and ads is adware.
This ad-supported software can come in various formats, including browser extensions or programs installed on the system either deliberately or not. The latter case usually happens due to a deceptive marketing technique called bundling, where several programs are offered within a single installer and some components deliberately hidden.
Nonetheless, one of the primary ways to remove "Your Windows PC has been infected" notifications, as well as other suspicious browser activities, is to uninstall the suspicious program from your system. Thus, you should check your browser extensions and the Programs & Features section, as listed below.
If you chose to perform a full system scan with tools such as or and nothing was detected, you should not be worried anymore. Just as a precautionary measure, you can delete web browser cache/data or reset Google Chrome, Mozilla Firefox, Safari, MS Edge, or another web browser that you are using.
From our report of Sep 2020 · not reviewed since
"Your Windows Is Infected" popup - an older variant of a popular scam
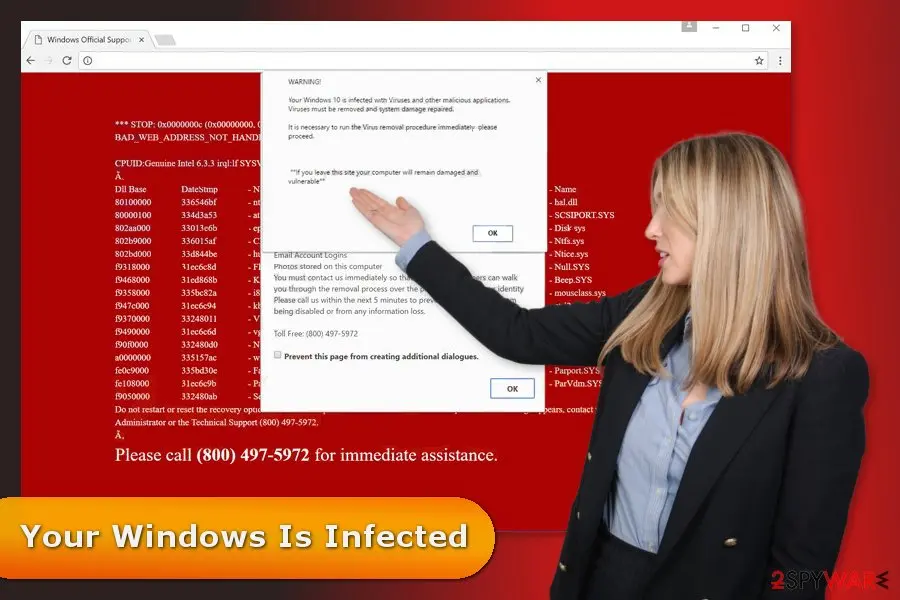
"Your Windows Is Infected" is a fake alert that asks to contact tech support service for immediate help to recover the computer from a potential threat.
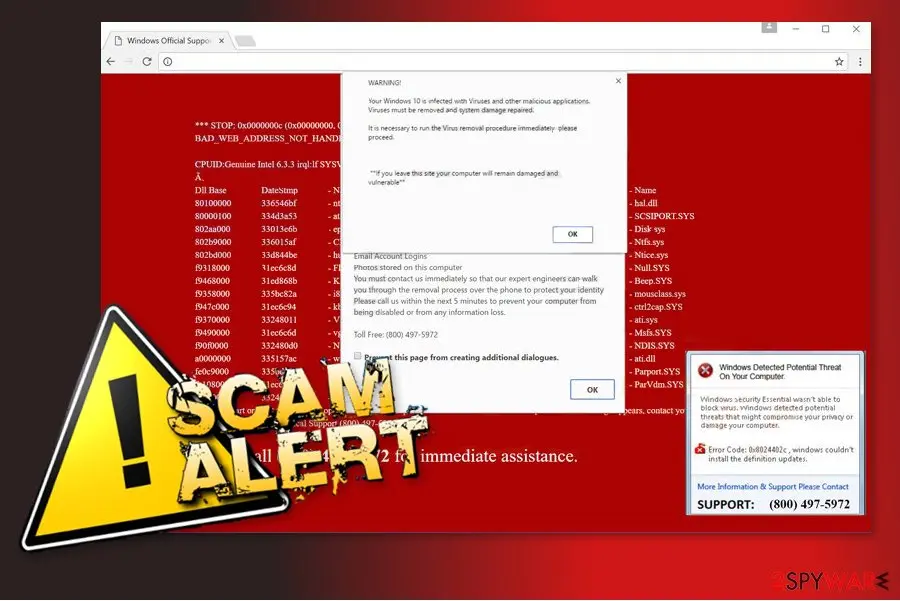
This warning shows up in the new browser's window.
In the background of the malicious website, users can see unknown symbols on the red background. Once a person visits such site, it also delivers a warning popup saying that Windows 10 is infected with viruses and other malicious applications.
"Your Windows Is Infected" virus also tells that people need to perform virus removal immediately. But if they leave this website, the computer will remain "damaged and vulnerable." However, it's just another tactic used by crooks in order to convince users into calling a fake support line.
Cyber criminals as people to contact a "certified technician" by dialing (800) 497-5972. Although the first instinct might encourage to grab your phone, you should not do it for several reasons:
Nevertheless, "Your Windows Is Infected" uses the name of Microsoft; you should never forget that they do not have a phone support line. Thus, seeing such alert should not trick you to call criminals. No one knows what exact purposes they might have. Most likely, you will suffer from cyber crime.
The same malicious website also provides a fake Windows Defender notification. The alert says that Windows Security Essential failed to block the virus. Thus, in order to protect privacy and computer, users have to call the support line.
To make this scam to look more realistic, crooks also included an error code 0x8024402c. However, this error has nothing in common with the scam you're dealing with.
However, seeing such security alerts warns that your computer might be at risk. Redirects to the malicious site usually are triggered by an adware program that managed to infiltrate the system without your knowledge.
The quickest way to locate adware is to scan the computer with the anti-malware program. At the end of the article, you will find a guide that will help to remove "Your Windows Is Infected" entirely.
- this phone called might be charged more than a regular call;
- crooks might offer to purchase useless security software;
- crooks might ask to install remote access tool in order to "fix the problem" quicker;
- your PC might get infected with malware;
- you might unintentionally reveal private information, such as credit card details.
From our report of Sep 2020 · not reviewed since
Fake Windows alert might be triggered by an adware program
The research revealed that behind redirects to "Your Windows Is Infected" usually stands an adware program.
This potentially unwanted application may have entered the system during the recent installation of freeware.
To avoid similar cyber infections, you have to always opt for Advanced/Custom software installation instead of Basic/Standard. One of the steps will include pre-selected third-party apps that you need to unmark.
Additionally, "Your Windows Is Infected" scam might be spread via potentially dangerous sites. Thus, once you visit an adult-themed, gambling or illegal video streaming site, it might force you to visit this tech support scam site.
The virus is noticed spreading in the United Kingdom, the United States and several countries in Europe. What is more, it is expected to spread further.
From our report of Sep 2020 · not reviewed since
Getting rid of "Your Windows Is Infected" virus scam
To remove "Your Windows Is Infected" malware from the computer, you need to find and delete adware program that is responsible for redirecting to this scam site.
We highly recommend opting for the automatic removal option and dedicate this task for anti-malware.
However, we are aware that not all of you are willing to use additional tools to get rid of the adware. In order to help you, we created a manual "Your Windows Is Infected" removal instructions. Please follow them attentively.
If you decide to terminate this threat manually, make sure that you delete all adware-related components from the computer and web browsers. Leaving some entries installed may allow continuing these annoying activities.
What to do after the Your Windows PC has been infected e-mail
If you only received the message and clicked nothing, step 3 is all you need.
If you clicked the link or typed anything on the page it opened, do every step, starting with the password.
Step 1: Change the password you typed on the fake page
If you entered a password after clicking the link in the Your Windows PC has been infected message, treat that account as known to the sender.
Open the provider's real site by typing its address yourself, not through any link in the e-mail, and change the password there. Choose a new one you have never used before, and change it on every other account that shared the old one.
Then use the option to sign out of all other sessions or devices, if the provider has one. This works the same in any browser on Windows 11 and Windows 10.
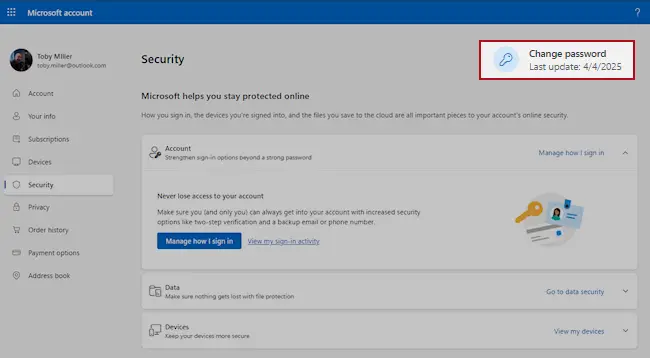
Microsoft account, Security page (account.microsoft.com/security): Change password. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Turn on two-step verification
Two-step verification asks for a code from your phone or an authenticator app whenever someone signs in from a new device. A stolen password alone is then not enough to open the mailbox.
Turn it on in the security settings of the e-mail account first, then for the bank, shop and social accounts that send their reset links to that address.
While you are there, check the recovery e-mail and phone number and the forwarding rules, which attackers sometimes change to keep access. The settings pages look the same on Windows 11 and Windows 10.
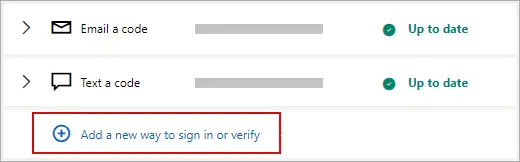
Microsoft account: Manage how I sign in, where two-step verification and the sign-in methods are. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Report the e-mail and delete it
Report the message instead of only deleting it. In Outlook choose Report > Report phishing, in Gmail the three-dot menu > Report phishing; the provider then blocks the same message for other people.
Do not reply and do not click anything else in it. On a work account, forward it to your IT team as an attachment first. Web mail and the mail apps on Windows 11 and Windows 10 offer the same options.
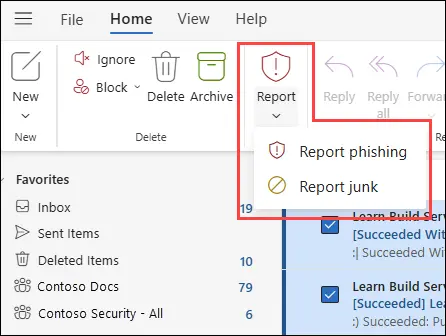
New Outlook for Windows and Outlook on the web: Report > Report phishing. Full procedure with screenshots: Report a phishing e-mail
Step 4: Scan the PC if you opened a file from the message
A page that only asked for a password installs nothing, so most readers can skip this step.
If the Your Windows PC has been infected e-mail or the page it opened made you download or open a file, delete it and run a full scan, then a Microsoft Defender Offline scan.
In Windows 11 and Windows 10 open Windows Security > Virus & threat protection > Scan options, select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts and the scan takes about 15 minutes, so save your work first.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
The instructions below will help you to locate all suspicious entries that are responsible for "Your Windows Is Infected" malware.
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
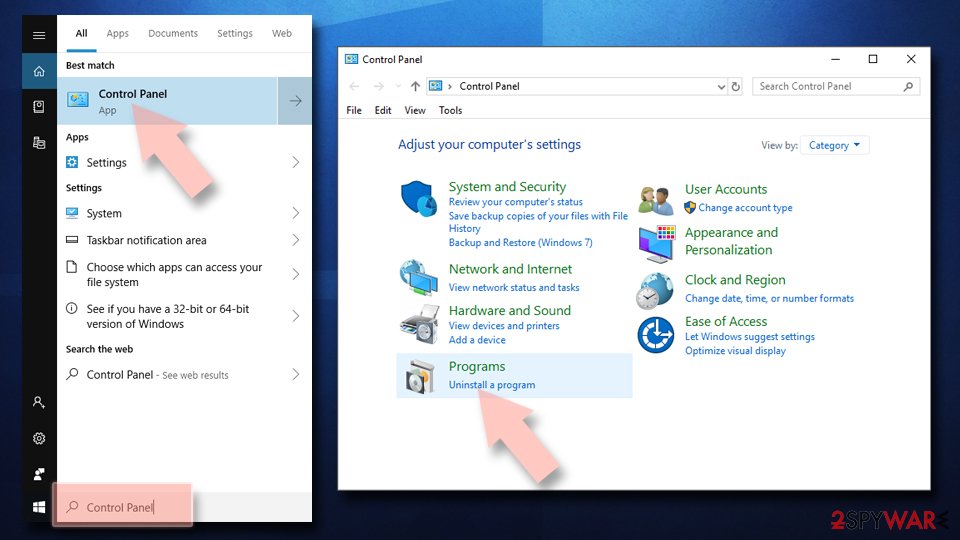
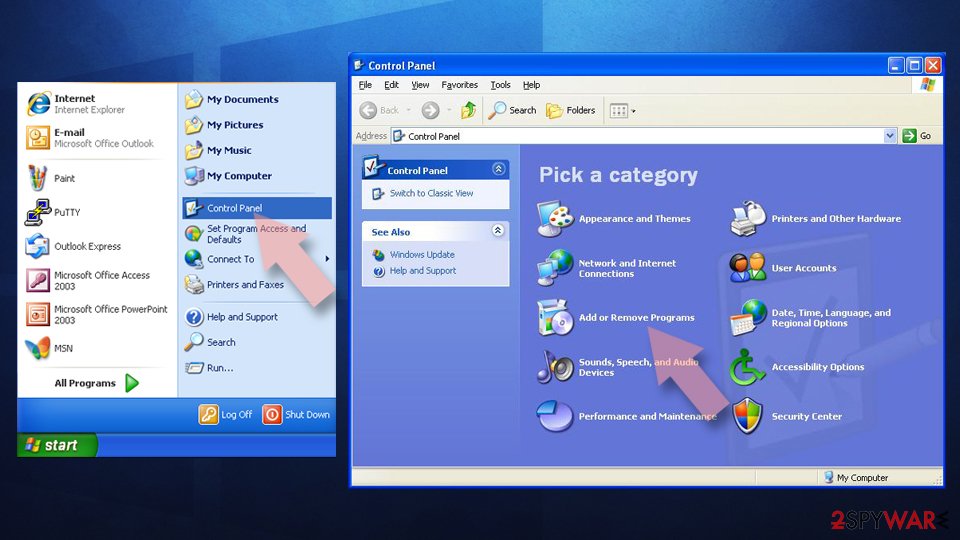
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
Remove the unwanted program:
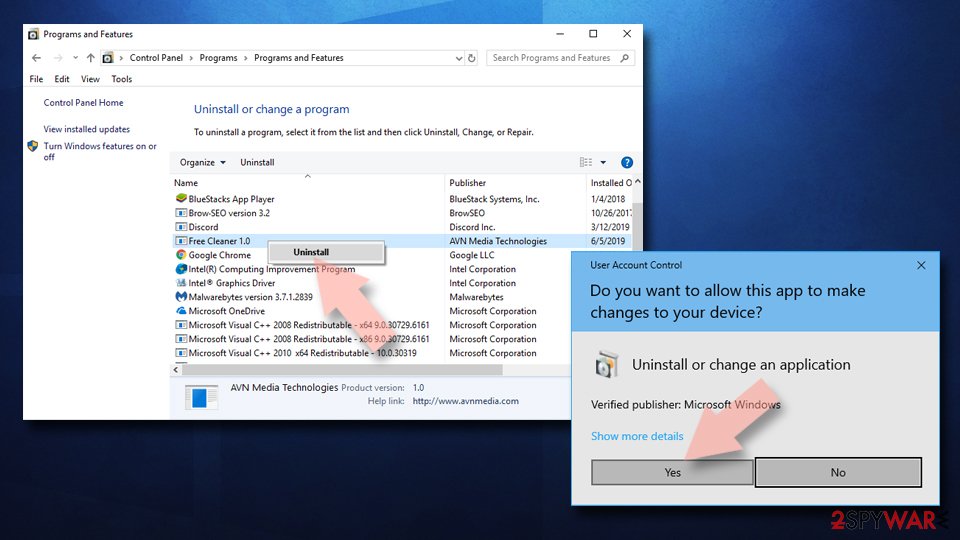
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
"Your Windows Is Infected" adware may have installed numerous extensions and tracking cookies to Chrome. Follow the steps to remove them all:
Delete malicious extensions from Google Chrome:
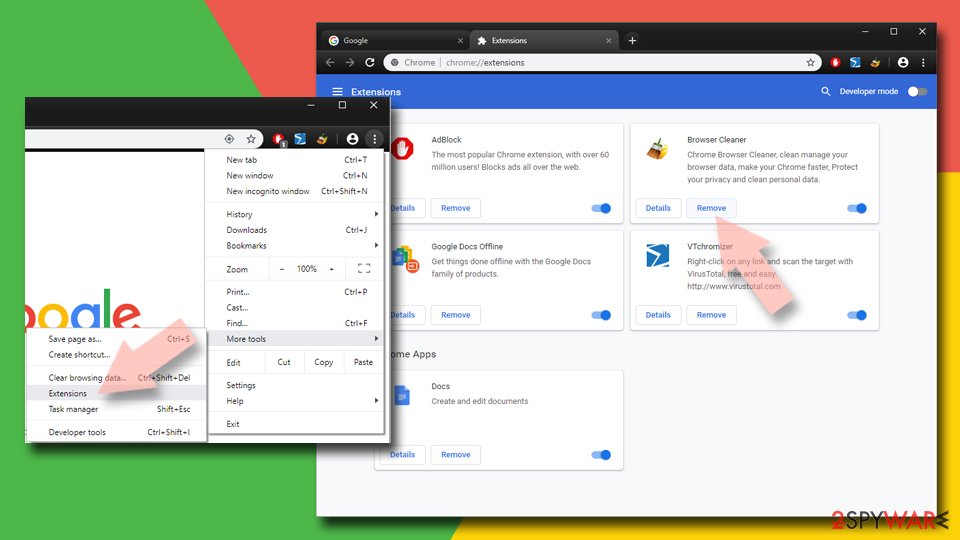
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
Clear cache and web data from Chrome:
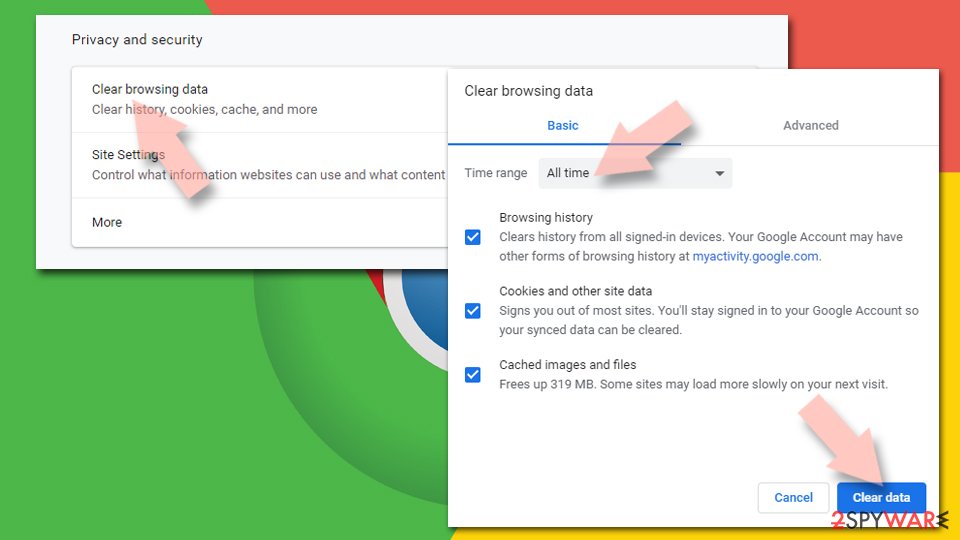
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
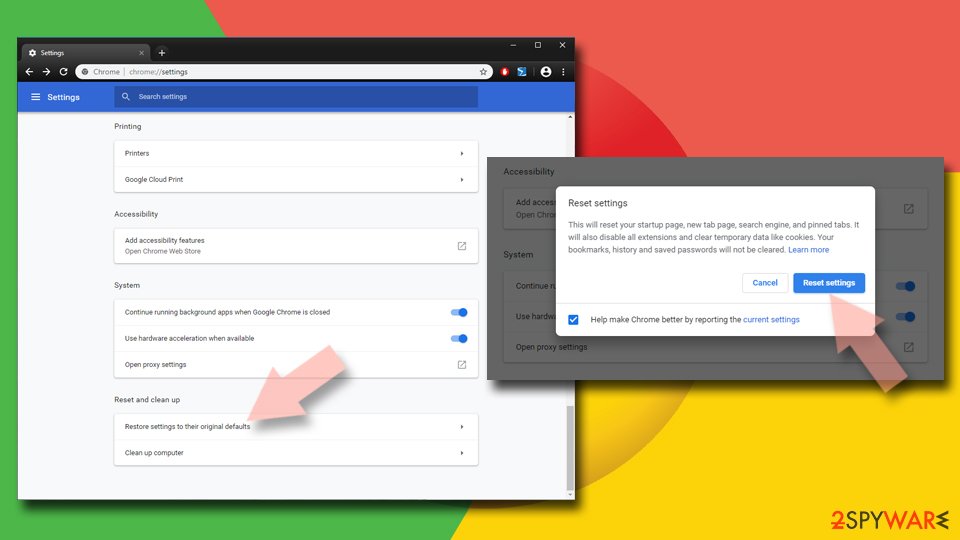
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Microsoft Edge
Follow the instructions to end up redirects to this tech support scam website.
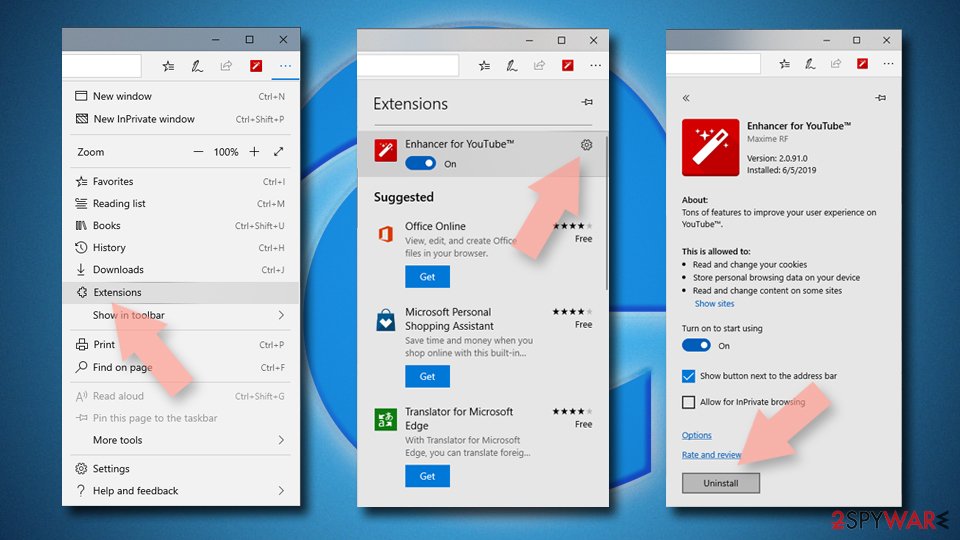
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.
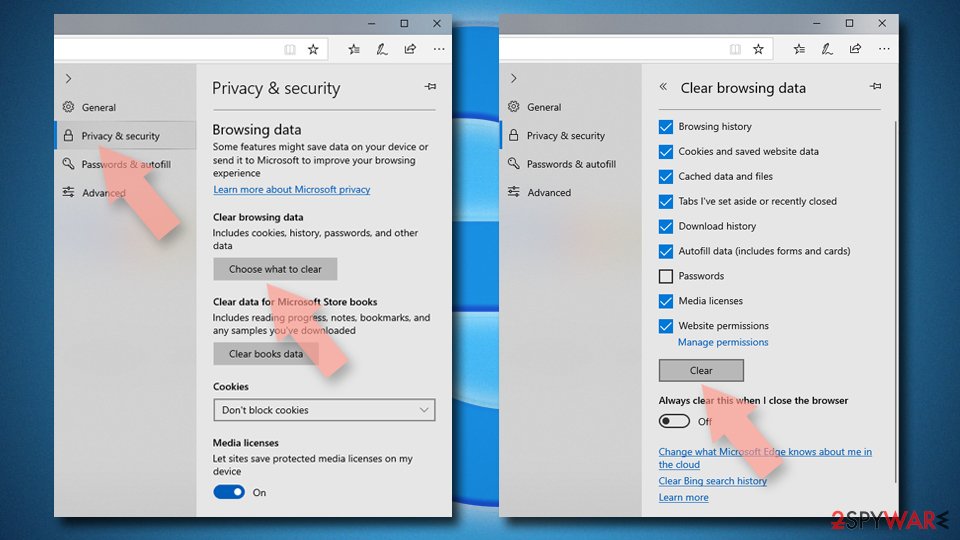
Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.
Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
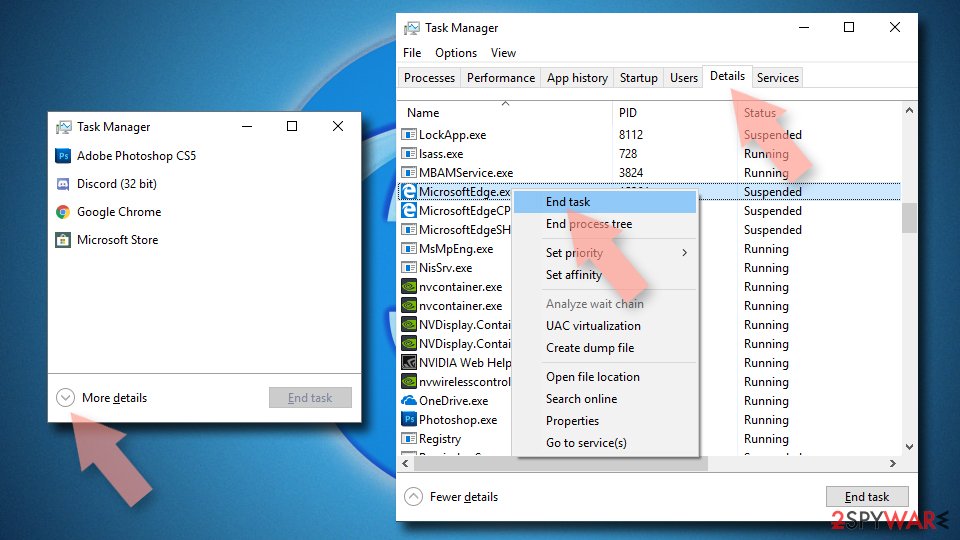
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.
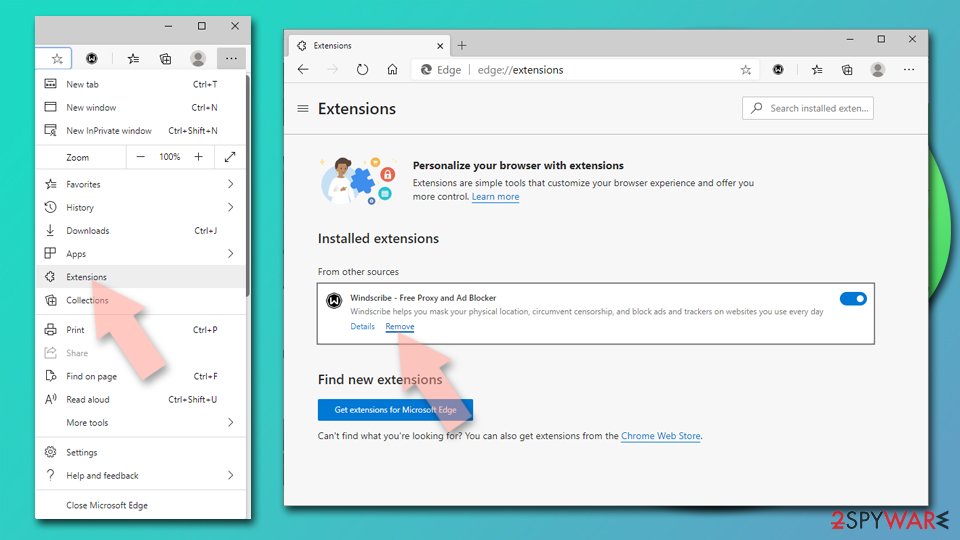
Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
Clear cache and site data:
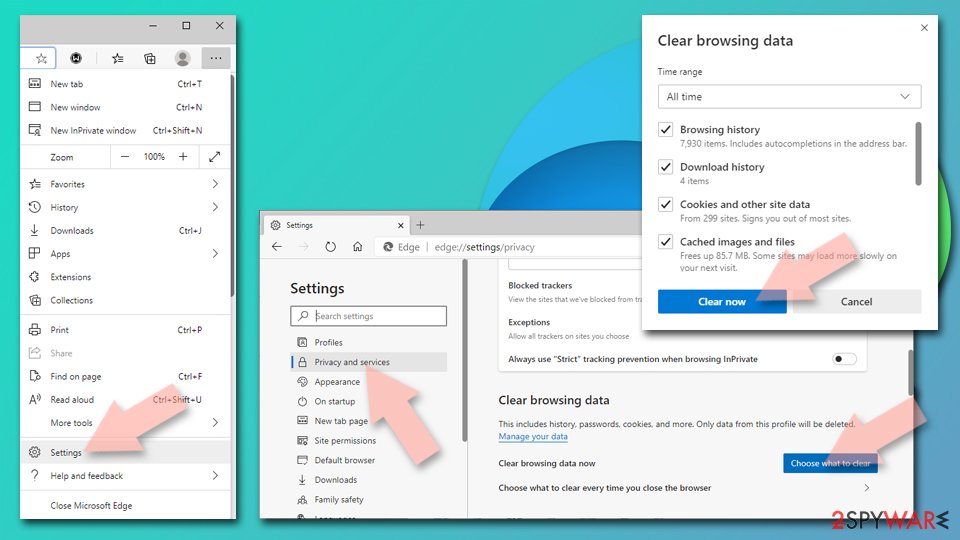
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
Reset Chromium-based MS Edge:
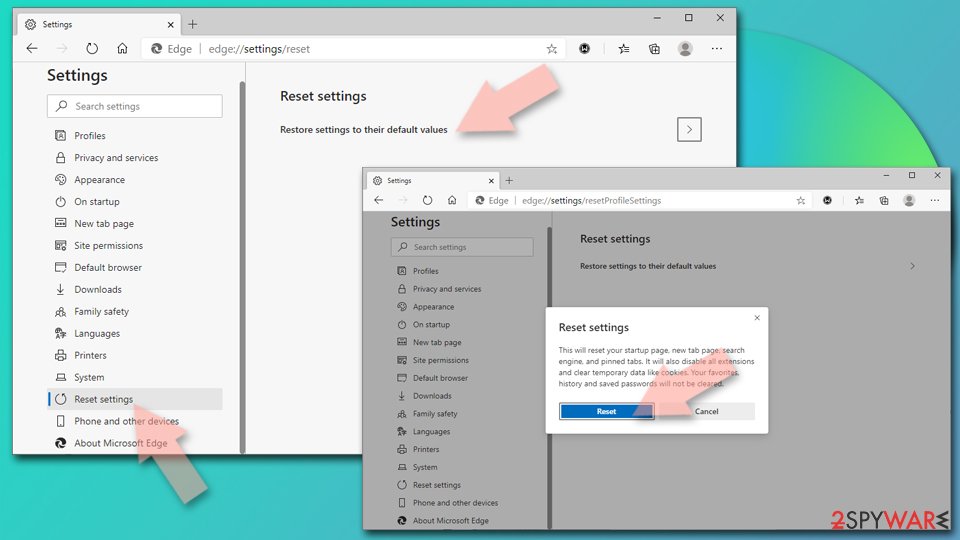
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.
Remove from Mozilla Firefox (FF)
Make sure that any suspicious extensions and add-ons haven't been installed to Mozilla Firefox. Then reset the browser. It helps to clean browser from all "Your Windows Is Infected" components.
Remove dangerous extensions:
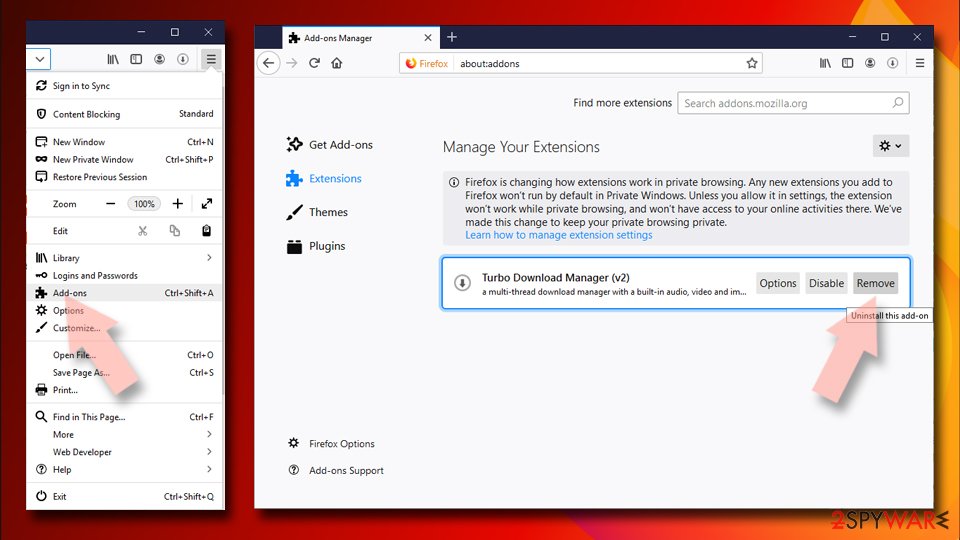
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
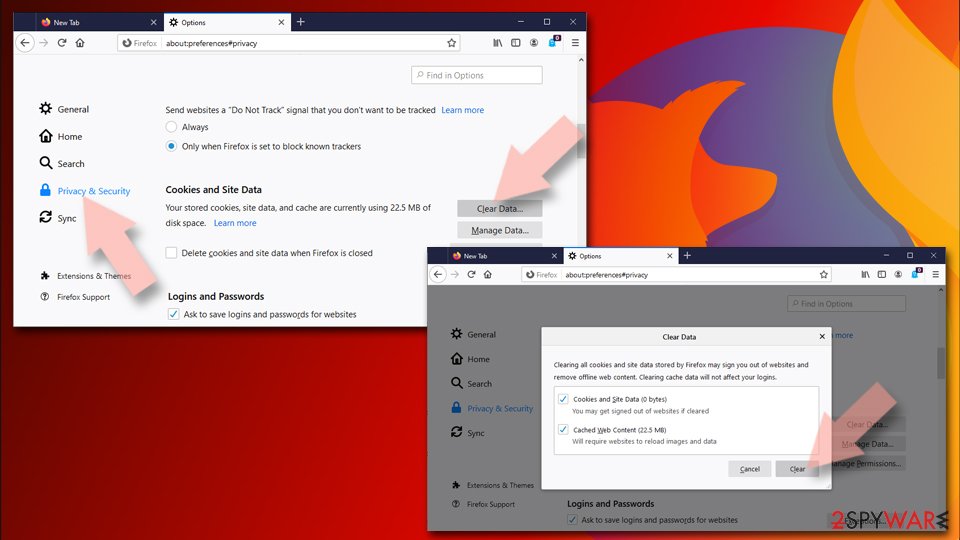
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
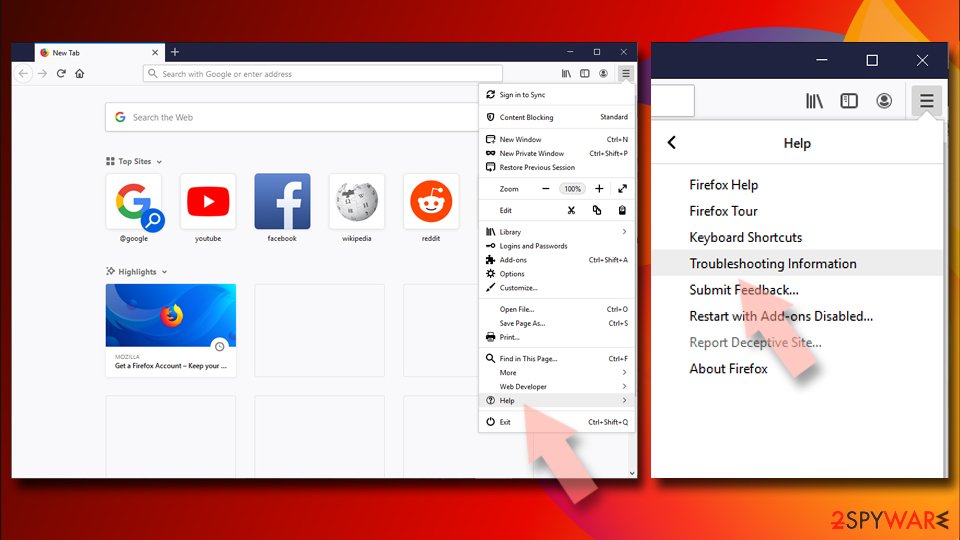
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
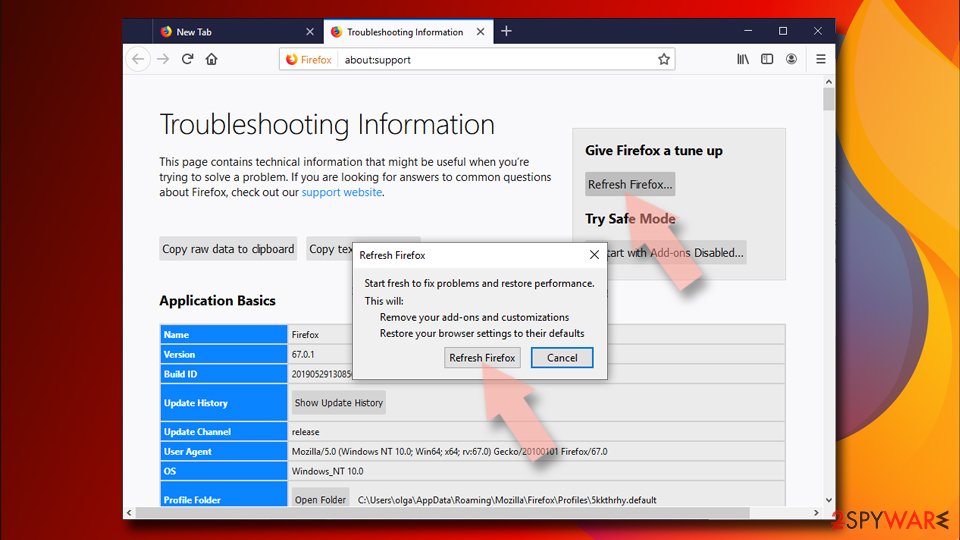
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
Remove dangerous extensions:
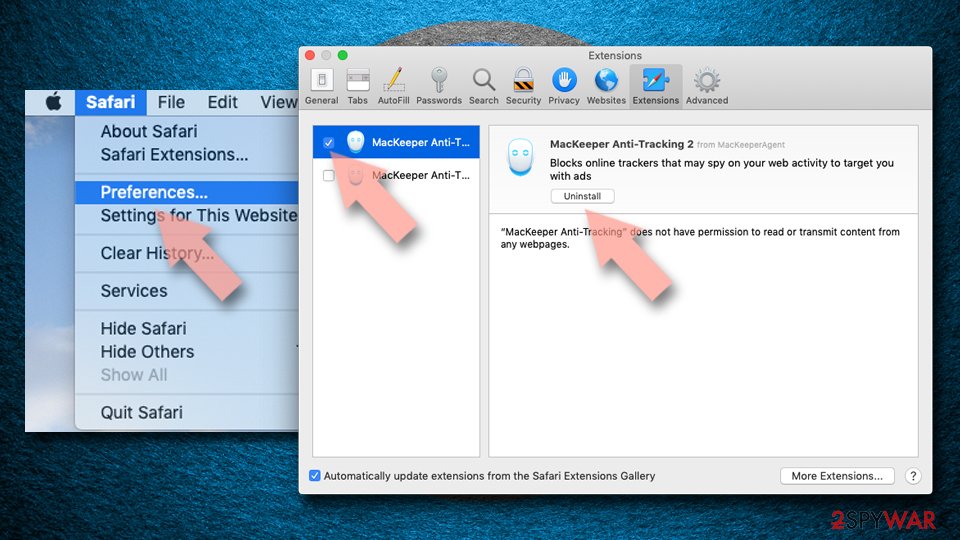
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
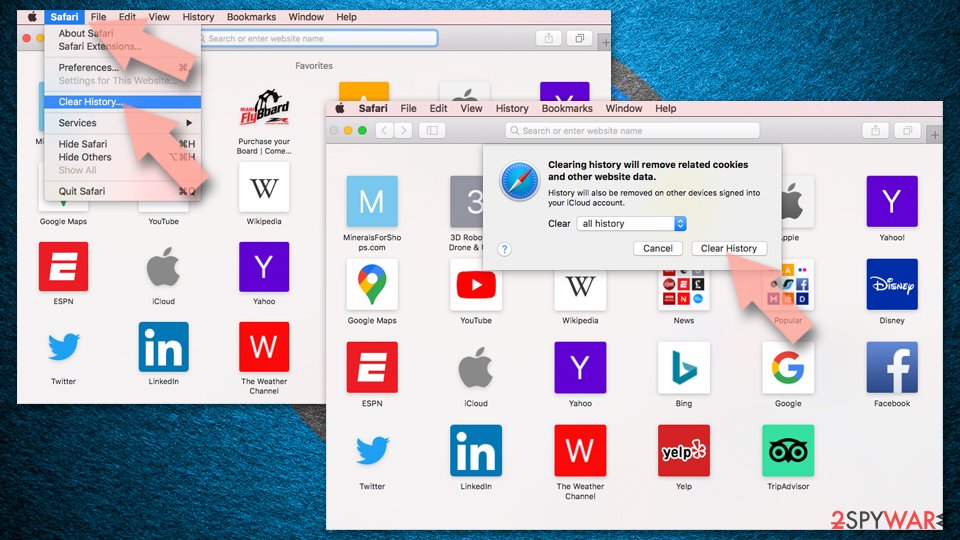
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
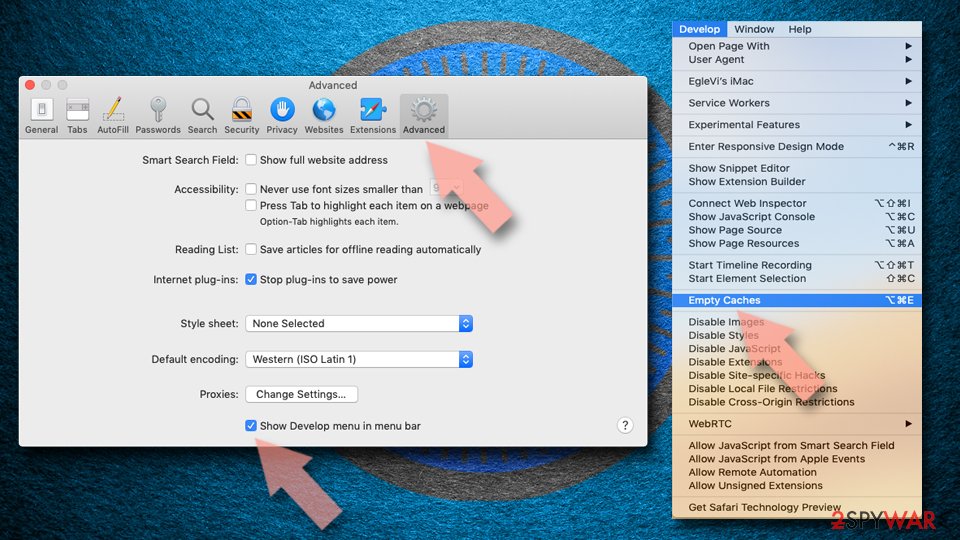
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
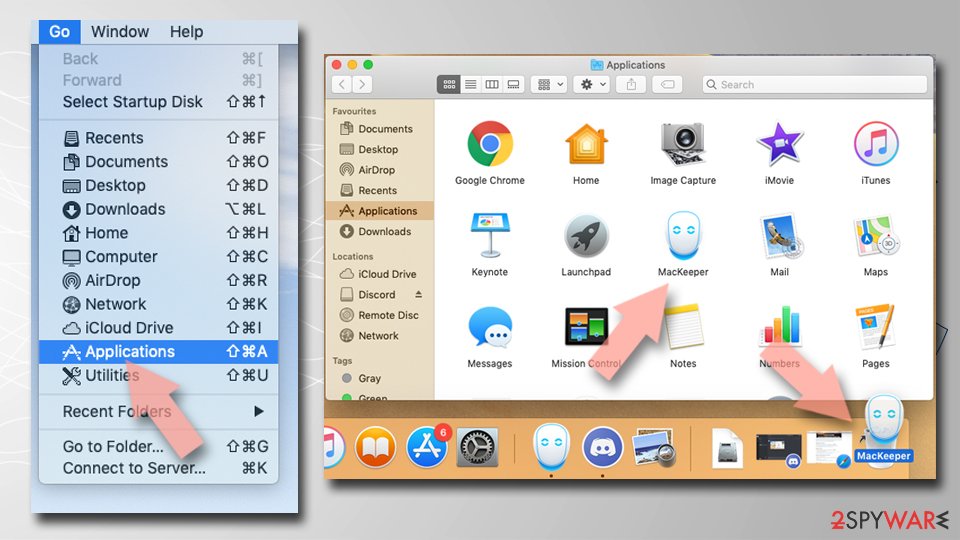
Remove the unwanted application:
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
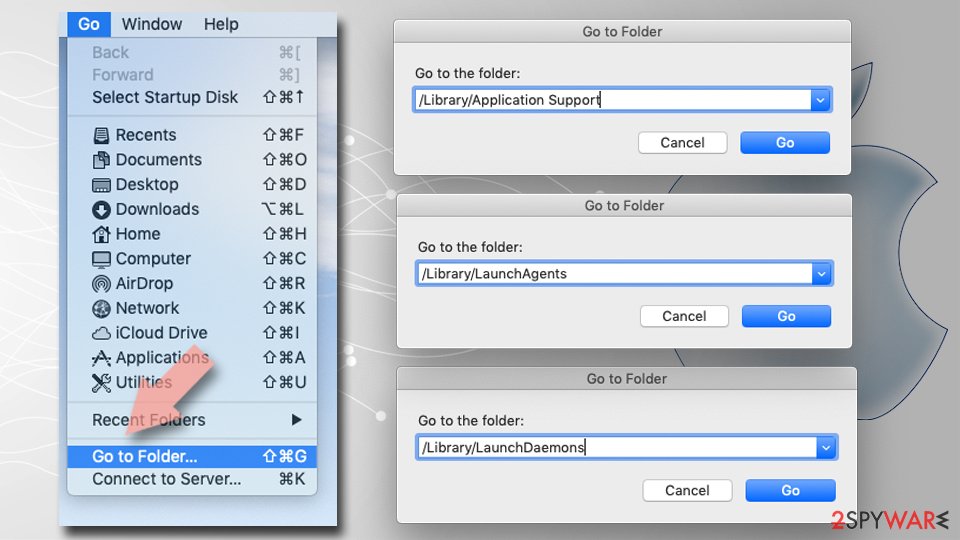
Delete leftover files and folders:
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Reset Internet Explorer
Redirects to the malicious site might be triggered by suspicious add-ons. Follow the steps to get rid of them:
Remove dangerous add-ons:
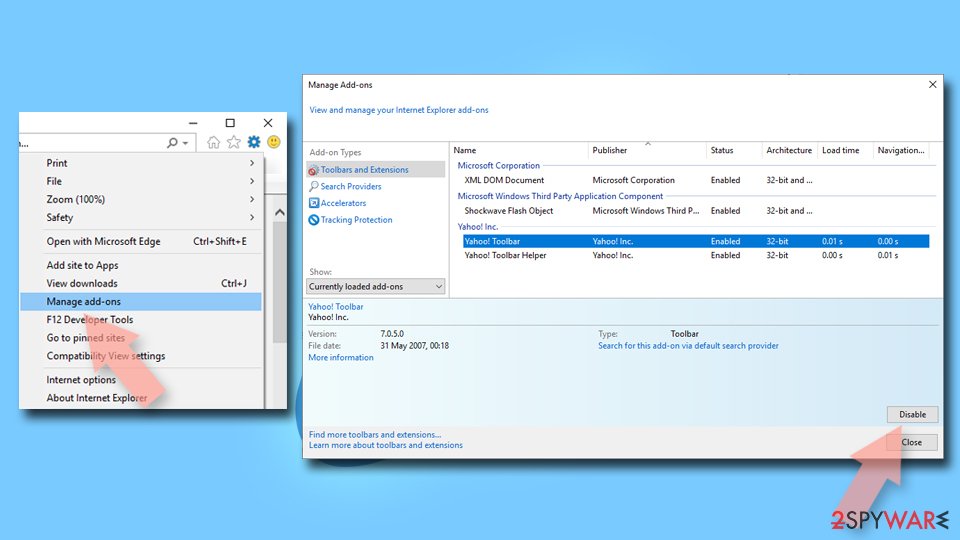
- Open Internet Explorer, click on the Gear icon (IE menu) on the top-right corner of the browser
- Pick Manage Add-ons.
- You will see a Manage Add-ons window. Here, look for suspicious plugins. Click on these entries and select Disable.
Change your homepage if it was altered:
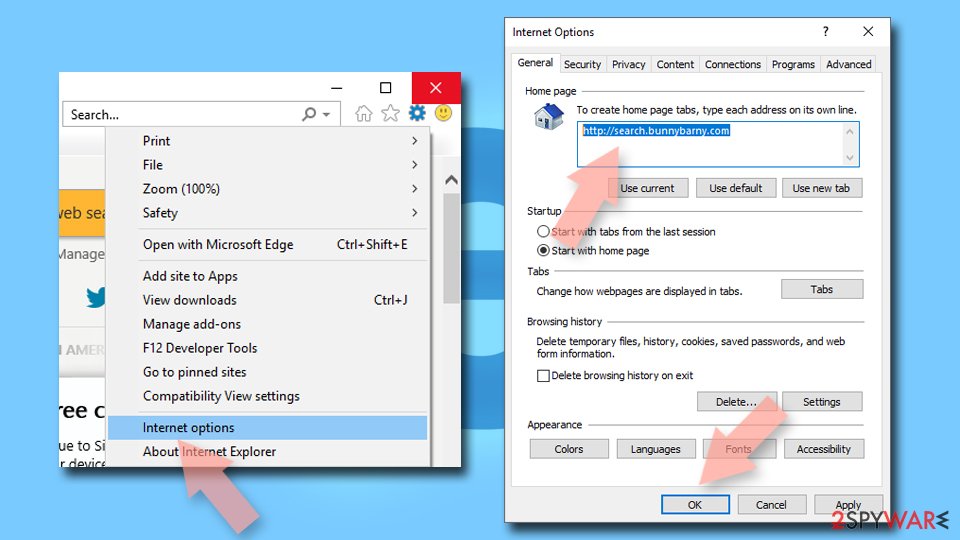
- Open IE and click on the Gear icon.
- Select Internet Options.
- In the General tab, delete the Home page address and replace it by your preferred one (for example, Google.com).
- Click Apply and then select OK.
Delete temporary files:
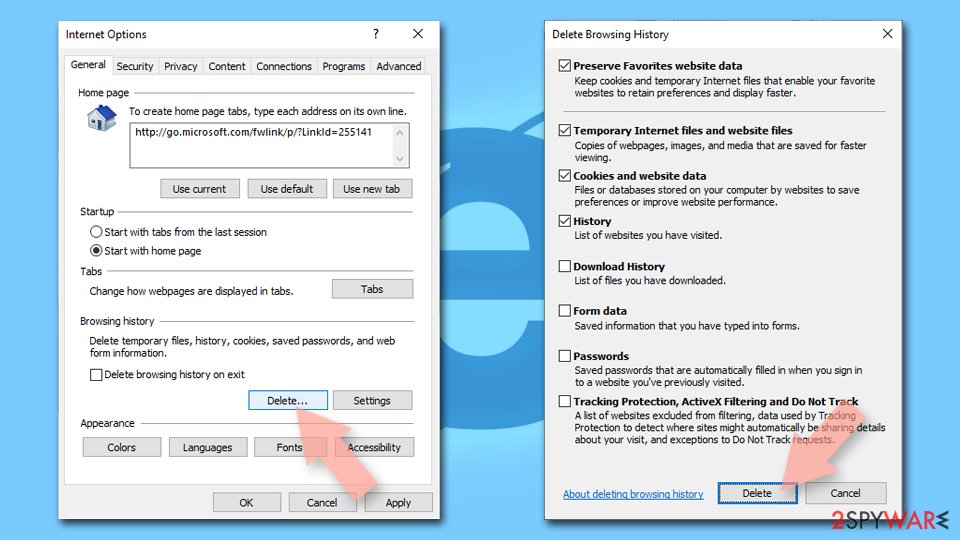
- Press on the Gear icon and select Internet Options.
- Under Browsing history, click Delete...
- Select relevant fields and press Delete.
Reset Internet Explorer:
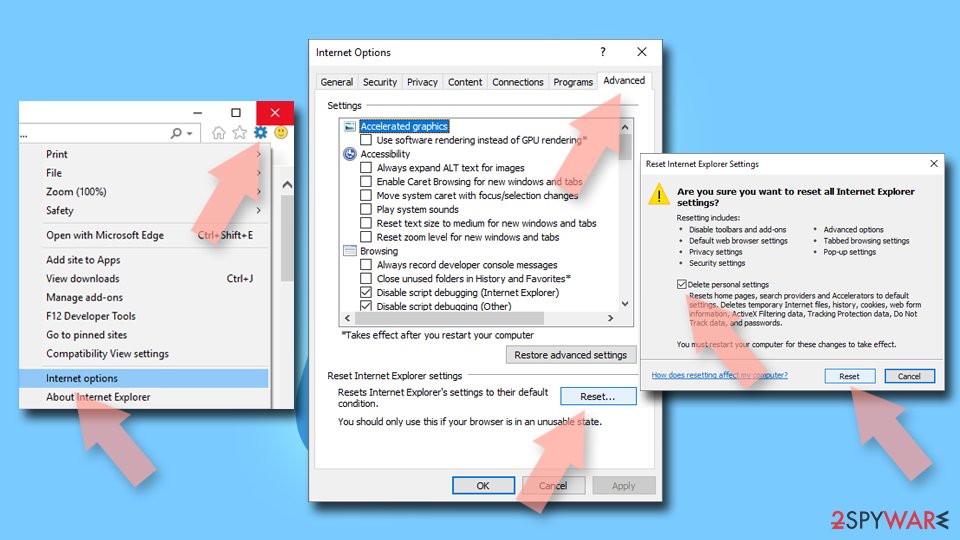
- Click on Gear icon > Internet options and select Advanced tab.
- Select Reset.
- In the new window, check Delete personal settings and select Reset.
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
Questions about Your Windows PC has been infected e-mail scam
Can I trust the people at 888-984-7569?
No. They may sound professional, know your Windows version and show you real system screens, but all of that is part of a sales script. The aim of the people behind 888-984-7569 is to get remote access to your PC and money from you, sometimes repeatedly through "refund" tricks.
Anything they found was invented or normal, such as warnings in Event Viewer that every Windows PC has. Hang up, do not let them connect and do not pay. If you have already done so, disconnect the PC from the internet and work through the steps for callers in this guide.
They called me back from 888-984-7569 offering a refund. Is it real?
No. The refund call is a second scam by the same people. They say they will return your money, ask you to log in to online banking while they are connected, then claim they sent too much and ask you to send the difference back, by transfer or gift cards.
In reality they moved your own money between your accounts or edited the page. Hang up on any call from 888-984-7569 or anyone who mentions your earlier repair.
If you want a refund, ask your bank or card issuer directly. If they had remote access, remove their tool and change your passwords from another device.
Is Your Windows PC has been infected really from Microsoft?
No. It is sent by scammers who copy the name and look of Microsoft. The sender address and the links do not belong to it, and the message asks for your password, which a real company does not request through an unexpected message.
If you want to be sure about your account, open the website or app of Microsoft the way you normally do, not through the message, and look for notices there. Then delete the message and report it as phishing. If you already followed its instructions, use the steps in this guide for your case.
I called 888-984-7569. What should I do?
888-984-7569 is answered by the scammers behind Your Windows PC has been infected. If you only talked, hang up, do not call back and block the number. If you installed a program or let them connect, disconnect the PC from the internet, uninstall the remote access tool and run a full scan and the Microsoft Defender offline scan.
Change passwords you typed during the call from another device. If you opened your bank during the call or sent money, call the bank immediately on the number on your card. Write down everything they said for the police report.
Is it true that your account needs urgent attention?
No. The claim that your account needs urgent attention is the hook of Your Windows PC has been infected, invented to give you a reason to act quickly. Scammers pick a story that could plausibly apply to many people, so it may feel relevant to you, but nothing in the message is based on your real accounts or devices.
If the claim concerns a service you use, check it there directly, by opening the website or app yourself. You will find no such problem. Then delete the message and report it as phishing.
What happens if I do what Your Windows PC has been infected asks?
The scammers get your password, and they use it quickly. Passwords are tried on the real service within minutes, cards are charged or added to phone wallets, remote access is used to open your bank, and crypto is moved on at once.
Documents surface later as accounts in your name. If you already did what the message asked, do not wait to see what happens; follow the steps in this guide for your case today. Speed matters more than anything else here.
How do I report Your Windows PC has been infected to my mail provider?
Use the built-in button. In Outlook, select the message and choose Report > Report phishing. In Gmail, open the message, click the three-dot menu and choose Report phishing.
Scam text messages can be forwarded to your carrier's spam number, which is 7726 in the US and the UK.
On social networks, use the report option on the message or the profile. Reporting trains the filters that protect you and other users, and it takes a few seconds. Then delete the message.
Can just reading Your Windows PC has been infected harm my PC?
No. Reading the e-mail does nothing to the PC. The risk lies in what the message wants you to do: your password. Every one of those needs an action from you, such as a click, a typed password, a payment or a call.
If you stopped at reading, you are fine. Delete it and report it. If you are unsure whether you clicked something, check your browser history for the time you read the message, and act on what you find there.
What should I do first after Your Windows PC has been infected?
Secure the account involved. From a device you trust, open the official app or website directly, change the password and sign out of all sessions. Turn on two-step verification with an app or a passkey rather than text messages if the service allows it.
Then check recent activity, linked e-mail addresses and recovery phone numbers for changes you did not make. If A warning that tells you to call 888-984-7569 involved money, call your bank using the number on the back of your card. Only after that look into how it happened.
Will Fortect remove Your Windows PC has been infected?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Your Windows PC has been infected, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- How-To Geek: Everything You Need To Know About the Blue Screen of Death (read October 6, 2026)
- FTC: How to recognize and avoid phishing scams (read October 6, 2026)
- CISA: Recognize and report phishing (read October 6, 2026)
- Microsoft Support: Protect yourself from phishing (read October 6, 2026)
- NCSC: Phishing attacks, dealing with suspicious e-mails and messages (read October 6, 2026)