
Blackworm: what it is and how to remove it
Blackworm is also known as Grew.a, Grew.b, Blackmal.e, Nyxem.e, Nyxem.d, Mywife.d, Tearec.a and CME-24. It is an extremely dangerous and rapidly spreading Internet worm propagated by e-mail via messages with infected attachments and unprotected network shares.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If Blackworm keeps coming back after uninstalling, a scan can find what reinstalls it.
Do it yourself · free Remove Blackworm yourself 4 steps, about 12 minutes, no software needed.
Start the steps
Blackworm: summary
| Distribution | Email attachments and links in such notifications can include malicious code, so opening files or installing programs can result in a worm infiltration |
|---|---|
| Name | Blackworm |
| Type | Worm |
| Issues | The infection can delete various files, install programs and other infections |
| Detection names | No Microsoft detection name is known |
| Damage | Not recorded in the old report |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 4 more facts
| Symptoms | An unknown program in Installed apps |
|---|---|
| Evidence | One write-up by a security site; details still limited |
| First seen | 26 April 2021 |
| Facts checked | 6 October 2026 |
What Blackworm does
From our report of Apr 2021 · not reviewed since
More from our earlier report on Blackworm
- You should get an anti-malware tool or a security program and eliminate all threats from the machine
- The system can be affected, so run and repair any damage that is found
How to remove Blackworm
Clean the USB drives as well as the PC, or the worm comes back the next time a stick is plugged in.
Step 1: Clean the USB drives
Blackworm spreads through USB sticks, so every drive used in this PC is suspect.
In File Explorer, switch on hidden items, delete the shortcuts that look like your folders, and run
attrib -h -r -s /s /d E:\*.*in Command Prompt (with your drive's letter) to restore the hidden ones.Right-click the drive and choose Scan with Microsoft Defender. Turn off AutoPlay for removable drives in Settings > Bluetooth & devices > AutoPlay (Windows 11) or Devices > AutoPlay (Windows 10).
Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 2: Remove it from startup
Whatever Blackworm installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to Blackworm or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Repair damaged system components
Once a computer is infected with malware, its system is changed to operate differently. For example, an infection can alter the Windows registry database, damage vital bootup and other sections, delete or corrupt DLL files, etc. Once a system file is damaged by malware, antivirus software is not capable of doing anything about it, leaving it just the way it is. Consequently, users might experience performance, stability, and usability issues, to the point where a full Windows reinstall is required.
Therefore, we highly recommend using a one-of-a-kind, patented technology of repair. Not only can it fix virus damage after the infection, but it is also capable of removing malware that has already broken into the system thanks to several engines used by the program. Besides, the application is also capable of fixing various Windows-related issues that are not caused by malware infections, for example, Blue Screen errors, freezes, registry errors, damaged DLLs, etc.
- Download the application by clicking on the link above
- Click on the ReimageRepair.exe
- If User Account Control (UAC) shows up, select Yes
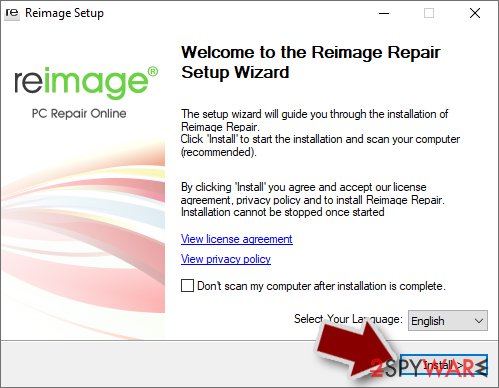
- Press Install and wait till the program finishes the installation process
- The analysis of your machine will begin immediately
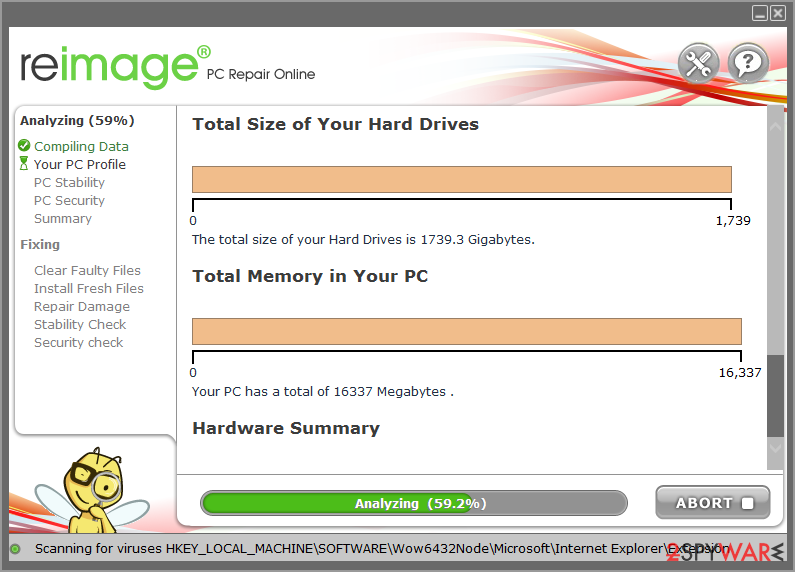
- Once complete, check the results - they will be listed in the Summary
- You can now click on each of the issues and fix them manually
- If you see many problems that you find difficult to fix, we recommend you purchase the license and fix them automatically.
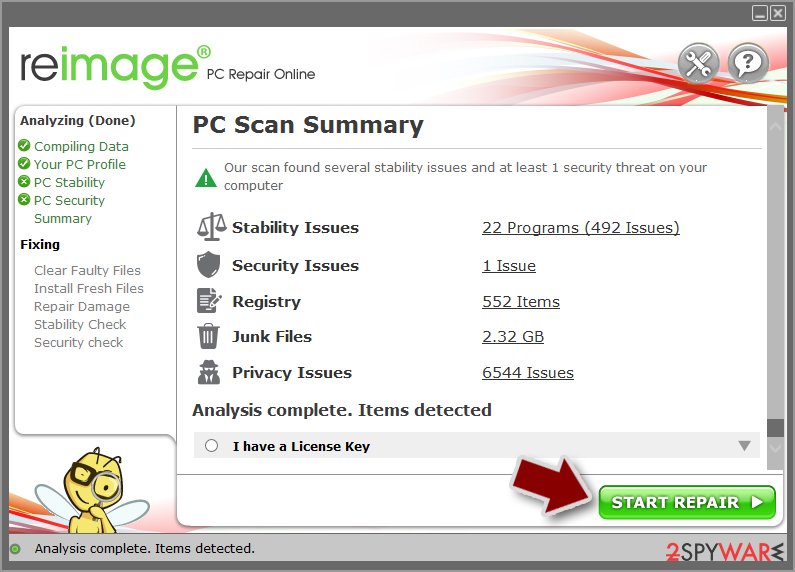
By employing , you would not have to worry about future computer issues, as most of them could be fixed quickly by performing a full system scan at any time. Most importantly, you could avoid the tedious process of Windows reinstallation in case things go very wrong due to one reason or another.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
Scan your system with anti-malware
If you are a victim of ransomware, you should employ anti-malware software for its removal. Some ransomware can self-destruct after the file encryption process is finished. Even in such cases, malware might leave various data-stealing modules or could operate in conjunction with other malicious programs on your device.
or can detect and eliminate all ransomware-related files, additional modules, along with other viruses that could be hiding on your system. The security software is really easy to use and does not require any prior IT knowledge to succeed in the malware removal process.
From our report of Apr 2021 · not reviewed since
Blackworm is a nasty worm that can delete various files like doc, rar, PSD, DMP, and zip formats
Blackworm is also known as Grew.a, Grew.b, Blackmal.e, Nyxem.e, Nyxem.d, Mywife.d, Tearec.a and CME-24.
It is an extremely dangerous and rapidly spreading Internet worm propagated by e-mail via messages with infected attachments and unprotected network shares. The user can accidentally infect a computer by opening a malicious e-mail attachment or running an infected executable file.
The worm is known for destroying various types of files and can disable the antivirus programs, stops updates for security tools. The infection can even affect other settings, damage data, or alter the preferences of the machine. You need to remove the infection as soon as possible.
Once the malicious piece gets executed, Blackworm secretly installs itself to the system and runs a spreading routine. The worm uses its own mail engine to send bogus letters to all the addresses it finds in local text and spreadsheet documents, presentations, databases, and other similar files.
It also creates infected files in unprotected network shares located in the same network or domain. Blackworm e-mail messages can have the following subjects and the following bodies: click to see examples or similar. There are many ways the threat can spread, but the best way to remove it - anti-malware tools like or .
The parasite's payload is large and destructive. Blackworm terminates active security-related processes, prevents installed antivirus software from running on every system startup. It also deletes essential executables and library files related to popular antiviruses and other security-related programs, and some file-sharing applications. You need to consider that and recover the damage using .
From our report of Apr 2021 · not reviewed since
Email attachments ven while looking normal can still be malicious
Worms and other more dangerous threats like trojans and keyloggers can spread via infected attachments on email notifications.
Threats can infect computers by copying themselves over the network and spreading as pieces in pirating software packages.
Make sure to avoid suspicious email notifications and any other content that raises any questions. Notice typos or grammar mistakes in senders' address, the topic of the email, messages themselves.
Make sure to stay wy from downloading those files or clicking on links and files from hose emails. This way, you can avoid virus activation and infiltration. Malware can be hidden in word files, excel, PowerPoint files, or added as zip, rar type of pieces.
From our report of Apr 2021 · not reviewed since
Clear the damage and remove threat fully
All this corrupts installed software and compromises system security.
Blackwork destroys all text documents (.doc, .pdf), spreadsheets (.xls), presentations (.ppt, .pps), databases (.mdb, .mde), archives (.rar, .zip), images (.psd) and memory dumps (.dmp) it finds in the compromised system. This may lead to catastrophic data losses. Make sure to remove as soon as possible and use or for this.
Blackworm automatically runs on every Windows startup. This is why the removal process should also result in the anti-malware tool and PC repair or optimization procedures. You need to repair the damage and recover processes, fix virus damage. Try .
After removal and prevention
Make the next attack harmless
Blackworm could only hurt the files that had no second copy, and the signs (blackworm in the list of installed apps) showed exactly which ones those were.
The 3-2-1 rule fixes that:
- three copies
- two media
- one disconnected
A practical version for a home PC: OneDrive or another cloud backup with version history, plus an external disk that you plug in once a week for File History and then unplug. Test a restore now and then by opening a few files from the backup on another device.
Details, schedules and what not to back up are in our 3-2-1 backup guide for Windows.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
Questions about Blackworm
Can I safely uninstall Blackworm?
If you did not install Blackworm yourself and it is not part of your hardware or a program you rely on, yes. Uninstalling an unwanted program does not harm Windows. Before you do, search the exact name and publisher to be sure it is not a driver tool, a printer utility or a game launcher with an odd name.
Then remove it from Settings, Apps, Installed apps. Ignore any offers or warnings in its uninstaller about losing protection or performance. Afterwards check Startup apps and your browsers for leftovers, and restart once to confirm that it does not reinstall itself.
How do I stop programs like Blackworm from being installed again?
Most unwanted programs arrive through installers, so the fix is in how you install software. Download programs from their official sites or the Microsoft Store, not from download portals or ads above search results. During setup, choose Custom or Advanced installation and untick every extra offer, including browsers, toolbars and optimizers.
Decline update prompts that appear inside other programs unless you know them. In Windows Security, turn on reputation-based protection and potentially unwanted app blocking. These steps would most likely have stopped Blackworm before it reached the app list.
Is Blackworm a virus?
In everyday language, yes: Blackworm is malware, a program that runs without your consent. More precisely, the reports point to a worm, based on what people saw: blackworm in the list of installed apps. It is not part of Windows and no legitimate program behaves this way while hiding from the user.
It should be removed, and the PC checked for other programs that may have come with it. Because there is no public analysis yet, we cannot list everything it does; the removal plan in this guide is written to cover the usual places this kind of malware uses to start and hide.
Should I reset my PC because of Blackworm?
Only if the signs point to deeper access. Reset when you see blackworm in the list of installed apps again after removal, when Windows Security cannot start or update, when remote access tools you did not install keep appearing, or when you simply cannot trust the PC any more.
Otherwise, the plan in this guide plus an offline scan is enough. If you do reset, choose Remove everything and Cloud download for a fresh copy of Windows, restore only documents and photos, and reinstall programs from their official sites. Change important passwords from the clean system afterwards.
Did Blackworm steal my passwords?
There is no evidence either way yet, because Blackworm has not been analysed in public. The reported sign, blackworm in the list of installed apps, does not show theft by itself. However, malware of this kind is often installed together with a password stealer, which works in seconds and leaves nothing to see.
The cautious approach costs little: once the PC is clean, change the passwords saved in your browsers from another device, starting with e-mail, then banking and payment accounts. Sign out of all sessions and turn on two-step verification. If a bank card was saved in the browser, ask the bank about a replacement.
Can I just delete the file Windows Security found?
Let Windows Security handle it instead. When it finds Blackworm, choose Remove or Quarantine; the scanner also removes related startup entries and tasks that a manual delete would miss. Deleting a running file by hand often fails, and many threats restore themselves from a second copy.
After the removal, run the Microsoft Defender offline scan, which works before Windows starts and catches parts that hide while Windows runs. Then check Task Scheduler for leftovers. Restart afterwards and check that the detection does not return.
Where does Blackworm come from?
We cannot name a source for Blackworm yet, because no one has traced its distribution in public. In the cases we see, a worm most often comes with pirated software, activators, game mods and cheats, or with downloads from sites that repackage free programs.
Removable drives are another route for self-spreading kinds. Your own history is the best clue: what did you install or plug in shortly before you first noticed blackworm in the list of installed apps? Whatever it was should be removed together with the malware and never reinstalled from the same place.
Are my files on the USB drive lost?
Usually not. USB worms hide the real folders and put shortcuts with the same names in their place. After scanning the drive on a cleaned PC, open it in File Explorer, choose View > Show > Hidden items, and your folders appear, faded.
Clear their Hidden attribute in Properties, delete the shortcuts and any unknown script files, then scan once more. Copy important files to a safe place before using the drive again. If anything is missing, a data recovery tool run from the cleaned PC may still find it.
Should I scan my other computers too?
It is a good idea, even for malware that does not spread by itself. The same download, USB stick or loader may have been used on other PCs in the household, and shared folders can carry files between them.
Run a full scan followed by the Microsoft Defender offline scan on each Windows PC that shared drives or files with the infected one. Do not copy programs or installers from the infected PC until it is clean, and change Wi-Fi and router passwords if they were saved on it.
Will Fortect remove Blackworm?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Blackworm, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)
- Microsoft Learn: How Microsoft names malware (read October 6, 2026)