
Critical Chrome Update scam: what it is and how to remove it
Critical Chrome Update is the scam that displays fake alerts about the needed browser or system updates and this way tricks people into installing other possibly malicious programs to the computer. If you are constantly redirected and such pop-ups go to your screen repeatedly, you should check your computer for Chrome virus - a potentially unwanted program that can be secretly running on the system.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Unsure whether runme.js is safe? A free scan checks the file and what starts it.
Do it yourself · free Remove Critical Chrome Update scam yourself 6 steps, about 18 minutes, no software needed.
Start the steps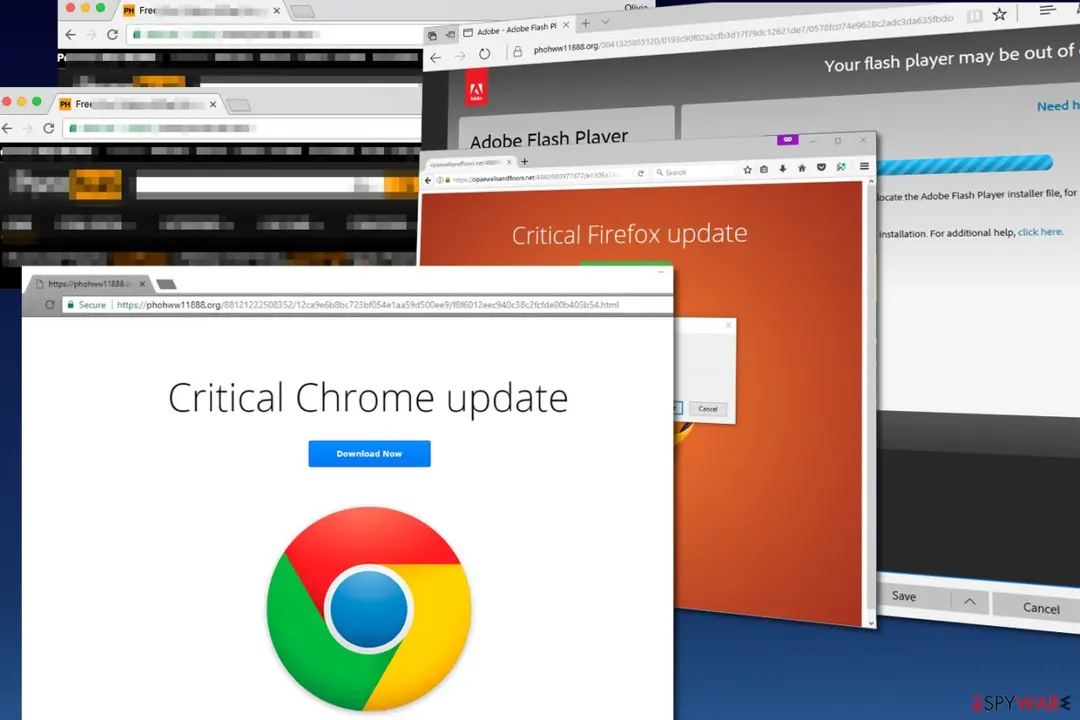
Critical Chrome Update scam: summary
| Distribution | Software bundles, PUPs installed on the system already, deceptive ads, software cracks |
|---|---|
| Name | Critical Chrome Update scam |
| Category | Malware |
| Family | Chrome virus |
| Symptoms | Delivers fake alerts, warning messages claiming about needed software, updates or additional programs. Tricks into installing fake applications, rogue tools |
| Main danger | Infects the system with malware, in particular, trojans and ransom-demanding threats |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 7 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Damage | Not recorded in the old report |
| Type | Loader |
| Evidence | 5 write-ups by security sites; details still limited |
| File names | runme.js |
| First seen | 10 May 2021 |
| Facts checked | 7 October 2026 |
What Critical Chrome Update scam does on an infected PC
From our report of May 2021 · not reviewed since
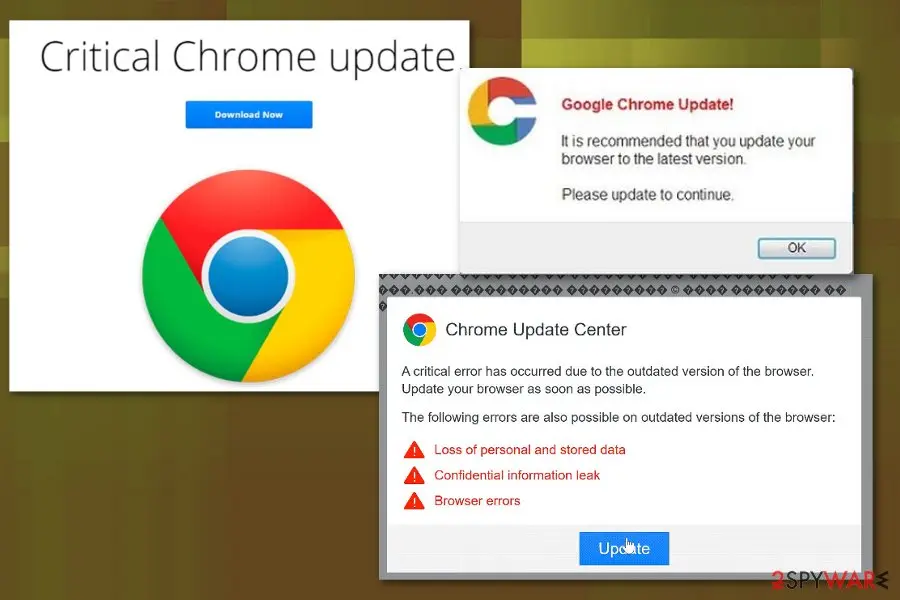
Critical Chrome Update is the fake alert that drops Kovter.C malware on the computer
Critical Chrome Update is the scam that displays fake alerts about the needed browser or system updates and this way tricks people into installing other possibly malicious programs to the computer. If you are constantly redirected and such pop-ups go to your screen repeatedly, you should check your computer for Chrome virus - a potentially unwanted program that can be secretly running on the system.
Note that Critical Chrome Update virus is totally malicious as it can emerge on your screen after clicking on one of Traffic Junky ads.
This ad-supported network is known to be serving promotional content on adult-only websites, and therefore visitors of these domains fell victims to KovCoreG malvertising attack that pushes Kovter virus to victims' computer. Installation of severe malware as such can also be a result of constant alerts about alleged updates.
Critical Chrome Update scam is a social engineering attack or a campaign based on technical support scam tactics. Unfortunately, such messages and various alerts can lead to the installation of rogue tools, applications, useless programs.
However, scams like this, in most cases, deliver messages and redirect to questionable or even malicious domains as hosts:
These pop-ups can also provide messages with phone numbers that claim to connect victims with the technical support team. Nevertheless, they are fake, and official technical support services are not delivering messages like this, especially are not encouraging to call questionable numbers. As a result, remove Critical Chrome Update virus without interacting and calling the provided number or contacting people behind the threat in any other way.
To go back to your previous browsing, get an automatic anti-malware tool and clean the machine fully. The proper scam removal requires tools like , so that the system gets fully recovered.
- iexaidlepro.org
- johphblogger-hints-and-tips.org
- tahxiintimes-niedersachsen.org
From our report of May 2021 · not reviewed since
A detailed scheme of the Critical Chrome Update scam functionality
After managing to compromise the Traffic Junky ad network, which serves ads via popular adult-oriented sites such as Pornhub, cybercriminals are now capable of serving deceptive via common web pages.
As a result, unsuspecting users can easily get infected with click-fraud malware known as Kovter Trojan.
Users who click on such ads are exposed to a malvertising attack that redirects them to deceptive pages that are picked based on their web browser used. Following the browser type and version, victims receive bogus offers to install one of these updates:
The final alert is picked using a JavaScript code that is the same as the one used in Neutrino and NeutrAds.
Research reveals that the attack chain starts with a redirect from advertisingms[.]com domain which corrupts the final link and throws the victim to a compromised malware-serving site. According to Proofpoint, this domain "inserts a call hosted behind KeyCDN," which happens to be a giant content delivery network.
Critical Chrome Update scam suggests installing an update for the popular web browser, however, instead of updating the browser, it drops a ZIP archive that contains a runme.js file. Once executed, it addresses the server responsible for the social engineering attack. The .JS file the downloads two files to victim's computer - .flv and .mp4 format file.
FLV file consists of three random digits, and the rest of them belong to an RC4 key. The MP4 record is encrypted with this key and hex-encoded. The MP4 file also stores a Powershell script that contains shellcode used to download and execute AVI file (Kovter virus).
- Critical Chrome Update
- Critical Firefox Update
- Adobe Flash Player update (Microsoft Edge/Internet Explorer users).
From our report of May 2021 · not reviewed since
Particular functions of the virus
Once executed, Kovter virus establishes itself into Windows Registry rather than dropping some files on the system.
This way, malicious software attempts to avoid detection. Besides, the virus sets up specific autorun entries, which runs the malware as soon as the victim starts the computer.
The malware operates silently, and the only noticeable problem is a slight decrease in the computer's performance. However, the majority of users might not suspect anything if they do not have anti-malware programs installed on their PCs.
From our report of May 2021 · not reviewed since
It is possible to notice and avoid possible infections
Dieviren.de team says that the trick to avoid installing the malicious Critical Chrome Update or Urgent Chrome Update, as well as malware delivered via deceptive versions of Flash Player or other well-known programs is to never install updates from random Internet sites.
Although cybercriminals use various techniques to trick victims into clicking on malicious advertisements, the method that is based on fake "updates" is actually very common and can be recognized easily. Such a technique mainly gets used to deliver more severe malware and directly infect the machine with threats.
When deceptive advertisement looks legit and includes official logos of the promoted software, it seems to be trustful and people tend to click on such content. However, you should never rely on the pop-up that claims you need to install or update anything randomly. The official software creators and providers are not showing such messages on browsers.
If you suspect that you need an update for Chrome - simply visit the official browser's developers' site and check whether there is an update available. However, when installing an application or direct program/ software update be aware of the additional installations. Choose Advanced or Custom options to avoid any unwanted applications.
From our report of May 2021 · not reviewed since
More from our earlier report on Critical Chrome Update scam
- For removal, use a reliable anti-malware program
How to check the PC for Critical Chrome Update scam
- File:
runme.js
How to remove Critical Chrome Update scam
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Check where runme.js runs from and stop it
runme.jsis the part you can see, and its location tells you whether it belongs there. Right-click it on the Processes page of Task Manager and choose Open file location, then right-click the file > Properties > Digital Signatures to see who signed it.An unsigned file, or one in a user folder such as
%AppData%, is the one to remove: end the task, then delete the file.Note the folder name, because the same folder usually holds its other files. This is the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 2: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to Critical Chrome Update scam or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 3: Remove it from startup
Whatever Critical Chrome Update scam installed usually starts with Windows.
Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 5: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
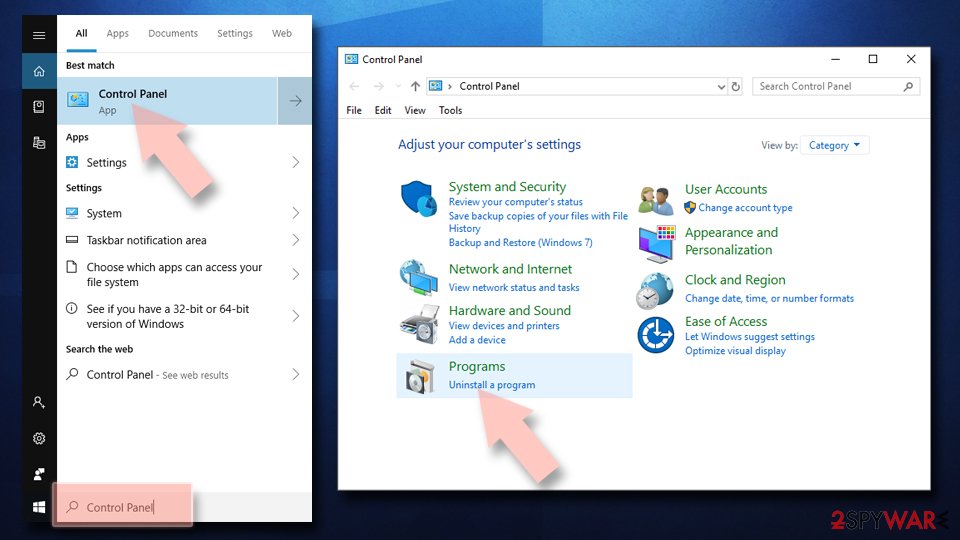
Uninstall from Windows 10/8:
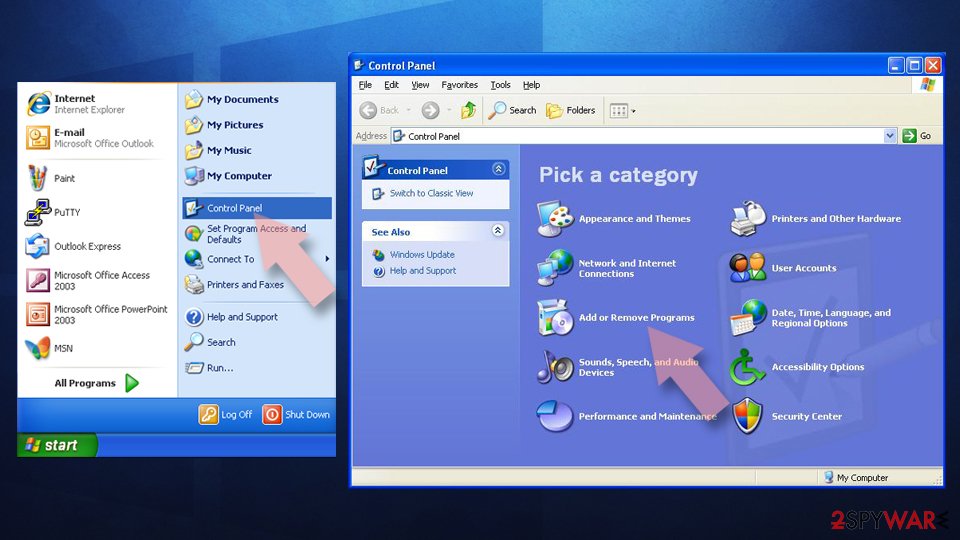
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
Remove the unwanted program:
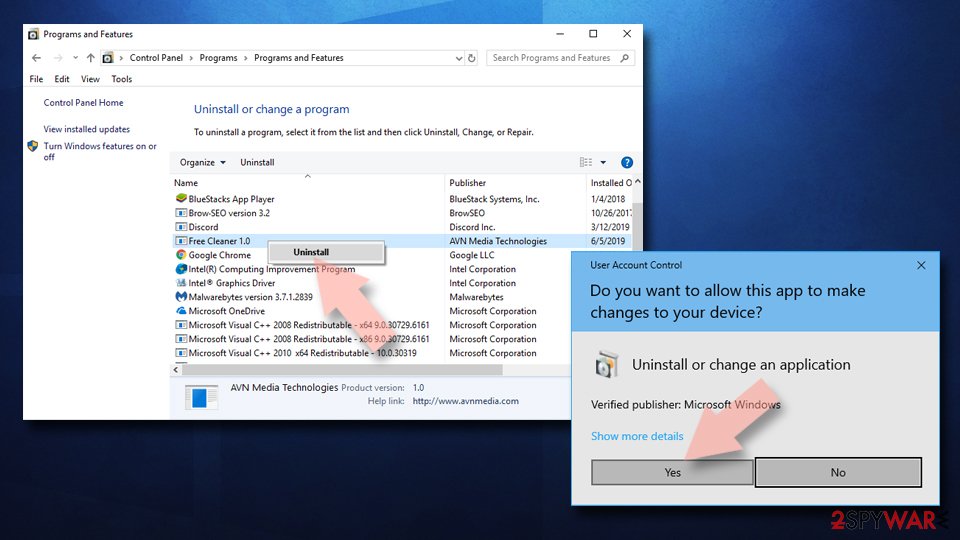
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
Delete malicious extensions from Google Chrome:
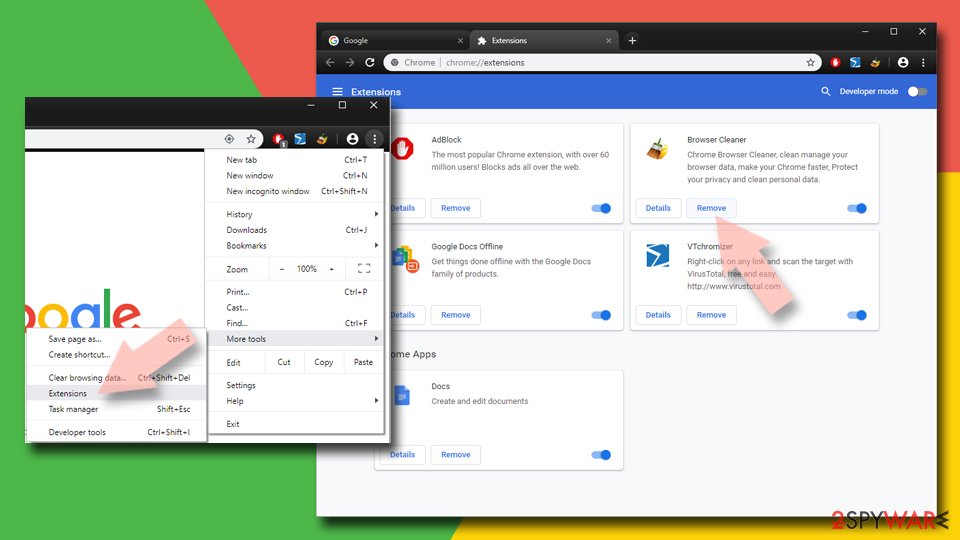
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
Clear cache and web data from Chrome:
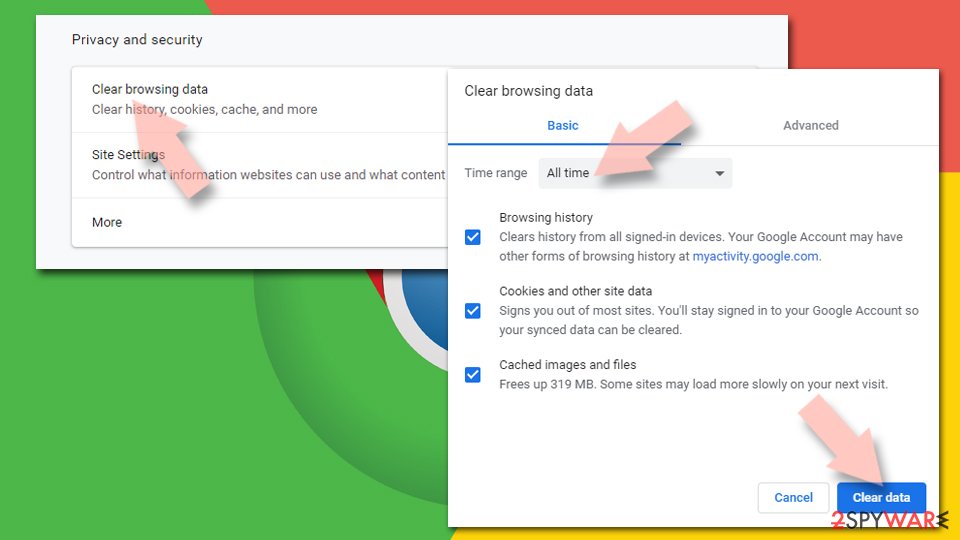
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
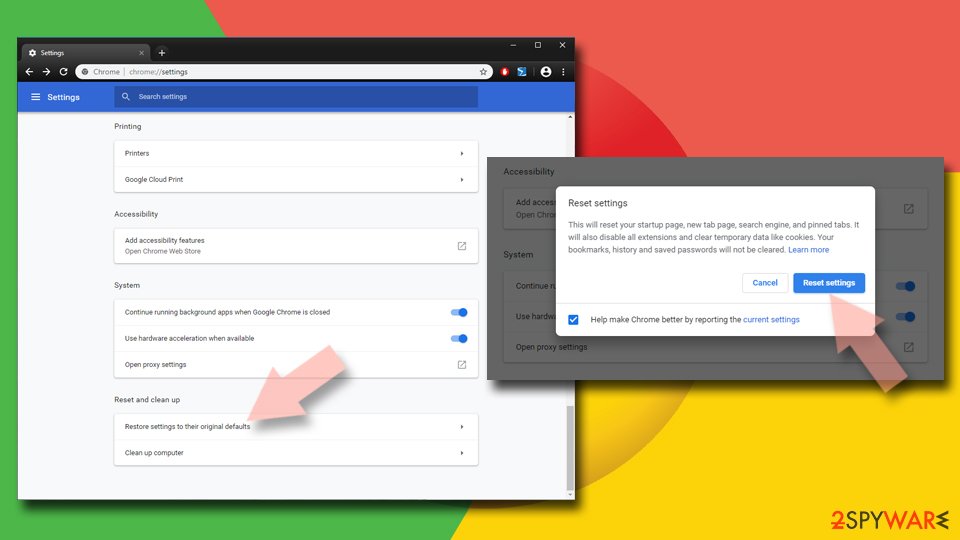
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Microsoft Edge
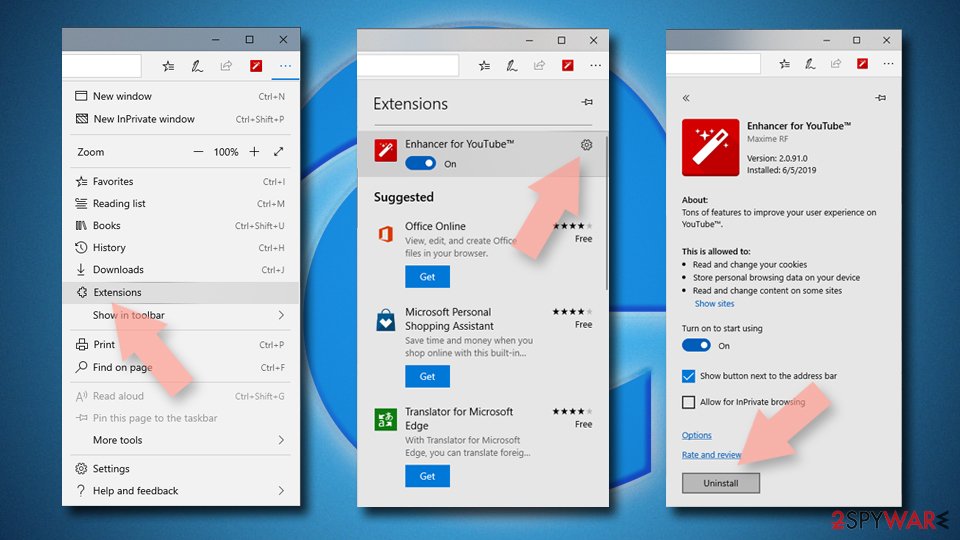
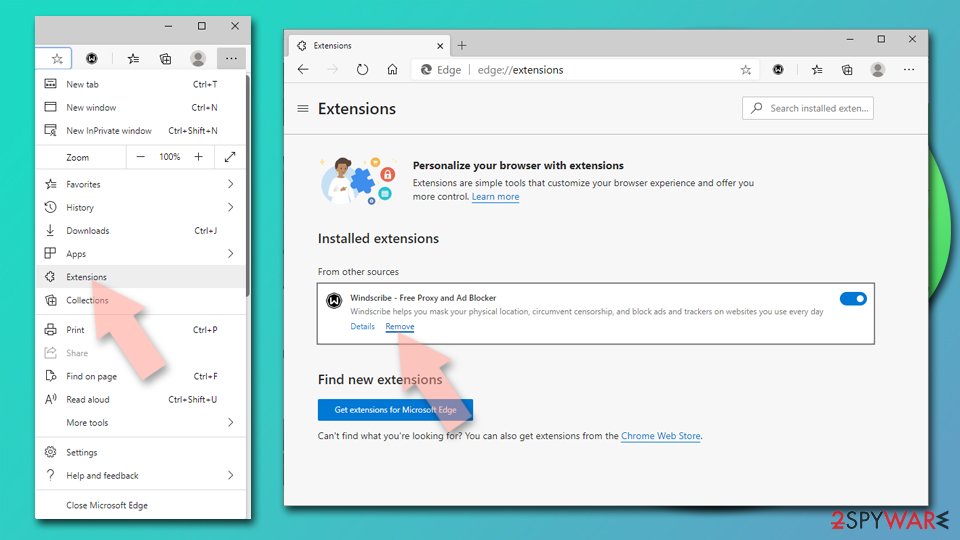
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.
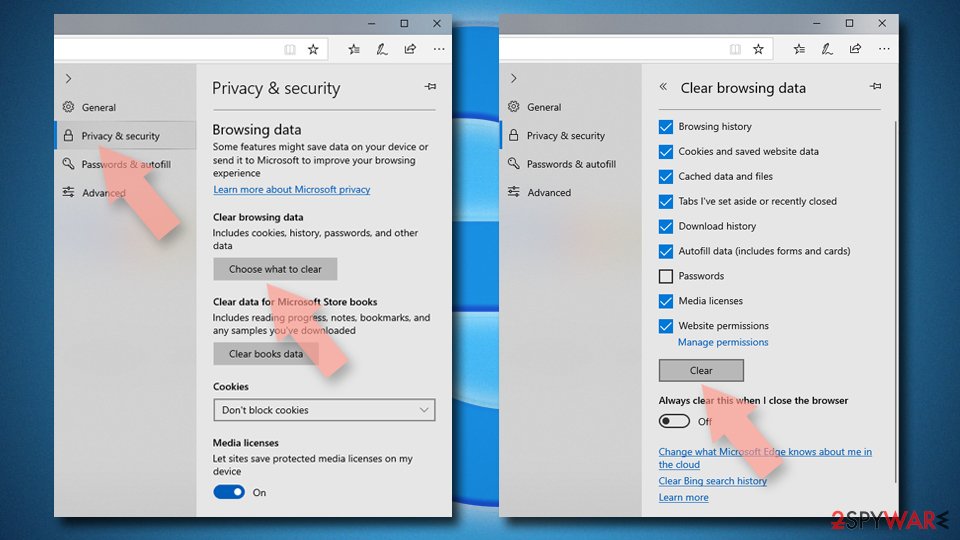
Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.
Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
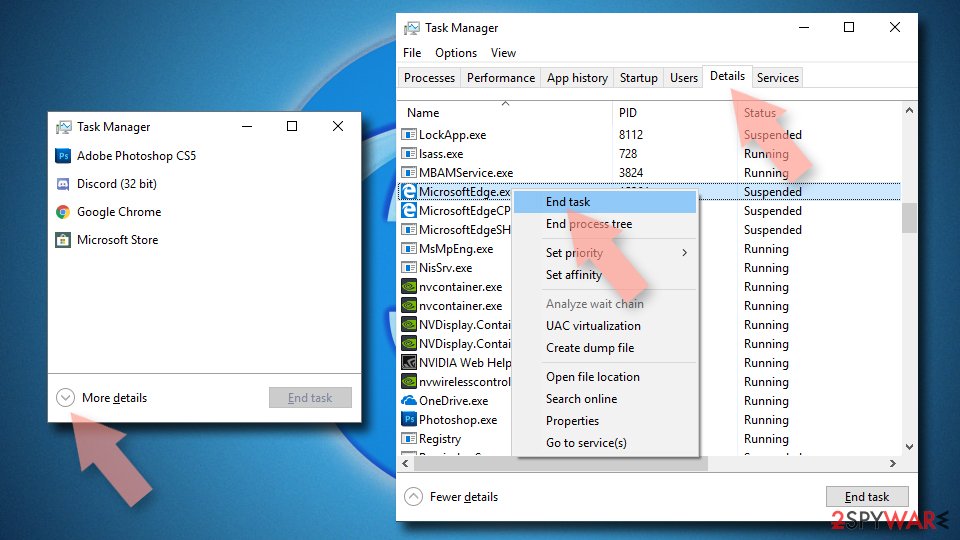
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.
Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
Clear cache and site data:
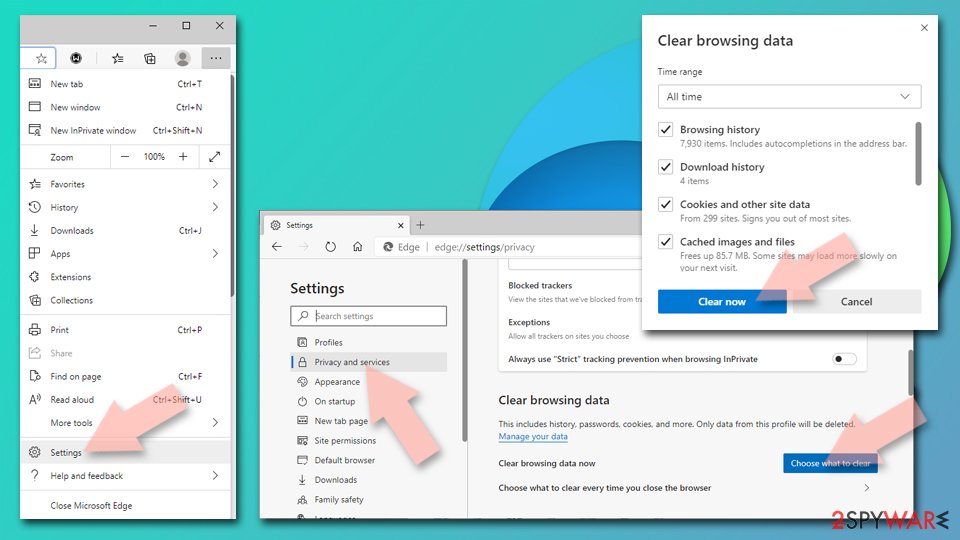
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
Reset Chromium-based MS Edge:
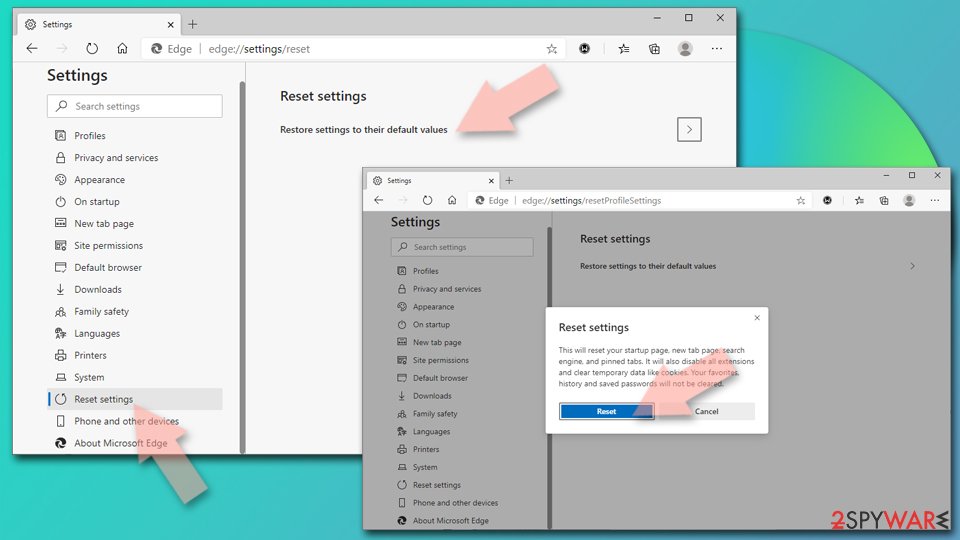
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.
Remove from Mozilla Firefox (FF)
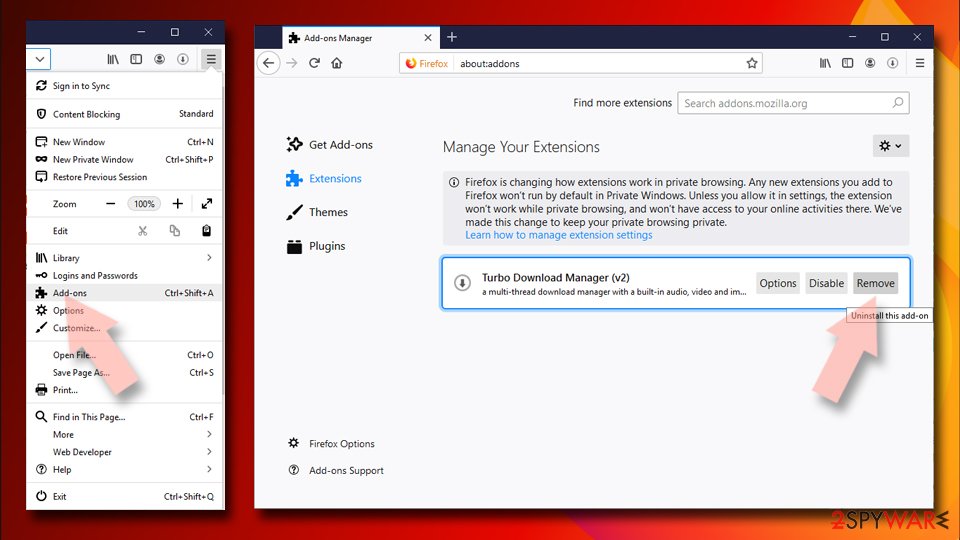
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
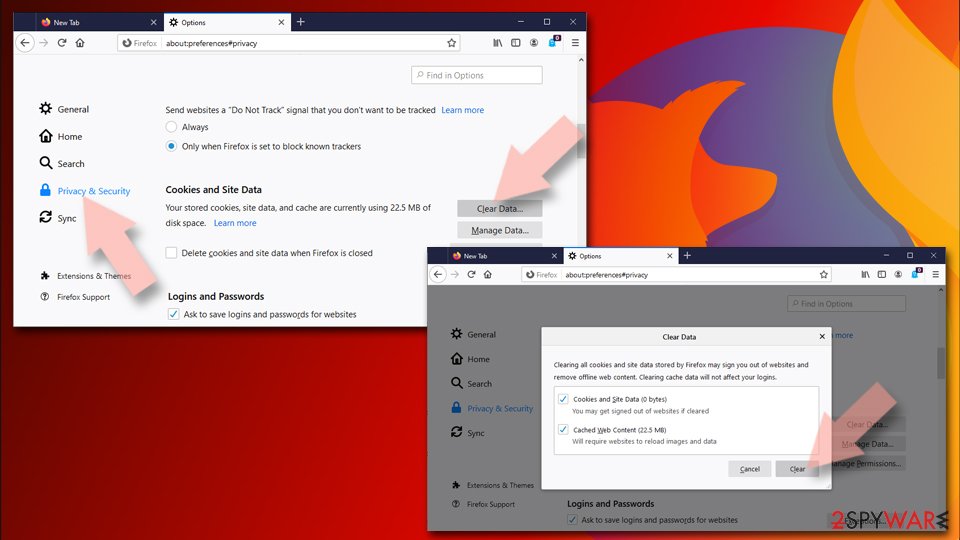
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
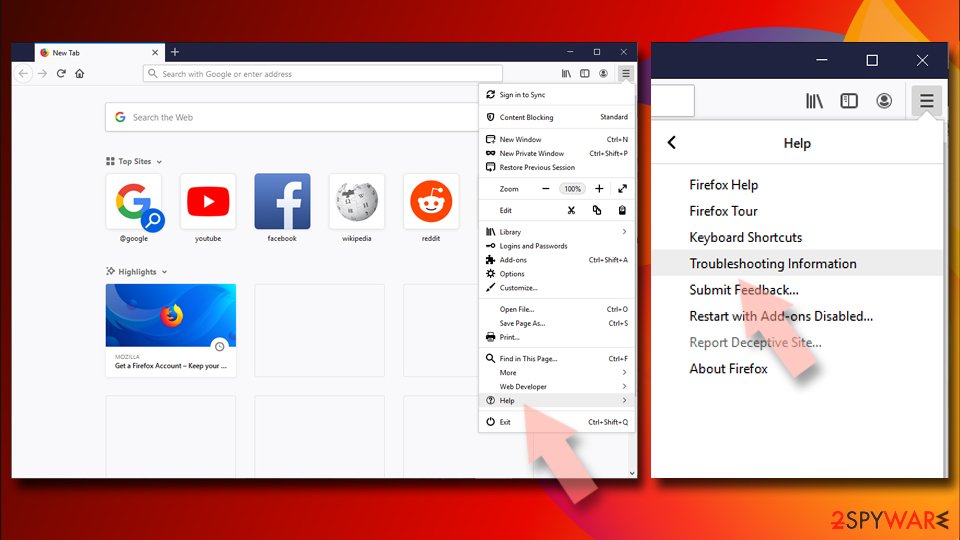
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
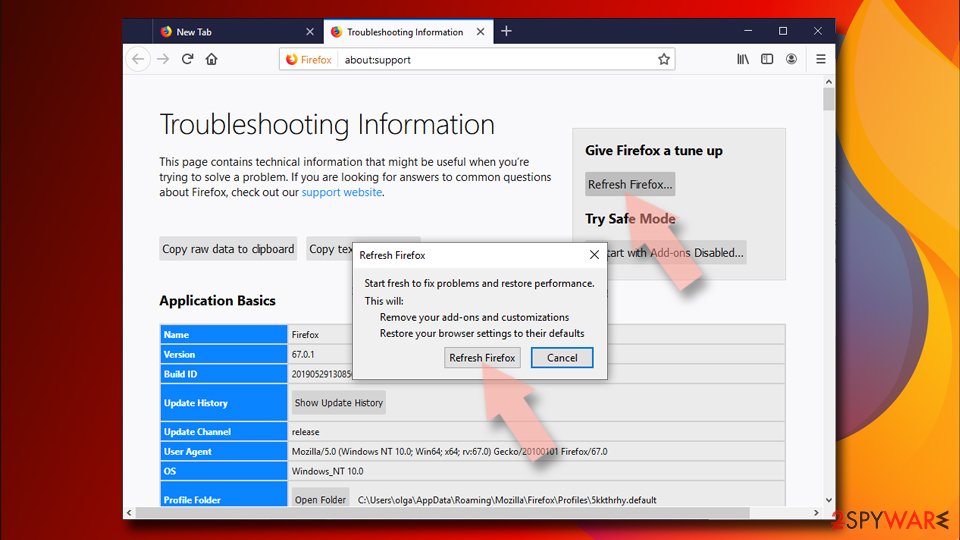
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
Remove dangerous extensions:
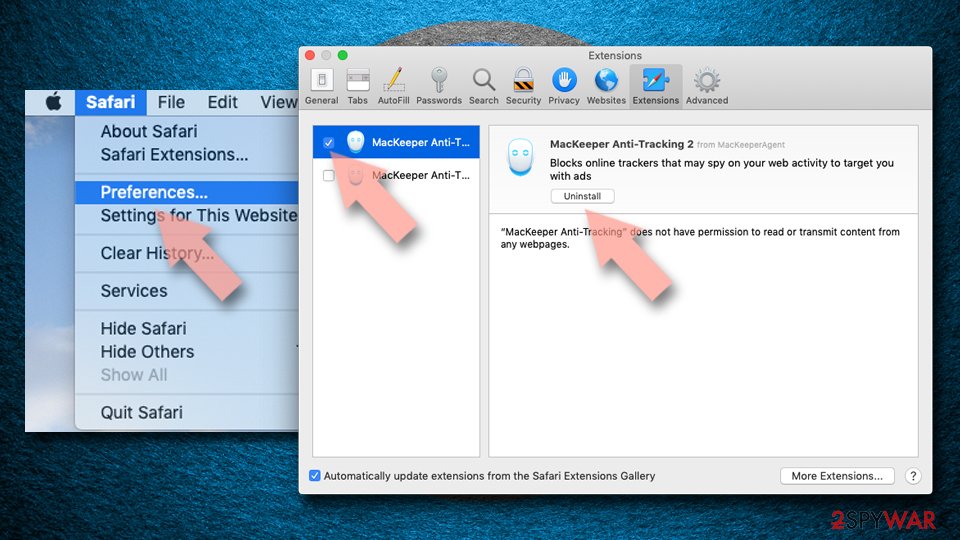
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
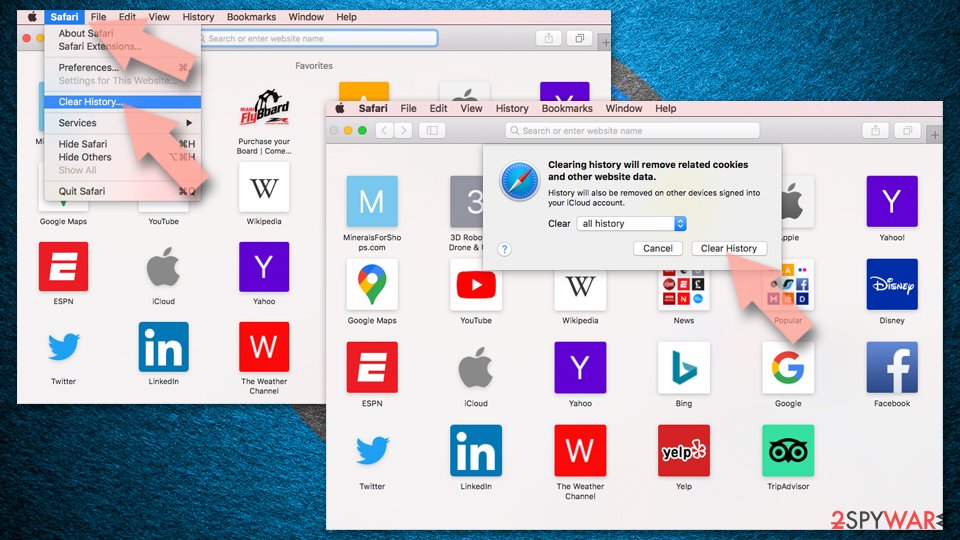
Reset Safari:
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
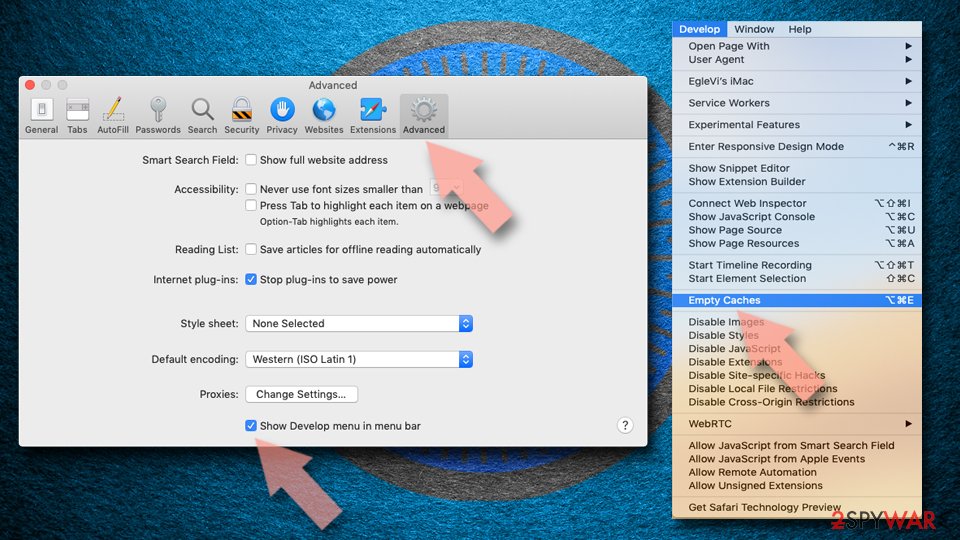
From our report of May 2021 · not reviewed since
Remove Kovter.C virus and stop the scammy messages
If you were redirected to a site containing Critical Chrome Update virus, close the web page immediately.
If it downloaded the malicious ZIP file to your computer automatically, do not open it and delete it as soon as possible.
However, if you launched the deceptive record, run anti-malware software as soon as you can (ideally, do it after performing a clean system boot).
It is essential to delete Kovter Trojan as soon as possible as it can perform a series of illegal activities on your computer.
You should remove virus with updated anti-spyware to be totally sure that all the related files, applications, and even malware get eliminated during one system check.
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed an unfamiliar process called runme.js in Task Manager, a sign of a program that could read browser data, the clean-up is only half of the work.
The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
Questions about Critical Chrome Update scam
Is runme.js a virus?
The name runme.js is not enough to say. Malware often uses technical-sounding names, and harmless updaters often use odd ones. Check three things:
- the folder the file runs from
- the Digital Signatures tab in its properties
- the program that starts it (Startup apps, Task Scheduler or services)
A signed file from a company whose product you use is almost certainly fine. An unsigned file in a user folder that no installed program explains should be removed, and the PC scanned with Microsoft Defender in offline mode.
runme.js keeps coming back. What should I do?
A process that returns after you end it has a restart mechanism, and that is a reason to treat runme.js as unwanted. Check Settings > Apps > Startup, Task Scheduler and the Services list for entries pointing to its folder, and disable them.
Look in Installed apps for anything added the same day and uninstall it. Then delete the folder and run a Microsoft Defender Offline scan, which works before Windows starts and can remove files that are locked or hidden while the system is running.
Can I just delete runme.js?
Deleting runme.js by hand rarely removes Critical Chrome Update scam. While the trojan runs, Windows may refuse to delete the file, and if you succeed, a scheduled task, a service or a second copy may bring it back at the next restart.
The file can also be only one part of the infection: loaders and remote access tools often install other programs. Use the Microsoft Defender offline scan, which removes the file together with its startup entries before Windows loads, and then check startup items and scheduled tasks as described in the plan.
Is a trojan infection worth reporting to the police?
If there was harm, yes. Unauthorised payments, accounts used for fraud, blackmail or a remote session during a scam call all belong in a report, and banks often ask for its reference number before they refund anything.
If antivirus caught Critical Chrome Update scam before it ran and nothing was misused, there is nothing to report. Keep the evidence anyway:
- protection history
- the original download
- the dates
Businesses may also have to notify a data protection authority if personal data could have been accessed.
How dangerous is Critical Chrome Update scam?
Treat it as serious until proven otherwise. The visible sign is an unfamiliar process called runme.js in Task Manager, and programs that behave this way often have more abilities than they show:
- copying passwords
- downloading other malware
- giving remote access
Its family is not known yet, so nobody can say which of these it uses. The good news is that the response is the same in every case and takes about an hour:
- cut the network
- remove the startup entry
- run an offline scan
- change passwords from a clean device
If someone had remote control, a full reset is safer.
What are the signs of a trojan infection?
Most trojans try to leave no visible signs, so look for side effects. Common ones:
- Windows Security turned off or unable to update
- new entries in Startup apps or Task Scheduler
- programs in Installed apps you did not install
- browser settings that changed by themselves
- unusual network activity while the PC is idle
- password-reset or login-alert e-mails you did not trigger
None of these proves an infection on its own. Together with an antivirus alert naming Critical Chrome Update scam, they are a strong reason to follow the full plan.
Should I reset my PC because of Critical Chrome Update scam?
Only if the signs point to deeper access. Reset when you see an unfamiliar process called runme.js in Task Manager again after removal, when Windows Security cannot start or update, when remote access tools you did not install keep appearing, or when you simply cannot trust the PC any more.
Otherwise, the plan in this guide plus an offline scan is enough. If you do reset, choose Remove everything and Cloud download for a fresh copy of Windows, restore only documents and photos, and reinstall programs from their official sites. Change important passwords from the clean system afterwards.
Why didn't my antivirus stop Critical Chrome Update scam?
New trojan builds are packed and changed often so that signatures do not match, and some are signed with stolen or bought certificates. Many arrive inside password-protected archives, which scanners cannot open until you extract them.
Some downloads also tell the user to turn off the antivirus "because it gives false alarms", a common line in cracked software instructions. Keep real-time protection on, never disable it for an installer, and run the offline scan whenever you suspect something slipped through.
Can Critical Chrome Update scam spread to other devices on my network?
Most trojans aimed at home users stay on the PC they infected, but an attacker with remote access can look at the network, open shared folders and try passwords on other devices. Loaders sometimes deliver worms or ransomware that do spread.
Disconnect the PC while cleaning, run a full scan on other Windows PCs, change the router's admin password and the Wi-Fi password if they were saved on the infected PC, and update the router's firmware. If other PCs show the same detection, treat them as infected too.
Will Fortect remove Critical Chrome Update scam?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Critical Chrome Update scam, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Proofpoint: Kovter Group malvertising campaign exposes millions to potential ad fraud malware infections (read October 7, 2026)
- Threatpost: Porn Site Becomes Hub for Malvertising Campaigns (read October 7, 2026)
- CSOonline: What is social engineering? How criminals exploit human behavior (read October 7, 2026)
- DieViren: DieViren (read October 7, 2026)
- FTC: How to recognize, remove and avoid malware (read October 7, 2026)