
Google Critical Security alert: what it is and how to remove it
Google Critical Security alert is a fraudulent message which has been actively spreading around within the Gmail inbox. The email from no-reply@accounts or similar email addresses claims that someone just used your password to try to sign in to your account.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If the "Someone just used your password to try and sign in to your account." warning keeps returning, an automatic scan can check browsers, extensions and installed programs in one pass.
Do it yourself · free Remove Google Critical Security alert yourself 2 steps, about 6 minutes, no software needed.
Start the steps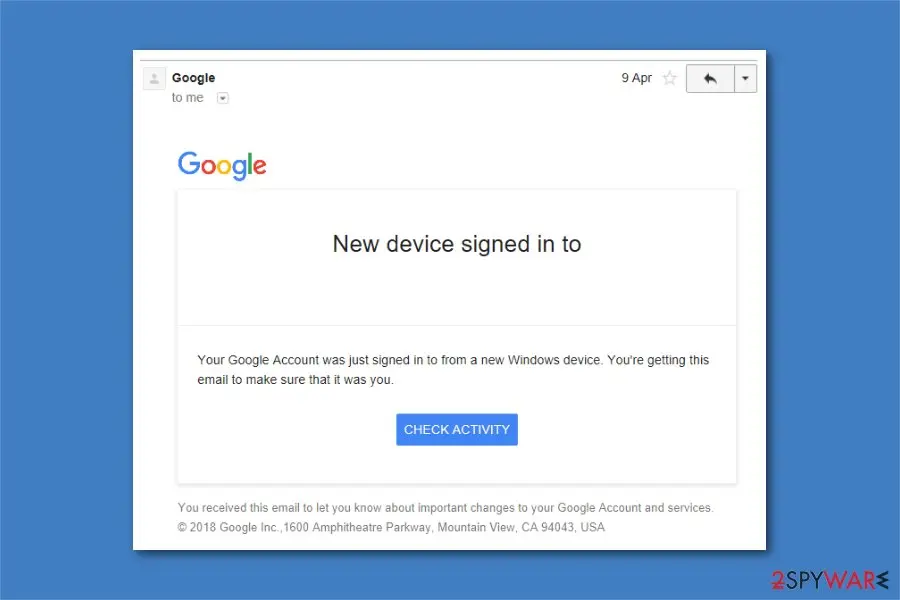
Google Critical Security alert: summary
| Distribution | Malicious spam emails |
|---|---|
| Name | Google Critical Security alert |
| Type | Malware/scam/fake alert |
| Also known as | Critical Security alert; Gmail Security Alert |
| Danger level | Medium. Users can be tricked into exposing their account credentials or lured into downloading malicious programs |
| Symptoms | Victims receive an email in their Gmail inbox which warns about unauthorized sign-in; they are encouraged to take precautionary measures to prevent unauthorized activity |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 5 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Damage | Not recorded in the old report |
| Evidence | 6 write-ups by security sites; details still limited |
| First seen | 10 December 2020 |
| Facts checked | 5 October 2026 |
What the Google Critical Security alert pop-up looks like
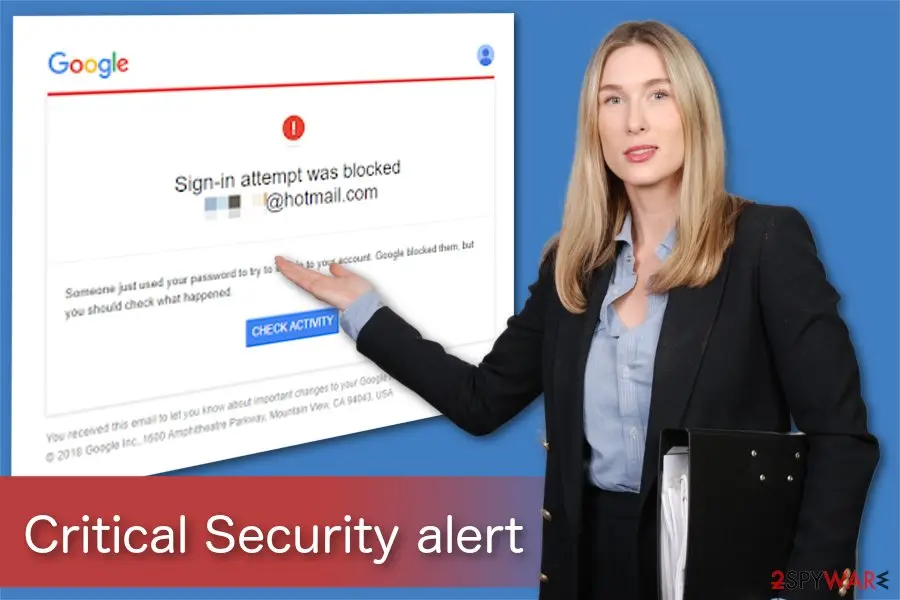
Someone just used your password to try and sign in to your account. Google blocked them, but you should check what happened.
Is the Google Critical Security alert warning real?
From our report of Dec 2020 · not reviewed since
- It's already in my template brochure to be used against corporates it's that good.
- Unforgivable for Google to send this out en mass.
- we used to take legitimate Google emails and adapt...
- but this is just perfect as is.
What the Google Critical Security alert scammers want
From our report of Dec 2020 · not reviewed since
Google Critical Security alert – a scam notification that you might receive via your Gmail
Google Critical Security alert is a fraudulent message which has been actively spreading around within the Gmail inbox.
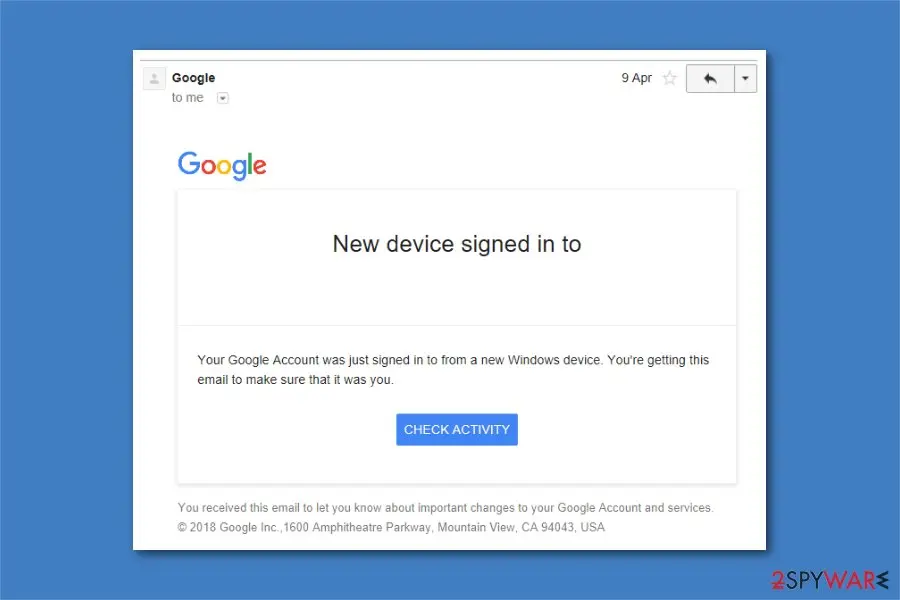
The email from no-reply@accounts or similar email addresses claims that someone just used your password to try to sign in to your account. Users are also advised to check the activity by clicking a button below the text.
However, experts warn that the alert is set to trick users into revealing their email account credentials to cybercriminals or installing malicious software on their devices. Therefore, you should never click on the embedded links inside, regardless of how realistic and believable the buttons look and feel (especially if it comes from an unrecognized account).
Nevertheless, the tech giant uses sophisticated technology to recognize and warn users about an illegitimate login attempt from a different device. For that reason, many warnings from Google are legitimate and should not be ignored. Those who use such services as VPN and Proxy might encounter several Google security alert email messages due to a different IP login, so the case is not always related to phishing.
It is not new that attackers are creating legitimate-looking emails to trick people into compromising their systems. Note that the email contains a fake logo and appears as a real notification. Unfortunately, people should be aware of this alert and learn how to identify this phishing scam.
The message displayed by the Critical Security alert scam contains the following text:
Furthermore, if you click on the "CHECK ACTIVITY" button included in the email, there is a substantial risk that you will be redirected to a malicious site. In this case, hackers can develop another spoofed Gmail log-in page where you would submit your credentials directly to the attackers without even knowing it.
Additionally, the scam email might be used to distribute other malicious programs and aim to infect computers worldwide. Likewise, experts warn about potential ransomware or malware attacks if you click on the content included in the fake alert.
We strongly advise you to stay cautious and remove Google Critical Security alert email together with related cyber threats if you clicked on anything suspicious. It might be hard to identify the malicious activity as it is usually performed in the background.
After Google the removal is completed, we suggest using the app - it might help you fix virus damage related to Windows system files. Also, if you believe that criminals might have stolen your credentials, change all your passwords immediately.
From our report of Dec 2020 · not reviewed since
Legitimate Google warnings sparked some concerns among security experts
The community using Google services got really concerned about the issue, and many rushed to social media like Twitter to report the problem.
The industry giant does not specify what security problems users are facing. So most people simply click on the link and are guided through the procedure.
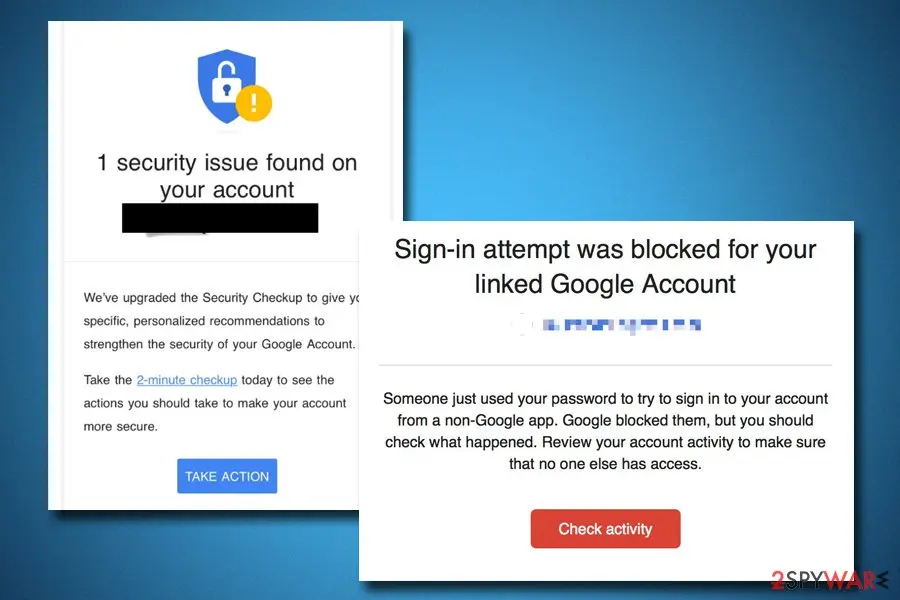
Unfortunately, it is not that hard for hackers to imitate these steps, as was the case with the Google Critical Security Alert email scam. Therefore, several security analysts and social engineering experts showed concerns:
The tech company said that these types of alerts were designed to go through a set of checks that would help users protect their accounts from hacking attempts and other dangers. Additionally, these messages cannot contain too much information about the possible security breach, as this data would only benefit the attacker.
Because the email from Google might be legitimate, further investigation is required. In fact, there is a higher chance of receiving a legit email than a fake one. Regardless of the situation, each instance should be carefully examined, as careless clicking on links might lead to severe consequences (note that many scam emails are recognized and put into the Spam box).
In case you are not sure if an email from Google saying Critical Security Alert is real or not, you should navigate to the checkup page manually at myaccount.google.com/security-checkup and see what is going on there. Clicking on random links is never advisable, and cybercrooks are often very good at producing high-quality phishing emails that can compromise personal information and make users install malicious software on their devices.
From our report of Dec 2020 · not reviewed since
Malicious spam emails might hide malware inside
A vast of cyber threats are delivered via spam emails.
This is a well-known malware distribution technique that is widely employed by criminals worldwide. Unfortunately, people still lack expertise in the IT field to identify phishing emails to protect their private information, finances, and computer.
Fraudulent emails are designed to impersonate a legitimate company or governmental institution, notify about a problem, create some sort of an urge to fix it by opening an attachment or clicking on the link. However, at this point, users who click on email content do not resolve an issue rather than install a malicious program.
Experts note that despite how legitimate the email looks, you should always contact the company directly and ask to confirm the email. Additionally, it would be best to use an antivirus with real-time protection to help you avoid infiltrating the system with malware.
How to get rid of the Google Critical Security alert pop-up
The warning is a web page and your PC is not infected by it.
Close it, then remove what keeps bringing it back.
Step 1: Close the page without touching its buttons
Press Ctrl + Shift + Esc to open Task Manager, select the browser on Processes and click End task: buttons on the page, including Close and Cancel, can trigger downloads or more pop-ups. When you reopen the browser, do not restore the previous tabs.
Warning: Never call a number shown in a browser warning; Microsoft and antivirus companies do not put phone numbers in warnings.
If the page opens again by itself, notifications or an extension are bringing it back. Task Manager works the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 2: Scan the PC, then run the offline scan
A scan finds the parts of Google Critical Security alert that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
Choose a proper web browser and improve your safety with a VPN tool
Online spying has got momentum in recent years and people are getting more and more interested in how to protect their privacy online.
One of the basic means to add a layer of security - choose the most private and secure web browser. Although web browsers can't grant full privacy protection and security, some of them are much better at sandboxing, HTTPS upgrading, active content blocking, tracking blocking, phishing protection, and similar privacy-oriented features.
However, if you want true anonymity, we suggest you employ a powerful VPN - it can encrypt all the traffic that comes and goes out of your computer, preventing tracking completely.
Lost your files? Use data recovery software
While some files located on any computer are replaceable or useless, others can be extremely valuable.
Family photos, work documents, school projects - these are types of files that we don't want to lose. Unfortunately, there are many ways how unexpected data loss can occur:
- power cuts
- Blue Screen of Death errors
- hardware failures
- crypto-malware attack
- even accidental deletion
To ensure that all the files remain intact, you should prepare regular data backups. You can choose cloud-based or physical copies you could restore from later in case of a disaster. If your backups were lost as well or you never bothered to prepare any, can be your only hope to retrieve your invaluable files.
From our report of Dec 2020 · not reviewed since
Eliminate Critical Security alert scam and related malware
If you have clicked on any buttons or links included in the phishing email, you must remove Critical Security alert and its malicious components from your system.
Warning: Keep in mind that eliminating the email from your inbox should do the trick, and you would remain safe if you do not click any links inside.
However, removing it from the inbox will not do wonders if you have already clicked on the link, especially if you downloaded something. Therefore, you should immediately perform a full system scan with powerful anti-malware, such as or .
[GI=method-1]If you believe that your system was attacked by malware and you can't delete it in a standard way, access Safe Mode with Networking and perform a full system scan from there:
Questions about Google Critical Security alert
Did the "Someone just used your password to try and sign in to your account." pop-up really find a virus?
It did not find anything, because a web page has no way to look at your files. The scan animation, the number of threats and the warning "Someone just used your password to try and sign in to your account." are part of the page and are the same for everyone who lands on it.
What the pop-up does tell you is that your browser was sent to a scam page, either through an ad, a redirect or a notification permission. That source is worth removing.
For a real answer about infections, run a scan in Windows Security or another antivirus you installed yourself, not one offered by the page. If the real scan finds nothing and the page stops after you clean up notifications and extensions, you are done.
I clicked on the "Someone just used your password to try and sign in to your account." pop-up. Am I infected?
Clicking a button on the page usually only opens another page or starts a download. If nothing was downloaded and you did not run any file, the PC is very likely fine, and closing the tab is enough.
If a file was downloaded, delete it from the Downloads folder without opening it. If you opened it, treat the PC as infected: uninstall anything new in Installed apps and run a full scan.
If the page that showed "Someone just used your password to try and sign in to your account." also led you to type a password or card number, change that password from another device and call your bank. The sections after the removal steps cover each of these cases in order.
The agent knew details about my PC. Were they real?
They looked real but proved nothing. Callers from pages like Google Critical Security alert open the Windows Event Viewer, which shows harmless warnings on every PC, or run a command that lists normal system details, and present them as signs of infection. Some type alarming text into a command window themselves.
Nothing they showed you came from a real scan. If they had remote access, follow the clean-up steps anyway, because they may have installed tools while you watched. Change any password they could have seen.
I closed it, but it appeared again the next day. Why?
A page that returns on its own has a trigger. Look at how it appeared: from a pop-up in the corner of the screen means a notification permission; on start-up means a session restore or a changed start page; while browsing any site means an extension; on one particular site means that site's ads.
Each has a quick fix in the browser settings. If none of them explains it, reset the browser, which clears permissions, extensions and start pages together.
Can Google Critical Security alert harm my PC just by being open?
No. A web page runs inside the browser's sandbox and cannot install programs, read your files or change Windows settings on its own. Google Critical Security alert can only make noise, fill the screen and try to persuade you. The risk begins when you follow it:
- calling the number
- paying
- downloading a file
- pasting a command
Close the page, and if it frightened you into doing one of those, follow the matching steps in this guide. Otherwise, nothing on the PC needs cleaning or repairing.
How did Google Critical Security alert find me?
It did not target you personally. Pages like this buy traffic from shady ad networks and from hacked sites, and they show A browser warning that reads "Someone just used your password to try and sign in to your account." to whoever is redirected to them.
Mistyped addresses, streaming and download sites, and earlier clicks on Allow for notifications are the most common entry points. Nothing about your PC was scanned or known in advance. Once you remove the trigger in the browser, the page has no way to reach you again unless you meet a similar ad.
Is my phone affected by Google Critical Security alert?
Not through the PC. A scam page in a Windows browser cannot reach a phone, even if both use the same account. The sign reported, A browser warning that reads "Someone just used your password to try and sign in to your account.", happened in a browser on the PC.
Phones can meet similar pages on their own, usually through ads or notifications, and the fix there is the same idea: remove notification permissions and unknown apps. If you used the phone to call a number shown on the page, follow the steps for callers in this guide.
The page will not close. What can I do?
Press Esc to leave full-screen mode, then close the tab. If the browser is frozen, open Task Manager with Ctrl + Shift + Esc, select the browser and click End task. When you restart the browser, do not restore tabs.
If the page loads again on start, open a new window and close the old one, then remove the page from the browser's startup settings. Restarting the PC also works. Nothing was installed by the page, so closing it by force is safe and loses nothing.
Which browser settings protect against fake alerts?
Three matter most. First, notifications: set your browser to ask before allowing them, and block sites you do not trust. Second, reputation checks: SmartScreen in Edge and Safe Browsing in Chrome warn you before known scam pages load, and Firefox has its own deceptive-content protection under Privacy & Security.
Third, pop-ups and redirects: keep the default blocking on. Add a reputable ad blocker if fake alerts keep reaching you through ads on sites you use. Review the notification list every few months.
Will Fortect remove Google Critical Security alert?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Google Critical Security alert, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- How-to Geek: What's the Difference Between a VPN and a Proxy? (read October 5, 2026)
- Wikipedia: Phishing (read October 5, 2026)
- CSO: What is ransomware? How it works and how to remove it (read October 5, 2026)
- Twitter: The AntiSocial Engineer (read October 5, 2026)
- FTC: How to spot, avoid and report tech support scams (read October 5, 2026)