
CyberWare scam: how to spot it and what to do
CyberWare is a cybercriminal group that has been performing malware delivery attacks and to various organizations and entities. Since its emergence, the gang began to operate vigilante activities in order to fight against, as they claim, scammers, fake loan sites, and various companies.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Do it yourself · free Remove CyberWare scam yourself 4 steps, about 12 minutes, no software needed.
Start the steps
CyberWare scam: summary
| Distribution | Spam emails, YouTube videos, fake screenshots, etc. |
|---|---|
| Name | CyberWare scam |
| Type | Cybercriminal gang spreading malware, scams, and DDoS attacks |
| Symptoms | A phishing e-mail asking you to sign in |
| Evidence | 4 write-ups by security sites; details still limited |
| Arrives as | |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 5 more facts
| Pretends to be | A well-known company |
|---|---|
| Claim | Your account needs urgent attention |
| Asks for | Your password |
| First seen | 21 August 2020 |
| Facts checked | 7 October 2026 |
What the CyberWare scam message looks like
The wording as reported: a phishing e-mail asking you to sign in
We are anonymous.
We are legion.
We do not forgive.
We do not forget.
Expect us.
From our report of Aug 2020 · not reviewed since
Hackers use email to deliver malicious files
MilkmanVictory ransomware was delivered via targeted emails.
Typically, the attacker's users various social engineering techniques in order to make users click on the email attachment or the embedded link. Hackers can disguise a link in a way that it might look legitimate and, if users do not hover over it, they will be sent to a malicious site.
While, in some cases, malware infiltration can occur right after that (in case the system suffers from software vulnerabilities), MilkmanVictory takes a simpler approach.
Instead, the malicious link redirects users to a file that looks like a simple PDF file - various obfuscation techniques are used to achieve that impression. Once clicked, a macro is executed, and the malicious payload is downloaded from a remote server onto the computer.
Thus, it is important to stay away from malicious emails that can be encountered at any time. Do not ignore the warnings provided by your email provider scanner - malicious files or links can often be detected, and users are always informed about those findings. Besides, uploading the file to an analysis site such as Virus Total or scanning it with reputable anti-malware software is advisable.
How to tell the CyberWare scam message is fake
From our report of Aug 2020 · not reviewed since
- If your system has suffered a malware attack due to CyberWare scams, you should terminate the infection by performing a full system scan with a powerful anti-malware software
Is CyberWare scam dangerous? What the senders want
From our report of Aug 2020 · not reviewed since
CyberWare scam is a term used to describe malicious activities performed by a hacking group
CyberWare is a cybercriminal group that has been performing malware delivery attacks and to various organizations and entities.
Since its emergence, the gang began to operate vigilante activities in order to fight against, as they claim, scammers, fake loan sites, and various companies. Over time, they produced DDoS attacks that were aimed at several companies worldwide, which took down their websites. In May, security researchers also spotted ransomware MilkmanVictory being spread via spam emails to the alleged scam companies.
CyberWare scams have been prominent over the past few months, as the gang has been demonstrating its dissatisfaction with activities of various legitimate companies, and spreading lies around the internet. While cybercriminals (according to the gang) aim justice, they have never provided any evidence for the claims and rather seek to be some type of internet heroes.
One of the prominent targets of CyberWare scam has been a company going under the name of Lajunen Loan, also known as Lajunen-laina, Banwulaina, or Zorgolaina. The attackers claim that the company is trying to scam victims by providing fake loan acquisition forms, where users need to pay the initial fee to apply for the payment. Nonetheless, they are never provided with the loan at the end, according to cybercriminals.
While the scam sites that attempt to steal money from victims are indeed dangerous and should be taken down, performing illegal acts (DDoS, ransomware attacks) is still an illegal activity and is punishable by law, regardless of how noble the goals of the attackers are.
CyberWare scam and vigilante acts are not justifiable, regardless of who their actions are aimed at. Scam and illegal sites are investigated by law enforcement and the local authorities. The worst part is that CyberWare scam affects even legitimate companies that have nothing to do with scamming.
With the MilkmanVictory ransomware, Cyberware hackers aimed to destroy the businesses of the alleged scammers. Instead of asking for a ransom and providing contact information, threat actors simply state that the computer was destroyed because "we know you are a scammer."
Cyberware uses HiddenTear open-source code as a base for their customized ransomware, and the same pattern was seen in the 2spyware ransomware, which was most likely compiled by the same gang in order to diminish the reputation of a legitimate malware removal guide website.
CyberWare scams can be observed in various other ways. For example, they are keen on using social media platforms such as Twitter or YouTube to upload videos that are voiced by a voice generator. They are often filled with threats and also often accompanied by a slogan:
Without a doubt, CyberWare scam removal is an important step to take. If you have been sent a suspicious email that claims about alleged scams or asks you to open suspicious email attachments, do not open them, as you might end up being infected with ransomware or other malware.
What to do after the CyberWare scam e-mail
If you only received the message and clicked nothing, step 3 is all you need.
If you clicked the link or typed anything on the page it opened, do every step, starting with the password.
Step 1: Change the password you typed on the fake page
If you entered a password after clicking the link in the CyberWare scam message, treat that account as known to the sender.
Open the provider's real site by typing its address yourself, not through any link in the e-mail, and change the password there. Choose a new one you have never used before, and change it on every other account that shared the old one.
Then use the option to sign out of all other sessions or devices, if the provider has one. This works the same in any browser on Windows 11 and Windows 10.
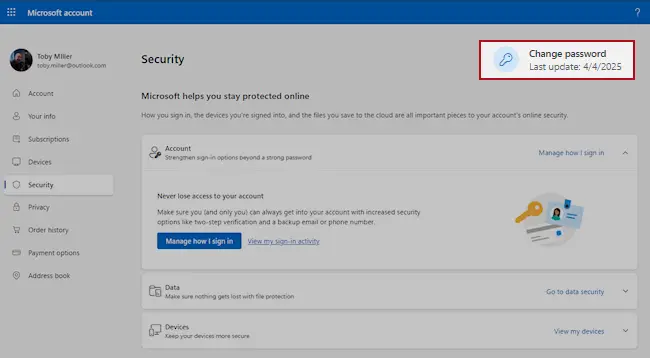
Microsoft account, Security page (account.microsoft.com/security): Change password. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Turn on two-step verification
Two-step verification asks for a code from your phone or an authenticator app whenever someone signs in from a new device. A stolen password alone is then not enough to open the mailbox.
Turn it on in the security settings of the e-mail account first, then for the bank, shop and social accounts that send their reset links to that address.
While you are there, check the recovery e-mail and phone number and the forwarding rules, which attackers sometimes change to keep access. The settings pages look the same on Windows 11 and Windows 10.
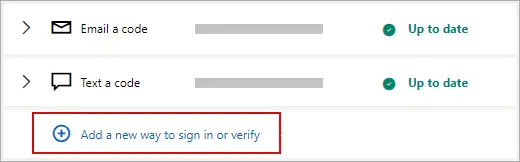
Microsoft account: Manage how I sign in, where two-step verification and the sign-in methods are. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Report the e-mail and delete it
Report the message instead of only deleting it. In Outlook choose Report > Report phishing, in Gmail the three-dot menu > Report phishing; the provider then blocks the same message for other people.
Do not reply and do not click anything else in it. On a work account, forward it to your IT team as an attachment first. Web mail and the mail apps on Windows 11 and Windows 10 offer the same options.
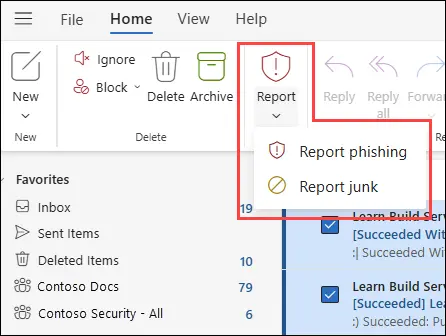
New Outlook for Windows and Outlook on the web: Report > Report phishing. Full procedure with screenshots: Report a phishing e-mail
Step 4: Scan the PC if you opened a file from the message
A page that only asked for a password installs nothing, so most readers can skip this step.
If the CyberWare scam e-mail or the page it opened made you download or open a file, delete it and run a full scan, then a Microsoft Defender Offline scan.
In Windows 11 and Windows 10 open Windows Security > Virus & threat protection > Scan options, select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts and the scan takes about 15 minutes, so save your work first.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
From our report of Aug 2020 · not reviewed since
CyberWare scam removal guide
If you encountered a CyberWare scam on Twitter, YouTube, or other platforms, you should not share, not like, as these guys are dangerous individuals who spread malware and perform other malicious activities. If you happen to be infected with malware that was distributed by the group, you can remove CyberWare virus by performing a full system scan with powerful anti-malware software.
Also, if you receive a malicious email, CyberWare scam removal can be performed simply by deleting the email - it is best not to interact with it in any way. Once the malicious content is opened, you might lose your personal files forever, or a Trojan might be able to spy on you without giving out any signs.
[GI=method-1]Access Safe Mode with Networking in case malware is tampering with your security software
Questions about CyberWare scam
I opened the "We do not forgive." e-mail. Am I hacked?
No. Opening and reading a phishing e-mail does not give anyone access to your account or your PC. Modern mail programs block scripts and remote content by default, so reading the message "We do not forgive." only showed you text and pictures.
The danger comes from clicking the button and typing your password on the page it opens, or from opening an attached file. If you did neither, report the message as phishing and delete it.
If you clicked but closed the page without typing anything, there is also nothing to fix. If you did type a password, change it from another device and turn on two-step verification.
How fast do I need to react after signing in on the "We do not forgive." page?
As fast as you can. Stolen passwords are often tried within minutes, and the first thing an attacker usually changes is the recovery e-mail or phone, which locks you out. Change the password from a clean device first, then sign out everywhere and review the recovery settings.
If you are already locked out, use the provider's account recovery form straight away and mention that the page behind "We do not forgive." took your password. Warn your contacts, since a taken-over mailbox is often used to send the same phishing to them.
Is CyberWare scam really from a well-known company?
No. It is sent by scammers who copy the name and look of a well-known company. The sender address and the links do not belong to it, and the message asks for your password, which a real company does not request through an unexpected message.
If you want to be sure about your account, open the website or app of a well-known company the way you normally do, not through the message, and look for notices there. Then delete the message and report it as phishing. If you already followed its instructions, use the steps in this guide for your case.
Is it true that your account needs urgent attention?
No. The claim that your account needs urgent attention is the hook of CyberWare scam, invented to give you a reason to act quickly. Scammers pick a story that could plausibly apply to many people, so it may feel relevant to you, but nothing in the message is based on your real accounts or devices.
If the claim concerns a service you use, check it there directly, by opening the website or app yourself. You will find no such problem. Then delete the message and report it as phishing.
What happens if I do what CyberWare scam asks?
The scammers get your password, and they use it quickly. Passwords are tried on the real service within minutes, cards are charged or added to phone wallets, remote access is used to open your bank, and crypto is moved on at once.
Documents surface later as accounts in your name. If you already did what the message asked, do not wait to see what happens; follow the steps in this guide for your case today. Speed matters more than anything else here.
Will a well-known company refund me if I fell for CyberWare scam?
A well-known company did not send the message and is not responsible for it, so a refund usually comes from your bank or card issuer, not from the brand. Call the bank first if you paid.
It still helps to tell the real company: they can secure your account, add notes for their fraud team and take down pages that use their name. Contact them through their official website or app only, never through the message or a search ad. Keep the message as evidence.
Should I reply or unsubscribe?
No. A reply confirms that your address is active and read, which leads to more scams. The unsubscribe link in a scam message is part of the scam and may lead to a phishing page. Mark the message as spam or phishing and delete it.
Block the sender if your mail app allows it, though scammers change addresses often. If the scam came by text message, do not reply STOP either. If it came through social media, use the platform's report function and block the account.
Does CyberWare scam mean my PC is hacked?
Not necessarily. The sign reported, an e-mail with the subject "We do not forgive.", is usually caused by a password that leaked or was phished, not by malware on the PC.
Passwords leak in breaches of other websites and are tried on many services. Still, rule out the PC:
- run a full scan in Windows Security
- check Installed apps for anything you do not recognise
- look at the browser's extensions
If all is clean, the problem lies with the account, and changing the password with two-step verification turned on is the fix.
How can I spot messages like CyberWare scam in future?
Check the sender's actual address, not only the name. Hover over links before clicking and compare the domain with the real one. Be suspicious of urgency, threats, prizes, unexpected invoices and requests for passwords, codes, card data or crypto.
Do not call phone numbers from unexpected messages; use the number on the official site or your card. When in doubt, go to the service directly through its app or a bookmark. Phishing protection and two-step verification limit the damage when a scam gets through.
Will Fortect remove CyberWare scam?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For CyberWare scam, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Wikipedia: Vulnerability (computing) (read October 7, 2026)
- FTC: How to recognize and avoid phishing scams (read October 7, 2026)
- CISA: Recognize and report phishing (read October 7, 2026)
- Microsoft Support: Protect yourself from phishing (read October 7, 2026)
- NCSC: Phishing attacks, dealing with suspicious e-mails and messages (read October 7, 2026)