
Fireball virus: what it is and how to remove it
Fireball virus is a highly dangerous Chinese malware (created by Rafotech) that has compromised over 250 million computers worldwide. The malicious software hijacks victims' web browsers and replaces current homepage, new tab and default search engine values with URL that points to Rafotech search engine.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
An automatic scan checks installed programs, startup items and browser extensions for anything that came with Fireball virus.
Do it yourself · free Remove Fireball virus yourself 5 steps, about 15 minutes, no software needed.
Start the steps
Fireball virus: summary
| Detection names | No Microsoft detection name is known |
|---|---|
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Name | Fireball virus |
| Type | Loader |
| Symptoms | An unknown program in Installed apps |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 3 more facts
| Evidence | 4 write-ups by security sites; details still limited |
|---|---|
| First seen | 8 June 2017 |
| Facts checked | 7 October 2026 |
What Fireball virus does on an infected PC
From our report of Jun 2017 · not reviewed since
Fireball malware is a browser hijacker that can function as a backdoor
Fireball virus is a highly dangerous Chinese malware (created by Rafotech) that has compromised over 250 million computers worldwide.
The malicious software hijacks victims' web browsers and replaces current homepage, new tab and default search engine values with URL that points to Rafotech search engine. Results brought by this questionable search tool seem to be provided by giant companies like Google or Yahoo, although actually they are filled with advertisements promoting possibly dangerous sites.
Each of the fake Rafotech search tools contains tracking pixels that are used to record private users' data. However, despite posing a threat to victim's privacy, displaying intrusive pop-up ads and manipulating search results, the hijacker is capable of doing so much more. It turns out that Fireball malware can be easily transformed into a weapon that could give the attackers opportunity to infect the compromised machines with additional viruses.
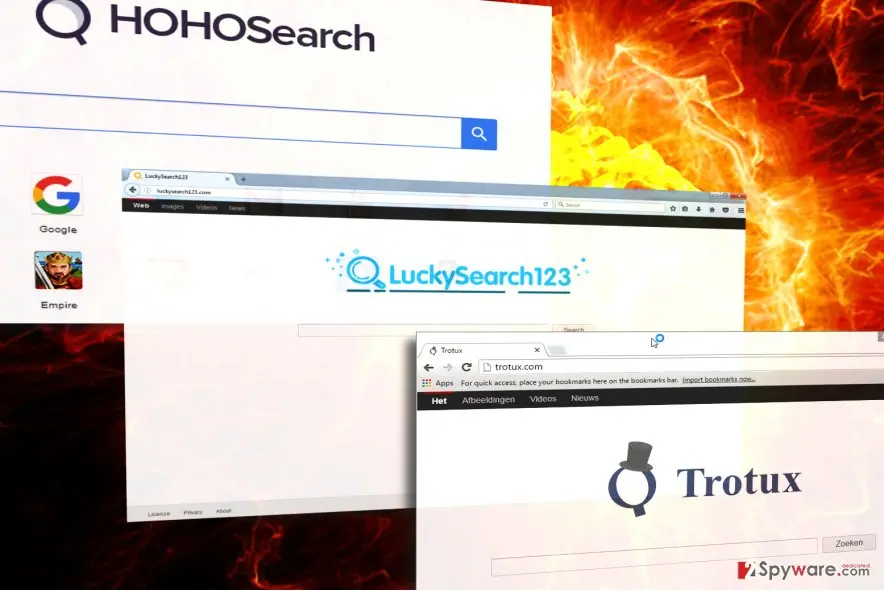
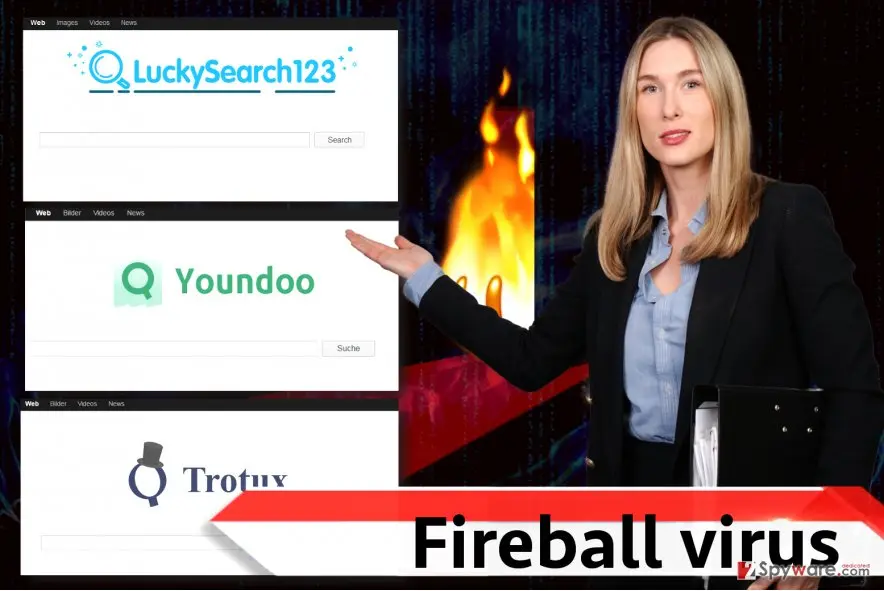
It is a must to remove Fireball hijacker as soon as possible because frauds can easily leverage it to execute any type of code on the system. For its removal, we highly suggest using or software. Below, you can see part of search engines run by Rafotech:
Research shows that the malicious Fireball adware mostly affected residents of India, Brazil, Mexico, Indonesia, and the United States. The developer of the malware, known as Rafotech, denies creating browser hijackers, but praises being a successful digital marketing company that provides a possibility to access over 300 million users worldwide.
However, the activity of this virus clearly discloses its relations with this company. On top of that, the cyber threat demonstrates a great sophistication level - it has anti-detection features, the structure of multiple layers and also ability to communicate with a Command & Control server.
This doesn't look like a typical browser hijacker to us - rather something way more powerful and malicious. In fact, the software reminds us of a critical backdoor . It goes without saying that Fireball malware removal should become your top-priority task. Remember that only reputable and up-to-date programs will detect the virus.
- Trotux.com;
- attirerPage.com;
- Startpageing123.com;
- Youndoo.com;
- Hohosearch.com;
- Yessearches.com;
- Luckysearch123.com.
How Fireball virus got on your PC
From our report of Jun 2017 · not reviewed since
Bundling is the main attack vector used by Fireball hijacker's developer.
At the moment, it is known that the hijacker is actively distributed with the help of DealWifi, Mustang Browser, Soso Desktop, FVP Imageviewer and much more. Users must be careful when installing free programs from the Internet, no matter if they appear to be legitimate at first sight.
The problem is, the developer of the described malware balances on the edge of legitimacy and leverages the fact that adware/browser hijackers are theoretically legitimate programs. At the moment of Fireball's installation, none of the malicious programs are installed alongside it.
However, cyber security experts have expressed their beliefs that the malware is distributed with the help of additional methods such as spam. What is more, the company is suspected of buying installs from malicious actors.
To prevent Fireball malware attack, avoid installing software from suspicious web sources. On top of that, always choose Custom or Advanced settings when installing software. These options allows modifying components of downloaded software packs, meaning you can deselect unwanted additions and install only the software you were initially looking for.
How to remove Fireball virus
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Programs like Fireball virus add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 2: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after Fireball virus, its publisher or created on the day the problem started.Delete those folders, and check
C:\Program FilesandC:\Program Files (x86)too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
A scan finds the parts of Fireball virus that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Fireball virus can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Jun 2017 · not reviewed since
Remove Fireball malware from your machine
Fireball virus has been bothering computer users for years, changing their browser settings and performing other intolerable activities.
If you have been bothered by the aforementioned search engines at least once in your lifetime, you must scan the system to remove Fireball malware ASAP.
Please do not try to root out the infection manually - it is a highly sophisticated threat that, as we mentioned, obfuscates itself on the system to avoid detection. The virus sneaks into the system using different names, and that is another reason why it could be impossible to detect it manually.
[GI=method-1]To remove Fireball malware, please carefully follow the given guide. You have to make sure that the virus won't try to block your anti-malware software, so reboot it into neutral mode - Safe Mode with Networking. Once you do so, launch the security software to eliminate the virus along with all of its files.
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed fireball virus in the list of installed apps, a sign of a program that could read browser data, the clean-up is only half of the work.
The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
Questions about Fireball virus
Is Fireball virus a virus?
Most programs that appear the way Fireball virus did are not viruses in the strict sense. They are potentially unwanted programs:
- real software that arrives bundled with other downloads and then shows offers
- changes browser settings
- starts with Windows
Some are harmless, some are annoying and a few carry adware. What makes it worth removing is that you did not choose it.
Uninstall it from Installed apps and check the startup list and the browsers for anything added the same day. If it refuses to uninstall or returns after a restart, treat it as more serious and run a Microsoft Defender offline scan.
Fireball virus came back after I uninstalled it. Why?
Something else is reinstalling it. Common causes are a second program from the same publisher, a scheduled task that downloads it again, or a browser extension that keeps prompting for it. Sort Installed apps by install date and uninstall each entry from the same day that you did not choose.
Then open Task Scheduler and look in the Task Scheduler Library for tasks with updater-style names that you do not recognise. Check Startup apps in Task Manager too. If Fireball virus still returns, start Windows in Safe Mode, uninstall it there and run a Microsoft Defender offline scan, which looks for loaders that ordinary scans can miss.
Which malware family is Fireball virus?
That is not known yet. Fireball virus has been reported by people who saw fireball virus in the list of installed apps, but no sample has been analysed publicly, so security companies have not assigned it to a family. The name you see may be a file or program name chosen by the authors, not a family name.
This does not stop you from removing it: the startup points, the offline scan and the account steps are the same for most families of this type. If Microsoft Defender or another scanner gives the file a detection name, write it down; that name is the best clue to the family and is useful when you report the incident.
How dangerous is Fireball virus?
Treat it as serious until proven otherwise. The visible sign is fireball virus in the list of installed apps, and programs that behave this way often have more abilities than they show:
- copying passwords
- downloading other malware
- giving remote access
Its family is not known yet, so nobody can say which of these it uses. The good news is that the response is the same in every case and takes about an hour:
- cut the network
- remove the startup entry
- run an offline scan
- change passwords from a clean device
If someone had remote control, a full reset is safer.
How do I know if my PC has Fireball virus?
Often you do not, which is the point of a trojan. Possible signs are an antivirus alert naming Fireball virus or a generic trojan detection, unknown programs or scheduled tasks, processes with random names in Task Manager, browser extensions you did not add, security settings turned off, slower performance, or account alerts about logins from unknown places.
The reliable check is a full scan followed by Microsoft Defender's offline scan. If you recently ran a crack, a fake installer or a command a website told you to paste, scan even without symptoms.
Should I check my other computers too?
Yes, it takes little time and removes doubt. Fireball virus itself usually stays on one PC, but the download that carried it may have been copied to other computers, shared drives may hold the same installer, and an attacker who had access could have tried saved passwords on other devices.
Run a full scan on every Windows PC in the home or office, check shared folders for the original download, and change Wi-Fi and router passwords if they were stored on the infected machine.
My antivirus was on. How did a trojan get past it?
Antivirus programs see a file only when it is written or run, and criminals test each new build against popular scanners before release. Detection catches up within hours or days, which is often after the first victims ran it.
Archives with passwords, installers that fetch the malware later, and scripts run through PowerShell make the job harder. That is why behaviour such as downloading cracks or pasting commands matters more than any setting. Keep Windows and Defender updated, and turn on Reputation-based protection in App & browser control.
I found AnyDesk or ScreenConnect that I did not install. Is that Fireball virus?
Not necessarily Fireball virus, but it is a warning sign. These are legitimate remote support tools, and criminals use them as ready-made backdoors, especially after tech support scams or fake invoice calls.
If you did not install it and no one you trust set it up, uninstall it, change passwords from a clean device and check your bank account. If someone connected to your PC through it, follow the steps for remote access trojans and consider a Windows reset. Installed apps sorted by date shows when it appeared.
Do I need to reinstall Windows to get rid of Fireball virus?
Usually not. A thorough clean-up is enough when the offline scan finds nothing afterwards and you do not see fireball virus in the list of installed apps again. A reset is the safer choice if an attacker had remote control, if security tools were switched off, or if detections come back after every clean-up.
Windows 11 can reset itself without a USB stick under Settings > System > Recovery > Reset this PC. Copy documents and photos out first and scan the copies. A reset does not change passwords or undo stolen data, so the account steps still apply.
Will Fortect remove Fireball virus?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Fireball virus, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Check Point Blog: FIREBALL – The Chinese Malware of 250 Million Computers Infected (read October 7, 2026)
- The Register: Goodness gracious, great Chinese 'Fireball' malware infects 250m systems worldwide (read October 7, 2026)
- FTC: How to recognize, remove and avoid malware (read October 7, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 7, 2026)
- Microsoft Learn: How Microsoft names malware (read October 7, 2026)