
Get-user-id ads: what it is and how to remove it
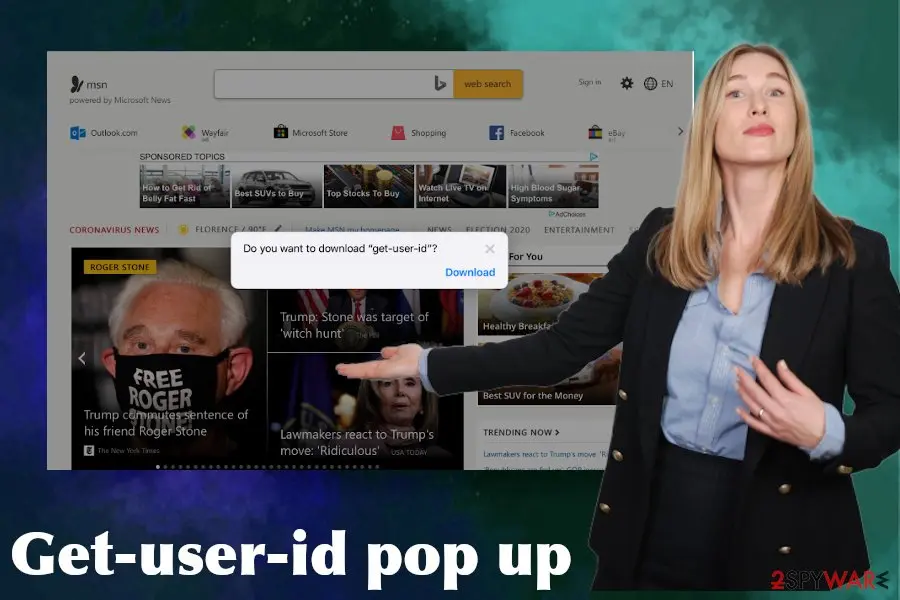
Get-user-id pop-up alert is a misleading notification that regularly shows up on websites like msn.com and asks unsuspecting users if they want to download some kind of user ID. The pop-up box is very primitive - it does not specify what kind of ID is offers to download or what is its propose.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
A scan of the PC is a quick way to confirm that nothing installed is behind the msn.com redirects.
Do it yourself · free Remove Get-user-id ads yourself 4 steps, about 12 minutes, no software needed.
Start the steps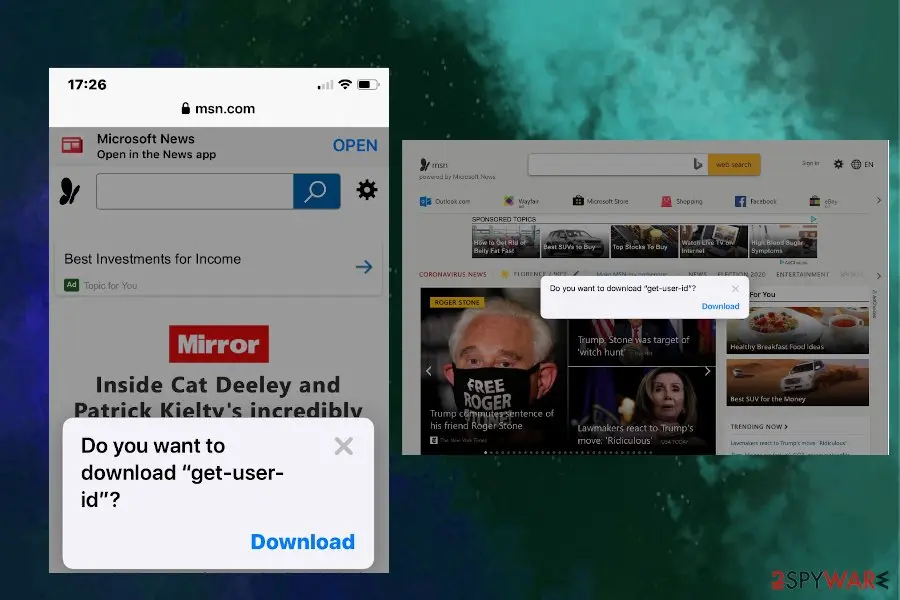
Get-user-id ads: summary
| Name | Get-user-id |
|---|---|
| Type | Scam, potentially unwanted program (PUP), adware |
| Compatibility | The pop-up emerges both on Windows, Mac, and iPhone devices |
| Danger | Medium. It's not yet clear what content the pop-up is set to download, so clicking on it poses a risk of allowing the installation of a dangerous cyber infection |
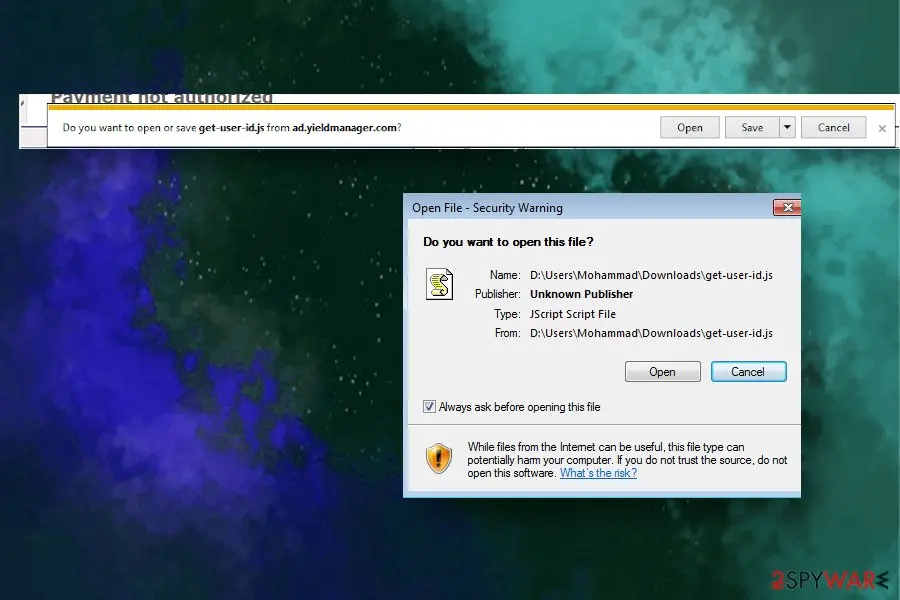
| Related files | Once clicked, the alert downloads the get-user-id.js file and saves it to D:\Users\Username\Downloads\ location |
| Affected web browsers | Any web browser can start loading the pop-up |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 11 more facts
| Web browser's maintenance | It recommended resetting the default web browser's settings. Adware and browser hijackers tend to distort the browser's settings to enable ads and redirects. Therefore, without a full reset, the browser may keep exhibiting intrusive behavior |
|---|---|
| Detection names | No Microsoft detection name is known |
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Symptoms | Redirects to an unknown domain |
| Evidence | 4 write-ups by security sites; details still limited |
| Domains | msn.com |
| Ads shown as | Redirects through ad pages |
| Browsers | Chrome, Edge and Firefox |
| First seen | 13 July 2020 |
| Facts checked | 6 October 2026 |
What the Get-user-id ads ads look like
Do you want to download "get-user-id"?
Is Get-user-id ads dangerous?
From our report of Jul 2020 · not reviewed since
Get-user-id pop-up message on Mac or Windows indicates an adware program to be hiding on the system
Get-user-id pop-up alert is a misleading notification that regularly shows up on websites like msn.com and asks unsuspecting users if they want to download some kind of user ID.
The pop-up box is very primitive - it does not specify what kind of ID is offers to download or what is its propose. It contains a single statement/question and a download button. Although it does not seem to be dangerous, the pop-up is considered a security risk as it typically comes from untrustworthy domains, such as ad.yieldmanager.com, apushnotification.com, notice-booster.site, notify-monad.com, and similar.
Get-user-id alert means that the system is infected by a potentially unwanted program (PUP) , namely adware. The latter is set to redirect the web browser to scam sites and automatically generate this controversial alert.
Not only it disrupts a web browser but also poses a risk of downloading another unwanted application or subscribe to the Push Notifications from an untrusted domain. Consequently, the default web browser, be it Google Chrome or Safari, may start generating intrusive ads and perform redirects to malware-laden third-party sites.
The reports about get-user-id pop-up alert are flooding Mac community forums and other online discussion domains. People consider the notification to be genuine and, unfortunately, many of them have fallen to click the download button. According to users, intrusive notifications stopped upon downloading the get-user-id.js file, though the anti-virus program keeps popping up with an alert about a potentially unwanted program.
We strongly recommend people not clicking on the get-user-id pop-up because it's a scam. Experts are currently working on specifying its real purpose, though it's clear that is basically used for spreading unwanted browser-based applications. Please note that cybercriminals tend to use suchlike social engineering strategies to trick less experienced PC users into trusting ads like Get User ID.
Some cybersecurity experts relate the "get-user-id" ads with older Java versions and urge people to either remove Java completely or update to the Java Version 7 Update 25 (or higher). According to them, the older versions are extremely vulnerable and can be easily exploited by criminals.
If you are not using Java, get-user-id removal requires the careful investigation of the machine and the elimination of all suspicious/unknown entries. Windows and Mac users are recommended to scan the system with a professional anti-malware program since it's the most reliable way of cleaning the malware.
If, however, you are determined to remove get-user-id virus manually, you should check the system very carefully. Mac users should double-check the following locations for suspicious entries and remove all of them:
Get-user-id pop-up ads on Chrome or Safari are intrusive, so leaving some related entries on the machine allows the notifications to keep returning. Thus, it's best to get rid of the malware package using a professional anti-malware tool. Anyway, we will provide a manual adware removal guide that the end of this article.
Such optimization programs may ensure full recovery of the system after malware installation. Otherwise, some potentially dangerous entries may keep functioning with the registries, thus slowing down the system.
- ~/Library/LaunchAgents
- /Library/LaunchAgents
- /Library/Application Support
- /Library/LaunchDaemons
From our report of Jul 2020 · not reviewed since
The web browser may start displaying intrusive pop-ups after incorrect installation of freeware
Based on NoVirus.uk research data, most of the time potentially unwanted programs (PUPs) are spread bundled with freeware and shareware.
Therefore, incorrect installation of various browser helpers, download assistants, converters, and etc. can end up with the infiltration of PUPs - adware and browser hijacker namely.
Any freeware or shareware can be, in fact, a software package. The only way to find it out is to opt for Advance technique for its installation. This method will unravel all setup windows and disclose the presence of additional features (add-ons, toolbars, extensions, etc.).
Make sure to deselect all additional programs during the installation. If, however, you skip as pre-selected additional application and click Next, it will automatically be installed. Unfortunately, statistically, the majority of users in China, America, and Europe opt for the Quick installation method and, therefore, ends up installing bundles without even being aware of that.
From our report of Jul 2020 · not reviewed since
More from our earlier report on Get-user-id
- This scam alert means a PUP to be installed.
- Thus, a full scan with anti-malware is recommended.
- Alternatively, you can check the system manually and delete all suspicious entries.
Check your browser and PC
- Address:
msn.com
How to remove Get-user-id ads
How to remove the Get-user-id extension
Do the browser steps in every browser and profile on the PC, then check Windows for the program that installed the extension.
Step 1: Remove extensions you did not add
Get-user-id often works through an extension, so go through the extension list of each browser:
chrome://extensionsedge://extensions- Extensions and themes in Firefox
Switch suspicious extensions off one at a time and reload the page where the problem shows, then remove the one that stops it, and any other you did not add.
Remember the other browsers and profiles on the PC. If Remove is missing or greyed out, a policy forces the extension, which the policy step deals with. Windows 11 and Windows 10 show the same pages.
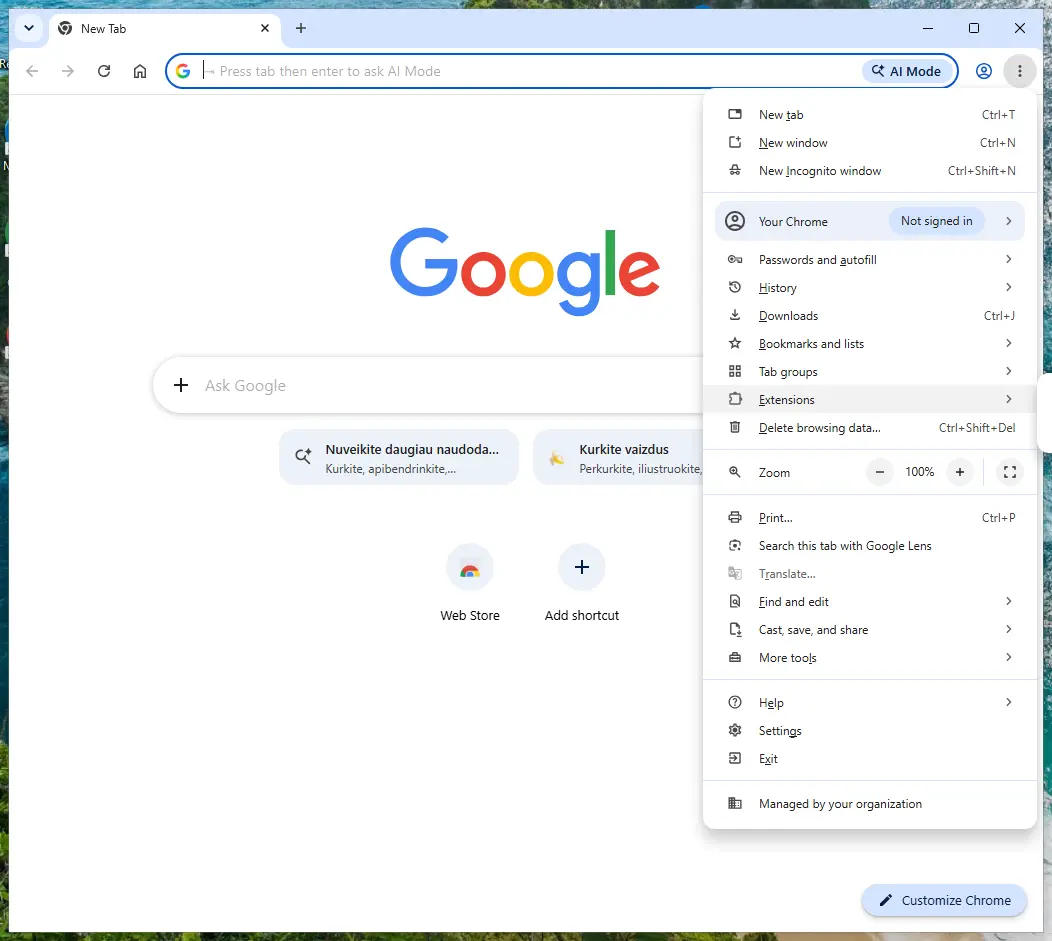
Chrome on Windows 11: More > Extensions > Manage extensions. Full procedure with screenshots: Remove a browser extension
Step 2: Uninstall programs you did not mean to install
Open Settings > Apps > Installed apps in Windows 11, or Settings > Apps > Apps & features in Windows 10, and sort the list by install date. Look at what appeared around the day the problem started and uninstall every program you do not recognise or did not choose.
Free converters, PDF and video tools, "system optimizers" and unknown browsers are the usual carriers of Get-user-id. If a name is unclear, search for it before you remove it, so you do not uninstall a driver or a Windows component.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 3: Reset the browser
Finish the browser part with a reset, which puts the search engine, start page, new tab page and site permissions back to their defaults and switches extensions off. Chrome: Settings > Reset settings > Restore settings to their original defaults.
Edge: Settings > Reset settings. Firefox: Help > More troubleshooting information > Refresh Firefox, which also removes its extensions. Your bookmarks and saved passwords are kept, and the menus are the same on Windows 11 and Windows 10.
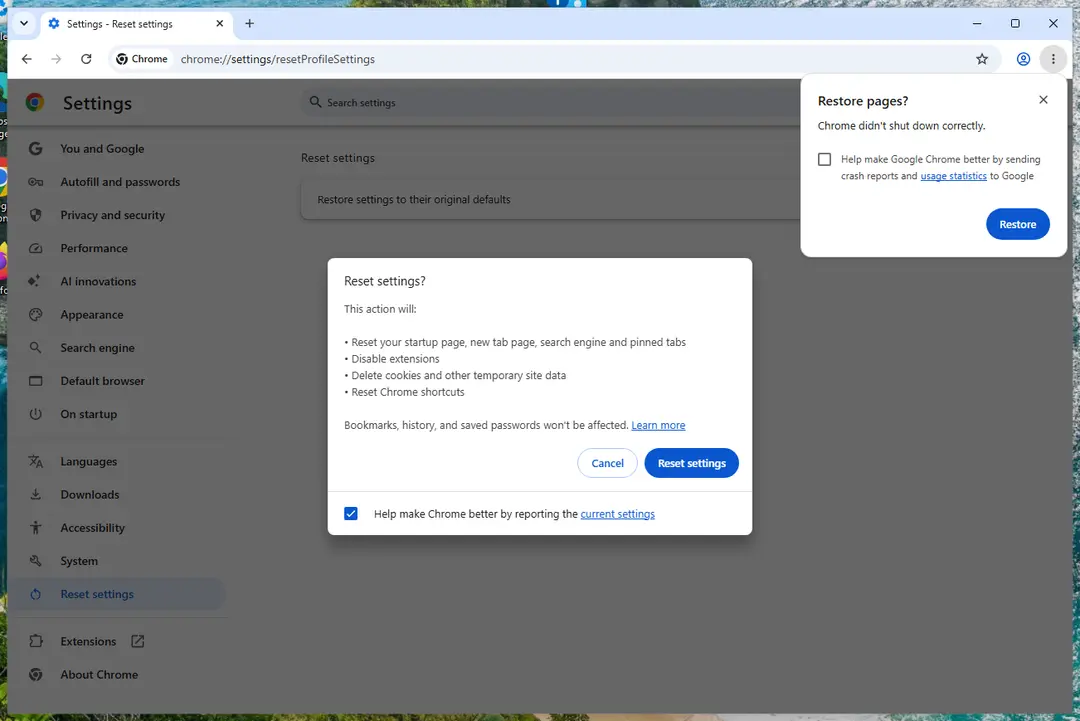
Chrome on Windows 11: Settings > Reset settings. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
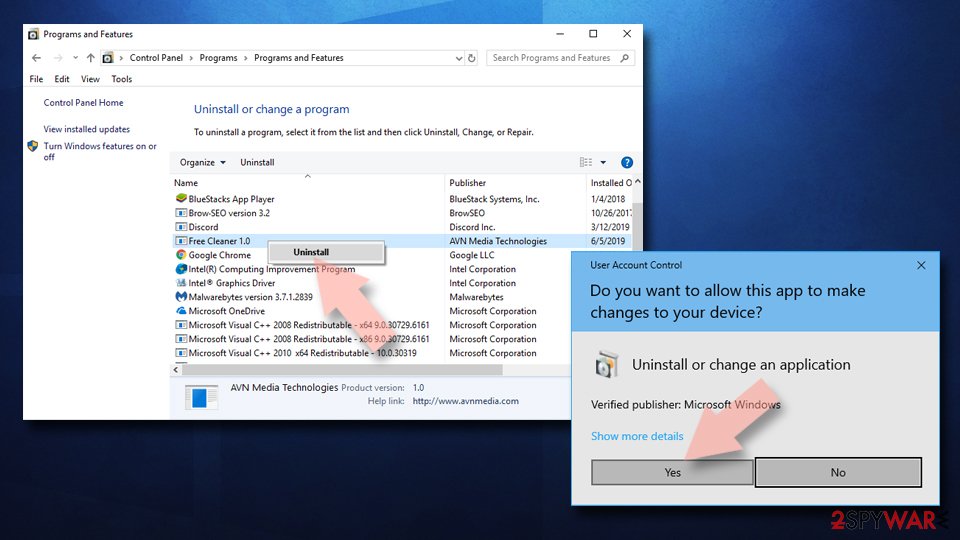
Uninstall from Windows
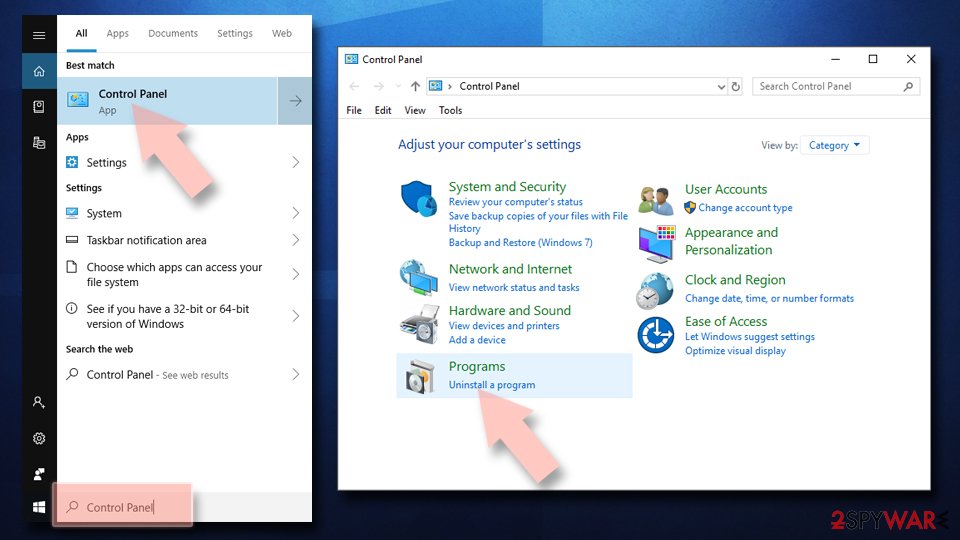
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
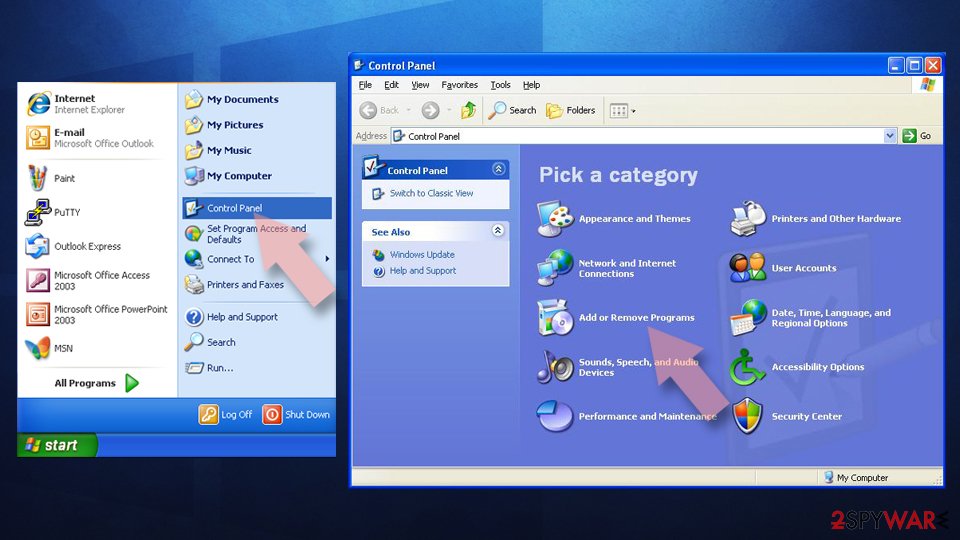
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
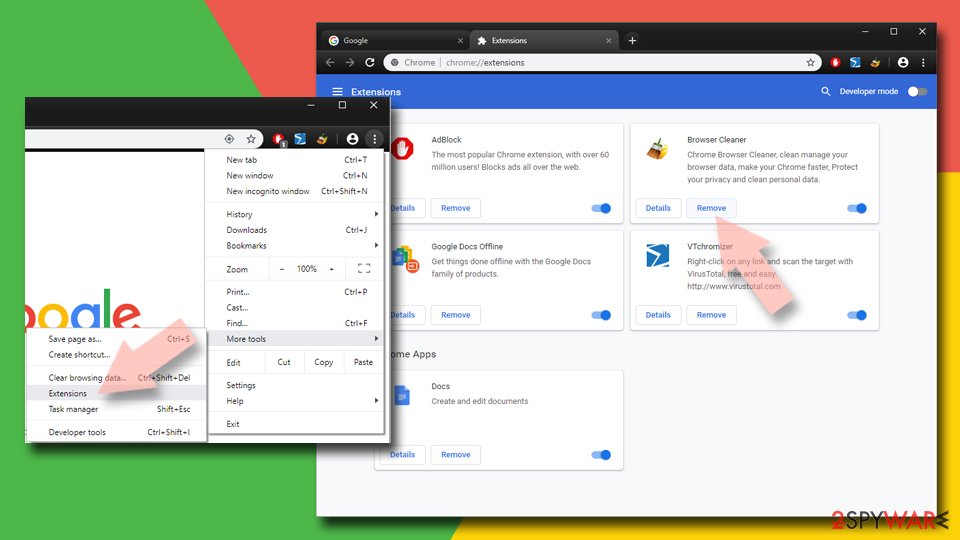
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
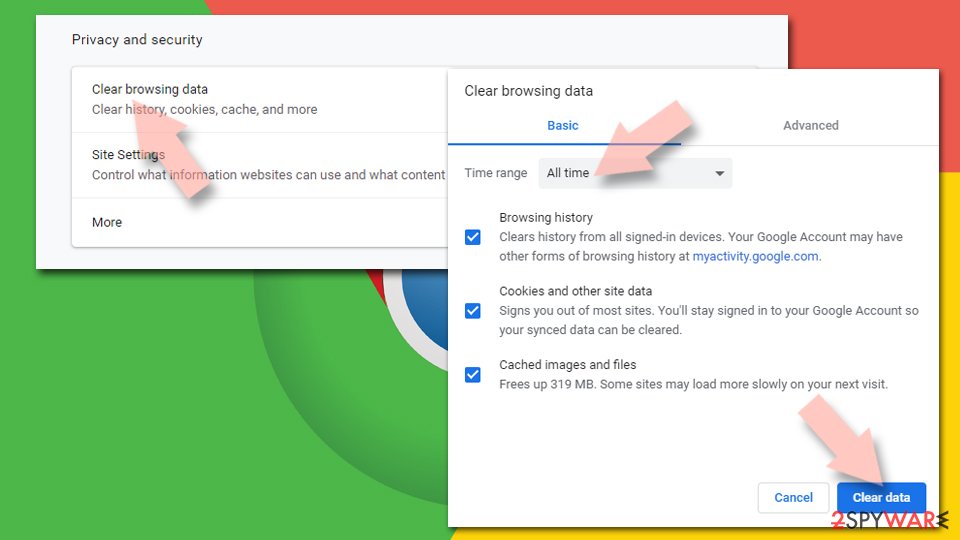
Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
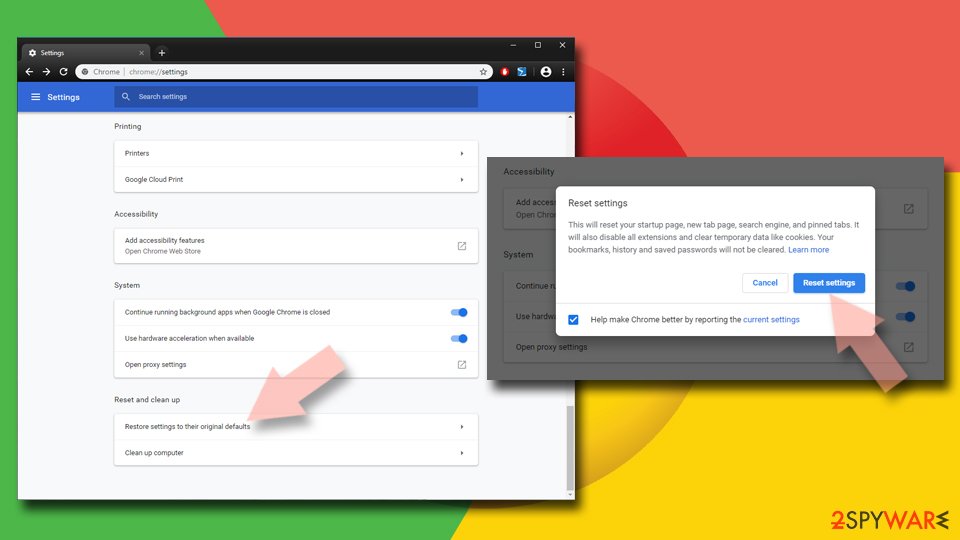
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Microsoft Edge
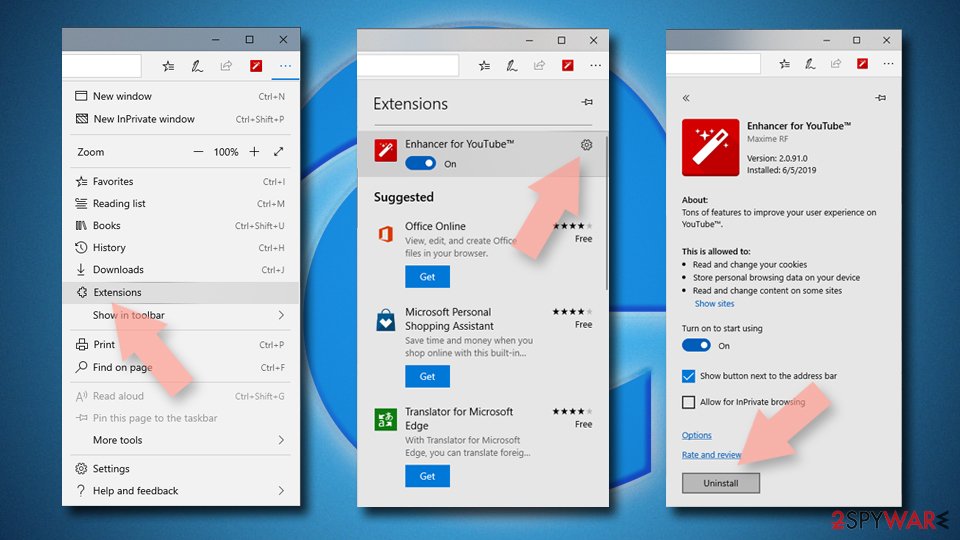
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.
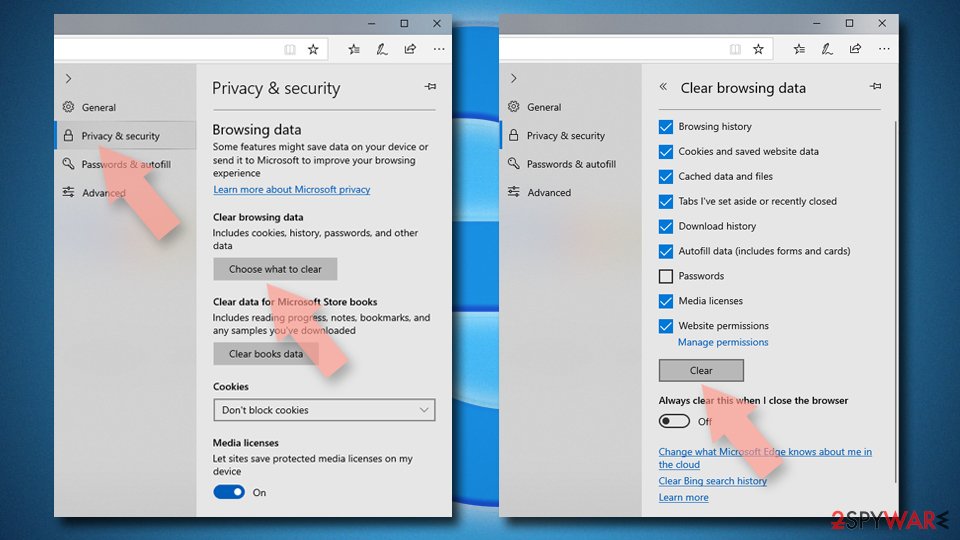
Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.
Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
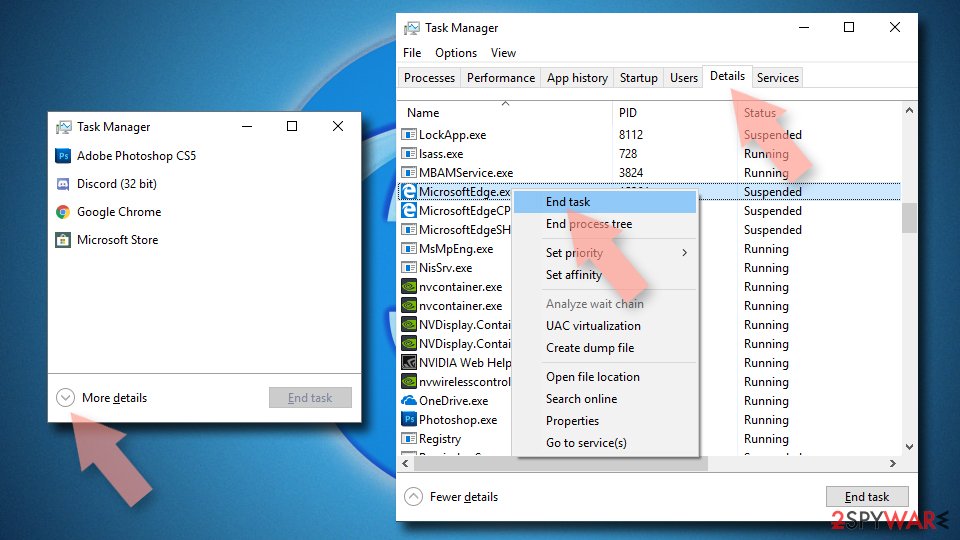
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.
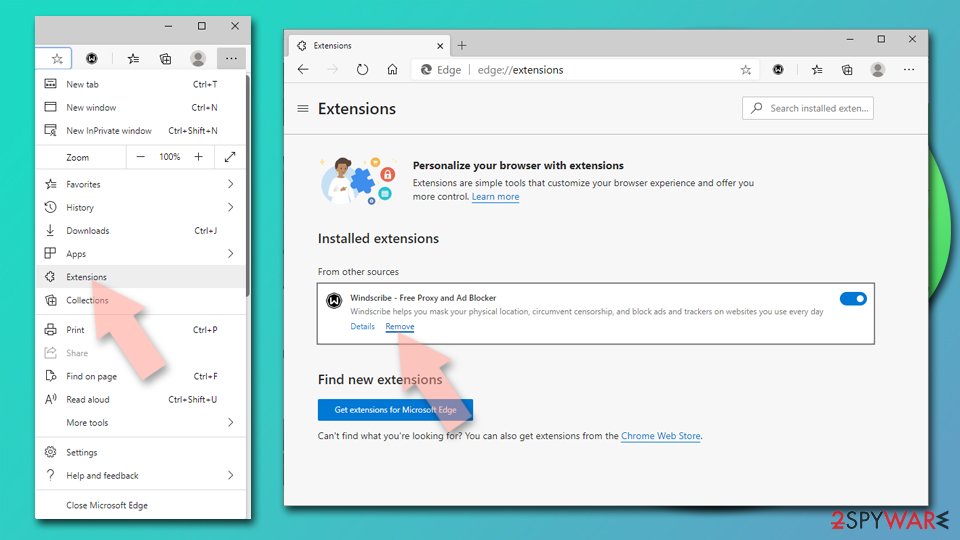
Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
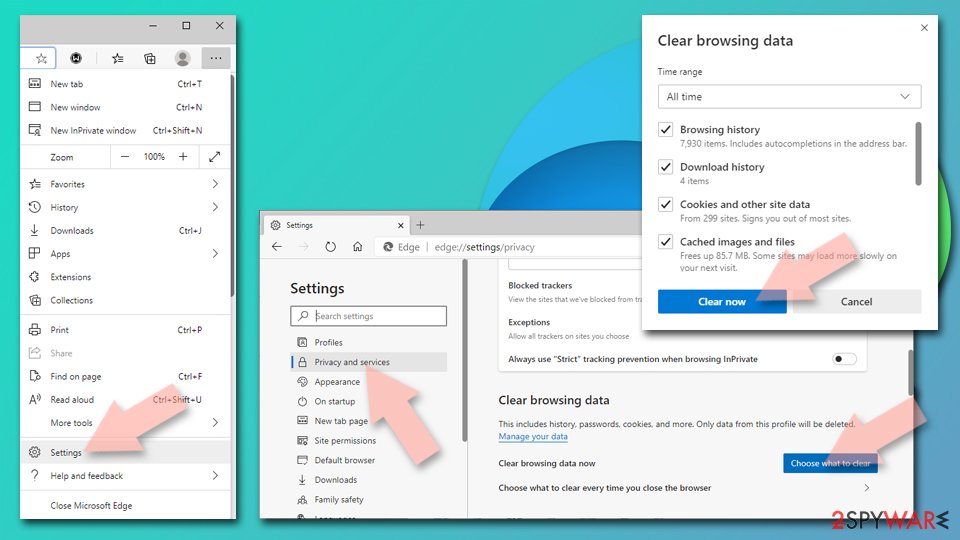
Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
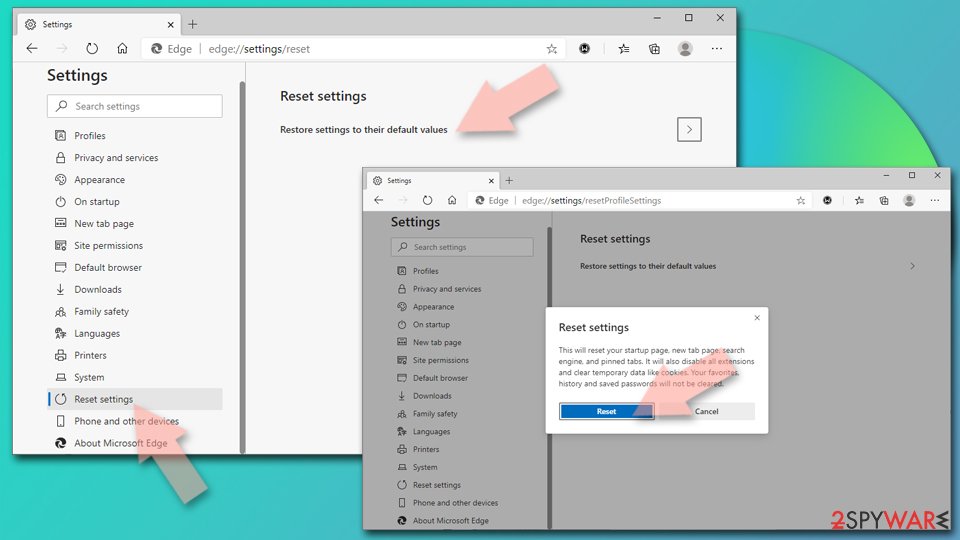
Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.
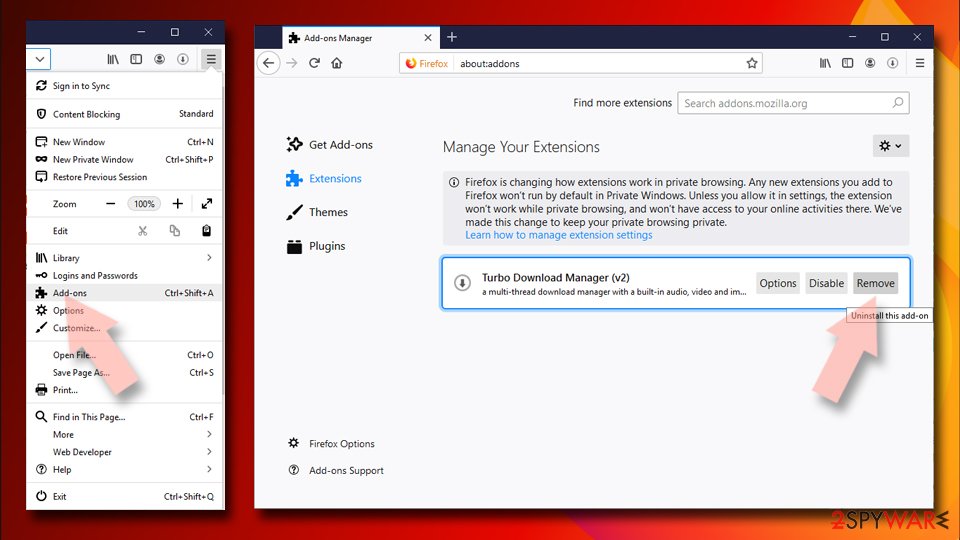
Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
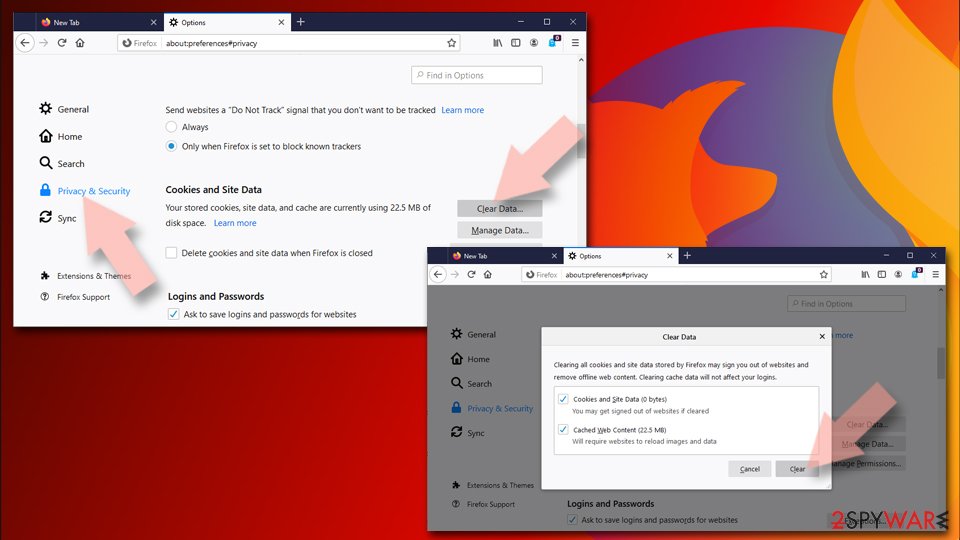
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
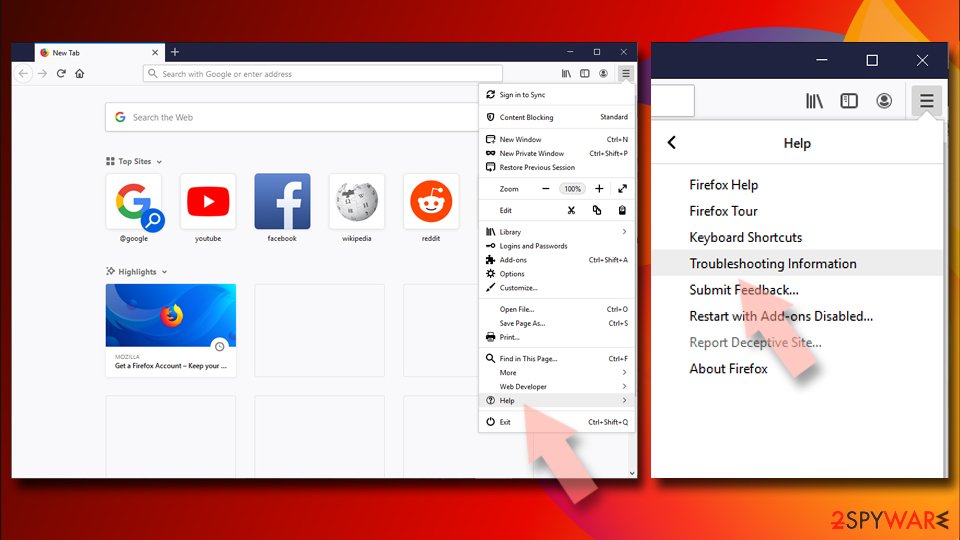
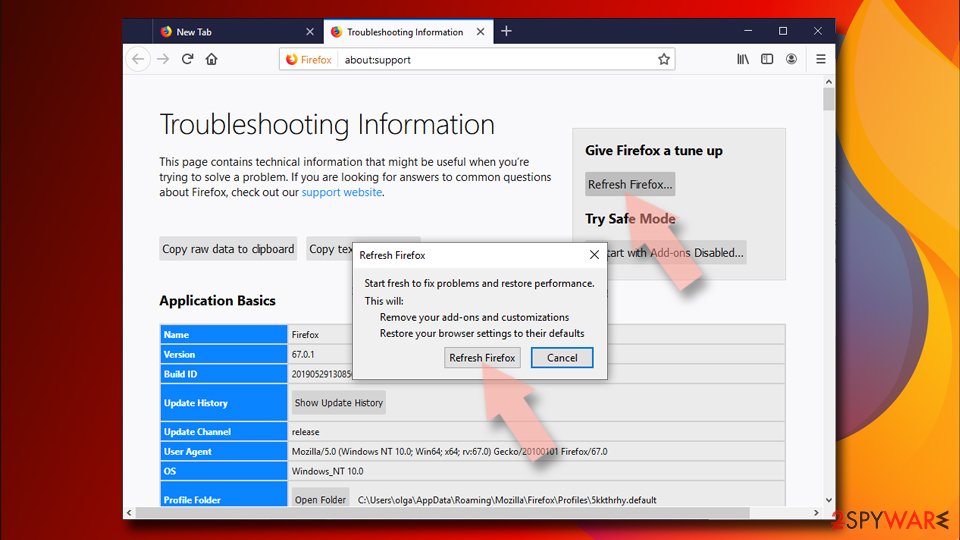
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
Remove dangerous extensions:
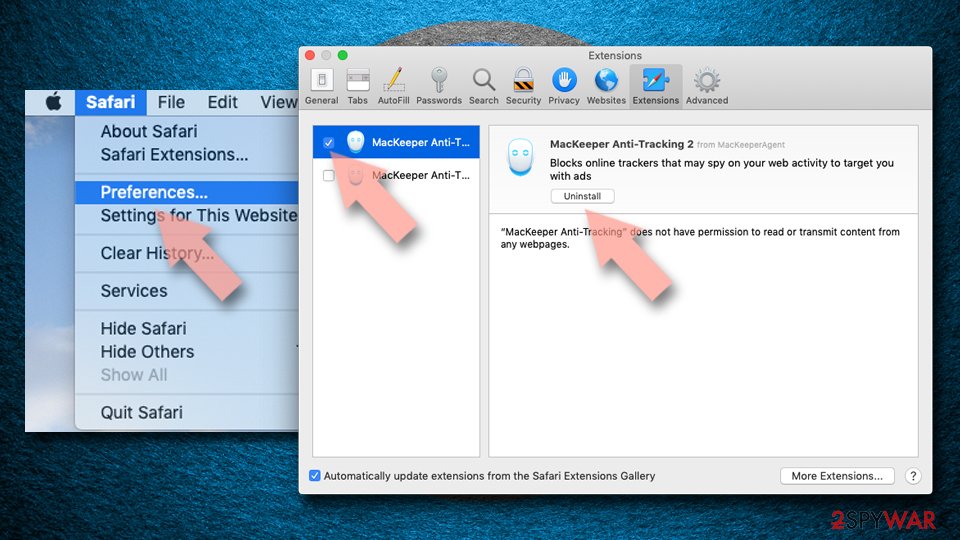
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
Clear history and website data:
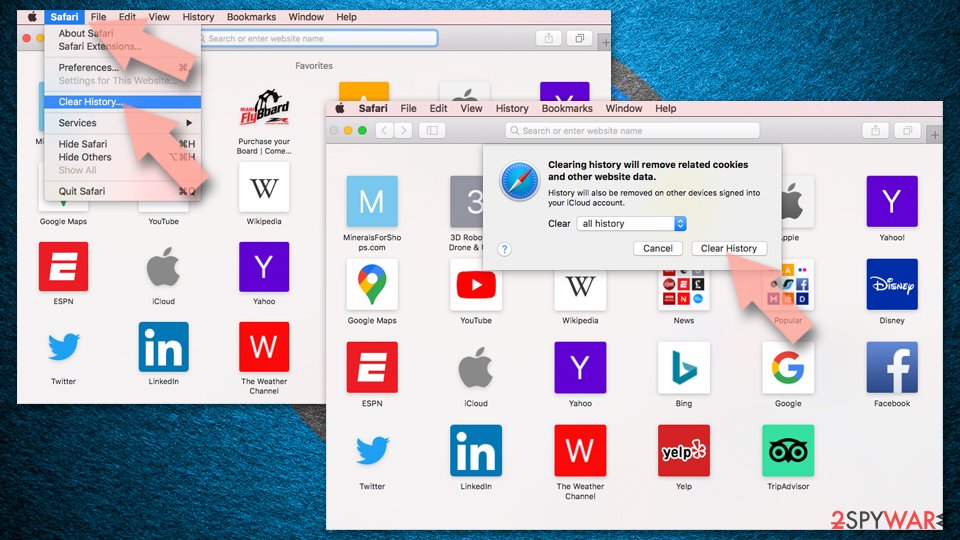
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
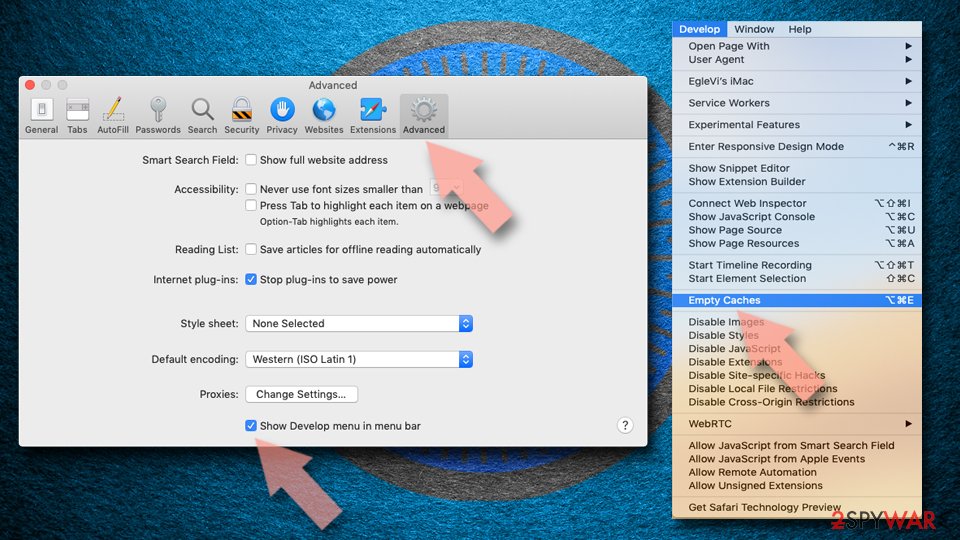
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
Remove the unwanted application:
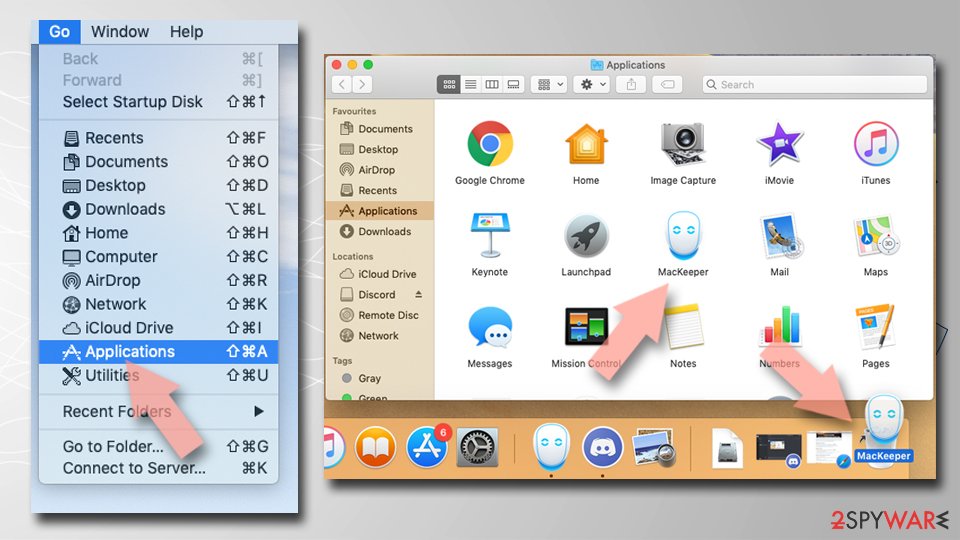
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
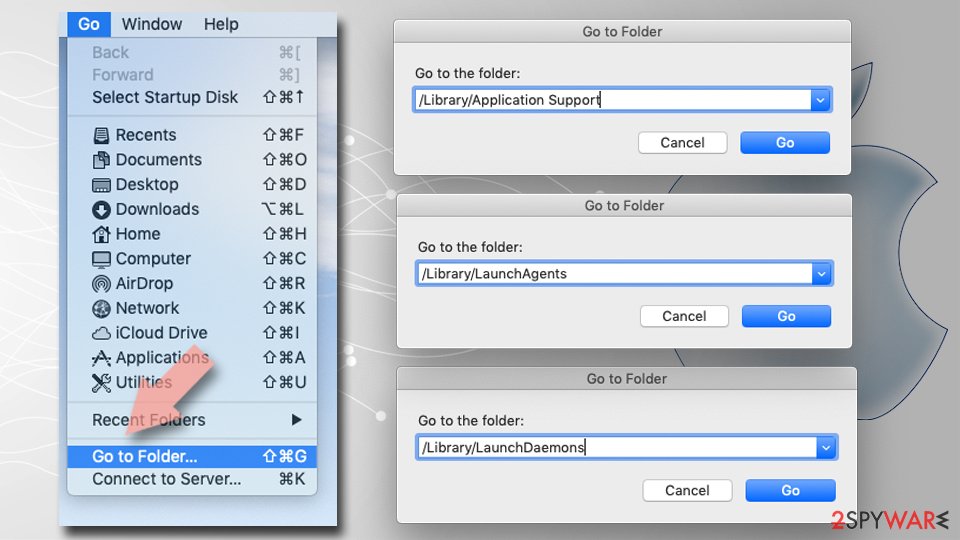
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Reset Internet Explorer
Remove dangerous add-ons:
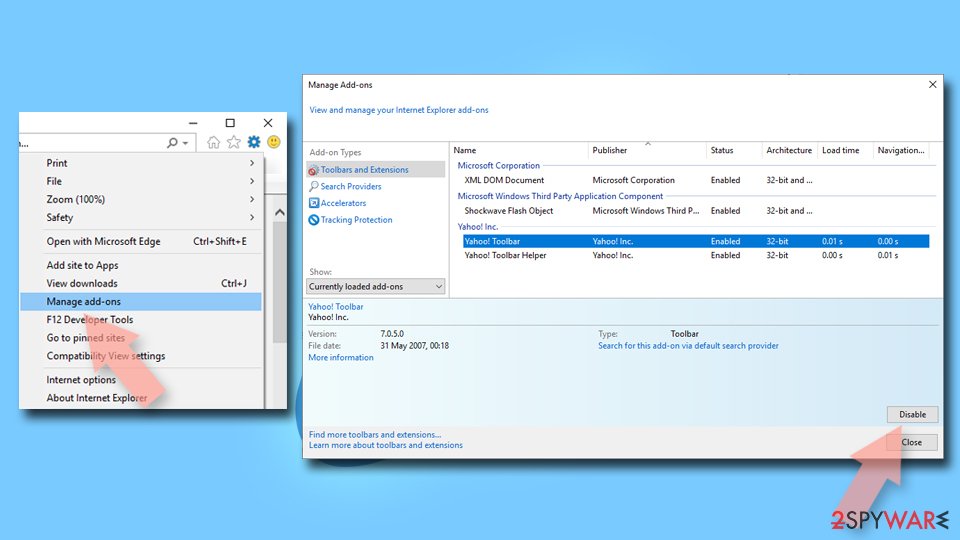
- Open Internet Explorer, click on the Gear icon (IE menu) on the top-right corner of the browser
- Pick Manage Add-ons.
- You will see a Manage Add-ons window. Here, look for suspicious plugins. Click on these entries and select Disable.
Change your homepage if it was altered:
- Open IE and click on the Gear icon.
- Select Internet Options.
- In the General tab, delete the Home page address and replace it by your preferred one (for example, Google.com).
- Click Apply and then select OK.
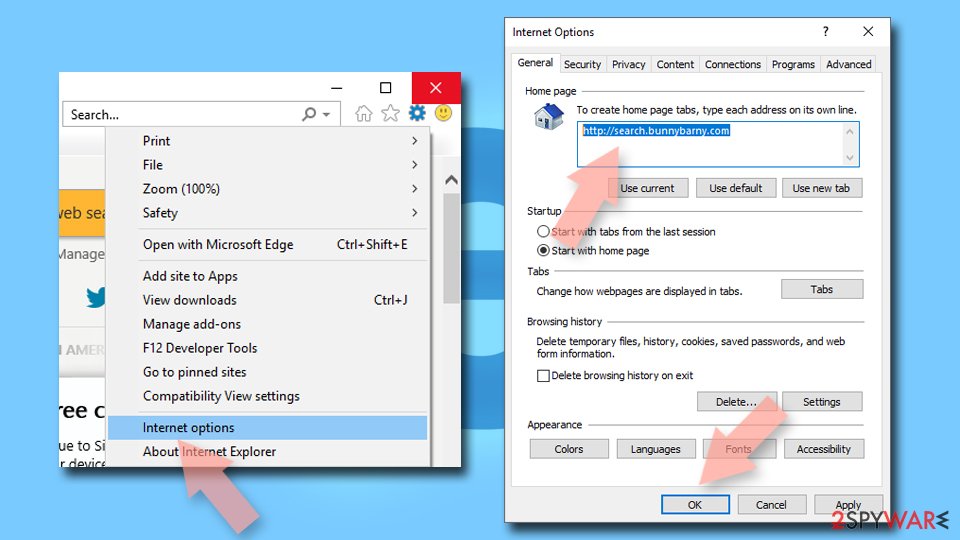
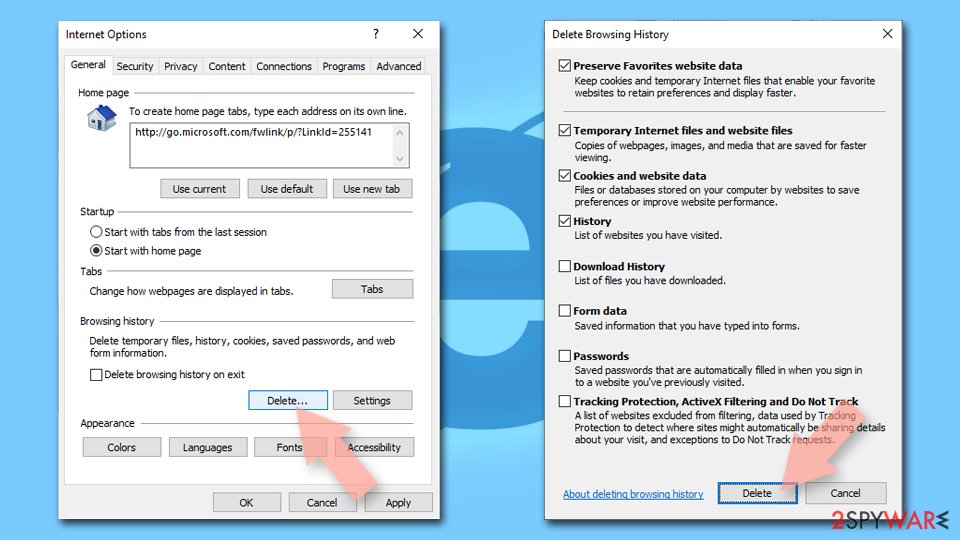
Delete temporary files:
- Press on the Gear icon and select Internet Options.
- Under Browsing history, click Delete...
- Select relevant fields and press Delete.
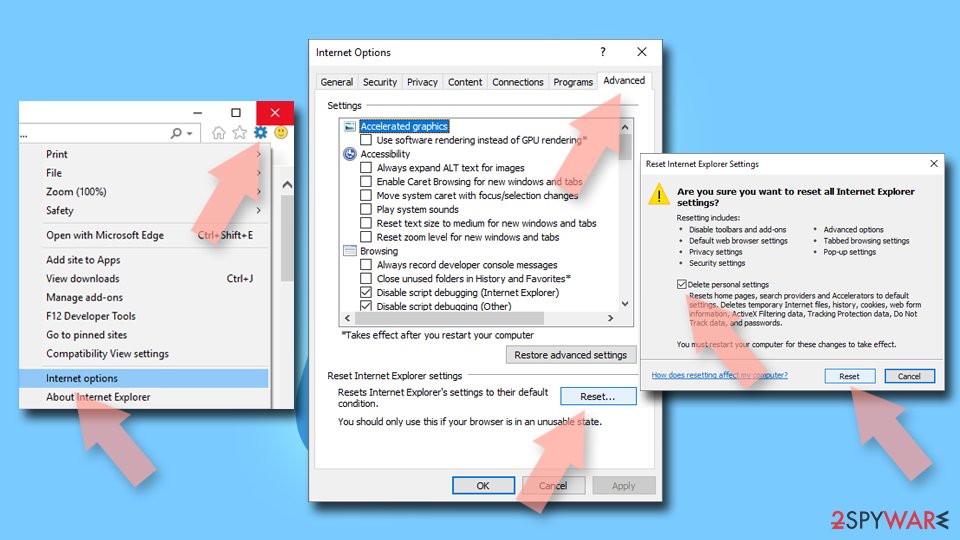
Reset Internet Explorer:
- Click on Gear icon > Internet options and select Advanced tab.
- Select Reset.
- In the new window, check Delete personal settings and select Reset.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
From our report of Jul 2020 · not reviewed since
Instructions for Get-user-id pop-up alert virus elimination
There are two methods that can be applied for Get-user-id virus removal.
However, none of them requires clicking on the Download button. In contrast, seeing an offer to download some kind of ID should be considered as a potential danger prompting you to close the current web browser's window.
The pop-up Get-user-id is triggered by a potentially unwanted program, so it will not stop from being displayed as long as the related malware remains active.
To uninstall it, you can either follow manual removal guide that is provided at the end of this article or run a full system scan with a professional anti-malware tool. Finally, double-check the system with to make sure that the registries, libraries, Temp folder, and other locations are free if intrusive entries.
Questions about Get-user-id ads
msn.com opens when I click links. What causes it?
When every click leads to msn.com first, an extension or a script on the page is rewriting the links. If it happens only on one site, that site uses aggressive ads; close it and use another source. If it happens everywhere, open the browser in a private window, where extensions are normally off, and try again.
No redirect in the private window means one of your extensions is responsible: remove the ones you do not know. A redirect in the private window too means the cause is outside the extensions, such as a notification permission, a changed search setting or a program installed on the PC. The removal steps in this guide cover each of those.
Is it safe that my browser was redirected to msn.com?
Landing on msn.com does not infect the PC by itself. A browser does not run programs from a page without your action. The danger is in the pages that come next:
- some ask you to allow notifications
- some show fake virus warnings
- some offer downloads
- ask for card details
If you only saw those pages and closed them, nothing more is needed than removing whatever caused the redirect. If you allowed notifications, remove that permission.
If you downloaded a file, delete it unopened, or uninstall it if you ran it. If you typed a password or card number on one of the pages, change the password and call your bank.
What is Get-user-id?
Get-user-id is an adware extension, a kind of adware. It earns money by showing redirects through ad pages, and each view, click or redirect pays whoever runs it. It is not something people usually choose; it arrives through a free download, a fake button or a misleading prompt.
Get-user-id does not encrypt files or take control of Windows, but its ads are sold to anyone, including scam operators, so they can lead to fake virus warnings and unwanted downloads. The steps in this guide remove it from Windows and from each browser.
Which browsers does Get-user-id affect?
In the cases we checked, Get-user-id showed up in Chrome, Edge and Firefox. That does not rule out others on your PC, since adware installers often target every browser they find, and permissions and extensions sync across computers signed in to the same browser account.
Open each browser you have, go to its extensions page and its notification settings, and remove anything you do not recognise. Profiles count separately: Chrome and Edge can each hold several, and each one needs checking on its own.
Are the pop-ups I see really from Get-user-id?
Compare them with the details in the table above. Get-user-id produces redirects through ad pages, and the clearest sign of it is redirects to msn.com. Other adware looks similar, so check the name of the sending site at the bottom of a notification, the address in the tab that opened, or the newest entries on the extensions page.
If those match, this guide fits. If you see a different name, the same kind of steps apply, but remove the item you actually find rather than guessing.
Why is my browser so slow since the ads started?
Each page now does extra work. An adware extension reads the page, decides where to put ads, loads them from ad servers and reports your visit, and that happens on every tab. Ad-supported programs add their own background activity.
Removing the extension or program usually makes the browser fast again at once. If it stays slow, open the browser's own task manager with Shift+Esc in Chrome or Edge and look for extensions using a lot of memory or processor time.
My scan found nothing, but the ads continue. Why?
Because the source may not be a file a scanner looks for. Browser notifications are a permission stored in the browser, and many adware extensions are not flagged because they come from an official store.
Some ad-supported programs are only reported if you enable detection of potentially unwanted apps. So a clean scan does not mean the job is done. Check each browser's notification permissions and extension list by hand, and turn on Potentially unwanted app blocking in Windows Security before scanning again.
Can an adware pop-up infect my PC just by appearing?
No. A pop-up, a notification or a new tab is only a web page or a message. It cannot run programs on Windows by itself, provided the browser and Windows are up to date. Infection needs a step from you:
- running a downloaded file
- installing an extension
- giving a stranger remote access
That is why scam pages work so hard to make you click. Close such pages with the tab's X or by closing the browser, not with buttons inside the page, which may start a download.
I let a "support technician" from an ad connect to my PC. What should I do?
Act quickly but calmly. Disconnect the PC from the internet first, so the connection ends. Uninstall the remote access tool they asked you to install and check Installed apps for anything else added during the call.
Run a Microsoft Defender full scan and offline scan. From another device, change your e-mail and banking passwords and sign out of all sessions.
If you paid by card, bank transfer or gift card, contact your bank or the card issuer immediately, and report the scam to the police. Do not answer if they call back.
Will Fortect remove Get-user-id?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Get-user-id, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Microsoft: Detect and block potentially unwanted applications (read October 6, 2026)
- Apple: get user id pop up (read October 6, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)