
Goodluckday.site ads: what it is and how to remove it
Goodluckday site is an adware-related application which produces annoying pop-ups on Mac devices. However, we should warn you that Android users are not protected as well.
Facts checked October 6, 2026. Removal steps checked against Apple's current documentation and the security vendors' reports. We have not run the malware on a Mac. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your Mac is infected.
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds before you decide anything.
A scan of the PC is a quick way to confirm that nothing installed is behind the hearthpwn.com redirects.
Do it yourself · free Remove Goodluckday.site ads yourself 4 steps, about 12 minutes, no software needed.
Start the steps
Goodluckday.site ads: summary
| Distribution | Software bundles, unprotected websites and their hyperlinks |
|---|---|
| Name | Goodluckday.site |
| Type | Adware |
| Sub-type | PUP |
| Main target | iPhones, iPads, other devices based on iOS, MacOS |
| Infected browsers | Google Chrome, Safari, etc. |
| Removal | Scan the Mac with security software to find the malware and anything installed with it. Fortect for Mac scans for malware and unwanted programs. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 10 more facts
| Signs | numerous advertisements during browsing sessions redirects to affiliate or scam pages tracking |
|---|---|
| Detection names | No Microsoft detection name is known |
| Damage | Not recorded in the old report |
| Symptoms | Redirects to an unknown domain |
| Evidence | 5 write-ups by security sites; details still limited |
| Domains | hearthpwn.com |
| Ads shown as | Redirects through ad pages |
| Browsers | Chrome, Edge and Firefox |
| First seen | 7 May 2019 |
| Facts checked | 6 October 2026 |
What the Goodluckday.site ads ads look like
The pop-up says that I'm an Aldi customer and offers a prize winning chance if I 'spin the wheel' - I'm not and I'm not acting on the offer in any way. It then goes on to recognise me as an iPhone/iPad user and offers the chance of winning an Aldi gift card in celebration of 1 Billion hours of YouTube watched every day
Is Goodluckday.site ads dangerous?
From our report of May 2019 · not reviewed since
Goodluckday site - an adware-based virus which redirects to scam pages on MacOS and iOS devices
Goodluckday site is an adware-related application which produces annoying pop-ups on Mac devices.
However, we should warn you that Android users are not protected as well. Numerous users have complained about this suspicious program redirecting them to other third-party websites, scam pages, and similar directories which are clearly unsafe. A big variety of users have also been experiencing pop-up ads from the affiliate website called Hearthpwn.com.
People who are typically willing to block Goodluckday.site are using iPhones and iPads running iOS 12.2 version. One of the victims has reported that he has been redirected by this adware while visiting www.express.co.uk. According to the victim, the suspicious-looking pop-up message looked like that:
Such social engineering is very similar to these scams:
Adware apps such as Goodluckday are capable of performing unwanted and even illegitimate activities that might relate to some unpleasant consequences. For example, ad-supported objects can redirect to potentially dangerous websites. If the user lands on such one, he/she might catch a spyware-related infection which can collect sensitive data.
In some more dangerous cases, Goodluckday.site might take to malware-laden websites where users can be infected with ransomware or a Trojan horse. However, talking about the adware application itself, it might produce these types of activities on the infected computer system:
To block Goodluckday site on iPhone, iPad, or similar device, make sure you carefully run thru your recently-installed apps and uninstall the ones that you can't remember downloading. Most probably, they got on your system via bundling. Additionally, clean web browsers such as Safari and Google Chrome to remove all add-ons and plugins that could be related to this virus.
If you want to proceed with the Goodluckday.site removal in a faster and more efficient way, you should download a reputable anti-virus/Mac optimization program, such as or other legit Mac tool from the Internet. This tool will perform a full system scan and will help you to spot the threat with all its additional components.
- Walmart Gift card virus
- Amazon Gift card scam
- eBay virus
- VISA Gift Card scam
- Advertising via infected browsers;
- Showing suspicious ads;
- Changing the browser's settings, e.g. start page, homepage, etc.;
- Injecting "helper objects", e.g. browser extensions/plug-ins/add-ons to start tracking user's online sessions.
From our report of May 2019 · not reviewed since
Unprotected browsing thru unsafe sites can bring adware and other PUPs to your Mac
If you are a frequent user of third-party applications and do not pay attention to site you are visiting, the risk of getting infected with adware or similar PUPs is not that low as you might think.
Most often, ad-supported programs and their objects sneak into the system via infectious hyperlinks, pop-up ads, pop-unders, banner ads, and other similar content. According to computer experts from NoVirus.uk, adware content has also been spread via software packages that are lurking in secondary download websites or indirect download links.
To prevent suspicious components from slipping into your device or machine, you should choose programs' sources wisely. Stay away from ads offering you to install Flash Player, Adobe Acrobat Reader or similar programs because there is a high chance that these ads are fake. To get these programs, always use official websites.
Staying cautious whenever you browse the Internet sphere will increase your computer's safety. It is very important to keep a distance from third-party websites and adult-related content. Additionally, always choose the Custom/Advanced configuration mode when downloading software to your system and deselect optional downloads.
From our report of May 2019 · not reviewed since
More from our earlier report on Goodluckday.site
- can help you to get rid of all adware-related content
Check your browser and PC
- Address:
hearthpwn.com
How to remove Goodluckday.site ads
How to remove Goodluckday.site from a Mac
Remove the app and what starts it, then check the browsers.
Step 1: Delete apps and downloads you did not intend to install
Open the Applications folder and your Downloads folder. Drag any app you did not install, and any disk image (
.dmg), installer (.pkg) or archive (.zip) that came from Goodluckday.site or a site you do not trust, to the Bin, then empty the Bin.Also check
~/Library/Application Supportfor a folder with the same name as the app you removed.Step 2: Remove unknown login items and background items
Open System Settings > General > Login Items & Extensions. Under Open at Login and Allow in the Background, switch off or remove anything you do not recognize, especially items whose developer is shown as an unknown name or that appeared on the day you ran the command.
Then open Finder, choose Go > Go to Folder and check
~/Library/LaunchAgents,/Library/LaunchAgentsand /Library/LaunchDaemons for property list (.plist) files you did not add. Drag suspicious ones to the Bin, then restart the Mac.Step 3: Check the browsers for extensions and changed settings
In Safari open Settings > Extensions and General (homepage). In Chrome open
chrome://extensions, in Firefoxabout:addons.Remove any extension you did not add, and reset the homepage and search engine if they changed. Browsers hold saved passwords and cookies, which is why the password step comes first.
Step 4: Quit what is running that you do not recognize
Open Activity Monitor (in Applications > Utilities, or search for it with Command + Space).
In the CPU or Network tab, look for a process you did not install or whose name is random, select it, click the stop button (the octagon with an X) and choose Quit or Force Quit.
Note the name first: you will look for the same name in the next steps. Malware that comes back after a restart is handled in the next two steps.
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Remove from Google Chrome
To get rid of the adware, reset Chrome by following these steps:
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.

Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.

Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.

Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.

Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.

Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.

Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.

Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.

Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.

Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.

Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.

Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.

- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.

Delete from Safari
To block goodluckday site virus completely, remove Safari data with the help of this guide:
Remove dangerous extensions:
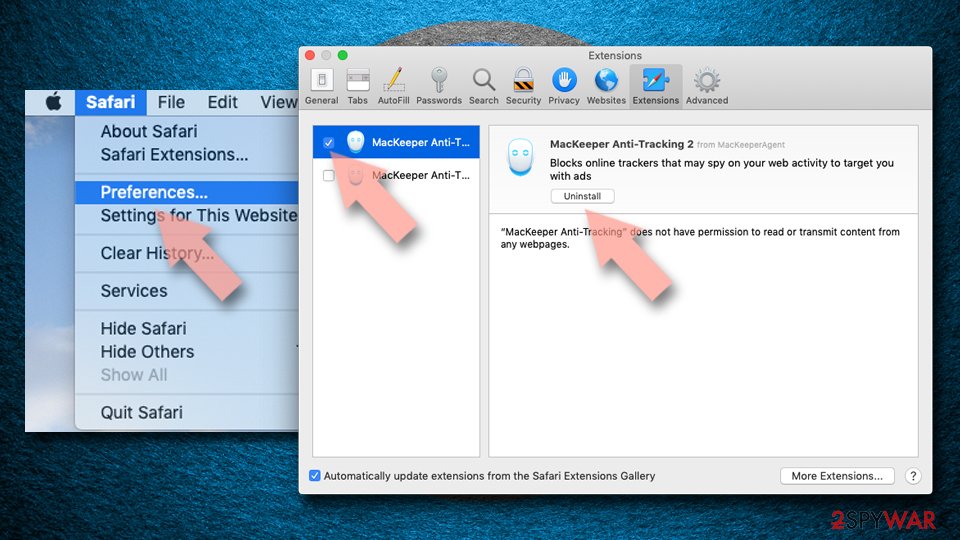
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
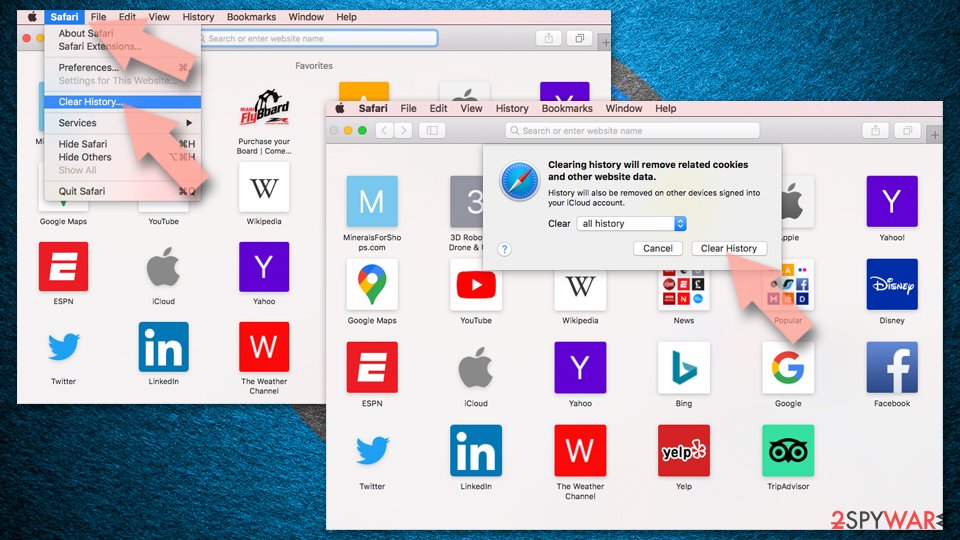
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
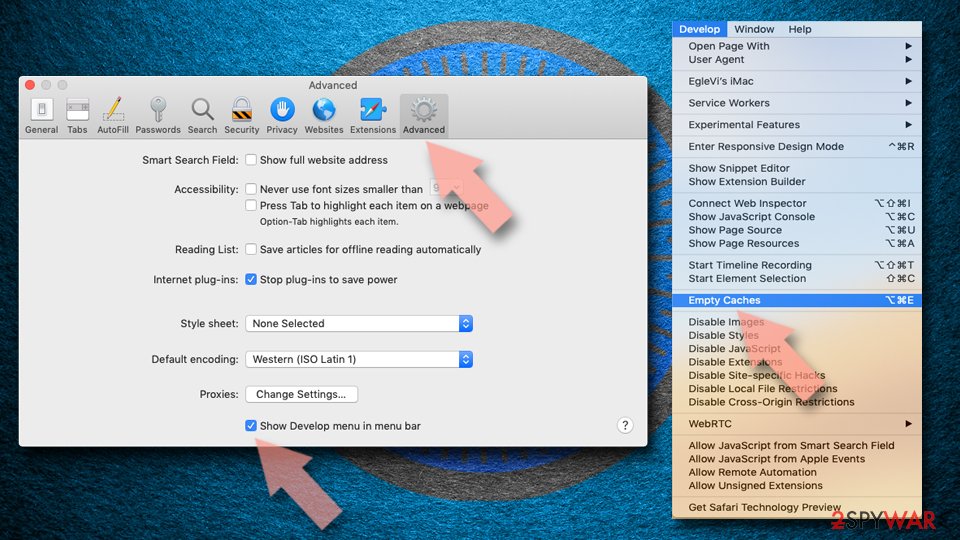
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
To remove Goodluckday.site from your Mac/Apple device, uninstall every suspicious app from the system. Get rid of all optimization tools, PDF creators and similar PUPs. To perform this process, follow the below-given guidelines:
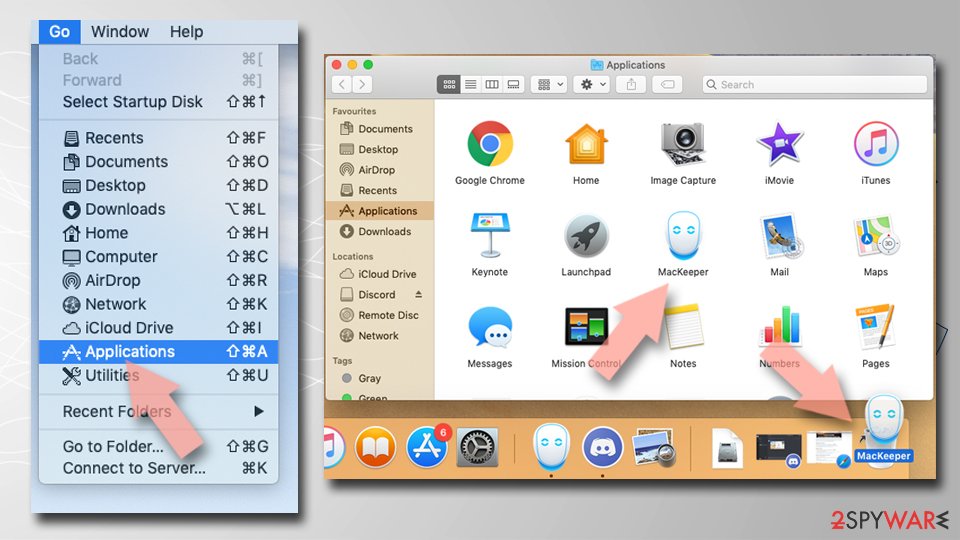
Remove the unwanted application:
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
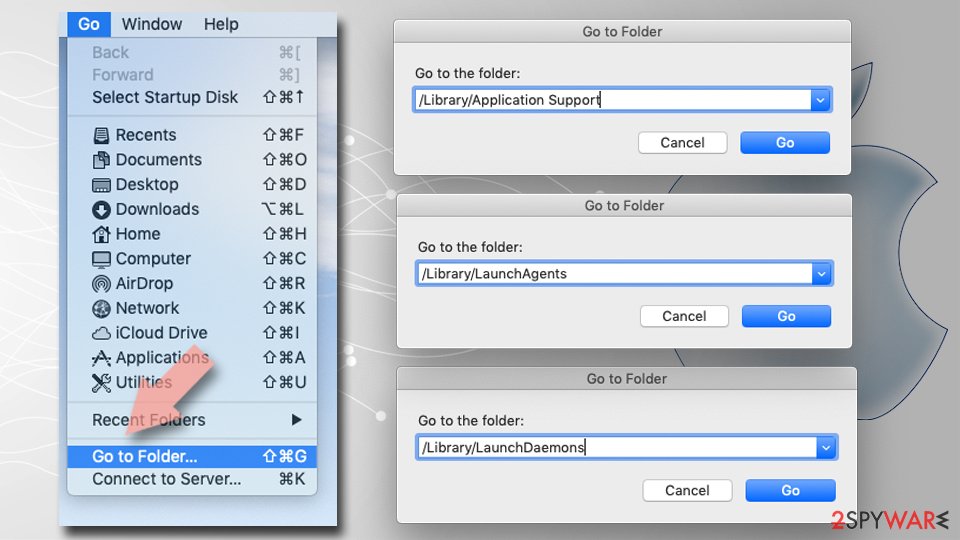
Delete leftover files and folders:
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Reset Internet Explorer
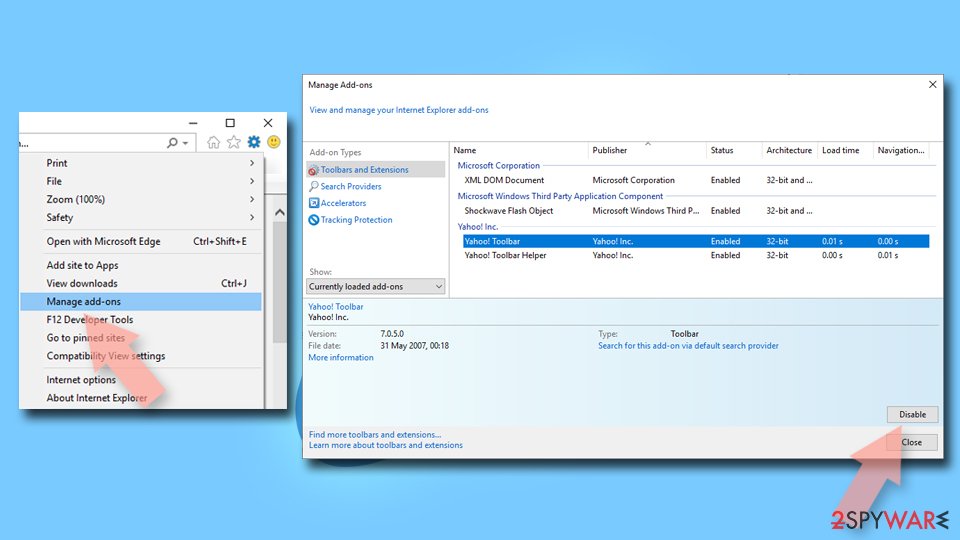
Remove dangerous add-ons:
- Open Internet Explorer, click on the Gear icon (IE menu) on the top-right corner of the browser
- Pick Manage Add-ons.
- You will see a Manage Add-ons window. Here, look for suspicious plugins. Click on these entries and select Disable.
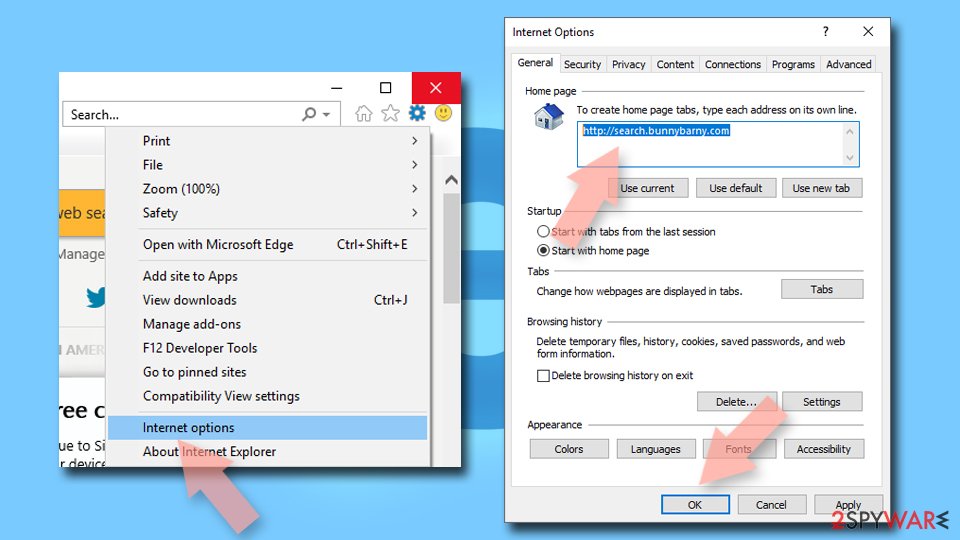
Change your homepage if it was altered:
- Open IE and click on the Gear icon.
- Select Internet Options.
- In the General tab, delete the Home page address and replace it by your preferred one (for example, Google.com).
- Click Apply and then select OK.
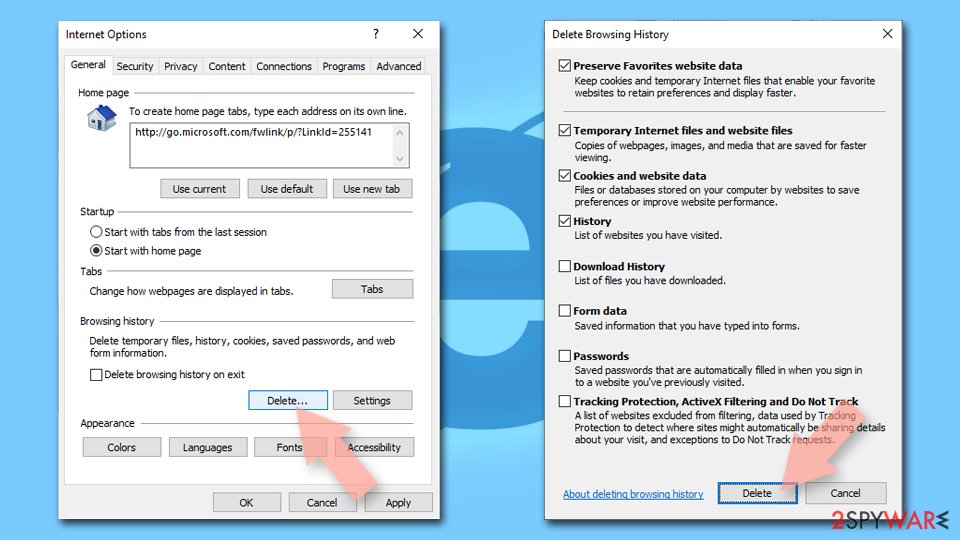
Delete temporary files:
- Press on the Gear icon and select Internet Options.
- Under Browsing history, click Delete...
- Select relevant fields and press Delete.
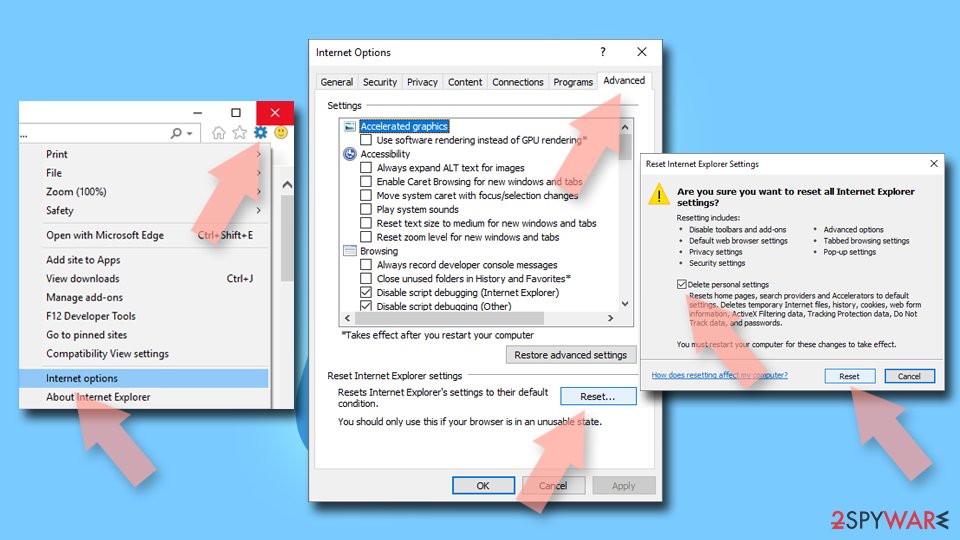
Reset Internet Explorer:
- Click on Gear icon > Internet options and select Advanced tab.
- Select Reset.
- In the new window, check Delete personal settings and select Reset.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
From our report of May 2019 · not reviewed since
How to block Goodluckday site virus. Detailed steps
To perform Goodluckday site removal, you need to find the third-party adware virus which is triggering unwanted ads on your system.
It might be hard to complete if you are a less-experienced user, so, in this case, you should continue with downloading and installing reputable security software and erasing all suspicious content from your Mac automatically.
Alternatively, block Goodluckday.site virus by cleaning all locations (your Applications, Safari, Chrome or other preferred web browsers). If you do not eliminate all virus-related components permanently, pop-ups ads from this third-party website might continue appearing. Once the deletion is completed, make sure that you take care of your device's or machine's safety in the upcoming future.
Questions about Goodluckday.site ads
Why does my browser keep going to hearthpwn.com?
Something is sending it there. On one site only, that site's ads are the cause and leaving the site ends it.
On many different sites, the usual causes are an extension you installed with something else, a site you once allowed to send notifications, or an ad-supported program in Windows that changes how the browser behaves. hearthpwn.com itself is only a stop on the way: it records the visit and forwards you to whatever advertiser pays most.
Check the extensions page, then the list of sites allowed to send notifications, then Installed apps sorted by date. Removing the cause stops the redirects; blocking the domain alone usually does not, because the network moves to a new one.
Is it safe that my browser was redirected to hearthpwn.com?
Landing on hearthpwn.com does not infect the PC by itself. A browser does not run programs from a page without your action. The danger is in the pages that come next:
- some ask you to allow notifications
- some show fake virus warnings
- some offer downloads
- ask for card details
If you only saw those pages and closed them, nothing more is needed than removing whatever caused the redirect. If you allowed notifications, remove that permission.
If you downloaded a file, delete it unopened, or uninstall it if you ran it. If you typed a password or card number on one of the pages, change the password and call your bank.
What is Goodluckday.site?
Goodluckday.site is an adware extension, a kind of adware. It earns money by showing redirects through ad pages, and each view, click or redirect pays whoever runs it. It is not something people usually choose; it arrives through a free download, a fake button or a misleading prompt.
Goodluckday.site does not encrypt files or take control of Windows, but its ads are sold to anyone, including scam operators, so they can lead to fake virus warnings and unwanted downloads. The steps in this guide remove it from Windows and from each browser.
Which browsers does Goodluckday.site affect?
In the cases we checked, Goodluckday.site showed up in Chrome, Edge and Firefox. That does not rule out others on your PC, since adware installers often target every browser they find, and permissions and extensions sync across computers signed in to the same browser account.
Open each browser you have, go to its extensions page and its notification settings, and remove anything you do not recognise. Profiles count separately: Chrome and Edge can each hold several, and each one needs checking on its own.
Are the pop-ups I see really from Goodluckday.site?
Compare them with the details in the table above. Goodluckday.site produces redirects through ad pages, and the clearest sign of it is redirects to hearthpwn.com. Other adware looks similar, so check the name of the sending site at the bottom of a notification, the address in the tab that opened, or the newest entries on the extensions page.
If those match, this guide fits. If you see a different name, the same kind of steps apply, but remove the item you actually find rather than guessing.
Can an adware pop-up infect my PC just by appearing?
No. A pop-up, a notification or a new tab is only a web page or a message. It cannot run programs on Windows by itself, provided the browser and Windows are up to date. Infection needs a step from you:
- running a downloaded file
- installing an extension
- giving a stranger remote access
That is why scam pages work so hard to make you click. Close such pages with the tab's X or by closing the browser, not with buttons inside the page, which may start a download.
My scan found nothing, but the ads continue. Why?
Because the source may not be a file a scanner looks for. Browser notifications are a permission stored in the browser, and many adware extensions are not flagged because they come from an official store.
Some ad-supported programs are only reported if you enable detection of potentially unwanted apps. So a clean scan does not mean the job is done. Check each browser's notification permissions and extension list by hand, and turn on Potentially unwanted app blocking in Windows Security before scanning again.
Why is my browser so slow since the ads started?
Each page now does extra work. An adware extension reads the page, decides where to put ads, loads them from ad servers and reports your visit, and that happens on every tab. Ad-supported programs add their own background activity.
Removing the extension or program usually makes the browser fast again at once. If it stays slow, open the browser's own task manager with Shift+Esc in Chrome or Edge and look for extensions using a lot of memory or processor time.
I let a "support technician" from an ad connect to my PC. What should I do?
Act quickly but calmly. Disconnect the PC from the internet first, so the connection ends. Uninstall the remote access tool they asked you to install and check Installed apps for anything else added during the call.
Run a Microsoft Defender full scan and offline scan. From another device, change your e-mail and banking passwords and sign out of all sessions.
If you paid by card, bank transfer or gift card, contact your bank or the card issuer immediately, and report the scam to the police. Do not answer if they call back.
Will Fortect remove Goodluckday.site?
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds on your Mac before you decide anything.
For Goodluckday.site, follow the plan on this page as well: removing a launch item or an app is done in macOS itself, and a scanner cannot undo what was typed or entered on the infected Mac, such as saved passwords that were copied.
Change your passwords from another device first, and if the page tells you to erase the Mac, a scan is not a substitute. The free scan costs nothing and the full-featured product needs a license.
Sources
- Discussions: goodluckyday.site (read October 6, 2026)
- Wikipedia: Third-party source (read October 6, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)