
HTML:RedirME-inf: what it is and how to remove it
HTML:RedirME-inf is a detection name for a potentially malicious threat when users visit particular websites, although they are not necessarily dangerous. It is likely that the detection of HTML:RedirME-inf is a false positive due to specific bugs within software updates for the engine.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
An automatic scan checks installed programs, startup items and browser extensions for anything that came with HTML:RedirME-inf.
Do it yourself · free Remove HTML:RedirME-inf yourself 5 steps, about 15 minutes, no software needed.
Start the steps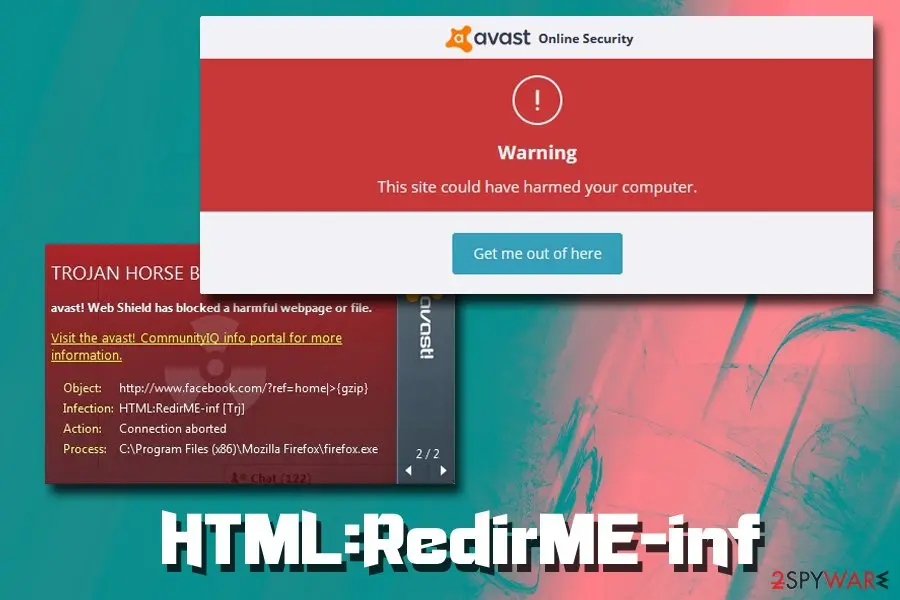
HTML:RedirME-inf: summary
| Name | HTML:RedirME-inf |
|---|---|
| Type | Trojan horse or a false positive |
| Risk factors | Sensitive data disclose to hackers, money loss, further malware infection, etc. |
| Symptoms | Rarely any symptoms are displayed apart from the AV detection |
| Infiltration | Software bundles, third-party sites, spam emails, web injects, exploits, etc. |
| Other resolutions | If it is a false positive, you should update security software database or add an exclusion |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Evidence | 4 write-ups by security sites; details still limited |
| First seen | 9 July 2019 |
| Facts checked | 6 October 2026 |
What HTML:RedirME-inf does on an infected PC
From our report of Jul 2019 · not reviewed since
HTML:RedirME-inf is a false positive by Avast or AVG anti-virus, although it might indicate malware
HTML:RedirME-inf is a detection name for a potentially malicious threat when users visit particular websites, although they are not necessarily dangerous.
It is likely that the detection of HTML:RedirME-inf is a false positive due to specific bugs within software updates for the engine.
All in all, if the detection is not a false positive, HTML:RedirME-inf removal should be performed immediately, as trojans are highly dangerous cyber infections.
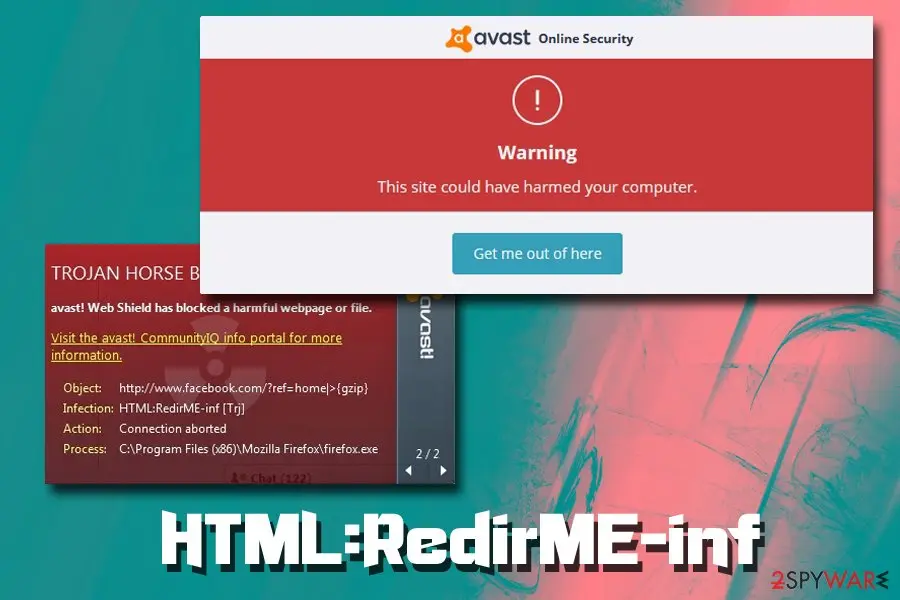
Users are confronted with the following message:
While it is possible that the detection is a false positive, you should not simply ignore it. The definition was put up for a reason, and that it does not mean that the real HTML:RedirME-inf trojan infection is not possible.
If that is the case, HTML:RedirME-inf virus can perform a variety of functions on the host machine:
Without a doubt, excessive spying might not only result in unexpected money loss, login credential disclosure, compromised credit history, but also identity fraud or theft. Therefore, it is vital to remove HTML:RedirME-inf before it can cause any of the mentioned damages.
To do that, users should scan their devices with an anti-malware program, and it would be best to do that while in Safe Mode. After that, it is strongly recommended to use for a swift recovery.
However, make sure you first make sure that HTML:RedirME-inf is not a false positive. To do that, scan that detected file with tools like Virus Total, or use an alternative security application, such as .
- Modify Windows registry;
- Schedule and run new tasks;
- Insert new processes and files;
- Record keyboard inputs;
- Take screenshots;
- Give the attacker remote access;
- Upload additional malware payloads, such as ransomware.
From our report of Jul 2019 · not reviewed since
Avoid trojan infections with the help of industry experts advise
Trojans are intrusive in nature, so they can perform a variety of system modifications, all while harvesting the most sensitive user information and not showing any signs of the activity whatsoever. For that reason, malware can lurk inside the machine for months before it is detected - if no adequate security measures are practiced, that is.
Users should be aware that negligence when it comes to online safety can result in drastic consequences, such as money loss, data loss, and other sensitive details expose to malicious actors. Thus, to avoid such consequences, you should take the advice from German security experts:
- When checking your email, never open attachments or click on links if it comes from an unknown sender;
- Email spoofing can make a fraudulent email look like it's coming from a legitimate source - keep that in mind and apply the previous rule;
- Use strong passwords for all your accounts and never reuse them;
- Enable two-factor authentication where possible;
- Update your operating system as soon as security patches are released;
- Install anti-malware software with a built-in real-time protection feature;
- Do not download pirated software, cracks, and keygens;
- Enable ad-block but do not forget to add exceptions for sites you want to support.
From our report of Jul 2019 · not reviewed since
More from our earlier report on HTML:RedirME-inf
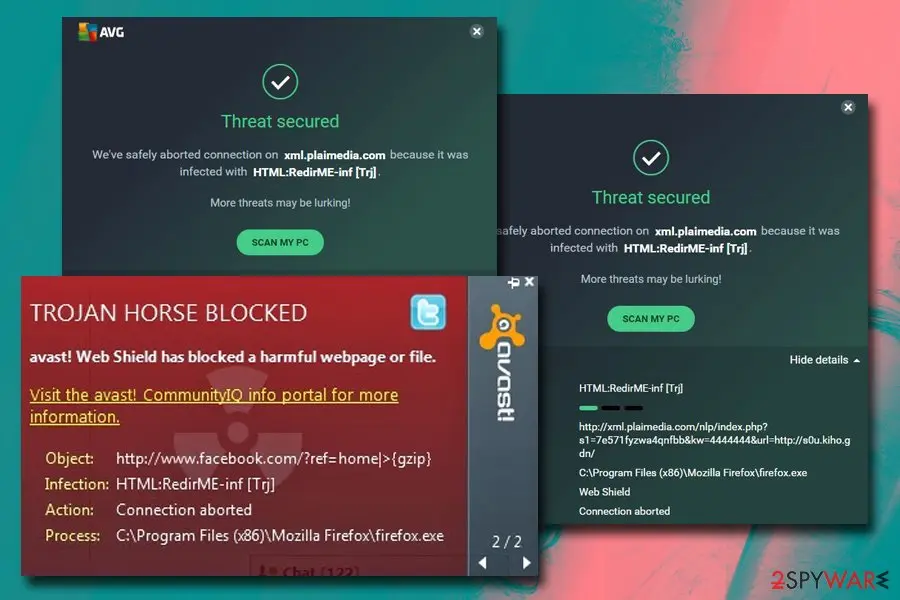
- In most of the cases, users complained that their AVG or Avast anti-malware software start spamming Google Chrome, Mozilla Firefox, Internet Explorer, or another browser with HTML:RedirME-inf Trj warnings.
- Back in 2011, Avast users were greatly affected by this issue, although the security firm quickly released a patch which stops the inadequate spam of detection which occurred on almost all legitimate websites.
- Nevertheless, users started complaining again seven years later, as AVG was marking xml.plaimedia.com site as malicious, even though users never visited it, and prompts came when they were using sites like google.ca.
- Use reputable anti-malware software to terminate the trojan
- We've safely aborted connection to xml.plaimedia.com because it was infected with HTML:RedirME-inf
How to remove HTML:RedirME-inf
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Programs like HTML:RedirME-inf add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 2: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after HTML:RedirME-inf, its publisher or created on the day the problem started. Delete those folders, and check C:\Program Files and C:\Program Files (x86) too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
A scan finds the parts of HTML:RedirME-inf that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
HTML:RedirME-inf can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Jul 2019 · not reviewed since
Remove HTML:RedirME-inf malware from your computer
Many reports has suggested that HTML:RedirME-inf is, in fact, a false positive.
These inconsistancies can happen from time to time, because certain files or installed programs might display a behavior that looks similar to malware. In such a case, anti-virus engine detects it as malicious and flags it. To make sure it is not a false detection, use another malware scanner.
If you are sure that the detection is not a false positive, you should not delay HTML:RedirME-inf removal. Because the infection is a trojan, it is not recommended trying to terminate it manually, as it performs deep modifications within the system, and only IT expert would be able to do such a tanks.
Thus, use anti-malware software to remove HTML:RedirME-inf virus. Before you perform a scan, enter Safe Mode with Networking as explained below.
[GI=method-1]To remove HTML:RedirME-inf virus, you should enter Safe Mode with Networking and perform a full system scan:
[GI=method-2]You can also use System Restore to terminate the infection:
After removal: passwords, accounts and prevention
Your passwords after HTML:RedirME-inf
Removing HTML:RedirME-inf does not undo what it may already have sent out while the PC showed HTML:RedirME-inf in the list of installed apps.
Treat saved browser passwords and logged-in sessions on this PC as known to the attacker.
From another device, change the e-mail password first and end all its sessions. Then do the same for the bank, PayPal, Microsoft, Google and Apple accounts. Stolen session cookies keep working after a password change until you sign out everywhere.
Move crypto to a new wallet created on a clean device. A step-by-step order for every kind of account is in our guide to account security after an infection.
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
Questions about HTML:RedirME-inf
Can I safely uninstall HTML:RedirME-inf?
If you did not install HTML:RedirME-inf yourself and it is not part of your hardware or a program you rely on, yes. Uninstalling an unwanted program does not harm Windows. Before you do, search the exact name and publisher to be sure it is not a driver tool, a printer utility or a game launcher with an odd name.
Then remove it from Settings, Apps, Installed apps. Ignore any offers or warnings in its uninstaller about losing protection or performance. Afterwards check Startup apps and your browsers for leftovers, and restart once to confirm that it does not reinstall itself.
HTML:RedirME-inf came back after I uninstalled it. Why?
Something else is reinstalling it. Common causes are a second program from the same publisher, a scheduled task that downloads it again, or a browser extension that keeps prompting for it. Sort Installed apps by install date and uninstall each entry from the same day that you did not choose.
Then open Task Scheduler and look in the Task Scheduler Library for tasks with updater-style names that you do not recognise. Check Startup apps in Task Manager too. If HTML:RedirME-inf still returns, start Windows in Safe Mode, uninstall it there and run a Microsoft Defender offline scan, which looks for loaders that ordinary scans can miss.
How do I know if my PC has HTML:RedirME-inf?
Often you do not, which is the point of a trojan. Possible signs are an antivirus alert naming HTML:RedirME-inf or a generic trojan detection, unknown programs or scheduled tasks, processes with random names in Task Manager, browser extensions you did not add, security settings turned off, slower performance, or account alerts about logins from unknown places.
The reliable check is a full scan followed by Microsoft Defender's offline scan. If you recently ran a crack, a fake installer or a command a website told you to paste, scan even without symptoms.
My antivirus was on. How did a trojan get past it?
Antivirus programs see a file only when it is written or run, and criminals test each new build against popular scanners before release. Detection catches up within hours or days, which is often after the first victims ran it.
Archives with passwords, installers that fetch the malware later, and scripts run through PowerShell make the job harder. That is why behaviour such as downloading cracks or pasting commands matters more than any setting. Keep Windows and Defender updated, and turn on Reputation-based protection in App & browser control.
I found AnyDesk or ScreenConnect that I did not install. Is that HTML:RedirME-inf?
Not necessarily HTML:RedirME-inf, but it is a warning sign. These are legitimate remote support tools, and criminals use them as ready-made backdoors, especially after tech support scams or fake invoice calls.
If you did not install it and no one you trust set it up, uninstall it, change passwords from a clean device and check your bank account. If someone connected to your PC through it, follow the steps for remote access trojans and consider a Windows reset. Installed apps sorted by date shows when it appeared.
Do I need to reinstall Windows to get rid of HTML:RedirME-inf?
Usually not. A thorough clean-up is enough when the offline scan finds nothing afterwards and you do not see HTML:RedirME-inf in the list of installed apps again. A reset is the safer choice if an attacker had remote control, if security tools were switched off, or if detections come back after every clean-up.
Windows 11 can reset itself without a USB stick under Settings > System > Recovery > Reset this PC. Copy documents and photos out first and scan the copies. A reset does not change passwords or undo stolen data, so the account steps still apply.
Which malware family is HTML:RedirME-inf?
That is not known yet. HTML:RedirME-inf has been reported by people who saw HTML:RedirME-inf in the list of installed apps, but no sample has been analysed publicly, so security companies have not assigned it to a family. The name you see may be a file or program name chosen by the authors, not a family name.
This does not stop you from removing it: the startup points, the offline scan and the account steps are the same for most families of this type. If Microsoft Defender or another scanner gives the file a detection name, write it down; that name is the best clue to the family and is useful when you report the incident.
Should I check my other computers too?
Yes, it takes little time and removes doubt. HTML:RedirME-inf itself usually stays on one PC, but the download that carried it may have been copied to other computers, shared drives may hold the same installer, and an attacker who had access could have tried saved passwords on other devices.
Run a full scan on every Windows PC in the home or office, check shared folders for the original download, and change Wi-Fi and router passwords if they were stored on the infected machine.
Is it safe to do online banking after seeing HTML:RedirME-inf in the list of installed apps?
Not on that PC until it is clean. A program that produces HTML:RedirME-inf in the list of installed apps runs with your rights and could read what you type or what the browser shows. Use a phone or another computer for banking and for changing passwords.
When the offline scan of the affected PC is clean and nothing suspicious starts with Windows any more, you can go back to using it. Check your bank statements for the past weeks either way, and call the bank if anything looks unfamiliar; banks can block cards and reset access quickly.
Will Fortect remove HTML:RedirME-inf?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For HTML:RedirME-inf, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- How-To Geek: How To Tell If a Virus Is Actually a False Positive (read October 6, 2026)
- Dieviren: Dieviren (read October 6, 2026)
- Wikipedia: Email spoofing (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)