
Iplogger.org: is it a virus? What it logs and how to stop redirects
Iplogger.org is a website that makes tracking links and records the IP address and device details of everyone who opens them; it is a legitimate service, not a virus, and visiting it installs nothing. Redirects to it that you did not ask for are worth checking, because attackers have used its links, and the fix is to scan the PC and clean the browser, not to remove the site.
Facts checked October 11, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If redirects to iplogger.org keep coming back, a free scan can check extensions, programs and browser settings in one pass.
Do it yourself · free Remove Iplogger.org yourself 1 step, about 5 minutes, no software needed.
Iplogger.org: summary
| Type | Link-shortening and IP-tracking website; not malware, but a tool that attackers also use |
|---|---|
| Risk | Medium: opening one of its links gives the link's owner your IP address and device details; the attached file or page is the bigger danger |
| Symptoms | A redirect to iplogger.org or iplogger.com, sometimes with slow browsing and ads on sites that had none |
| How to get rid of it | Nothing to uninstall for the website; scan, remove unknown programs and extensions, and reset the browser if redirects continue |
| Our check (6 October 2026) | Stopped by Cloudflare's bot check; no notification request, pop-up or redirect on that one visit, and the real page was not seen |
| Running since | 3 April 2011, the date in the public domain record |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 14 more facts
| Installed on the PC | Nothing: visiting the site installs no program |
|---|---|
| Used by criminals | Documented twice in 2020: a Paradise ransomware check-in address (Trend Micro) and a hidden iframe on a coronavirus site (Unit 42) |
| Microsoft detection | None: Microsoft Defender has no detection name for the website, because nothing is installed by visiting it. Trojan:Script/Wacatac, a broad Microsoft label, is not tied to it |
| First reported by us | 9 July 2020 |
| Evidence | The site's home page, Trend Micro (18 March 2020), Unit 42 (22 April 2020), our test |
| Name | Iplogger.org |
| Domains | iplogger.org |
| Domain registered | 3 April 2011 |
| Ads shown as | Redirects through ad pages |
| Browsers | Chrome, Edge and Firefox |
| First seen | 9 July 2020 |
| Distribution | Typically ad scripts on free streaming, file-hosting and adult sites, typo domains and hacked websites |
| Damage | Redirects to scam pages, fake updates and tech support scams |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026. Our own browser test was stopped by Cloudflare's bot check, so the description of the service comes from the site's home page read by an automated fetch, and the attack cases come from Trend Micro and Unit 42. We did not create or open a tracking link and we did not test the app.
What IPLogger is and how it logs a visit
Iplogger.org is a website that makes tracking links, not a virus: you do not install it, and opening its home page installs nothing. The link is the tool. Whoever creates it sees who opened it.
- 1
Someone creates a tracking link
On iplogger.org a person pastes any web address or picture and gets back a short link. The site also hands out an "invisible image" (a tracking pixel), which can sit on a web page or in a message without being seen.
- 2
You open the link or load the page
Your browser asks the IPLogger server for the link or the pixel. That request is all it takes: you do not have to click anything on the page that appears, and you may be sent on to the real destination within a moment.
- 3
The owner reads the log
The person who made the link opens a list of every visit. The site says each entry can hold the IP address, the city and country, hardware details such as screen resolution, the browser and its version, the referrer page and, where the visitor agrees, GPS coordinates.
- What it is
- A link shortener and IP tracker run as a website, with an Android app and a Telegram bot; not a program on your PC
- Who runs it
- The home page names Wowlink Pte. Ltd. (Singapore) as the owner of its consent-collection technology; it does not say who operates the site
- Addresses
iplogger.org; our 2020 capture also showsiplogger.com, which we did not test in 2026- Home page claim
- "Log and Track IP addresses" and "check URL for hidden redirects for safety reasons"
- Its own abuse rule
- The site says it may block links and accounts used for spam, malware or fraudulent sites, and that abusers may face legal consequences
- Registered
- 3 April 2011 (public registry record), so it is not a new throwaway domain
That is why "iplogger.org virus" has two honest answers. The service is legitimate and has real uses for site owners who want visitor statistics. The same tool is just as useful to someone who wants your address without asking, which is why criminals reach for it too, and why a redirect to it that you did not expect deserves a look.
IP logger detected warnings and our review of iplogger.org
An "IP logger detected" warning means a security program or a chat app recognised a link that leads to an IP tracking service such as iplogger.org.
In our reading, it is a warning about the link, not about a virus on your PC. Opening that link would give its owner your IP address and device details, so do not open it. We found no single official source that names every tool that shows this exact message.
If you see the warning, note where the link came from, for example a message in a game chat or a page that redirected you. Delete the message or close the page. If the warning keeps coming without you clicking anything, a program or extension may be calling the address, so run a scan in Windows Security and check your extensions as the steps above show.
Our review of iplogger.org: it is a legitimate link and IP tracking service, registered on 3 April 2011, and opening its site installs nothing. The weak point is how others use it. Anyone can make a link that records who opens it, and in 2020 Trend Micro and Unit 42 documented criminals using its addresses. Treat an unknown IPLogger link like any unknown link from a stranger.
Is Iplogger.org dangerous?
Our test on 6 October 2026
We loaded https://iplogger.org/ in a clean desktop Chromium browser from Lithuania, with no extension and no account, and did not click anything. We never got past the site's bot check, so this test says almost nothing about the site itself.
iplogger.org home page · desktop Chromium · Lithuania (EU) · 6 October 2026
- Page answeredStatus 403 with the title "Just a moment...": a Cloudflare page headed "Performing security verification", which checks whether a visitor is a bot.
- The real pageNot seen. Our automated browser did not pass the check, so we saw none of the site's own content, scripts or ads.
- Notification requestNone on this one visit, but the page that loaded was only the check page.
- Pop-ups and redirectsNone on this one visit; the address stayed
https://iplogger.org/. - Ad networks and service workerNone identified. Only Cloudflare's own challenge addresses were contacted, so this says nothing about what the real page loads.
- Tracking linksNot tested. We did not create or open an IPLogger link, so we did not see what one does to a visitor beyond what the site itself describes.
Not tested Nothing on this one visit is not the same as nothing there. We saw only a bot check. What the service does is not in doubt, because the site says it logs every visit; whether a particular link sends you to something harmful depends on who made it.
What has changed since our 2020 report
April 2011
The domain is registered
The public registry record shows iplogger.org registered on 3 April 2011 and paid up to April 2027. A site that old is an established service, not a throwaway address, and that is also why its name turns up in so many reports.
March 2020
Paradise ransomware uses an IPLogger link
On 18 March 2020 Trend Micro described a new Paradise ransomware variant that spread through Internet Query (IQY) files in spam. The IQY file contacts the attackers' server to fetch an Excel formula, which runs a PowerShell command that downloads the program. Trend Micro lists an
iplogger.orgshort link,hxxps://iplogger[.]org/1AsWy7, as a "check in" address and calls it a "malware accomplice". The attack uses no Excel vulnerability, so even fully patched systems were exposed.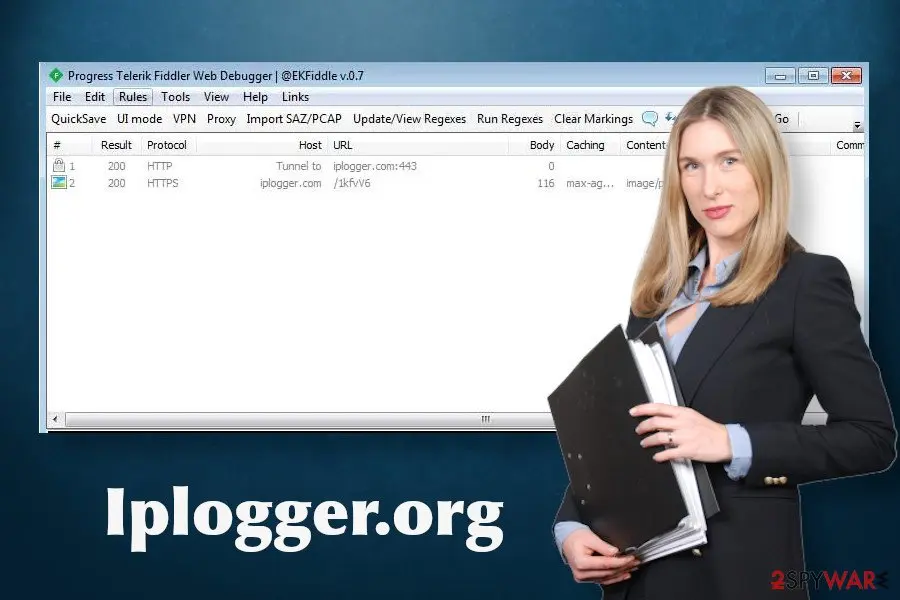
A capture from our 2020 report: Fiddler shows an HTTPS connection to iplogger.com and one request for a short path that returned a 116-byte image. It shows what an IPLogger request looks like in a traffic log; it does not say which program made it. April 2020
Coronavirus websites send visitors' addresses to it
Palo Alto Networks' Unit 42 wrote on 22 April 2020 that some coronavirus-related websites carried suspicious scripts. On
coronavirus-game.ruan obfuscated script dropped an invisible iframe that sent each visitor's IP address to iplogger.org, which Unit 42 called a legitimate IP logging service. It is the same kind of invisible image the site sells to its own customers.9 July 2020
Our first report: a misleading URL and a trojan
We described iplogger.org as a legitimate service whose domain trojans can open, and we wrote about the Paradise case. That is still accurate for the two cases above. What we could not confirm now are the trojan names we listed: see the section on redirects.
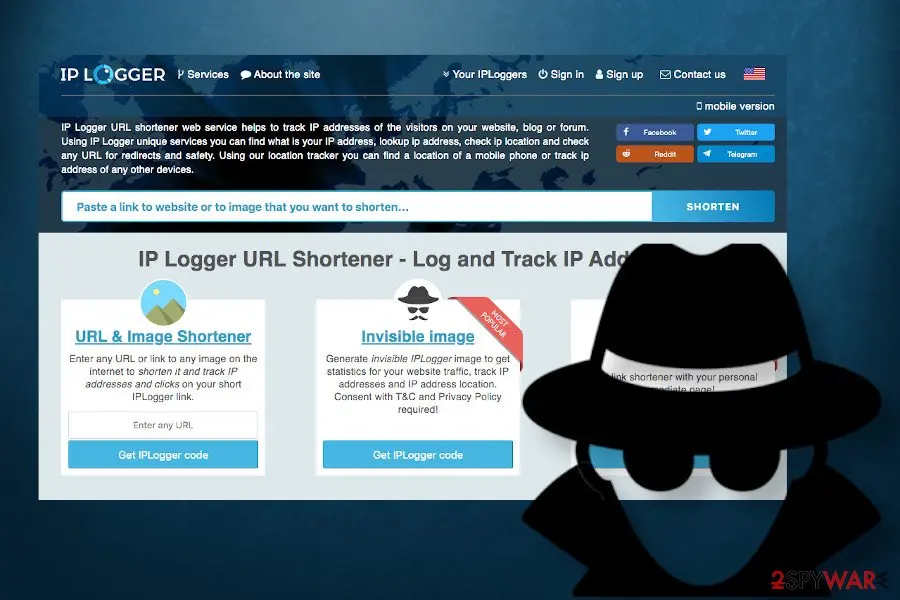
The IP Logger home page as shown in our July 2020 report, with the URL and image shortener and the "invisible image" tool. 2020
Traffic came from the US, India, Brazil, Germany and Russia
Our 2020 report showed a traffic-by-country chart for the site: United States 10.99%, India 9.84%, Brazil 9.04%, Germany 3.52% and Russia 2.92% of desktop visits. The picture does not name the tool or the month, and we could not check the figures in 2026. They describe the website's visitors, not users of the app.
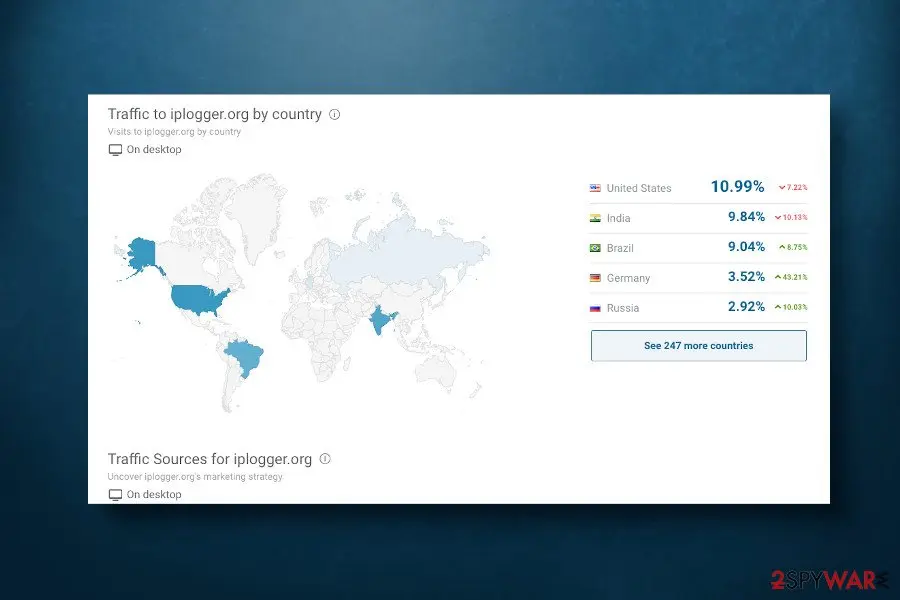
Traffic to iplogger.org by country, as it appeared in our 2020 report. Source tool and date are not shown in the picture. 6 October 2026
Our new check: stopped at Cloudflare's bot check
Our test browser was held at Cloudflare's "Performing security verification" page. A separate automated fetch of the home page returned the normal page, which still sells short links, an invisible image, a URL checker and a Telegram bot, and offers "consent collection" for links. The business has not changed since 2020.
Why your browser opens iplogger.org
A redirect to iplogger.org does not prove an infection. Work out which of these four cases fits before you remove anything.
| What you saw | What it usually means | What to do |
|---|---|---|
| You clicked a link someone sent you and iplogger.org or another short address flashed past | The sender made a tracking link. Your IP address and browser details were logged. Nothing was installed. | Nothing to remove. See "What the owner of an IPLogger link learns" below. |
| A page you opened loaded it in the background, with nothing visible | A script or a one-pixel image on that page, the pattern Unit 42 found on coronavirus-game.ru. The page sent your address to its owner. | Close the page. Check the extensions and notification permissions in your browser if it keeps happening on many sites. |
| Redirects to iplogger.org keep coming on many sites, with slow browsing or ads where there were none before | Something on the PC or in the browser is opening it: an extension, an allowed notification site or a program you ran. | Follow "If redirects continue or you ran a file" below. |
| You installed the IP LOGGER app and see its address in your traffic | The app talks to its own service. This is expected and not a sign of malware. | Remove the app if you do not use it. We did not test the app. |
Our July 2020 report listed three detection names that supposedly launch the site: Trojan:Win32/Hynamer.C!ml, Trojan.Agent.Wacatac and Logger.exe. We could not confirm any of them in 2026: Microsoft's threat search had no entry for Hynamer.C!ml, and no source we found ties Logger.exe to the site. Microsoft does describe Trojan:Script/Wacatac as a broad heuristic label, not one virus, triggered by things such as unauthorised registry changes and in-memory code execution, which also fires on harmless files. A detection with a Wacatac name is a reason to scan, not proof that iplogger.org is involved.
What the owner of an IPLogger link learns, and the real risks
Opening a tracking link is not harmless: it hands over your address and device details to a stranger. It is rarely dangerous on its own, and the dangerous cases are what comes with the link.
- High
A link that is only the first step
In the Paradise case the IPLogger link was one stop on the way to a PowerShell download. A short link hides its target, and opening an attachment is what starts the damage, not the logging.
- Medium
Your IP address and rough location
The owner sees the IP address your provider gave you and the city and country it points to. It is not your name or street address, but it ties your visit to your connection, and a stalker or harasser can combine it with what they already know.
- Medium
Device and browser fingerprints
The site lists screen resolution, battery status, audio capabilities, the browser and its version and the referrer page, which together can tell your device from others.
- Medium
Exact location, if you agree
The site's geo-logger can collect GPS coordinates, but only if your phone or browser asks and you say yes. Declining the location prompt is enough to stop it.
- Low
Just opening the home page
Our July 2020 report said that direct access to the address does not expose personal data. That is too broad: any site you visit sees your IP address. The home page itself is not a way to infect a PC.
What a tracking link can record about a visit
- IP address
- City and country
- Browser and version
- Operating system
- Device type
- Screen resolution
- Referrer page
- Time of visit
- GPS location (only if you allow it)
The list is the site's own description of its logs. Whether a given link collects more than the basics depends on how its owner set it up; we did not create or open one.
How to remove Iplogger.org
How to stop the Iplogger.org redirects
Work in this order and test a few links after each step, so you know which one was the cause.
Which browser shows the ads?
Remove extensions you do not recognise
Paste
chrome://extensionsinto the address bar and click Remove on anything you did not install yourself, especially video downloaders, "search" or PDF helpers added recently.Full procedure with screenshots: Remove a browser extension
Clear the site data
Press Ctrl + Shift + Delete, choose All time, tick Cookies and other site data and Cached images and files, and click Delete data.
Reset Chrome
Open Settings > Reset settings > Restore settings to their original defaults and confirm with Reset settings. This resets the start page, search engine and pinned tabs and turns off extensions; bookmarks and saved passwords stay. To stop notifications after you close Chrome, also turn off Settings > System > Continue running background apps when Google Chrome is closed.
Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Remove extensions you do not recognise
Paste
edge://extensionsinto the address bar and click Remove under anything you did not install yourself.Full procedure with screenshots: Remove a browser extension
Clear the site data
Open Settings > Privacy, search, and services > Delete browsing data > Choose what to clear, set All time, tick Cookies and other site data and Cached images and files, and click Clear now.
Reset Edge
Open Settings > Reset settings > Restore settings to their default values and confirm with Reset. Extensions are turned off and the start page goes back to default; favourites, history and saved passwords stay. To stop notifications after you close Edge, turn off Settings > System and performance > Continue running background extensions and apps when Microsoft Edge is closed.
Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Remove add-ons you do not recognise
Paste
about:addonsinto the address bar, open Extensions, and choose Remove from the three-dot menu of anything you did not install yourself.Full procedure with screenshots: Remove a browser extension
Clear cookies and site data
Open Settings > Privacy & Security > Cookies and Site Data > Clear Data, tick both boxes and click Clear.
Refresh Firefox
Open the menu > Help > More troubleshooting information and click Refresh Firefox. Add-ons and custom settings are removed and the home page goes back to default; bookmarks, history and passwords stay.
Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Take back the notification permission
Safari 18 and later on macOS: open Safari > Settings > Websites > Notifications, select any site you do not recognise and set it to Deny, or click Remove. Untick Allow websites to ask for permission to send notifications at the bottom so no site can ask again.
Remove extensions you do not recognise
In Safari > Settings > Extensions, select anything you did not install yourself and click Uninstall.
Clear the site data
In Safari > Settings > Privacy > Manage Website Data, remove the site's data, or use History > Clear History > all history. To empty the cache as well, turn on Show features for web developers in Settings > Advanced and choose Develop > Empty Caches.
Check the Mac for apps from the ads
Ads also target Mac users with fake players and "cleaners". In Finder > Applications, move anything unknown to the Bin. In System Settings > General > Login Items & Extensions, remove unknown items. Then use Go > Go to Folder to check
/Library/LaunchAgents,~/Library/LaunchAgents,/Library/LaunchDaemonsand/Library/Application Supportfor folders and files with the same unknown names, and empty the Bin.
Then, whichever browser you use
Step 1: Scan the PC if you downloaded anything from the ads
Most people who only saw the notifications can skip this step. If a notification or the page it opened made you download or run a file, delete the file and run a full scan, then a Microsoft Defender Offline scan.
In Windows 11 and Windows 10 open Windows Security > Virus & threat protection > Scan options, select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts and the scan takes about 15 minutes, so save your work first.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
After removal: keep the ads from coming back
If redirects continue or you ran a file
If you only opened a link, there is nothing to remove. These steps are for redirects that keep coming on their own, or for a file you ran after an email, an attachment or a download.
- 1
Scan from outside Windows
Open Windows Security > Virus & threat protection > Scan options, run a Full scan, then the Microsoft Defender Antivirus (offline scan) (Run a Microsoft Defender Offline scan). Malware that is running can block a scan, and the offline scan starts before Windows and the malware load.
- 2
If the scan will not run, use Safe Mode with Networking
Some trojans stop security programs from starting. Restart in Safe Mode with Networking, which loads only the drivers and services needed to reach the internet, press 5 or F5 on the Startup Settings screen, and scan again there (Start Windows or a Mac in Safe Mode On uGetFix).
- 3
Uninstall what you do not recognise
Open Settings > Apps > Installed apps in Windows 11 (Apps & features in Windows 10), sort by install date and uninstall anything installed on the day the redirects began (Uninstall a program or app in Windows On uGetFix). Unwanted programs and altered browser settings can open the address even when the scan finds nothing.
- 4
Clean the browser
Remove extensions you did not install, clear notification permissions and reset the browser: use the browser steps above.
- 5
As a last resort, restore the system
If Safe Mode did not help, open Start, search for Create a restore point, choose System Restore and pick a restore point from before the problem began. Programs installed after that point are removed; your documents are not touched.
A security program may offer to block the address. That does not remove whatever is opening it, and the domain is a normal service used by many sites, so a block can break links you want. Blocking helps only after the real cause is gone. We found no setting in Windows Security for a blocked-sites list, and one the old guide mentioned is not part of Windows.
If you opened an attachment, such as an Excel "web query" file, or typed a password into a page a link opened, change that password now from a different device, turn on two-step verification, and call your bank if you gave a card number.
How to keep it from happening again
The old three-step rule still holds: keep the system updated, use security software and be careful online. The 2020 Paradise case shows why the third step matters most, since it needed no hole in Excel.
Do
- Keep Windows updated, and look at Settings > Windows Update > Update history now and then to check that updates really installed ().
- Keep Microsoft Defender on, with Real-time protection running.
- Open attachments only from people you expect to hear from, and treat an unexpected Excel, Word or "web query" file as suspect, even when it is not a program.
- Download software only from its maker's site or the Microsoft Store.
- Keep a current backup of your files (File History or OneDrive), so an infection or a failed disk does not cost you your documents.
- On public networks, a VPN hides your IP address from the sites you visit, but it does not stop malware and does not make an attachment safe.
Don't
- Run a file that arrived by email just because the sender looks familiar.
- Use cracks, keygens or pirated software: Microsoft names pirated software and phishing as ways the Wacatac family spreads.
- Click a short link in a message from someone you do not know; ask for the full address.
- Assume a fully updated PC is safe from a file you open yourself: updates do not help when the user starts the attack.
- Approve a location request from a page you reached through a short link.
If you use IPLogger, or want to check a link
The service has legitimate uses, and using it is not a crime. Use it for your own site or your own links, and tell visitors.
- 1
Use it on what you own
Statistics for your own blog or shop is the use the site is built for. Turn on its Consent collection option for short links, which the site says follows GDPR and ePrivacy rules, and mention the logging in your privacy policy.
- 2
Do not send tracking links to people who did not ask
The site says it may block links and accounts used for spam, malware or fraud, and that abusers may face legal consequences. In many countries, collecting a person's data without a legal basis is a privacy offence, whatever tool does it.
- 3
To check a link you were sent
The site offers a URL checker that follows hidden redirects; we did not test it, and sending an address to a third party reveals it. Better: ask the sender for the full address, or open it only in a browser profile with notifications blocked and no saved logins.
- 4
If someone logged your address
Do not click further, and do not reply with details. If you are being harassed, keep the messages and tell the platform or the police. A VPN gives you a different address going forward.
Questions about Iplogger.org
Is iplogger.org a virus?
No. Iplogger.org is a website that shortens links and records who opens them, and visiting it installs nothing.
It is a legitimate service that criminals have also used: in March 2020 Trend Micro listed one of its short links as a check-in address in a Paradise ransomware attack, and in April 2020 Unit 42 saw coronavirus websites send visitors' addresses to it.
That makes a redirect to the site worth checking, but it is not proof of infection. If it keeps appearing on many sites, run a Full scan and the Microsoft Defender offline scan, then clean the browser. If you only clicked a link, there is nothing to remove.
Is iplogger.org safe to open?
The home page itself is not a way to infect a PC, but we could not test it fully: on 6 October 2026 our test browser was stopped by Cloudflare's bot check, so we saw only that page. A link created on the site is a different matter.
It hides where it goes, and opening it tells its creator your IP address and device details. Open short links only when you know the sender, use a browser profile with notifications blocked, and never run a file or approve a location request that follows. If you are unsure, ask the sender for the full address.
What can someone see if I click an IPLogger link?
They can see your IP address, the city and country it points to, your browser and operating system, screen details and the page you came from, according to the site's own description. They see your exact GPS location only if your browser or phone asks and you agree. They do not see your name, your passwords or your files.
The address does tie the visit to your internet connection, which matters if you are being harassed. Do not click further, keep the message, and tell the platform or the police. A VPN gives you a different address afterwards.
Why does my browser redirect to iplogger.org?
Four things can send you there:
- a tracking link someone sent you
- a web page with a hidden pixel or iframe
- a program or browser extension on your PC
- the IP LOGGER app itself
A single flash of the address after you clicked a link is the first case and needs no cleanup. Redirects on many sites, with slow browsing and ads that were not there before, point to the third.
Then run a Full scan and the offline scan, remove extensions and programs you do not recognise, take back notification permissions and reset the browser. We could not confirm the three trojan names our 2020 report listed.
How do I remove iplogger.org?
There is nothing called iplogger.org to remove, because it is a website and not a program. What you remove is whatever keeps opening it. Run a Full scan in Windows Security, then the Microsoft Defender Antivirus (offline scan), which starts before Windows loads.
Uninstall unknown programs in Settings > Apps > Installed apps, remove unknown browser extensions and reset the browser. If the scan will not start, use Safe Mode with Networking and press 5 or F5 on the Startup Settings screen. Blocking the address does not remove the cause, so do it only afterwards, if at all.
Is the IP LOGGER app safe?
We did not test it, so we cannot say. The app is listed in Google Play as an IPLOGGER URL Shortener and lets its owner manage links and see the logs.
It talks to its own service, so seeing its traffic is normal. Our 2020 report repeated user complaints about wrong locations and an error saying to check the internet connection; we could not re-check them and have not kept them as findings.
Install apps only from Google Play or the maker's site, read what permissions it asks for, and remove it if you no longer use it. It works for logging other people's visits, so use it only on your own links.
Are iplogger.org and iplogger.com the same?
We could not confirm that they are the same. Our 2020 report called the two interchangeable. Our 2020 capture shows a connection to iplogger.com, so the name was in use at the time, but we did not test that address in 2026, and the home page we read names iplogger.org only.
If you meet iplogger.com, treat it like iplogger.org: the owner of the link sees your visit. The domain iplogger.org was registered on 3 April 2011, according to the public registry. Ask the sender for the real address of whatever the link leads to.
Did iplogger.org spread ransomware?
No. The ransomware in the 2020 report, Paradise, did not come from the site; the attackers used one of its short links. Trend Micro described on 18 March 2020 how an IQY file in spam fetched an Excel formula from the attackers' server, ran a PowerShell command and downloaded the ransomware, with an iplogger.org link listed as a check-in address.
The attack used no hole in Excel, so patched systems were exposed. The lesson is about attachments, not the website: do not open unexpected files, and keep a backup of your documents. We do not know whether the link is still used for that.
Can I block iplogger.org?
You can, but it is usually the wrong first step. Windows Security has no list of blocked sites, and the site is a normal service that many page owners use, so a block may break links you want.
A block on your router, a DNS filtering service or your hosts file would stop the address from loading, but it does not remove the program or extension that opened it, and it does not stop a link that uses a different address.
Find the cause first with a Full scan, the offline scan and a browser clean-up. Block the address only afterwards if you still want to.
Will Fortect remove Iplogger.org?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Iplogger.org, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- iplogger.org: home page (read by automated fetch, our browser test was stopped by Cloudflare) (read October 6, 2026)
- iplogger.org: Tracking pixel or Invisible Image Logger (read October 6, 2026)
- RDAP lookup: iplogger.org registration record (read October 6, 2026)
- Trend Micro: New Variant of Paradise Ransomware Spreads Through IQY Files (read October 6, 2026)
- Unit 42: Studying How Cybercriminals Prey on the COVID-19 Pandemic (read October 6, 2026)
- Microsoft Security Intelligence: Trojan:Script/Wacatac threat description (read October 6, 2026)
- Microsoft Support: Virus and threat protection in the Windows Security app (read October 6, 2026)
- Microsoft Support: Windows startup settings (read October 6, 2026)
- Microsoft Support: System Restore (read October 6, 2026)
- Microsoft Support: Windows Update FAQ (view update history) (read October 6, 2026)
- Google Play: IPLOGGER URL Shortener (read October 6, 2026)