
Kkll ransomware: what it is and how to get your files back
Kkll ransomware is a version of the STOP/Djvu family that encrypts your files, adds .kkll to their names and asks $980 in a note called _readme.txt. Whether you can decrypt them depends on the key type: files locked with an offline key the free Emsisoft decryptor knows can be opened, the rest need backups.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Before you restore backups, a full scan can confirm the program that added .kkll is gone.
Do it yourself · free Remove Kkll ransomware yourself 6 steps, about 18 minutes, no software needed.
Start the steps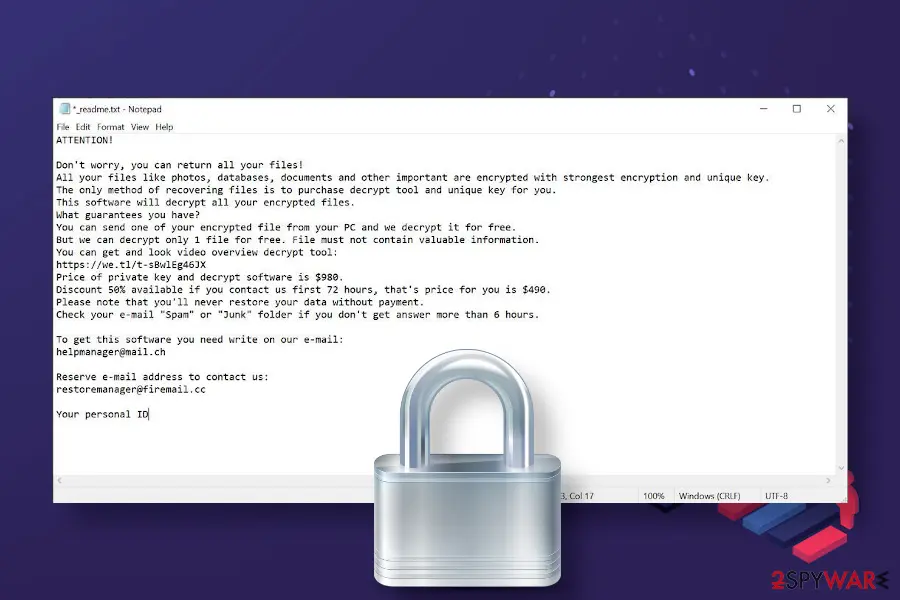
Kkll ransomware: summary
| Type | File-encrypting ransomware of the STOP/Djvu family |
|---|---|
| Risk | High: files are lost unless the key was an offline key Emsisoft has; the crack that brought it may also carry a password stealer |
| Symptoms | Files renamed .kkll, _readme.txt in folders, files that no longer open |
| How to get rid of it | Scan in Safe Mode with Microsoft Defender, remove the crack, then try the Emsisoft decryptor and backups; see the plan |
| Our check | Source check on 6 October 2026 (Emsisoft, BleepingComputer, Microsoft, CISA) and our June 2020 screenshots; we did not run the malware |
| First seen | 5 June 2020 (our first report and the VirusTotal sample) |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 14 more facts
| Name | Kkll ransomware (STOP/Djvu) |
|---|---|
| Encrypted file extension | .kkll |
| Ransom note | _readme.txt, quoted below |
| Decryptor | Emsisoft STOP Djvu decryptor, only for offline-key files |
| Price in the note | $980, or $490 within 72 hours |
| Contact | Two e-mail addresses in _readme.txt; no web page and no wallet address printed here |
| Evidence | 0 write-ups by security sites; no sample analysed yet |
| Encrypted files | .kkll |
| Free decryptor | The free Emsisoft STOP Djvu decryptor works only for files locked with an offline key it holds, and we could not confirm a key for .kkll (checked 6 October 2026) |
| Microsoft Defender name | Ransom:Win32/StopCrypt (the Microsoft family name for STOP/Djvu; the exact label for the .kkll sample is not confirmed) |
| Distribution | Typically cracked programs, keygens and game cheats, fake installers, e-mail attachments, and Remote Desktop with weak passwords in small offices |
| Damage | Files on the PC and connected drives encrypted, restore points often deleted, sometimes a password stealer installed as well |
| Detection names | Microsoft: Ransom:Win32/StopCrypt (the Microsoft family name for STOP/Djvu; the exact label for the .kkll sample is not confirmed) |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against Emsisoft's STOP Djvu decryptor page and blog post, BleepingComputer's STOP support topic, Microsoft Support and CISA, plus our own June 2020 screenshots. We did not run the malware.
What Kkll ransomware is
Kkll is one of the file extensions of the STOP/Djvu ransomware family: it encrypts documents, photos, videos and databases, adds .kkll to each name and leaves a ransom note called _readme.txt in the folders it touched.
It targets Windows, 32-bit and 64-bit. Our June 2020 guide listed it beside Zipe, Nlah, Pezi and other extensions of the same family and called it the 230th variant; we found no source for that count, so we do not repeat it (Emsisoft counted 160 in October 2019).
- Family
- STOP/Djvu ransomware
- Extension
.kkll, for example1.jpg.kkllorpaper.txt.kkll- Note
_readme.txtin every folder it touched; our June 2020 report says it also lands on the desktop- Price in the note
- $980, or $490 if the victim writes within 72 hours
- Contact in the note
- Two e-mail addresses,
helpmanager@mail.chand a reserve address on a second mail service; no web page - Our first report
- 5 June 2020
- Files that can come back
- Only if they were locked with an offline key that Emsisoft holds
Do not write to the addresses; they are shown only to identify the note. The video link in the note differs from copy to copy (our screenshot shows another), and we did not open it.
How the Kkll story went
18 October 2019
Emsisoft releases a decryptor
The post counted 160 variants (new ones since August 2019) and over 116,000 confirmed victims. The free tool covered 148 of the 160.
5 June 2020
Our first Kkll report
We described
.kkllas a new Djvu version from the first half of June. The screenshot is a Windows folder called Test with six.txtfiles ending in.kkll(paper, given, pride and others), next to a panel of icons such as document.doc.kkll, music.mp3.kkll and my photo.jpg.kkll.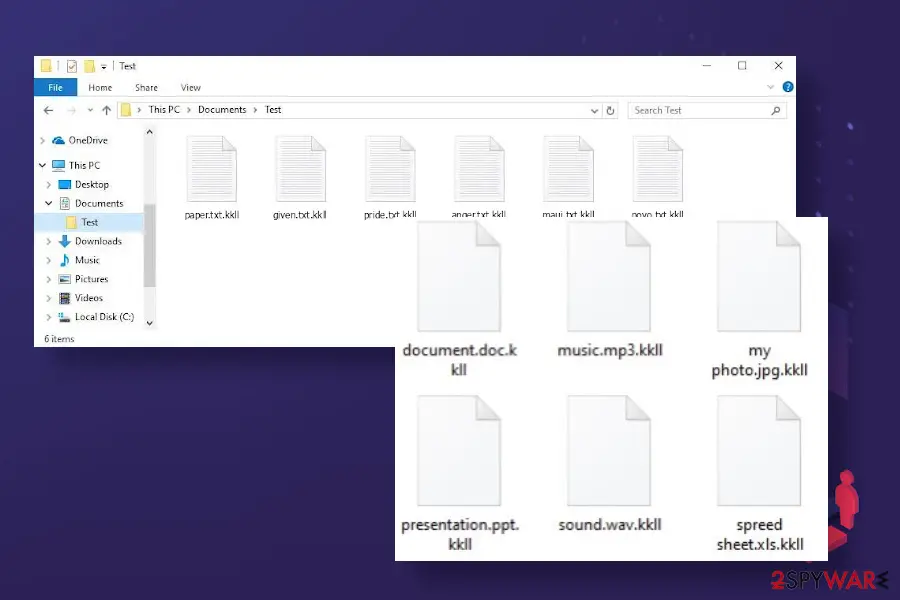
Files renamed with .kkllin our June 2020 screenshot (the folder and the icon panel are two pictures put together).December 2024
The .held variant, then silence
A BleepingComputer moderator wrote that since the release of
.heldin December 2024 there was no news or explanation for the disappearance of the STOP Djvu gang.6 October 2026
Our recheck
We rebuilt the guide from Emsisoft's and BleepingComputer's descriptions. Emsisoft's decryptor page still shows version 1.0.0.5 of 18 October 2019, and we found nothing new about
.kkllitself.
What we checked and what we did not
We did not run this malware and no website is involved, so there is no site test: this is a check of sources and of our own 2020 screenshots, and a quiet check proves nothing about what the file does on your PC.
Kkll ransomware · source check · 6 October 2026
- Family and extensionOur screenshots show
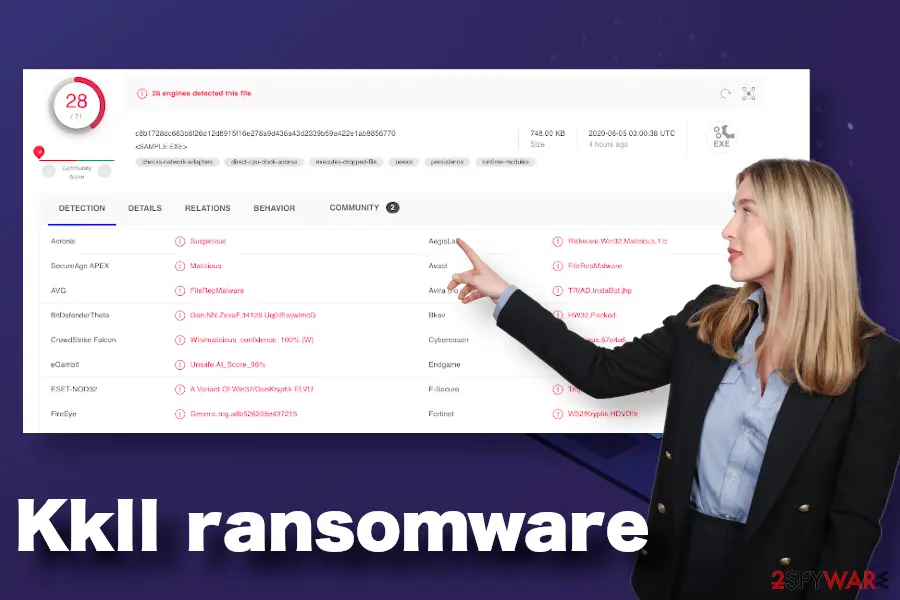
.kkllfiles and_readme.txtopen in Notepad with the Djvu wording. - Detection on day oneOur VirusTotal screenshot of 5 June 2020 shows 28 of 71 engines flagging a 748 KB sample, among them Avast and AVG (FileRepMalware) and ESET-NOD32 (A Variant Of Win32/GenKryptik.ELVU).
- DecryptorEmsisoft says files locked with an offline key it has can be decrypted for all STOP Djvu versions.
- An offline key for .kkll?Not confirmed. Only running the decryptor on your own files shows it.
- Microsoft label, registry, shadow copiesNo exact Microsoft label for
.kklland no source on registry or shadow-copy changes, so none are listed.
Files probably lost unless the key is offline If your ID does not end in t1, an online key was most likely used and only the attackers hold it. The crack that brought the malware may also have installed other threats.
- File extension:
.kkll - Note file:
_readme.txt
How Kkll ransomware behaves
How the family locks files, step by step
Whether files can be saved is settled before the encryption starts, by the kind of key the malware obtains.
- 1
A crack starts the malware
Emsisoft says STOP spreads almost only through key generators and cracks. Our 2020 guide put it the same way: the payload hides inside pirated programs and runs when the hacked software is installed.
- 2
It asks its server for a key
If the command servers answer, BleepingComputer's support topic says the malware gets a random online key that belongs to this victim alone.
- 3
No answer: a built-in key
When the server cannot be reached it falls back on a hard-coded offline key. One extension has one offline ID, so many victims share it.
- 4
Files are locked
Emsisoft names Salsa20 and says encrypted files are 334 bytes larger than the originals in the new variants. Everything outside the system folders is a target, and
.kkllis appended to each name. - 5
The note is written
_readme.txtnames the price, two addresses and your personal ID.
Online key or offline key: what your ID tells you
Look at the end of the personal ID in _readme.txt. An ID ending in t1 is generally an offline ID, and only then can the free Emsisoft decryptor help.
| Offline key | Online key | |
|---|---|---|
| Used when | The malware found no server | The malware reached its server |
| Shared by | Many victims: one offline ID per extension | Nobody: one key per victim |
| ID in the note | Generally ends in t1 | Does not end in t1 |
| Emsisoft decryptor | Works only if Emsisoft already holds this key | Cannot work: only the attackers hold the key |
| Message it prints | "No key for New Variant offline ID ... decryption MAY be possible in the future" | "this ID appears to be an online ID. decryption is impossible" |
Our 2020 guide mixed this up. It named AES for old versions and RSA for new ones; Emsisoft names Salsa20. It said new strains rarely get online IDs, which is the wrong way round: online keys are the normal case and the offline key is the fallback. It was right that unique server-made IDs killed the old STOPDecrypter for files locked after August 2019.
What it does to the PC
Beyond the encryption, the public record is thin: most of what our 2020 guide listed is general ransomware behaviour we could not tie to .kkll.
Kkll ransomware · behaviour claims · 6 October 2026
- Encrypts non-system files, appends `.kkll`Seen in our June 2020 screenshot and in Emsisoft's description of the family.
- Files in `%AppData%` or `%Temp%`From our 2020 guide; no source we could check. Look there during the scan, but delete nothing by hand that you cannot identify.
- Elevated PowerShell deletes shadow copiesFrom our 2020 guide, and common in ransomware, but not confirmed for
.kkll. Check whether Previous Versions lists anything. - Hosts file blocks security sitesBleepingComputer advises resetting the hosts file if the decryptor cannot connect. We have no test showing Kkll doing it.
Behaviour beyond the encryption is not confirmed Treat the PC as untrusted until it has been scanned in Safe Mode: whatever came with the crack may still be running.
How it reaches PCs
The documented route is a crack or keygen for paid software; Emsisoft calls it almost the only one.
- High
Cracks and key generators
Emsisoft's October 2019 post says STOP spreads almost exclusively through them. Our 2020 guide named programs people go hunting for, such as Adobe Photoshop CS6 Extended, GTA 3, Adobe Acrobat XI Pro and Camtasia 9 with serial keys, shared on peer-to-peer sites and doubtful download pages.
- High
Pirated installers and activators
BleepingComputer lists adware bundles, pirated software, Office and Windows activators, cracks and shady sites. Our 2020 guide cited Reddit reports that put pirated programs first.
- Low
Spam attachments
Our 2020 guide said more than half of ransomware arrives as a PDF or ZIP in a fake courier, business or government e-mail. We found no source for that figure, and neither Emsisoft nor BleepingComputer names e-mail for this family: possible, unproven.
What to do in the first hour
- 1
Stop running the crack
Close the installer, crack or keygen folder, and do not start those files again.
- 2
Disconnect
Unplug the cable or turn off Wi-Fi so nothing is sent out or encrypted on shared drives.
- 3
Keep the note, back up the locked files
Photograph the screen; keep
_readme.txt. Our 2020 guide advised copying the.kkllfiles to a USB or external drive before the scan, so a mistake in removal cannot lose them for good. We keep that advice; unplug the drive afterwards. - 4
Do not write to the attackers
The free test file starts a conversation: they ask for your ID and a file, name the price and expect you to buy the coins.
- 5
Report it
In the US, CISA's guide lists cisa.gov/report, your local FBI field office and the FBI's IC3 at ic3.gov. Elsewhere, use your national police or cybercrime service.
The Kkll ransomware note
ATTENTION!
Don't worry, you can return all your files!
All your files like photos, databases, documents and other important are encrypted with strongest encryption and unique key.
The only method of recovering files is to purchase decrypt tool and unique key for you.
This software will decrypt all your encrypted files.
What guarantees you have?
You can send one of your encrypted file from your PC and we decrypt it for free.
But we can decrypt only 1 file for free. File must not contain valuable information.
You can get and look video overview decrypt tool:
hxxps://we.tl/t-WJa63R98Ku
Price of private key and decrypt software is $980.
Discount 50% available if you contact us first 72 hours, that's price for you is $490.
Please note that you'll never restore your data without payment.
Check your e-mail "Spam" or "Junk" folder if you don't get answer more than 6 hours.
To get this software you need write on our e-mail:
helpmanager@mail.ch
Reserve e-mail address to contact us:
restoremanager@firemail.cc
Your personal ID:
Can Kkll ransomware files be decrypted?
Can .kkll files be decrypted?
Sometimes: only with Emsisoft's STOP Djvu decryptor and only if your files were locked with an offline key it holds. Online-key files cannot be opened by anyone but the attackers.
Our 2020 guide said there is no Kkll decryptor and that the old STOPDecrypter fails on new Djvu. Half true: Emsisoft's tool is made for the whole family and opens offline-key files only. The guide also hoped researchers would find a flaw in the encryption; six years on we found no report of one.
| What the tool says | What it means | What to do |
|---|---|---|
Files open, ID ends in t1 | Offline key that Emsisoft holds | Check the files, then copy them to a clean drive |
| "No key for New Variant offline ID" | Offline ID, key not known yet | Keep copies and retry every week or two; there is no timetable |
| "this ID appears to be an online ID" | Online key | The tool cannot help; use backups |
Waiting has a catch: a BleepingComputer moderator says Emsisoft gets an offline key only after some victim has paid and passed the key on, and nothing announces it. Sending file pairs to Emsisoft works only for old Djvu.
- 1
Clean the PC first
Finish the scan in the removal plan, or the malware can lock the restored files again.
- 2
Work on copies
Copy the
.kkllfiles and one_readme.txtto a USB drive, and read how your personal ID ends. Send the ID to nobody. - 3
Get the tool from Emsisoft only
Use the emsisoft.com page in our sources and press Download; open
decrypt_STOPDjvu.exefrom the pop-up at the bottom of the browser. - 4
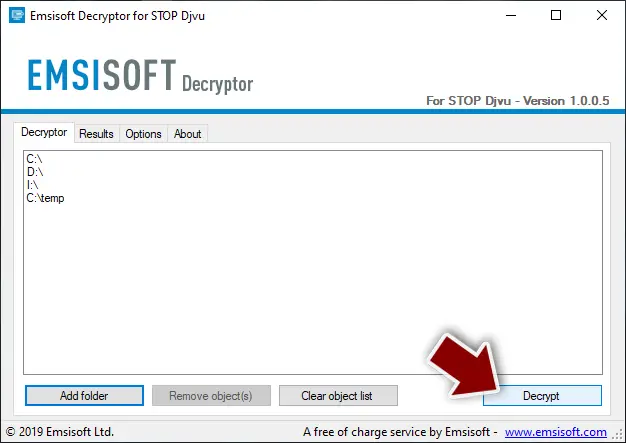
Accept the prompts, press Decrypt
Say Yes to User Account Control and the License Terms, OK to the Disclaimer. The tool lists your drives; Add folder adds more. It needs an internet connection to ask Emsisoft's server for the key.
Do
- Keep the encrypted files even if the tool fails today
- Check that decrypted files open before deleting the encrypted ones
Don't
- Do not buy a "decryptor" from anyone, the note's authors included
Should you pay the ransom?
No. The note asks $980, or $490 within 72 hours. Our 2020 guide said to expect payment in Bitcoin and that many victims pay because they cannot reach their files; the note names no currency, and no source we read says paying works reliably.
- High
You pay and get nothing
Nobody can hold the authors to a promise. Our 2020 guide noted that some Djvu victims called the criminals polite and got a tool at once; that is no reason to expect it, and a payment cannot be taken back.
- Medium
The 72-hour discount is pressure
Half price only if you write first, within three days: the timer exists to hurry you.
- Medium
The free test file
One file decrypted for free proves nothing about the rest. Avoid any contact with the authors.
BleepingComputer says online-key files cannot be decrypted without the private key the criminals keep, and that offline keys reach Emsisoft only after a victim has paid. Our 2020 guide did not recommend paying either, and suggested copying the data and trying recovery programs.
How to remove Kkll ransomware
Tools you'll need
All of these are free except where noted. Download them on a clean device if the infected PC is offline.
- A USB stick: to keep the ransom note, two or three encrypted files and screenshots off the infected PC.
- Microsoft Defender Offline: built into Windows 11 and Windows 10; scans before Windows starts, so running malware cannot hide.
- Microsoft Safety Scanner: a second, portable scanner with current signatures; each download works for 10 days.
- ID Ransomware: identifies the family from the note and one encrypted file and says whether a decryptor exists.
- No More Ransom: the free decryptors from police and security companies; check it again every few months.
- Fortect (optional): scans Windows for malware and repairs the system files and settings it damaged. The free scan is in the box above.
How to remove Kkll ransomware and get your files back
Work in this order.
Disconnecting comes first, removal comes before any restore, and nothing here asks you to contact the attackers.
Step 1: Disconnect the PC and unplug backup drives
Unplug the network cable or turn off Wi-Fi, and disconnect USB drives, external disks and network shares, so Kkll ransomware cannot reach more files. Pause OneDrive, Google Drive or Dropbox sync, because synced folders upload the encrypted copies over the good ones.
Leave the PC on but offline while you read the next steps, since a restart can let the ransomware run again. This applies to Windows 11 and Windows 10 alike.
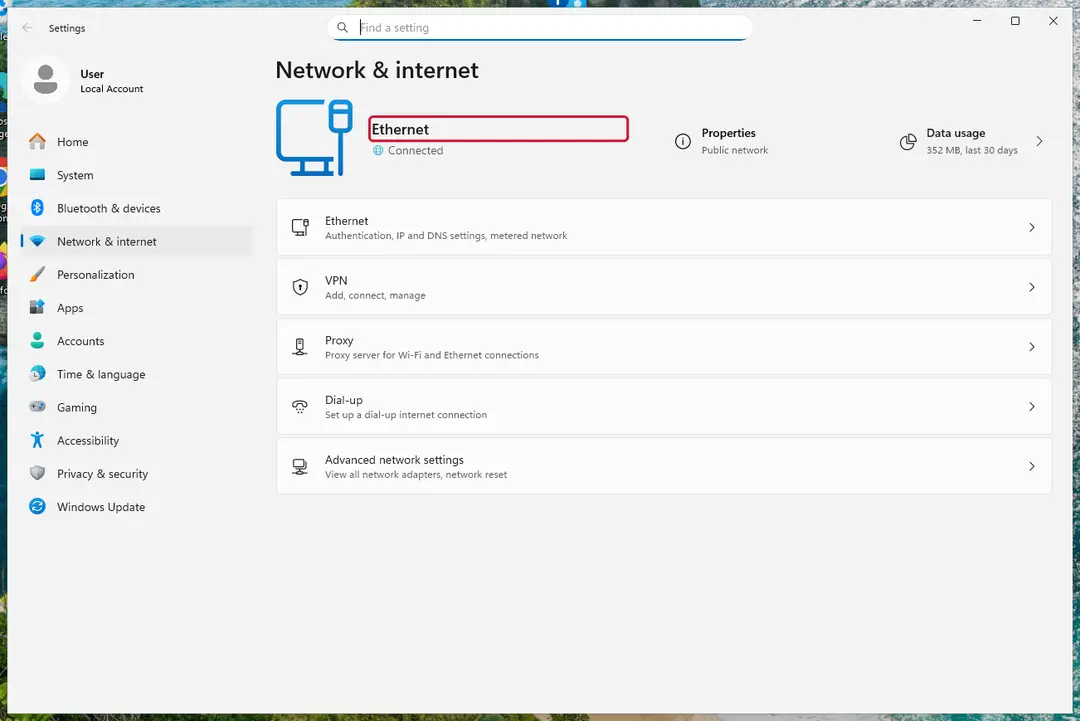
Windows 11: turn off Wi-Fi to take the PC offline. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 2: Save the ransom note and confirm the family
Your files now end in
.kklland the instructions are in_readme.txt. Save both to a USB stick, a copy of the note and two small encrypted files, before anything else.On another device, check them with ID Ransomware or Crypto Sheriff: the family name decides which decryptor, if any, can help. Keep the note's ID and contact line for your report.
Windows 11: the ransom note and encrypted files to copy for identification. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 3: Check for a free decryptor
Our last check found that for Kkll ransomware, the free Emsisoft STOP Djvu decryptor works only for files locked with an offline key it holds, and we could not confirm a key for .kkll (checked 6 October 2026).
Look again yourself in the No More Ransom list and the free decryptor pages of Emsisoft, Avast and Kaspersky, which add new families every year.
A decryptor needs the ransomware gone first, or it encrypts the files again. Keep at least one copy of the encrypted files on an external drive, even if no tool works yet.
Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 4: Remove the ransomware before you restore or decrypt
Removing Kkll ransomware does not bring the files back, but it has to come first. Start with Defender's Full scan, then the offline scan from the same Scan options page, which checks the disk before Windows loads.
If the scan cannot start, use Safe Mode with Networking. Delete the ransom notes only after you have saved a copy, because removal tools sometimes leave them behind on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Look for shadow copies of the files
Windows keeps shadow copies for restore points and backups, and some ransomware fails to delete them.
vssadmin list shadowsin an administrator Command Prompt tells you at once whether any exist.If they do, right-click the folder that held your files, open Properties > Previous Versions, select a version from before the attack, and click Open to check it before you Restore or copy the files out. Windows 11 and Windows 10 both have the tab.
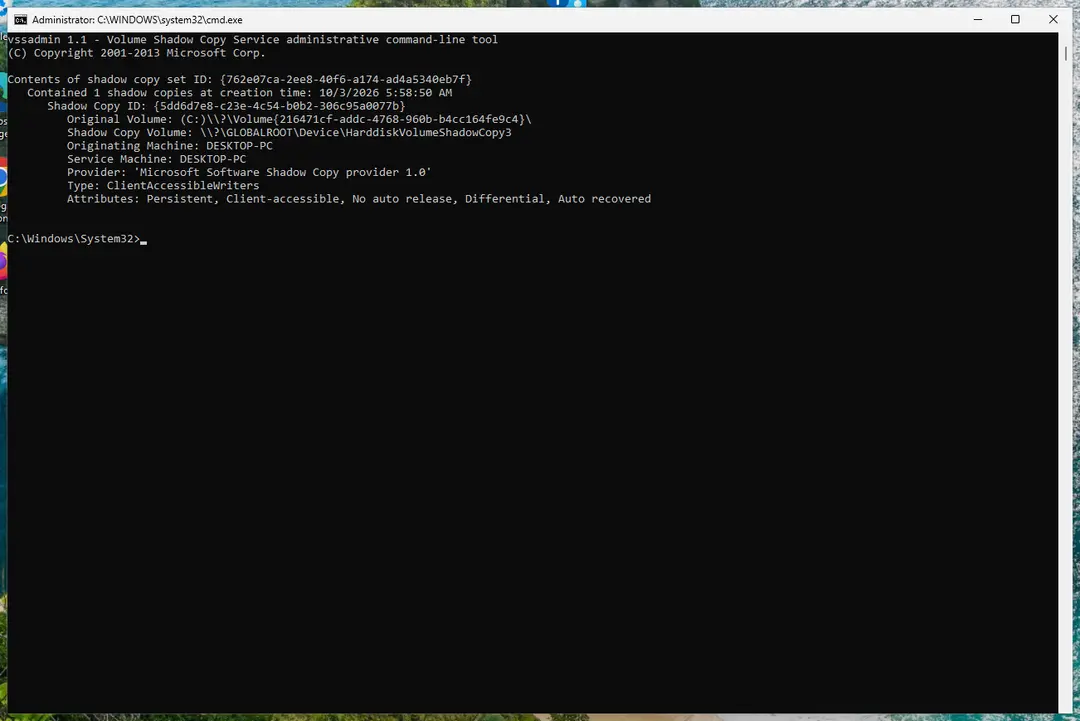
Windows 11: vssadmin list shadows shows whether shadow copies exist. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 6: Restore the files from a backup or recover deleted originals
A backup made before the attack is the surest way back. Connect it only once the PC is clean, then restore from File History, Windows Backup, OneDrive's Restore your OneDrive or your own external copies.
Without a backup, try file recovery: the originals that Kkll ransomware deleted may still be on the disk until something overwrites them. Install nothing new on the drive you want to recover from on the Windows 11 or Windows 10 PC.
Full procedure with screenshots: Recover deleted files (Recycle Bin, backups, OneDrive) On uGetFix
Report it and recover your files
Report it
Report the attack even if you do not expect the files back: insurers and banks ask for the report number, and police use the contacts in the note to link cases.
- United States
- FBI IC3 · FTC ReportFraud
- United Kingdom
- Report Fraud (formerly Action Fraud) · NCSC
- Australia
- ReportCyber (ASD)
- EU countries
- Europol: national reporting sites
Give the victim ID, the note and the date the files were encrypted. A business that holds personal data may also have to notify its data protection authority, in the EU within 72 hours.
Other ways to get files back
Removing the ransomware and recovering files are separate jobs: a scan clears the malware but does not turn .kkll files back into documents.
Once the PC is clean, try these in order and before saving anything new to the disk.
- 1
Your own backups
An external drive, a NAS or cloud storage (OneDrive, iCloud, Dropbox) is the most reliable source. Plug it in only after the PC is clean.
- 2
Previous Versions
Right-click the folder and choose Restore previous versions (on Windows 11 you may need Show more options first), pick a date before the attack and copy files out. Our 2020 guide said this needs System Restore on and that the malware reportedly deletes the copies; the only way to know is to restore one file. System Restore itself does not bring back personal files.
- 3
Shadow Explorer
Our 2020 guide recommended this free program for browsing shadow copies; it cannot find what was deleted, and we have not tested it on
.kkllfiles. - 4
Windows File Recovery
Microsoft's
winfrcan find deleted files that were not overwritten, for examplewinfr C: E: /regular /n \Users\<name>\Documents\with E: on a different drive. It does not decrypt, and it helps only if the originals were deleted rather than overwritten. - 5
Keep the encrypted copies
With an offline ID, retry the decryptor every week or two.
Back up with the 3-2-1 rule
CISA's ransomware guide says to keep backups offline, because many variants look for backups they can reach and delete or encrypt them.
| Number | Rule | Example |
|---|---|---|
| 3 | Three copies of what matters | The file and two backups |
| 2 | Two kinds of storage | Your disk and a USB drive |
| 1 | One copy away from the PC | An unplugged drive, or cloud storage with version history |
How to prevent Kkll ransomware and the next attack
Our 2020 guide warned that pirated downloads are illegal and risk your files.
The documented route is the same, so these habits follow from it.
Do
- Buy the software or use a free alternative
- Keep Microsoft Defender and Windows updates on
- Show file extensions in File Explorer (View > Show > File name extensions)
- Keep an offline backup
Don't
- Do not download keygens, cracks, cheats or pirated installers
- Do not switch off antivirus because a crack tells you to
- Do not open attachments from unknown senders
Questions about Kkll ransomware
How do I open .kkll files?
You cannot open .kkll files normally, because the content is encrypted. They open again only if the free Emsisoft STOP Djvu decryptor has the key for your files. Check your personal ID at the bottom of _readme.txt: an ID ending in t1 is generally an offline ID, which many victims share and which Emsisoft may have or receive later.
An ID not ending in t1 means an online key that only the attackers hold. Renaming the files to remove the extension does nothing, since the data inside stays locked.
Is there a free Kkll decryptor?
There is a free STOP Djvu decryptor from Emsisoft, but it is made for the whole family and works only for files locked with an offline key it has. We could not confirm that a key exists for .kkll. Download it only from the emsisoft.com page listed in our sources, because lookalike decryptor sites are a common trap.
Its page still shows version 1.0.0.5 of October 2019. The older STOPDecrypter tool that our 2020 guide mentioned does not work on new variants. Do not buy a decryptor from anyone.
Should I pay the Kkll ransom?
No, do not pay the ransom. The note asks $980, or $490 if you write within 72 hours, and offers to decrypt one file for free. Nobody can hold the attackers to their promise, and the discount timer is there to hurry you.
A payment cannot be taken back, and it does not tell you whether your files were locked with an online key. Our 2020 guide advised against paying even though some victims said the criminals sent a tool at once. Keep the note, copy the files, run the scan in our plan and check the offline-key decryptor and your backups instead.
How did Kkll ransomware get on my PC?
Most likely through a crack, keygen or pirated installer for paid software. Emsisoft says STOP is spread almost exclusively through key generators and cracks, and BleepingComputer adds adware bundles, pirated software, activators for Office and Windows and shady sites.
Our 2020 guide listed Photoshop CS6, GTA 3, Acrobat XI Pro and Camtasia 9 with serial keys among the downloads, and also named spam attachments, but no source we read ties e-mail to this family. Think back to what you downloaded just before the files stopped opening, and do not run it again.
Will my passwords be stolen?
They might be. Emsisoft says some versions of STOP bundle password-stealing Trojans, and the cracks that carry STOP often carry other malware. Our 2020 guide named AZORult, though we could not confirm it.
We have no evidence about the .kkll sample in particular. Change your important passwords, starting with e-mail and banking, from a clean device, and turn on two-step sign-in so that a stolen password is not enough. Then scan the PC as described in the plan before you sign in to anything from it.
How is Kkll different from .djvu and other STOP extensions?
It is not different in how it works, only in the extension and the ID it uses. Kkll, .zipe, .nlah, .pezi, .gero, .rumba and .radman all belong to STOP/Djvu, so the same kind of note and the same decryptor apply.
What differs is the key: old Djvu variants have an extra option of submitting file pairs to Emsisoft, while new variants after August 2019 do not. The ID of your own note decides what is possible, not the name of the extension. Our 2020 guide called Kkll the 230th variant; we could not confirm that number.
Do data recovery programs or paid recovery services work on .kkll files?
Not on the encrypted content. A recovery program can bring back a file that was deleted and not overwritten, but it cannot decrypt a locked one, and ransomware usually writes the locked data over the original.
Previous Versions and Windows File Recovery are worth a try for that reason, and a backup is better than both. A service that promises to decrypt online-key files is almost certainly paying the attackers or is a scam, so ask where the key comes from before you hand over money.
Will Fortect remove Kkll ransomware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Kkll ransomware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Emsisoft: STOP Djvu decryptor (read October 6, 2026)
- Emsisoft: Emsisoft releases new decryptor for STOP Djvu ransomware (read October 6, 2026)
- BleepingComputer: STOP Ransomware (.STOP .Djvu, .Puma, .Promo) support topic (read October 6, 2026)
- Microsoft Support: Windows File Recovery (read October 6, 2026)
- Microsoft Support: Backup and restore with File History (read October 6, 2026)
- Microsoft Support: Start your PC in safe mode in Windows (read October 6, 2026)
- Microsoft Support: Virus and threat protection in the Windows Security app (read October 6, 2026)
- Microsoft Security Intelligence: Ransom:Win32/StopCrypt.NDD!MTB threat description (read October 6, 2026)
- CISA: #StopRansomware Guide (read October 6, 2026)