
Maos virus: what it is and how to remove it
Maos is a dangerous computer virus known for its ability to lock all pictures, documents, videos, databases, and other personal files, rendering them useless. This is done with the help of a sophisticated encryption algorithm known as RSA - this cipher is strong and can't be deciphered without a special decryption key, which is located on the cybercriminals' servers.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Before you restore backups, a full scan can confirm the program that added .maos is gone.
Do it yourself · free Remove Maos virus yourself 6 steps, about 18 minutes, no software needed.
Start the steps
Maos virus: summary
| Name | Maos virus |
|---|---|
| Type | Ransomware, file-locking malware |
| File extension | .maos appended to all personal files, rendering them useless |
| Family | Djvu |
| Ransom note | _readme.txt; the text is quoted in full below |
| Ransom size | $480/$980 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 14 more facts
| Contact | support@fishmail.top and datarestorehelp@airmail.cc |
|---|---|
| File Recovery | There is no guaranteed way to recover locked files without backups. Other options include paying cybercriminals (not recommended, might also lose the paid money), using Emisoft's decryptor (works for a limited number of victims), or using third-party recovery software |
| Detection names | No Microsoft detection name is known |
| Encrypted file extension | .maos |
| Decryptor | No free decryptor is known for this variant; check No More Ransom (nomoreransom.org) for updates |
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Symptoms | Files renamed with a new extension and a ransom note left in folders |
| Evidence | 4 write-ups by security sites; no sample analysed yet |
| Encrypted files | .maos |
| Attacker contacts | support@fishmail.top |
| Free decryptor | No free decryptor is known (checked 7 October 2026) |
| First seen | 12 December 2022 |
| Facts checked | 7 October 2026 |
- File extension:
.maos - Note file:
_readme.txt - Contact:
support@fishmail.top
From our report of Dec 2022 · not reviewed since
More from our earlier report on Maos virus
- After disconnecting the computer from the network and the internet, do a complete system scan using the security program
- As soon as it is installed, malware has the potential to severely harm some system files, causing instability problems, including crashes and errors.
- Any such damage can be automatically repaired by using PC repair
How Maos virus behaves
From our report of Dec 2022 · not reviewed since
Maos ransomware is a type of malware that may leave you locked out of personal file access forever
Maos is a dangerous computer virus known for its ability to lock all pictures, documents, videos, databases, and other personal files, rendering them useless.
This is done with the help of a sophisticated encryption algorithm known as RSA - this cipher is strong and can't be deciphered without a special decryption key, which is located on the cybercriminals' servers.
All files affected by the virus become distinctively different from normal ones as they acquire a .maos extension and lose their original icons, rendering them inaccessible. This can be incredibly disruptive to victims, who may not have backups of their important files.
Malware will then display a ransom note _readme.txt, demanding payment in order to receive the decryption key. To be more precise, crooks are asking to pay $480/$980 in bitcoin and deliver in a special cryptocurrency wallet. Victims are also offered to conduct test decryption to convince them that the decryption is allegedly possible - support@fishmail.top and datarestorehelp@airmail.cc emails are used for this purpose.
From our report of Dec 2022 · not reviewed since
More about the malware family
Djvu, which Maos virus stems from, is a widely-used and highly-effective type of malware that was first discovered in 2017.
It continues to be a major threat to individuals and organizations today, with nearly a thousand different versions having been identified. It is estimated that hundreds of people fall victim to it every day.
One of the most common ways that people become infected with Djvu ransomware is through the use of pirated software installers. These installers often contain malware, which can be difficult to detect and can infect a system as soon as the software is installed.
Some of the latest versions of ransomware include Mppn, Kcvp, Kcbu, and Tcbu, which are all highly dangerous and can cause significant damage to a victim's files and system.
It is important to avoid using pirated software and to be cautious when opening emails or downloading files from unknown sources to protect yourself from Djvu ransomware and other forms of malware.
From our report of Dec 2022 · not reviewed since
The ransom note
Once it has successfully infiltrated a system and completed the encryption of a victim's files, the Mppn virus immediately opens a ransom note called _readme.txt.
This note explains that the victim's files have been encrypted and that a ransom must be paid in order to receive the decryption key. The note typically includes instructions for how to make the payment, as well as telling users that they have an opportunity to allegedly reduce the ransom size by paying sooner than later:
Both law enforcement authorities and the security community strongly discourage victims of ransomware from paying the ransom. This is because making a payment to cybercriminals not only supports their illegal activities but also does not guarantee that the decryption key will be provided.
If you have fallen victim to ransomware, it is important to avoid paying the ransom. Instead, you should use a reputable anti-malware program to remove Maos ransomware and restore your files from backups, if available.
It is also a good idea to regularly back up your important files to protect yourself from ransomware and other data loss scenarios. If you do not have backups, we provide alternative solutions that might just work for you.
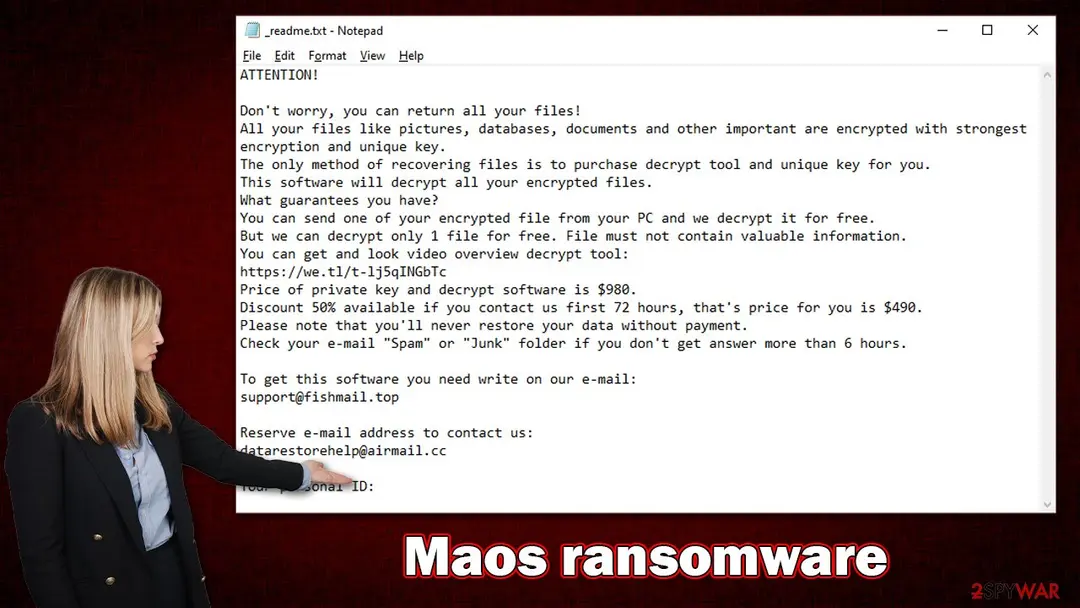
The Maos virus ransom note
ATTENTION!
Don't worry, you can return all your files!
All your files like pictures, databases, documents and other important are encrypted with strongest encryption and unique key.
The only method of recovering files is to purchase decrypt tool and unique key for you.
This software will decrypt all your encrypted files.
What guarantees you have?
You can send one of your encrypted file from your PC and we decrypt it for free.
But we can decrypt only 1 file for free. File must not contain valuable information.
You can get and look video overview decrypt tool:
https://we.tl/t-67n37yZLXk
Price of private key and decrypt software is $980.
Discount 50% available if you contact us first 72 hours, that's price for you is $490.
Please note that you'll never restore your data without payment.
Check your e-mail "Spam" or "Junk" folder if you don't get answer more than 6 hours.
To get this software you need write on our e-mail:
support@fishmail.top
Reserve e-mail address to contact us:
datarestorehelp@airmail.cc
Your personal ID:
How to remove Maos virus
Tools you'll need
All of these are free except where noted. Download them on a clean device if the infected PC is offline.
- A USB stick: to keep the ransom note, two or three encrypted files and screenshots off the infected PC.
- Microsoft Defender Offline: built into Windows 11 and Windows 10; scans before Windows starts, so running malware cannot hide.
- Microsoft Safety Scanner: a second, portable scanner with current signatures; each download works for 10 days.
- ID Ransomware: identifies the family from the note and one encrypted file and says whether a decryptor exists.
- No More Ransom: the free decryptors from police and security companies; check it again every few months.
- Fortect (optional): scans Windows for malware and repairs the system files and settings it damaged. The free scan is in the box above.
How to remove Maos virus and get your files back
Work in this order.
Disconnecting comes first, removal comes before any restore, and nothing here asks you to contact the attackers.
Step 1: Disconnect the PC and unplug backup drives
Unplug the network cable or turn off Wi-Fi, and disconnect USB drives, external disks and network shares, so Maos virus cannot reach more files. Pause OneDrive, Google Drive or Dropbox sync, because synced folders upload the encrypted copies over the good ones.
Leave the PC on but offline while you read the next steps, since a restart can let the ransomware run again. This applies to Windows 11 and Windows 10 alike.
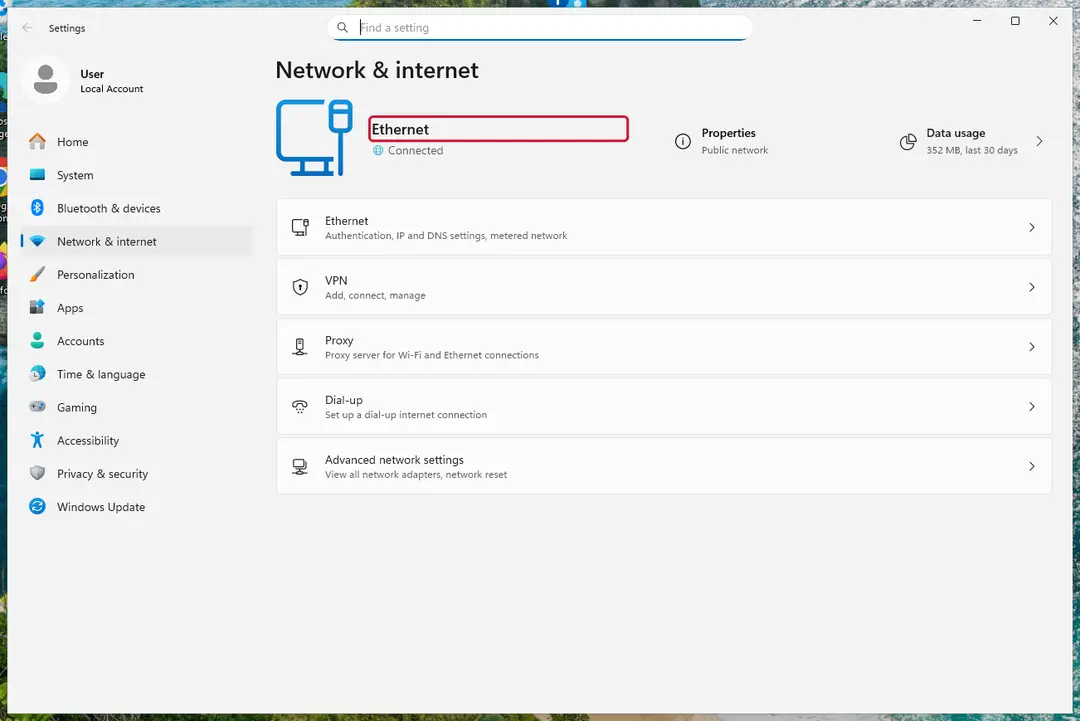
Windows 11: turn off Wi-Fi to take the PC offline. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 2: Save the ransom note and confirm the family
Your files now end in
.maosand the instructions are in_readme.txt. Save both to a USB stick, a copy of the note and two small encrypted files, before anything else.On another device, check them with ID Ransomware or Crypto Sheriff: the family name decides which decryptor, if any, can help. Keep the note's ID and contact line for your report.
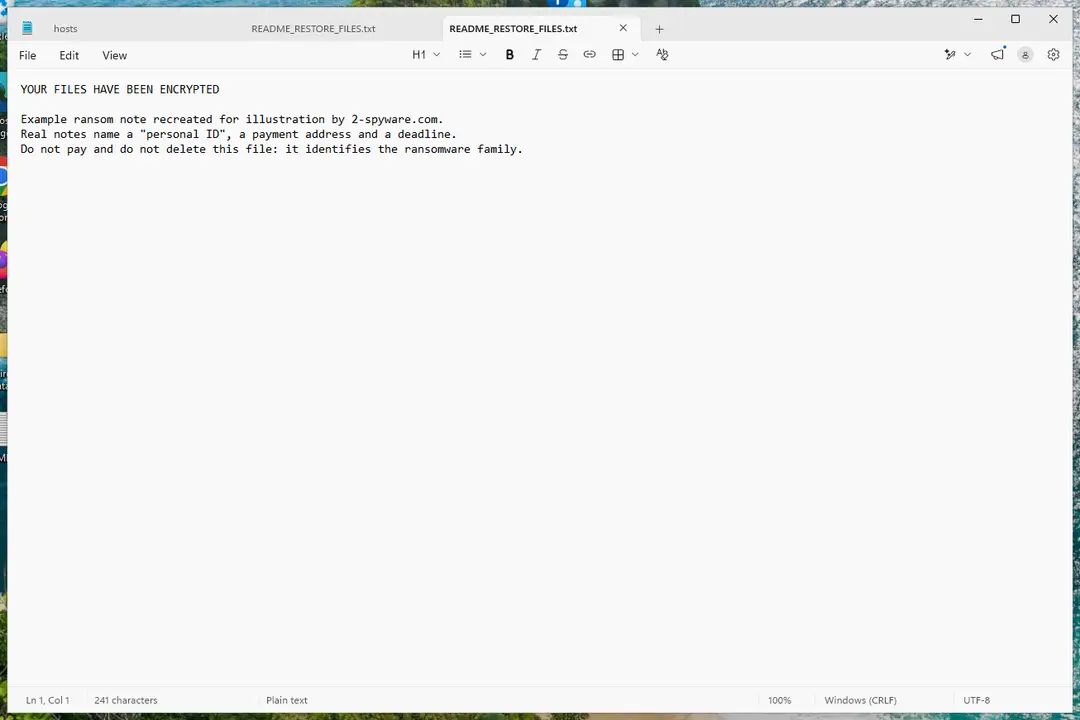
Windows 11: the ransom note and encrypted files to copy for identification. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 3: Check for a free decryptor
Our last check found that for Maos virus, no free decryptor is known (checked 7 October 2026). Look again yourself in the No More Ransom list and the free decryptor pages of Emsisoft, Avast and Kaspersky, which add new families every year.
A decryptor needs the ransomware gone first, or it encrypts the files again. Keep at least one copy of the encrypted files on an external drive, even if no tool works yet.
Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 4: Remove the ransomware before you restore or decrypt
Removing Maos virus does not bring the files back, but it has to come first. Start with Defender's Full scan, then the offline scan from the same Scan options page, which checks the disk before Windows loads.
If the scan cannot start, use Safe Mode with Networking. Delete the ransom notes only after you have saved a copy, because removal tools sometimes leave them behind on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Look for shadow copies of the files
Windows keeps shadow copies for restore points and backups, and some ransomware fails to delete them.
vssadmin list shadowsin an administrator Command Prompt tells you at once whether any exist.If they do, right-click the folder that held your files, open Properties > Previous Versions, select a version from before the attack, and click Open to check it before you Restore or copy the files out. Windows 11 and Windows 10 both have the tab.
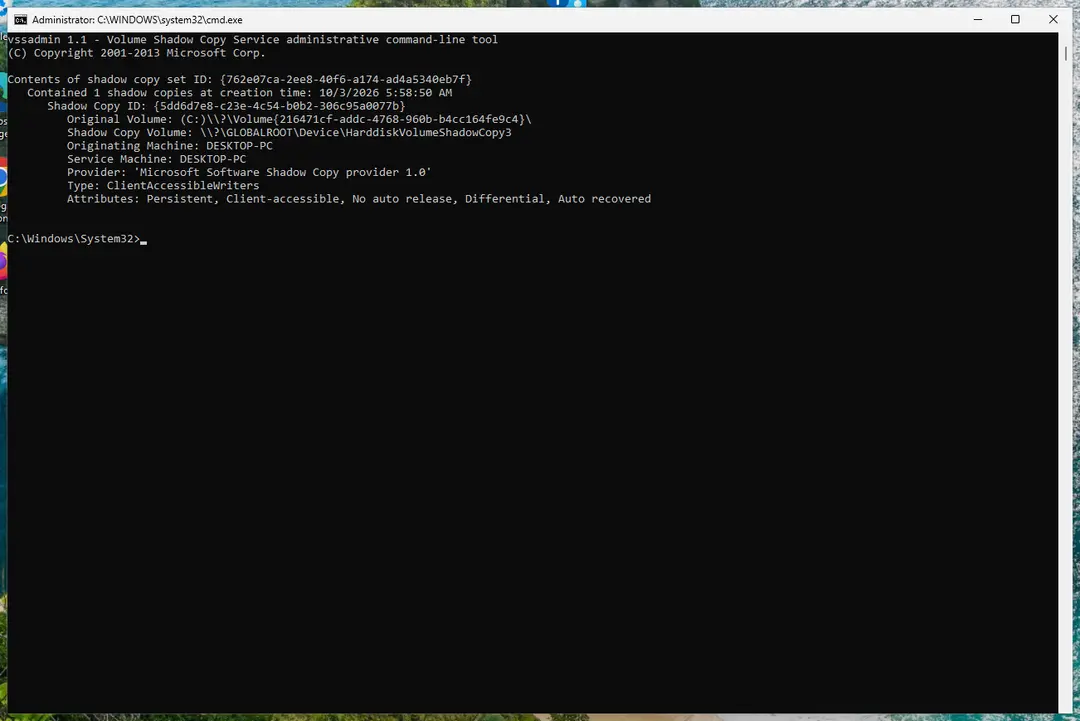
Windows 11: vssadmin list shadows shows whether shadow copies exist. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 6: Restore the files from a backup or recover deleted originals
A backup made before the attack is the surest way back. Connect it only once the PC is clean, then restore from File History, Windows Backup, OneDrive's Restore your OneDrive or your own external copies.
Without a backup, try file recovery: the originals that Maos virus deleted may still be on the disk until something overwrites them. Install nothing new on the drive you want to recover from on the Windows 11 or Windows 10 PC.
Full procedure with screenshots: Recover deleted files (Recycle Bin, backups, OneDrive) On uGetFix
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Restore Windows "hosts" file to its original state
Some ransomware might modify Windows hosts file in order to prevent users from accessing certain websites online. For example, Djvu ransomware variants add dozens of entries containing URLs of security-related websites, such as 2-spyware.com. Each of the entries means that users will not be able to access the listed web addresses and will receive an error instead.
Here's an example of "hosts" file entries that were injected by ransomware:
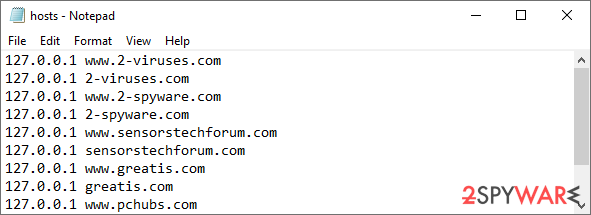
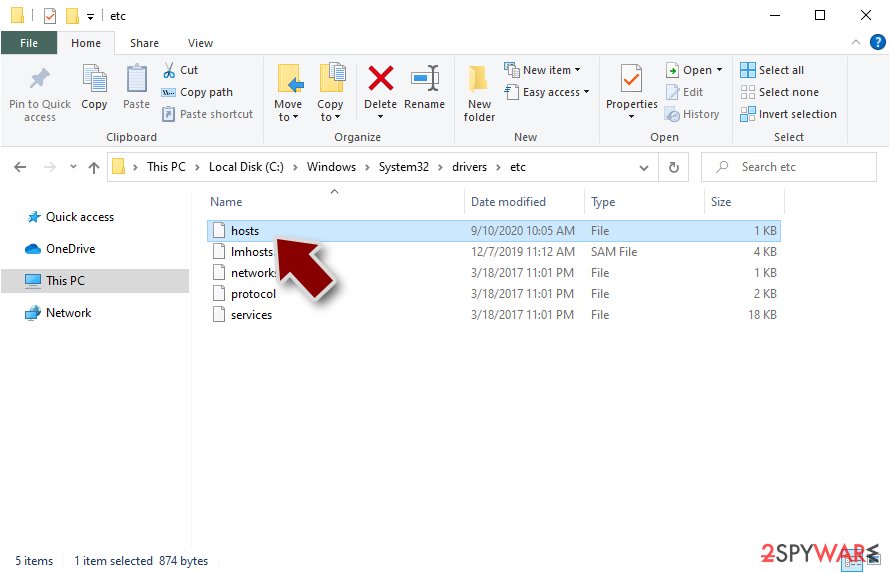
In order to restore your ability to access all websites without restrictions, you should either delete the file (Windows will automatically recreate it) or remove all the malware-created entries. If you have never touched the "hosts" file before, you should simply delete it by marking it and pressing Shift + Del on your keyboard. For that, navigate to the following location:
C:\\Windows\\System32\\drivers\\etc\\
Restore files using data recovery software
Since many users do not prepare proper data backups prior to being attacked by ransomware, they might often lose access to their files permanently. Paying criminals is also very risky, as they might not fulfill the promises and never send back the required decryption tool.
While this might sound terrible, not all is lost - data recovery software might be able to help you in some situations (it highly depends on the encryption algorithm used, whether ransomware managed to complete the programmed tasks, etc.). Since there are thousands of different ransomware strains, it is immediately impossible to tell whether third-party software will work for you.
Therefore, we suggest trying regardless of which ransomware attacked your computer. Before you begin, several pointers are important while dealing with this situation:
- Since the encrypted data on your computer might permanently be damaged by security or data recovery software, you should first make backups of it - use a USB flash drive or another storage.
- Only attempt to recover your files using this method after you perform a scan with anti-malware software.
Install data recovery software
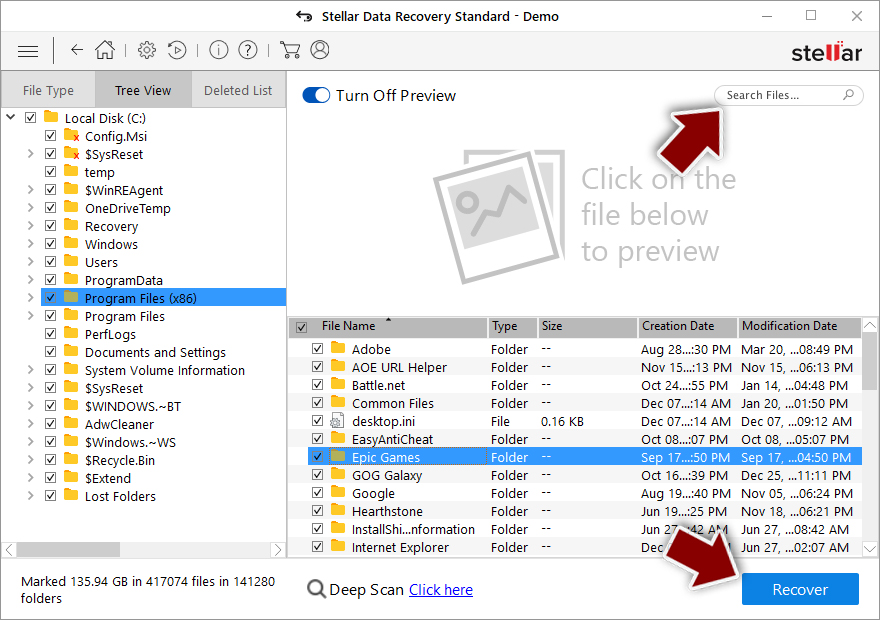
- Download .
- Double-click the installer to launch it.

- Follow on-screen instructions to install the software.
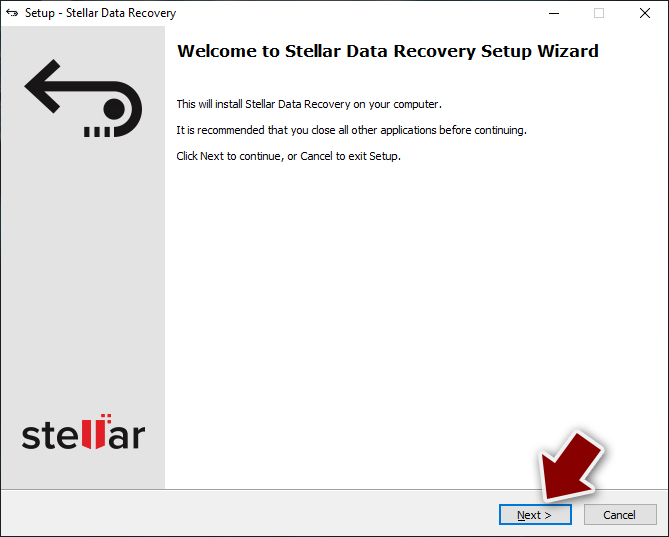
- As soon as you press Finish, you can use the app.
- Select Everything or pick individual folders where you want the files to be recovered from.
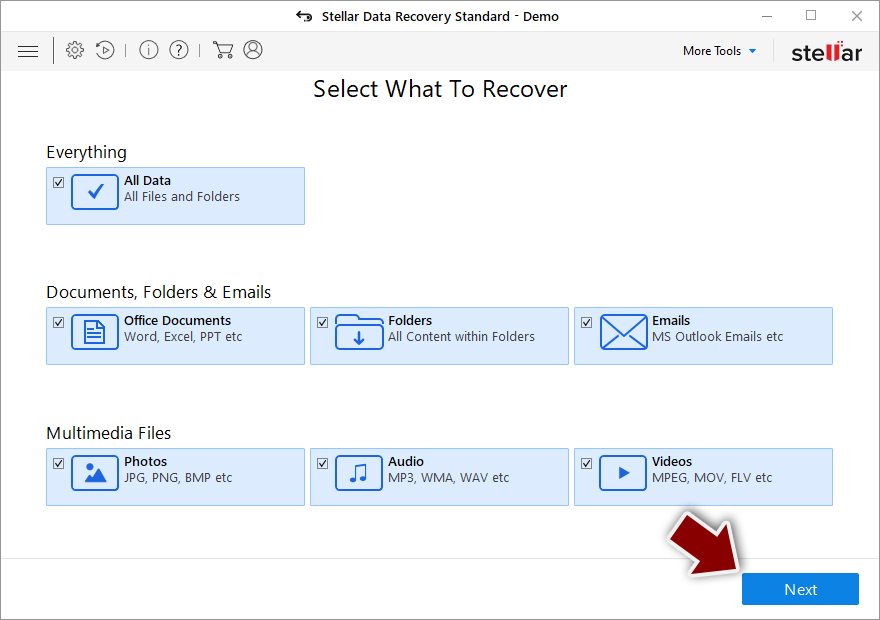
- Press Next.
- At the bottom, enable Deep scan and pick which Disks you want to be scanned.
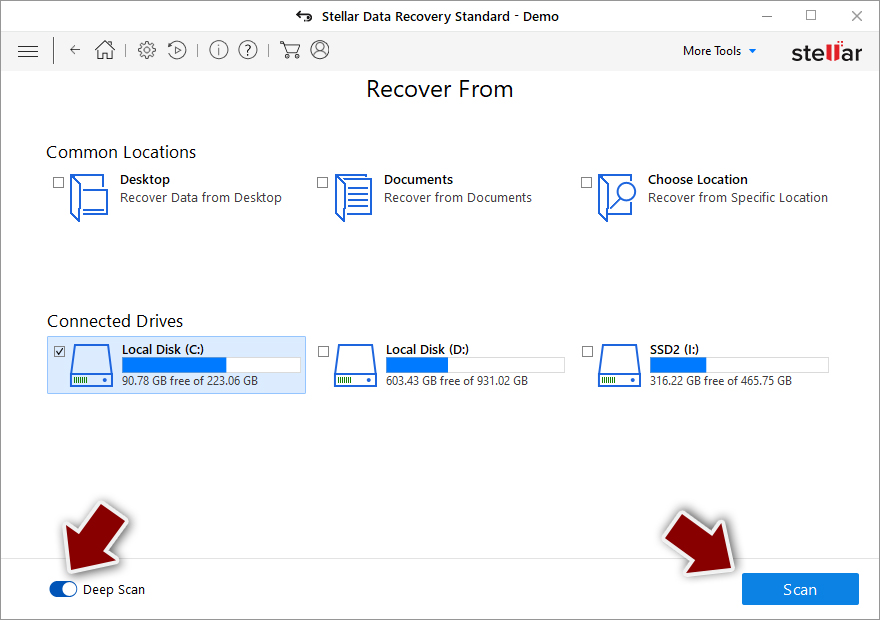
- Press Scan and wait till it is complete.
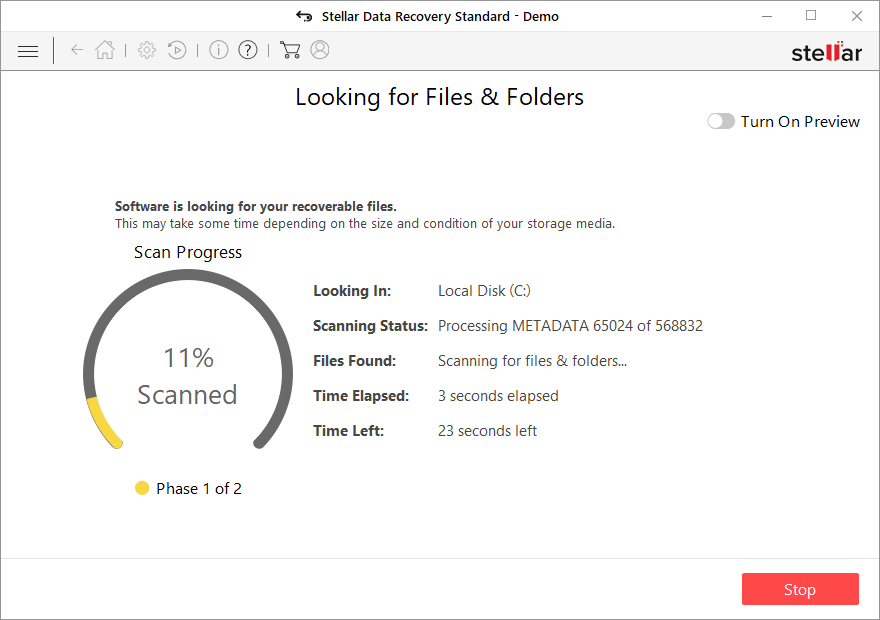
- You can now pick which folders/files to recover - don't forget you also have the option to search by the file name!
- Press Recover to retrieve your files.
Find a working decryptor for your files
File encryption is a process that is similar to applying a password to a particular file or folder. However, from a technical point of view, encryption is fundamentally different due to its complexity. By using encryption, threat actors use a unique set of alphanumeric characters as a password that can not easily be deciphered if the process is performed correctly.
There are several algorithms that can be used to lock data (whether for good or bad reasons); for example, AES uses the symmetric method of encryption, meaning that the key used to lock and unlock files is the same. Unfortunately, it is only accessible to the attackers who hold it on a remote server - they ask for a payment in exchange for it. This simple principle is what allows ransomware authors to prosper in this illegal business.
While many high-profile ransomware strains such as Djvu or Dharma use immaculate encryption methods, there are plenty of failures that can be observed within the code of some novice malware developers. For example, the keys could be stored locally, which would allow users to regain access to their files without paying. In some cases, ransomware does not even encrypt files due to bugs, although victims might believe the opposite due to the ransom note that shows up right after the infection and data encryption is completed.
Therefore, regardless of which crypto-malware affects your files, you should try to find the relevant decryptor if such exists. Security researchers are in a constant battle against cybercriminals. In some cases, they manage to create a working decryption tool that would allow victims to recover files for free.
Once you have identified which ransomware you are affected by, you should check the following links for a decryptor:
- No More Ransom Project
- Free Ransomware Decryptors by Kaspersky
- Free Ransomware Decryption Tools from Emsisoft
- Avast decryptors
If you can't find a decryptor that works for you, you should try the alternative methods we list below. Additionally, it is worth mentioning that it sometimes takes years for a working decryption tool to be developed, so there are always hopes for the future.
From our report of Dec 2022 · not reviewed since
1. Remove malware correctly
If you realize that your files have been locked by ransomware, it is important to remain calm and take action to prevent further damage.
The first step in dealing with a ransomware infection is to remove it from your system. This is essential in order to prevent it from encrypting any more of your files and causing further damage.
The correct way of doing so is by disconnecting your affected device from the internet and network, as crooks may send the commands via Command & Control server.
Some ransomware is designed to self-destruct after encrypting a victim's data, but this is not always the case. In many instances, ransomware is spread alongside other types of malware, such as data stealers or keyloggers. This means that it is essential to remove all malware components in order to recover effectively from a ransomware infection.
The most effective way to eliminate all malware components is to use robust anti-malware software. This type of program is specifically designed to detect and remove malware, including ransomware and any other malicious components that may be present on a system. By using a program like or , you can quickly and easily locate all malicious components and remove them from your system.
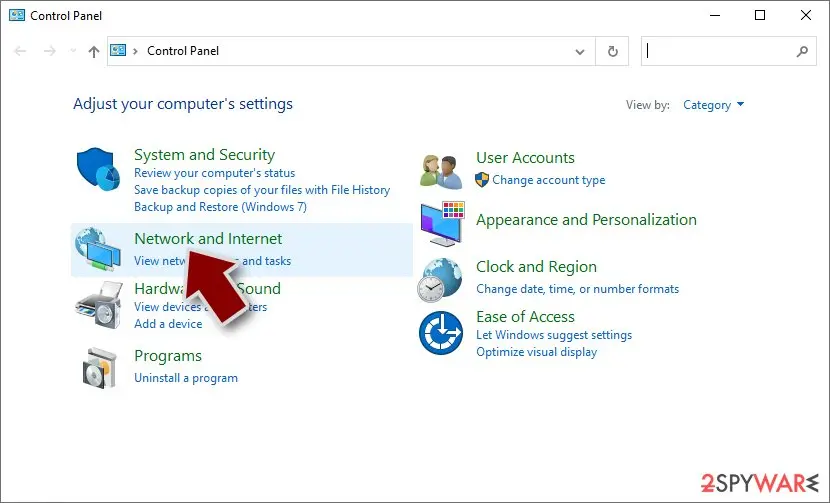
- Type in Control Panel in Windows search and press Enter
- Go to Network and Internet
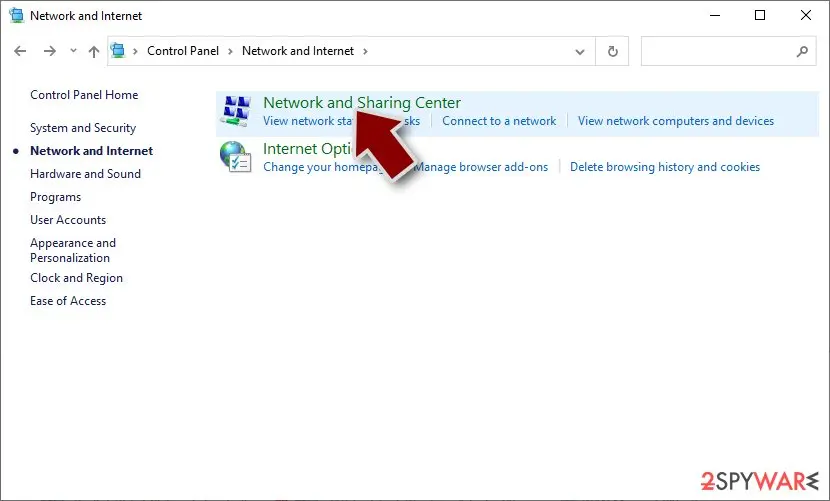
- Click Network and Sharing Center
- On the left, pick Change adapter settings
- Right-click on your connection (for example, Ethernet), and select Disable
- Confirm with Yes.
From our report of Dec 2022 · not reviewed since
2. Use a repair tool
Once malware is installed on a system, it can potentially cause severe damage to system files, resulting in instability issues such as crashes and errors.
By using this type of program, it is possible to fix any problems caused by malware and restore the system to its normal functioning state. It is important to use a trusted and reputable PC repair program in order to ensure that the repair process is successful and that no further harm is done to the system.
- Download
- Click on the ReimageRepair.exe
- If User Account Control (UAC) shows up, select Yes
- Press Install and wait till the program finishes the installation process
- The analysis of your machine will begin immediately
- Once complete, check the results - they will be listed in the Summary
- You can now click on each of the issues and fix them manually
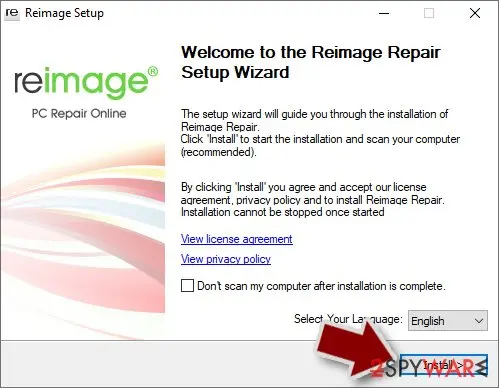
From our report of Dec 2022 · not reviewed since
3. Data recovery process for .maos files
It is important to understand the limitations of security software and to have a plan in place for recovering from a ransomware infection.
Removal of malware is something that this software is designed for, although it would not restore files affected by ransomware back to normal, despite popular belief.
That being said, anti-malware is a solution that can prevent ransomware from being executed on your system in the first place, so you should never ignore warnings coming from it. If you have already been infected and have no file backups, you are limited options, although you shouldn't give up just yet.
As your first step to data recovery, you should make copies of all your encrypted files and place them onto a separate medium, as they might become corrupted during the recovery process.
This option might not work for everyone, as it only works if data was locked with an offline ID.
From here, there are three available outcomes:
- After pressing Download button, a small pop-up at the bottom, titled decrypt_STOPDjvu.exe should show up - click it.
- If User Account Control (UAC) message shows up, press Yes.
- Agree to License Terms by pressing Yes.
- After Disclaimer shows up, press OK.
- The tool should automatically populate the affected folders, although you can also do it by pressing Add folder at the bottom.
- Press Decrypt.
- "Decrypted!" will be shown under files that were decrypted successfully - they are now usable again.
- "Error: Unable to decrypt file with ID:" means that the keys for this version of the virus have not yet been retrieved, so you should try later.
- "This ID appears to be an online ID, decryption is impossible" - you are unable to decrypt files with this tool.
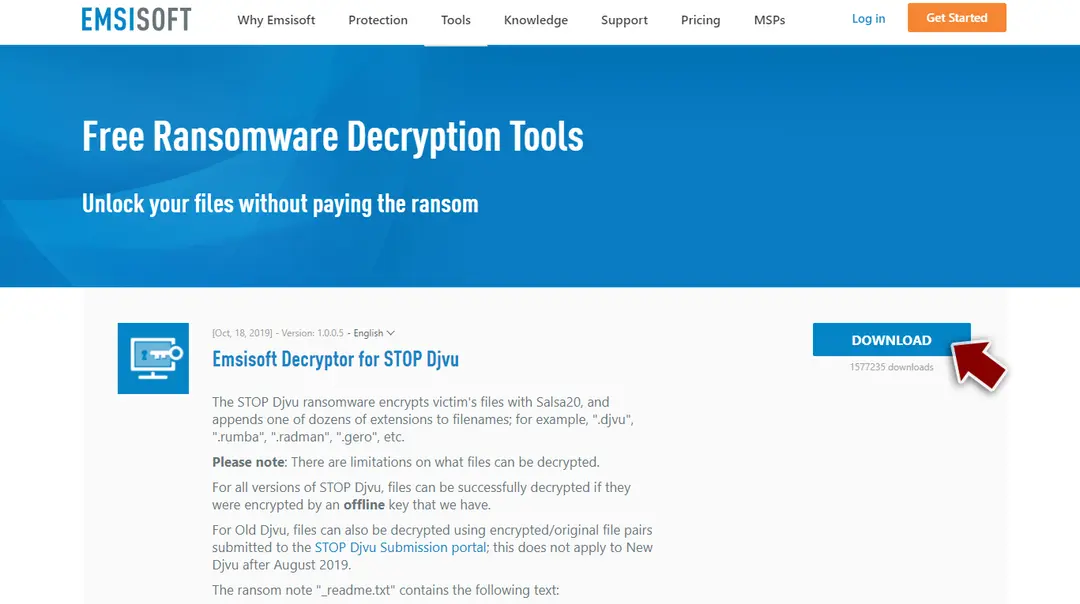
Report it and recover your files
Report it
Report the attack even if you do not expect the files back: insurers and banks ask for the report number, and police use the contacts in the note to link cases.
- United States
- FBI IC3 · FTC ReportFraud
- United Kingdom
- Report Fraud (formerly Action Fraud) · NCSC
- Australia
- ReportCyber (ASD)
- EU countries
- Europol: national reporting sites
Give the victim ID, the note and the date the files were encrypted. A business that holds personal data may also have to notify its data protection authority, in the EU within 72 hours.
Make the next attack harmless
Maos virus could only hurt the files that had no second copy, and the signs (files that end in .maos and no longer open) showed exactly which ones those were.
The 3-2-1 rule fixes that:
- three copies
- two media
- one disconnected
A practical version for a home PC: OneDrive or another cloud backup with version history, plus an external disk that you plug in once a week for File History and then unplug. Test a restore now and then by opening a few files from the backup on another device.
Details, schedules and what not to back up are in our 3-2-1 backup guide for Windows.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
Questions about Maos virus
How do I open .maos files?
You cannot open them by renaming or with another program, because the content of files ending in .maos has been encrypted. The only ways back are a working decryptor for the family, or clean copies from elsewhere:
- OneDrive versions
- File History
- an offline backup drive
- Previous Versions if the ransomware did not delete them
Identify the family first by uploading the ransom note and one encrypted file to ID Ransomware or No More Ransom. Avoid websites and programs that promise to open any encrypted file; they do not work and some are scams.
Is there a free Maos virus decryptor?
We last checked on 7 October 2026, and for Maos virus no free decryptor is known. We check No More Ransom, which collects free tools from police and security companies, and the decryptor pages of the major antivirus vendors. A working decryptor exists only when the encryption has a flaw or the keys were leaked or seized.
Ignore sites and videos that offer a "Maos virus decryptor" for download or for a fee: these are usually scams or malware. Real decryptors are free and come from known security companies or law enforcement. Keep the encrypted files in case a tool appears later.
Are ransomware recovery services legitimate?
Some are, but read the offer carefully. Genuine data-recovery firms recover deleted originals from disks or rebuild damaged files, and they say so. Others promise to "decrypt any ransomware" for a fixed price, which is impossible without the key; they quietly pay the attackers and keep a margin, sometimes without telling the victim.
Be especially careful with services that contact you after you post about the attack online. Ask for references, a written method and a no-result-no-fee clause, and check the free tools on No More Ransom first.
Should I pay the ransom?
We advise against it, and so do the FBI, Europol and national cyber agencies. Payment does not guarantee a working tool: some attackers never reply, some tools damage files, and some variants have no decryptor at all. Paying also funds further attacks and can make you a target again.
Before considering payment, try every recovery option in this guide and report the attack. Companies must involve their legal adviser and insurer, because payments to sanctioned groups can be illegal. If files are truly irreplaceable, store the encrypted copies and wait; decryptors sometimes appear later.
How did Maos virus get on my computer?
The way Maos virus spreads has not been documented yet, so look at your own recent activity. On home PCs, ransomware most often comes with cracked programs, game cheats, key generators and fake updates, or with an e-mail attachment that was opened. On business networks, attackers usually log in through Remote Desktop with a stolen or guessed password.
Think back to what was downloaded or installed in the days before files that end in .maos and no longer open, and check the Downloads folder and Installed apps sorted by date. Keep anything suspicious for your report, but do not run it again.
Did Maos virus steal my files or passwords?
We do not know yet. Nothing published so far shows data theft by Maos virus, but the only confirmed sign is files that end in .maos and no longer open, which says nothing about what happened before. Many current ransomware attacks copy files or run a password stealer first, so it is wise to act as if they did.
From a clean device, change the passwords that were saved in the browsers on this PC, starting with e-mail and banking, sign out of all sessions and turn on two-step verification. Watch bank statements and account activity for the next few weeks.
Is Maos virus the same as other ransomware with a similar name?
Not necessarily. Ransomware names come from the file extension, the note or a word in the code, so unrelated families often end up with similar names, and one family can appear under several names. The difference matters: a decryptor or advice for one family does not fit another and can damage files.
Compare the ending added to your files and the exact name of the note with the summary table at the top of this guide, then upload the note and one encrypted file to ID Ransomware from a clean device. If the result names another family, follow the guide for that family instead.
Can I delete _readme.txt?
Yes, the note itself is harmless text and deleting it does not affect your files. Keep at least one copy first, outside the infected PC. _readme.txt contains your personal ID and the attackers' contact details, which identification services use to tell which family encrypted your files, and which a decryptor may need later.
Police reports also ask for it. Once you have saved a copy, you can remove the notes from every folder after the ransomware program has been removed and your files are restored or backed up.
Will .maos spread to my other drives?
It can. Ransomware encrypts every drive and network share it can reach while it runs, so external disks, USB sticks and shared folders connected during the attack may also have files ending in .maos. Disconnect everything now, then check each device from a clean computer.
Do not plug a backup drive into the infected PC until the ransomware has been removed with an offline scan. Cloud folders such as OneDrive sync the encrypted versions, but they keep earlier versions you can usually restore.
Will Fortect remove Maos virus?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Maos virus, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Comparitech: What is RSA encryption and how does it work? (read October 7, 2026)
- Trend Micro: Command and Control [C&C] Server (read October 7, 2026)
- Norton: Keyloggers 101: A definition + keystroke logging detection methods (read October 7, 2026)
- CISA: StopRansomware (read October 7, 2026)
- No More Ransom (read October 7, 2026)