
Mozart malware: what it is and how to remove it
Mozart malware is a backdoor that was first identified by security researcher Vitali Kremez at the end of February 2020. While the virus operations are likely to be common to a backdoor (such as other privilege escalation, malware proliferation, harvesting of information, data corruption, etc.), one of its unique features lie within the communication protocol, which is transferred over a DNS instead of a regular HTTP/HTTPS.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
An automatic scan can look at calc.exe and the other programs installed around the same time.
Do it yourself · free Remove Mozart malware yourself 6 steps, about 18 minutes, no software needed.
Start the steps
Mozart malware: summary
| Distribution | Security researchers found malware samples that were distributed with the help of malicious emails with an attached PDF ("15-feb-sell-out.pdf") file that includes a malicious link which, once clicked, downloads the payload. Nevertheless, many other distribution methods can be used by attackers, including exploits, web injects, drive-by downloads, software cracks, etc. |
|---|---|
| Damage | It is yet unclear what the main goals of perpetrators are, although most malware is created for financial benefit – it can relate to sensitive information harvesting, data theft, illegitimate money transfers, and other malicious activities |
| Name | Mozart malware |
| Type | Backdoor, Trojan |
| Special features | Hides communications by using DNS protocol instead of HTTP/S |
| Associated files | calc.exe, mozart.txt |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 7 more facts
| Symptoms | Typically, backdoors are a stealthy type of malware, which means that symptom exposure [to home users] is minimal – users may see the slowdown of their internet speed, increased network activity, application crashes, high resource usage, etc. |
|---|---|
| Termination | Backdoor malware can establish root access inside a compromised machine, which means its manual termination becomes impossible. Only next-gen anti-malware software can detect and delete all the malicious files implemented by the malware |
| Detection names | No Microsoft detection name is known |
| Evidence | 6 write-ups by security sites; details still limited |
| File names | calc.exe |
| First seen | 26 February 2020 |
| Facts checked | 6 October 2026 |
What Mozart malware does on an infected PC
From our report of Feb 2020 · not reviewed since
Mozart malware is a computer threat that uses DNS protocol to communicate with remote servers, this way evading AV detection
Mozart malware is a backdoor that was first identified by security researcher Vitali Kremez at the end of February 2020.
While the virus operations are likely to be common to a backdoor (such as other privilege escalation, malware proliferation, harvesting of information, data corruption, etc.), one of its unique features lie within the communication protocol, which is transferred over a DNS instead of a regular HTTP/HTTPS.
This allows Mozart malware to evade the detection of security applications that monitor the HTTP traffic for malicious activity. Another benefit of the DNS protocol is that the commands from the attackers can be transferred via the DNS TXT records, which might induce malicious actions, such as data deletion, malicious code execution, etc.
Despite being evasive when it comes to its communications with a remote server, Mozart malware removal can be performed with multiple different anti-virus programs that detect the malicious activity of the virus.
Named after one of the greatest musicians of all time, Mozart virus is a relatively new strain that infected a few hundred people worldwide so far. It is also believed that that malware is still in development, as, during testing, the commands via the DNS were not reaching the target.
Since Mozart malware is relatively unknown in the cybersecurity world, the first samples were caught in the wild, spreading with the help of malicious PDF attachments that include a malicious link to a .zip file. If executed, it triggers a JavaScript command, which downloads a file calc.exe and places it in the Temp subfolder.
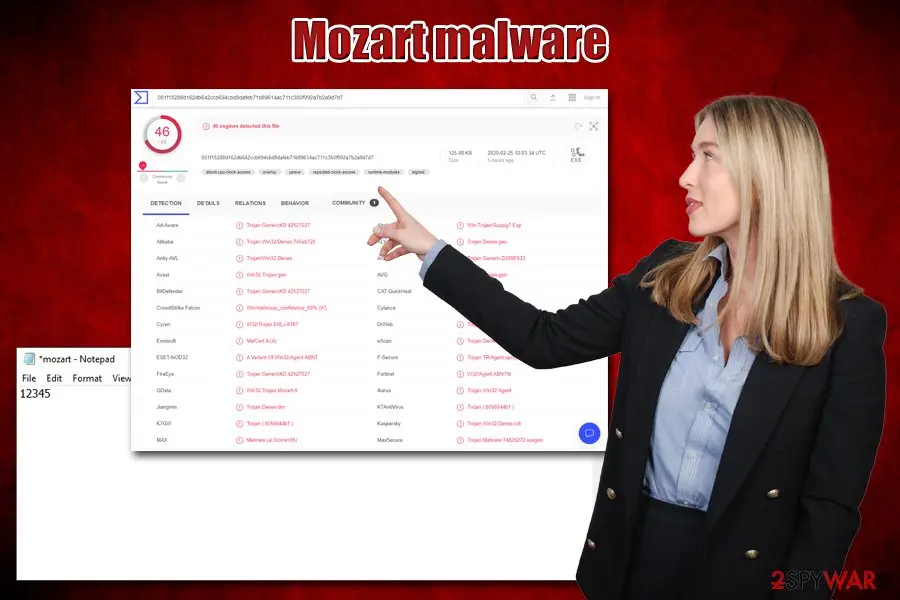
From there, Mozart malware triggers the system infection process, which firstly creates a text file mozart.txt in the same Temporary file folder and inserts "12345" content inside. After that, the Trojan imports several files into the Startup folder, which makes it load every time the Windows system is booted.
Mozart malware is programmed to receive the following seven DNS request tasks, which would allow malware to update itself, allocate memory, check which updates were applied, and other commands:
After the necessary system changes, Mozart malware will continually query the .gettask command, although no response from the DNS server is received. There is also a chance that malicious actors behind the malware are first seeking to create a botnet before issuing Mozart malware with task execution.
While the virus is yet to be armed with malicious commands, we suggest you don't wait and remove Mozart malware from the tour computer as soon as possible. Backdoors can allow the attackers to take over the infected machine eventually, which can result in a variety of negative consequences for the victim, including money loss, other malware infection, data loss, and even identity theft.
To get rid of Mozart virus, perform a full system scan with a reputable anti-malware software that detects the threat. After malware removal, we suggest scanning the machine with to fix the virus damage done, or otherwise, Windows might suffer from various stability issues.
- .getid
- .gettasks
- .gettasksize
- .gettask
- .reporttask
- .reportupdates
- .getupdates
From our report of Feb 2020 · not reviewed since
More from our earlier report on Mozart malware
- Affected system files may cause various stability and performance issues even after malware virus termination (in some cases, users might not be able to operate Windows at all).
How Mozart malware got on your PC
From our report of Feb 2020 · not reviewed since
Emails can be used to transfer all types of information - from informative messages to sophisticated and obfuscated attachments.
As a general rule, threat actors behind malware often employ social engineering techniques in order to make users open the malicious file, triggering the infection chain.
There are several tactics that can be used to comprise a phishing email - these can also be targeted or sent to random users. Typically, botnets are employed to send out spam to hundreds or even thousands of others, infecting even more victims worldwide.
Luckily, implemented security measures within email provider systems scan all emails for malicious indicators, and flag them - place them into the "Junk" or "Spam" folders. In most cases, such emails are not even checked by most, preventing malware from spreading.
However, threat actors are continually working on new and advanced techniques to bypass built-in scanners, so these malicious emails might also end up in your Inbox. At this point, it is up to you whether you will get infected or not - you should learn to recognize malicious email traits.
Thus, never allow a document, such as MS Office file, to run macro commands and also click on links that would automatically download and execute a file. Keep in mind that a single action (namely, a click) can initiate a set of events that will eventually plant malware on your machine. So don't do it.
It is also worth mentioning that scanning such attachments, and links with tools like Virus Total or anti-malware software can save you from malware infection as well - so make sure you have comprehensive security solutions installed on your machine at all times.
How to check the PC for Mozart malware
- File:
calc.exe
How to remove Mozart malware
How to remove Mozart malware and lock the attacker out
Someone may have had remote control of the PC.
Cut the connection first, then remove the trojan and secure your accounts.
Step 1: Remove remote access tools and lock the attacker out
Attackers keep access through remote control tools and extra user accounts. Disconnect the PC from the internet, then remove every remote access program you did not install yourself from the installed apps list in Windows 11 or Windows 10.
Look for a user account you do not know and delete it, and switch off Remote Desktop in Settings > System. Reconnect only for the scan.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 2: Check where calc.exe runs from and stop it
In Task Manager (Ctrl + Shift + Esc) find
calc.exeon Processes, right-click it and choose Open file location before ending anything.Windows' own files live in
C:\Windows\System32; the same name in%AppData%, %Temp% or C:\Users\Public is an impostor. If the folder is wrong, right-click the process again, choose End task and delete the file.If it starts again within seconds, a task or another process restarts it, so run the scan step in Safe Mode. Task Manager works the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 3: Delete scheduled tasks that bring it back
Programs like Mozart malware add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 5: Scan the PC, then run the offline scan
A scan finds the parts of Mozart malware that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
Mozart malware can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Feb 2020 · not reviewed since
Use security software to delete Mozart Trojan from your machine
Just like many other backdoors, Mozart Trojan is targeting Windows systems exclusively and can result in privilege escalation, which means that the attackers could take over your machine completely.
Besides, it may also gain root access to the PC, which would make Mozart malware removal extremely difficult. Without a doubt, such action cannot be executed manually, and an automatic removal tool should be used instead.
Additionally, because Mozart virus uses various methods to disguise itself from anti-malware software, you should access Safe Mode with Networking, as explained below, although this might not always be necessary. Then, perform a full system scan using , , or another reputable tool to remove Mozart malware from your system thoroughly.
[GI=method-1]Access Safe Mode with Networking in case Mozart malware is tampering with your security software:
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed an unfamiliar process called calc.exe in Task Manager, a sign of a program that could read browser data, the clean-up is only half of the work.
The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
Questions about Mozart malware
Is calc.exe a virus?
The name calc.exe is not enough to say. Malware often uses technical-sounding names, and harmless updaters often use odd ones. Check three things:
- the folder the file runs from
- the Digital Signatures tab in its properties
- the program that starts it (Startup apps, Task Scheduler or services)
A signed file from a company whose product you use is almost certainly fine. An unsigned file in a user folder that no installed program explains should be removed, and the PC scanned with Microsoft Defender in offline mode.
calc.exe keeps coming back. What should I do?
A process that returns after you end it has a restart mechanism, and that is a reason to treat calc.exe as unwanted. Check Settings > Apps > Startup, Task Scheduler and the Services list for entries pointing to its folder, and disable them.
Look in Installed apps for anything added the same day and uninstall it. Then delete the folder and run a Microsoft Defender Offline scan, which works before Windows starts and can remove files that are locked or hidden while the system is running.
My antivirus was on. How did a trojan get past it?
Antivirus programs see a file only when it is written or run, and criminals test each new build against popular scanners before release. Detection catches up within hours or days, which is often after the first victims ran it.
Archives with passwords, installers that fetch the malware later, and scripts run through PowerShell make the job harder. That is why behaviour such as downloading cracks or pasting commands matters more than any setting. Keep Windows and Defender updated, and turn on Reputation-based protection in App & browser control.
Should I check my other computers too?
Yes, it takes little time and removes doubt. Mozart malware itself usually stays on one PC, but the download that carried it may have been copied to other computers, shared drives may hold the same installer, and an attacker who had access could have tried saved passwords on other devices.
Run a full scan on every Windows PC in the home or office, check shared folders for the original download, and change Wi-Fi and router passwords if they were stored on the infected machine.
Which malware family is Mozart malware?
That is not known yet. Mozart malware has been reported by people who saw an unfamiliar process called calc.exe in Task Manager, but no sample has been analysed publicly, so security companies have not assigned it to a family. The name you see may be a file or program name chosen by the authors, not a family name.
This does not stop you from removing it: the startup points, the offline scan and the account steps are the same for most families of this type. If Microsoft Defender or another scanner gives the file a detection name, write it down; that name is the best clue to the family and is useful when you report the incident.
How dangerous is Mozart malware?
Treat it as serious until proven otherwise. The visible sign is an unfamiliar process called calc.exe in Task Manager, and programs that behave this way often have more abilities than they show:
- copying passwords
- downloading other malware
- giving remote access
Its family is not known yet, so nobody can say which of these it uses. The good news is that the response is the same in every case and takes about an hour:
- cut the network
- remove the startup entry
- run an offline scan
- change passwords from a clean device
If someone had remote control, a full reset is safer.
Do I need to reinstall Windows to get rid of Mozart malware?
Usually not. A thorough clean-up is enough when the offline scan finds nothing afterwards and you do not see an unfamiliar process called calc.exe in Task Manager again. A reset is the safer choice if an attacker had remote control, if security tools were switched off, or if detections come back after every clean-up.
Windows 11 can reset itself without a USB stick under Settings > System > Recovery > Reset this PC. Copy documents and photos out first and scan the copies. A reset does not change passwords or undo stolen data, so the account steps still apply.
I found AnyDesk or ScreenConnect that I did not install. Is that Mozart malware?
Not necessarily Mozart malware, but it is a warning sign. These are legitimate remote support tools, and criminals use them as ready-made backdoors, especially after tech support scams or fake invoice calls.
If you did not install it and no one you trust set it up, uninstall it, change passwords from a clean device and check your bank account. If someone connected to your PC through it, follow the steps for remote access trojans and consider a Windows reset. Installed apps sorted by date shows when it appeared.
How do I know if my PC has Mozart malware?
Often you do not, which is the point of a trojan. Possible signs are an antivirus alert naming Mozart malware or a generic trojan detection, unknown programs or scheduled tasks, processes with random names in Task Manager, browser extensions you did not add, security settings turned off, slower performance, or account alerts about logins from unknown places.
The reliable check is a full scan followed by Microsoft Defender's offline scan. If you recently ran a crack, a fake installer or a command a website told you to paste, scan even without symptoms.
Will Fortect remove Mozart malware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Mozart malware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Twitter: #Mozart" TLD #Loader & DNS TLD Commands (read October 6, 2026)
- Virus Total: 051f15288d162db642ccb694cbd8dafeb71b89614ac711c350f992a7b2a9d7d7 (read October 6, 2026)
- CSO Online: Social engineering explained: How criminals exploit human behavior (read October 6, 2026)
- Wikipedia: Rootkit (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)