
Msftconnecttest redirect ads: what it is and how to remove it
Msftconnecttest.com redirect is a DNS hijacking attack that redirects you to fake COVID-19 app pages hosting Oski Trojan malware. It spreads via compromised router settings or malware on your device.
Facts checked October 8, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If redirects to msftconnecttest.com keep coming back, a free scan can check extensions, programs and browser settings in one pass.
Do it yourself · free Remove Msftconnecttest redirect ads yourself 3 steps, about 9 minutes, no software needed.
Start the steps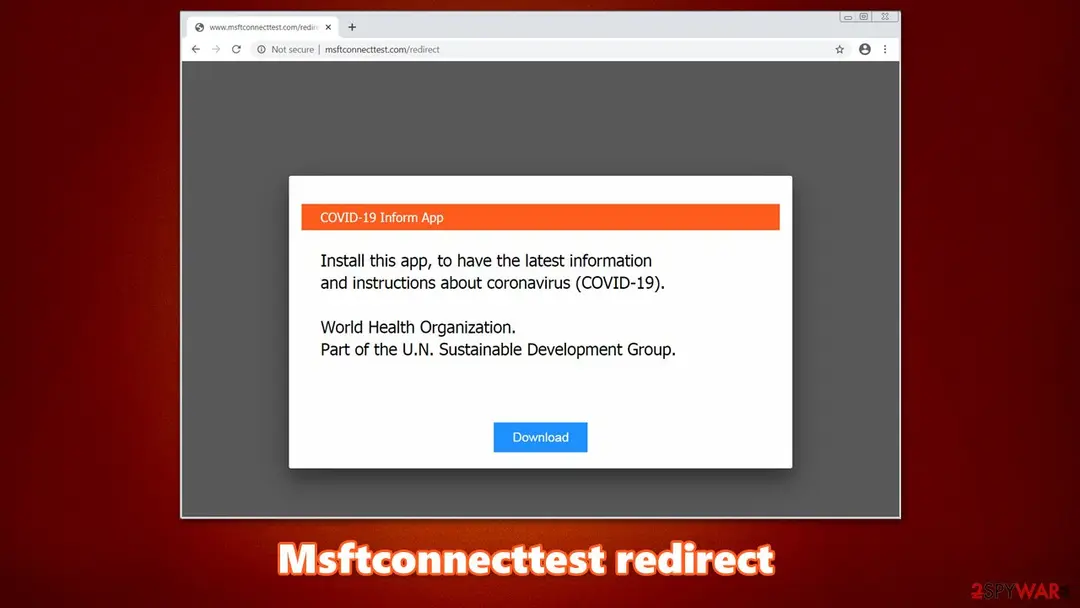
Msftconnecttest redirect ads: summary
| Distribution | The delivery methods of DNS hijacking are unknown, although it is speculated that the attack is performed via weakly protected Remote Desktop (RDP) connections |
|---|---|
| Name | Msftconnecttest redirect |
| Type | Potentially unwanted program/redirect virus/adware |
| Platform | Windows OS |
| Symptoms | Disables access to particular websites; blocks the downloading of some software, e.g., antivirus; changes DNS settings; attempts to install Oski info-stealing Trojan via a fake COVID-19 information app |
| Relations | azureedge.net, 109.234.35.230 and 94.103.82.249 DNS servers, connecttest.txt |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Damage | Not recorded in the old report |
| Evidence | 5 write-ups by security sites; details still limited |
| Domains | msftconnecttest.com |
| Ads shown as | Redirects through ad pages |
| Browsers | Chrome, Edge and Firefox |
| First seen | 27 January 2023 |
| Facts checked | 5 October 2026 |
What the Msftconnecttest redirect ads ads look like
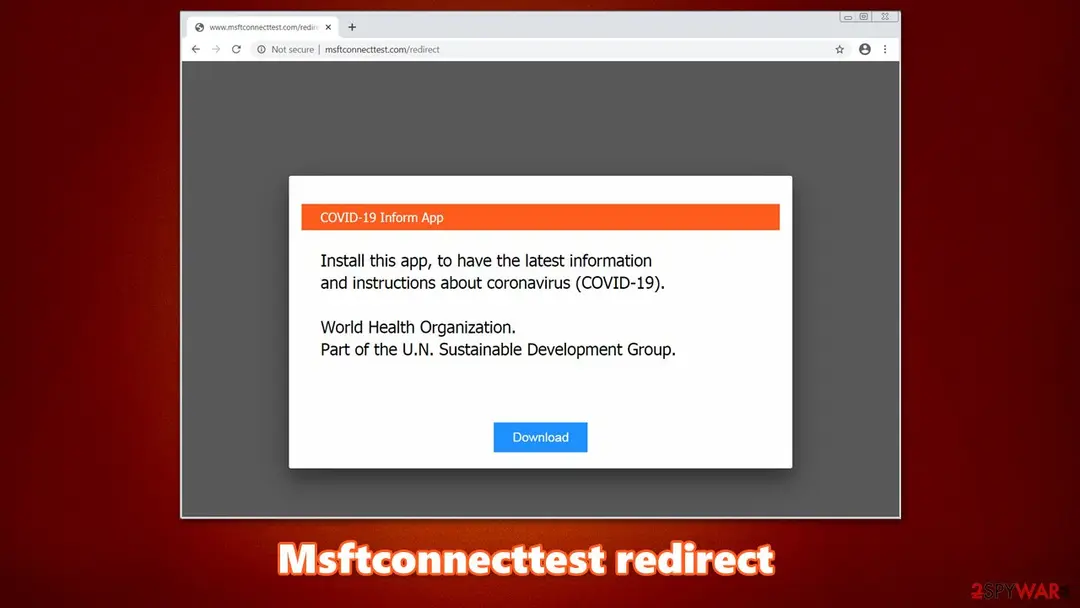
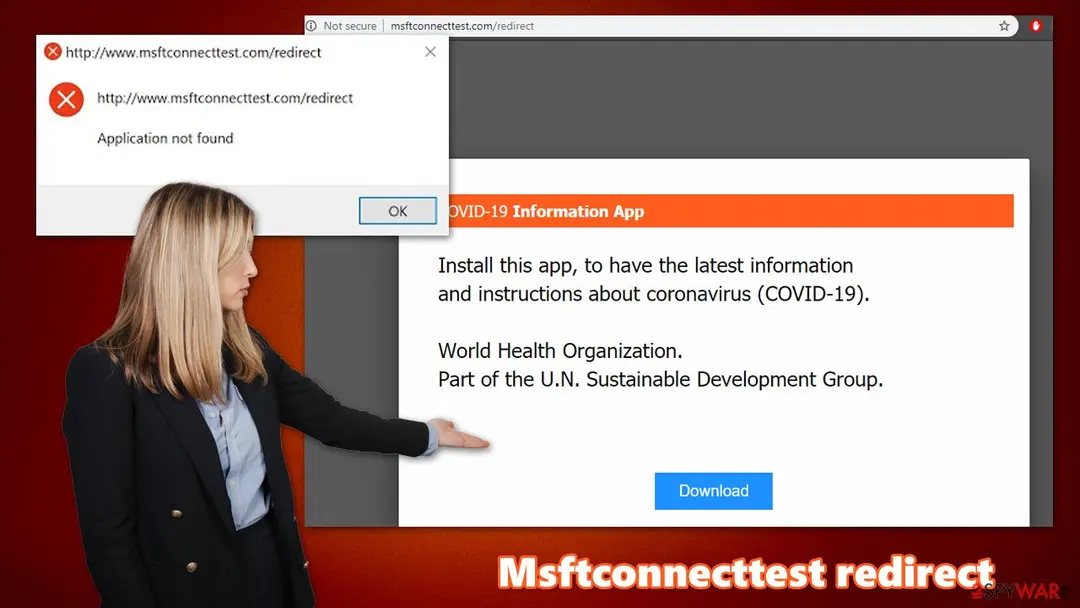
Install this app, to have the latest information and instructions about coronavirus (COVID-19).
Msftconnecttest not working: when Windows says No Internet access
When msftconnecttest is not working, Windows usually shows No Internet access even though pages may still open.
Microsoft Learn explains that Windows sends a small test request to www.msftconnecttest.com/connecttest.txt and expects the text Microsoft Connect Test. If that answer does not arrive, the network icon reports a problem. Apps such as Outlook, Teams and Windows Update rely on the same result.
To test it yourself, open www.msftconnecttest.com/connecttest.txt in a browser. A page with only the words Microsoft Connect Test means the test address works. If something else loads, such as a login page, an ad or a download offer, the network or a program is changing your traffic. A hotel or airport login page is normal; anything else points to the DNS or proxy hijack described above.
If the test page fails, check the proxy settings and the DNS server addresses in Windows and on the router. Microsoft lists an unknown proxy, a wrong DNS server address and a firewall block as common causes. Microsoft also says not to switch off the connection test to hide the warning. In PowerShell, Get-NetConnectionProfile shows Internet when Windows sees a working connection.
Is Msftconnecttest redirect ads dangerous?
From our report of Jan 2023 · not reviewed since
More from our earlier report on Msftconnecttest redirect
- Eliminate the malicious DNS settings by accessing your router administrator's panel or internet settings.
- If you have infected your computer with malware, you should get rid of it and then perform a full system scan with to repair the system damage
Check your browser and PC
- Address:
msftconnecttest.com
How to remove Msftconnecttest redirect ads
How to stop the Msftconnecttest redirect redirects
Work in this order and test a few links after each step, so you know which one was the cause.
Step 1: Check the browser's extensions
Redirects to
msftconnecttest.comon sites that normally behave mean something in the browser is sending you there. In Chrome openchrome://extensions, in Edge edge://extensions, in Firefox the menu > Extensions and themes.Remove every extension you do not remember adding, especially new tab, search, coupon, PDF or video downloader add-ons. The extension pages look the same on Windows 11 and Windows 10.
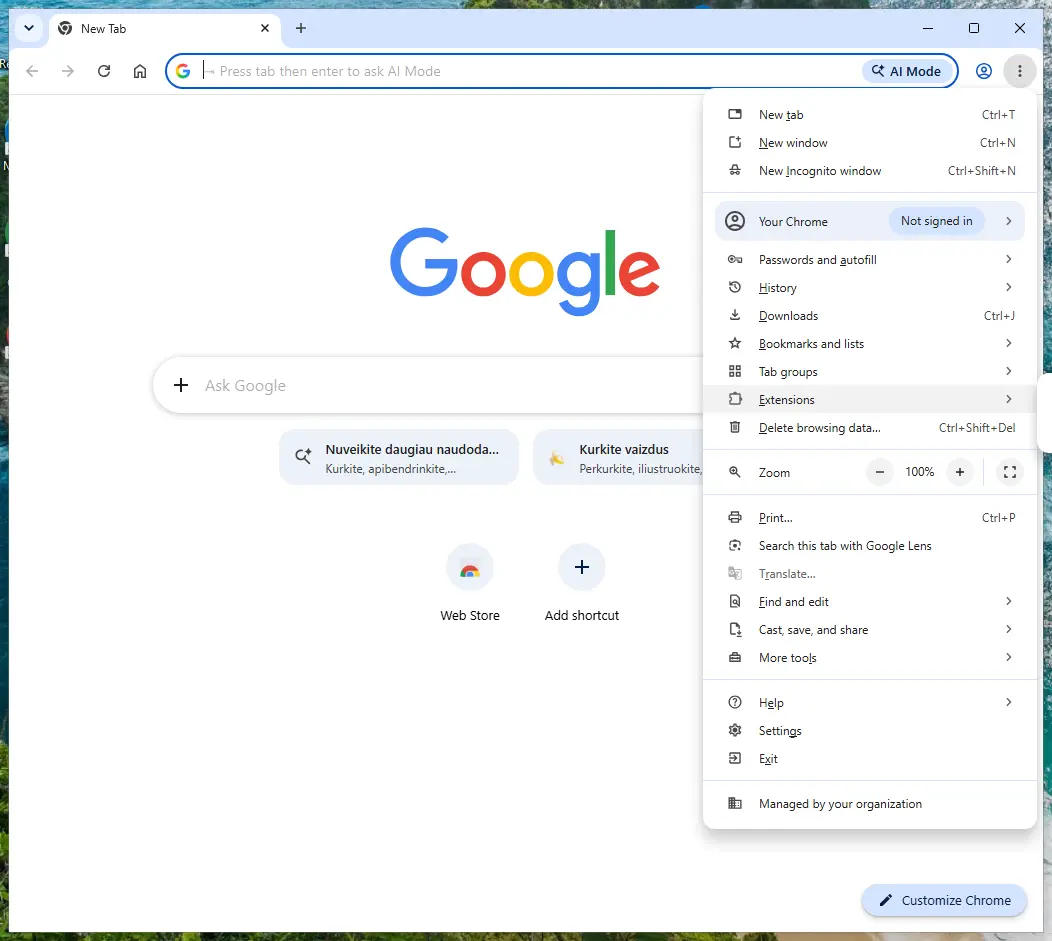
Chrome on Windows 11: More > Extensions > Manage extensions. Full procedure with screenshots: Remove a browser extension
Step 2: Reset the browser if the redirects continue
If
msftconnecttest.comstill opens after the extensions are gone, put the browser's settings back to their defaults. In Chrome open Settings > Reset settings > Restore settings to their original defaults; in Edge Settings > Reset settings; in Firefox Help > More troubleshooting information > Refresh Firefox.Tip: Bookmarks and saved passwords stay, while site permissions, the start page and the search engine are reset.
Redirects that survive a reset in every browser point to a program installed in Windows 11 or Windows 10, so uninstall anything you do not recognise in Settings > Apps > Installed apps.
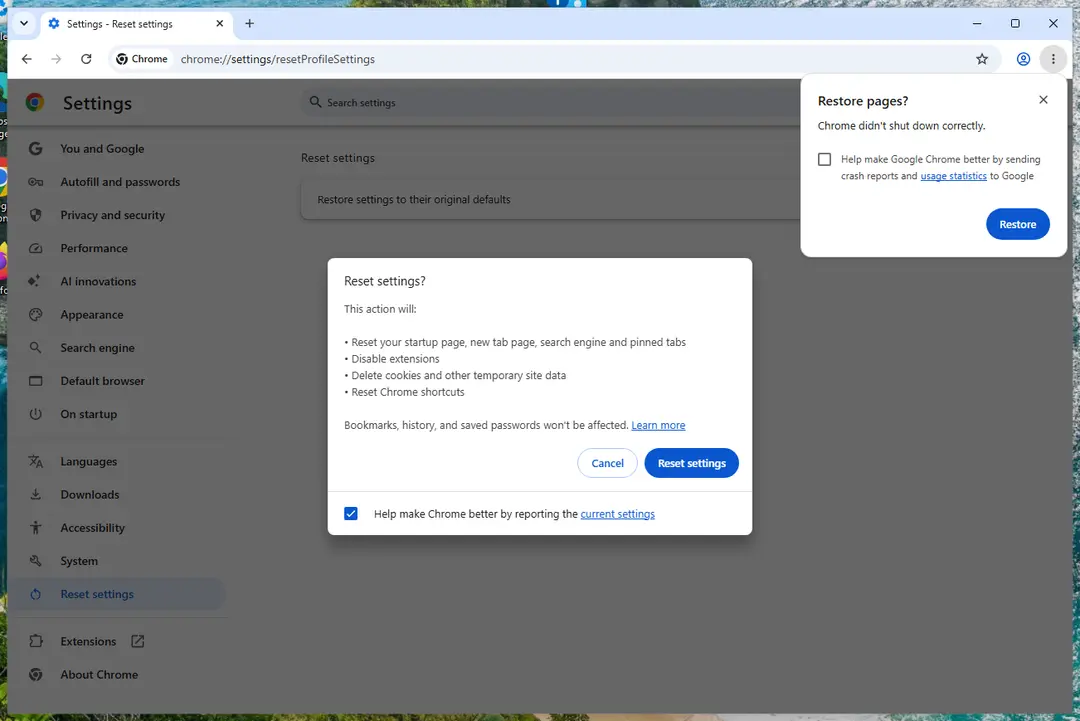
Chrome on Windows 11: Settings > Reset settings. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 3: Scan the PC if you downloaded anything from the ads
If you only saw the notifications and clicked nothing, you can stop before this step. If a notification led you to download or run something, delete that file, then scan Windows.
In Windows Security > Virus & threat protection > Scan options, run a Full scan, then choose Microsoft Defender Antivirus (offline scan) and Scan now. The offline scan restarts the PC and takes about 15 minutes on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
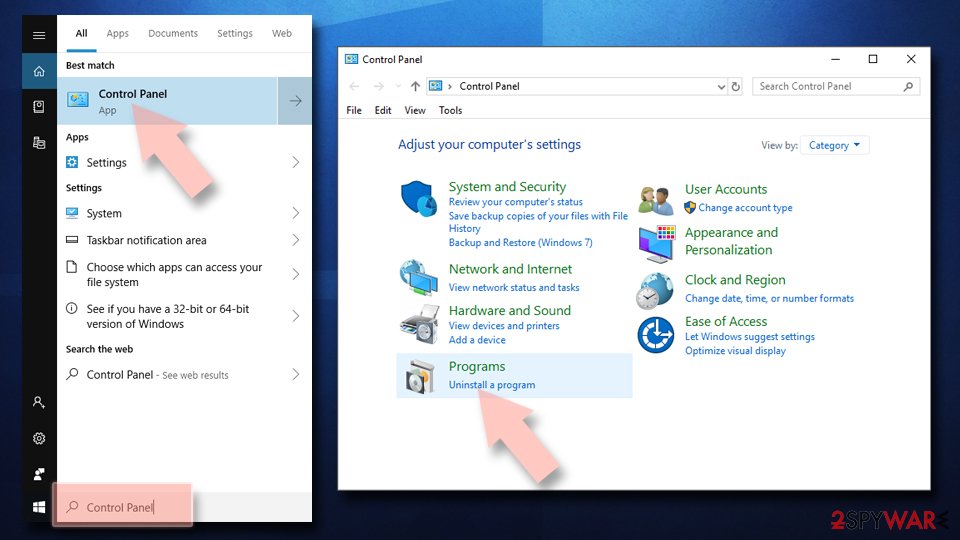
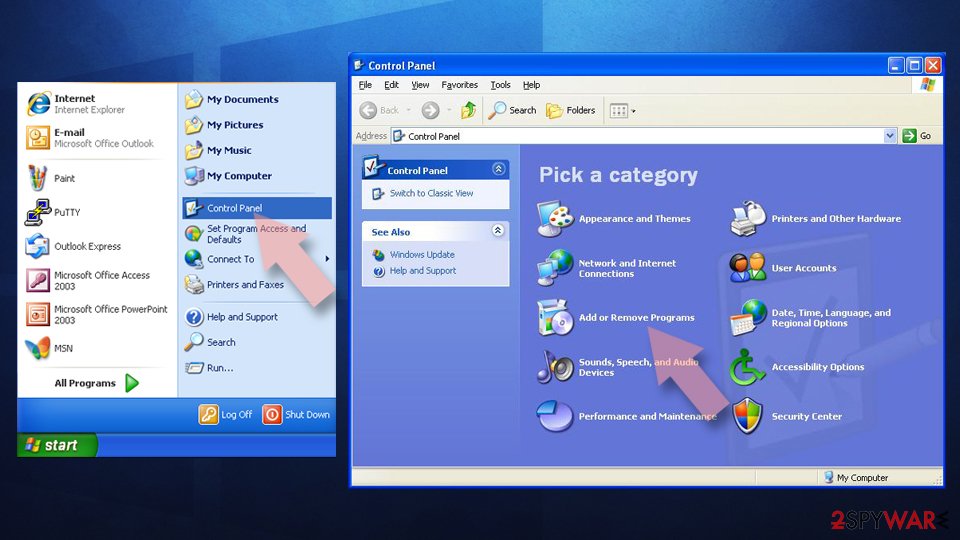
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
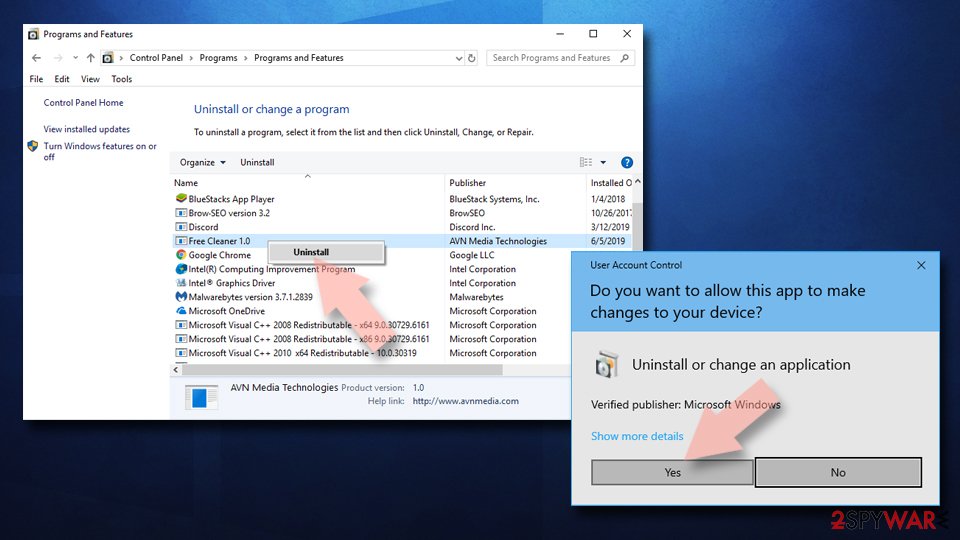
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
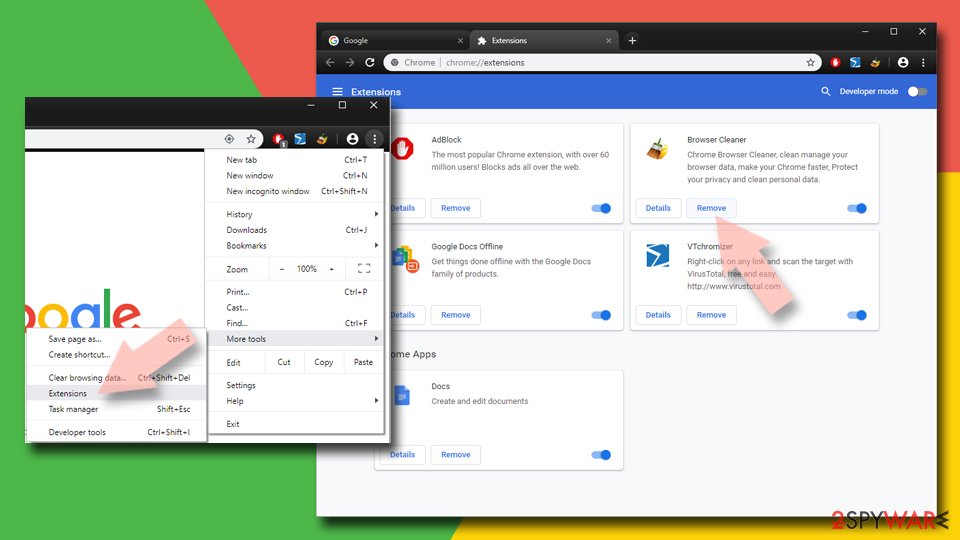
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
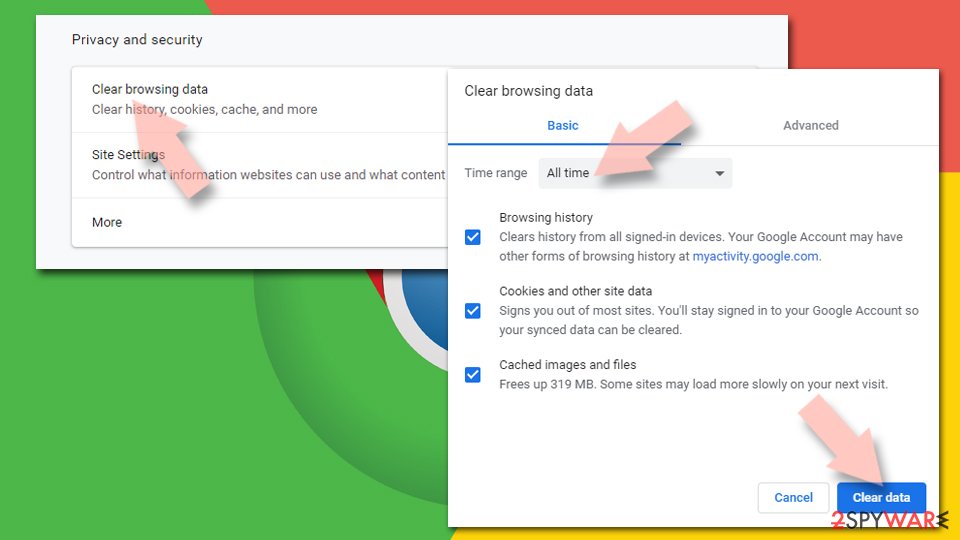
Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
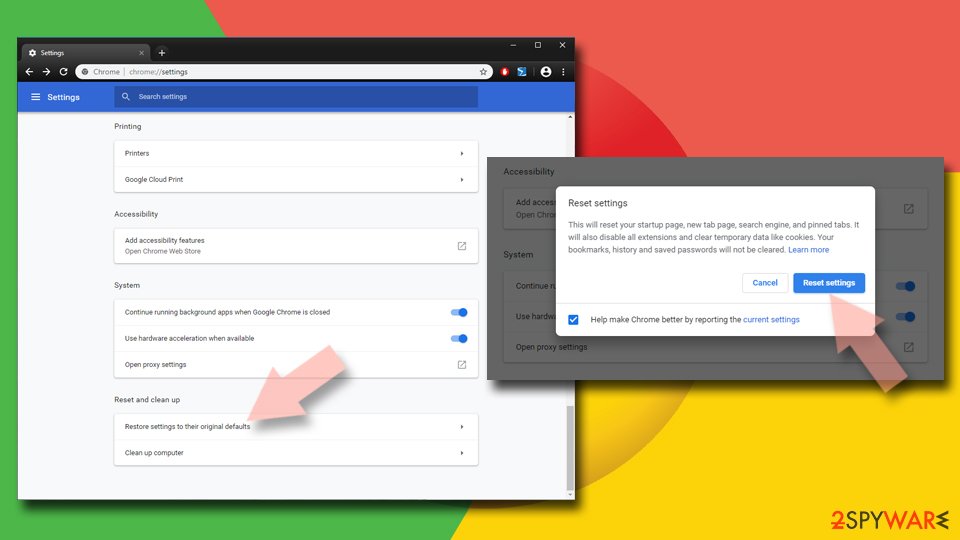
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Microsoft Edge
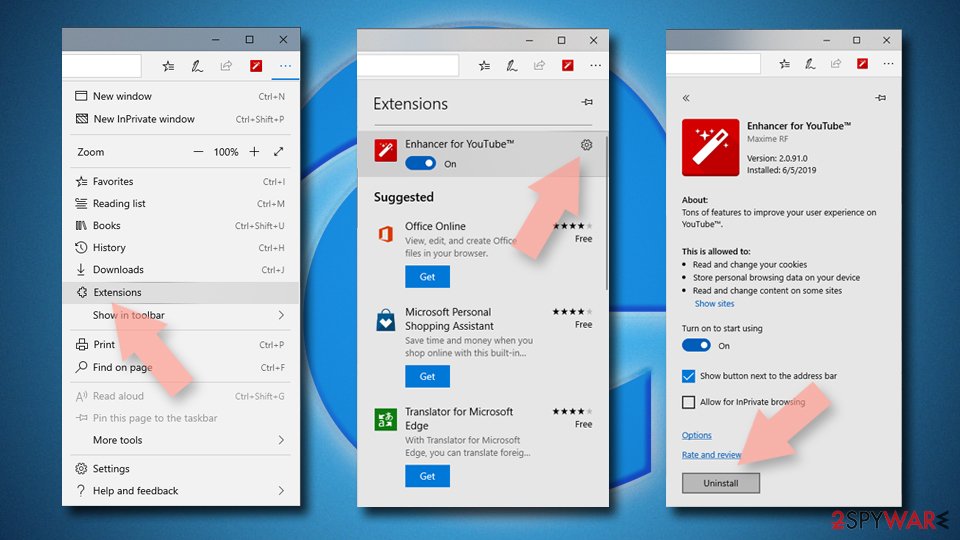
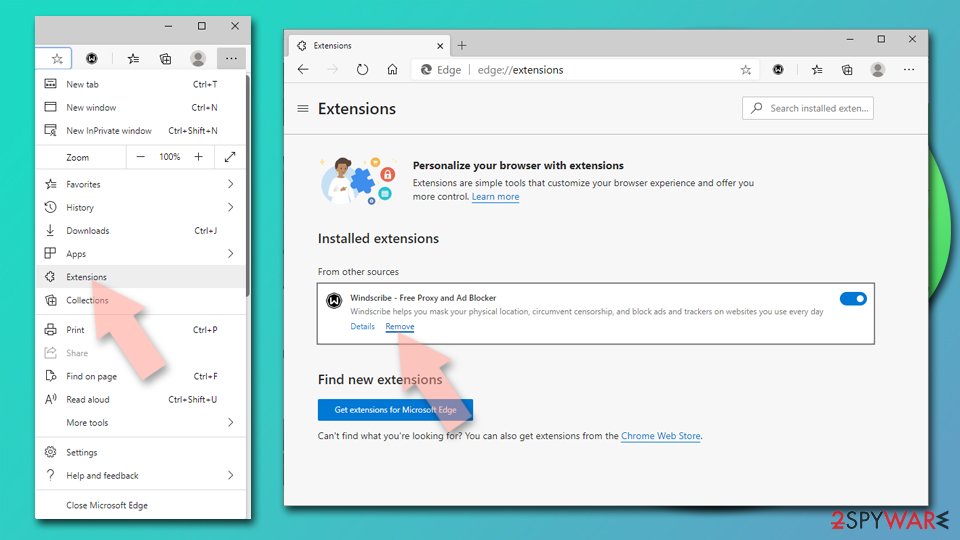
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.
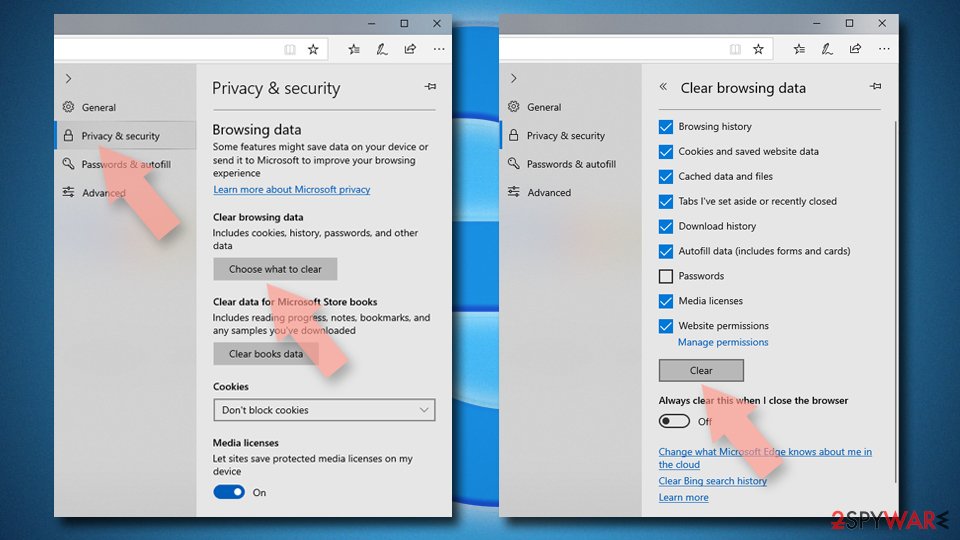
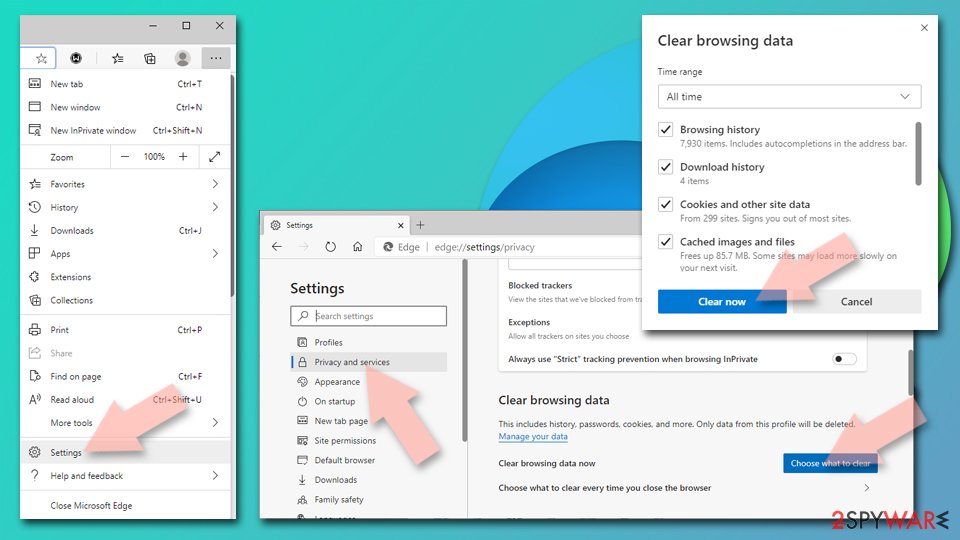
Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.
Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
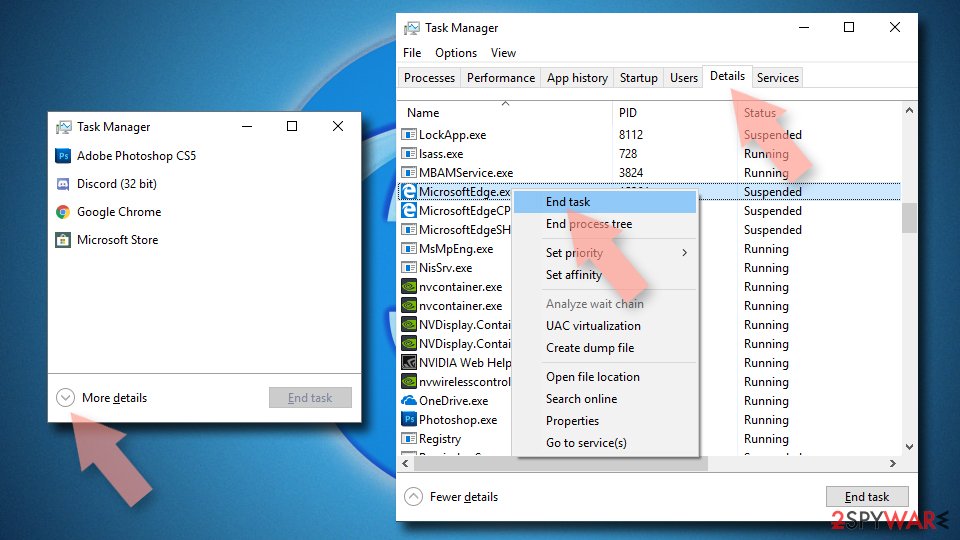
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.
Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
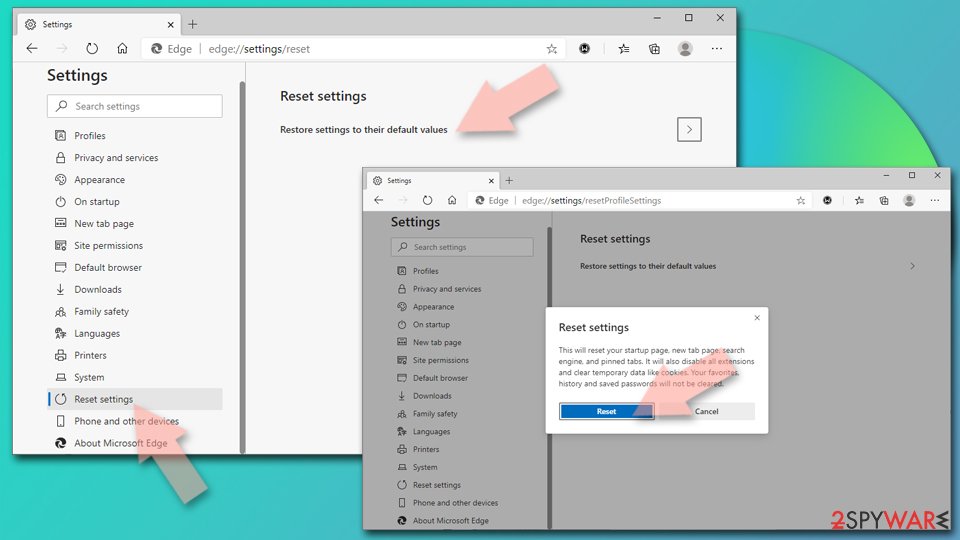
Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.
Remove from Mozilla Firefox (FF)
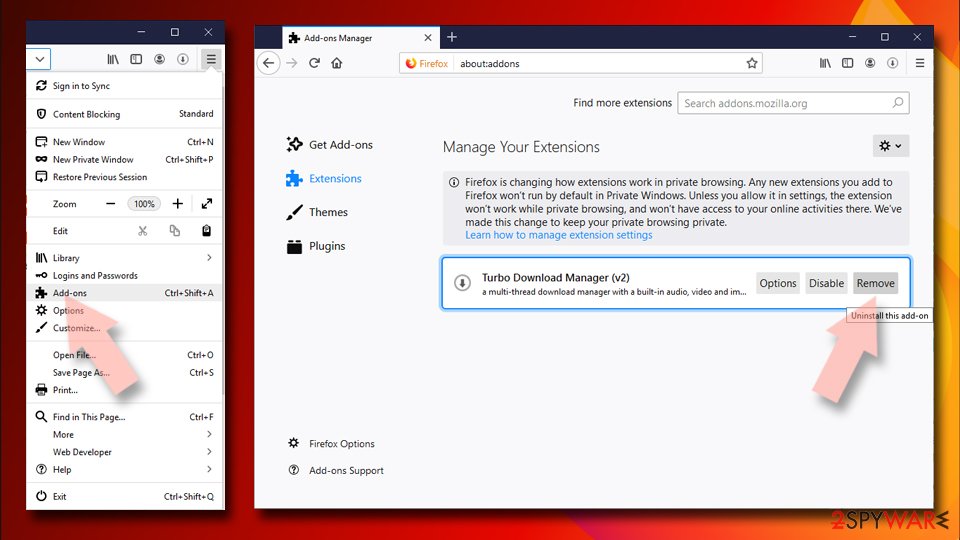
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
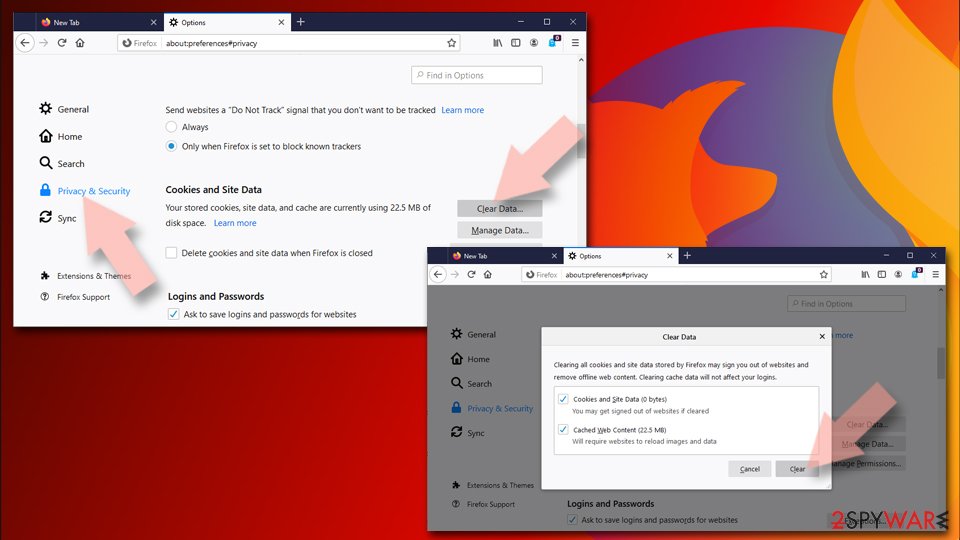
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
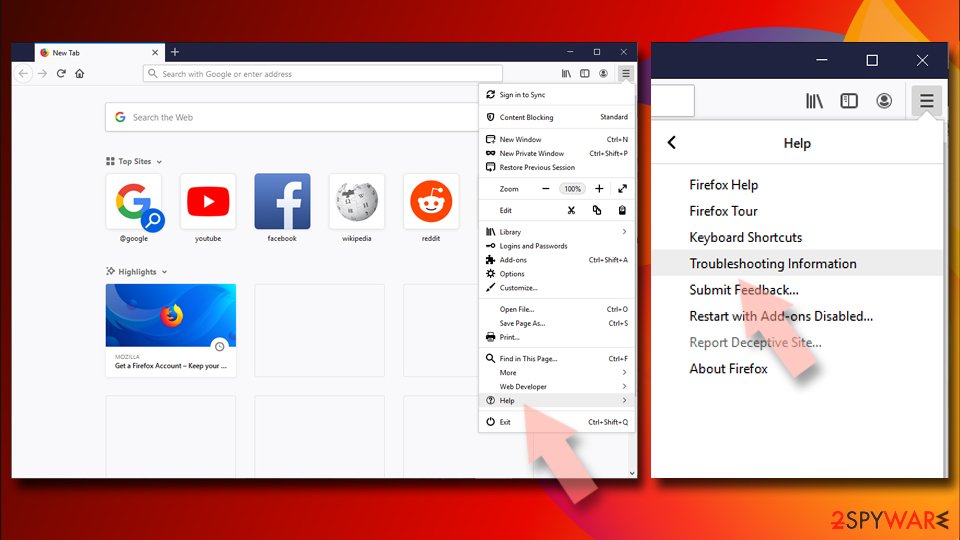
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
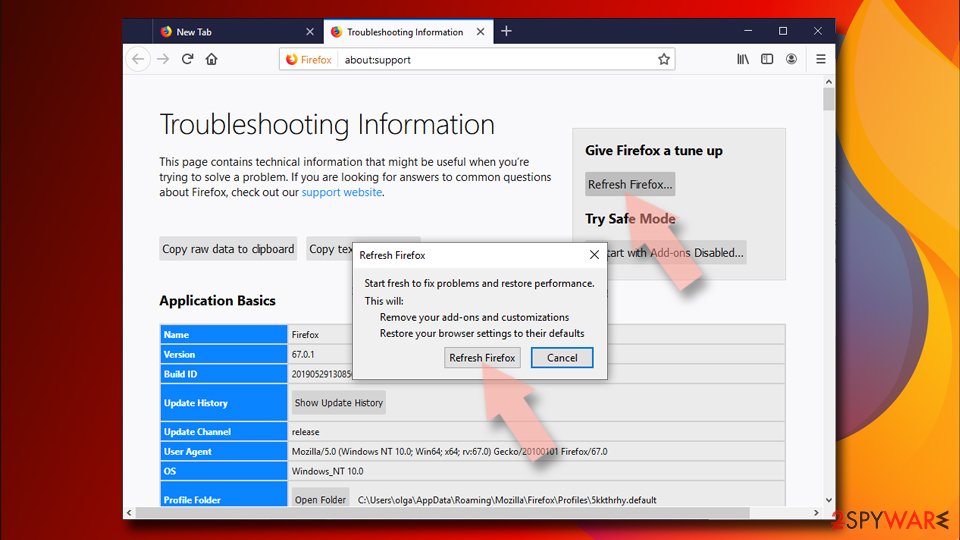
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
From our report of Jan 2023 · not reviewed since
Msftconnecttest redirect: what is it, and how to fix it?
Msftconnecttest redirect is a phenomenon that users are facing for several years now.
According to them, all of a sudden, their Google Chrome, Mozilla Firefox, Safari, MS Edge, or another browser can not correctly connect to the internet, and instead delivers "http://msftconnecttest.com/redirect" error message. Additionally, it was reported that a suspicious connecttest.txt file is attempted to be downloaded. The connectivity issues also prevent users from downloading security software to check the system for malware.
It was reported that the web browsers begin random redirects to msftconnecttest.com, which displays a message asking to download and install an application "COVID-19 Inform App" allegedly developed by the WHO (World Health Organization) to keep up with the coronavirus pandemic.
It is easy to assume that the redirect is not something legitimate and suspicious. It is the case in many situations - the reason is often related to DNS hijacking, where hackers meddle with the router's settings, changing the channels the internet is delivered through. 109.234.35.230 and 94.103.82.249 are known malicious DNS servers used by cybercriminals to deliver fake messages to users.
In other cases, however, Msftconnecttest can relate to legitimate Microsoft domain that regular users should not be able to access, and issues usually arise due to internet connectivity problems or incorrectly set network settings. Regardless of which problem you are dealing with, we provide answers for both situations.
From our report of Jan 2023 · outdated details corrected in October 2026
That is Msftconnecttest.com?
Originally, Msftconnecttest.com is a legitimate domain used by Microsoft to send probes to a computer - it shows the connectivity status.
This is done to check whether the machine is actively using the internet or not. If the server receives a failed request via the "Microsoft Connect Test," it warns users about connection problems.
However, those with the suspicious redirect problem will not be rerouted via the official Microsoft IP address but one that is under the attacker's control. As a result, users see a completely different landing address that can be configured by hackers. In some cases,
In 2023, there were no exact details about how attackers managed to gain access to users' routers. However, there have been several reports from the infected users that they did have a Remote Desktop connection open. This way, the attackers can scan the internet and access the router or computer via the default port. Thus, to mitigate this attack, you should never leave your RDP visible.
Those who are affected by the Msftconnecttest redirect hijack will not see the official MSN.com or any other website for that matter. Instead, they will be shown a suspicious notification that reads:
It is not a surprise that this scam is not the only one that attempts to push malware through fake emails, ads, and redirects, which allegedly provides information on the coronavirus pandemic situation. Malicious actors want to abuse the concerns about the global crisis - ransomware attacks have plagued the health sector, despite the increasing workloads.
Those who get tricked by this message and downloads the alleged COVID-19 app, instead infect their machines with Oski Trojan. This malware can steal a variety of information once installed, including browser cookies, login credentials, F2A databases, text files, crypto wallets, and more.
As a result, the infected users can suffer serious privacy issues to the point where they could lose their identity. Therefore, it is important to stop the redirect and never download anything offered.
In case malware was indeed installed, Msftconnecttest redirect removal should be first performed with powerful anti-malware, such as or . Since a Trojan infection can seriously impact system files, resulting in crashes and other stability issues, experts also recommend using to fix virus damage.
From our report of Jan 2023 · not reviewed since
DNS hijacking - a rather rare but dangerous practice
DNS hijacking is something that does not come along often, although tools like DNS Unlocker has caused major issues to users in the past.
DNS, or a Domain Name System, is users to convert IP addresses into domain names - it would not be possible to access any website by typing in an URL without it. In other words, you would have to know the IP address of every website to visit it (a real pain, indeed).
DNS address can be provided by your ISP or set to come from another provider, such as Google. By using different DNS, you can bypass certain restrictions. On the contrary, cybercriminals might use this practice in order to restrict their internet access, deliver intrusive advertisements, or redirect them to malware-laden websites.
In most cases, the malware installed on the computer behind users' backs is the culprit of unsolicited changes made to DNS servers. Nonetheless, the attackers can access router settings via other channels, such as RDP or unprotected WiFi connection.
Thus, be careful with potentially unwanted programs, as they might change DNS settings without permission. When installing new apps/freeware from third parties, always pick Advanced/Custom installation settings when prompted, decline all the offers, read the fine print, and remove all the ticks from pre-checked checkboxes.
From our report of Jan 2023 · not reviewed since
Deal with suspicious redirects
Msftconnecttest redirect removal is necessary not only for the normal operation of the computer but also for your own safety.
There are several steps that you can take to do that, although the most important thing is to eliminate the Oski Trojan if such was installed on your system. In case you experience crashes, errors, and other Windows issues, you can employ to fix them automatically.
Once you are sure that the malware is eliminated and your computer is clean, you should then remove Msftconnecttest redirect problems. First of all, you need to ensure that you delete the DNS settings applied by the attackers.
To do that, you can either reset your network components or change the DNS manually (alternatively, you can access your router's Administrator's panel) and change the settings from there. Here's how to do that:
Once you change the DNS settings, you should reboot all your devices connected to the network, including gaming consoles, laptops, tablets, phones, etc. Finally, you should reset all the installed web browsers, change all the passwords for all your accounts, employ a secure password-managing app, and enable two-factor authentication where possible.
Other ways to fix the issue that could be useful if your DNS was already correct and no proxy was set up before:
- Right-click on Start and select Settings
- Go to Network & Internet and select Ethernet on the left
- On the right, pick Change adapter options
- Right-click on your connection and select Properties
- Select Internet Protocol Version 4 (TCP/IPv4) and pick Properties
- Check Obtain DNS server automatically and click OK.
- Check your network settings on your device and ensure that the correct network is selected and that the settings are correct.
- Disconnect and reconnect to your network.
- Restart your router or modem.
- If the problem persists, contact your internet service provider or a technical support representative for assistance in resolving the issue.
Questions about Msftconnecttest redirect ads
What is msftconnecttest.com?
Msftconnecttest.com is a legitimate domain originally used by Microsoft to send connectivity probes to your computer. When your system accesses this domain, Microsoft's servers receive a response indicating whether your internet connection is active. The legitimate purpose is to detect and alert you to connectivity problems.
However, hackers have hijacked this domain through DNS poisoning attacks. They redirect msftconnecttest.com requests to malicious IP addresses (like 109.234.35.230 or 94.103.82.249) under their control. Users are shown fake COVID-19 app installation pages or other malicious content instead of legitimate connectivity checks.
Is the COVID-19 app offer real?
No. The "COVID-19 Information App" offered on fake msftconnecttest pages is a scam designed to trick you into downloading malware. The pages falsely claim the app comes from the World Health Organization (WHO) and provides coronavirus information. In reality, downloading and installing the app infects you with Oski Trojan malware.
Oski steals passwords, login credentials, cryptocurrency wallet information, browser cookies, and F2A authentication databases. The WHO and legitimate organizations never distribute apps through malicious redirects. If you want official COVID-19 information, visit official government or WHO websites directly.
How did I get the msftconnecttest redirect?
Your router or computer DNS settings have been hijacked through DNS poisoning. Attackers typically gain access via weakly protected Remote Desktop (RDP) connections left open on your network. Once inside, they modify your router's DNS settings to redirect all requests to msftconnecttest.com toward malicious servers.
Some users had RDP connections visible on the internet using default ports, making it easy for attackers to scan and access their systems. In rare cases, malware on your computer changes DNS settings directly. Your internet service provider's DNS may also be compromised in widespread attacks affecting multiple users.
What can the attacker do with access to my router?
DNS hijacking allows attackers to redirect any website request to malicious pages they control. You cannot safely access any website because even legitimate addresses could route to fake login pages or malware sites. Attackers can block your access to antivirus websites, making it difficult to download security tools and clean your system.
They can intercept your browsing traffic, capturing passwords and personal information. Remote access to your router lets them monitor all device activity on your network. In worst cases, they use the compromised network as a launching point for attacks against other systems, making your router an accomplice in cybercrime.
How do I know if I have this problem?
You have a DNS hijacking problem if accessing any website redirects you to msftconnecttest.com with a suspicious COVID-19 app offer, or if you cannot access any websites normally. Your browser may show error messages about connection failures even though your internet connection works. A suspicious file called connecttest.txt may be automatically downloaded.
You might experience intermittent connectivity or inability to reach certain sites while others load. Run the steps below to check your DNS settings. If your computer's DNS settings are correct but the problem persists, your router's DNS has been hijacked.
What is DNS and why does hijacking matter?
DNS (Domain Name System) translates website addresses like google.com into IP addresses that your computer actually uses to connect. Without DNS, you would need to memorize every IP address to visit websites. By hijacking DNS, attackers can make typing google.com connect you to a fake website instead, stealing your login credentials.
They can block access to security websites so you cannot download removal tools. DNS hijacking is more dangerous than malware because it compromises everything you do online at the network level. Even if your computer is clean, the hijacked DNS still redirects all your traffic to attacker-controlled pages.
How do I fix the DNS hijacking?
Reset your DNS settings by right-clicking Start, selecting Settings, going to Network & Internet, selecting Ethernet on the left, clicking Change adapter options, right-clicking your connection, selecting Properties, choosing Internet Protocol Version 4 (TCP/IPv4), clicking Properties, and checking Obtain DNS server automatically. Click OK and reboot.
Alternatively, access your router's administrator panel directly (typically 192.168.1.1 in your browser), log in with admin credentials, and reset the DNS settings to automatic or your ISP's default DNS servers. If you do not know your admin password, perform a factory reset on your router. After changing DNS settings, reboot all your devices connected to the network.
What if I downloaded the COVID-19 app and installed it?
Scan your entire system immediately with reputable anti-malware software to detect and remove Oski Trojan and any other malware installed. Download the latest version of security tools from a clean device if necessary. Run a full system scan and allow the tool to remove all detected threats.
Change all your passwords for every online account, especially email, banking, and social media, because the malware may have stolen them. Monitor your bank and credit accounts for unauthorized transactions. Consider placing a fraud alert with credit bureaus.
Enable two-factor authentication on all important accounts. Check your router password and wireless network settings to ensure attackers did not modify them. Replace your RDP password if you have Remote Desktop enabled.
Will Fortect remove Msftconnecttest redirect?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Msftconnecttest redirect, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Reddit: msftconnecttest virus? (read October 5, 2026)
- BankInfoSecurity: Fresh COVID-19 Phishing Scams Try to Spread Malware: Report (read October 5, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)
- Microsoft Learn: Network Connection Status Indicator (NCSI) troubleshooting guidance (read October 8, 2026)