
OpenSea email scam: how to spot it and what to do
OpenSea email scam is a phishing campaign targeting NFT marketplace users with fake migration notices claiming urgent listing expiration. Victims lose millions to credential theft and account takeovers.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Do it yourself · free Remove OpenSea email scam yourself 4 steps, about 12 minutes, no software needed.
Start the steps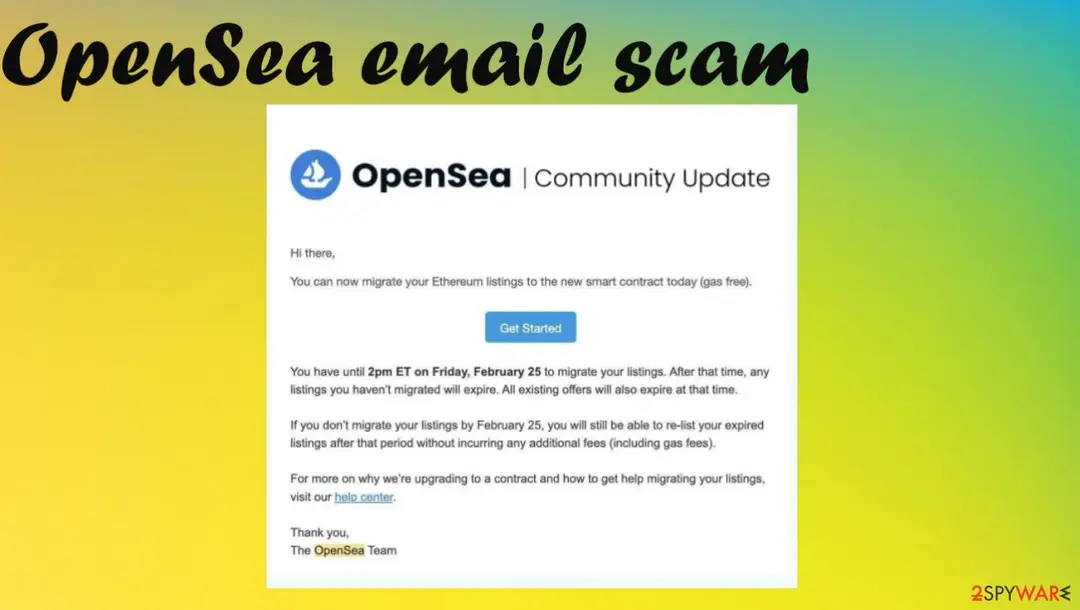
OpenSea email scam: summary
| Distribution | The email appears in boxes for users and randomly chosen inboxes due to the deceptive pop-ups, and other phishing methods. Breaches can reveal details like this later used in scam campaigns |
|---|---|
| Name | OpenSea email scam |
| Type | Phishing scam campaign, fraud |
| Claims | Users must migrate their listings to avoid additional fees due to expiration. The email states that this is the official notification from OpenSea |
| Issues | The email leads to unauthorized purchases and fund transactions, illegal access to the computer, and financial losses |
| Danger | The successful campaign ends with financial losses or hacked accounts |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Symptoms | A phishing e-mail asking you to sign in |
|---|---|
| Evidence | 4 write-ups by security sites; details still limited |
| Arrives as | |
| Pretends to be | A well-known company |
| Claim | Your account needs urgent attention |
| Asks for | Your password |
| First seen | 25 April 2022 |
| Facts checked | 5 October 2026 |
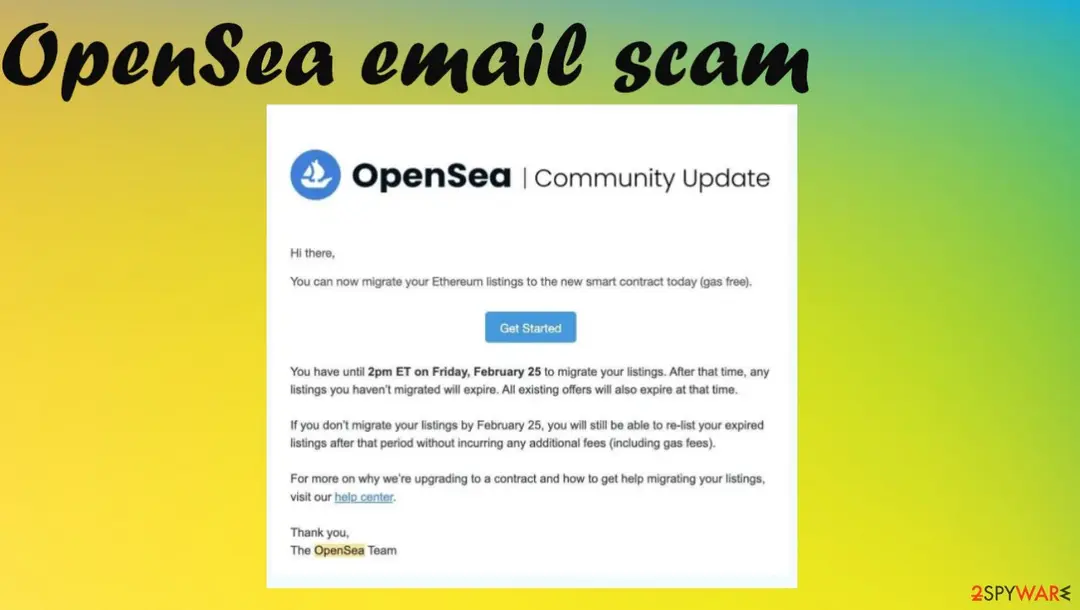
What the OpenSea email scam e-mail looks like
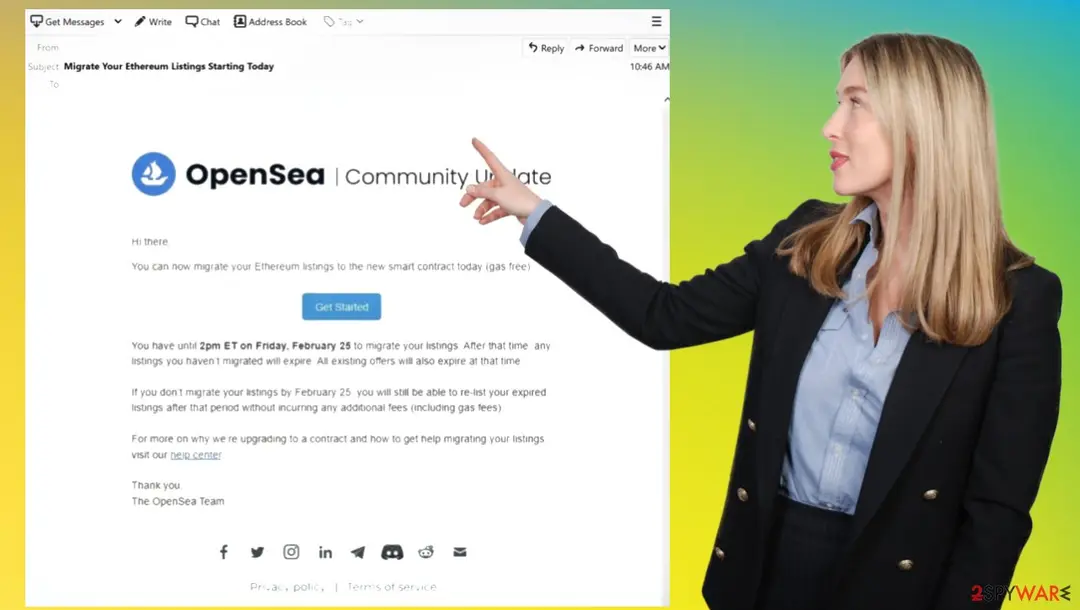
Subject: Migrate Your Ethereum Listings Starting Today
OpenSea | Community Update
Hi there,
You can now migrate your Ethereum listings to the new smart contract today (gas free).
You have until 2 pm ET on Friday, February 25 to migrate your listings. After that time, any listings you haven't migrated will expire. All existing offers will also expire at that time.
If you don't migrate your listings by February 25, you will still be able to re-list your expired listings after that period without incurring any additional fees (including gas fees).
For more on why we're upgrading to a contract and how to get help migrating your listings, visit our help center.
Thank you,
The OpenSea Team
How to tell the OpenSea email scam e-mail is fake
From our report of Apr 2022 · not reviewed since
- Threats need to be removed with anti-malware apps and these emails should be ignored to avoid issues with security
- Try running the so the system issues get fixed
Is OpenSea email scam dangerous? What the senders want
From our report of Apr 2022 · not reviewed since
OpenSea email scam is a phishing campaign that involves false claims about the NFT marketplace
OpenSea email scam is a malicious campaign that relies on fake letters that try to trick people into disclosing account details and credentials.
This is the phishing campaign that targets account in the NFT marketplace. These emails have lures that claim users need to move their listings to avoid the expiration fees. People are tricked into revealing their login information this way.
The particular theme for these phishing spam has already swindled details of various accounts and managed to cause losses of millions for the particular OpenSea users. OpenSea email scam emails can have subjects like "Migrate Your Ethereum Listings Starting Today" and other lines with false claims, so users reveal various details that later get used to gather funds from real accounts of people to wallets run by cybercriminals.
These issues started back in February and campaigns still can occur in your email box. Those subject lines are particularly misleading and deceptive, so more people fall for the trick and reveal needed details from criminals. Try to avoid any interaction with emails from questionable sources and even those with legitimate and relevant themes or mentions of the real companies and platforms.
The email reads:
From our report of Apr 2022 · not reviewed since
More details about the phishing email scam
OpenSea email scam aims to extract user account credentials and steal NFTs, and funds stored on the marketplace accounts, The victim can understand what happens only after the losses.
Any suspected victims are recommended to change the passwords of all possibly exposed accounts. Experts note that these scams go around often.
OpenSea email scam letters can include various details about the platform and similar services to keep the legitimate image. These letters encourage people to migrate their Ethereum listings to a new smart contract because these listings can be expired and people might lose them or get huge fees for the expiration.
These platforms and cryptocurrency is popular and these facts encouraged scammers to alter their methods to these popular things that can lure people. OpenSea emails in this scam are in no way related to the marketplace or any legitimate services involving NFTs or cryptocurrency.
These campaigns aim to gather user account credentials and steal funds, and NFTs stored on that accounts, so these are financial criminals. Revealing your user account credentials can lead to additional hacking and losses, so you should ignore any suspicious emails and make sure to not click on anything suspicious.
If you open OpenSea email scam message or another questionable email, make sure to run or on the machine to ensure that any threats that managed to get dropped on the system get detected and removed. These campaigns get advanced and more dangerous.
From our report of Apr 2022 · not reviewed since
Types of common email scam campaigns
OpenSea email scam is a phishing email campaign that relies on deceptive emails that should trick users into giving away their sensitive or private details.
These attacks send emails with fake logos or information that imitates the legitimate company or services. These emails create urgency for the interaction and lead victims to potential risk.
Such messages lead to clicking on a link and entering details in survey or login forms by displaying identical or legitimate-looking content, so people believe that the transaction is legitimate. These emails can also have various attachments of files with malicious files and release malware to the machine besides phishing people. These are malicious emails.
Potential victims can also be lured into interaction with similar campaigns to OpenSea emails. That is mostly done with questionable materials or even sextortion email help, clickbait contents, themes related to celebrities, giveaways, prizes, and lotteries. There are various methods by that criminals aim to get a profit.
From our report of Apr 2022 · not reviewed since
Can there be malware on the machine?
OpenSea email scam is not a virus related to particular potentially unwanted programs or malware.
However, these emails can drop various files that lead to issues with the security of the machine. Your device might get infected if you click on a link or download a file from the spam email.
Such infections can be silent or just affect the browsing experience. There are various threats using emails to spread around, so you should scan the machine fully with anti-malware tools to check the security state of the machine. It helps to clean the threats and potentially unwanted or dangerous files.
Social engineering tactics and fraud issues stem from these OpenSea email scam messages, but there are malicious programs that can find their way on your machine and alter settings, damaging the processes or programs. The system should be checked more frequently and these infiltrations can be avoided this way. You find the guide below that shows how to clear browsers and the machine.
What to do after the OpenSea email scam e-mail
If you only received the message and clicked nothing, step 3 is all you need.
If you clicked the link or typed anything on the page it opened, do every step, starting with the password.
Step 1: Change the password you typed on the fake page
If you entered a password after clicking the link in the OpenSea email scam message, treat that account as known to the sender.
Open the provider's real site by typing its address yourself, not through any link in the e-mail, and change the password there. Choose a new one you have never used before, and change it on every other account that shared the old one.
Then use the option to sign out of all other sessions or devices, if the provider has one. This works the same in any browser on Windows 11 and Windows 10.
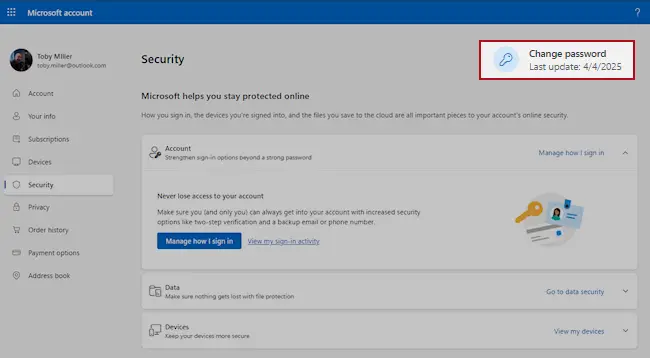
Microsoft account, Security page (account.microsoft.com/security): Change password. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Turn on two-step verification
Two-step verification asks for a code from your phone or an authenticator app whenever someone signs in from a new device. A stolen password alone is then not enough to open the mailbox.
Turn it on in the security settings of the e-mail account first, then for the bank, shop and social accounts that send their reset links to that address.
While you are there, check the recovery e-mail and phone number and the forwarding rules, which attackers sometimes change to keep access. The settings pages look the same on Windows 11 and Windows 10.
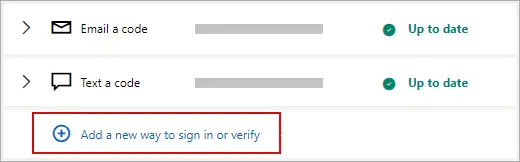
Microsoft account: Manage how I sign in, where two-step verification and the sign-in methods are. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Report the e-mail and delete it
Report the message instead of only deleting it. In Outlook choose Report > Report phishing, in Gmail the three-dot menu > Report phishing; the provider then blocks the same message for other people.
Do not reply and do not click anything else in it. On a work account, forward it to your IT team as an attachment first. Web mail and the mail apps on Windows 11 and Windows 10 offer the same options.
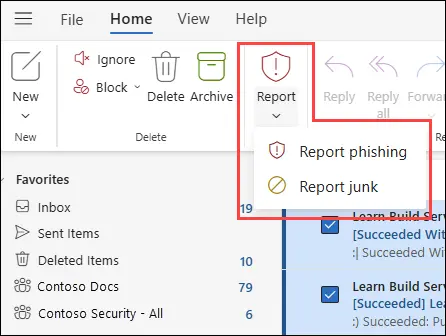
New Outlook for Windows and Outlook on the web: Report > Report phishing. Full procedure with screenshots: Report a phishing e-mail
Step 4: Scan the PC if you opened a file from the message
A page that only asked for a password installs nothing, so most readers can skip this step.
If the OpenSea email scam e-mail or the page it opened made you download or open a file, delete it and run a full scan, then a Microsoft Defender Offline scan.
In Windows 11 and Windows 10 open Windows Security > Virus & threat protection > Scan options, select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts and the scan takes about 15 minutes, so save your work first.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
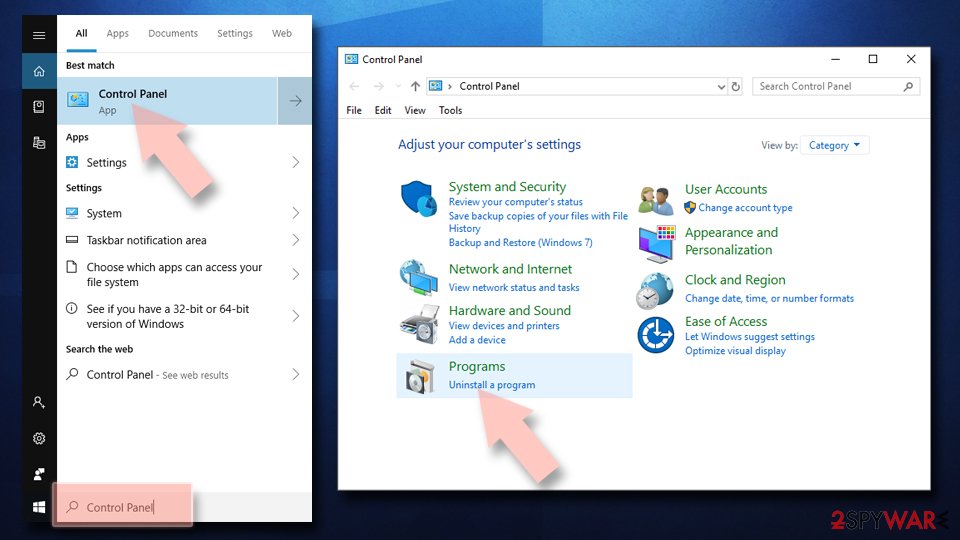
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
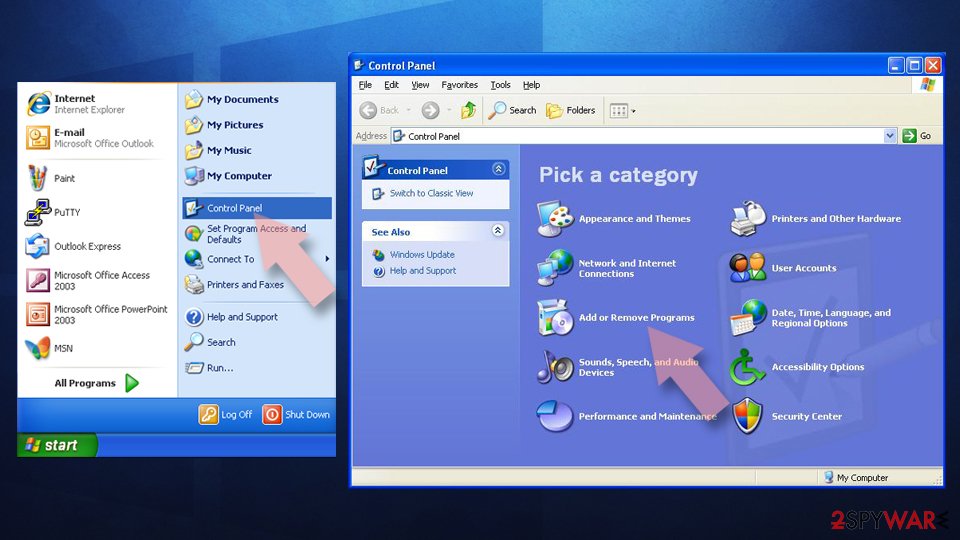
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
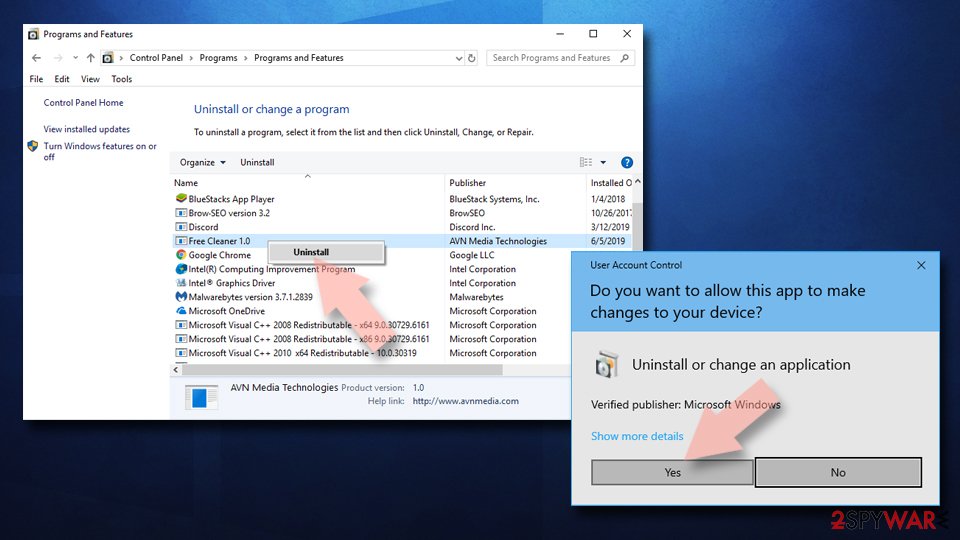
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
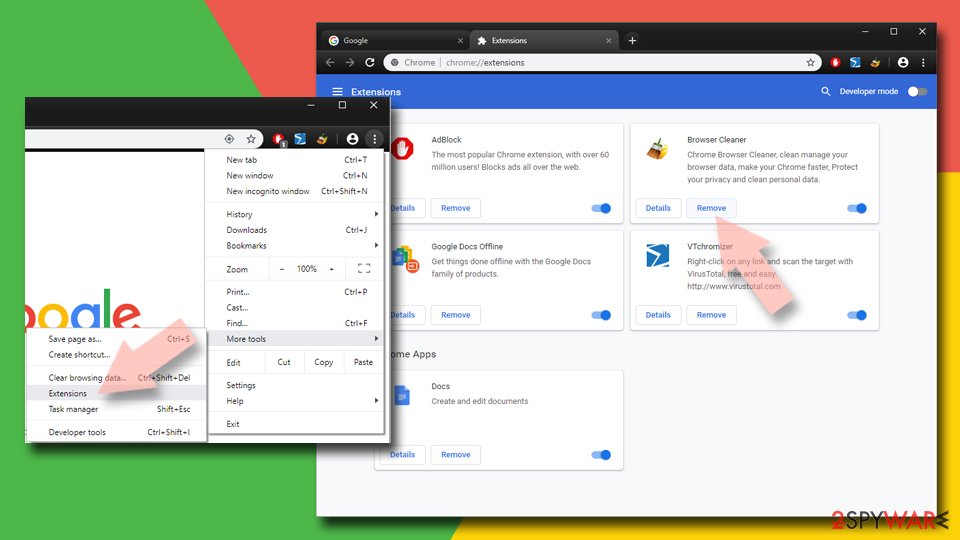
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
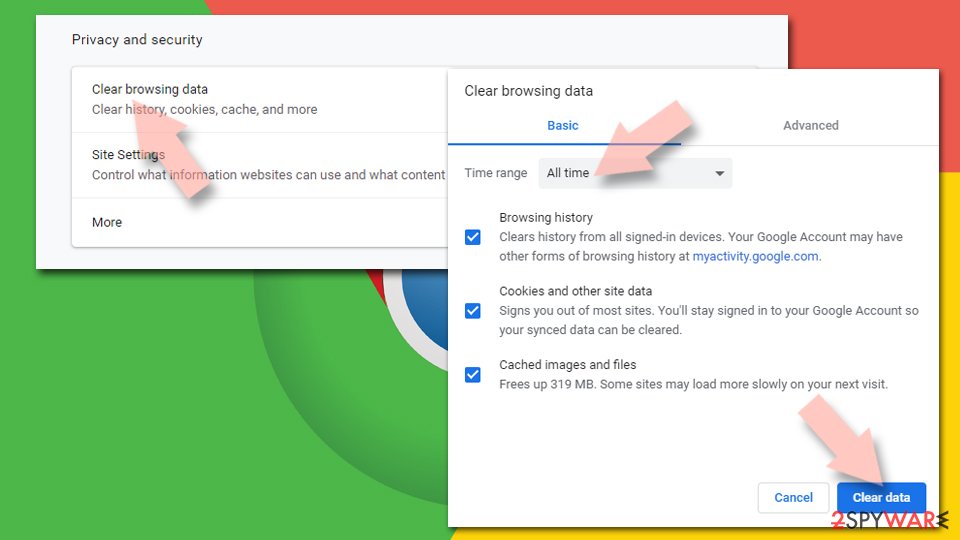
Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
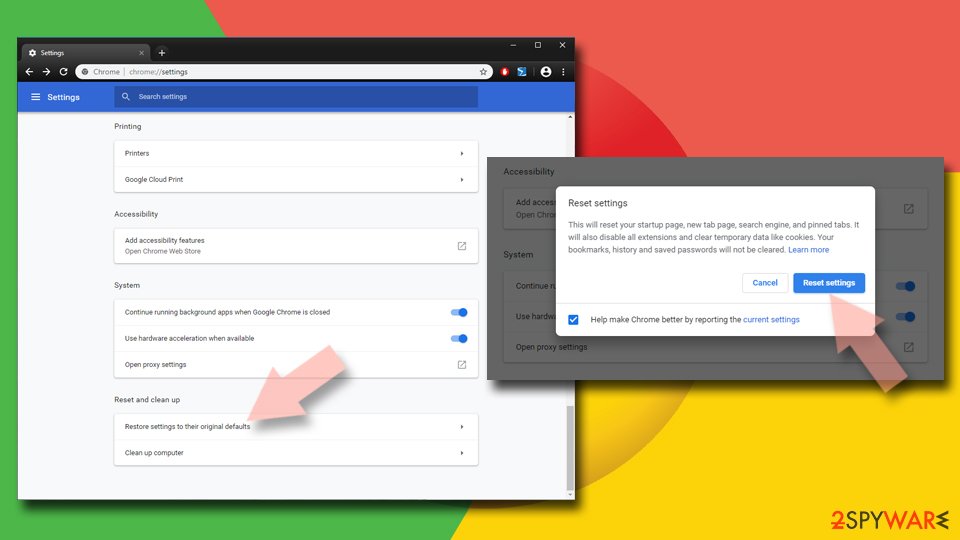
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Microsoft Edge
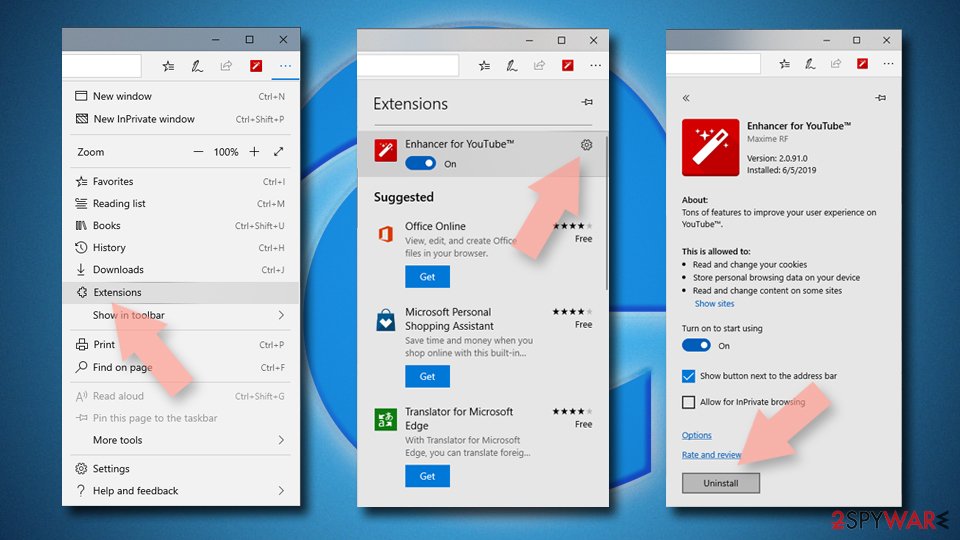
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.
Clear cookies and other browser data:
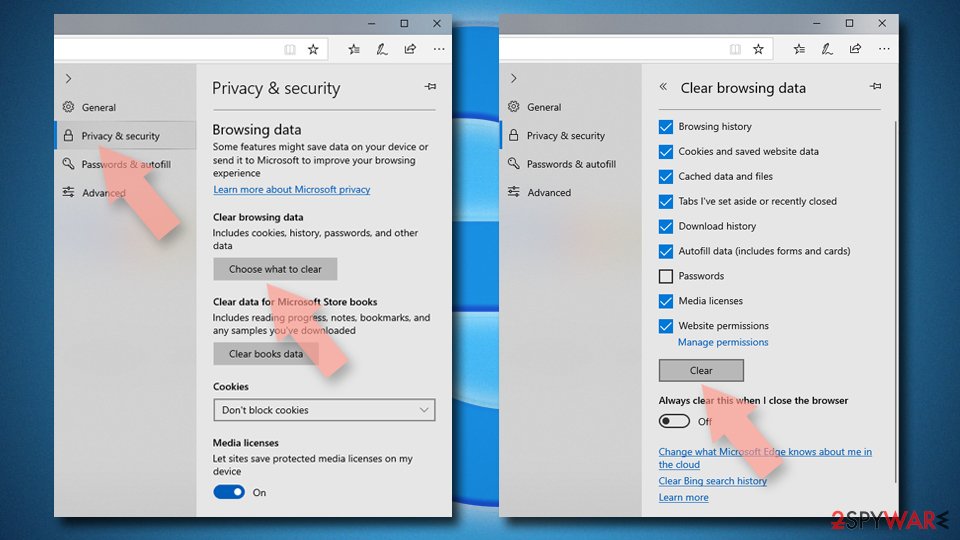
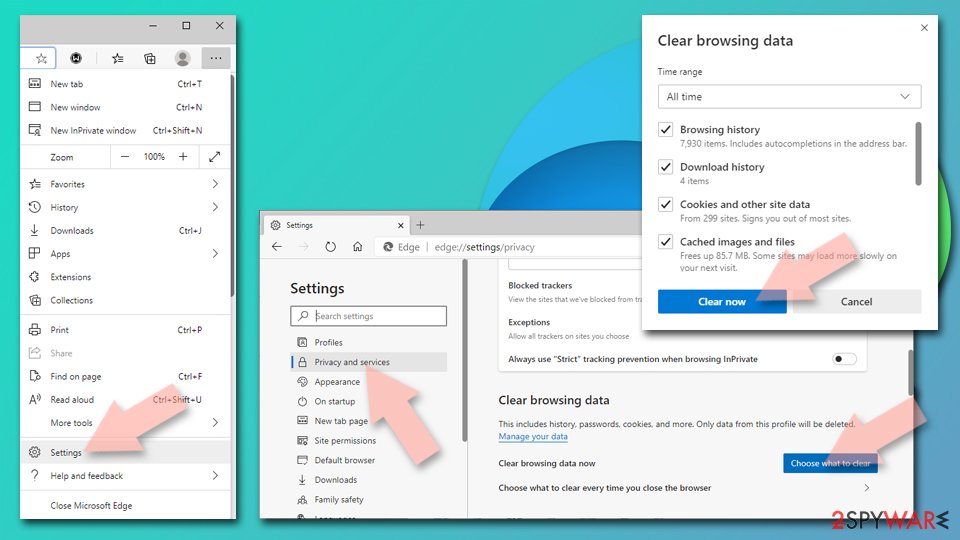
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.
Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
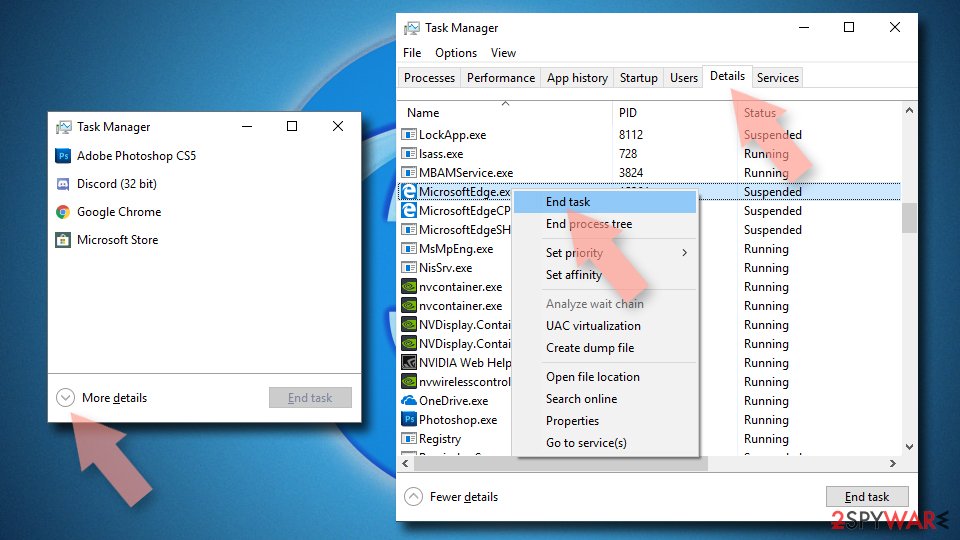
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.
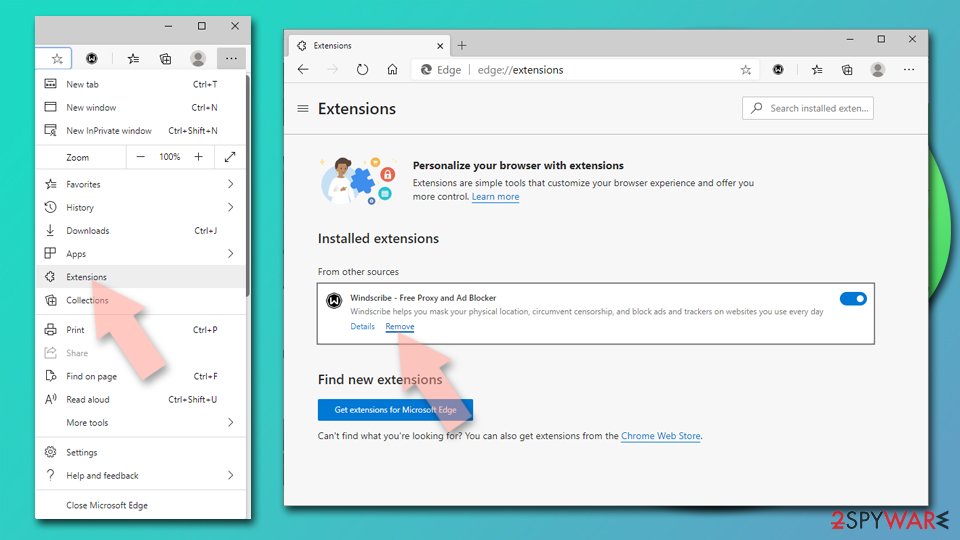
Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
Reset Chromium-based MS Edge:
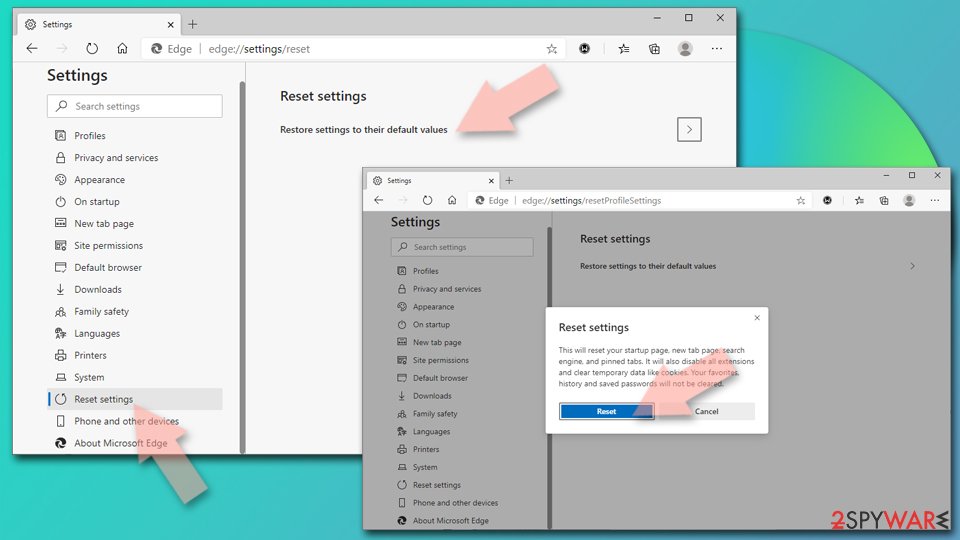
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.
Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
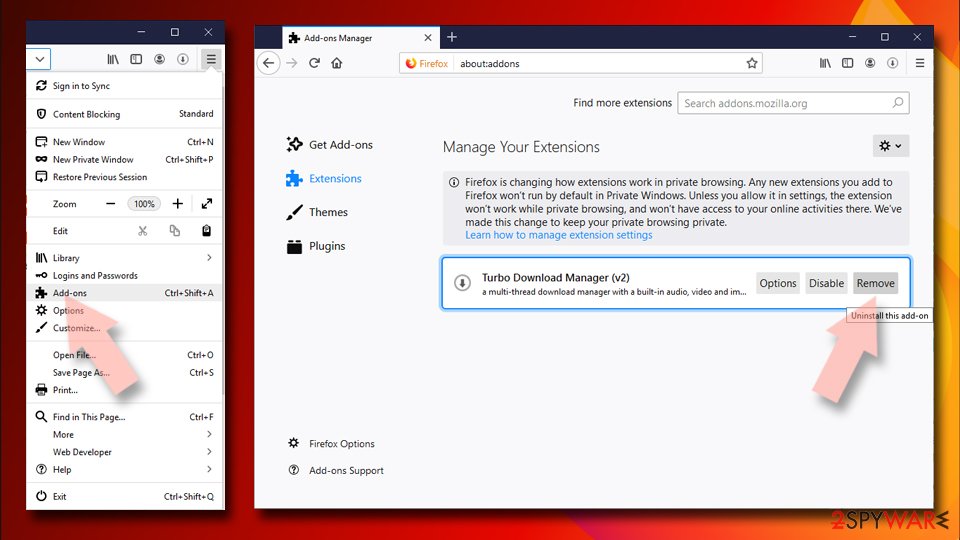
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
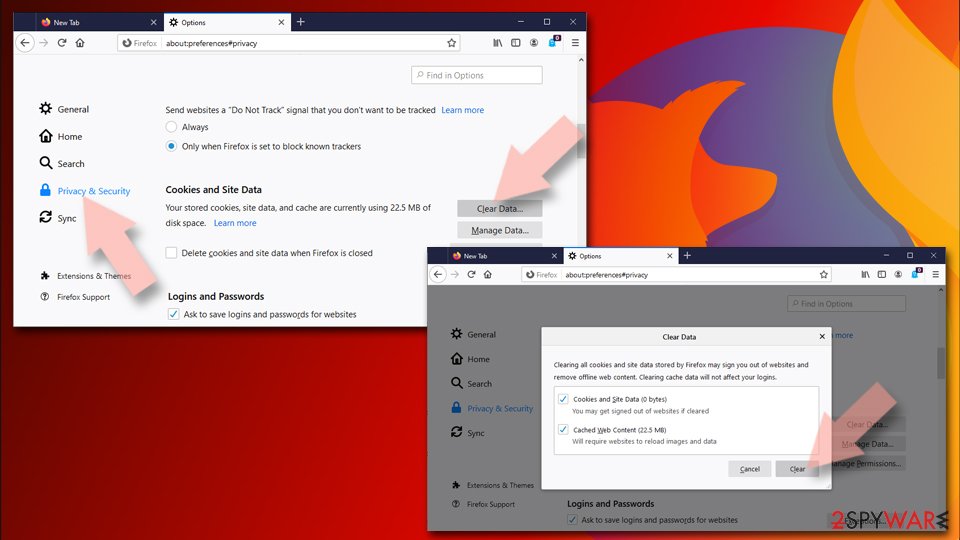
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
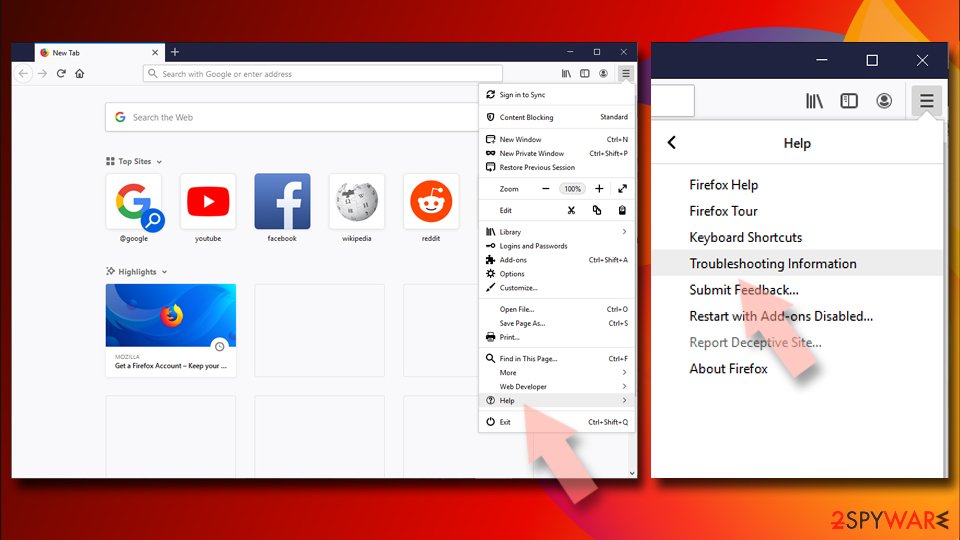
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
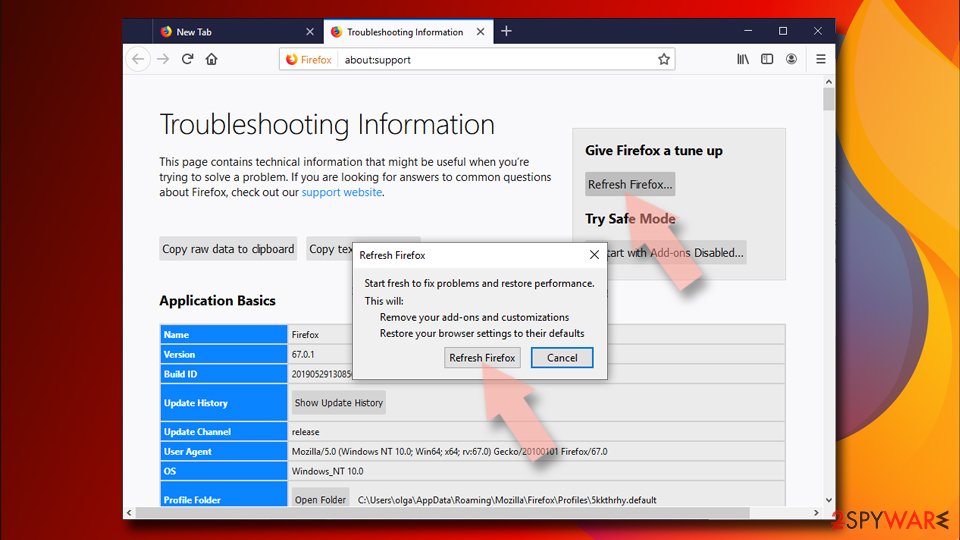
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
Remove dangerous extensions:
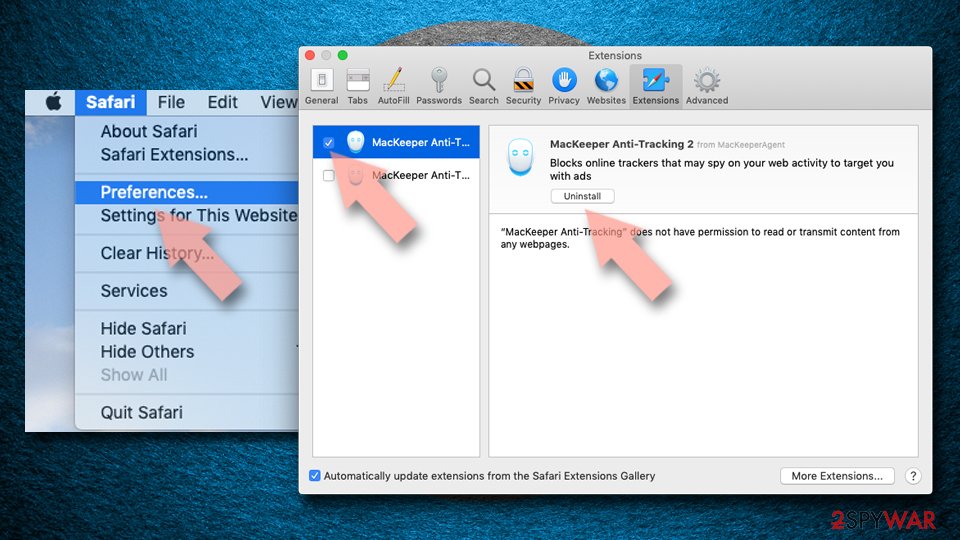
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
Clear history and website data:
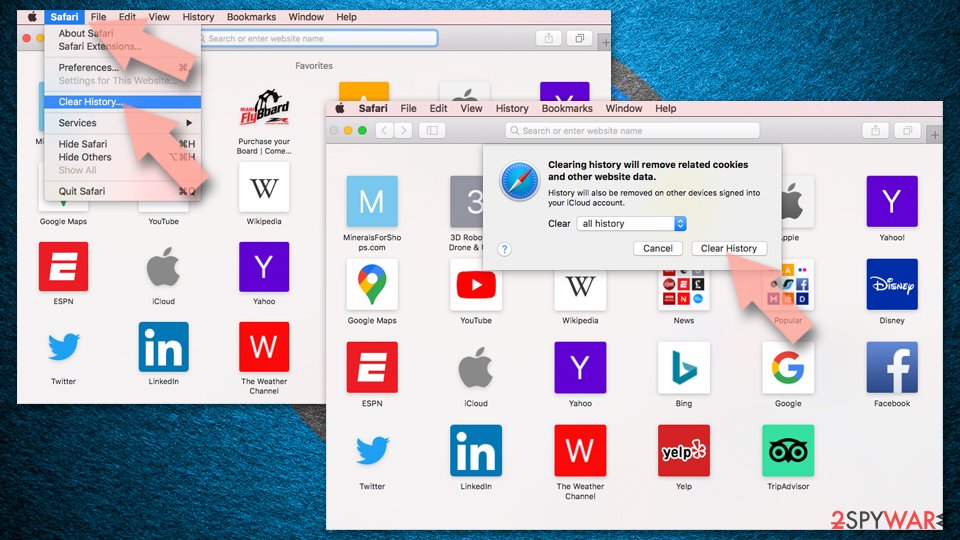
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
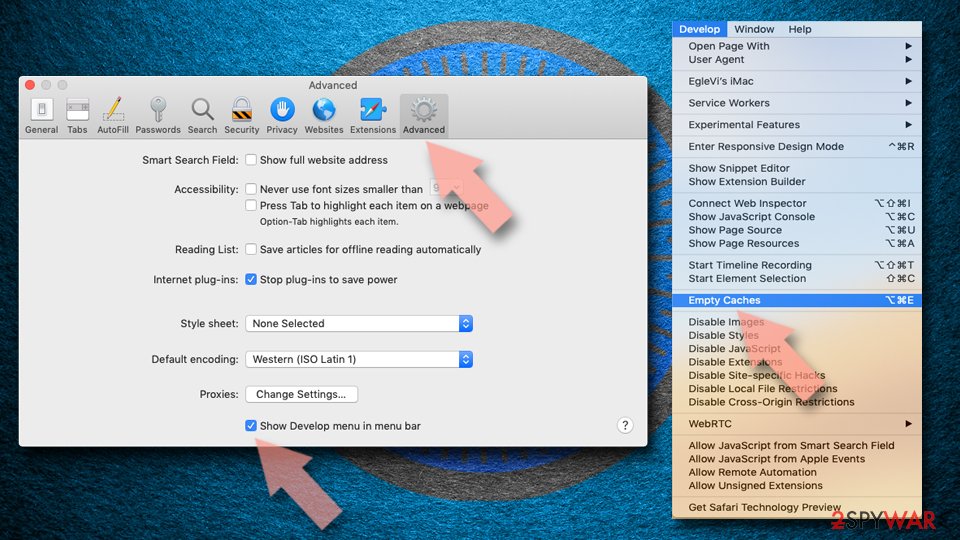
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
Remove the unwanted application:
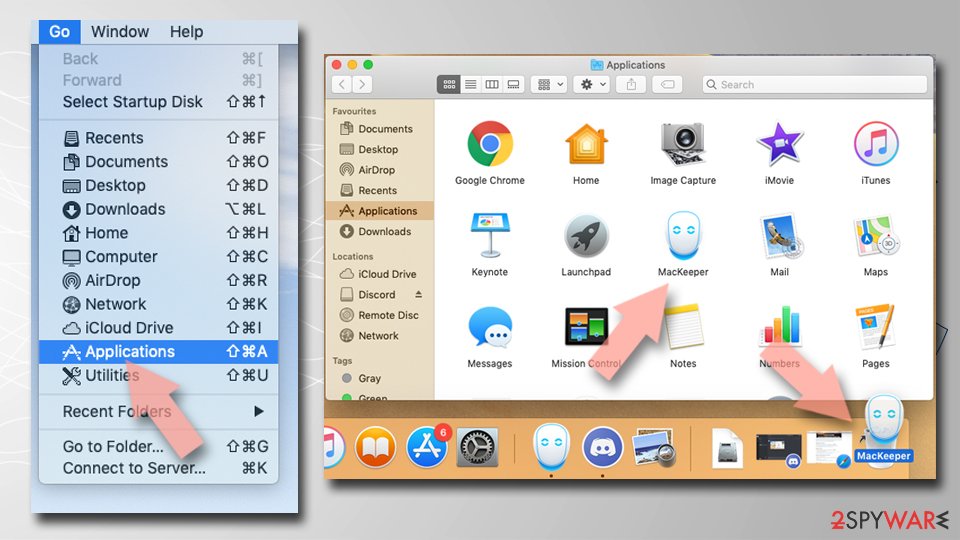
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
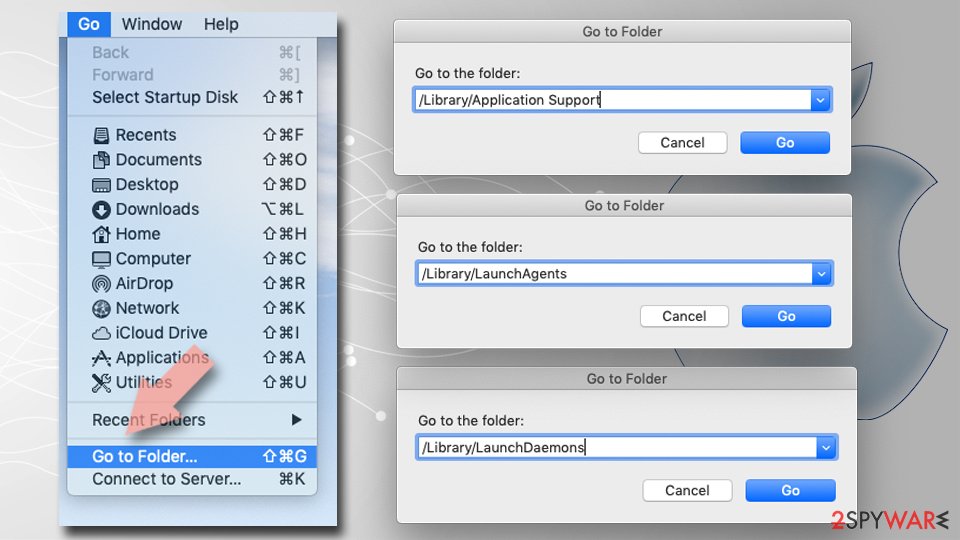
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
Questions about OpenSea email scam
What is the OpenSea email scam?
The OpenSea email scam is a phishing campaign targeting users of the NFT marketplace. Scammers send emails claiming users must migrate Ethereum listings to a new smart contract to avoid expiration fees.
Subject lines read "Migrate Your Ethereum Listings Starting Today" with false deadlines like "February 25." The emails contain legitimate-looking OpenSea branding and logos. When users click links in the email and enter their login credentials, attackers steal account access and drain wallets of NFTs and cryptocurrency.
How does the OpenSea phishing email trick users?
The scam creates urgency by claiming listings expire on a specific date without migration. Users who click the email link are taken to a fake OpenSea login page that looks identical to the real site.
Users enter their credentials thinking they are logging into OpenSea, but instead provide login information to criminals. The deceptive design and use of legitimate company branding make victims believe the email is official. These campaigns have swindled millions from OpenSea users.
What happens if I click the link and log in?
If you enter your credentials on the fake login page, attackers gain access to your OpenSea account. They can transfer all NFTs and cryptocurrency from your account to their own wallets.
If you reused the same password on other platforms, attackers can compromise those accounts too. Your personal information may be sold to other criminals or used for additional fraud. Immediately change your password and check your account activity if you suspect you were victimized.
How do I know if the OpenSea email is fake?
Legitimate companies like OpenSea never ask you to migrate listings via email links. Real OpenSea communications come from official OpenSea channels, not through email asking you to log in. The email address may appear legitimate but is actually a spoofed address.
Check the sender's email domain carefully—scammers often use addresses that look similar but are slightly different. Hover over links before clicking to see the actual URL. When in doubt, log into OpenSea directly through the official website instead of clicking email links.
What should I do if I fell for the scam?
Immediately change your OpenSea password and check your account for unauthorized transactions. Review your connected wallets and revoke access if necessary. Monitor your cryptocurrency wallets for suspicious transfers.
If you provided payment information, contact your bank or credit card company to report fraud. File a report with the FTC at ic3.gov.
Scan your computer with antivirus software to remove any malware that may have been downloaded. Enable two-factor authentication on all accounts.
Can the criminals be stopped?
Blockchain transactions, once completed, cannot be reversed. Cryptocurrency transferred to criminal wallets is nearly impossible to recover. Law enforcement agencies in multiple countries track NFT theft, but success rates are low due to the anonymous nature of cryptocurrency.
Reporting to the FTC and local law enforcement is important for statistics and investigation, but does not guarantee recovery. OpenSea has improved its official communications and security measures, but users must remain vigilant against phishing attempts.
Will OpenSea compensate me for stolen NFTs?
OpenSea itself does not automatically compensate victims of phishing scams. The loss is due to user credential compromise, not a vulnerability in OpenSea's platform. Victims may attempt to file claims or pursue legal action, but recovery is unlikely.
OpenSea advises users to enable two-factor authentication and verify emails directly with OpenSea support rather than clicking email links. Always assume responsibility for account security—phishing scams succeed because users enter credentials on fake sites they control.
How can I protect my OpenSea account from phishing?
Enable two-factor authentication on your OpenSea account. Never click login links in emails—instead, navigate to OpenSea.io directly in your browser. Verify official email addresses carefully.
Bookmark the legitimate OpenSea website and use the bookmark instead of clicking email links. Be skeptical of urgent deadlines or migration requests in emails.
Never share your private keys or seed phrases. Keep your computer free of malware. Use a hardware wallet for valuable NFTs instead of browser wallets.
Will Fortect remove OpenSea email scam?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For OpenSea email scam, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Securitymetrics: 7 Ways to Recognize a Phishing Email: Email Phishing Examples (read October 5, 2026)
- ZDNet: Scam artists swindle NFTs worth 'millions' in OpenSea phishing attack (read October 5, 2026)
- Dieviren: Dieviren (read October 5, 2026)
- FTC: How to recognize and avoid phishing scams (read October 5, 2026)
- CISA: Recognize and report phishing (read October 5, 2026)