
Precomp.exe: is it a virus or a game installer tool, and how to remove the miner
Precomp.exe is either the genuine open-source Precomp tool that game installers use to unpack data, or a cryptocurrency miner that borrows its name. Check the folder it runs from and whether it keeps running after a setup, and remove it with a Microsoft Defender full and offline scan only if it is the miner.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Fake Precomp.exe files rarely come alone; an automatic scan looks for the rest of the infection.
Do it yourself · free Remove Precomp.exe yourself 4 steps, about 12 minutes, no software needed.
Start the steps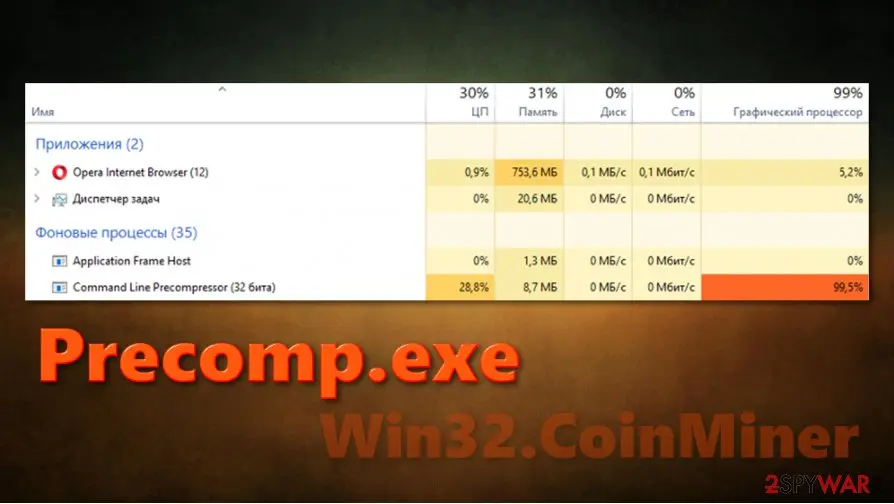
Precomp.exe: summary
| Type | Two cases. The genuine Precomp compression tool used by game installers, and a cryptocurrency miner that copies the name |
|---|---|
| Risk | None from the genuine tool. High from a miner: it takes the processor or graphics card, slows the PC and may arrive with other software from a crack |
| Symptoms | precomp.exe in Task Manager as Command Line Precompressor with high CPU or GPU use, running with no setup open, in an AppData\Roaming folder beside config.xml and OpenCL.dll |
| How to get rid of it | Leave it if it runs only during a setup. If it is a miner: end the process, remove its start-up entries, run a Microsoft Defender full and offline scan, delete the folder |
| Our check (6 October 2026) | No sample run. Tool documentation, Microsoft's miner entry and process-database reports read; they describe two programs, not one |
| First reported by us | 4 November 2020 (the Precomp tool itself dates from 2006) |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 15 more facts
| Detection names | Microsoft Trojan:Win32/CoinMiner; file.net names Kaspersky Trojan.Win32.Miner.tlfy and Symantec ML.Attribute.HighConfidence for files called precomp.exe |
|---|---|
| Name | Precomp.exe |
| Files and processes | Precomp.exe and %AppData% |
| Evidence | Reports from affected users; details still limited |
| File name | Precomp.exe |
| Description | Command Line Precompressor: a genuine open-source tool used by some game installers, and the name a miner copies |
| What it is | Of unknown origin |
| Role | A miner uses the processor or graphics card for someone else's profit and may start with Windows |
| Fake copies seen in | %AppData% (C:\Users\<you>\AppData\Roaming) |
| Linked threat | Cryptocurrency miners of the CoinMiner family (Microsoft: Trojan:Win32/CoinMiner) |
| First seen | 4 November 2020 |
| Microsoft Defender name | Trojan:Win32/CoinMiner |
| Distribution | Left by an unwanted program or its uninstaller |
| Damage | Usually low; it can restart the unwanted program |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against the Precomp readme and licence, the author's forum thread, Microsoft's CoinMiner entry, file.net's process page and Microsoft documentation. We had no sample of a miner and ran no test.
What the Precomp.exe file is
What Precomp.exe is: a real compression tool, and a name that miners borrow
There are two different programs behind the name Precomp.exe. One is a genuine, open-source command-line tool that game installers use to unpack compressed data. The other is a cryptocurrency miner that hides under the same name. The file name alone cannot tell you which one you have; the folder it runs from and what it does can. Our 2020 guide treated every Precomp.exe as a miner and said WinRAR and uTorrent use it; neither holds up.
- The genuine tool
- Precomp, a command-line precompressor by Christian Schneider, published as open source (Apache License 2.0) at github.com/schnaader/precomp-cpp. Its readme says it further compresses files that are already compressed (PDF, PNG, ZIP, GIF, JPG, MP3) and writes a
.pcffile, or restores the original from one - Why it is on your PC
- Some game and program installers carry a copy of it to rebuild their compressed data during setup. Reader comments on file.net describe it appearing for the length of a game install, from a
%Temp%folder, then disappearing - The impostor
- A cryptocurrency miner. Microsoft documents that a miner (Trojan:Win32/CoinMiner) "can be installed with the same name as a legitimate process", is often bundled with installers for software cracks and key generators, and drops library files beside itself. Microsoft's page does not list Precomp.exe among the names it saw; file.net names Kaspersky's Trojan.Win32.Miner.tlfy and Symantec's ML.Attribute.HighConfidence for files of this name
- Part of Windows
- No. Windows does not ship it and does not need it
- Part of WinRAR or uTorrent
- Not as far as we can find. Neither the Precomp readme nor its credits mention either program. Our 2020 text repeated this from a process-database page that files the name under those programs; treat it as unconfirmed
- Task Manager name
- "Command Line Precompressor". The genuine tool and, in our 2020 pictures, the suspicious copies show the same name, so the name proves nothing
- Not on Mac or Android
- This guide is about a Windows
.exe. A Precomp build exists for Linux and macOS, but that is the same legitimate tool and no miner of this name is described for those systems in the sources we read
The useful rule from the sources is simple. A genuine copy runs while a setup is unpacking and stops with it. A miner runs when nothing is being installed, keeps the processor or the graphics card busy for hours, and starts again after a restart.
What we could check, and what we could not
This is a file name, not a website, so there is no site to test, and we did not run any sample of the file. We read the tool's own documentation, Microsoft's description of the miner family, process-database reports and our own 2020 screenshots. Where the sources only describe, we say so.
Public record · read on 6 October 2026
- The genuine tool exists and is documentedThe GitHub repository of Precomp (copyright 2006 to 2021, Apache 2.0, official releases for Windows and Linux) and the author's own thread on the encode.su forum describe a decompress-and-recompress tool. Nothing there describes mining.
- The genuine tool can be flagged by mistakeIn the author's forum thread, a user reported that Bitdefender blocked the tool's website; the author called it a false positive and pointed to a VirusTotal report with 1 detection out of 63. A detection of a Precomp.exe is therefore not proof of a miner by itself.
- Microsoft on miners using ordinary namesTrojan:Win32/CoinMiner (published 16 December 2014, updated 16 March 2018): runs mining software silently, can use the name of a legitimate process, may arrive with cracks and key generators, and makes the PC slower. Microsoft Defender Antivirus detects and removes it.
- Process-database reports of a miner using this namefile.net names two detections for files called precomp.exe (Kaspersky Trojan.Win32.Miner.tlfy, Symantec ML.Attribute.HighConfidence) and quotes reader comments such as a file in a
youtubejsfolder inAppData\Roamingusing 97% of the GPU for over a month, and one inAppData\Roaming\WinRARwith a config file that told it not to run on battery power. These are reader reports, not lab analyses. - Our own run of the fileNot done. We have no sample, so we claim no lab result, no network traffic and no hash of a malicious copy.
- A quiet check on your PCIf a scan finds nothing, that is a result for that scan only. Miners are written to stay unnoticed, and an antivirus program may not flag a miner that looks like a tool (a comment on file.net says Windows Defender and Malwarebytes did not flag a file of this name that used the whole GPU).
Two programs, one name Most reports of the name come from game installs and are harmless. A smaller group describe a miner in a user folder. Judge your copy by where it lives and what it does, not by the name.
Is Precomp.exe safe or a virus?
Precomp.exe through the years
The tool is old and the confusion is just as old. These dated entries show the real program, the miner reports and what our own guide said in 2020.
2006
Precomp begins
The copyright line of the project runs from 2006. The author, Christian Schneider, publishes it as a command-line tool for squeezing files that are already compressed.
16 December 2014
Microsoft describes the CoinMiner trojan
Microsoft's entry for Trojan:Win32/CoinMiner appears. It says the miner may be bundled with installers for cracks and key generators, may drop library files, and can use the name of a legitimate process. It was updated on 16 March 2018.
6 January 2016
Source code on GitHub
The project's first commit is the source of version 0.4.4, with the licence changed to Apache 2.0. Later versions add 64-bit builds, and since 0.4.3 builds for Linux, Unix and macOS.
2016 to 2017
The files in our third picture
The folder in our third picture holds
config.xml,msvcr120.dll,OpenCL.dllandprecomp.exe, dated 2016 and 2017 in the listing. Microsoft describes miners as a program plus library files: a program plus its libraries. OpenCL is an interface for running calculations on the graphics card, and it is not in the list of libraries that Precomp's readme credits.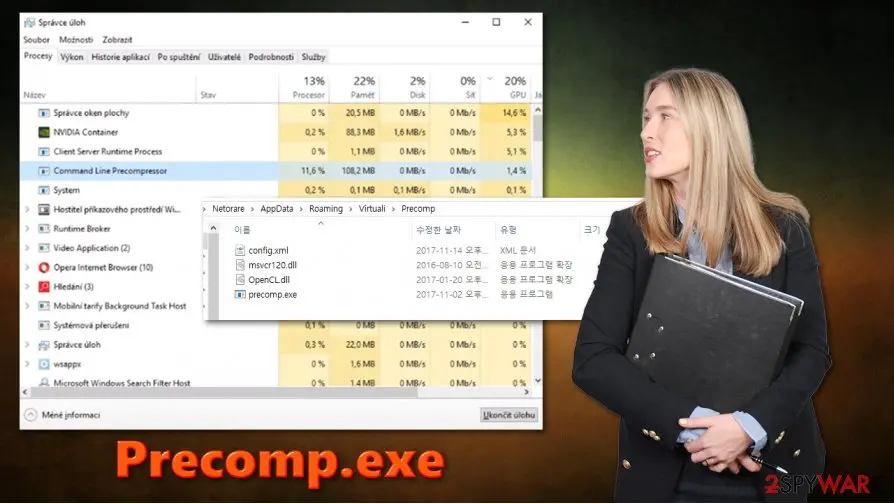
From our 2020 guide: Command Line Precompressor in Task Manager (Czech interface) and a folder AppData\Roaming\Virtuali\Precomp holding config.xml, msvcr120.dll, OpenCL.dll and precomp.exe. The woman is a stock photo and has nothing to do with the file. 4 November 2020
Our first guide
We published the guide as a miner warning, with a Task Manager picture showing 99.5% GPU use. It also said WinRAR and uTorrent use the process, which we could not confirm in 2026.
From our 2020 guide: Task Manager (Russian interface) showing Command Line Precompressor at 28.8% CPU and 99.5% GPU. One moment on one PC, not proof of what the file is. 2021 and 2025
The project is kept up to date
The readme gives the copyright as 2006 to 2021, the last change to the code that we saw is from 20 November 2021, and the licence file was updated on 26 June 2025.
6 October 2026
This rewrite
We split the page into the two cases and replaced "every Precomp.exe is a virus" with checks you can do yourself.
Genuine Precomp or a miner: how to tell them apart
Compare your copy with this table. One match is a hint, three or more is a clear picture. If you are still unsure, treat it as the miner: the cost of a wrong guess is a game you reinstall.
| What you look at | Genuine Precomp from an installer | Miner under the same name |
|---|---|---|
| Where the file is | In a setup's own folder, usually %Temp% or the install folder you chose, next to files of the installer | In a user folder that nobody asked for: AppData\Roaming\<some name>, a youtubejs, YCanPDF, WinRAR or Yandex folder, next to config.xml and library files |
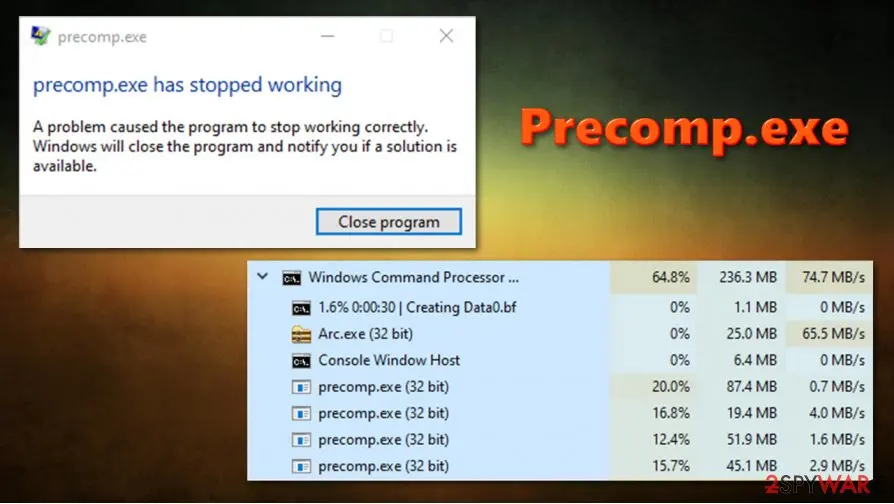
| When it runs | Only while a game or program is installing, often as several processes under one command window | With no setup running, for hours or days, and again after every restart |
| What it uses | The processor, heavily, and the disk. Setup takes a while and ends | Processor or graphics card at 90 to 100% with nothing to show for it, fans at full speed |
| Files beside it | Installer files, Arc.exe or similar, temporary data files | A configuration file, OpenCL.dll or other libraries, sometimes a start-up shortcut or task |
| How it started | Because you started a setup, usually a repack of a game | You never started it; it appeared after a crack, a key generator or a cracked installer |
| What closing it does | The setup fails or stops, as reader comments on file.net report | Nothing visible breaks; it comes back at the next start |
What our 2020 guide got right and wrong
The old text listed a long set of dangers. Here each one is sorted by what the sources we read support.
- High
A miner can run under this name
Supported. Microsoft describes miners that use legitimate-looking names, and file.net lists detections and reader reports for files called precomp.exe. It uses your processor or graphics card for someone else's profit, makes the PC slow and hot, and raises your power bill.
- High
The dropper may carry more
A miner that arrives with a crack or key generator came from software you should not trust. Microsoft says such miners are bundled with other software, so the same download may have installed other things. Scan for more than one file.
- Medium
High CPU use means a virus
Corrected. A genuine Precomp also uses a lot of processor while a game is unpacking, and several reader comments say exactly that. High use with no setup running is the warning sign, not the use itself.
- Medium
Slow PC, crashes, freezes
Plausible for a miner running at full load. Our 2020 picture shows 28.8% CPU and 99.5% GPU at one moment, so it describes one PC at one time.
- Low
Data theft and personal information disclosure
Not documented for the miner family in the Microsoft page. Treat your passwords as at risk only if your scan finds a second threat.
- Low
Corrupted Windows files
Not in the sources. A miner takes processing power; it is not described as damaging system files. Run a system file check only if Windows itself misbehaves.
- Low
The 2020 text on WinRAR and uTorrent
Corrected. We found no support that either program uses Precomp, and a WinRAR folder holding it is a place a miner can hide, not proof of WinRAR.
How to check the Precomp.exe file
Precomp.exe detection names
If Windows Security shows Trojan:Win32/CoinMiner, it has found Precomp.exe or a file that belongs to it.
Write the name down before you click Remove: it is the most useful search term later, and you will need it if you report the incident.
A family name in the label is more informative than a heuristic one. Our page on why one threat has many antivirus names lists the common formats and what each part means.
Check your copy in five minutes
The steps work in Windows 11 and Windows 10. Do not delete anything yet: if it is the genuine tool inside a running setup, deleting it makes the setup fail.
- 1
Ask what you were doing
If you started a game or program setup in the last hour, especially a repack, and the process stops when the setup ends, it is almost certainly the genuine tool. Wait for the setup to finish, then look again.
- 2
Find the file
Press Ctrl + Shift + Esc to open Task Manager. On the Details tab right-click
precomp.exeand choose Open file location. On the Processes tab, right-click a column heading and add GPU if you want to see graphics-card use. - 3
Read the folder
A setup's own folder, such as one under
%Temp%, points to the installer. A folder inAppData\Roamingwith a name you do not know, or one named after another program, does not. Look forconfig.xmlandOpenCL.dllbeside it, as in the third picture below. - 4
Read the properties
Right-click the file, choose Properties, open the Details tab. Note the product name and size. In our pictures the suspicious copies still show "Command Line Precompressor", so the description cannot clear a file.
- 5
Look up the hash
Open Windows PowerShell and run
Get-FileHash "C:\path\to\precomp.exe". Microsoft documents SHA256 as the default algorithm. Paste the result into the search box of VirusTotal. A search by hash asks about the file without sending it; uploading sends the file itself, which you should not do for a file with personal content. - 6
Compare with the official release
The author publishes releases at github.com/schnaader/precomp-cpp/releases. A repack carries its own copy and may use another version, so a different hash alone does not make a file a miner.
- 7
Check the start-up places
Open Startup apps (Windows 11) or Startup (Windows 10) in Task Manager, the folder
shell:startup(Win + R), and Task Scheduler (Task Scheduler Library) for an entry that points to the same folder.
| What you find | What it means | Do this |
|---|---|---|
| Runs during a setup, then ends, in the setup's own folder | Genuine Precomp, very likely | Let the setup finish. Nothing to remove |
Runs with no setup, in AppData\Roaming\<name>, with a config file and OpenCL.dll | A miner using the name | Go to "Removing it" |
Still running hours after a setup, from %Temp% | A setup that hung or left a copy behind, or a miner placed there | End it, run the scans, then decide |
| A scan alert for CoinMiner or Miner but no process | A copy is on the disk or in a start-up place | Run the full and offline scan |
| Nothing of the above | No sign on this check. Not a clearance: miners hide, and they can wait | Run one full Microsoft Defender scan anyway |
Where Precomp.exe comes from
No source tells how your copy arrived. The descriptions agree on a few routes, and the first one is by far the most common in the reports we read.
- High
Cracked and pirated installers
Microsoft names installers for cracks and key generators as a way miners arrive. Reader comments on file.net tie the file to cracked and repacked games. Our 2020 guide named pirated video games and cracked software for the same reason.
- High
Dropped by other malware
Microsoft says the miner may be bundled with other software you installed. If you find the miner, assume the download that brought it may have installed something else.
- Medium
E-mail attachments and links
The old guide listed attachments and links with macros. We found no report that ties this file name to e-mail, so we mention it as a general risk, not as a known route.
- Medium
A genuine copy in a repack
Because the real tool is used by repack installers, a repack makes a good place to hide a miner with the same name beside it. A repack from an unknown uploader is a risk even if each file looks ordinary.
What to do with Precomp.exe
How to remove Precomp.exe
It is usually a leftover of an unwanted program.
Uninstall the program, then delete what remains.
Step 1: Uninstall programs you did not mean to install
Precomp.exe rarely comes alone: it is usually installed by, or together with, a free program. In Windows 11 open Settings > Apps > Installed apps, in Windows 10 Settings > Apps > Apps & features, and sort by install date.
Uninstall every entry from the day the trouble began that you did not install on purpose, for example a download manager, a converter or a browser you never chose.
Keep drivers and entries from Microsoft, Intel, AMD, NVIDIA or your PC's maker unless you are sure.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 2: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after Precomp.exe, its publisher or created on the day the problem started. Delete those folders, and check C:\Program Files and C:\Program Files (x86) too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 3: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Scan the PC, then run the offline scan
A scan finds the parts of Precomp.exe that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Removing it: the order that works
Remove it only if your check points to a miner. Safe Mode and System Restore are not needed, and a restore point made after the infection holds the miner too.
- 1
End the process
In Task Manager, Details tab, right-click
precomp.exe> End task. Note the folder first (Open file location). - 2
Remove its start-up entries
Delete a shortcut to it in
shell:startup, and in Task Scheduler > Task Scheduler Library delete a task that starts a file in the same folder. In Startup apps (Windows 11) or Startup (Windows 10) set a matching entry to Disabled. - 3
Run a Microsoft Defender full scan
Windows Security > Virus & threat protection > Scan options > Full scan > Scan now. Microsoft says Defender Antivirus detects and removes Trojan:Win32/CoinMiner and recommends a full scan because it can find hidden malware. Microsoft Safety Scanner is a free second opinion.
- 4
Run the offline scan
On the same page choose Microsoft Defender Antivirus (offline scan) > Scan now. The PC restarts and scans before Windows loads.
- 5
Delete what is left
After the scans, if the folder you noted still holds
precomp.exe,OpenCL.dlland a config file, close the process and delete the folder. Check that nothing important is stored there. - 6
Restart and look again
Open Task Manager and watch the processor and GPU for ten minutes with nothing running. If the load or the process returns, something starts it: check Task Scheduler and Startup again.
- 7
If a program owns it
If the file belongs to a program you installed on purpose and it causes trouble, uninstall that program in Settings > Apps > Installed apps. Do not delete files from its folder by hand.
- 8
Check Windows only if needed
If Windows tools misbehave after the clean-up, open Command Prompt as administrator and run
sfc /scannow, then, if it reports damage,DISM /Online /Cleanup-Image /RestoreHealth.
Do
- Scan with Microsoft Defender or another known antivirus that is already installed.
- Change the passwords of accounts you used on this PC if the scan found anything besides the miner.
- Reinstall the cracked program from a source you can trust, or buy it.
Don't
- Download a "Precomp.exe remover" from search results; that is how people install a second problem.
- Delete the file while a setup is running: it will fail halfway.
- Treat a clean scan as proof, if the PC still runs hot with nothing open.
After the check: keep Windows clean
Miners are only one of the many things a bad download can carry, and many stay quiet for weeks. These habits cover the whole group.
Do
- Get programs and games from the maker's site or a known store, not from cracks or torrent bundles.
- Keep Windows Security on with real-time protection, and Windows Update automatic.
- Run a full scan from time to time, not only when something feels wrong.
- Check the processor and GPU in Task Manager when the fans are loud and nothing is open.
- Use strong passwords, never repeated, and keep a backup of your files on a drive that is disconnected afterwards.
Don't
- Open unexpected attachments or let a document run macros.
- Visit sites that hand out cracks, key generators and "free" versions of paid programs.
- Assume that a clean scan means a clean PC. No antivirus detects everything, and the criminals change their files.
Questions about Precomp.exe
Is Precomp.exe a virus?
It depends on which Precomp.exe you have. The name belongs to a genuine open-source tool, Precomp by Christian Schneider, which some game installers use to unpack compressed data during setup. It also belongs to a cryptocurrency miner that copies the name; Microsoft documents that miners can use the name of a legitimate process.
A copy that runs only during a setup, from the setup's own folder, is very likely the genuine tool. A copy that runs for hours with no setup, from a user folder in AppData\Roaming beside a config file and OpenCL.dll, is a miner. Check the folder and the behaviour, not the name.
Why is Precomp.exe using so much CPU?
A genuine Precomp uses a lot of processor on purpose: it is decompressing and recompressing data for a game installer, and reader comments on file.net report 25 to 50% CPU for as long as the setup runs. That use ends when the setup ends.
If the process is still busy hours later with no setup open, or it uses the graphics card, it is not doing installer work. Our 2020 picture shows 28.8% CPU and 99.5% GPU in one moment, which fits a miner but is one reading on one PC. Watch Task Manager for ten minutes with nothing running before you decide.
Is Precomp.exe a Windows file or part of WinRAR?
No. Precomp.exe is not a Windows file, and we found no support that it belongs to WinRAR or uTorrent. Our 2020 guide repeated that link from a process-database page, and we have corrected it. The Precomp readme and its credits name neither program.
A Precomp.exe in a folder called WinRAR inside AppData\Roaming is a reason to look closer, not a sign that WinRAR put it there, because that is also a place where miners hide. A genuine copy comes with a setup you started yourself.
How do I know if my Precomp.exe is a coin miner?
Compare four things. First, where the file is:
- a miner usually sits in AppData\Roaming in an unfamiliar folder
- with a config.xml and OpenCL.dll
- while the genuine copy sits in a setup's folder
Second, when it runs: a miner runs with no setup open. Third, what it uses: a miner takes 90 to 100% of the processor or the graphics card.
Fourth, its hash: run Get-FileHash in PowerShell and look the result up on VirusTotal. One match is a hint, and a clean scan does not clear it.
How do I remove Precomp.exe?
Remove it only if the checks point to a miner. End the process in Task Manager, delete its start-up shortcut and scheduled task, then run a Microsoft Defender full scan and the offline scan from Windows Security.
Microsoft says Defender Antivirus detects and removes the CoinMiner family. After the scans, delete the leftover folder, restart and watch the processor and graphics card for ten minutes. If it is the genuine tool inside a running setup, leave it alone: deleting it makes the setup fail.
Is it safe to end or delete Precomp.exe during a game install?
No, not while the setup is running. Reader comments on file.net say that ending the process or deleting the file made the installation stop or fail, because the installer needs the tool to rebuild its data. Wait until the setup finishes and the process disappears.
If it stays after the setup is done, then check its folder and run the scans. Ending it early only wastes the time the setup has already spent, and a half-finished install may leave broken files that you then have to remove and install again from the start.
Can a pirated game cause Precomp.exe high CPU usage?
Yes, in two ways. Repacked games often use the genuine tool during setup, so you may see it using a lot of CPU for a while, and that is normal. Cracks and key generators are also where Microsoft says miners are bundled, so a miner with the same name may arrive in the same download.
You cannot tell which from the download alone. Check whether the process runs after the setup, and where its file is. We do not advise using pirated software, because the same download can carry other malware.
Does Windows Defender detect Precomp.exe?
Sometimes, but do not rely on it. Microsoft says Defender Antivirus detects and removes Trojan:Win32/CoinMiner, yet a file.net comment says Windows Defender and Malwarebytes did not flag a file of this name that used the whole GPU.
In the other direction, the genuine tool can be flagged by mistake: the author called a Bitdefender block on his site a false positive. A clean scan therefore never clears the file; judge by location and behaviour, and run the offline scan if something still looks wrong.
Can Precomp.exe steal my passwords or install ransomware?
We found no source that says so for a miner of this name. Microsoft's CoinMiner entry describes mining, a slower PC and bundled software, not data theft or ransomware. Our 2020 guide said more, without a source, and we have corrected it.
The risk that remains is the download that brought the miner: a crack or key generator can carry other malware. If the scan finds a second threat, change your passwords from a clean device and treat the PC as compromised.
Will Fortect remove Precomp.exe?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Precomp.exe, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- GitHub: schnaader/precomp-cpp (Precomp readme, licence, credits) (read October 6, 2026)
- encode.su forum: Precomp 0.4.5 (author's thread) (read October 6, 2026)
- Microsoft Security Intelligence: Trojan:Win32/CoinMiner (read October 6, 2026)
- file.net: precomp.exe Windows process (detections, reader comments) (read October 6, 2026)
- Microsoft Learn: Get-FileHash (read October 6, 2026)
- VirusTotal documentation: How it works (read October 6, 2026)
- Microsoft Learn: Microsoft Defender offline scan (read October 6, 2026)
- Microsoft Learn: Use the System File Checker tool (read October 6, 2026)