
Program:Win32/Wacapew.B!ml: what it is and how to remove it
Program:Win32/Wacapew.B?ml may be a false positive or the genuine SDBbot Remote Access Trojan. The 2020 guide noted Windows Defender had issues with false positives that were later fixed.
Facts checked October 13, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If mswinload0.dll returns after removal, a full scan can find the entry that brings it back.
Do it yourself · free Remove Program:Win32/Wacapew.B!ml yourself 6 steps, about 18 minutes, no software needed.
Start the steps
Program:Win32/Wacapew.B!ml: summary
| Detection names | No Microsoft detection name is known |
|---|---|
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Name | Program:Win32/Wacapew.B!ml |
| Type | Loader |
| Symptoms | An unknown process in Task Manager and a Windows Security "Threats found" notification |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 5 more facts
| Evidence | 5 write-ups by security sites; no sample analysed yet |
|---|---|
| File names | mswinload0.dll |
| First seen | 11 June 2020 |
| Microsoft Defender name | Program:Win32/Wacapew.B!ml |
| Facts checked | 5 October 2026 |
What Program:Win32/Wacapew.B!ml does on an infected PC
What readers reported about Program:Win32/Wacapew.B!ml
Is new Bitdefender 2013 Plus good to protect against FBI virus?. My old desktop was infected with the FBI virus. I threw out the computer and downloaded Bitdefender Antivirus 2013 Plus on my laptop. Do I need to purchase another malware software program to defend against the FBI virus?
How to get rid of IncrediBar in Firefox?. Hello, I have some troubles with Incredibar. It seems there is no an easy way to remove it.. there is no such program in add/remove program list. Can anyone help me to delete Incredibar? I'm using Firefox as a default Browser. thanx in advance Moly
From the comments under our earlier guide; names and contact details removed.
What Grayware/Win32.Wacapew means and how it relates to the Microsoft name
Grayware/Win32.Wacapew is a label for the same Wacapew family written in another style, not a separate threat.
We found no reliable source that names the antivirus engine using exactly this label. Our reading: it is how another scanner, for example one of the engines in a VirusTotal report, names a file that Microsoft calls Program:Win32/Wacapew. The family name Wacapew links the two.
The first word of both names says the same thing. Microsoft Learn lists Program as a type of unwanted software, not as a type of malware such as Trojan or Backdoor. Grayware is a common industry word for programs between clean and malicious, such as bundled installers, cracks and tools with odd behaviour. Win32 in both names means the Windows 32-bit platform, so the file is a Windows program.
Microsoft also notes that security vendors sometimes use different names for one family, and that a suffix starting with ! is an internal Microsoft marker. So Grayware/Win32.Wacapew, Wacapew.B!ml and Wacapew.C!ml all point to the same kind of suspicious Windows file. To check any such name, open Windows Security, go to Protection history, note the file path, and upload that file to VirusTotal to compare the verdicts of many engines.
From our report of Jun 2020 · not reviewed since
Program:Win32/Wacapew.B!ml can be a false positive detection or refer to an SDBbot Remote Access Trojan
Program:Win32/Wacapew.B!ml is a generic detection name delivered to Windows users by Windows Defender antivirus program.
Typically, people encounter a pop-up flagging malicious behavior on the machine after installing a piece of software, especially keygens, cracks of software for hack tools for the Windows license key. This issue has been extremely prevalent in 2019 as there were many reports on Microsoft forums.
Nevertheless, people keep asking how to remove Program:Win32/Wacapew.B!ml trojan up till now. If you keep getting a report from Windows Defender reporting this infection, the culprit may be wrong virus definitions of the in-built Windows security software.
However, ignoring this detection may be a huge mistake because the detection may refer to the malicious mswinload0.dll file, which is one of the core processes run by Get2 downloader and SDBbot RAT.
Program:Win32/Wacapew.B!ml detection alert by Windows Defender Antivirus can be a false positive. According to user reports, this security tool has had some issues with virus definitions and tended to flag reliable software as malicious. Upon testing the issue, Microsoft has initiated comprehensive log changes for security intelligence update version 1.293.1036.0 and added renewed threat detections.
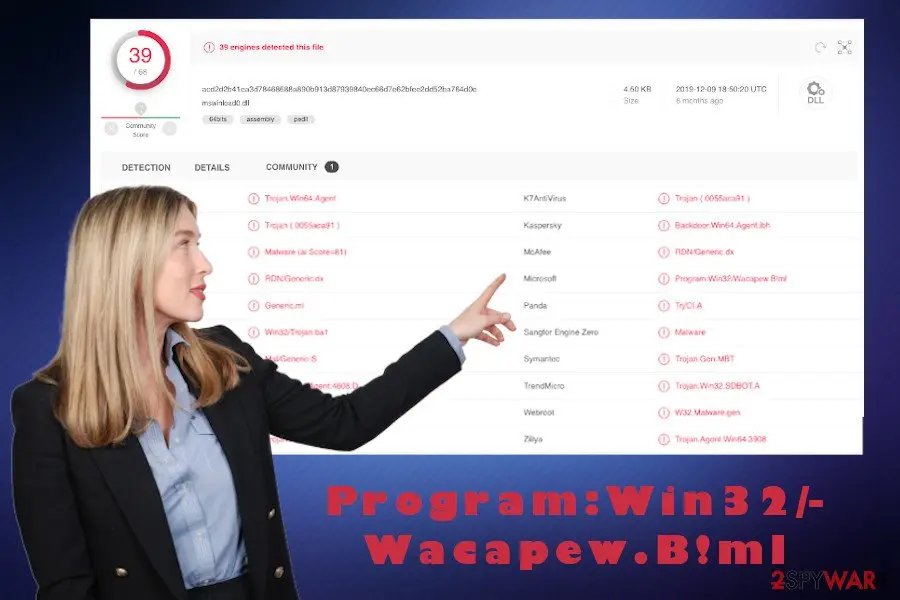
Upon the update, the issue regarding false positive detection of the Program:Win32/Wacapew.B!ml virus seems to have stopped. However, people are still having this same detection warning brought by Windows Defender Antivirus, while scanning the machine with alternative AV engines report the following detections:
In this case, the Program:Win32/Wacapew.B!ml detection can be related to a highly dangerous SDBbot Remote Access Trojan and Get2 Downloader. According to Proofpoint researchers who detected this threat in spring 2019, this malicious RAT allows hackers to take full control over the host machine and subsequently sends commands to download and run files, monitor the activities, harvest information, log keystrokes, take screenshots, capture Webcam shoots, and similar.
Program:Win32/Wacapew.B!ml virus is typically downloaded by a Get2 trojan. The latter can get into the system silently via spam email attachments (hpe_s_hp-inv_02[.]xls, dc123456[.]xls, business cloud invoice no142 09-09-2019[.]xls, etc.), roots into the system without manifesting its presence, thus ensuring persistence.
After that, the Get2 Trojan runs a pack of malicious processes and downloads the FlawedGrace, FlawedAmmyy, Snatch, and SDBbot RAT as secondary payloads. According to cybersecurity experts, Windows Defender and other AV security tools recognize the malicious performance of the mswinload0.dll file.
Anyway, if your security suite keeps warning you about a highly dangerous Trojan, evaluate the situation adequately, and take needed actions to remove Program:Win32/Wacapew.B!ml virus from the system completely. If the detection turns out to be related to the SDBbot RAT, it may lead to privacy violations, identity theft, or money loss.
If Program:Win32/Wacapew.B!ml Windows Defender Antivirus detection is bound to this particular security suite and none of the other AV engines detect issues on your device, it's possible that it's a false positive detection and you should report this issue to the Microsoft support.
Otherwise, take action to protect yourself from hackers by initiating a thorough Program:Win32/Wacapew.B!ml removal. Malicious Trojans usually enable commands to disable AV software. You can rely on tools like , , or another robust anti-malware.
Post Trojan state of the Windows machine can not be pleasant. Malicious viruses tend to alter Windows registry entries, startup programs, core processes, some system files, etc. that eventually can cause errors and BSODs. Therefore, right after you remove Program:Win32/Wacapew.B!ml virus detection, try optimizing the system with repair suite.
- Trojan.GenericKD.42040575
- TR/Agent.gyhwl
- Malware@#15ko81j88dnzv
- W64/Agent.SE!tr
- RDN/Generic.dx
- Win32/Trojan.ba1
- Trojan.Win32.SDBOT.A
- Backdoor.Win64.Agent.ibh, etc.
From our report of Jun 2020 · not reviewed since
Terminate Program:Win32/Wacapew.B!ml trojan to protect yourself from identity theft
When the Program:Win32/Wacapew.B!ml virus gets onto the machine, it can decrease its performance, increase vulnerability, and download other malicious entries to the system.
Although it may be difficult to detect this entry manually, you can suspect the presence of a Trojan if the system keeps restarting all of a sudden, CPU usage gets high, AV engine keeps flagging malicious behavior, etc.
Keep in mind that severe computer viruses are exceptionally persistent and can hide malicious files over the system, disable AV tools, quarantine legitimate software, remove Windows registry entries, etc. Therefore, you should go to the Safe Mode and then focus on Program:Win32/Wacapew.B!ml removal.
To remove Program:Win32/Wacapew.B!ml virus completely, try using reputable anti-malware tools, such as . Robust security tool ensures elimination of malicious files, clean PUPs, and other viruses. Nevertheless, AV tools are not programmed to repair the Registries and other Windows locations.
[GI=method-1]If you are dealing with the Program:Win32/Wacapew.B!ml trojan virus on your machine, try restarting it to Safe Mode with Networking and launch the security tool. Set it to scan the system thoroughly. Note that a full scan can take some time, so be patient.
[GI=method-2]If Safe Mode does not work, try to quarantine Program:Win32/Wacapew.B!ml malware using System Restore feature.
From our report of Jun 2020 · not reviewed since
More from our earlier report on Program:Win32/Wacapew.B!ml
- It's a generic virus detection name that can either be a false positive or flag a malicious banking Trojan infection
- The main symptom - Windows Defender keeps launching warning popups reporting the malicious behavior of the Program:Win32/Wacapew.B!ml virus.
- Apart from warnings, the Windows machine may become sluggish, CPU consumption may jump from low to high, etc.
- Win64:Trojan-gen (Avast), Malware@#15ko81j88dnzv (Comodo), Trojan.TR/Agent.gyhwl (F-Secure), Mal/Generic-S (Sophos AV), Win64:Trojan-gen (AVG), Trojan.GenericKD.42040575 (BitDefender), Trojan.GenericKD.42040575 (B) (Emsisoft), etc.
- If any AV engine reports a malicious application, reboot the system into Safe Mode and perform a thorough system scan.
- Malicious Trojans and spyware are capable of corrupting Windows registries and startup programs.
- Thus, the repair is required upon virus removal.
- In the registry-based persistence mechanisms, a separate loader DLL is used to execute the RAT payload.
- In the analyzed sample, the loader was named "RegCodeLoader[.]dll" and saved to disk as "mswinload[.]dll" or "mswinload0[.]dll".
- The application shimming-based persistence doesn't use a separate DLL, but the code it patches into services[.]exe is similar in functionality.
- In both cases the random registry key and value name is patched into the loader code.
How Program:Win32/Wacapew.B!ml got on your PC
From our report of Jun 2020 · not reviewed since
Malicious payloads can get into the system via malicious spam email attachments or pirated software like keygens and cracks.
Beware that suchlike malicious files do not disclose their presence. Instead, they remain in disguise with legitimate Windows system files, such as mswinload0.dll, Svchost.exe, or Winrmsrv.exe.
Payloads are responsible for downloading cyber threats, such as Trojans, spyware, malware, RATs, and more. Beware that they are developed in an extremely sophisticated manner to bypass antivirus programs without being noticed. Thus, you should evaluate online risks to prevent launching malicious files related to viruses.
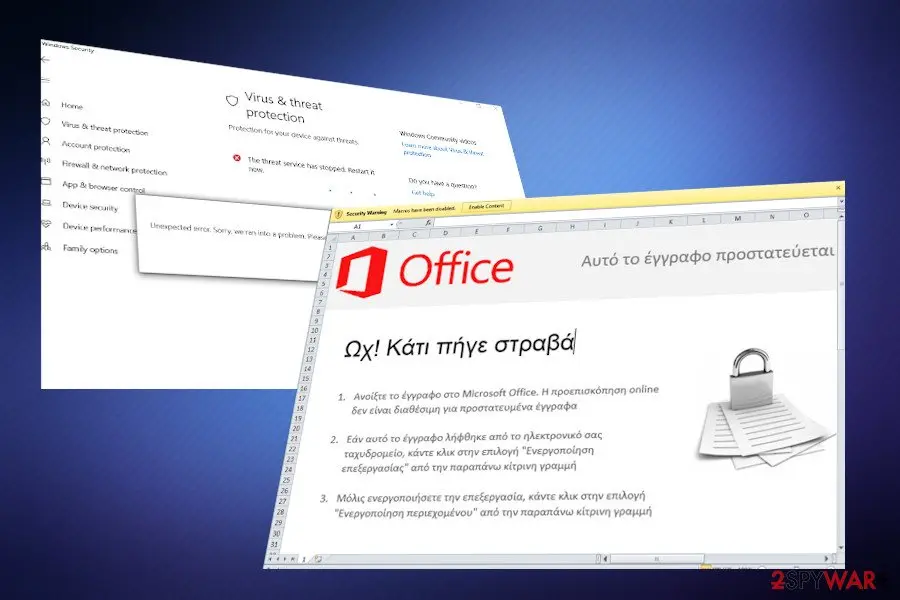
In most of the cases, such viruses are being disseminated via malicious spam email attachments. Hackers can release tens of thousands of email that contain Microsoft Excel attachments under names like
Such attachments require to enable macros, which is a catch used by hackers to make users download malicious virus payload. Thus, if you received a questionable email message that you were not waiting for, it's better to send it to spam inbox or completely remove it.
Another perfect perfect medium for viruses to spread is pirated software. As pointed out by NoVirus.uk team , hackers can fill keygens and software cracks with malicious virus payloads quite easily. Thus, instead of downloading a "help" to hack some paid software, you can get your machine hacked.
- Subject - HPE INV-02 - Invoice and documents. Attachment hpe_s_hp-inv_02[.]xls.
- Subject - Need to Apply. Attachment dc123456[.]xls
- Subject - Document. Attachment business cloud invoice no142 09-09-2019[.]xls
- Subject - EXECUTIVE SUMMARY. Attachment προτιμολογιο[.]xls
How to check the PC for Program:Win32/Wacapew.B!ml
Program:Win32/Wacapew.B!ml detection names
If Windows Security shows Program:Win32/Wacapew.B!ml, it has found Program:Win32/Wacapew.B!ml or a file that belongs to it.
Write the name down before you click Remove: it is the most useful search term later, and you will need it if you report the incident.
A family name in the label is more informative than a heuristic one. Our page on why one threat has many antivirus names lists the common formats and what each part means.
- File:
mswinload0.dll
How to remove Program:Win32/Wacapew.B!ml
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Check where mswinload0.dll runs from and stop it
In Task Manager (Ctrl + Shift + Esc) find
mswinload0.dllon Processes, right-click it and choose Open file location before ending anything.Windows' own files live in
C:\Windows\System32; the same name in%AppData%, %Temp% or C:\Users\Public is an impostor. If the folder is wrong, right-click the process again, choose End task and delete the file.If it starts again within seconds, a task or another process restarts it, so run the scan step in Safe Mode. Task Manager works the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 2: Delete scheduled tasks that bring it back
Programs like Program:Win32/Wacapew.B!ml add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 3: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after Program:Win32/Wacapew.B!ml, its publisher or created on the day the problem started.Delete those folders, and check
C:\Program FilesandC:\Program Files (x86)too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 5: Scan the PC, then run the offline scan
A scan finds the parts of Program:Win32/Wacapew.B!ml that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
Program:Win32/Wacapew.B!ml can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed an unfamiliar process called mswinload0.dll in Task Manager, a sign of a program that could read browser data, the clean-up is only half of the work.
The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
Choose a proper web browser and improve your safety with a VPN tool
Online spying has got momentum in recent years and people are getting more and more interested in how to protect their privacy online.
One of the basic means to add a layer of security - choose the most private and secure web browser. Although web browsers can't grant full privacy protection and security, some of them are much better at sandboxing, HTTPS upgrading, active content blocking, tracking blocking, phishing protection, and similar privacy-oriented features.
However, if you want true anonymity, we suggest you employ a powerful VPN - it can encrypt all the traffic that comes and goes out of your computer, preventing tracking completely.
Lost your files? Use data recovery software
While some files located on any computer are replaceable or useless, others can be extremely valuable.
Family photos, work documents, school projects - these are types of files that we don't want to lose. Unfortunately, there are many ways how unexpected data loss can occur:
- power cuts
- Blue Screen of Death errors
- hardware failures
- crypto-malware attack
- even accidental deletion
To ensure that all the files remain intact, you should prepare regular data backups. You can choose cloud-based or physical copies you could restore from later in case of a disaster. If your backups were lost as well or you never bothered to prepare any, can be your only hope to retrieve your invaluable files.
Questions about Program:Win32/Wacapew.B!ml
Is Program:Win32/Wacapew.B?ml a real threat?
It can be either a false positive or a genuine threat. Windows Defender may flag it as both—a false positive with incorrect virus definitions, or a genuine SDBbot Remote Access Trojan. In 2019, Microsoft identified issues with security intelligence update version 1.293.1036.0, causing false positive detections.
However, when other security tools also detect it, the detection likely refers to actual malware. The mswinload0.dll file associated with this detection is used by Get2 downloader and SDBbot RAT for persistence mechanisms.
What is SDBbot and why does it matter?
SDBbot is a highly dangerous Remote Access Trojan discovered by Proofpoint researchers in 2019. It allows hackers to take full control of infected machines and execute arbitrary commands. The trojan monitors activities, harvests information, logs keystrokes, takes screenshots, and captures webcam footage.
It is typically downloaded by Get2 Trojan via spam email attachments containing malicious Excel files. Once installed, it downloads secondary payloads like FlawedGrace, FlawedAmmyy, and Snatch ransomware, making it a serious threat to system security and privacy.
How does Program:Win32/Wacapew.B?ml get installed?
It is typically delivered through spam emails containing malicious attachments disguised as business documents. Common attachment names include hpe_s_hp-inv_02[.]xls, dc123456[.]xls, and business invoice files. Users are tricked into enabling macros, which activates the malicious payload.
The Get2 Trojan then silently roots into the system without manifesting its presence, ensuring persistence. Additionally, pirated software like keygens and cracks commonly contain this trojan as a hidden payload, exploiting users seeking free licensed software alternatives.
What damage can Program:Win32/Wacapew.B?ml cause?
If genuine malware, it enables hackers to remotely control your machine completely. This leads to privacy violations, identity theft, and financial losses. Malicious trojans can disable antivirus software, corrupt Windows registry entries, modify startup programs, and alter core processes.
Post-infection, your machine may experience errors and blue screen crashes. The mswinload0.dll or mswinload[.]dll file uses registry-based persistence mechanisms or application shimming to ensure the trojan remains active. Once infected, your personal information and finances are at severe risk.
Should I assume it's malware or false positive?
If only Windows Defender detects it and other antivirus engines report nothing, it is likely a false positive. However, if multiple security tools detect malware, treat it as genuine. The difference is critical because false positives waste resources while genuine threats require immediate removal.
Since Microsoft fixed the false positive issue in 2019 security intelligence update 1.293.1036.0, modern Windows Defender versions should be more accurate. When in doubt, scan with alternative security software like Microsoft Defender Offline Scanner or professional antivirus tools before concluding the status.
How do I remove Program:Win32/Wacapew.B?ml?
Reboot into Safe Mode with Networking and launch your antivirus software to perform thorough system scans. If Windows Defender quarantined the file, ensure it remains isolated. Run Microsoft Defender's offline scan for comprehensive detection.
Alternative security tools can help remove components that Windows Defender might miss. Note that trojans often hide malicious files using legitimate Windows system names like svchost.exe or Winrmsrv.exe. After removal, use system repair tools to fix any registry corruption or damaged files caused by the infection.
What if Windows Defender keeps detecting it after removal?
Clear the detection history folder within Windows Defender to prevent repeated false alerts from cached scan results. This bug affected Windows versions released in 2019 and later, where Windows Defender repeatedly flagged files even after deletion.
Navigate to the appropriate Windows Defender scan history location and delete detection records. If the issue persists, it indicates either incomplete malware removal or genuine infection still present on the system. Perform additional scans with alternative antivirus software to confirm complete elimination and verify no trojan components remain.
How can I prevent this infection?
Avoid opening email attachments from unknown senders, especially Excel files requesting macro activation. Never enable macros unless absolutely certain of the sender's legitimacy.
Do not download pirated software, keygens, or cracks from unauthorized sources. Keep your operating system and security software updated with latest patches and definitions. Install reliable antivirus software that warns about unwanted programs.
Be cautious of social engineering emails impersonating legitimate companies, and verify sender addresses by hovering over links before clicking. Maintain regular backups of important data.
Should I report this to Microsoft?
If you determine it is a false positive and no other security tools detect malware, report it to Microsoft support for review. Provide details about your Windows version, security intelligence update number, and which other antivirus engines you used for verification.
However, if multiple security tools detect genuine malware, focus on removal rather than reporting. Microsoft uses false positive reports to improve detection accuracy in future security intelligence updates. Reporting helps prevent future users from experiencing unnecessary alerts if the detection truly is erroneous.
Will Fortect remove Program:Win32/Wacapew.B!ml?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Program:Win32/Wacapew.B!ml, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- ProofPoint: TA505 Distributes New SDBbot Remote Access Trojan with Get2 Downloader (read October 5, 2026)
- Microsoft: Change logs for security intelligence update version 1.293.1036.0 (read October 5, 2026)
- VirusTotal: mswinload0.dll (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)
- Microsoft Learn: How Microsoft names malware (read October 13, 2026)