
SendGrid email scam: how to spot it and what to do
SendGrid is a legitimate marketing platform that is used by many website developers to monetize their content. In order to operate successfully, users need to create an account on the official website and register their credentials.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Do it yourself · free Remove SendGrid email scam yourself 4 steps, about 12 minutes, no software needed.
Start the steps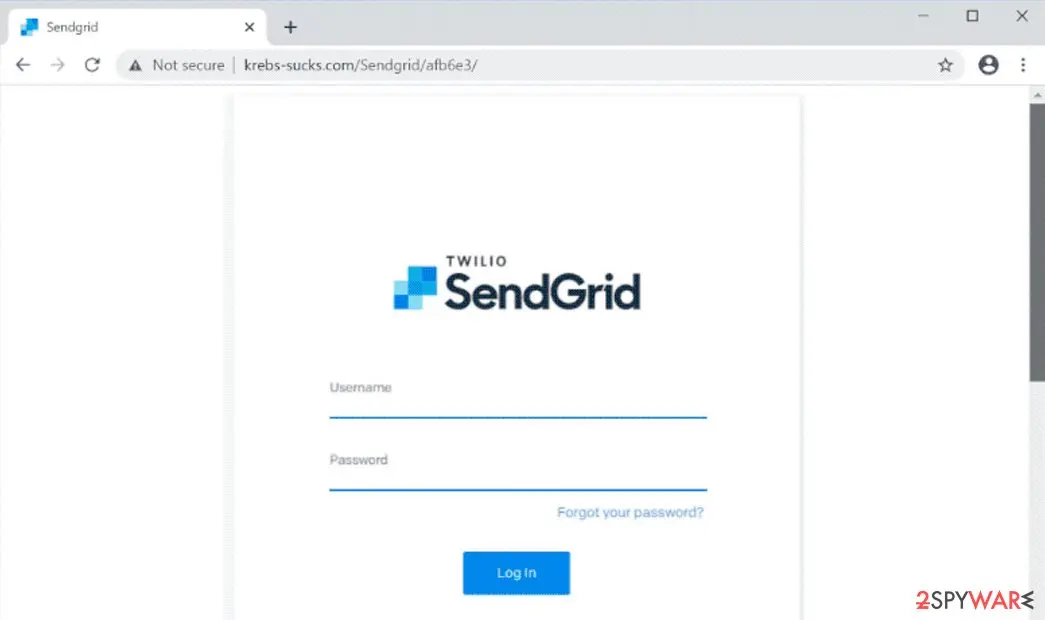
SendGrid email scam: summary
| Distribution | Spam emails sent en masse |
|---|---|
| Name | SendGrid email scam |
| Type | Email scam |
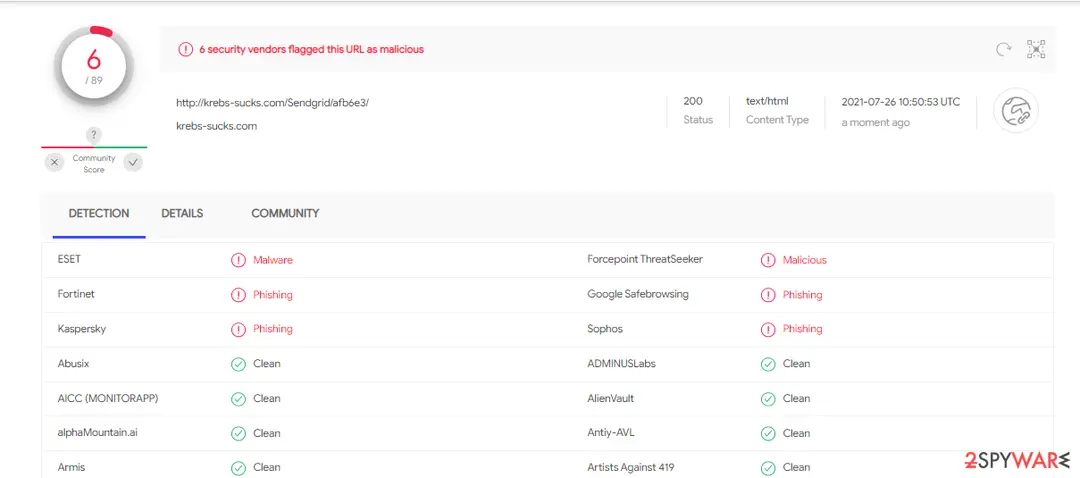
| Related domain | krebs-sucks.com |
| Dangers | Sensitive information leak to cybercriminals, further phishing attacks, identity theft, malware infection, etc. |
| Detection | Always pay attention to the URL address of the domain – it is one of the main giveaways the the sate is fake; no Microsoft detection name is known for this name |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Symptoms | A phishing e-mail asking you to sign in |
|---|---|
| Evidence | 4 write-ups by security sites; details still limited |
| Arrives as | |
| Pretends to be | A well-known company |
| Claim | Your account needs urgent attention |
| Asks for | Your password |
| First seen | 26 July 2021 |
| Facts checked | 6 October 2026 |
What the SendGrid email scam e-mail looks like
This email is to notify you that an invoice has been created for your account at
SendGrid, which is due on Wed, 19 Aug 2020 20:35:05 +0000
The Invoice ID is 009334, and is due for the amount of 89.95 dollars.
If you have a credit card on file with us, this invoice will automatically be billed on Wed, 19 Aug 2020 20:35:05 +0000
You may login anytime to make a manual payment at:
Invoice ID - Login
We are available 24/7. If you have any questions, comments, or concerns, please do not hesitate to contact us.
This is an automated alert for your SendGrid account with the username . Manage your alert settings.
:copyright: SendGrid Inc.
1801 California St.
Suite 500, Denver, CO 80202 USA
Since you're a SendGrind customer, we send you emails from time to time with product updates, webinar invites, onboarding help, and im portant info about your account. You can find out more about how we process personal data in our Priv acy Policy. If you no longer wish to receive these emails, you can unsubscribe.
Is SendGrid email scam dangerous? What the senders want
From our report of Jul 2021 · not reviewed since
The contents of the email and scam techniques
It is not a secret that cybercriminals create scams in order to gain maximum benefit from the attack.
Therefore, malware is commonly used along with phishing. In fact, some of the most prominent malware, such as Moqs ransomware, is spread with the help of fake installers on various torrent sites, where people are tricked into believing that they are downloading a software crack or a pirated game installer.
Yes, phishing has been around for many years, although it became much more sophisticated over the years. Fake emails barely included any text inside and only came with a malicious attachment or a link. Since then, threat actors have managed to come up with new techniques that are more efficient in convincing users that email is harmless.
Names of popular companies, such as Amazon or Microsoft, are commonly used to mislead victims. In this case, SendGrid is used, although the real company has nothing to do with this scam. Within the email, users are shown the following information:
Not only cybercriminals are misusing the name of a well-known marketing company, but they are also trying to create a sense of urgency - this is one of the most used tricks in social engineering attacks. In this case, people are tricked into believing that their accounts will be billed automatically.
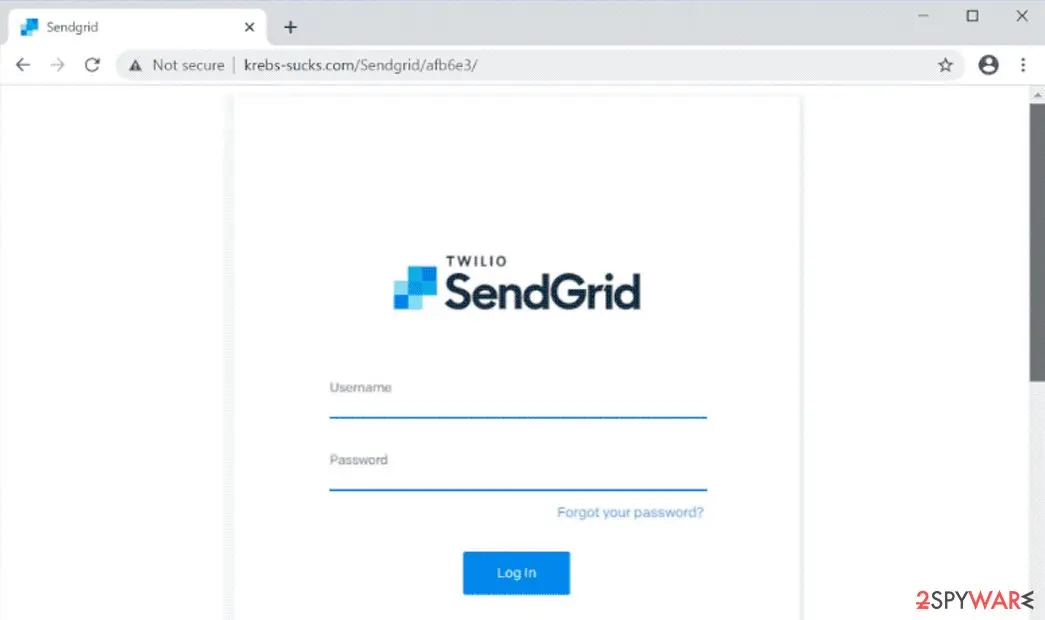
Naturally, many people would not know anything about any invoice, hence trying to log into the account and see what is happening. As soon as they click on a link that apparently should lead to a login page, they will be redirected to the krebs-sucks.com website instead.
Unfortunately, not many users pay close attention to the web address bar, and they might not notice that it is fake. The contents of the page look very convincing, however - there is a company's logo and login field that looks legitimate. However, the SendGrid email scam should not be trusted.
From our report of Jul 2021 · not reviewed since
SendGrid's name used to steal user credentials
SendGrid is a legitimate marketing platform that is used by many website developers to monetize their content.
In order to operate successfully, users need to create an account on the official website and register their credentials. Cybercriminals now came up with an idea to use the company's name to trick already existing users into accessing malicious links that lead to spoofing websites, where they are asked to enter their login information.
Once that is done, malicious actors manage to get user login details without problems and then hijack the official account. This information can be later used to be sold online on hacking forums, for illegitimate purchases, or for further phishing attempts. Without a doubt, this social engineering attack can cause significant damage to the user.
If you have received an email from SendGrid that doesn't seem right - ignore it immediately. If you have already clicked on malicious links, entered your information, or downloaded something on your system, make sure you remediate the situation as per the instructions we provide below.
What to do after the SendGrid email scam e-mail
If you only received the message and clicked nothing, step 3 is all you need.
If you clicked the link or typed anything on the page it opened, do every step, starting with the password.
Step 1: Change the password you typed on the fake page
If you typed a password on the page the SendGrid email scam message opened, assume the sender has it. Go to the real site by typing its address yourself and change the password there, choosing one you have never used.
Change it anywhere else the same password was used, and sign out all other sessions if the service offers it. Any browser on Windows 11 or Windows 10 will do, as long as you do not follow the e-mail's link.
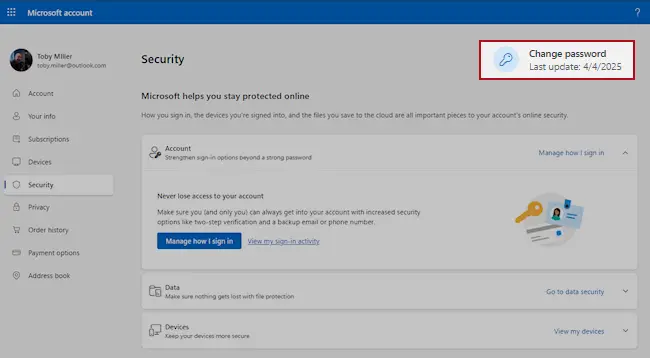
Microsoft account, Security page (account.microsoft.com/security): Change password. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Turn on two-step verification
With two-step verification on, a stolen password alone no longer opens the account, because a sign-in from a new device also needs a code from your phone.
Switch it on for the e-mail account first, then for banking, shopping and social accounts that use that address.
Check the recovery phone, the recovery e-mail and any forwarding rules while you are in the settings, since attackers change them to come back. The pages are the same on Windows 11 and Windows 10.
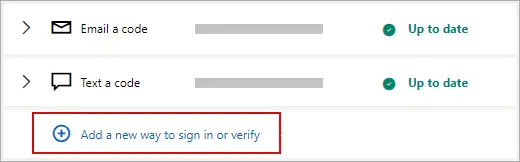
Microsoft account: Manage how I sign in, where two-step verification and the sign-in methods are. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Report the e-mail and delete it
Do not reply and do not click anything else in the message. In Outlook select the e-mail and choose Report > Report phishing; in Gmail open the three-dot menu next to Reply and pick Report phishing.
That trains the filter for everyone on the service, and the message goes to the junk folder. If the e-mail came to a work address, forward it to your IT team as an attachment first.
The steps are the same in the web mail and the mail apps on Windows 11 and Windows 10.
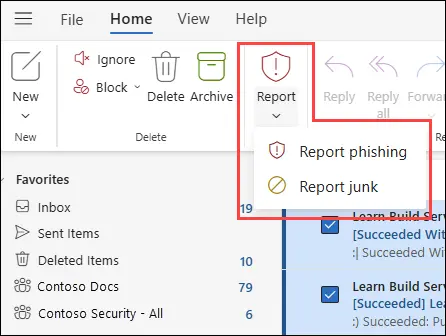
New Outlook for Windows and Outlook on the web: Report > Report phishing. Full procedure with screenshots: Report a phishing e-mail
Step 4: Scan the PC if you opened a file from the message
A fake sign-in page only steals what you type, so most readers can skip this step. If the SendGrid email scam e-mail made you download or open a file, delete it and scan the PC.
In Windows Security > Virus & threat protection > Scan options, run a Full scan and then Microsoft Defender Antivirus (offline scan) > Scan now. The offline scan restarts Windows 11 or Windows 10 and takes about 15 minutes.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Choose a proper web browser and improve your safety with a VPN tool
Online spying has got momentum in recent years and people are getting more and more interested in how to protect their privacy online.
One of the basic means to add a layer of security - choose the most private and secure web browser. Although web browsers can't grant full privacy protection and security, some of them are much better at sandboxing, HTTPS upgrading, active content blocking, tracking blocking, phishing protection, and similar privacy-oriented features.
However, if you want true anonymity, we suggest you employ a powerful VPN - it can encrypt all the traffic that comes and goes out of your computer, preventing tracking completely.
Lost your files? Use data recovery software
While some files located on any computer are replaceable or useless, others can be extremely valuable.
Family photos, work documents, school projects - these are types of files that we don't want to lose. Unfortunately, there are many ways how unexpected data loss can occur:
- power cuts
- Blue Screen of Death errors
- hardware failures
- crypto-malware attack
- even accidental deletion
To ensure that all the files remain intact, you should prepare regular data backups. You can choose cloud-based or physical copies you could restore from later in case of a disaster. If your backups were lost as well or you never bothered to prepare any, can be your only hope to retrieve your invaluable files.
From our report of Jul 2021 · not reviewed since
How to fix your account and leaked password
Once the credentials are entered, they are delivered to cybercriminals.
Even if you realized that the page is fake, your credentials are already leaked, and you should take action immediately. In order to resolve the situation, you should immediately change your login password for every account that it is used on.
If you can no longer access your account, you should contact SendGrid via their official email or a support line and explain what happened - the support staff should help you immediately.
Note that you should never use the same password for multiple accounts and preferably rely on a password manager or browser-offered strong passwords. Enabling two-factor authentication can also be one of the best ways to protect your online account from theft.
From our report of Jul 2021 · not reviewed since
If you downloaded any malicious files...
As previously mentioned, by accessing your credentials, hackers might be able to get into your other accounts.
In fact, they might also connect to your Windows remotely and plant malware manually. Additionally, if you have clicked on malicious links via a phishing email, it might trigger a chain of events where malware would be downloaded and installed automatically without your knowledge.
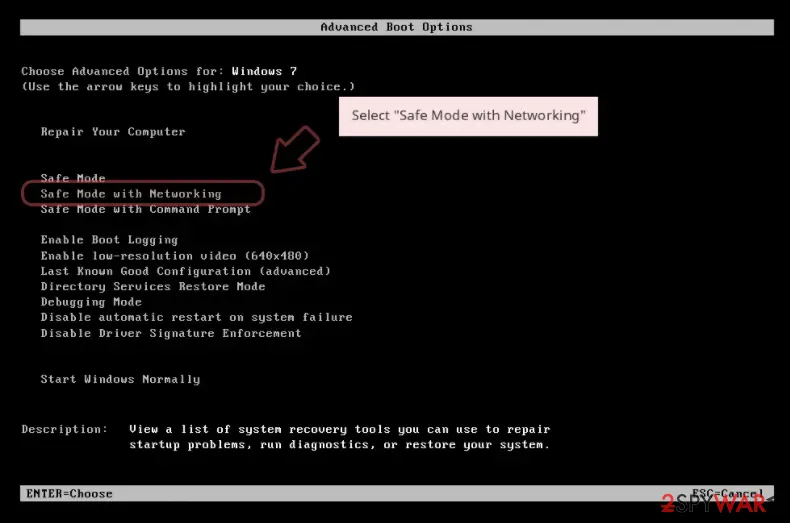
While in most cases, the scan can be performed without problems, sometimes a virus can terminate any processes related to cybersecurity software. In such a case, accessing Safe Mode with Networking and performing a scan from there would resolve the situation:
From our report of Jul 2021 · not reviewed since
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
From our report of Jul 2021 · not reviewed since
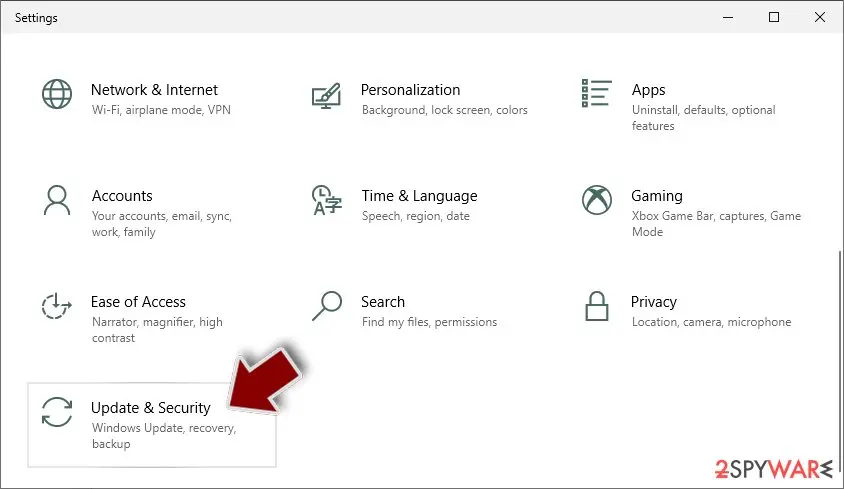
Windows 10 / Windows 8
Once inside the Safe Mode, launch the security app and perform a system-wide scan.
It should be able to find all the malicious files and remove the SendGrid email virus automatically.
It is also important to note that, once the elimination process is complete, it might not be the end of troubles. Malware such as Cometer or ZeroAccess can seriously damage Windows system files, making the OS crash or prevent normal functions from working correctly (such as the Task Manager, for example).
- Right-click on Start button and select Settings.
- On the left side of the window, pick Recovery.
- Click Restart now.
- Select Troubleshoot.
- Go to Advanced options.
- Select Startup Settings.
- Click Restart.
- Press 5 or click 5) Enable Safe Mode with Networking.
- Download installer
- Click on ReimageRepair.exe
- If User Account Control (UAC) shows up, select Yes
- Press Install and wait till the program finishes the installation process
- The analysis of your machine will begin immediately
- Once complete, check the results - they will be listed in the Summary
- You can now click on each of the issues and fix them manually
Questions about SendGrid email scam
Does getting "This email is to notify you that an invoice has been created…" mean my account was compromised?
Not by itself. Phishing waves are sent to long lists of addresses collected from old breaches, websites and guessing, and the sender does not know whether you even have the account the message mentions. Getting "This email is to notify you that an invoice has been created…" only means your address is on such a list.
It becomes a problem if you sign in through the link. To be sure, open the real service from a bookmark and check recent activity and security alerts. If you see nothing unusual and you did not type your password into the fake page, your account is fine.
I typed my password after "This email is to notify you that an invoice has been created…". What now?
Act within the hour. From another device, open the real site of the account the message "This email is to notify you that an invoice has been created…" imitated and change the password.
If the same password is used anywhere else, change it there too. Sign out of all other sessions, check the recovery e-mail and phone number, and look for mail forwarding rules or filters you did not create.
Then turn on two-step verification with an authenticator app or a passkey. If the fake page also asked for a card number or a bank login, call your bank and ask them to block the card. Finally, report the e-mail so others are warned.
Could SendGrid email scam be a genuine message?
We checked it, and it is not. A well-known company is only the costume. The message exists to get your password, and real companies handle that inside your account, after you sign in normally, not through links, attachments or phone numbers in a message you did not expect.
Scammers copy logos and footers perfectly, so the design proves nothing. The sender address, the link target and the request are the reliable signs, and all three point to a scam here. Delete it, and if you are worried, check your account directly.
Why does SendGrid email scam say that your account needs urgent attention?
Because that story works. A problem that needs fixing, a deadline and a simple solution make people act before they check.
The claim that your account needs urgent attention is the same for everyone who received SendGrid email scam; it was written once and sent in bulk. Nothing about your own situation triggered it.
If you are unsure, look at the real account or service the normal way, without using the message. The claim will not be there, which settles the question. Then report the message.
What does SendGrid email scam want from me?
In the end, your password. Everything else in SendGrid email scam, from the logo to the deadline, is there to get you to that point without stopping to think.
Knowing the goal helps you judge your risk. If you did not give it, you lost nothing and can delete the message. If you did, the steps in this guide are ordered by what you handed over:
- passwords first
- then card and bank details
- then documents and anything you installed
- ran
Act on the highest item on that list first.
How do I contact the real a well-known company?
Not through anything in SendGrid email scam. Type the official website address into the browser yourself, use the app you already have, or use the phone number printed on your card, contract or a previous genuine invoice.
Search results can be risky too, because scammers buy ads for support numbers. Once you reach the real a well-known company, you can ask whether there is any problem with your account and report the scam message; many companies have a dedicated address for phishing reports on their security page.
What is the single best habit against scams like this?
Never act on a message through the message itself. If something claims to be from a well-known company and asks you to sign in, pay, call or open a file, close it and go to the service the way you always do:
- a bookmark
- the app
- the number on your card
Real problems will be visible there. This one habit defeats almost every phishing, invoice, delivery and account-suspension scam, regardless of how convincing the design is, because the scammers can copy the look but not the real account.
Should I scan my PC after SendGrid email scam?
Yes, it is a quick way to rule out one possible cause. Open Windows Security and run a full scan; it takes about half an hour.
If it finds nothing and there are no unknown programs or extensions, the account problem behind an e-mail with the subject "This email is to notify you that an invoice has been created…" most likely started with a leaked or phished password.
If it finds a stealer or trojan, remove it first, then change your passwords from another device, then sign out of all sessions, because stolen cookies keep working until you do.
Is it worth reporting a scam if I lost nothing?
Yes. Reports from people who did not fall for SendGrid email scam are how blocklists, mail filters and hosting companies find new scam pages quickly, often before most recipients open the message. Reporting the message as phishing in your mail app is enough for most people.
If the message impersonates a company, its security or abuse team usually accepts forwarded copies too. Police reports matter mainly when money or documents were lost, but national fraud centres also collect reports without losses to spot campaigns.
Will Fortect remove SendGrid email scam?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For SendGrid email scam, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Imperva: Phishing attacks (read October 6, 2026)
- ZDNet: Torrent websites infect 12 million users a month with malware (read October 6, 2026)
- NIST: Back to Basics: What's multi-factor authentication - and why should I care? (read October 6, 2026)
- FTC: How to recognize and avoid phishing scams (read October 6, 2026)
- CISA: Recognize and report phishing (read October 6, 2026)