
Trojan.gen.npe.2: what it is and how to remove it
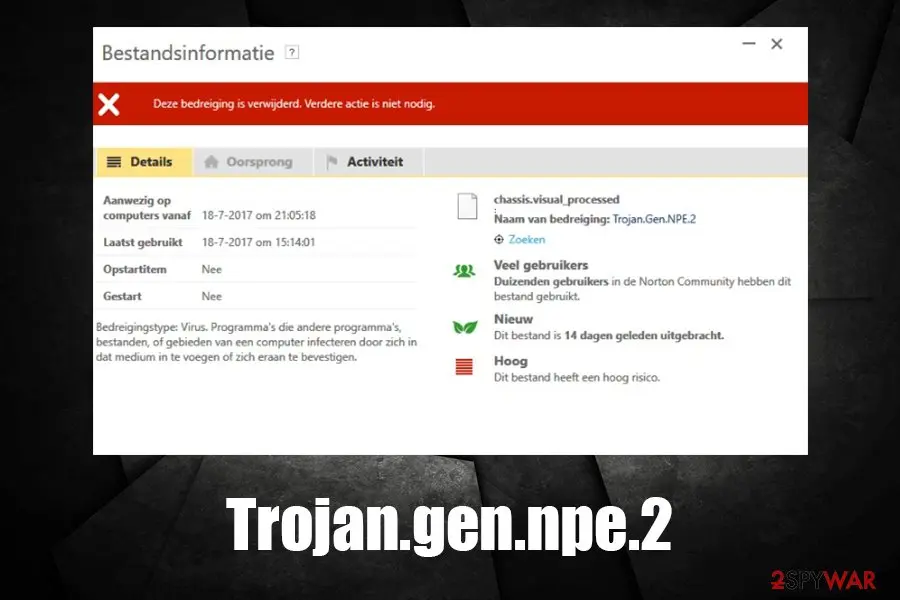
Trojan.gen.npe.2 is a heuristic detection name used by security software, particularly Symantec, for various malware types including trojans, info-stealers, and cryptominers. This generic detection can sometimes indicate false positives, requiring verification before taking action.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Programs like Trojan.gen.npe.2 usually arrive in groups; a free scan lists the companions that are easy to miss.
Do it yourself · free Remove Trojan.gen.npe.2 yourself 5 steps, about 15 minutes, no software needed.
Start the steps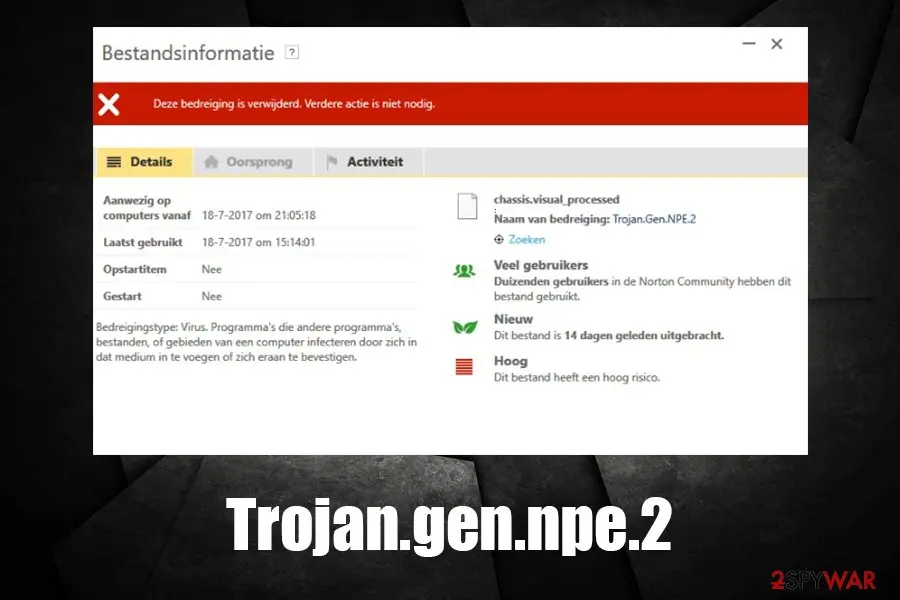
Trojan.gen.npe.2: summary
| Damage | Installation of other malware, sensitive data disclosure to cybercriminals, financial loss, identity theft, etc. |
|---|---|
| Name | Trojan.gen.npe.2 |
| Type | Malware, false-positive |
| Infiltration | The infection might occur in various ways, as Trojans are malicious apps that pretend to be legitimate executables. These can be downloaded after being tricked by a scam, fake update, or other phishing techniques. Besides, malicious spam email attachments are also often used to proliferate Trojans |
| Symptoms | Symptoms can greatly vary, as Trojans are programmed to perform different actions on the infected system. In most cases, stealthy malware will display no symptoms, although users can notice suspicious files running in the background, application crashes, mouse movements, etc. |
| Termination | Run a full system scan with anti-malware software; if a detection is a false-positive, add it to exception list |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 5 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Distribution | Not recorded in the old report |
| Evidence | 4 write-ups by security sites; details still limited |
| First seen | 26 March 2020 |
| Facts checked | 5 October 2026 |
What Trojan.gen.npe.2 does on an infected PC
From our report of Mar 2020 · not reviewed since
Trojan.gen.npe.2 - a computer threat that should not be ignored
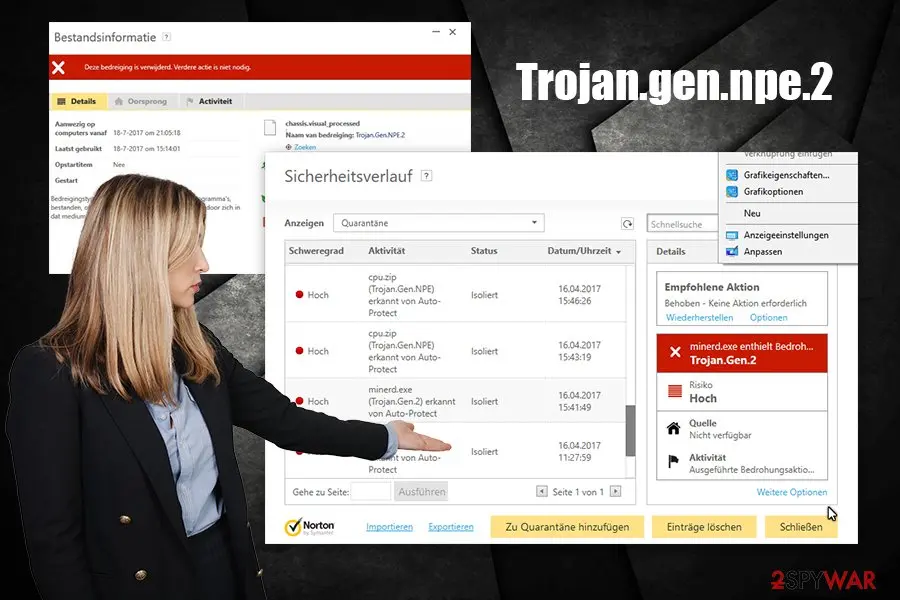
Trojan.gen.npe.2 is a heuristic detection name that can be used by security software providers, especially Symantec.
Because the infection name is generic, there might be a variety of different malware that is hiding behind it, including Trojans, info-stealers, or cryptominers. Due to this, the symptoms of the infection may vary greatly, although most of the malware behind Trojan.gen.npe.2 is created to operate silently in the background.
Besides its malicious properties, Trojan.gen.npe.2 virus is also known to be a false-positive, and there were instances where legitimate tools like Wordpress or Windows files were flagged. This happens when a non-malicious file performs Windows system changes in order to operate and resembles malware. In case your security software flagged the infection, you should never ignore it and investigate first.
If Trojan.gen.npe.2 is genuine malware, it is usually a Trojan - a type of malicious software designed to perform a different variety of functions on the infected systems.
These threats are spread with the help of deception - users typically believe that they are launching a legitimate file on their system (such as pirated program installer). In some cases, Trojan.gen.npe.2 Trojan might also deliver the application, but also run malicious activities in the background.
However, the presence of Trojan.gen.npe.2 malware might not be so evident, especially if no security software is used. Nevertheless, users might encounter the following symptoms:
Since Trojan.gen.npe.2 can represent a variety of different threats, the goal of the infection might also vary. For example, malware like AZORult is developed to steal sensitive data in the background, with the help of a variety of functions, including keylogging, screenshot taking, etc. Unfortunately, such a virus usually operates silently, complicating Trojan.gen.npe.2 removal if no security software is used.
Personal information is among the most desired attributes in the cybercriminal world - the data can be sold on the dark web for profit or leveraged to steal money from bank accounts and similar. Without a doubt, such activity can harm the infected users greatly, resulting in vast financial losses, as well as identity theft.
Nevertheless, Trojan.gen.npe.2 might have other goals, including cryptomining. This process helps cybercriminals to acquire digital currency, such as Bitcoin or Monero, by using a botnet of infected computers. In such a case, the infected users could experience lag, software crashes, OS reboots, high usage of hardware (fan in particular), and high CPU/GPU usage.
Additionally, victims might also expect large electricity bills due to excessive usage of computing power. It is important to note that Trojan.gen.npe.2 malware may damage Windows system files as well - you can repair this with the help of tools like later, however.
If that did not convince you to remove Trojan.gen.npe.2, you should also be aware that the threat can proliferate other malware, such as ransomware. This devastating computer infection renders all local and networked files useless and then asks for a ransom payment for a decryption tool.
In this case, users may lose their data permanently, along with the money, as cybercriminals not always keep their promises and deliver the required decryptor.
Keep in mind that Trojan.gen.npe.2 removal might compromise a useful file or a program, so you should be aware that the detection can also mean a false positive. If you are completely sure that the detection is an FP, you should add an exclusion on the security tool. The best way to determine whether Trojan.gen.npe.2 detection is actually correct is by scanning the file in question with another security tool.
- Software crashes
- System reboots
- Errors and BSODs
- Unsolicited mouse movements
- High CPU usage
- Unknown files running in the background, etc.
From our report of Mar 2020 · not reviewed since
Avoid Trojan and other malware by being careful online
Unfortunately, most users do not take cybersecurity seriously, and act careless when using their computers.
For example, downloading software cracks or pirated software installers is one of the leading causes for malware infections, including Djvu ransomware, which infects hundreds of users each day. Nevertheless, many still risk their online security and computer safety despite knowing about the risks.
Unfortunately, employing anti-malware software is not enough to protect you from all harm online. Cybercriminals are sophisticated individuals and they are always looking for ways how to bypass the implemented security measures and prevent anti-malware tools from detecting viruses. Therefore, there are several other things you should keep in mind, including:
- Update your operating system and installed programs on a regular basis (as soon as patches are released);
- Protect all your accounts with strong passwords and use two-factor authentication where possible;
- When using Remote Desktop, employ a VPN and never use a default TCP/UDP port;
- Never allow spam email attachments to run macro function ("Allow Content") and do not click on suspicious links inside;
- Backup your files regularly;
- Do not download software cracks, loaders, keygens, and other suspicious tools.
From our report of Mar 2020 · not reviewed since
More from our earlier report on Trojan.gen.npe.2
- Malware can weaken the defenses of the Windows operating system and even corrupt some files.
- To recover from this, the affected users can employ after the virus is eliminated
How to remove Trojan.gen.npe.2
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to Trojan.gen.npe.2 or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 2: Remove it from startup
Whatever Trojan.gen.npe.2 installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Mar 2020 · not reviewed since
Trojan.gen.npe.2 removal instructions
You should not remove Trojan.gen.npe.2 if the detection is a false positive, as it may stop a legitimate application to stop working.
If you are not sure whether the file is actually malicious, you should upload it to services like Virus Total for analysis, or scan with another anti-malware tool. Once you are sure that the detection is not a false-positive, you can hurry up with Trojan.gen.npe.2 removal. In some cases, this process might be hindered by malware's functionality - you can bypass that by accessing Safe Mode with Networking.
However, everything becomes a bit more complicated for those that do not use anti-virus software and are not aware of Trojan.gen.npe.2 virus' presence. Unfortunately, as mentioned above, Trojans rarely show any symptoms, so detecting the infecting is hardly possible without security software. Thus, ensure you are running anti-malware software at all times and perform regular scans.
[GI=method-1]In case Trojan.gen.npe.2 is tampering with your security software, access Safe Mode with Networking:
After removal: passwords, accounts and prevention
Secure your accounts after the clean-up
Assume that whatever was saved in the browsers on this PC while the PC showed trojan.gen.npe.2 in the list of installed apps has been copied:
- passwords
- cookies
- autofill data
Work from a clean device, or from this PC once the offline scan finds nothing.
Start with your main e-mail account, because it can reset everything else, then banking and payment, then social and gaming accounts. Change each password, sign out of all sessions and turn on two-step verification: Turn on two-step verification / secure a hacked account.
The full order, including crypto wallets and card replacement, is in securing your accounts after malware.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
Questions about Trojan.gen.npe.2
What does Trojan.gen.npe.2 detection mean?
Trojan.gen.npe.2 is a heuristic detection name used by security software providers, especially Symantec, to identify suspicious files exhibiting malware-like behavior. Because this detection name is generic, it can represent a variety of different malware types hiding behind it, including trojans, info-stealers, or cryptominers.
The infection name doesn't specify what exact threat you're dealing with—only that something detected exhibits characteristics the antivirus recognizes as malicious. Different malware instances detected under this name may have completely different functions and impacts on your system.
Due to this generic nature, your security software cannot tell you precisely what the threat does, only that it needs investigation and possible removal.
Is Trojan.gen.npe.2 definitely a virus?
Trojan.gen.npe.2 is known to be a false-positive in some cases, meaning legitimate tools or Windows system files have been flagged as malicious. There were instances where legitimate tools like WordPress or Windows files were incorrectly flagged.
This happens when non-malicious files perform Windows system changes to operate normally, resembling patterns that malware exhibits. If your security software flagged this detection, you should never ignore it but investigate first before taking action.
The best approach is scanning the flagged file with another security tool to compare their findings. If multiple security tools confirm the threat, it's almost certainly malicious. If only one tool flags it and others clear it, it's likely a false-positive requiring exclusion rather than removal.
How can I determine if this detection is real?
Verify whether Trojan.gen.npe.2 is genuine malware or a false-positive by scanning the flagged file with multiple security tools. Upload the suspicious file to services like Virus Total for analysis from dozens of security engines simultaneously.
If the majority of security tools flag it as malicious, the detection is almost certainly correct and requires removal. If only one or two tools flag it while most others declare it clean, it's likely a false-positive, and you should add the file to your antivirus exceptions list rather than deleting it.
Never remove files you're completely sure are legitimate, as this may stop legitimate applications from working. Taking time to verify prevents accidentally deleting essential system files or legitimate programs.
What symptoms can Trojan.gen.npe.2 cause?
Symptoms vary greatly depending on which specific malware is hiding behind the Trojan.gen.npe.2 detection name. Most malware behind this detection is created to operate silently in the background, displaying no obvious symptoms. However, you might encounter suspicious files running in the background, application crashes, mouse movements you didn't initiate, unexplained system slowdowns, or other suspicious activities.
If the underlying malware is a cryptominer, you'll see high CPU and GPU usage, significant system lag, fan running at full capacity, and elevated electricity bills. If it's an info-stealer like AZORult, the malware operates completely silently while stealing sensitive data through keylogging and screenshot capture. Without security software detecting it, you might never know the infection is present.
What can different Trojan.gen.npe.2 variants do?
Different malware types detected under this name serve various purposes. Some variants are developed to steal sensitive data in the background, including banking credentials, personal information, and other confidential details that can be sold or used for identity theft.
Others operate as cryptominers, hijacking your computer resources to generate cryptocurrency for cybercriminals. Some variants open backdoors for remote hackers to gain complete control of your system. Ransomware detected under this name can encrypt your files and demand ransom payment for the decryption key.
The diversity of threats hidden behind this generic detection name means the specific danger depends on which variant has infected your system—ranging from data theft to complete system compromise.
How does Trojan.gen.npe.2 get on my computer?
Trojan.gen.npe.2 infections typically arrive through deception methods where users believe they're launching legitimate files. Pirated program installers are common infection vectors—users download what they think is legitimate software from illegal sources. Malicious spam email attachments are frequently used, disguised as legitimate documents.
Fake updates claiming your software is outdated trick you into installing malware. Exploit kits silently download malware when you visit compromised websites. Malvertising—malicious advertisements—automatically download infections when clicked.
In all cases, trojans depend on tricking users into either explicitly launching a malicious file or inadvertently visiting a compromised site. If you lack robust security protection, the malware installs successfully and begins its malicious operations immediately.
Can I be safe from Trojan.gen.npe.2 after removal?
After confirming the detection is genuine and removing the malware, you need to assess and repair any damage caused to your operating system. Trojan.gen.npe.2 malware may have damaged Windows system files, modified registry entries, or corrupted various program functions.
Security tools cannot fully repair this damage during removal—you need separate recovery tools to fix corrupted files and system stability issues. After malware removal, your system may still experience performance problems until these repairs are complete. To prevent reinfection, maintain antivirus software at all times with regular scans.
Never download software from untrusted sources. Be extremely cautious with email attachments and unsolicited update notifications. Keep your operating system and programs updated with security patches to close vulnerabilities malware exploits.
What if my antivirus keeps detecting Trojan.gen.npe.2?
If your security software repeatedly detects Trojan.gen.npe.2 after you believe it's been removed, the malware may be reinfecting your system or the initial removal was incomplete. Access Safe Mode with Networking to run security scans when the malware cannot interfere with removal processes.
Download the latest virus definition updates for your security software before scanning. Run a full system scan using these updated definitions. Try alternative security tools if your primary antivirus cannot remove it completely—different products may have better detection signatures for this particular threat.
If the detection persists after multiple removal attempts and you're confident the file is malicious, consider restoring your system from a backup made before the infection occurred. However, if no security tools can find the file anymore, the detection may be a false-positive requiring exclusion.
Will Fortect remove Trojan.gen.npe.2?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Trojan.gen.npe.2, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- How-To Geek: Everything You Need To Know About the Blue Screen of Death (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)
- Microsoft Learn: How Microsoft names malware (read October 5, 2026)