
Trojan.Multi.BroSubsc.gen: what the Kaspersky alert means and how to remove it
Trojan.Multi.BroSubsc.gen is the verdict Kaspersky gives when a website that is allowed to show advertising notifications is found in your browser's settings; it is not a program you can uninstall. Run Kaspersky's Advanced Disinfection, then block or remove every unknown site in each browser's notification list.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Clicked a notification from the site's address and installed something? A free scan checks programs and browsers in one pass.
Do it yourself · free Remove Trojan.Multi.BroSubsc.gen yourself 2 steps, about 6 minutes, no software needed.
Trojan.Multi.BroSubsc.gen: summary
| Type | A Kaspersky verdict for a website that is allowed to show advertising notifications in your browser; not a program you can uninstall |
|---|---|
| Risk | Low to medium: ads and the pages they open; no case we read shows stolen passwords, ransomware or a backdoor |
| Symptoms | A Kaspersky alert with Object: System Memory, often the only sign; advertising notifications, even with the browser closed |
| How to get rid of it | Update Kaspersky, run a Quick scan and Advanced Disinfection with a restart; block or remove every unknown site in each browser's notification list; remove unknown extensions |
| Our check (6 October 2026) | No PC or site test: we read Kaspersky's threat page, its support post, a 2019 Habr post and four forum cases. A quiet scan clears nothing |
| Running since | Kaspersky's detect date is 2 February 2019; our guide first appeared on 4 November 2020 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 12 more facts
| Detection | Kaspersky: Trojan.Multi.BroSubsc.gen (class Trojan, platform Multi). No Microsoft detection name is known: a notification permission in a browser is not a file, so Microsoft Defender has nothing to name unless a program was installed from the ads |
|---|---|
| Most attacked users | Russia 44.48%, then Brazil, India, Kazakhstan and Ukraine, all under 4% (Kaspersky Threats) |
| Not to be confused with | Ransomware, a password stealer or a Task Manager blocker; the sources do not support those readings |
| Name | Trojan.Multi.BroSubsc.gen |
| Evidence | Reports from affected users; details still limited |
| Ads shown as | Desktop notifications |
| Browsers | Chrome, Edge and Firefox |
| Installed on the PC | Nothing; a browser notification permission only |
| First seen | 4 November 2020 |
| Distribution | Typically redirects from streaming and download sites, fake "click Allow" checks and fake video players |
| Damage | Notification ads that lead to scam pages, fake virus alerts and unwanted downloads |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against Kaspersky's threat page for Trojan.Multi.BroSubsc, its support forum post of 21 September 2021, four forum threads from 2021 and 2023, a Kaspersky support article, a 2019 Habr post quoting Kaspersky support, and the current help pages of Google, Microsoft, Mozilla and Apple. We ran no scanner and opened no site, and the removal steps were not tried on a live case.
What Trojan.Multi.BroSubsc.gen is, and what it is not
Trojan.Multi.BroSubsc.gen is the verdict Kaspersky gives when it finds, in the settings of a browser, a website that is allowed to show you advertising notifications. It is not a program you installed and cannot uninstall. Kaspersky's threat page says the family is installed on browsers deceptively after a visit to fraudulent or advertising resources, and that it shows advertising messages even when the browser is inactive.
- 1
You press Allow on a prompt
A page asks whether it may show notifications and disguises the question as a check, a video player or a download. Kaspersky's support post of 21 September 2021 puts it this way: if you agree to accept notifications from a site, the browser settings end up holding the unwanted resource. Chrome's help page says the browser asks whenever a site, app or extension wants to send notifications, and the answer is kept until you change it (Chrome Help).
- 2
The browser keeps the site in its settings
The site's address stays in the browser's list of allowed senders. Microsoft's page for Edge says notifications for an allowed site still appear when the browser is closed (Microsoft Support); Apple says the same for Safari on a Mac. This is the mechanism behind Kaspersky's line about ads with an inactive browser.
- 3
Kaspersky reads those settings
Support told users in February 2019, in a text a user copied to Habr, that the verdict is given while checking autorun objects, when the settings of a supported browser (then Chrome, Yandex, Opera and Vivaldi) hold a URL that Kaspersky detects as the source of these ad notifications. The alert in our pictures names the object as System Memory; we found no source that explains that label.
- 4
Treating it flips Allow to Block
According to the same text, treatment changes the status of the detected URLs from Allow to Block. The Habr post says the window offered to treat by restarting the PC and that, with some probability, the alert then came back, round and round. That fits a list that holds more than one such site.
- Shown by
- Kaspersky products: the cases we read name Free Antivirus, Endpoint Security for Windows and the Virus Removal Tool
- Kaspersky's labels
- Class Trojan, platform Multi, parent class TrojWare; detect date 2 February 2019 on its threat page
- What it points at
- A website allowed to send notifications in your browser; the detection is about a setting, not a file we could name
- What it is not
- Not ransomware: a forum helper wrote on 29 June 2023 that it is definitely not a ransomware issue. In another case the helpers said the evidence pointed to adware
- How to stop it
- Block or remove the sites in your browser's notification list, and let Kaspersky run its Advanced Disinfection with a restart
- Spelling
- Kaspersky writes BroSubsc. Our 2020 guide wrote Brosubsc, and one of its pictures is named brosubc
Our 2020 guide called this a trojan that deactivates Task Manager, steals passwords and installs more malware. None of that is in the Kaspersky pages and forum cases we read. The chapters below say, claim by claim, what held up and what did not.
Is Trojan.Multi.BroSubsc.gen dangerous?
How to read the name and the alert, part by part
Kaspersky does not publish a page that explains each part of the name, so the right-hand column says where each reading comes from. Where it is our reading, it says so.
| Part | What it means | Where the meaning comes from |
|---|---|---|
| Trojan | Kaspersky's behaviour class. Its class text describes programs that spy on the user, but the family text for BroSubsc speaks only of advertising messages | Kaspersky threat page; that the class label is a poor fit for this family is our reading |
| Multi | The platform label: not tied to one operating system. Kaspersky gives no description for it | Kaspersky threat page ("No platform description") |
| BroSubsc | The family name. Kaspersky does not spell it out; "Bro" for browser and "Subsc" for subscription would fit how the family works, but that is our reading | Not defined in the sources we read |
| gen | A generic rule that covers many sites and cases, not one fixed file | Our reading of the usual naming; not defined on the pages we found |
| Object: System Memory | The place the product reports the detection. We found no source that says what is held in memory in this case | The alert in our 2020 pictures and in the Endpoint Security log a forum user posted on 11 May 2021 |
| Resolve button | The button in the Notification Center that starts the treatment | Our 2020 pictures show it beside the alert |
Search for the whole string you were shown. A detection named Trojan.Multi.Accesstr.ash, which appeared in the same forum log for a different PC, is a different alert and needs its own look.
What we checked on 6 October 2026, and what we could not
There is no website to open and no file to run, because the verdict names a permission inside your own browser and the sites behind it differ from PC to PC. We read Kaspersky's threat page, its support post, a 2019 Habr post that quotes Kaspersky support, a Kaspersky support article and four forum cases. We ran no scanner and opened no site.
Our reading of the sources, 6 October 2026
- The name is a real vendor detectionKaspersky's threat page lists Trojan.Multi.BroSubsc with a detect date of 2 February 2019, the class Trojan, the platform Multi and a list of ten countries.
- The vendor explains what triggers itThe same explanation appears in 2019 (support text copied to Habr) and in a post of 21 September 2021 on Kaspersky's own forum: browser settings that hold a URL giving out advertising notifications.
- Which sites are on your PCNot knowable from here. The alert in our pictures shows the name and the object System Memory, and no web address. Only your browser's list shows the sites.
- Harm beyond adsNone shown in the cases we read. A 2023 user had never seen an ad and asked whether it gave backdoor access; the helpers answered that Kaspersky and the AdwCleaner log pointed to adware. That is two forum members' view, not a Kaspersky statement.
- Only one vendorThe 2023 user wrote that he could find no other discussion of whether the name was a false positive. We found no other security vendor's name for it, and a helper said only Kaspersky's virus lab can confirm or deny a false positive.
- A clean rescanDoes not clear the browser. A helper wrote in January 2023 that a Kaspersky scan with no detection means a clean system, but the check only knows the URLs Kaspersky lists. In a 2021 case it returned once after the browser was deleted and reinstalled.
A permission to remove, not proof of a hacked PC On the sources we read, this verdict is about advertising notifications, and the people who answered called it adware. We tested no PC and cannot say what caused your alert. Look at every site in your browser's notification list, not only the ones Kaspersky changed to Block, and treat a page you typed a password on as a separate matter.
The detection from 2019 to 2026
Our guide dates from 4 November 2020. Its three pictures all show the same Kaspersky alert, so the history below uses two of them where our own guide enters the story, and the pictures are not screenshots we took.
2 February 2019
Kaspersky lists the family
The threat page gives the detect date 02/02/2019, the class Trojan, the platform Multi and this description: malware of this family is installed on browsers deceptively after the user visits fraudulent or advertising resources, and it displays advertising messages even if a browser is inactive. It gives no sample hashes and no date for its country statistics.
13 February 2019
A signature is added
The Habr post below quotes Kaspersky support saying the signature in question was added on 13 February 2019. That is eleven days after the threat page's date, and we cannot tell how the two relate.
28 February 2019
A user explains the alert on Habr
A Habr user wrote that he was swamped with reports from Kaspersky Free Antivirus users who saw a window about infection with this name, which offered treatment by restart and then, with some probability, appeared again, round and round. He copied support's answer: users complain of advertising notifications after rash clicks on dubious sites, and the verdict appears when browser settings hold detected URLs. He listed where to switch notifications off in Chrome, Opera and Vivaldi, and for Firefox the setting dom.webnotifications.enabled in about:config, which he credited to a commenter. The page shows 189 thousand readers.
4 November 2020
Our first guide
We published it as a trojan that is mostly active in Russia and drops advertising content even when the browser is disabled. The first half of that is Kaspersky's own country list; the guide then added Task Manager, registry and password claims that no source we read supports.
From our 2020 guide: the Kaspersky alert as it looked then. The wooden horse and the woman are stock art; only the alert window shows the detection, and it is not a screenshot we took. 26 March 2021
An administrator asks why it is hard to remove
A user of Kaspersky Endpoint Security for Windows 11.0.0.6499 wrote that the report said the path was System memory and the action N/A, that deleting and reinstalling the browser seemed to help but in one case it came back, and asked whether it could be a false positive. Replies said to deny all notifications or allow only chosen sites, to check the Allowed box at chrome://settings/content/notifications and to remove suspicious sites; another wrote that Advanced Disinfection makes it go away. The false positive question got no answer.
1 April 2021
Our guide was last edited
The old page has not changed in its claims since. Our backlink data lists 3 referring domains and 8 links to it, and we have no search volume for the name.
From our 2020 guide: the same alert with a red warning circle and a horse silhouette added. Illustration, not a screenshot we took. 11 May 2021
A log shows the fields
In the same thread a Kaspersky Endpoint Security log was posted. For the BroSubsc detection it shows type Trojan, threat level Exactly, precision High, object type File, object name System Memory and the reason Expert analysis. A second PC in the log shows Trojan.Multi.Accesstr.ash with the reason Automatic analysis. We read Expert analysis as a rule written by an analyst; Kaspersky does not say so.
21 September 2021
Kaspersky posts its removal guide
A forum post titled What to do if Kaspersky detects trojan.multi.brosubsc.gen gives the explanation above and two steps: update the databases, run a Quick scan and then Advanced Disinfection with a Windows restart; and check the browser's notifications, subscriptions, permissions and extensions, resetting or disabling anything suspicious. The thread from March 2021 was closed with a link to it.
16 to 17 January 2023
Detected twice
A user whose product treated it twice found that only a news site had notifications allowed, switched them off in Chrome and ran a full scan with nothing found. He asked whether the PC was clean. A helper pointed to the 2021 post and later to Kaspersky's adware article, and wrote that if he had followed them and Kaspersky reported nothing, it was safe to assume the system was clean; for doubts he should contact Kaspersky Support. The thread is marked solved.
16 February 2023
Kaspersky's adware article is updated
Support article 10319 tells readers to update databases, run a Full Scan, remove the program from Programs and Features if one brought the ads, and remove the extension. For Chrome it adds a check of chrome://settings/content/notifications: an unknown site in the Allow tab is removed with the Other options button.
20 June to 18 July 2023
A Virus Removal Tool user asks if it is a trojan
He had never seen an unwanted ad and asked about backdoor access. A reader guessed ransomware; a helper replied that ransomware encrypts files and that this was definitely not that. An AdwCleaner scan log he posted listed potentially unwanted entries and adware, and the helper said Kaspersky Threats and AdwCleaner pointed to adware. The thread ends with a request for the full detection window.
Across more than seven years the explanation has not changed: a browser permission for a site that sends ads. What changed is the number of people who ask whether the word trojan means they are infected.
Where Kaspersky sees it most
The old guide said the trojan is mostly active in Russia. Kaspersky's page supports that, and gives the share of attacked users by country; it gives no date and no user count.
| Rank | Country | Share of attacked users |
|---|---|---|
| 1 | Russian Federation | 44.48% |
| 2 | Brazil | 3.69% |
| 3 | India | 3.36% |
| 4 | Kazakhstan | 2.44% |
| 5 | Ukraine | 2.36% |
| 6 | Mexico | 2.15% |
| 7 | Algeria | 2.09% |
| 8 | Saudi Arabia | 1.77% |
| 9 | France | 1.72% |
| 10 | Vietnam | 1.66% |
The old guide called these countries victims. Kaspersky's wording is attacked users, which means users whose product reported the detection; it does not say how many lost money or data, and the cases we read show none who did.
What it can cost you
The old guide listed stolen passwords, drained bank accounts and ransomware. No Kaspersky page or forum case we read ties the detection to any of them. The real cost is what the ad pages try to get from you.
- Medium
Ads that reach you outside the browser window
Kaspersky says the family displays advertising messages even when the browser is inactive, and Microsoft says site notifications appear with Edge closed. They look like system alerts and invite a click.
- Medium
What the ad pages offer
A notification opens a page, and a page can offer a fake cleaner, a survey, a prize or a download. That choice is where money and data are lost, and it is not specific to this name.
- Low
Stolen passwords and bank access
The old guide said the trojan steals saved passwords and uses them on bank and social accounts. We found no source for this in the Kaspersky family text or in four forum cases. If you typed a password into a page a notice opened, treat that password as exposed.
- Low
More malware installed by it
The old guide said trojans pass on miners and ransomware. The only helpers who answered the question said this detection was not ransomware and pointed to adware. We know of no case where this detection installed other software.
- Low
A repeating alert
The 2019 Habr post describes a window that offers treatment by restart and then returns. It is tiring rather than harmful, and it stops when every ad-sending site has been removed from the browser.
What you may notice, and what the cases show
The old guide said the trojan shows very few symptoms, then listed a slow PC and a high CPU load. The cases show a different picture: the alert is often the only sign.
| Sign | What we found |
|---|---|
| A Kaspersky alert naming Trojan.Multi.BroSubsc.gen with Object: System Memory | The first and in the 2023 case the only sign. That user had never seen an unwanted ad. |
| Advertising notifications in the corner of the screen | What Kaspersky's family text describes. Check which site sends them in the browser's notification list. |
| Treatment asks for a restart and the alert returns | Described in the 2019 Habr post, and in the 2021 case where it came back once after the browser was reinstalled. |
| A slow PC, windows that struggle to minimise and maximise, a high CPU load | In the old guide only. We found no case that reports them for this detection, so they point to something else. |
| Task Manager will not open and shows an nvapi.dll error | In the old guide only. No Kaspersky page or case we read mentions it. |
| No sign at all | Does not clear the browser, and does not prove anything is wrong. |
Our 2020 claims, checked one by one
We kept every claim of the old guide here so you can see which ones the sources support. Where no source supports one, we say so rather than drop it silently.
| The old guide said | What the sources show |
|---|---|
| It is a trojan with complex functionality | Kaspersky classes it as a Trojan, but its family text describes only advertising messages. We found no source for complex functionality. |
| It disables Task Manager and you get an nvapi.dll error | No source. The four forum cases and Kaspersky's pages do not mention Task Manager. |
| It disguises itself as a legitimate process and stays hidden for weeks | No source. In every case Kaspersky itself found and could treat it. |
| It disables your antivirus so it cannot find the parasite | No source. In each case the antivirus found it, and the reports show the product acted on it. |
| It adds rogue entries to the Windows Registry | No source. Kaspersky's explanation is that the verdict reads browser settings in an autorun check. |
| It steals passwords, empties bank accounts and sells your identity | No source in the family text or the cases. |
| It installs other malware, miners or ransomware | No source. A helper wrote that it is definitely not a ransomware issue. |
| Most victims are in Russia, then Brazil, India, Kazakhstan, Ukraine, Mexico, Algeria, Saudi Arabia, France and Vietnam | Supported: this is Kaspersky's own top ten, with Russia at 44.48%. |
| It shows intrusive pop-up notifications in any browser | Partly supported: Kaspersky says it displays advertising messages, and the check supports Chrome, Yandex, Opera and Vivaldi. |
| Removal needs Safe Mode with Networking or System Restore, and only a reliable antivirus will do | Kaspersky's own steps are different: update, Quick scan, Advanced Disinfection with a restart, and a check of the browser's notification list and extensions. |
Check your browser and PC
How it gets onto a PC: what our old guide said and what the sources show
The route in Kaspersky's text is a click on a prompt after a visit to a fraudulent or advertising resource. The old guide named email attachments, fake updates, cracks and pirate sites instead; the table says what supports each claim.
| The old guide said | What the sources show |
|---|---|
| Email spam with attachments or links runs the payload | Not in Kaspersky's family text or in any case we read. The route there is a notification prompt on a website. |
| Fake updates, cracked software or a malicious advertisement | Kaspersky names fraudulent and advertising resources, so the advertisement part fits. No source ties a fake update or a crack to this detection. |
| Pirate networks such as The Pirate Bay, eMule or BitTorrent | Not mentioned in any source we found. The advice to avoid them stays in the prevention list, because cracks are risky for other reasons. |
| Installation happens when users do not follow security measures | The cases show a click, not a missing measure: one 2023 user wrote that he visited no fraudulent site he knew of, and only a news site had notifications allowed. |
- 1
A click you may not remember
The permission can be weeks or years old. Chrome says it may remove the notification permission of sites you have not visited for a while and show a Safety Check list of removed permissions, so an old grant may already be gone.
- 2
A site you think is harmless
In the January 2023 case the only site with notifications allowed was a news site. We do not know whether that site was the source of the detection; the user guessed so, and no helper confirmed it.
Which browsers the check reads
The old guide said the trojan can enter Chrome, Firefox, Explorer and Safari. Kaspersky's own list was shorter, and it was written in 2019 and repeated in 2021, so it may have grown since.
| Browser | What the sources say | Where to look |
|---|---|---|
| Google Chrome | Named as supported in 2019 and in the 2021 post | chrome://settings/content/notifications, or Settings > Privacy and security > Site settings > Notifications |
| Yandex Browser, Opera, Vivaldi | Named as supported in 2019 and 2021. A 2019 Habr commenter could not find a notification page in Vivaldi | Open the browser's site settings and search for notifications; Kaspersky gave Opera's older path as Settings, Advanced, Privacy and Security, Content Settings, Notifications |
| Microsoft Edge | Not on Kaspersky's list. Edge is built on the same engine as Chrome, which is our reading, and Microsoft documents the same kind of site notifications | Settings > Privacy, search, and services > Site permissions > All sites |
| Mozilla Firefox | Not on Kaspersky's list. Mozilla says web push works while Firefox is open. A Habr commenter named the setting dom.webnotifications.enabled; that is a user's tip, not a vendor step | Settings > Privacy & Security > Permissions > Notifications > Settings |
| Safari and Internet Explorer | The old guide named them. Kaspersky's list has neither, and Apple documents site notifications for Safari on a Mac | Safari > Settings > Websites > Notifications |
How to remove Trojan.Multi.BroSubsc.gen
How to stop Trojan.Multi.BroSubsc.gen notifications
Do this in every browser you use, and in every profile inside it: each keeps its own list of sites allowed to send notifications.
Nothing has to be uninstalled for the notifications themselves.
Which browser shows the ads?
Step 1: Remove the site's address from Chrome's notification list
Chrome keeps a list of every site you once allowed to send notifications, and
the site's addressis on it. Pastechrome://settings/content/notificationsinto the address bar, find the site's address under Allowed to send notifications, open the three-dot menu next to it and pick Remove.Then click Add next to Not allowed to send notifications and type the site's address, so the site cannot ask a second time. Repeat it in every Chrome profile you use on Windows 11 or Windows 10, since each profile has its own list.
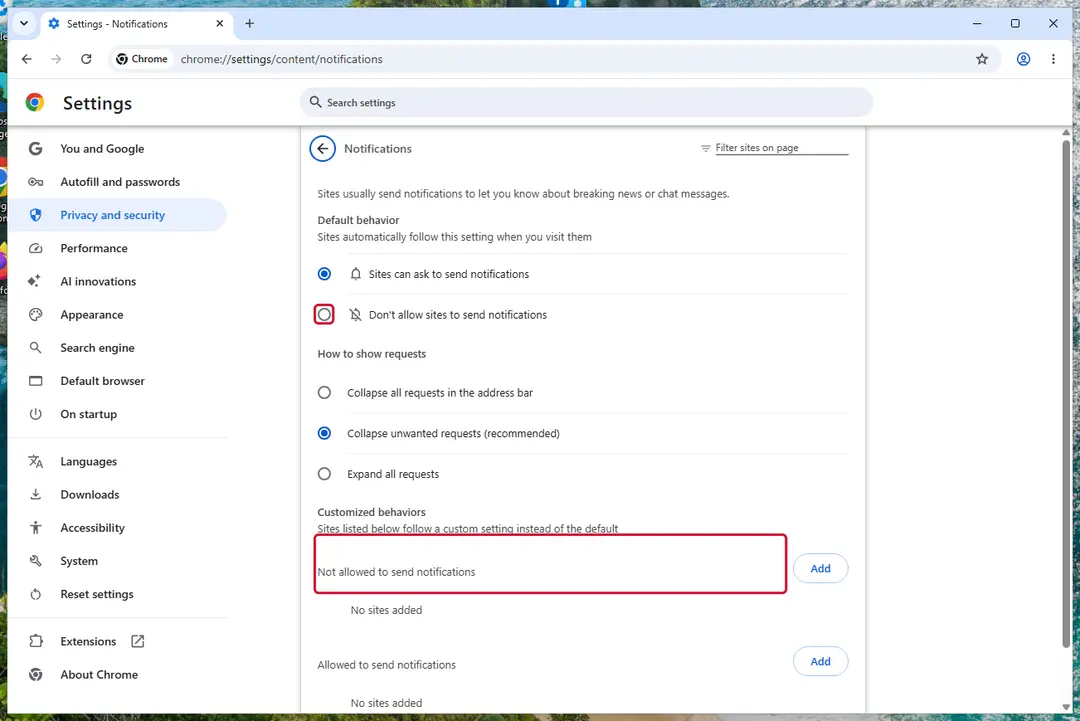
Chrome on Windows 11: Settings > Privacy and security > Site settings > Notifications. Full procedure with screenshots: Stop website notifications and pop-ups
Still there? More for Google Chrome
Chrome on a computer
Click More (three dots) > Settings > Privacy and security > Site settings > Notifications. Under Allowed to send notifications find a site you do not recognise, click More next to it and choose Block (or Remove). You can also type
chrome://settings/content/notificationsin the address bar, as Kaspersky's own steps suggest (Chrome Help). Each Chrome profile keeps its own list.Full procedure with screenshots: Stop website notifications and pop-ups
Remove extensions you do not recognise
Type
chrome://extensionsin the address bar and press Remove on any extension you did not add, such as a video downloader or a search helper.Full procedure with screenshots: Remove a browser extension
Reset Chrome
Go to Settings > Reset settings > Restore settings to their original defaults > Reset settings. The start page and search engine return to default and extensions are switched off; bookmarks and passwords stay. Kaspersky's post says to reset or disable anything suspicious.
Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 1: Remove the site's address from Edge's notification list
Open Settings and more (the three dots) > Settings > Privacy, search, and services > Site permissions > All permissions > Notifications. Remove
the site's addressfrom the Allowed list, then click Add site next to Not allowed to send notifications and enter it there.Edge is built into both Windows 11 and Windows 10, so check it even if you normally use another browser. If the notifications came with the Edge logo, this is the browser that holds the permission.
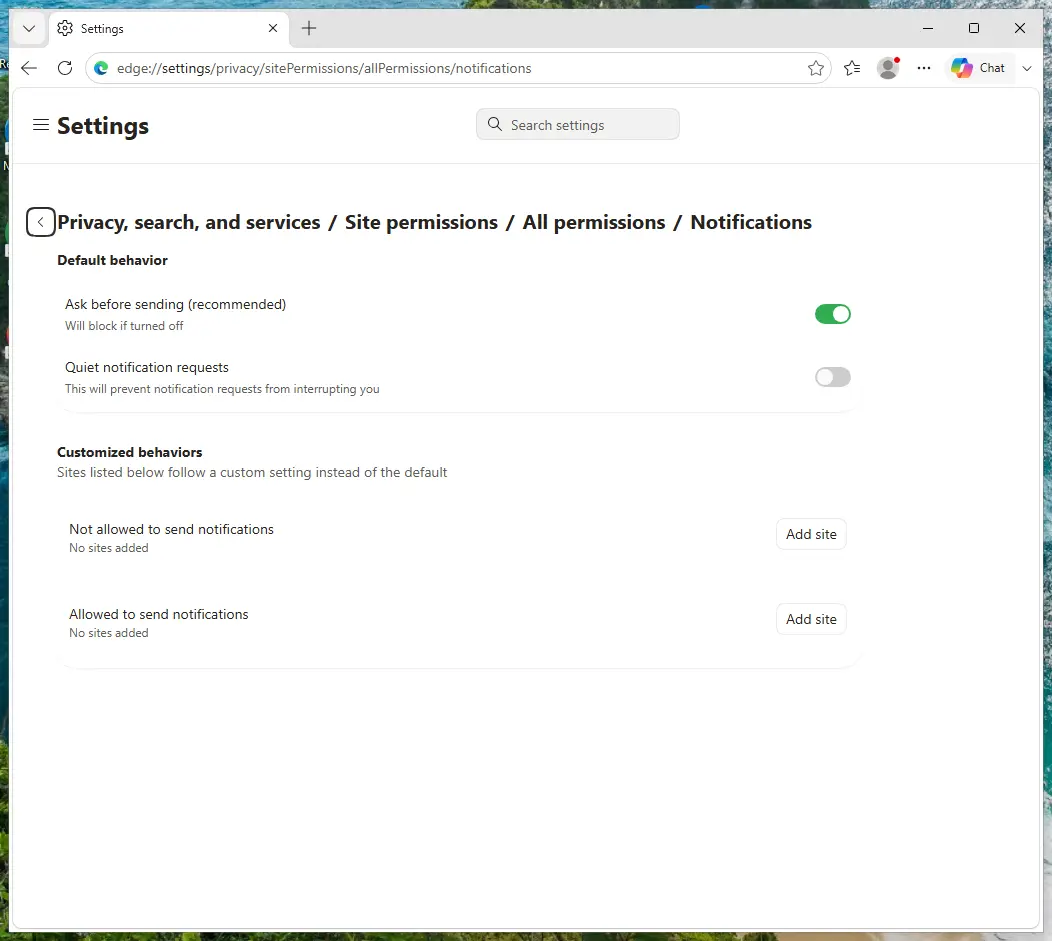
Edge on Windows 11: Site permissions > All permissions > Notifications. Full procedure with screenshots: Stop website notifications and pop-ups
Still there? More for Microsoft Edge
Block the site in Edge
Click Settings and more (three dots) > Settings > Privacy, search, and services > Site permissions > All sites. Select the website, find Notifications and choose Block from the drop-down menu (Microsoft Support). Do it for each site you do not recognise.
Full procedure with screenshots: Stop website notifications and pop-ups
Remove extensions you do not recognise
Type
edge://extensionsin the address bar and press Remove under any extension you did not add.Full procedure with screenshots: Remove a browser extension
Reset Edge
Go to Settings > Reset settings > Restore settings to their default values > Reset. Extensions are switched off and the start page returns to default; favourites, history and passwords stay.
Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 1: Remove the site's address from Firefox's notification permissions
Open the menu (three lines) > Settings and click Permissions and data in the left list, then Notifications. Select
the site's address, click Remove Website and confirm with Save Changes.In versions older than Firefox 152 the same list sits under Privacy & Security, behind a Settings button next to Notifications. Firefox shows these notifications only while it is running, on Windows 11 and Windows 10 alike.
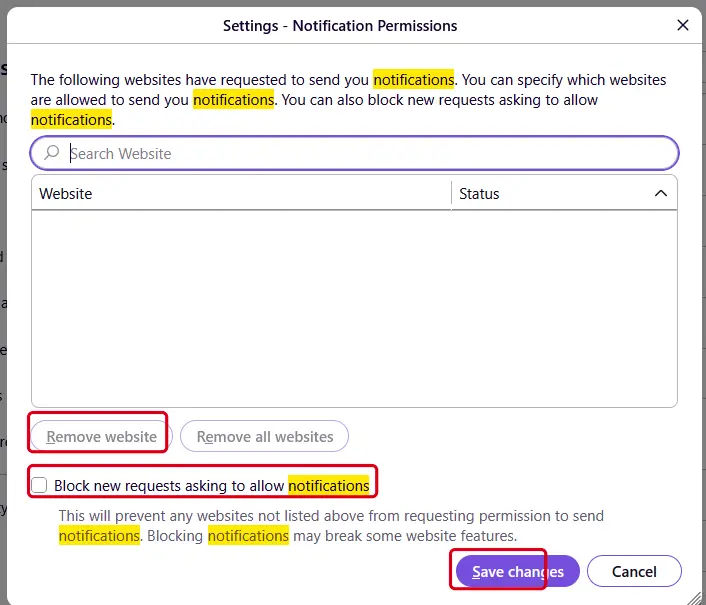
Firefox on Windows 11: the Notification Permissions window. Full procedure with screenshots: Stop website notifications and pop-ups
Still there? More for Mozilla Firefox
Remove the site from Firefox's notification permissions
Click the menu button > Settings > Privacy & Security, go to Permissions and click Settings… next to Notifications. Select the website, click Remove Website and then Save Changes; choose Block in its Status drop-down instead if you also want to stop it asking again. To stop all new requests, tick Block new requests asking to allow notifications (Mozilla Support).
Full procedure with screenshots: Stop website notifications and pop-ups
Remove add-ons you do not recognise
Type
about:addonsin the address bar, open Extensions and choose Remove from the three-dot menu of any add-on you did not install.Full procedure with screenshots: Remove a browser extension
Refresh Firefox
Open the menu > Help > More troubleshooting information > Refresh Firefox. Add-ons and custom settings go; bookmarks, history and passwords stay.
Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Stop notifications from a site in Safari on a Mac
Choose the Apple menu > System Settings > Notifications, go to Application Notifications, click the website and turn off Allow Notifications. To remove it from the list, deny the website's permission in Safari > Settings > Websites > Notifications. Untick Allow websites to ask for permission to send notifications so that no site can ask again (Apple Support).
Remove extensions you do not recognise
Open Safari > Settings > Extensions, select any you did not install and press Uninstall.
Then, whichever browser you use
Step 2: Scan the PC if you downloaded anything from the ads
If you only saw the notifications and clicked nothing, you can stop before this step. If a notification led you to download or run something, delete that file, then scan Windows.
In Windows Security > Virus & threat protection > Scan options, run a Full scan, then choose Microsoft Defender Antivirus (offline scan) and Scan now. The offline scan restarts the PC and takes about 15 minutes on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Remove it from Windows 11 and Windows 10
Kaspersky's own steps come first, then the browser steps below, then a Microsoft scan as a second opinion. We did not run any of them on an infected PC; each step names its source.
- 1
Copy the alert
Take a screenshot of the full detection window, with its extended details. Forum helpers ask for exactly that, and for the product name and version, before they say anything about your case.
- 2
Update and run a Quick scan
Kaspersky's 2021 post tells you to update the product's databases and run a Quick scan. A scan does not remove a browser permission by itself, which is why the next two steps matter.
- 3
Run Advanced Disinfection and restart
Choose Advanced Disinfection and let Windows restart when asked. According to the support text on Habr, treatment sets the URLs it found from Allow to Block. An administrator in the 2021 thread wrote that it goes away after Advanced Disinfection.
- 4
Review the notification list in every browser
Open each browser you use, in each profile, and look at the sites allowed to send notifications. Remove or block any you did not choose, and not only the ones Kaspersky changed. The tabs in the browser steps give the menu path for Chrome, Edge, Firefox and Safari.
- 5
Remove extensions you do not recognise
Kaspersky's post says to check installed extensions, and its adware article says to remove the advertising extension. Do this in each browser as well.
- 6
Uninstall a program you did not choose
If ads began after you installed something, open Settings > Apps > Installed apps (Apps & features in Windows 10), sort by install date and uninstall what appeared at that time. Kaspersky's article names Control Panel > Programs and Features for the same job.
- 7
Run a Microsoft scan as a second opinion
Open Windows Security > Virus & threat protection > Scan options, choose Full scan and Scan now. For a second pass choose Microsoft Defender Offline scan: Microsoft says it runs outside the normal Windows kernel, takes about 15 minutes and restarts the PC; with BitLocker on, suspend protection first, and read the result under Protection history.
- 8
Look again after a day
Open the notification lists again and run the Quick scan once more. If the verdict returns, a site has been allowed again, or an extension or program is putting it back; follow the steps for asking Kaspersky below.
You do not need Safe Mode, System Restore or a registry cleaner for this detection. The old guide sent you there, and none of Kaspersky's pages we read does. Never install a repair tool because a notification tells you to.
Could it be a false alarm?
Possibly, and only Kaspersky's virus lab can say, as a helper wrote in June 2023. The cases show a verdict that was explained as adware, never one that was shown to be wrong. Use the table to decide how careful to be.
| Points to an ad-notification permission | Points to something else |
|---|---|
| Your browser's notification list holds sites you do not know | The list is empty or holds only sites you chose, and the alert returns after you treated it |
| You see ad notifications outside the browser window | You have never seen an ad, as in the 2023 case, and the alert stays |
| It goes away after Advanced Disinfection and a check of the list | It returns after you reinstalled the browser, as in the 2021 case |
| The report names only this one detection | The same report names other detections, such as the Accesstr name in the 2021 log, or a file path |
- 1
Ask Kaspersky with the evidence
The Kaspersky Support Forum has a Virus and Ransomware section. Give the product and version, the date, the full detection window and what the browser's list showed. Helpers there also asked for an AdwCleaner scan log, with the instruction not to fix anything first.
- 2
Do not turn off protection
Do not switch off your security product or exclude a folder to stop the alert.
- 3
Do not rely on one scan
A scan with nothing found means the sites Kaspersky lists are gone. Another site you allowed can still send notifications, so review the browser list yourself.
After removal: keep the ads from coming back
If you clicked a notification, installed something or typed data
The permission itself costs nothing once removed. What a page asked of you after a click is the part that needs care.
- 1
Change passwords you typed
If you entered a password on a page that a notification opened, change it from another device, start with your email and then the account in question, and turn on two-step sign-in.
- 2
Check your card statements
Look for payments you did not make. If you entered card details on such a page, call your bank.
- 3
Uninstall what the page offered
A cleaner, a video player or a browser add-on offered by an ad page is not something Kaspersky's detection removes. Remove it under Settings > Apps > Installed apps.
- 4
Scan twice
Run the Windows Security Full scan and then the Microsoft Defender Offline scan, as in the removal steps. The scans find files and programs, not browser permissions, so the notification list still needs its own review.
How to avoid it next time
Most of the old guide's advice still holds. We added the one step that matters most for this detection: control who may ask for notifications.
Do
- Press Block on a notification prompt you did not ask for, or close the tab.
- Stop sites from asking: in Chrome open Settings > Privacy and security > Site settings > Notifications and choose the quieter messaging option; in Firefox tick Block new requests asking to allow notifications; in Safari on a Mac untick Allow websites to ask for permission to send notifications.
- Review the notification list in each browser once a month and remove sites you no longer want. Chrome's Safety Check also lists permissions it removed from unused sites.
- Keep a security product with web protection on. Kaspersky's adware article suggests turning on the check of web links against its adware URL database.
- Look at the sender, the wording and the address before you open an email attachment or link, and scan an attachment before you open it. The old guide's advice about spam still holds even though no source ties email to this detection.
- Get programs from the maker's own site or an official store, not from cracks or pirate networks.
- Keep a current backup of important files, so a bad infection costs you a reinstall rather than your documents.
Don't
- Do not press Allow to prove you are human, to play a video or to start a download.
- Do not click a notification that says you have a virus or that something must be removed.
- Do not install a program that a notification or a page offers as a fix.
- Do not run a repair or registry tool because a pop-up tells you to.
- Do not call a number shown in an alert.
Questions about Trojan.Multi.BroSubsc.gen
What is Trojan.Multi.BroSubsc.gen?
It is the name Kaspersky products give to a website that is allowed to show advertising notifications in your browser, not a program on your disk. Kaspersky's threat page says malware of this family is installed on browsers deceptively after a visit to fraudulent or advertising resources and shows advertising messages even if a browser is inactive.
Kaspersky support explained in 2019 and again in 2021 that the verdict is given when an autorun check finds browser settings holding a URL that sends these notifications. The detection date on the threat page is 2 February 2019.
Is Trojan.Multi.BroSubsc.gen a virus?
On the sources we read it is not a virus in the sense of a program that spreads or damages files. Kaspersky classes it as a Trojan, but its family text describes only advertising messages, and the helpers who answered users in 2023 said Kaspersky Threats and the AdwCleaner log pointed to adware.
One of them added that it is definitely not ransomware. We could not test a PC, so we cannot rule out other problems on yours. Review your browsers' notification lists and run the removal steps.
How do I remove Trojan.Multi.BroSubsc.gen?
Update Kaspersky, run a Quick scan, then Advanced Disinfection with the Windows restart it asks for. After that, open the notification list of every browser and profile and block or remove each site you do not know, and remove extensions you did not add.
Kaspersky's post of 21 September 2021 gives these steps. If ads started after you installed a program, uninstall it under Settings, Apps, Installed apps. A Microsoft Defender full scan is a useful second opinion, but it does not remove a browser permission.
Why does Kaspersky say the object is System Memory?
We do not know, and Kaspersky does not say. The alert in our 2020 pictures, the Endpoint Security log posted on 11 May 2021 and the Virus Removal Tool user of 2023 all report System Memory as the object.
Kaspersky's explanation is that the verdict comes from browser settings read during an autorun check. We found no source that links the two. Treat the label as a place name in the report and look at the sites in your browser's notification list.
Why does Trojan.Multi.BroSubsc.gen keep coming back?
The most likely reason is that another site in your browser still has permission to send notifications. The 2019 Habr post describes a window that offered treatment by restart and then returned, round and round.
In March 2021 an administrator wrote that it came back once after the browser was deleted and reinstalled. Treating changes the sites Kaspersky found from Allow to Block, and others may remain. Check every browser and profile, remove unknown extensions and ask Kaspersky Support with the full report if it still returns.
Can Trojan.Multi.BroSubsc.gen steal my passwords or bank details?
We found no source that says so. Our 2020 guide claimed it steals saved passwords and drains bank accounts, but Kaspersky's family text and the four forum cases mention only advertising notifications. The cases show users asking about backdoors and ransomware and being told it is adware.
The risk lies in what you do after clicking a notification. If you typed a password or card number on a page that a notification opened, change the password from another device and tell your bank.
Do I need Safe Mode or System Restore?
No, none of the Kaspersky pages we read asks for either. Our 2020 guide sent readers to Safe Mode with Networking and System Restore, but the detection is about a setting in your browser.
Kaspersky's steps are to update, run a Quick scan, run Advanced Disinfection with a restart, and review the browser's notifications, subscriptions, permissions and extensions. Safe Mode would not remove a site's permission. System Restore is not named by Kaspersky or by the browser help pages we read.
Does it affect Mac, Firefox or Edge?
Kaspersky's 2019 and 2021 texts name Chrome, Yandex Browser, Opera and Vivaldi as the browsers the check reads, so Firefox, Edge and Safari are not on its list, though the list may have grown. The permission itself exists in every browser:
- Mozilla
- Microsoft
- Apple each document how to remove it
If you see ad notifications in Edge, Firefox or Safari on a Mac, the same cure applies even without a Kaspersky alert. The steps for each browser are above, and they work whether or not a security product shows an alert.
Can I be sure my PC is clean after the alert stops?
A Kaspersky forum helper wrote in January 2023 that a scan without detections means the system is clean, but that only covers what Kaspersky knows. We cannot clear your PC, and a quiet scan never clears a site.
Open the notification list in each browser, remove sites you did not choose, run a Microsoft Defender full scan and look again after a day. If you want certainty, send Kaspersky Support the full report, because only its virus lab can confirm or deny a false positive.
Will Fortect remove Trojan.Multi.BroSubsc.gen?
No program removes Trojan.Multi.BroSubsc.gen itself, because there is nothing on the PC to remove: the notifications come through a permission saved in the browser, and only the browser's settings take it away, as the steps above show.
What Fortect can do is check the rest of Windows. Its free scan looks for malware, unwanted programs and damaged system files, which is useful if you clicked the ads, downloaded something from the pages they opened, or are not sure what else changed on the PC.
If the scan finds nothing and the notifications stopped after you removed the permission, this problem is solved. Use Microsoft Defender as a second opinion whenever you have downloaded files from pages like these.
Sources
- Kaspersky Threats: Trojan.Multi.BroSubsc (detect date 02/02/2019) (read October 6, 2026)
- Habr: Trojan.Multi.BroSubsc.gen, Kaspersky alert (28 February 2019, quoting Kaspersky support) (read October 6, 2026)
- Kaspersky Support Forum: What to do if Kaspersky detects trojan.multi.brosubsc.gen (21 September 2021) (read October 6, 2026)
- Kaspersky Support Forum: Trojan.Multi.BroSubsc.gen difficult to remove (26 March to 21 September 2021) (read October 6, 2026)
- Kaspersky Support Forum: trojan.multi.brosubsc.gen detected (twice) (16 to 17 January 2023) (read October 6, 2026)
- Kaspersky Support Forum: Questions on Trojan.Multi.BroSubsc.gen (20 June to 18 July 2023) (read October 6, 2026)
- Kaspersky Support: How to remove advertising applications from your browser (updated 16 February 2023) (read October 6, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 6, 2026)
- Microsoft Support: Manage website notifications in Microsoft Edge (read October 6, 2026)
- Mozilla Support: Web Push notifications in Firefox (read October 6, 2026)
- Apple Support: Customize website notifications in Safari on Mac (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline scan in Windows (read October 6, 2026)