
TrustedInstaller: what it is and how to remove it
TrustedInstaller is a legitimate Windows process that protects critical system files. Cybercriminals often abuse this process due to its high privileges and functionality.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Do it yourself · free Remove TrustedInstaller yourself 2 steps, about 6 minutes, no software needed.
Start the steps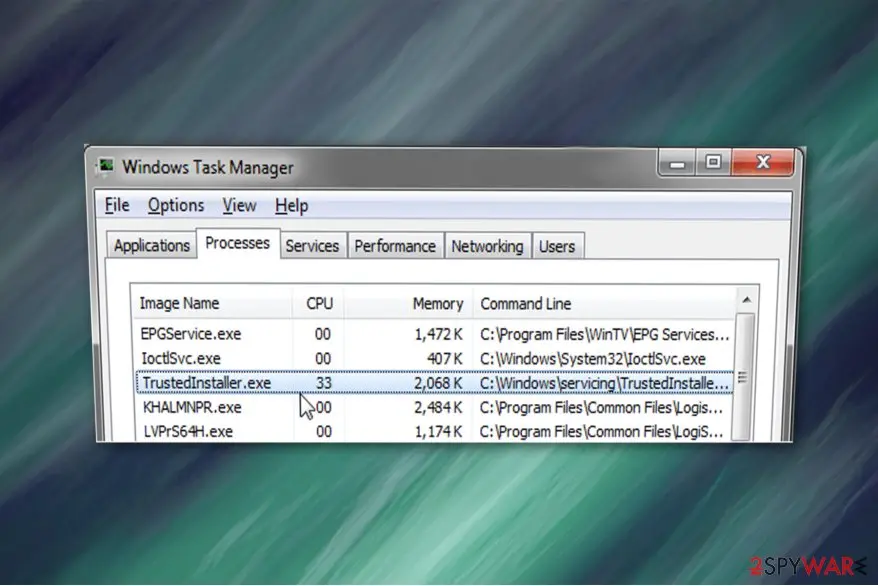
TrustedInstaller: summary
| Detection names | None: the genuine file is not detected |
|---|---|
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Name | TrustedInstaller |
| Type | Windows system file |
| Symptoms | An unknown process in Task Manager |
| Check the PC | The genuine file needs no removal. Fortect's free scan checks Windows for malware hiding under system file names and for damaged system files. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Files and processes | TrustedInstaller.exe and C:\Windows\servicing\TrustedInstaller.exe. |
|---|---|
| Evidence | 7 write-ups by security sites; details still limited |
| File name | TrustedInstaller.exe |
| What it is | Of unknown origin |
| First seen | 2 January 2021 |
| Facts checked | 5 October 2026 |
What the TrustedInstaller file is
From our report of Jan 2021 · outdated details corrected in October 2026
TrustedInstaller is original Windows process, but is often abused by malware
TrustedInstaller is a legitimate Windows process and is a part of Windows Resource Protection (WRP) technology.
It runs under Windows Module Installer service, which is responsible for protecting unauthorized changes being made to .exe, .sys, .dll and other important files. For that reason, users cannot delete or modify certain files, even with Administrator's rights.
Nevertheless, TrustedInstaller, or TrustedInstaller.exe, is often abused by cybercriminals due to its functionality. It can be hijacked, replaced, or corrupted by malware, which can render the computer vulnerable to other severe infections and also compromise its operation by slowing down and crashing installed software. Besides, information tracking by recording keystrokes or taking screenshots is likely as well.
In other cases, users are facing an issue with the process, as it prevents them from opening regular files, such as pictures or video clips. While it can also be malware's doing, it can be a simple bug.
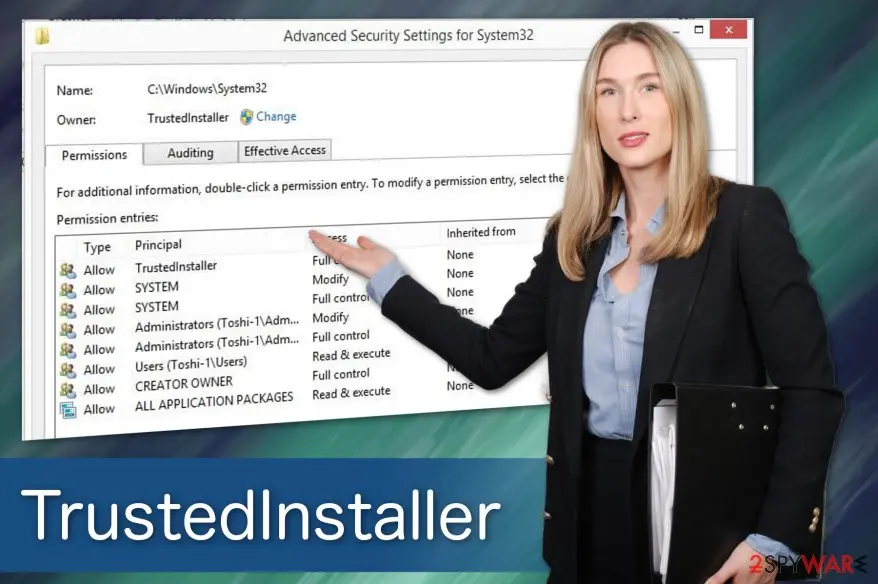
TrustedInstaller permission to modify files may be acquired by gaining ownership of them - we explain how to do that at the bottom of the article. Nevertheless, if you are having any type of problems with the file (like a high CPU usage), it is crucial to make sure it is not affected by a computer virus.
TrustedInstaller.exe is an inbuilt user account used for Windows versions starting from Vista, which is no longer supported. Users would not even notice its presence most of the time. However, if malware replaced the mentioned file, it can cause problems. Nevertheless, you might see the following message if you try to edit/delete/install/uninstall specific files or folders on your OS:
This happens because the built-in user account is in control of all your files and will overwrite your decisions. The primary goal of TrustedInstaller is to control user's ability to interact with the newest Windows updates, system files, and other essential programs. While it might be annoying sometimes, it is a useful feature for people without much computer knowledge, as it will prevent them from damaging system files.
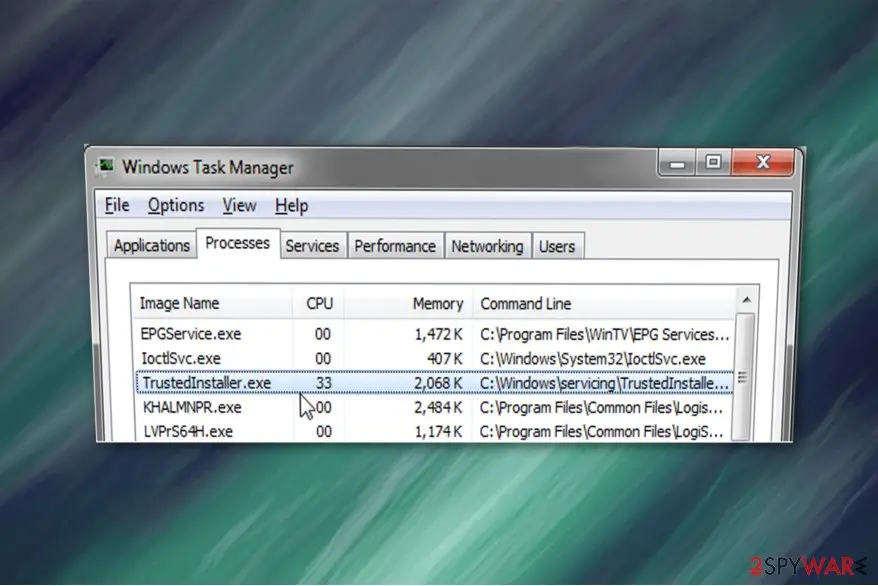
The easiest way to identify if the running process is malicious program is by checking the CPU usage. If TrustedInstaller is using high amounts of your computer resources, it indicates that your system might be at risk.
In spite of that, you might notice that your computer is significantly slower, it takes more time for programs to load or they continuously crash. Additionally, you should also check the location of TrustedInstaller, which should be located in C:\Windows\servicing\TrustedInstaller.exe.
Moreover, this dangerous TrustedInstaller malware can collect personally identifiable information, including:
Usually, it happens when the inexperienced computer user submits logins and passwords in the fake pop-up window. Additionally, be aware that TrustedInstaller virus might be able to let inside other dangerous cyber threats via backdoors. Likewise, to fix your computer, you will need to get rid of all of them. This procedure requires specific IT skills, and it might be challenging for a regular user.
Therefore, we suggest you remove TrustedInstaller virus right away if you do not want to suffer from financial losses. Be aware that the service is an important part of Windows if you delete or corrupt the original file you might damage the OS and the only way to repair it would be to reinstall it, resulting in personal data loss.
The best environment for that would be Safe Mode - the best place perform troubleshooting in.
- names;
- email addresses;
- home addresses;
- credentials .
From our report of Jan 2021 · not reviewed since
Take ownership of files controlled by TrustedInstaller
Warning: please be aware that TrustedInstaller account is there for a reason, and it prevents users and malicious actors from damaging important files that might corrupt the operation of Windows OS. Therefore, before you perform the following actions, make sure you do know what you are doing, as modifying system data might permanently corrupt it.
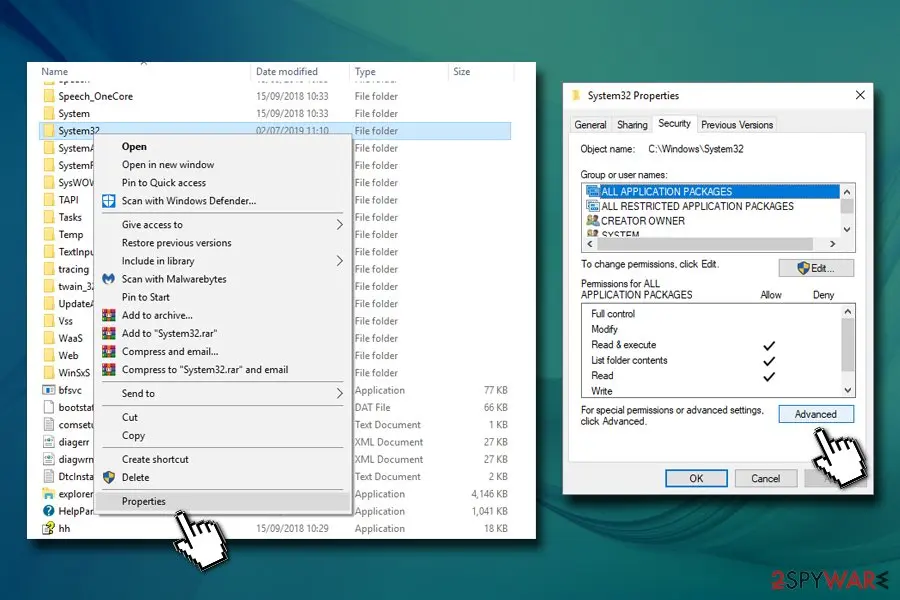
To gain Trustedinstaller permission, perform the following steps:
After these actions, you should be able to overwrite Trustedinstaller's permission and be able to modify files under its control.
- Right-click on the folder you want to gain permission to and select Properties
- Select Security tab and click on Advanced
- In Advanced Security Settings, click Change next to the Owner
- Under Enter the object name to select, type in your username or Administrators and click on Check Names - Windows will fill in the name automatically
- Click OK
- Tick the Replace owner on subcontainers and objects box, and then click OK
- In the Properties window, select Edit
- Click on Administrators or Users (depending which option you chose previously)
- At the bottom of the window, make sure you tick Full control under Allow
- Click Apply and then OK

How to check the TrustedInstaller file
- Path:
C:\Windows\servicing\TrustedInstaller.exe. - File:
TrustedInstaller.exe
From our report of Jan 2021 · not reviewed since
More from our earlier report on TrustedInstaller
- Especially dangerous if not detected early
- Infected or hacked websites, malicious attachments, spam emails, etc.
- High CPU usage, slowdown of the OS operation, crashes
- Use security software like or
- Malware may sometimes damage Windows system files and the registry database, which can result in stability and other issues.
- To fix virus damage after malware removal, scan it with
- You Require Permission from TrustedInstaller
Where TrustedInstaller comes from
From our report of Jan 2021 · not reviewed since
According to DieViren.de experts, a vast of malicious programs enter the computer systems via spam emails which contain the malware.
They can disguise as the invoices or receipts from popular companies or even governmental authorities. Therefore, many gullible people are tricked to install the virus manually.
It might happen when you open the attachment in the spam email. Note that letter usually urges to open the added files for further information. Unfortunately, but the attachment downloads the malware once the person clicks on it. Likewise, you should never open emails which raise any suspicions.
Also, you can unconsciously download the malicious program from hacker-controlled sites. Typically, the user is redirected to such page by clicking on the malware-laden ad . Since they are designed to look legitimate, it is hard to determine the origins. Therefore, it is one of the most popular ways to infiltrate malware.
We suggest you protect your system by avoiding any illegal downloads, advertising content and suspicious email letters. If you closely monitor your online activity and use a professional antivirus tool, you should be able to prevent malware from entering your system.
What to do with TrustedInstaller
How to check TrustedInstaller
The genuine file is part of Windows and needs no removal.
These steps tell it apart from an impostor.
Step 1: Check the location and signature of the file
Open Task Manager (Ctrl + Shift + Esc), right-click the process on Processes and choose Open file location. A file that belongs to Windows is in
C:\Windows\System32orC:\Windows\SysWOW64, a program's file in its folder under C:\Program Files.The same name in
%AppData%or%Temp%is an impostor to remove. Right-click the file > Properties > Digital Signatures to see who signed it, which works the same in Windows 11 and Windows 10.Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 2: Scan the PC, then run the offline scan
A scan finds the parts of TrustedInstaller that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
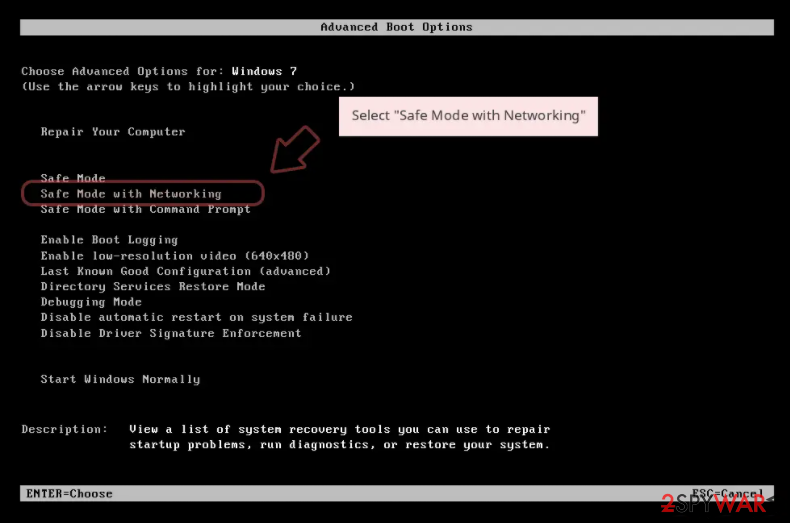
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
Windows 10 / Windows 8
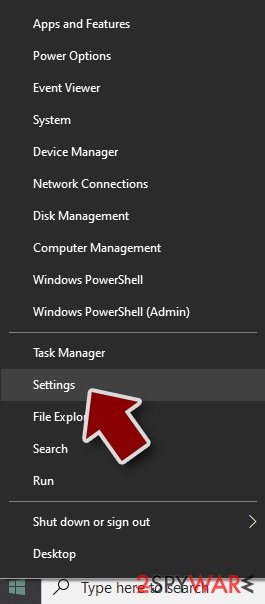
- Right-click on Start button and select Settings.
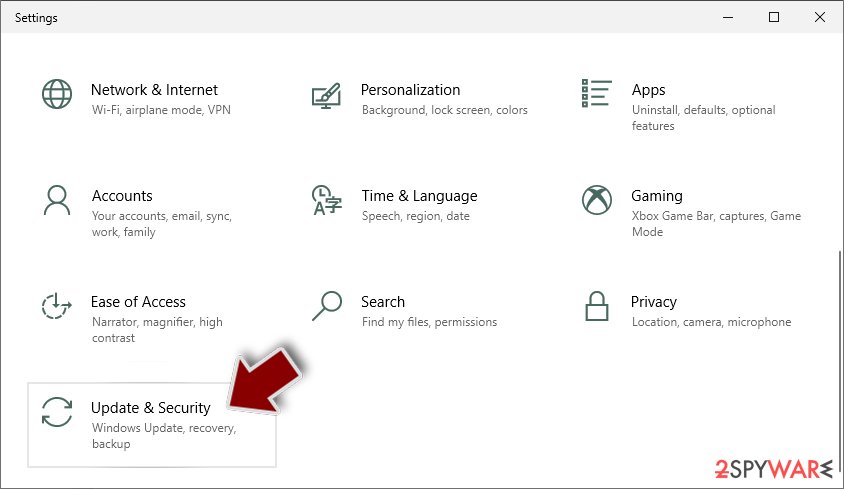
- Scroll down to pick Update & Security.
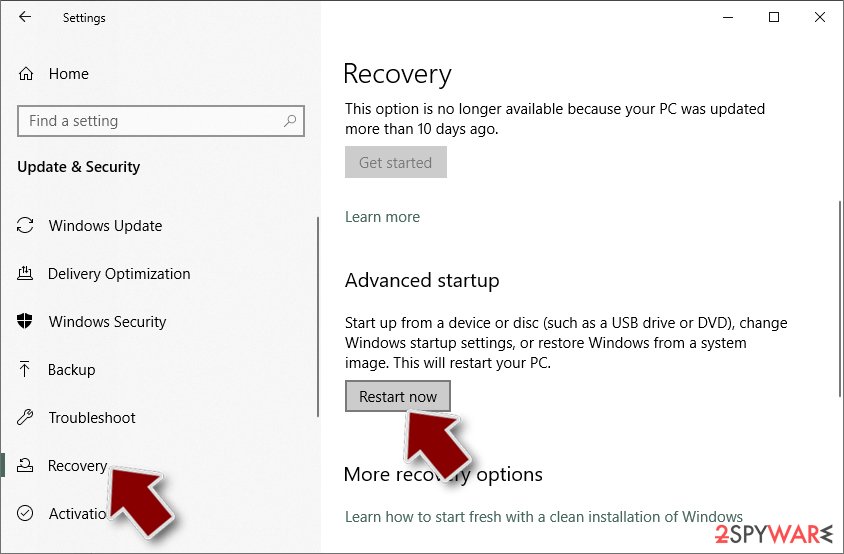
- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.
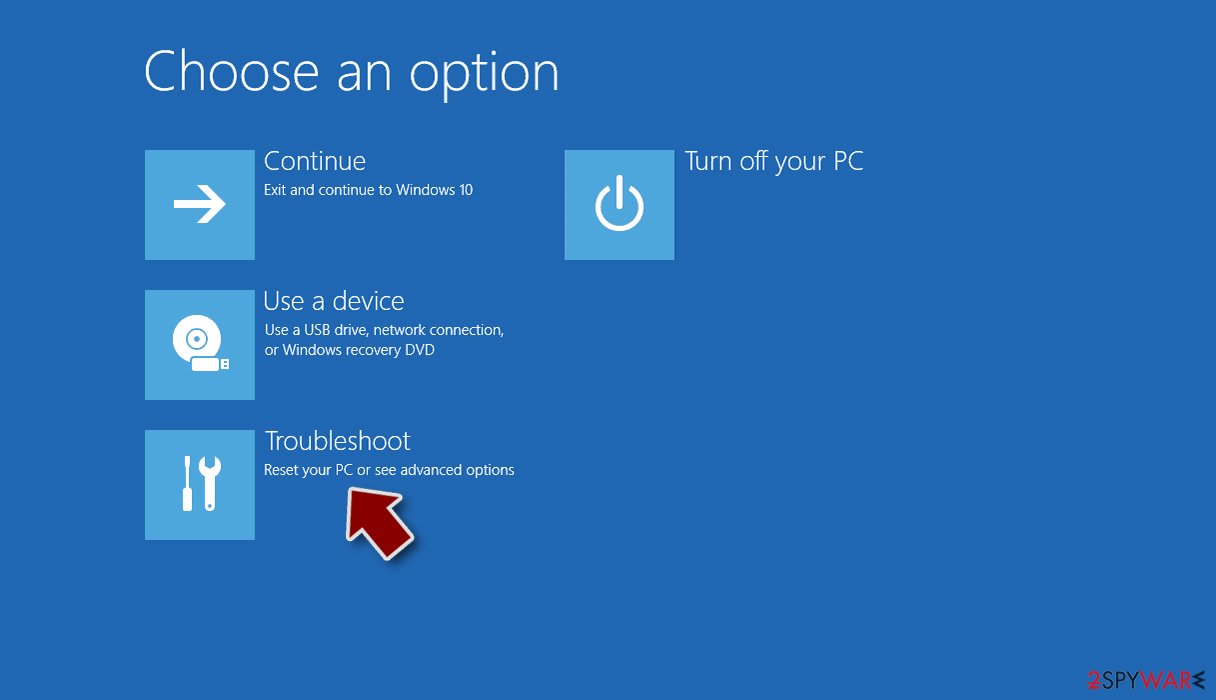
- Select Troubleshoot.
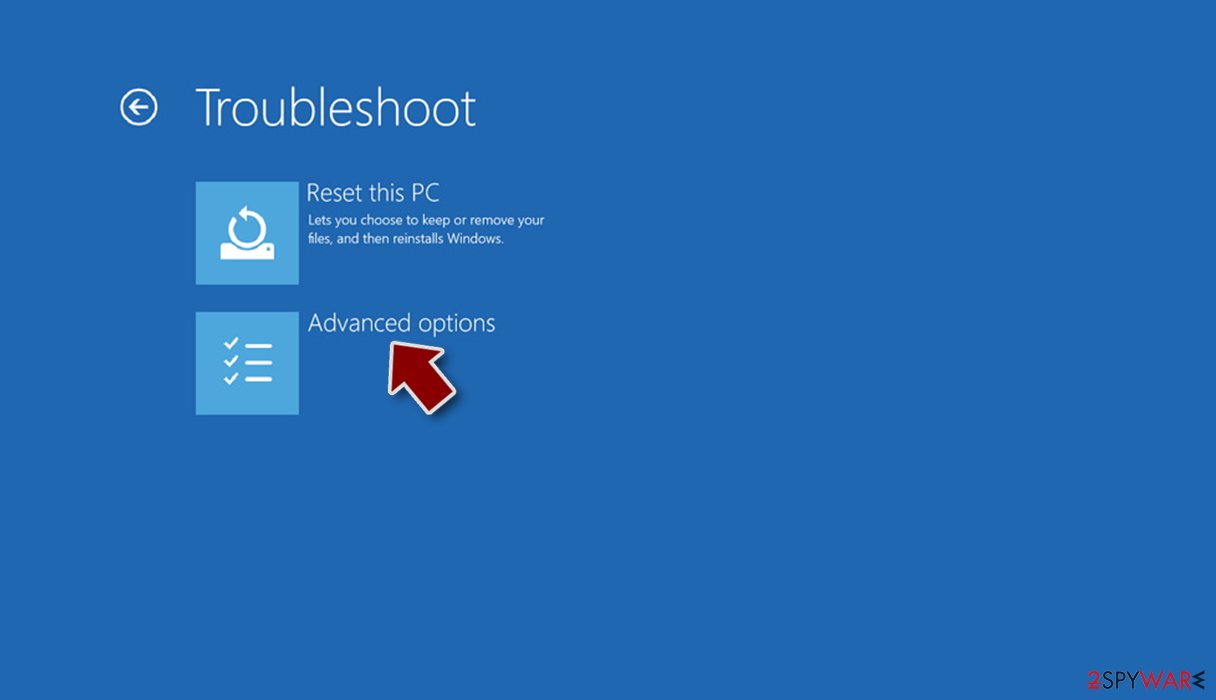
- Go to Advanced options.
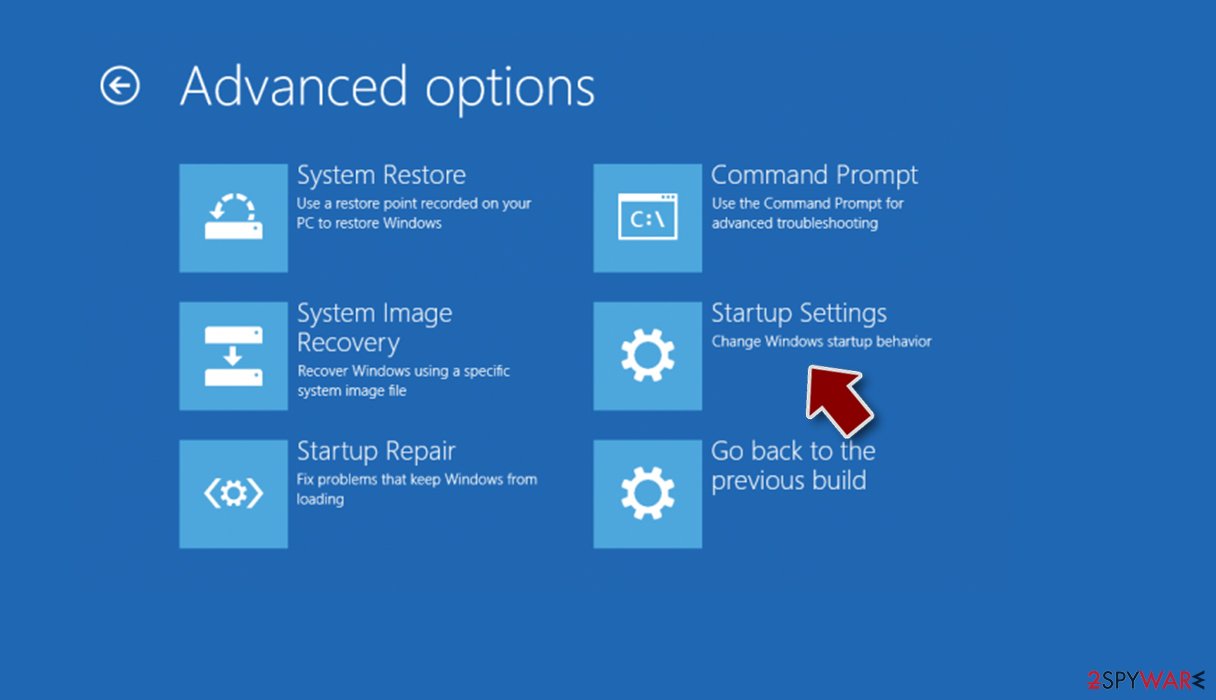
- Select Startup Settings.
- Press Restart.
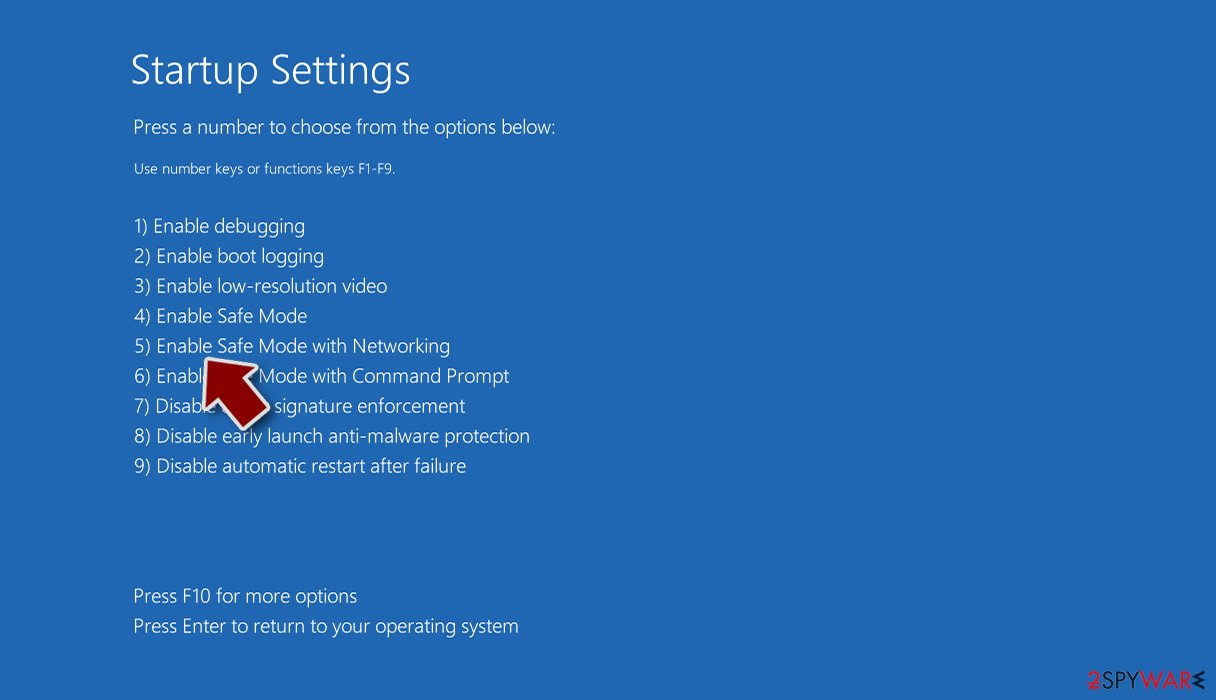
- Now press 5 or click 5) Enable Safe Mode with Networking.
Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
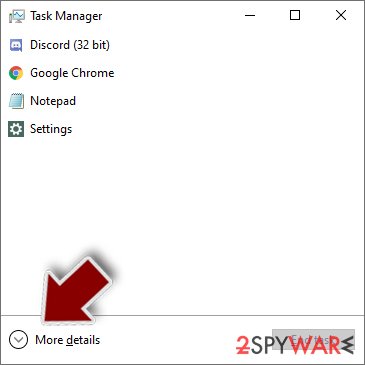
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.
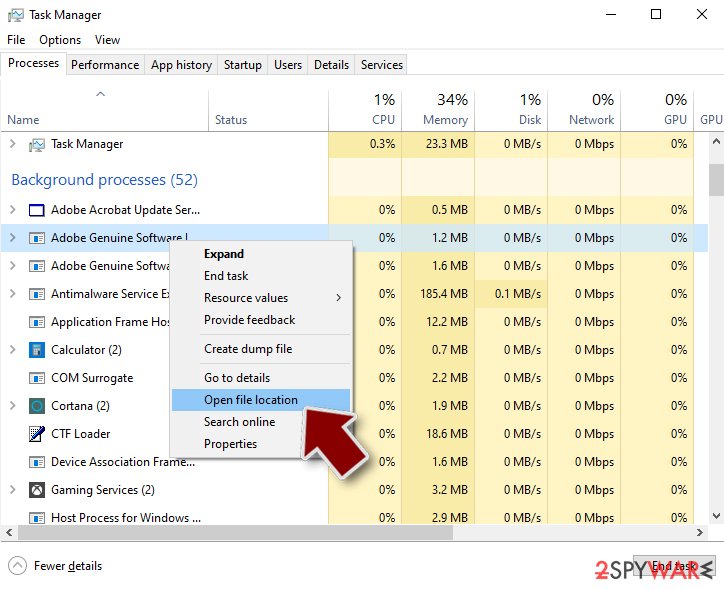
- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.
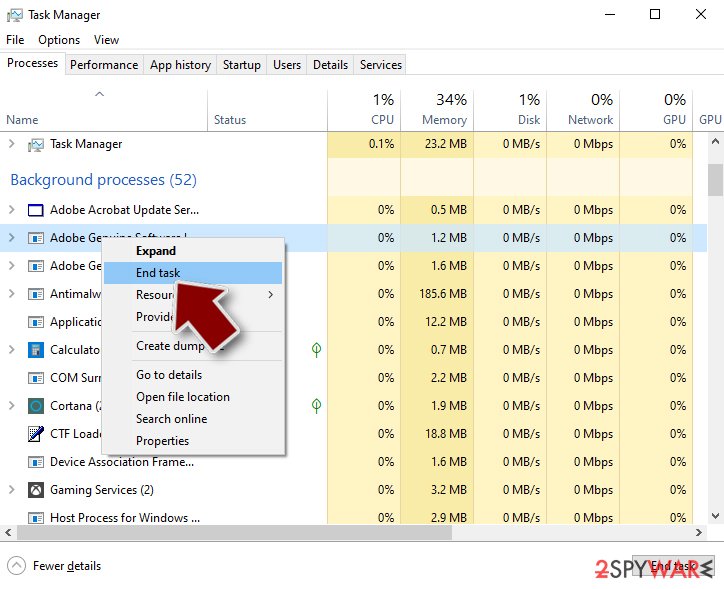
- Go back to the process, right-click and pick End Task.
- Delete the contents of the malicious folder.
Step 3. Check program Startup
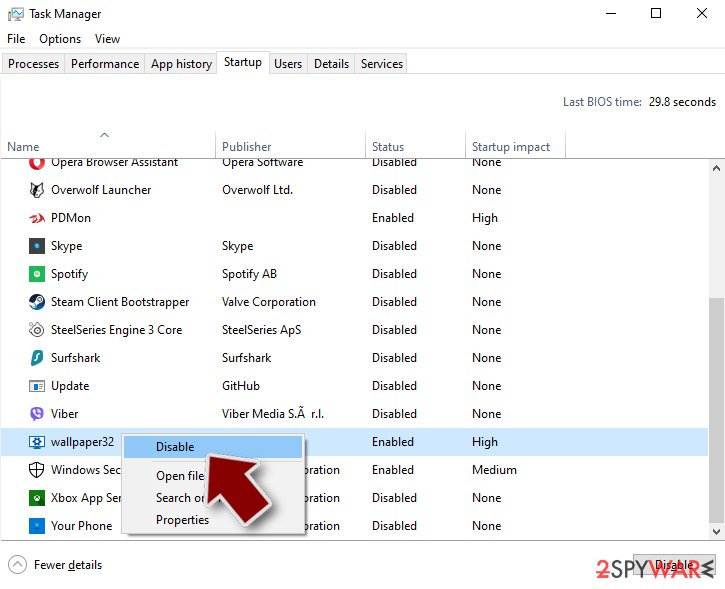
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.
Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.
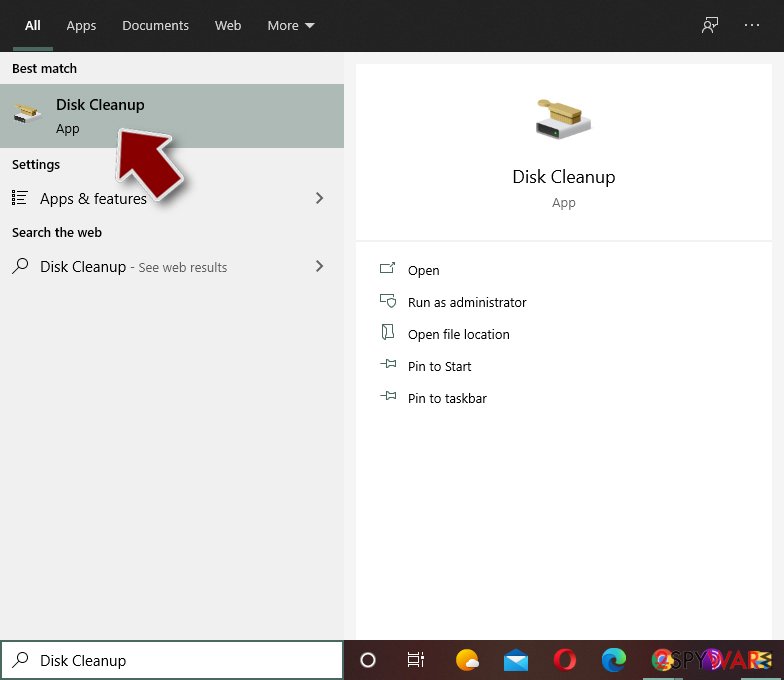
- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.
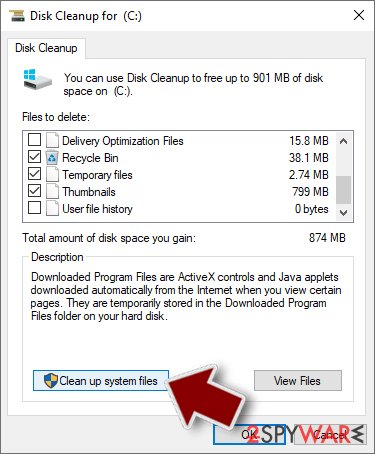
- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
From our report of Jan 2021 · not reviewed since
Remove TrustedInstaller virus automatically
We would like to warn you not to try to remove TrustedInstaller virus without any assistance.
This malicious program is dangerous and might damage your computer permanently. However, you can use a powerful anti-malware software to eliminate the virus for you.
Download or and run a full system scan. The security program will identify the malware together with other potentially dangerous computer threats and remove them. Note that this is the safest option you can choose to protect your system.
However, TrustedInstaller removal might require rebooting your computer into Safe Mode.
[GI=method-1]Firstly, you need to deactivate the malware since it might not allow you to install the security software. For that, reboot you computer to Safe Mode with Networking:
[GI=method-2]If you are still unable to get the antivirus tool, try the System Restore method:
Questions about TrustedInstaller
What is TrustedInstaller?
It is a legitimate Windows process that functions as part of Windows Resource Protection technology. TrustedInstaller runs under the Windows Module Installer service and protects critical system files like .exe, .sys, and .dll files from unauthorized modification.
Users cannot delete or modify certain protected files even with Administrator rights when TrustedInstaller is active. This process has been included in all Windows versions since Windows Vista. The service exists specifically to prevent users and malicious actors from damaging important system files that could corrupt Windows.
Is TrustedInstaller malware?
No, the legitimate TrustedInstaller.exe is not malware itself. However, cybercriminals often abuse, hijack, or corrupt this process because of its functionality and high privileges. When malware replaces or corrupts the file, it can render your computer vulnerable to severe infections and compromise system operation.
The malicious version may slow down and crash installed software. If you suspect TrustedInstaller is compromised, it is critical to verify the file location and check for malware.
How can I tell if TrustedInstaller is infected?
Check the file location, which should be C:\Windows\servicing\TrustedInstaller.exe. Legitimate TrustedInstaller runs from this directory. Monitor CPU usage; if the process uses high amounts of system resources, it indicates potential compromise.
Your computer may be significantly slower with programs taking longer to load or continuously crashing. If you encounter high CPU usage or the file is in an unusual location, your system may be at risk and requires scanning.
What problems does malicious TrustedInstaller cause?
An infected version may collect personally identifiable information including login credentials and passwords. High CPU usage, system slowdowns, crashes, and software failures can occur. The malware prevents users from opening regular files like pictures and videos by restricting access.
Information tracking through keystrokes and screenshots is possible. The malicious process can let other dangerous cyber threats inside through backdoors, allowing multiple infections to establish themselves.
How do I remove malicious TrustedInstaller?
Use security software like Microsoft Defender to scan and remove the infection. Reboot into Safe Mode first, which is the best environment for troubleshooting. After removal with antivirus tools, run a system repair tool to fix any damage the malware caused.
Do not attempt manual deletion without expert assistance, as removing the legitimate process could damage Windows and require complete reinstallation. If uncertain, seek professional help rather than risk corrupting your system.
What if I need to modify TrustedInstaller-protected files?
You must take ownership of the files by changing the owner from TrustedInstaller to your Administrator account. Right-click the folder, select Properties, go to the Security tab, and click Advanced. Click Change next to the Owner field and type your username or Administrators group.
Check the Replace owner on subcontainers box and click OK. In the Properties window, select Edit and grant yourself Full Control permissions. This process allows you to modify protected files, but only proceed if you understand the consequences.
Why does malware target TrustedInstaller?
Cybercriminals abuse this process because it has high system privileges and protects important Windows files. When compromised, TrustedInstaller can bypass security restrictions and prevent legitimate system protection mechanisms from functioning.
The high privilege level allows malware to establish persistence and avoid removal. Users often avoid touching TrustedInstaller assuming it is always legitimate, making it an attractive target for malicious actors.
How can I prevent TrustedInstaller compromise?
Protect your system by avoiding illegal downloads, suspicious advertising content, and dubious email letters. Closely monitor your online activity and use professional antivirus tools. Keep your operating system updated with security patches.
Do not download files from untrusted sources or click suspicious email links. Maintain regular backups of important files. If malware does infiltrate, early detection through regular scans prevents extensive system compromise.
Will Fortect remove TrustedInstaller?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For TrustedInstaller, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- How stuff works: In Windows, what is Safe Mode used for and why? (read October 5, 2026)
- MakeUseOf: What Is the Windows Registry and How Do I Edit It? (read October 5, 2026)
- DieViren: DieViren (read October 5, 2026)
- Wikipedia: Malvertising (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)