
WebHelper: what it is and how to remove it
WebHelper is malware that can silently infiltrate the system and run in the background while recording the victim's keystrokes, playing sounds, and reducing PC speed. Those infected with it can notice a few suspicious processes running in the background, namely, utorrentie.exe and webhelper.dll - they are not a part of Windows system and should not be present by default.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Unsure whether utorrentie.exe is safe? A free scan checks the file and what starts it.
Do it yourself · free Remove WebHelper yourself 6 steps, about 18 minutes, no software needed.
Start the steps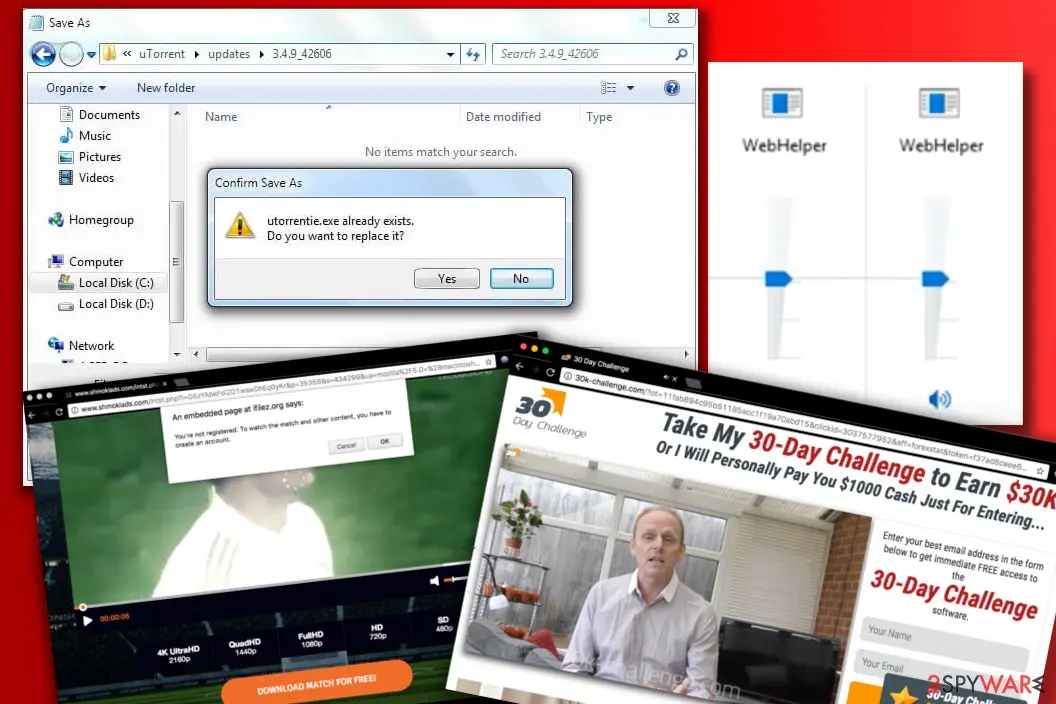
WebHelper: summary
| Distribution | Insecure freeware installations |
|---|---|
| Name | WebHelper |
| Type | Malware |
| Sub-type | Tracking software |
| Symptoms | Infiltrates the system unnoticed Records keystrokes Plays sounds Displays ads Tracks online activities, etc. |
| Danger level | High |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 7 more facts
| Associated entries | utorrentie.exe and webhelper.dll |
|---|---|
| Detection names | No Microsoft detection name is known |
| Damage | Not recorded in the old report |
| Evidence | 5 write-ups by security sites; details still limited |
| File names | utorrentie.exe and C:\Users\ |
| First seen | 6 May 2021 |
| Facts checked | 7 October 2026 |
What WebHelper does on an infected PC
From our report of May 2021 · not reviewed since
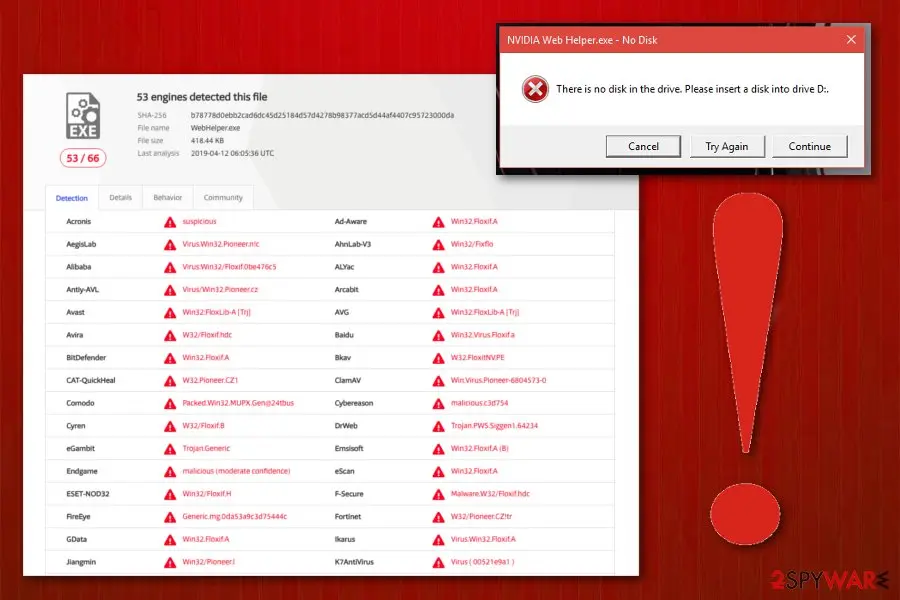
WebHelper is a malicious application that is detected by more than 50 anti-virus programs
WebHelper is malware that can silently infiltrate the system and run in the background while recording the victim's keystrokes, playing sounds, and reducing PC speed.
Those infected with it can notice a few suspicious processes running in the background, namely, utorrentie.exe and webhelper.dll - they are not a part of Windows system and should not be present by default. In other words, if you see these processes running in the background, it is likely that you are infected with the virus.
The malicious app typically travels together with its components in one pack with uTorrent, so you should be very careful when downloading it from the Internet. If you use uTorrent, BitTorrent, and similar services to download files and programs, you can notice Web Helper 32-bit opening and playing advertisements on your computer's desktop repeatedly.
Unfortunately, there are more issues to come as the malware can cause high CPU usage and track you in the background without permission. The information that is typed via the keyboard or mouse inputs can be easily be read by malware operators; thus, eliminating this app quickly is vital to one's security and online safety.
While some might think that shutting down the process will do the trick, it is not the case, as there are numerous components on the machine that will make WebHelper resurface as soon as you reboot your system.
If you found WebHelper entries on your computer, you should know that the most visible issue it causes is serving advertisements based on users' browsing activities and performed searches. For that, malware tracks the user for some time and collects information about their interests, such as most visited websites, mostly clicked ads, etc. Additionally, it can record your keystrokes.
Unfortunately, this information, which is collected by the virus can include numerous amounts of personal data, including:
Once the described adware collects the needed amount of information, it sends this data to its C&C servers.
Another issue is its audio ads confusing users out of nowhere. It is difficult to see what program or process is responsible for this task. The cause of the sound can be detected by opening the Volume Mixer. However, if you thought that disabling sound on WebHelper will solve the issue, we will have to disappoint you that it will help only for a limited amount of time.
Users keep complaining about WebHelper Audio Malware that is causing issues with advertisements and even error or malware alerts in audio or video form out of nowhere :
Audio advertisements served by Web Helper are not only annoying. We should also warn you that its pop-ups and banners can contain links to possibly insecure websites.
Typically, you can't remove WebHelper by uninstalling the app or resetting your web browsers. For that, you need to be aware of some special tips that we provided below for full malware removal. Finally, make sure you also perform a scan with to fix virus damage, e.g., corrupted files and similar components.
- passwords;
- banking data;
- PC IP address;
- system details;
- location;
- mostly visited sites;
- data entered, etc.
From our report of May 2021 · not reviewed since
There are two different components related to malware
WebHelper travels together with two different components that can show up in the Task Manager.
They do not relate to Windows in any way.
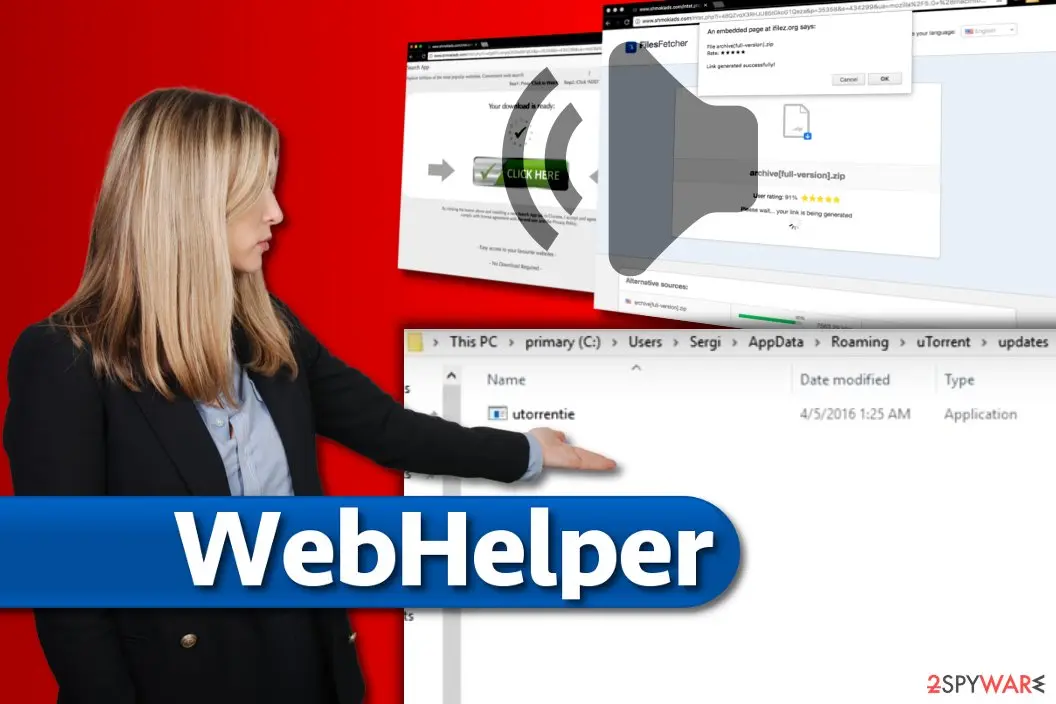
utorrentie.exe is the uTorrent helper that can reinstall itself and annoy users by its reappearance. However, its main task is to use the PC's resources and communicate with its servers. It can also load third-party advertisements on your computer.
The biggest problem related to such activity is a regular data tracking and computer slowdowns. We are sure that you do not want to deal with such virtual annoyances, so we highly recommend you to remove utorrentie.exe together with Web Helper.
It acts as a browser helper object (BHO) that reinstalls WebHelper if deleted launches it and performs its unwanted activities, including displaying sound ads, pop-ups, and banners on the target system. If deleted, it typically reappears once the system is rebooted. The anonymous developer can also initiate tracking activities with the help of this .dll file.
From our report of May 2021 · not reviewed since
Tips on malware avoidance in the future
Although this intruder is part of uTorrent, you can install similar ad-supported programs unknowingly, so we want to provide you with a guide on how to prevent this from happening in the future.
- When installing free software, you should opt for Custom or Advanced installation options. These will give you an opportunity to see all the extra items added to your download.
- If you do not do it and rely on Standard or Default installation options, you will simply clutter your computer with potentially unwanted programs because these installation options tend to include statements granting your permission to install all suggested additions.
- Simply pick Custom or Advanced option and deselect the extras you don't want on your computer.
From our report of May 2021 · not reviewed since
More from our earlier report on WebHelper
- Alternatively, you can delete malware with the help of security software quickly and effortlessly - use
- can fix the damaged Windows system files that could otherwise result in errors, system crashes and other stability issues
- I get ads when I join community csgo servers (which is normal), but for the first time I've got a video saying "you have a virus, bla bla bla call this number bla bla bla if you close this window your computer will die bla bla bla".
- So I checked where it was coming from on volume mixer and it was coming from steam client web helper.
How to check the PC for WebHelper
- Path:
C:\Users\ - File:
utorrentie.exe
How to remove WebHelper
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Check where utorrentie.exe runs from and stop it
utorrentie.exeis the part you can see, and its location tells you whether it belongs there. Right-click it on the Processes page of Task Manager and choose Open file location, then right-click the file > Properties > Digital Signatures to see who signed it.An unsigned file, or one in a user folder such as
%AppData%, is the one to remove: end the task, then delete the file.Note the folder name, because the same folder usually holds its other files. This is the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 2: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to WebHelper or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 3: Remove it from startup
Whatever WebHelper installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 5: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
To remove WebHelper (utorrentie.exe) from Windows 10 or similar Windows OS, you need to create a fake copy of its executable file. Here is what you need to do: First, end uTorrent process running on your computer. Simply press Ctrl + Alt + Del, select it and click End Task. Go to C:\Users\
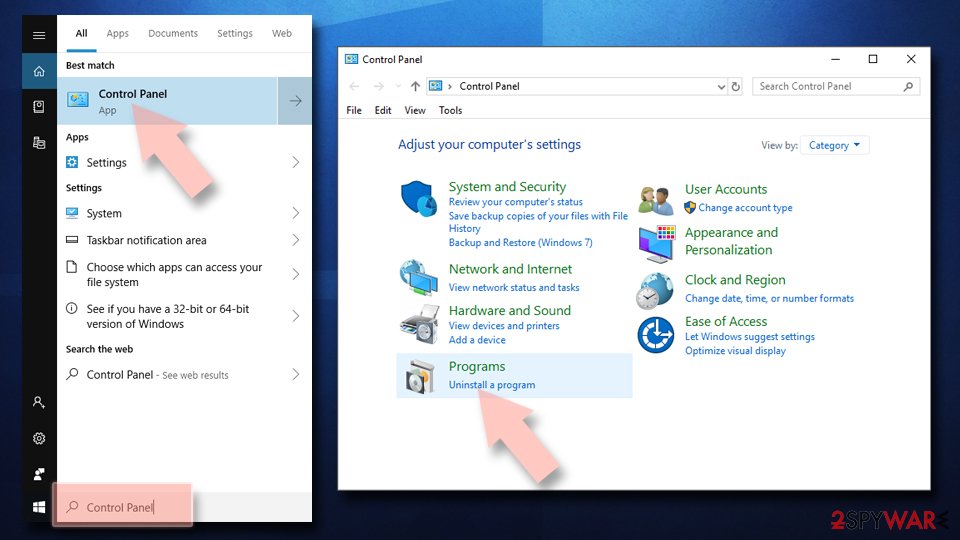
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
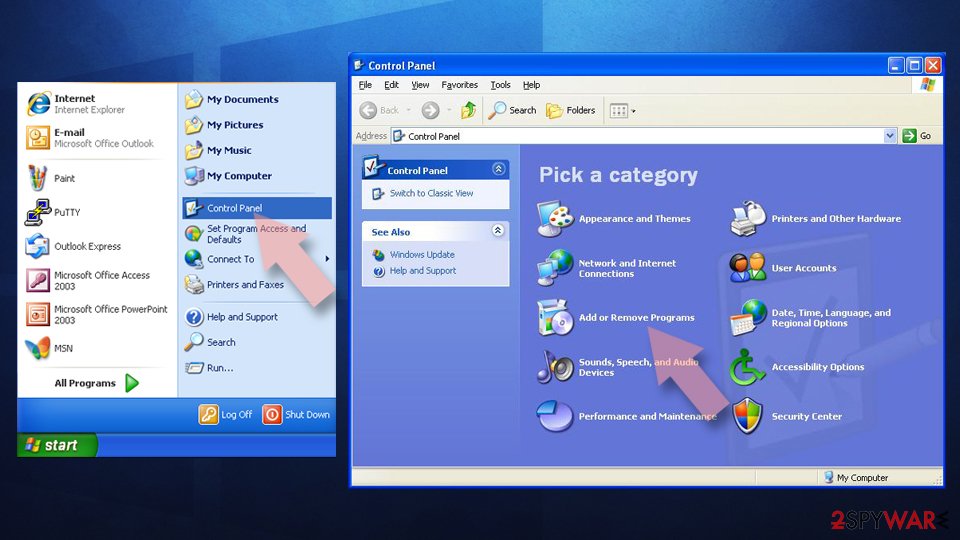
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
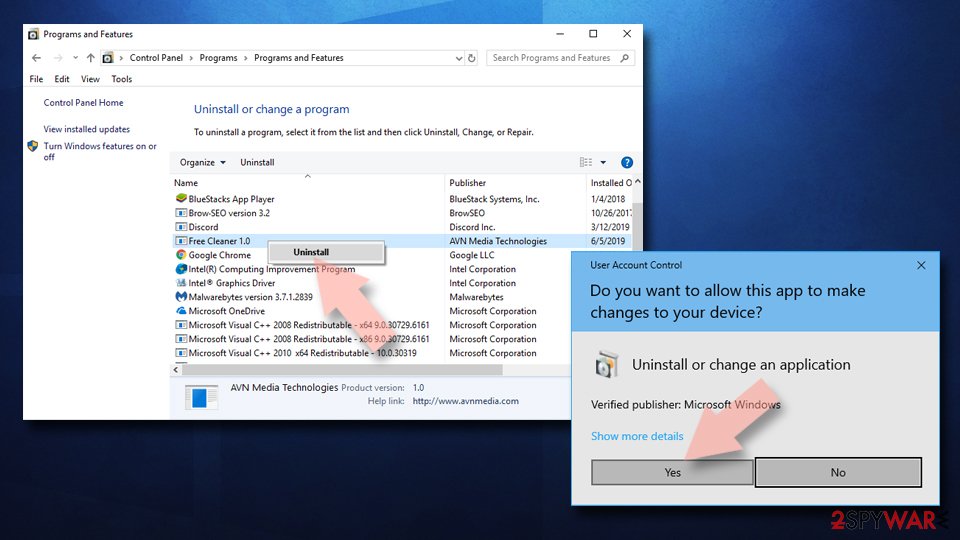
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
If this adware hijacks your Chrome, make sure you reset it to fix this web browser for good
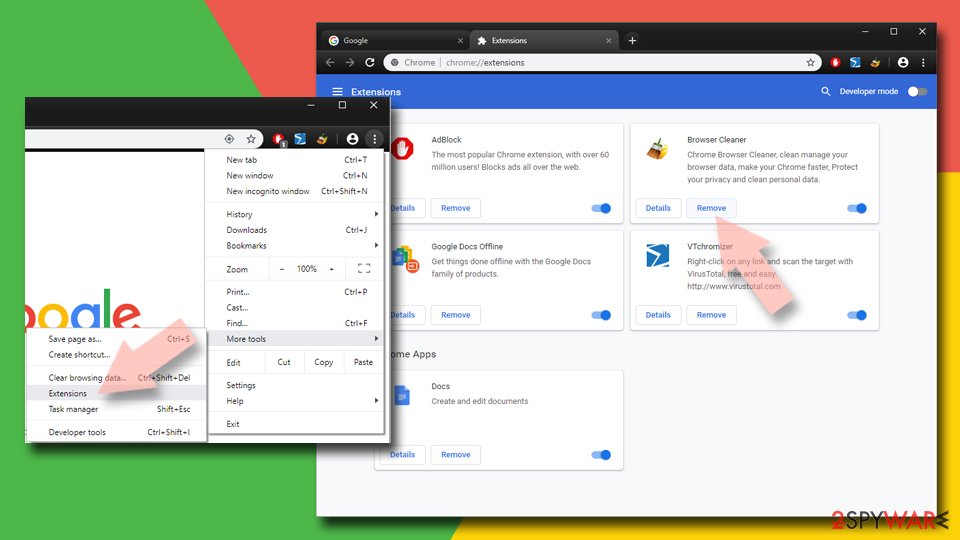
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
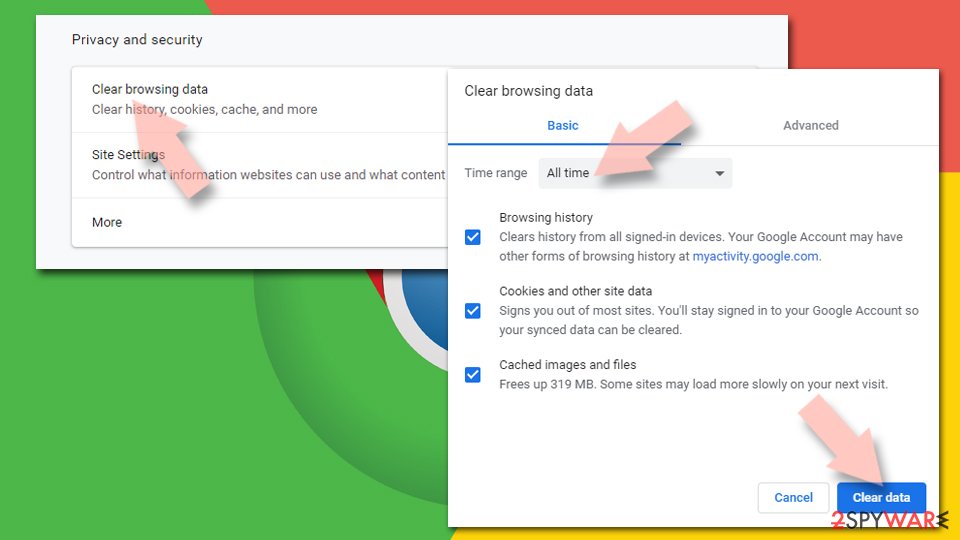
Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
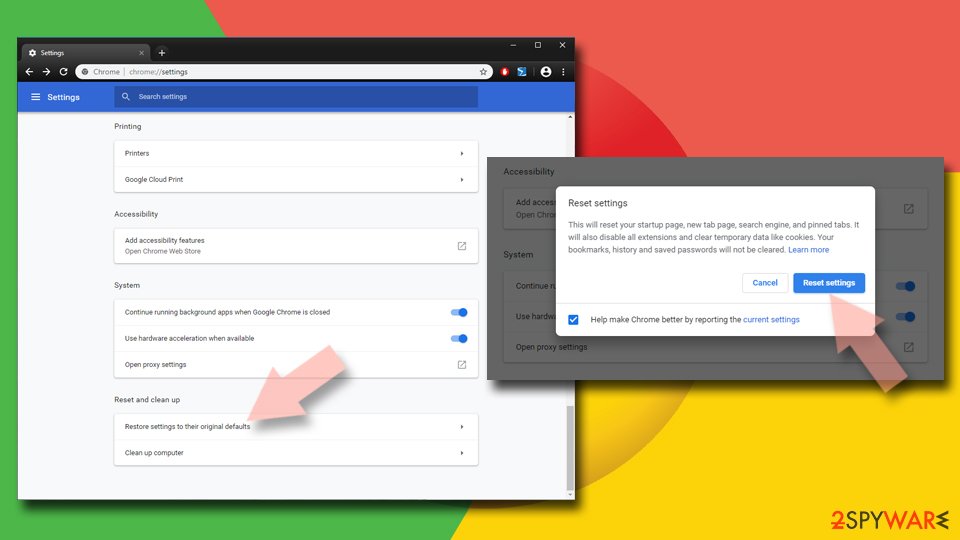
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Microsoft Edge
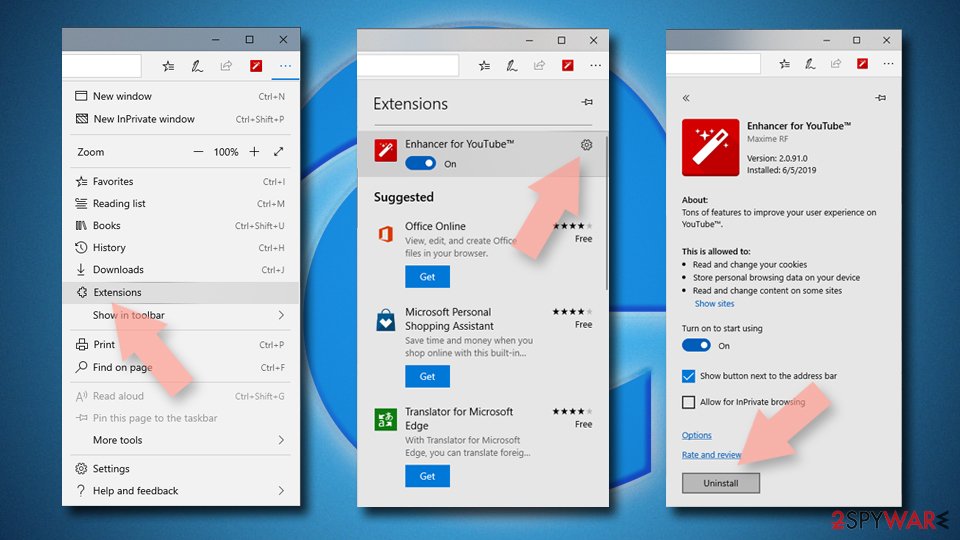
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.
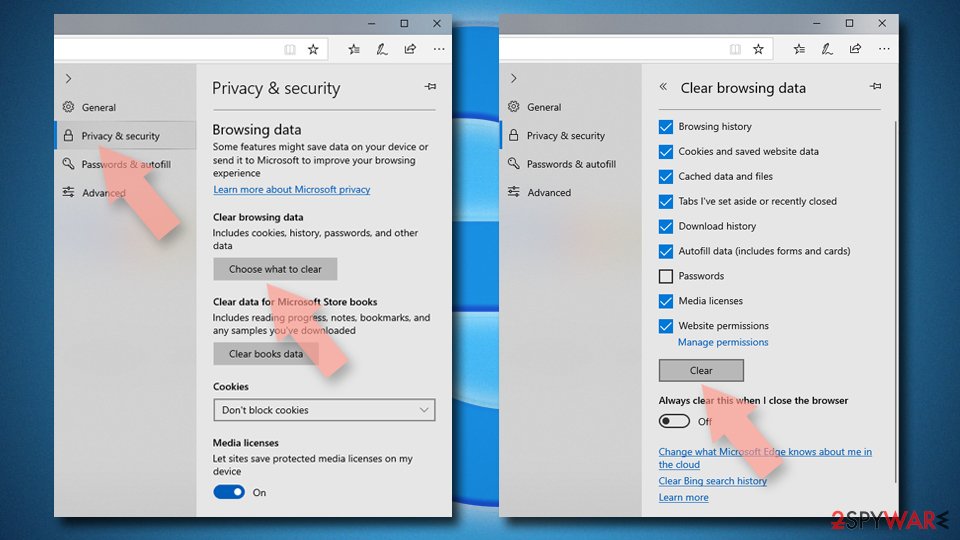
Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.
Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
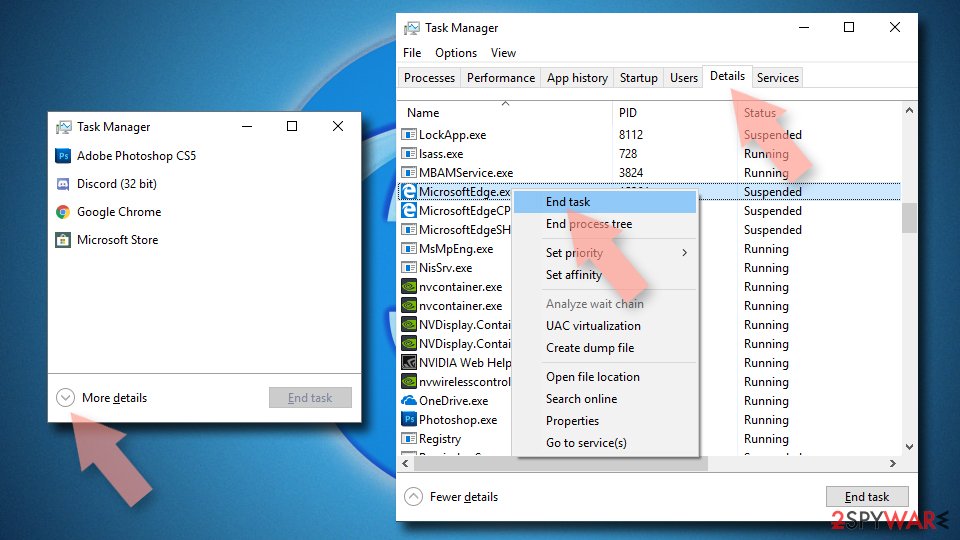
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.
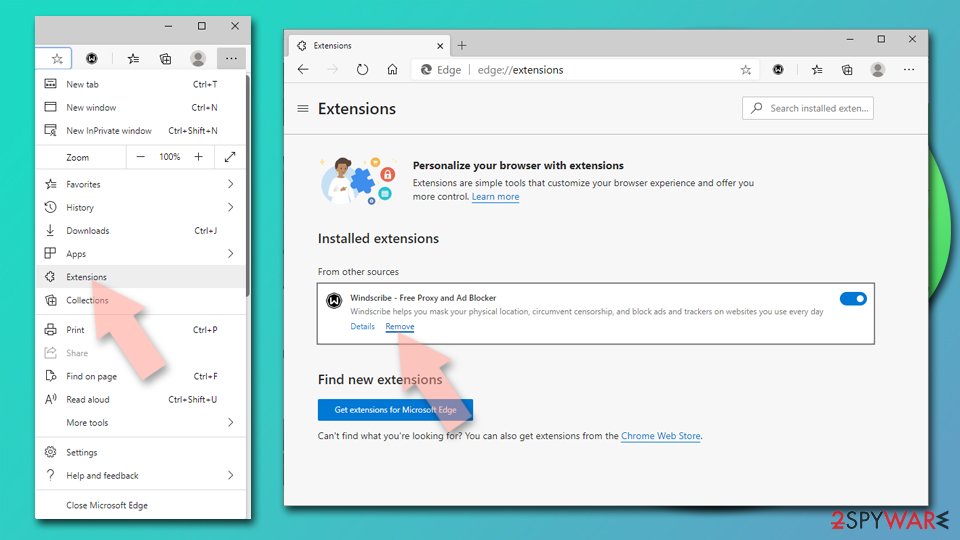
Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
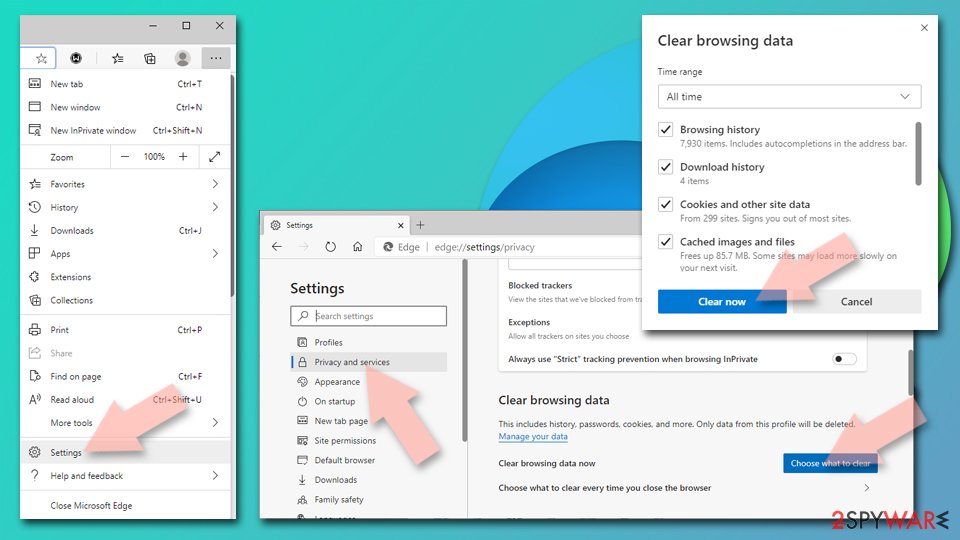
Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
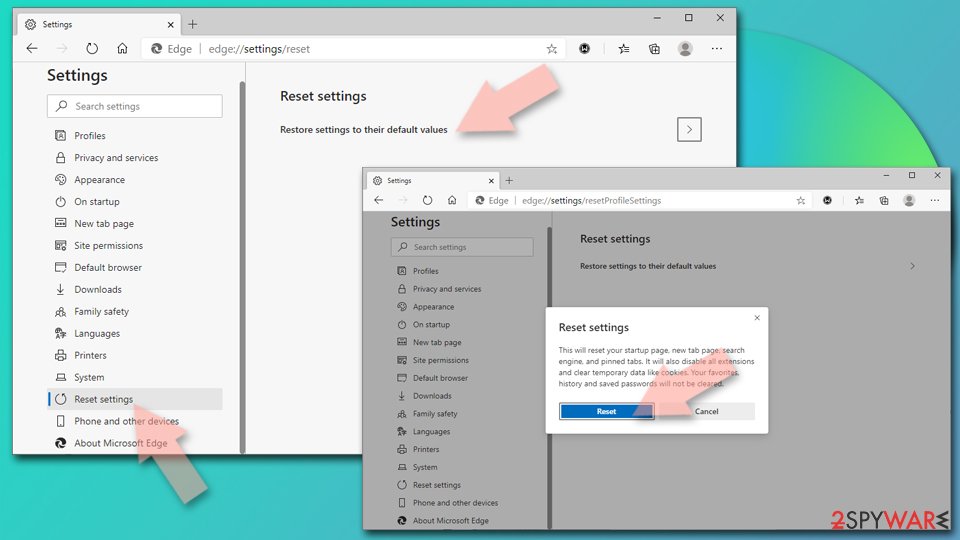
Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.
Remove from Mozilla Firefox (FF)
Don't forget to clean your browser from unwanted content, in case of additional changes
Remove dangerous extensions:
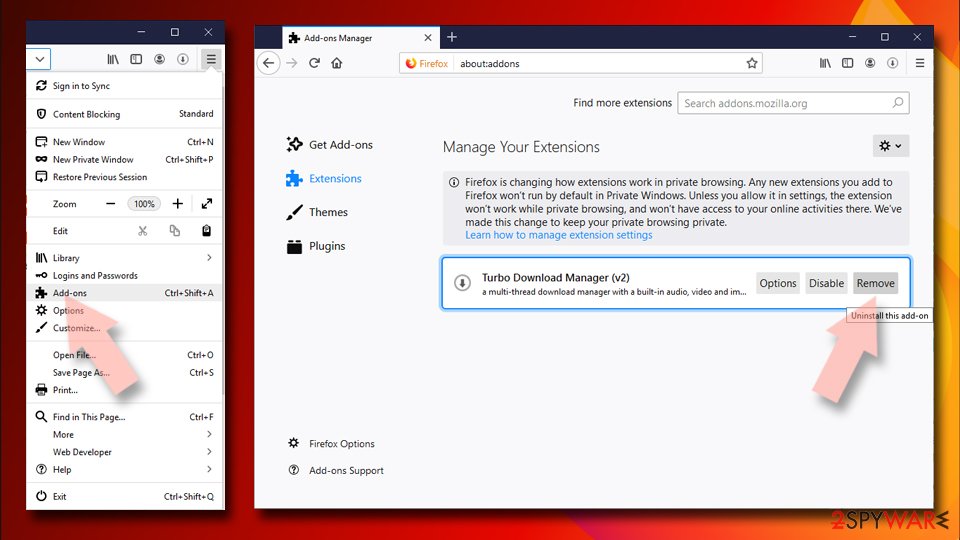
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
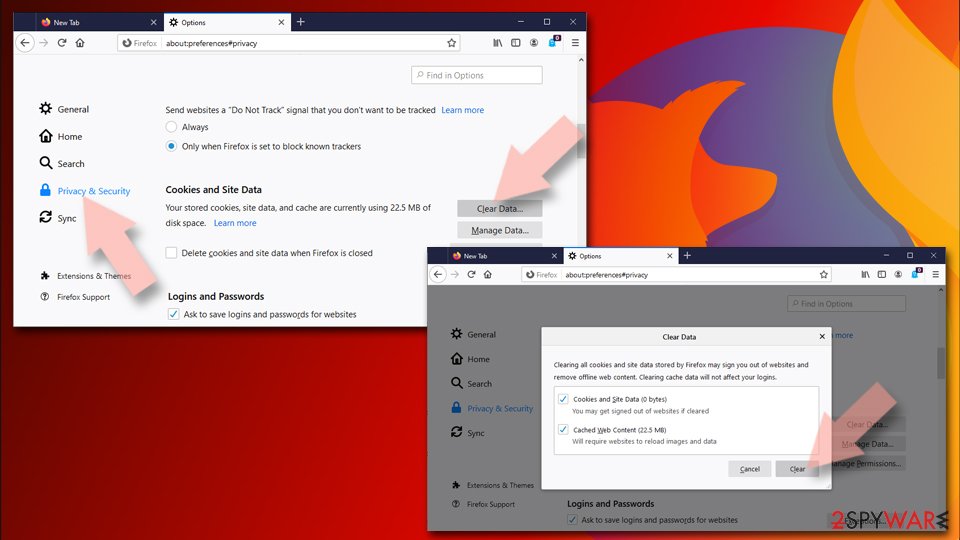
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
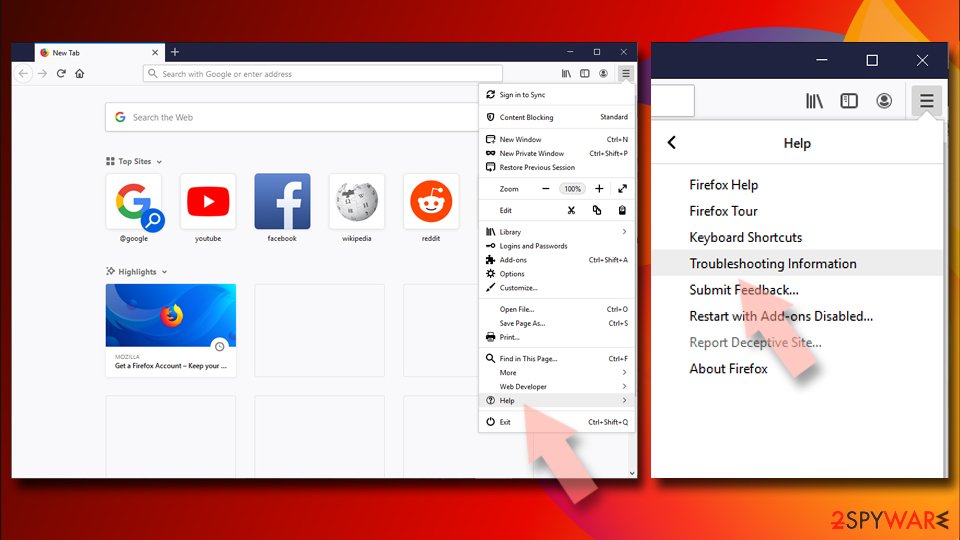
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
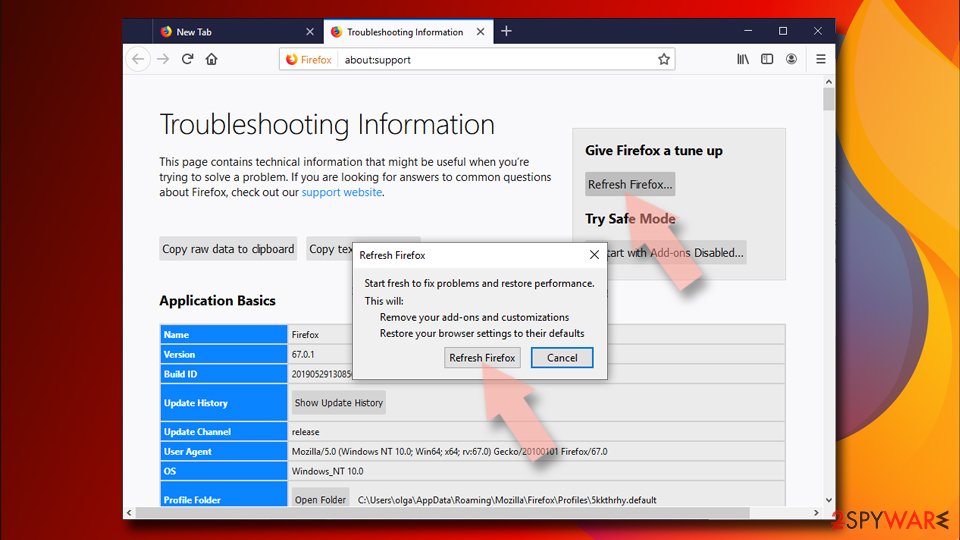
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
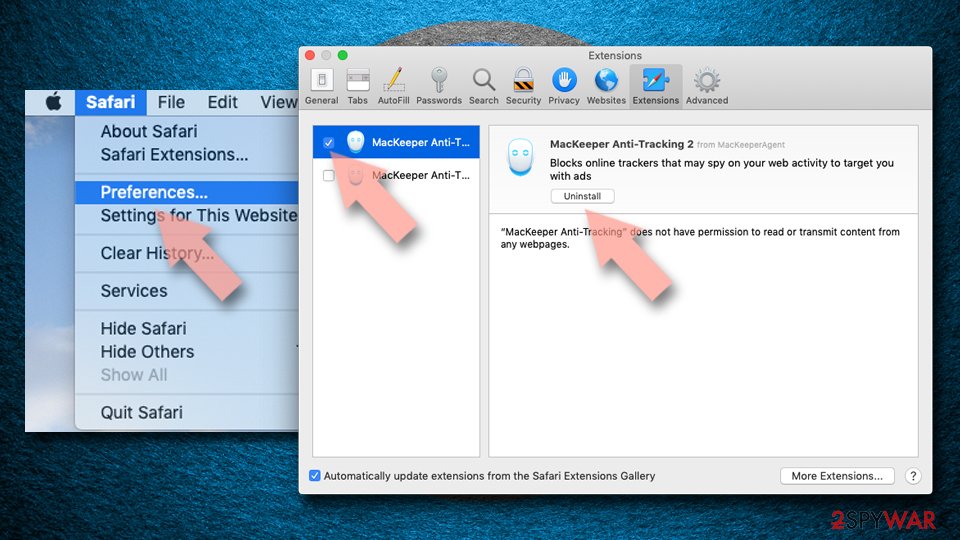
Remove dangerous extensions:
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
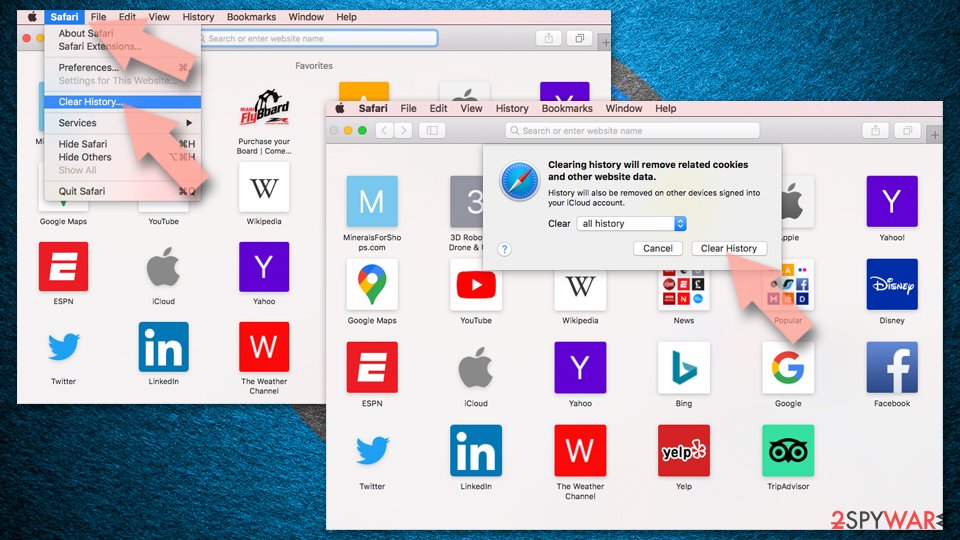
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
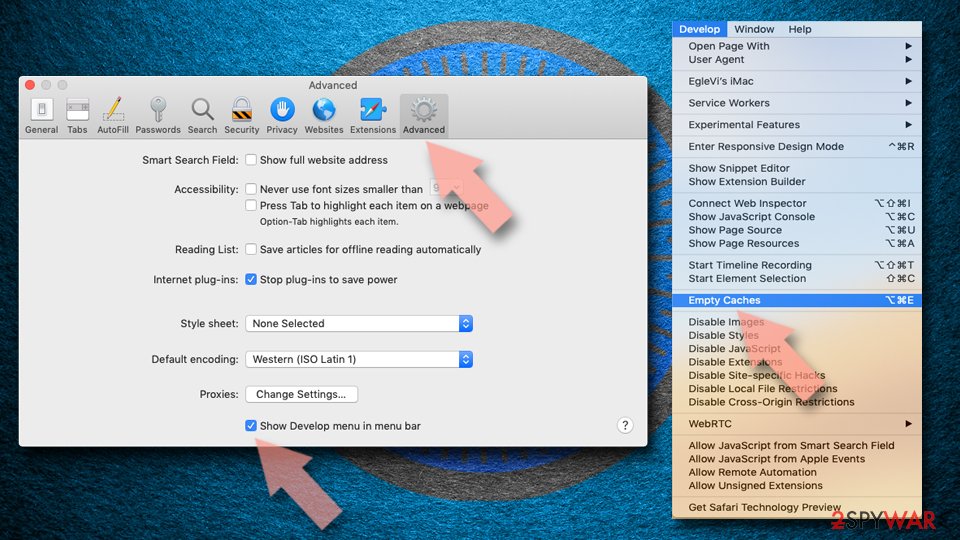
Reset Safari:
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
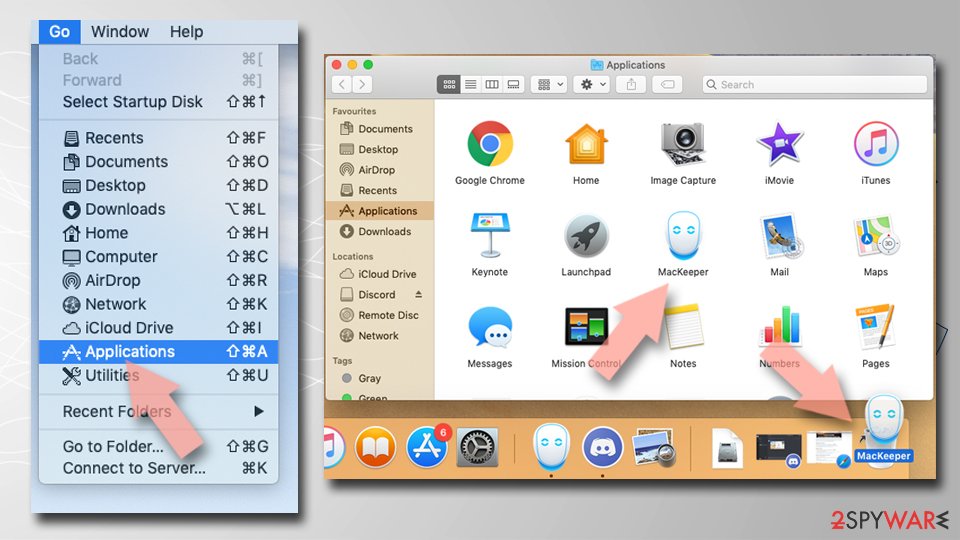
Remove the unwanted application:
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
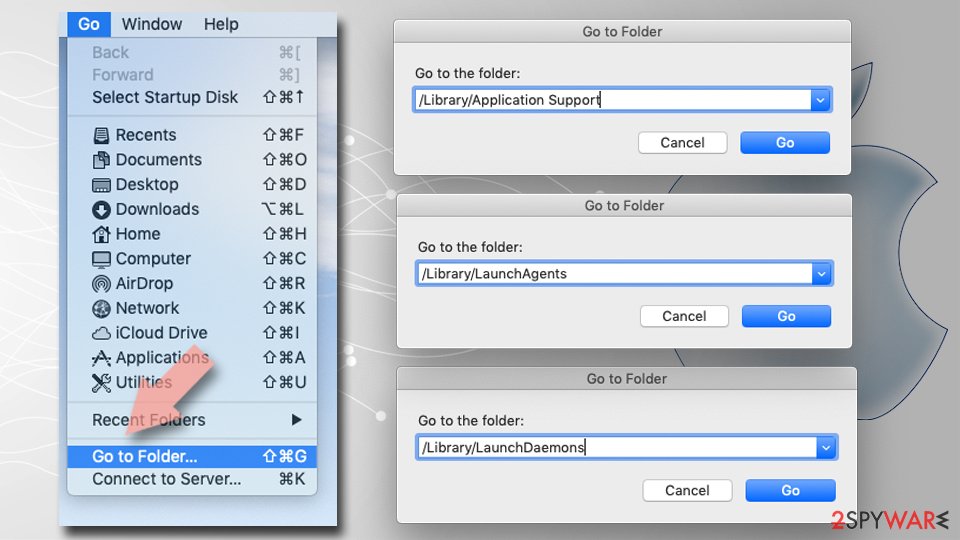
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
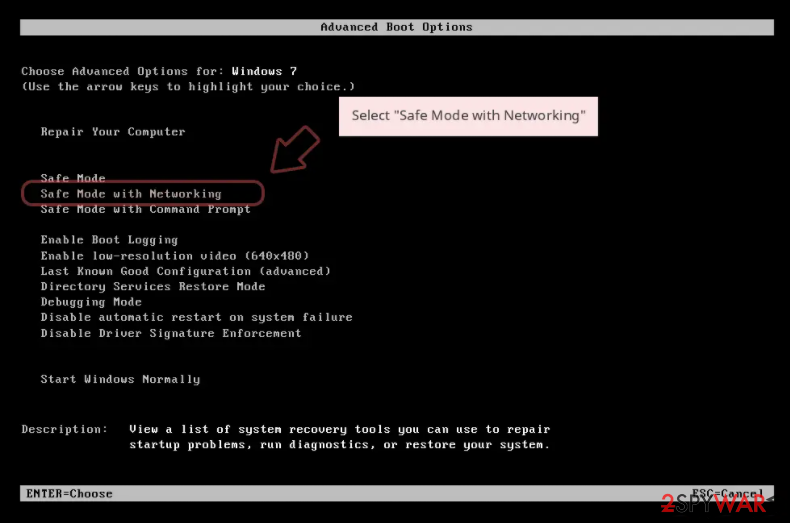
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
Windows 10 / Windows 8
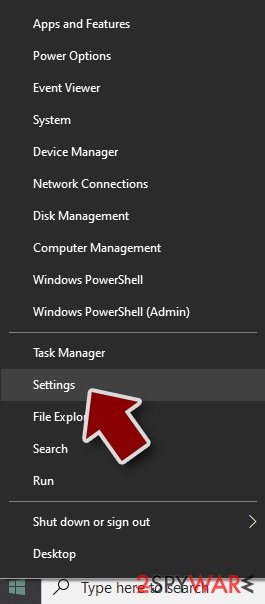
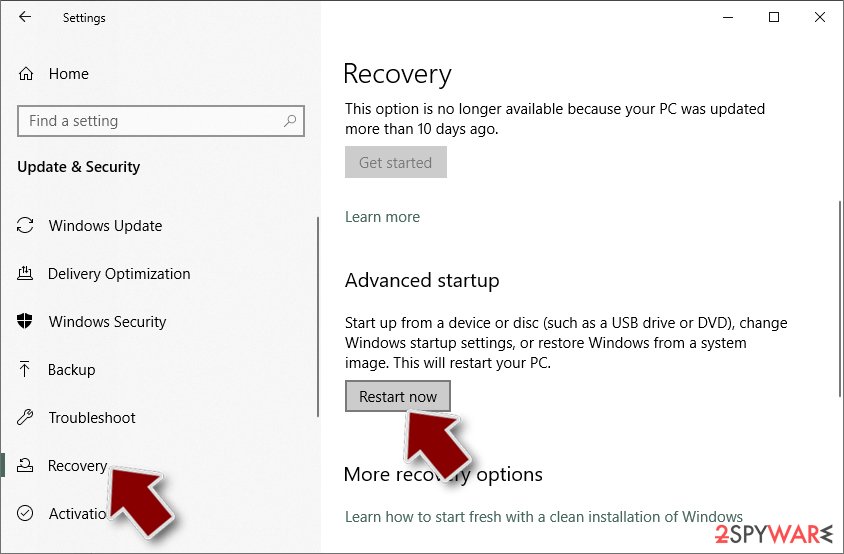
- Right-click on Start button and select Settings.
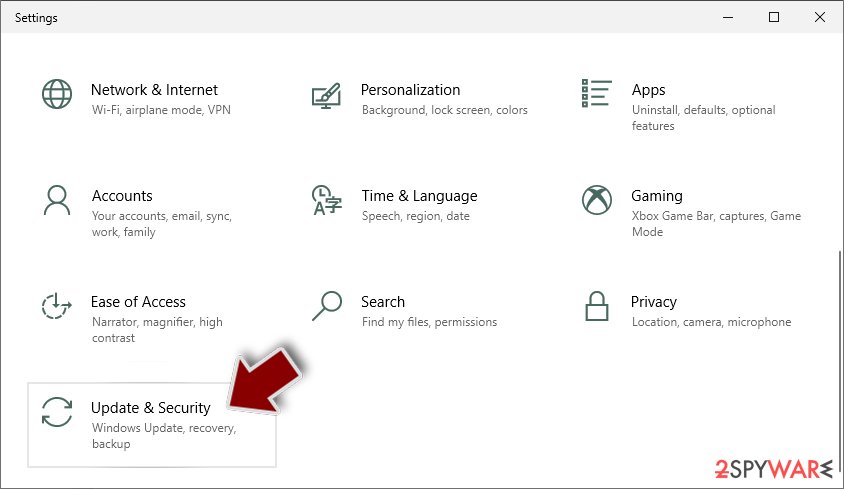
- Scroll down to pick Update & Security.
- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.
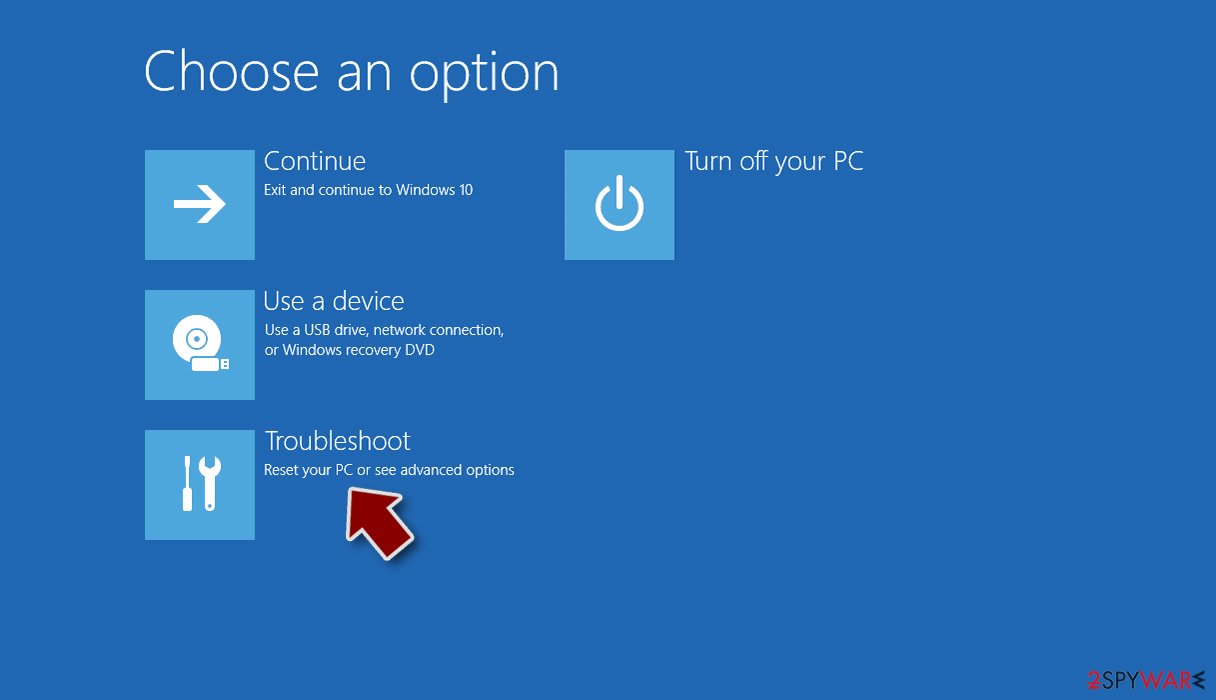
- Select Troubleshoot.
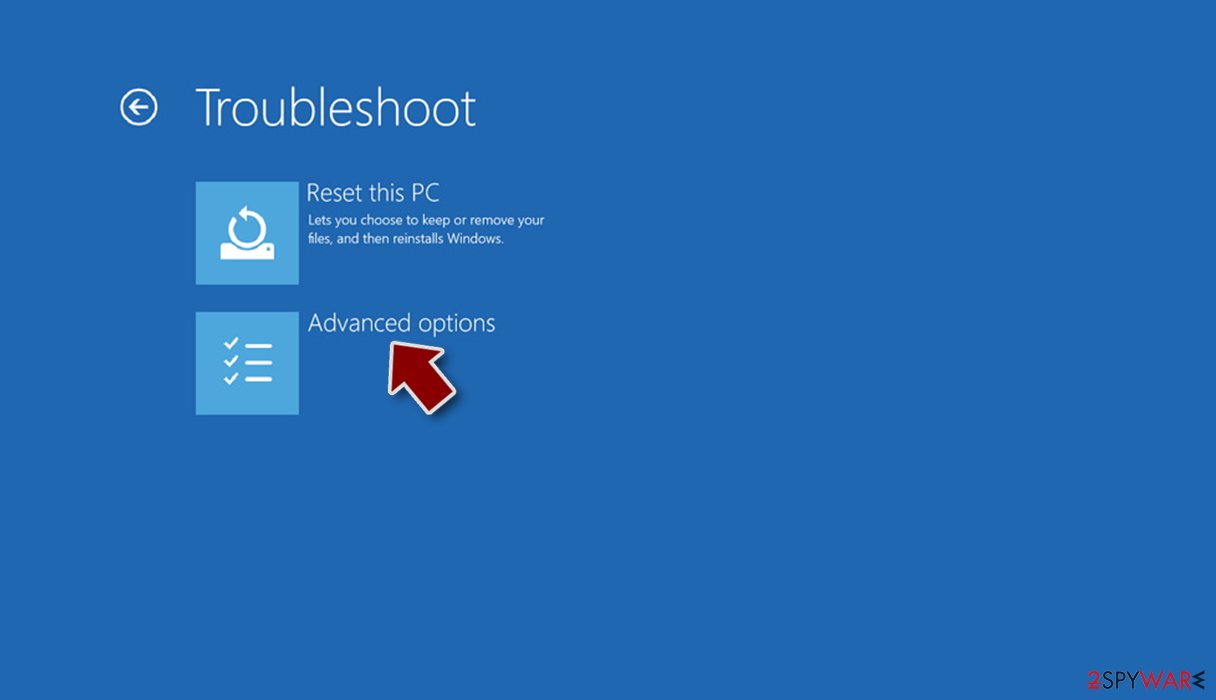
- Go to Advanced options.
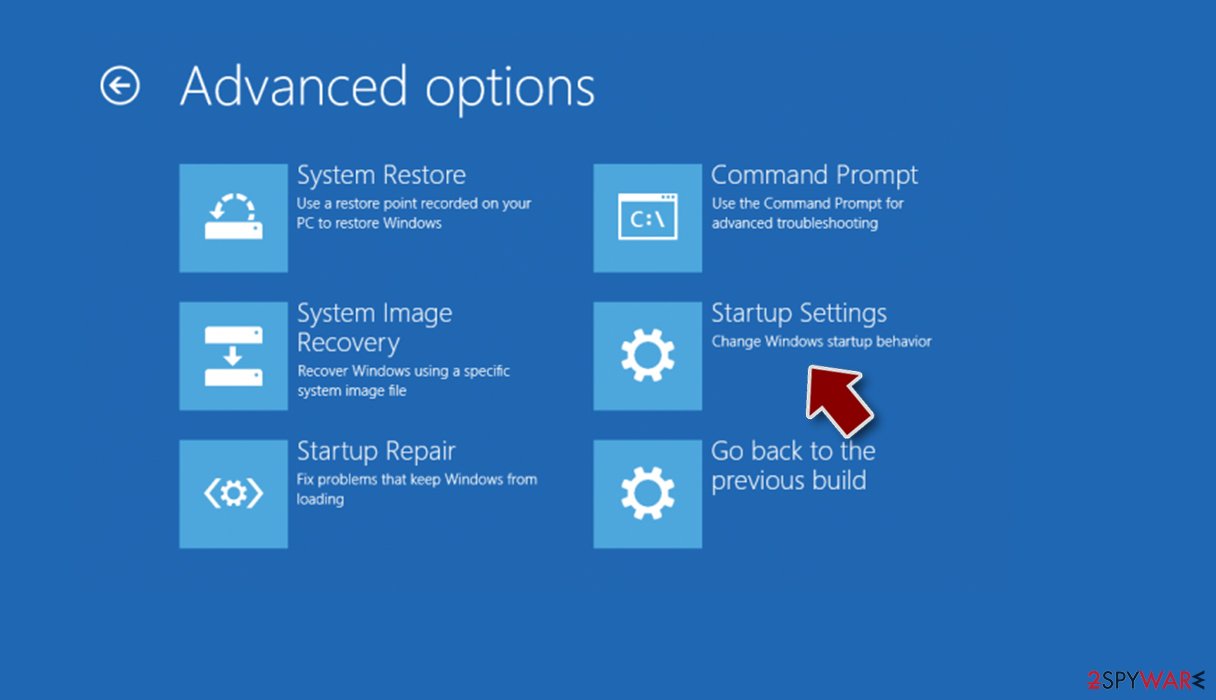
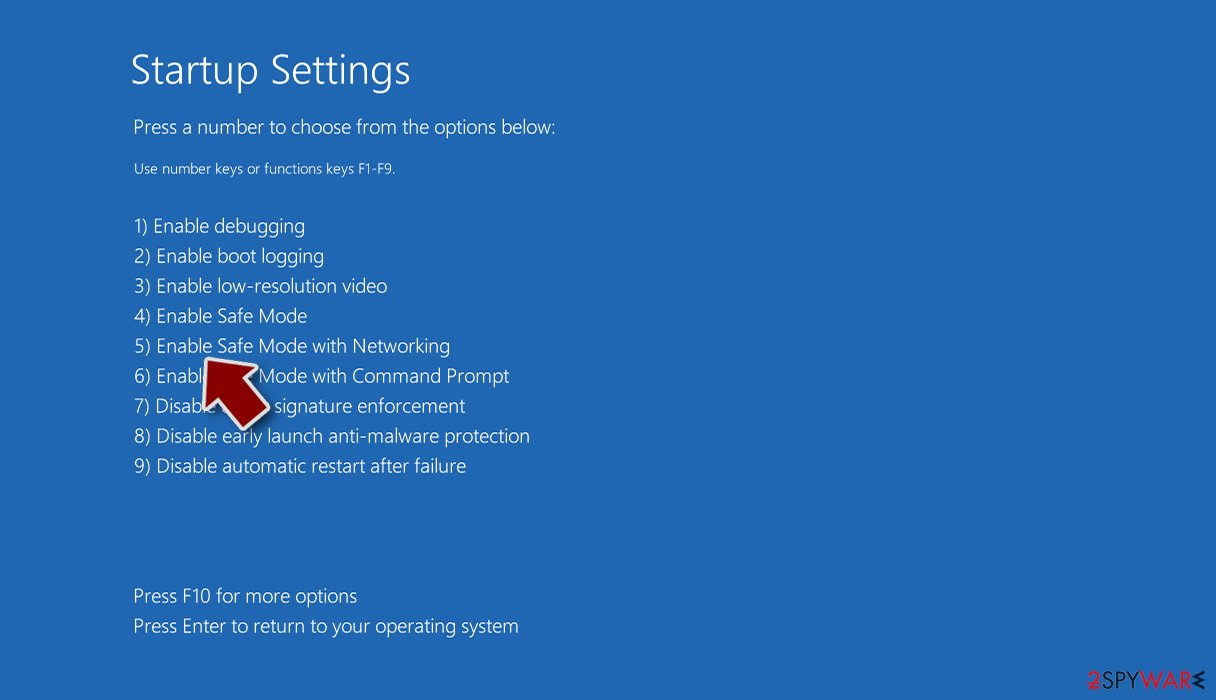
- Select Startup Settings.
- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.
Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
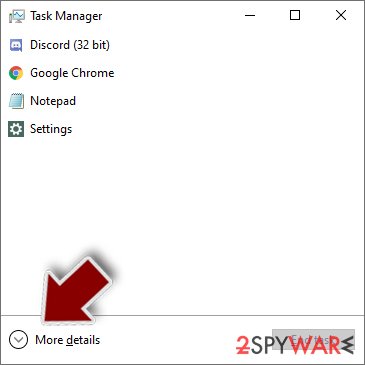
- Click on More details.
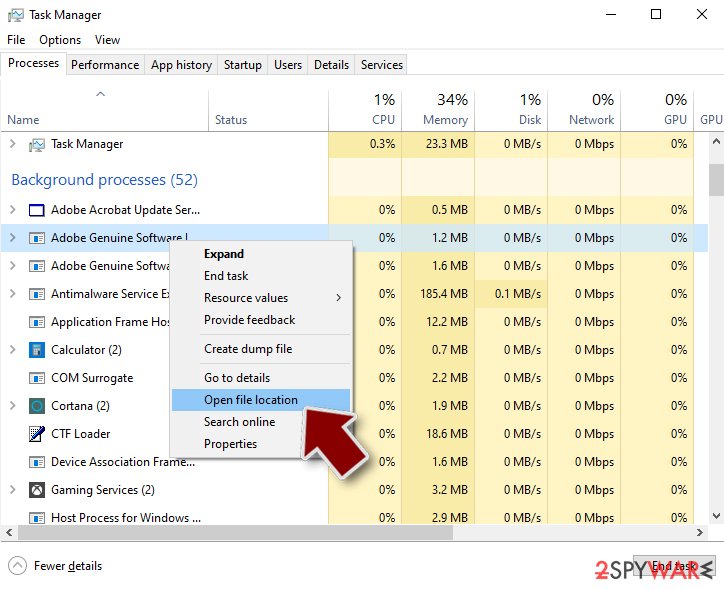
- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.
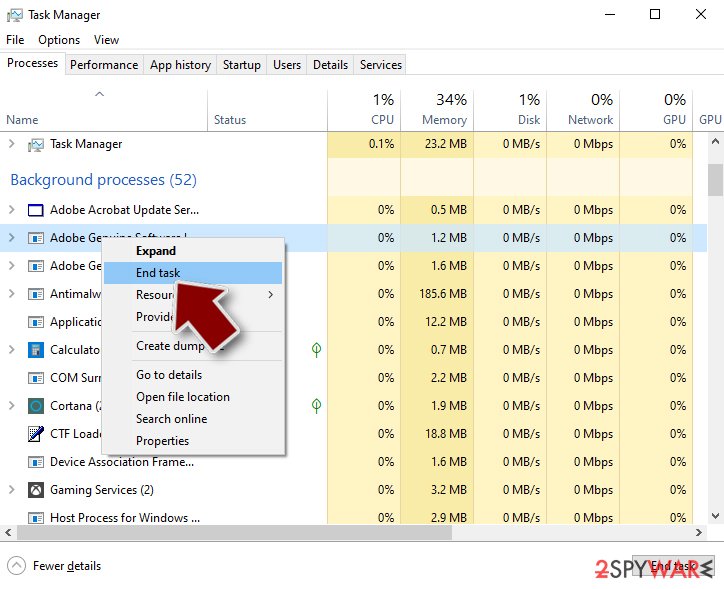
- Go back to the process, right-click and pick End Task.
- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.
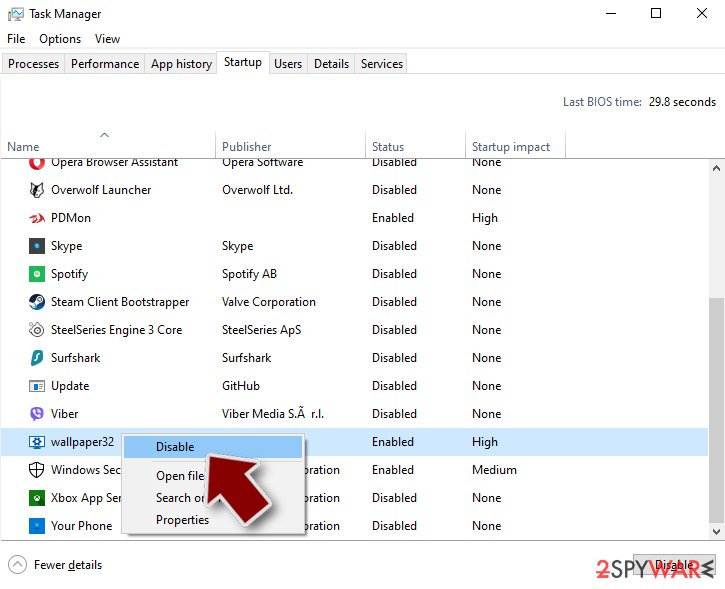
Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.
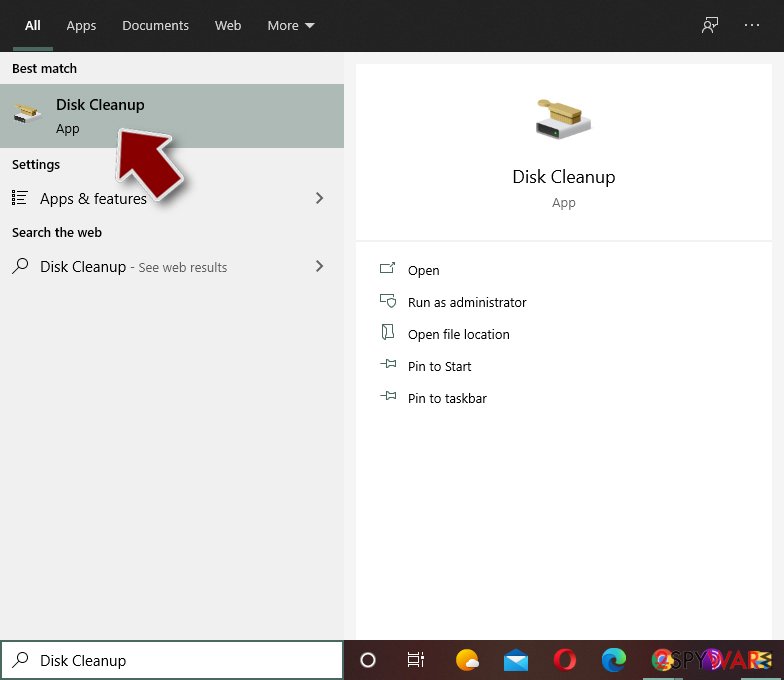
- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.
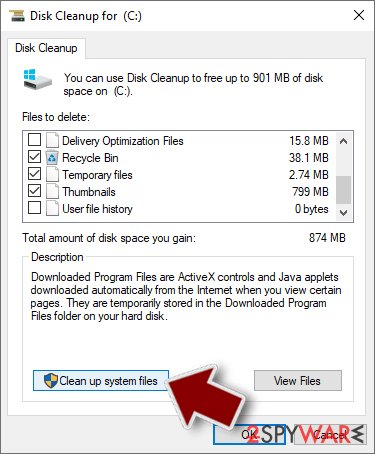
- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of May 2021 · not reviewed since
Get rid of the virus and end associated processes
There is a way to remove virus for good.
Keep in mind that it isn't a critical computer program and it hardly poses a threat to your security. However, Zondervirus.nl team says that its activities are highly annoying, to say at least. Besides, its intensive data tracking can cause a loss of specific information.
You can delete Web Helper using the steps given below. Make sure you uninstall this adware via Control Panel and then reset all web browsers which are affected.
If you are not willing to perform WebHelper removal manually, you can check the system for regular adware/browser hijacking software with anti-malware software. Please, make sure you update them to their latest version to have a full virus database.
From our report of May 2021 · not reviewed since
Video guide for WebHelper termination
Since there are a few files that can be left behind while uninstalling the program, you should take more steps and perform virus removal this way.
We have a video guide that shows you step-by-step what to fo. There are a few techniques needed for the thorough system cleaning, so follow the video and repeat all the shown procedures because WebHelper can be a persistent threat. There is no other way to end those possibly malicious processes caused by the tracking application besides fully cleaning the system.
TIP: Some computer experts suggest disabling automatic uTorrent updates to solve the problem. However, we do not consider such a move to be safe (speaking about your computer's security).
- First, end uTorrent process running on your computer. Simply press Ctrl + Alt + Del, select it and click End Task.
- Go to C:\Users\ \AppData\Roaming\uTorrent\updates and then open the folder named after the uTorrent version you're using. Inside this folder, you will find utorrentie.exe file. Do not do anything with it.
- Go back one folder and right-click anywhere in it. Select New > Text Document and name it however you want, let's say test.txt. Press anywhere in the folder to save the name and then open the text file you just created. Go to File>Save As.
- Now, choose the location to save the new file. Select the folder that contains utorrentie.exe file and saves the file under utorrentie.exe name here. You must select All files in the Save as type option.
- You will be asked whether you want to overwrite the file that already exists. Click Yes.
- You can now delete the test.exe file from the updates folder. Go to the folder containing the utorrentie.exe file. Right-click on this file and select Properties.
- In General tab, put a check on Read-only option in the Attributes section. Click Apply and OK.
After removal: passwords, accounts and prevention
Secure your accounts after the clean-up
Assume that whatever was saved in the browsers on this PC while the PC showed an unfamiliar process called utorrentie.exe in Task Manager has been copied:
- passwords
- cookies
- autofill data
Work from a clean device, or from this PC once the offline scan finds nothing.
Start with your main e-mail account, because it can reset everything else, then banking and payment, then social and gaming accounts. Change each password, sign out of all sessions and turn on two-step verification: Turn on two-step verification / secure a hacked account.
The full order, including crypto wallets and card replacement, is in securing your accounts after malware.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
Questions about WebHelper
Is utorrentie.exe safe?
It depends on where the file is and who signed it, not on the name. Open Task Manager, go to the Details tab, right-click utorrentie.exe and choose Open file location. A file inside Program Files or System32 with a valid digital signature from a known company is usually part of a legitimate program.
A file in AppData, Temp or ProgramData with no signature, especially one that restarts itself after you end it, is suspicious. If you cannot tie the process to anything you installed, uninstall recent unfamiliar programs and run a Microsoft Defender Offline scan.
Can I end utorrentie.exe in Task Manager?
Ending an unknown process is safe in the sense that Windows will warn you before you close anything critical, and a restart brings back whatever Windows needs. Ending utorrentie.exe will not remove it, though: if a task or startup entry launches it, it returns at the next sign-in.
Use ending the process as a test. If something important stops working, it belonged to a program you use. If nothing changes and it comes back by itself, find and disable its starter, delete the file and scan the PC.
Can I just delete utorrentie.exe?
Deleting utorrentie.exe by hand rarely removes WebHelper. While the trojan runs, Windows may refuse to delete the file, and if you succeed, a scheduled task, a service or a second copy may bring it back at the next restart.
The file can also be only one part of the infection: loaders and remote access tools often install other programs. Use the Microsoft Defender offline scan, which removes the file together with its startup entries before Windows loads, and then check startup items and scheduled tasks as described in the plan.
Can WebHelper spread to other devices on my network?
Most trojans aimed at home users stay on the PC they infected, but an attacker with remote access can look at the network, open shared folders and try passwords on other devices. Loaders sometimes deliver worms or ransomware that do spread.
Disconnect the PC while cleaning, run a full scan on other Windows PCs, change the router's admin password and the Wi-Fi password if they were saved on the infected PC, and update the router's firmware. If other PCs show the same detection, treat them as infected too.
Can I keep using the PC while WebHelper is on it?
Not for anything that matters. As long as the program behind an unfamiliar process called utorrentie.exe in Task Manager runs, it can see what you type and what the browser stores, and it may download more malware. Disconnect the PC from the internet while you remove it, and do your banking, e-mail and password changes from another device.
Once the offline scan finds nothing and the sign does not return after a few restarts, normal use is fine. If the scan keeps finding new items, or you cannot remove the startup entry, a reset of Windows is the safer choice.
Should I reset my PC because of WebHelper?
Only if the signs point to deeper access. Reset when you see an unfamiliar process called utorrentie.exe in Task Manager again after removal, when Windows Security cannot start or update, when remote access tools you did not install keep appearing, or when you simply cannot trust the PC any more.
Otherwise, the plan in this guide plus an offline scan is enough. If you do reset, choose Remove everything and Cloud download for a fresh copy of Windows, restore only documents and photos, and reinstall programs from their official sites. Change important passwords from the clean system afterwards.
What are the signs of a trojan infection?
Most trojans try to leave no visible signs, so look for side effects. Common ones:
- Windows Security turned off or unable to update
- new entries in Startup apps or Task Scheduler
- programs in Installed apps you did not install
- browser settings that changed by themselves
- unusual network activity while the PC is idle
- password-reset or login-alert e-mails you did not trigger
None of these proves an infection on its own. Together with an antivirus alert naming WebHelper, they are a strong reason to follow the full plan.
Is WebHelper a known trojan?
Not as a documented family, at least not yet. What is known is the visible sign, an unfamiliar process called utorrentie.exe in Task Manager, which matches a hidden program working for someone else.
New threats are often seen by victims weeks before researchers publish anything about them. Treat WebHelper as you would any trojan:
- remove what starts it
- run an offline scan
- change passwords from another device
If a scan reports a detection name, keep it; it usually reveals the family and whether it is known to download other malware. We update this guide when an analysis appears.
Can a normal remote support program be a backdoor?
Yes. Tools such as AnyDesk, TeamViewer and ScreenConnect are legitimate, but whoever controls the account behind them controls the PC. Scammers install them during fake support calls, and some trojan campaigns install them silently because antivirus programs do not flag a genuine, signed product.
If you find one you did not set up, uninstall it, check Startup apps for related entries and change passwords from another device. If money or accounts were involved, call your bank and report the incident.
Will Fortect remove WebHelper?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For WebHelper, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Wikipedia: μTorrent (read October 7, 2026)
- Reddit: Steam Client WebHelper Virus??? (read October 7, 2026)
- ZonderVirus: Zondervirus (read October 7, 2026)
- FTC: How to recognize, remove and avoid malware (read October 7, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 7, 2026)