
Windows Active HotSpot: what it is and how to remove it
Windows Active HotSpot is a dangerous rogue anti-spyware, which belongs to same cyber crooks as Windows Expert Console, Windows Cleaning Toolkit and many other rogues. In most of the cases, users don't even notice their infiltration moment because they always rely on trojans when they try to infect computers.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If iexplore.exe returns after removal, a full scan can find the entry that brings it back.
Do it yourself · free Remove Windows Active HotSpot yourself 5 steps, about 15 minutes, no software needed.
Start the steps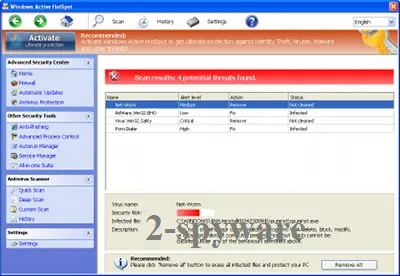
Windows Active HotSpot: summary
| Detection names | No Microsoft detection name is known |
|---|---|
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Name | Windows Active HotSpot |
| Type | Rogue antivirus |
| Symptoms | An unknown process in Task Manager |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 4 more facts
| Files and processes | iexplore.exe |
|---|---|
| Evidence | One write-up by a security site; details still limited |
| First seen | 5 December 2013 |
| Facts checked | 7 October 2026 |
From our report of Dec 2013 · not reviewed since
What Windows Active HotSpot is
Windows Active HotSpot is a dangerous rogue anti-spyware, which belongs to same cyber crooks as Windows Expert Console, Windows Cleaning Toolkit and many other rogues.
In most of the cases, users don't even notice their infiltration moment because they always rely on trojans when they try to infect computers. However, no matter that it's really hard to notice Windows Active HotSpot's or other rogue's infiltration, you won't miss its fake alerts and system scanners that typically report about tons of viruses detected.
Once they 'inform' users that their PCs are in trouble, they offer purchasing licensed version and fixing everything. Please, do NOT believe these offers because in reality they seek the only thing – to mislead your into thinking that you must purchase Windows Active HotSpot's license. Instead of that you must do another thing – remove Windows Active HotSpot from the system ASAP.
Is Windows Active HotSpot a real security program?
- File:
iexplore.exe
From our report of Dec 2013 · not reviewed since
HOW CAN Windows Active HotSpot INFECT MY COMPUTER?
Just like we mentioned previously, Windows Active HotSpot infiltrates computers secretly.
This is possible with the help of trojan horse, which is also used for downloading malicious files on the system and making several system modifications. Once trojan prepares computer for Windows Active HotSpot, virus starts displaying continuous alerts and system scanners that all announce about viruses. For example:
You must NEVER believe these fake alerts because they seek to make you spend your money on useless software! Besides, if you fall for purchasing Windows Active HotSpot's license, you may notice additional problems on your computer, such as browser's redirects to unknown websites, the loss of your personal information and similar issues.
That's why you must ignore all alerts that belong to this rogue anti-spyware and remove Windows Active HotSpot from the system. For that you can follow this guide:
From our report of Dec 2013 · not reviewed since
More from our earlier report on Windows Active HotSpot
- Error Attempt to run a potentially dangerous script detected.Full system scan is highly recommended.
- Error System data security is at risk!To prevent potential PC errors, run a full system scan.
- Firewall has blocked a program from accessing the Internet c:\windows\system32\iexplore.exe is suspected to have infected your PC.
- This type of virus intercepts entered data and transmits themto a remote server.
How to remove Windows Active HotSpot
Nothing it reports is real.
These steps remove it and undo a payment if you made one.
Step 1: Do not pay, and undo a payment if you made one
Windows Active HotSpot reports problems to sell a licence: the "threats" or "errors" it lists are invented or harmless leftovers. If you already paid, ask your card issuer to dispute the charge and cancel the subscription both in the seller's account and through your bank.
If you called a phone number it showed and let someone connect, treat the PC as remotely accessed and remove the remote tool. Uninstalling it from Windows 11 or Windows 10 does not cancel a subscription by itself.
Full procedure with screenshots: What to do after paying a scammer
Step 2: Uninstall programs you did not mean to install
Open Settings > Apps > Installed apps in Windows 11, or Settings > Apps > Apps & features in Windows 10, and sort the list by install date. Look at what appeared around the day the problem started and uninstall every program you do not recognise or did not choose.
Free converters, PDF and video tools, "system optimizers" and unknown browsers are the usual carriers of Windows Active HotSpot. If a name is unclear, search for it before you remove it, so you do not uninstall a driver or a Windows component.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 3: Remove it from startup
Whatever Windows Active HotSpot installed usually starts with Windows.
Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 5: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
From our report of Dec 2013 · not reviewed since
HOW TO REMOVE Windows Active HotSpot?
If you think your PC is infected with Windows Active HotSpot, you should immediately check it with updated anti-spyware.
If you were tricked into purchasing licensed version, don't wait and connect your credit card company.
The latest parasite names used by FakeVimes:
Questions about Windows Active HotSpot
What is iexplore.exe and why is it running?
Every process is started by something:
- a program you installed
- a Windows service
- a scheduled task
- a startup entry
To learn why iexplore.exe runs, find its file with Open file location in Task Manager, then look for an entry pointing to that file in Settings > Apps > Startup and in Task Scheduler.
Sort Installed apps by date to see what arrived when the process first appeared. Once you know the owner, you can decide whether to keep it, switch it off at startup or uninstall it completely.
Can I end iexplore.exe in Task Manager?
Ending an unknown process is safe in the sense that Windows will warn you before you close anything critical, and a restart brings back whatever Windows needs. Ending iexplore.exe will not remove it, though: if a task or startup entry launches it, it returns at the next sign-in.
Use ending the process as a test. If something important stops working, it belonged to a program you use. If nothing changes and it comes back by itself, find and disable its starter, delete the file and scan the PC.
Do I need to buy antivirus after removing Windows Active HotSpot?
No. Windows 11 and Windows 10 include Microsoft Defender in Windows Security, which provides real-time protection, scheduled scans, the offline scan and protection against unwanted apps at no cost. Keep it switched on and updated, and turn on Reputation-based protection under App & browser control.
If you prefer a third-party product, buy it from the vendor's own site after reading independent test results, never from a pop-up or a phone call. The lesson of Windows Active HotSpot is that security offers which arrive unasked are the ones to avoid.
Why does Windows Active HotSpot look so official?
Because copying the design costs nothing and makes people trust it. The program behind an unfamiliar process called iexplore.exe in Task Manager borrows Windows colours, icons and wording, sometimes even the name of a well-known security brand. None of that gives it access to real security information.
A real alert can be checked in seconds: open Windows Security from the Start menu and look at Protection history. If nothing is listed there, the official-looking window is fake, and the program that draws it is what needs to be removed.
Should I reset my PC because of Windows Active HotSpot?
Only if the signs point to deeper access. Reset when you see an unfamiliar process called iexplore.exe in Task Manager again after removal, when Windows Security cannot start or update, when remote access tools you did not install keep appearing, or when you simply cannot trust the PC any more.
Otherwise, the plan in this guide plus an offline scan is enough. If you do reset, choose Remove everything and Cloud download for a fresh copy of Windows, restore only documents and photos, and reinstall programs from their official sites. Change important passwords from the clean system afterwards.
I let a technician connect to my PC because of Windows Active HotSpot. Is it safe now?
Not until you check. While connected, the caller could install other programs, create a user account or look at saved passwords. Disconnect from the internet, uninstall the remote access program and anything else installed during the call, and run a full scan and the Microsoft Defender offline scan.
From another device, change your e-mail and banking passwords and turn on two-step verification. If the caller opened your online banking, call the bank today. A reset of Windows is the safest option if you cannot tell what was done.
Did Windows Active HotSpot steal my information?
Not by itself, as far as reports show. Programs that display an unfamiliar process called iexplore.exe in Task Manager are built to scare people into paying or calling; they rarely take data on their own.
The risk comes from what you did in response: typing card details into the program, or letting a caller connect to your PC. If you did neither, uninstalling the program is enough. If you did either, treat that information as exposed:
- block the card
- change passwords from another device
- remove any remote-access tool that was installed
What should I do if I already clicked or replied to Windows Active HotSpot?
Stop all contact, do not click anything else and secure your accounts right away. If you typed a password, change it at once from a clean device, then turn on two-factor authentication.
If you gave card or bank details, call the bank on the number printed on your card and ask to block or replace it. If you installed something or allowed remote access, disconnect from the internet and follow the removal plan. Keep screenshots and the message, because they help when you report it.
Will Fortect remove Windows Active HotSpot?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Windows Active HotSpot, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- FTC: How to recognize, remove and avoid malware (read October 7, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 7, 2026)
- Microsoft Learn: How Microsoft names malware (read October 7, 2026)