
XZZX ransomware: what it is and how to recover your files
XZZX ransomware is a November 2017 CryptoMix variant that encrypts your files with AES and RSA and renames them to a 32-character code ending in .XZZX. No free decryptor is confirmed for it, so remove the program and restore from a clean backup; do not pay.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Make sure nothing will rename more files to .XZZX: an automatic scan checks the PC first.
Do it yourself · free Remove XZZX ransomware yourself 6 steps, about 18 minutes, no software needed.
Start the steps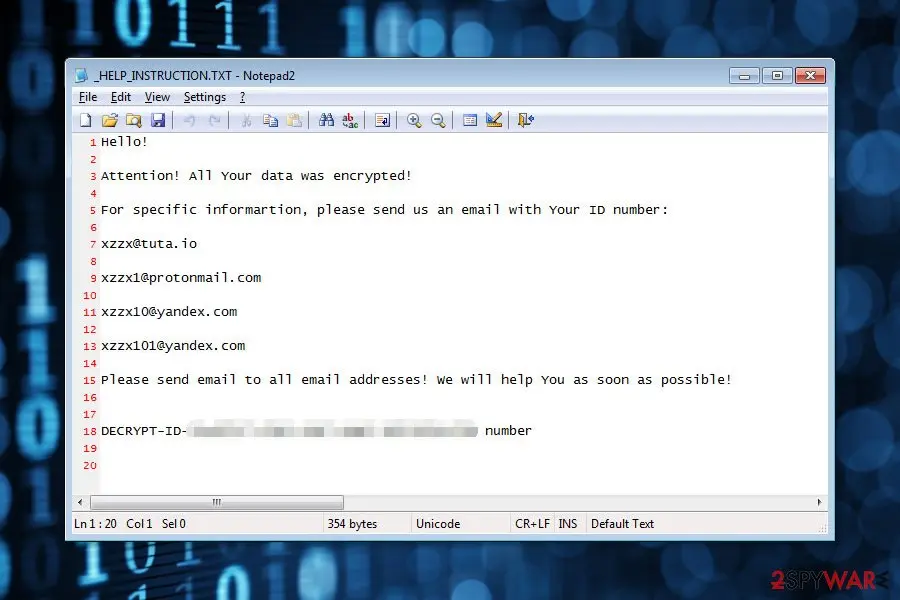
XZZX ransomware: summary
| Type | File-encrypting ransomware (CryptoMix family) |
|---|---|
| Risk | High: files are encrypted with AES and RSA, shadow copies are deleted and no free decryptor is confirmed |
| Symptoms | Files renamed to [32 characters].XZZX, _HELP_INSTRUCTION.TXT in folders, files that will not open |
| How to get rid of it | Disconnect, scan with Microsoft Defender Offline and Safe Mode, then restore from a clean backup; see the plan |
| Our check | Source check on 6 October 2026 (BleepingComputer, PCrisk, Avast, Coveware, No More Ransom); we did not run the malware |
| First seen | 13 November 2017 (BleepingComputer); our first report 14 November 2017 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 12 more facts
| Name | XZZX ransomware, XZZX CryptoMix, XZZX virus |
|---|---|
| Encrypted file extension | .XZZX after a 32-character name |
| Ransom note | _HELP_INSTRUCTION.TXT, quoted below |
| Decryptor | None confirmed for XZZX; CryptoMix tools exist for older versions |
| Contact | Four e-mail addresses, no wallet and no price |
| Detection names | No Microsoft detection name is known from public sources; scan results may vary |
| Evidence | 0 write-ups by security sites; no sample analysed yet |
| Encrypted files | .XZZX |
| Free decryptor | No free decryptor is known (checked 6 October 2026) |
| Distribution | Typically cracked programs, keygens and game cheats, fake installers, e-mail attachments, and Remote Desktop with weak passwords in small offices |
| Damage | Files on the PC and connected drives encrypted, restore points often deleted, sometimes a password stealer installed as well |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against BleepingComputer's reports on XZZX and the .0000 variant, PCrisk, Avast, Coveware, the No More Ransom list and Microsoft Support. We did not run the malware, and ransomware has no site to test.
What XZZX ransomware is
XZZX is a November 2017 variant of the CryptoMix ransomware family: it encrypts your files with AES and RSA, renames each one to a 32-character code ending in .XZZX, and leaves a note that names no price and no wallet, only four e-mail addresses.
- Family
- CryptoMix (earlier versions were also called CryptFile2, Zeta and CryptoShield)
- Discovered
- 13 November 2017, by Lawrence Abrams of BleepingComputer
- Extension
- A 32-character code plus
.XZZX, for example0D0A516824060636C21EC8BC280FEA12.XZZX - Note
_HELP_INSTRUCTION.TXT, placed in the folders it encrypted- Runs from
C:\ProgramData\[random].exe(BleepingComputer)
How the XZZX story went
March 2016
CryptoMix first spotted
Avast dates the first sightings to March 2016. In early 2017 its authors renamed it CryptoShield.
21 February 2017
A free decryptor for offline keys
Avast and CERT.PL released a decryptor for files encrypted with the program's fixed offline key. Its extension list (
.CRYPTOSHIELD,.scl,.rscl,.lesli,.rdmk,.code,.rmd) does not include.XZZX.13 November 2017
BleepingComputer finds XZZX
Lawrence Abrams reports a CryptoMix variant that appends
.XZZX, with the same encryption and new contact addresses.14 November 2017
Our first report
We described the note, the RSA and AES encryption and the four addresses. A reader asked how to clean a PC when most files were backed up.
The same note on our 2017 report artwork. The woman and the red banner are decoration; the Notepad2 window is the real note. 16 to 17 November 2017
The .0000 variant
MalwareHunterTeam finds a variant that adds
.0000. BleepingComputer reports that it holds the same 11 RSA keys as XZZX.January 2019
The charity story
Coveware reports CryptoMix attackers claiming that ransoms fund a children's charity, with real children's photographs from crowdfunding pages.
6 October 2026
Our recheck
We compared the old guide with BleepingComputer, PCrisk, Avast, Coveware and the No More Ransom list and corrected the decryptor claim.
What we checked and what we did not
We did not run this malware, and ransomware has no website to test, so this is a check of sources. It tells you about the family, not about your PC.
XZZX ransomware · source check · 6 October 2026
- Note and addressesThe four addresses are identical in BleepingComputer, PCrisk and our own 2017 screenshot.
- Extension and keysBoth BleepingComputer and PCrisk show a 32-character name ending
.XZZXand 11 RSA-1024 keys. - DecryptorThe No More Ransom list has CryptoMix decryptors by CERT-PL and Avast. No source says they open
.XZZXfiles, or that they do not. Not confirmed. - BehaviourThe command list is from BleepingComputer's analysis of one sample. We did not run it.
- How it spreadNo source we read documents how XZZX itself reached PCs.
Serious, with no confirmed free fix This is real file-encrypting ransomware. Removing it protects the PC but does not return files. A source check proves nothing about whether a particular PC is clean.
- File extension:
.XZZX - Note file:
_HELP_INSTRUCTION.TXT
Names, files and indicators
Use these only to confirm that a scan found the right family.
We found no Microsoft Defender name for XZZX in public sources.
| Indicator | Value | Source |
|---|---|---|
| Encrypted file | [32 letters and digits].XZZX | BleepingComputer, PCrisk |
| Program | C:\ProgramData\[random].exe | BleepingComputer |
| SHA256 of the sample | 33a60a16e50b8df2a731023951475ff0f973fc66334d2cfa6ce30aa36bb36414 | BleepingComputer |
| Contact addresses | xzzx@tuta.io, xzzx1@protonmail.com, xzzx10@yandex.com, xzzx101@yandex.com | BleepingComputer, PCrisk, our 2017 screenshot |
How XZZX ransomware behaves
How the encryption works
Each victim gets an AES key, and that key is locked with one of 11 RSA-1024 public keys built into the program, so nothing can unlock it without the attackers' private key.
- 1
AES encrypts the files
PCrisk describes AES as the symmetric part: it makes one key for the victim and encrypts the data with it.
- 2
RSA locks the AES key
The program carries 11 public RSA-1024 keys and uses one of them on the AES key. The matching private key is held by the attackers.
- 3
No network is needed
BleepingComputer notes that the built-in keys let it work completely offline, so unplugging the cable does not stop a running encryption.
- 4
Names are replaced
Each original name becomes 32 random letters and digits plus
.XZZX, so you can no longer tell which file is which.
What else it does to the PC
Besides encrypting, it stops security and update services and deletes the Windows restore points, so the old advice to roll back with System Restore rarely works here.
- 1
It stops services
BleepingComputer's command list has
sc stopforVVS(as written there; the Volume Shadow Copy service is VSS, so possibly a typo),wscsvc(Security Center),WinDefend(Microsoft Defender),wuauserv(Windows Update),BITS,ERSvcandWerSvc. - 2
It switches off boot recovery
bcdedit /set {default} recoveryenabled Noandbootstatuspolicy ignoreallfailuresstop Windows starting its recovery tools after failed boots. We have not tested the effect on the Advanced startup menu. - 3
It deletes shadow copies
vssadmin.exe Delete Shadows /All /Quietremoves the snapshots that Previous Versions and System Restore use.
What the note says
The note asks you to e-mail all four addresses with your ID number and promises help "as soon as possible". It gives no price, no wallet and no deadline.
| Part of the note | What it says | What it means |
|---|---|---|
| Opening | "Attention! All Your data was encrypted!" | The wording earlier CryptoMix notes used |
| Contact | Four addresses at tuta.io, protonmail.com and yandex.com, all beginning xzzx | The note tells you to write to every one |
| Your ID | DECRYPT-ID- and a long code | It identifies your files to the attacker; do not send it |
| Price | Not mentioned | The 2017 guide was right; PCrisk says the earlier CryptoMix demanded 5 bitcoins |
How it reaches PCs
No source we read documents how XZZX itself spread.
The 2017 guide named malicious spam as the main route; PCrisk and Avast add the others.
- High
E-mail attachments
PCrisk lists JavaScript files and Office macros. The 2017 guide described spam posing as an important document, statement or invoice.
- Medium
Exploit kits
Avast saw CryptoMix delivered by the RIG exploit kit in February 2017; nothing ties this to XZZX.
- Medium
Trojans, fake updaters and downloads
PCrisk names trojans that open a backdoor, fake software updaters, and free-software or torrent sites that disguise malware.
Other CryptoMix variants and lookalikes
| Name | How it relates | What to do |
|---|---|---|
.0000 | A November 2017 variant with the same 11 RSA keys and note name | Treat like XZZX; its addresses begin y0000 |
| CryptoShield, CryptFile2, Zeta | Earlier names of CryptoMix (Avast) | The Avast and CERT-PL decryptors were made for these |
| Charity-story CryptoMix | A 2019 campaign using a fake children's charity (Coveware) | Do not pay |
| STOP/Djvu and others | Different families with their own keys | Their decryptors do not apply to .XZZX |
Was anything stolen?
The sources we read describe encryption only, not data theft, but PCrisk warns that password-stealing trojans can arrive together with ransomware.
- Medium
Other malware may have come with it
If it arrived by attachment or fake updater, change your passwords from a clean device.
- Low
No leak site documented
The note only asks for contact; neither BleepingComputer nor PCrisk mentions a leak site.
What to do in the first hour
- 1
Disconnect from the network
Unplug the cable or turn Wi-Fi off to stop the spread to shared folders.
- 2
Unplug external drives
Disconnect USB drives and backup disks. Do not plug a backup in again until the PC is clean.
- 3
Keep the note and one encrypted file
Photograph
_HELP_INSTRUCTION.TXTand copy it with a small.XZZXfile to a USB stick. - 4
Pause cloud sync
Pause OneDrive, Dropbox or iCloud on the PC so that encrypted copies do not overwrite the clean versions online.
Cryptomix variant XZZX ransomware infected PC. How can I remove it? I have the majority of files backed up, so I want just to clean my PC and get back to normal life.
A reader's question under our 2017 guide. With a backup the plan below is the whole job: clean first, restore second.
The XZZX ransomware note
Hello!
Attention! All Your data was encrypted!
For specific informartion, please send us an email with Your ID number:
xzzx@tuta.io
xzzx1@protonmail.com
xzzx10@yandex.com
xzzx101@yandex.com
Please send email to all email addresses! We will help You as soon as possible!
DECRYPT-ID-[your ID] number
Can XZZX ransomware files be decrypted?
Can .XZZX files be decrypted?
Not by anything we can confirm. Our 2017 guide said no decryptor existed, which was true for XZZX then, but the family has free decryptors for older versions, so check before you give up.
| Tool | What it covers | Works on .XZZX? |
|---|---|---|
| CryptoMix decryptor by CERT-PL (No More Ransom) | Files encrypted by CryptoMix | Not confirmed |
| Avast CryptoMix decryptor (2017) | Files locked with the fixed offline key; other files are left untouched | Not confirmed; .XZZX is not in its extension list |
| ID Ransomware (web service) | Names the family from a note and a sample file | Identifies only; does not decrypt |
- 1
Keep the encrypted files
Copy the
.XZZXfiles and one note to a USB drive. Decryptors sometimes appear years later. - 2
Identify the family
On another device, upload
_HELP_INSTRUCTION.TXTand one small.XZZXfile to ID Ransomware, then search the No More Ransom list for the name it returns. - 3
Try a tool on a copy
Run the CERT-PL or Avast tool on a copy only. If it cannot decrypt, it changes nothing. Avoid any site that sells an "XZZX decryptor".
Should you pay the ransom?
No. The note names no price, so you would learn it only by writing to the attackers, and Avast warned that CryptoMix victims who paid 5 to 10 bitcoins were left without decrypted files. The 2017 guide added that criminals may not even have a key; Avast says the code has flaws that can make files undecryptable.
- High
Pressure through a fake charity
In 2019 Coveware saw CryptoMix negotiators claim the money would go to a children's charity, with real children's photographs. The story was invented.
- Medium
You mark yourself as a payer
Writing to the addresses tells the attackers that your address is live.
Do
- Report the attack to your national cybercrime service
Don't
- Do not send your DECRYPT-ID to the addresses
- Do not pay in bitcoin to a page you were sent by e-mail
How to remove XZZX ransomware
Tools you'll need
All of these are free except where noted. Download them on a clean device if the infected PC is offline.
- A USB stick: to keep the ransom note, two or three encrypted files and screenshots off the infected PC.
- Microsoft Defender Offline: built into Windows 11 and Windows 10; scans before Windows starts, so running malware cannot hide.
- Microsoft Safety Scanner: a second, portable scanner with current signatures; each download works for 10 days.
- ID Ransomware: identifies the family from the note and one encrypted file and says whether a decryptor exists.
- No More Ransom: the free decryptors from police and security companies; check it again every few months.
- Fortect (optional): scans Windows for malware and repairs the system files and settings it damaged. The free scan is in the box above.
How to remove XZZX ransomware and get your files back
Work in this order.
Disconnecting comes first, removal comes before any restore, and nothing here asks you to contact the attackers.
Step 1: Disconnect the PC and unplug backup drives
Unplug the network cable or turn off Wi-Fi, and disconnect USB drives, external disks and network shares, so XZZX ransomware cannot reach more files. Pause OneDrive, Google Drive or Dropbox sync, because synced folders upload the encrypted copies over the good ones.
Leave the PC on but offline while you read the next steps, since a restart can let the ransomware run again. This applies to Windows 11 and Windows 10 alike.
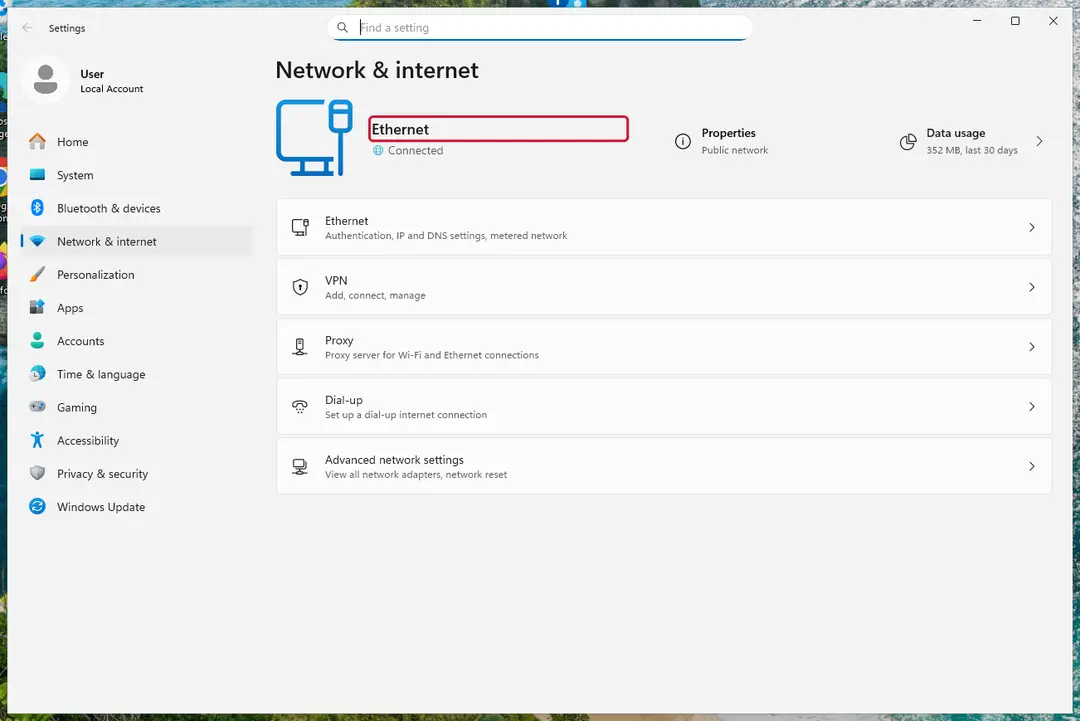
Windows 11: turn off Wi-Fi to take the PC offline. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 2: Save the ransom note and confirm the family
Your files now end in
.XZZXand the instructions are in_HELP_INSTRUCTION.TXT. Save both to a USB stick, a copy of the note and two small encrypted files, before anything else.On another device, check them with ID Ransomware or Crypto Sheriff: the family name decides which decryptor, if any, can help. Keep the note's ID and contact line for your report.
Windows 11: the ransom note and encrypted files to copy for identification. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 3: Check for a free decryptor
Our last check found that for XZZX ransomware, no free decryptor is known (checked 6 October 2026). Look again yourself in the No More Ransom list and the free decryptor pages of Emsisoft, Avast and Kaspersky, which add new families every year.
A decryptor needs the ransomware gone first, or it encrypts the files again. Keep at least one copy of the encrypted files on an external drive, even if no tool works yet.
Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 4: Remove the ransomware before you restore or decrypt
Removing XZZX ransomware does not bring the files back, but it has to come first. Start with Defender's Full scan, then the offline scan from the same Scan options page, which checks the disk before Windows loads.
If the scan cannot start, use Safe Mode with Networking. Delete the ransom notes only after you have saved a copy, because removal tools sometimes leave them behind on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Look for shadow copies of the files
Windows keeps shadow copies for restore points and backups, and some ransomware fails to delete them.
vssadmin list shadowsin an administrator Command Prompt tells you at once whether any exist.If they do, right-click the folder that held your files, open Properties > Previous Versions, select a version from before the attack, and click Open to check it before you Restore or copy the files out. Windows 11 and Windows 10 both have the tab.
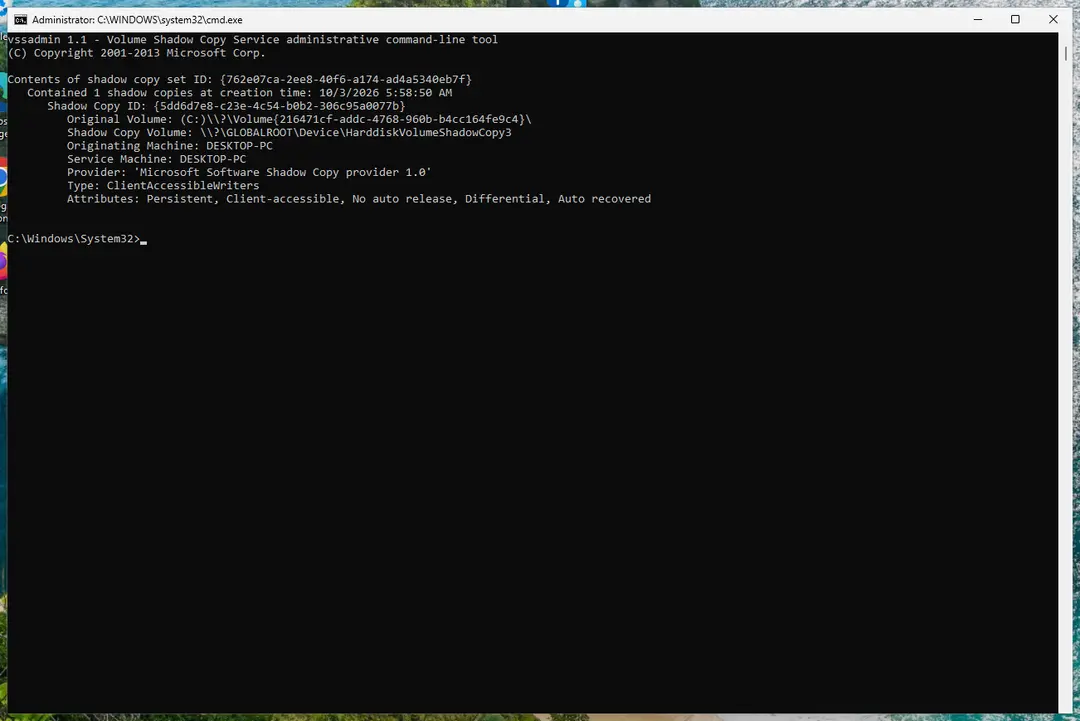
Windows 11: vssadmin list shadows shows whether shadow copies exist. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 6: Restore the files from a backup or recover deleted originals
A backup made before the attack is the surest way back. Connect it only once the PC is clean, then restore from File History, Windows Backup, OneDrive's Restore your OneDrive or your own external copies.
Without a backup, try file recovery: the originals that XZZX ransomware deleted may still be on the disk until something overwrites them. Install nothing new on the drive you want to recover from on the Windows 11 or Windows 10 PC.
Full procedure with screenshots: Recover deleted files (Recycle Bin, backups, OneDrive) On uGetFix
Report it and recover your files
Report it
Report the attack even if you do not expect the files back: insurers and banks ask for the report number, and police use the contacts in the note to link cases.
- United States
- FBI IC3 · FTC ReportFraud
- United Kingdom
- Report Fraud (formerly Action Fraud) · NCSC
- Australia
- ReportCyber (ASD)
- EU countries
- Europol: national reporting sites
Give the victim ID, the note and the date the files were encrypted. A business that holds personal data may also have to notify its data protection authority, in the EU within 72 hours.
Ways to get files back
Check these in order, before you save anything new to the disk.
The 2017 guide offered Previous Versions and ShadowExplorer; the correction is that this program deletes shadow copies, so they are usually empty.
- 1
Your own backups
An external drive, a NAS or cloud storage is the most reliable source. Connect it only after the PC is clean, then open a few files.
- 2
Cloud version history
OneDrive, Dropbox and iCloud keep earlier versions. In OneDrive on the web, Settings has Restore your OneDrive (PCrisk).
- 3
Previous Versions and shadow copies
Right-click a folder, choose Properties then Previous Versions (Windows 11: Show more options first). Or run
vssadmin list shadowsas administrator. An empty list is what BleepingComputer's commands predict; ShadowExplorer can browse any that remain. - 4
Windows File Recovery
winfr C: D: /regular /n \Users\<name>\Documents\looks for deleted files in free space. The drives must differ, and Microsoft warns that free space may be overwritten, especially on an SSD. We expect little here; not confirmed.
Back up with the 3-2-1 rule
The 2017 guide said recovery may fail without backups.
The 3-2-1 rule that PCrisk describes turns that into a plan.
| Number | Rule | Example |
|---|---|---|
| 3 | Three copies of every important file | The working file and two backups |
| 2 | Two kinds of storage | Your disk and an external drive |
| 1 | One copy kept off the PC | An unplugged drive, or cloud storage with version history |
How to prevent XZZX ransomware and the next attack
Do
- Delete unexpected e-mails, and open an attachment only after you know who sent it
- Keep Windows, Microsoft Defender and your programs updated, from the program's own menu
- Install programs only from the maker's website or the Microsoft Store
- Turn on file extensions (View > Show > File name extensions) so a
.pdf.execannot pass as a document
Don't
- Do not click ads that offer security software or updates
- Do not download pirated programs or other illegal content
- Do not run
.js,.exeor macro documents from unknown senders
Questions about XZZX ransomware
How do I remove XZZX ransomware?
Disconnect the PC, scan it, and only then restore files. Boot into Safe Mode with Networking (on Windows 11 and 10:
- Recovery settings
- Advanced startup
- Troubleshoot
- Advanced options
- Startup Settings
- Restart
- then press 5)
- run a full Microsoft Defender scan
- finish with a Microsoft Defender Offline scan from Windows Security
Delete the random executable in C:\ProgramData if a scan lists it. Removal stops further encryption but does not return files, so keep the encrypted copies and restore from a clean backup afterwards.
How do I open .XZZX files?
You cannot open .XZZX files with any program. XZZX renamed each file to 32 random characters and encrypted its contents, so the original name and type are lost too. Renaming them changes nothing and may make a later decryption harder, so leave them alone.
Copy them to an external drive and restore your documents from a backup or from cloud version history. Without a backup, keep the copies and wait for a tool that supports XZZX.
Is there a decryptor for XZZX ransomware?
No decryptor is confirmed for XZZX. The files are locked with an AES key wrapped in one of 11 RSA-1024 public keys, so the private key sits with the attackers.
Avast and CERT-PL made free decryptors for earlier CryptoMix versions that used a fixed offline key, and the No More Ransom list carries them, but no source says they open .XZZX files. Try one on a copy of a file, keep every encrypted file and check the list again later. A decryptor sold to you is most likely a scam.
Do data recovery companies or paid decryption services work?
Mostly not for this family. A service cannot break the 11 RSA keys, so the good ones only check whether a free tool or a surviving copy exists, which you can do yourself with ID Ransomware and the No More Ransom list.
Services that promise to decrypt XZZX for a fee usually pay the attackers or do nothing. A recovery firm may find unencrypted originals in free space on a hard disk, but that is rare on an SSD. Ask for the method and a refund promise before you pay.
Should I pay the XZZX ransom or e-mail the addresses?
No, do not write to the addresses and do not pay. The note names no price, so you would learn it only by contacting criminals, and nothing obliges them to send a working key.
Avast reported in 2017 that CryptoMix victims who paid 5 to 10 bitcoins were left without decrypted files, and Coveware saw the family use a fake children's charity to press victims in 2019. Report the attack to your national cybercrime service and use the recovery options in this guide.
How did XZZX get on my PC?
We cannot say how it reached your PC, because no source we read documents XZZX's own spreading. The usual routes for this family are malicious e-mail attachments such as JavaScript files or Office documents with macros, exploit kits, trojans, fake software updaters and downloads from torrents or free-software sites.
Check your e-mail and downloads from the day before the first renamed file, and close remote desktop access if you do not need it. Remove the cause before you restore anything.
Was my data stolen by XZZX?
We found no evidence that XZZX copies files out. Neither BleepingComputer nor PCrisk describes a leak site or a data upload for this variant, and the note only asks you to make contact.
PCrisk does warn that password-stealing trojans can be installed together with a ransomware infection, so change your passwords for e-mail, banking and cloud storage from a clean device and turn on two-step sign-in. One source check does not prove that nothing was taken.
Is XZZX the same as CryptoMix, and what is the .0000 variant?
XZZX is a version of CryptoMix, found on 13 November 2017; CryptoMix is the family name, and earlier versions were also called CryptFile2, Zeta and CryptoShield. A few days later a variant appeared that adds .0000 to file names and uses contact addresses beginning y0000.
BleepingComputer found that it carries the same 11 RSA keys as XZZX, so it behaves the same way. Match the extension on your files with this guide before you try a tool.
I have backups. How do I clean the PC and get back to normal?
Clean first and restore second. Keep the backup drive disconnected, boot into Safe Mode with Networking, run a full Microsoft Defender scan and then a Microsoft Defender Offline scan.
When both are clean, change your passwords from another device, update Windows, connect the backup and copy your files back, opening a few documents before you delete the encrypted copies. If the PC still behaves oddly, reinstalling Windows from official media is the surest way to remove everything.
Will Fortect remove XZZX ransomware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For XZZX ransomware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- BleepingComputer: XZZX Cryptomix Ransomware Variant Released (read October 6, 2026)
- BleepingComputer: 0000 Cryptomix Ransomware Variant Released (read October 6, 2026)
- PCrisk: XZZX Ransomware (read October 6, 2026)
- Avast: CryptoMix, Avast adds a new free decryption tool (read October 6, 2026)
- Coveware: CryptoMix Ransomware Exploits Child Cancer Crowdfunding (read October 6, 2026)
- No More Ransom: decryption tools (read October 6, 2026)
- Microsoft Support: Windows startup settings (Safe Mode) (read October 6, 2026)
- Microsoft Support: Virus and threat protection in Windows Security (Microsoft Defender Offline scan) (read October 6, 2026)
- Microsoft Support: Windows File Recovery (read October 6, 2026)